Home Blog Page 318

WhatsApp Hacked! Attackers Injected Spyware

Whatsapp

The popular messaging application WhatsApp revealed that it discovered a vulnerability in its network system that allowed hackers to install spyware via an infected WhatsApp voice call. The Facebook-owned social messenger stated the spyware can exploit the mobile device, its calls, texts, and other data. It can also activate the phone’s camera, microphone, and able to perform other malicious activities. According to Facebook, the malicious spyware was developed by Israel-based cyber intelligence company NSO Group.

“A buffer overflow vulnerability in WhatsApp VOIP stack allowed remote code execution via specially crafted series of SRTCP packets sent to a target phone number. The issue affects WhatsApp for Android prior to v2.19.134, WhatsApp Business for Android prior to v2.19.44, WhatsApp for iOS prior to v2.19.51, WhatsApp Business for iOS prior to v2.19.51, WhatsApp for Windows Phone prior to v2.18.348, and WhatsApp for Tizen prior to v2.18.15,” Facebook said in a statement.

According to Facebook, the mobile devices with WhatsApp or WhatsApp Business installed in them are affected, including Apple’s iPhone (iOS), Android phones, Windows Phones, and Tizen devices. However, the company clarified that it’s unclear on the number of people spied on by hackers.

Facebook has advised its users to update their WhatsApp applications for further protection. The company said it has implemented a server-side change to protect users and pushed out updates for the various smartphone WhatsApp versions.

WhatsApp encountered a similar issue earlier in 2018 when the Indian Army issued a warning to the users of WhatsApp, alleging that Chinese hackers are targeting them to extract personal data. The Army took to the microblogging site, Twitter to urge users to use WhatsApp with caution. Indian Army’s official handle, the Additional Directorate General of Public Interface (ADGPI) also posted a video that said, “Stay cautious, stay alert, stay safe! The Chinese were penetrating the digital world.”

The video urged users to save contacts by name and to constantly keep a vigil on all WhatsApp groups and numbers. “Chinese are using many platforms to penetrate your digital world. WhatsApp groups are a new way of hacking into your system. Chinese numbers barge into your groups and start extracting all the data. If you change your mobile number, inform the group admin; if you change your SIM card, destroy it completely,” it advises.

Also, a survey by Natalie Silvanovich, a digital forensics expert at Google Project Zero, discovered that answering a WhatsApp video call can compromise smartphones. The researcher stated that a security bug in the WhatsApp messenger application allows attackers to take control of the smartphone by placing a WhatsApp video call.

Describing the issue as a “memory corruption bug in WhatsApp’s non-WebRTC video conferencing implementation,” the security researcher stated that a memory heap overflow issue causes when an attacker places a specially created malformed RTP (Real-time Transport Protocol) via WhatsApp video call request, resulting in the break-in to the mobile memory.
WekaIO raises $31.7 million to expand its global reach

Startup funding

WekaIO, a developer of data storage and file management systems for artificial intelligence, recently announced that it has secured $31.7 million in a Series C funding round led by Hewlett Packard Enterprise (HPE) and Mellanox Technologies along with the participation from the existing investors NVIDIA, Seagate, and Western Digital Capital.

The California-based startup stated the new investment will be used to expand its global reach and accelerate market demand. Founded in 2013, WekaIO develops technology for data-intensive applications within enterprises and allows storage and swift transmission of artificial intelligence applications, machine learning, financial, and medical analysis.

WekaIO helps enterprises manage, scale, and futureproof their data centers in order to resolve data storage concerns. The company claims that its AI-based storage platform WekaIO Matrix is the fastest shared parallel file system that delivers a high-end software-defined storage solution that removes the barriers between the data and the computer layer, accelerating artificial intelligence, machine learning, genomics, research, and analytics workloads.

Commenting on the new investment, Liran Zvibel, the CEO and co-founder of WekaIO said, “This latest round of financing sets the stage for substantial growth and allows us to continue our mission to deliver an enterprise-grade HPC storage solution at cloud-scale economics. Modern workloads need a modern file system and legacy solutions just can’t keep pace. In under two years since our launch from stealth, we’ve been lauded with industry awards and accolades, been validated in production environments with leading enterprise organizations, and broken records on industry-leading benchmark tests beating out some of the world’s largest supercomputers. This additional capital will allow us to increase our presence worldwide and continue to innovate in order to exceed the evolving needs of our customers.”

“We are seeing an explosion of artificial intelligence, machine and deep learning along with high-performance computing in the enterprise market,” said Paul Glaser, Head of Pathfinder, HPE. “By combining HPE’s industry-leading server architecture with WekaIO’s performance-leading software in an integrated, tested, and validated package, we can deliver best of breed solutions to our customers. This is a great example of HPE’s Pathfinder program that seeks to partner with emerging companies that are strategically aligned with HPE to drive innovative customer solutions and benefits.”


Red Balloon Security discovers vulnerability “Thrangrycat” in Cisco security products

CISCO

Security firm Red Balloon Security recently discovered a critical vulnerability in Cisco’s products, including routers, switches, and firewalls, which are used among the private and government networks.

Founded in 2011, Red Balloon Security is a cybersecurity provider and research firm focussed on the protection of embedded devices. The New York-based company claims that its advanced suite of host-based firmware security solutions secures embedded systems by continuously monitoring critical elements of the firmware.

Red Balloon stated the vulnerability, codenamed as “Thrangrycat,” is caused due to hardware design flaws within Cisco’s Trust Anchor module (TAm), which is a proprietary hardware security module used in a wide range of Cisco products, including enterprise routers, switches, and firewalls.

According to Red Balloon, the vulnerability provides hackers a backdoor into highly secure networks, allowing them to bypass security defenses in order to gain full and persistent access inside the network. Cybercriminals might use this vulnerability to interrupt communications, steal or manipulate data, install stealthy implants, and can make attacks on other connected devices.

Speaking on the latest discovery, Dr. Ang Cui, the founder and chief scientist of Red Balloon Security said, “This is a significant security weakness which potentially exposes a large number of corporate, government and even military networks to remote attacks. We’re talking about tens of millions of devices potentially affected by this vulnerability, many of them located inside of sensitive networks. These Cisco products form the backbone of secure communications for these organizations, and yet we can exploit them to permanently own their networks. Fixing this problem isn’t easy, because to truly remediate it requires a physical replacement of the chip at the heart of the Trust Anchor system. A firmware patch will help to offset the risks, but it won’t completely eliminate them. This is the real danger, and it will be difficult for companies, financial institutions and government agencies to properly address this problem.”

A similar research from RedTeam Pentesting revealed that there are potential vulnerabilities in Cisco’s small business routers that could allow a remote attacker to exploit the devices to get sensitive diagnostic data. The German-based security firm stated the discovered vulnerabilities are located in the web-based management interface used for the routers and can be remotely exploitable.

Cisco stated the issue existed in its RV320 and RV325 Dual Gigabit WAN VPN business routers. The researchers at RedTeam stated the flaw CVE-2019-1652 allows attackers with administrative privileges on an affected device to execute arbitrary commands on the system and another flaw CVE-2019-1653 allows intruders to retrieve sensitive information including the router’s configuration file containing MD5 hashed credentials and diagnostic information. It’s found that approximately 9,657 Cisco routers (6,247 RV320 and 3,410 RV325) worldwide are vulnerable to the information disclosure, according to the researchers.

Two Chinese nationals indicted for Anthem hack

Department of Justice

The United States Department of Justice (DoJ) has indicted two Chinese nationals for their role in the Anthem hack. The hack, which, in its time, was considered one of the biggest cyber security attack the nation had ever witnessed, had compromised data of nearly 80 million people. The leaked data included birthdays and Social Security Numbers of the customers. Even though there were four companies that were victims in the released indictment, only Anthem had been named.

The other companies that were hacked around the same time as Anthem included Community Health Systems and federal Office of Personnel Management (OPM). In the OPM hack, exposed sensitive personal information of about 21.5 million government workers were compromised. The hack campaign which started in 2014 went for another three years or even more.

The DoJ has not accused both the persons, Fujie Wang and the other who has only been identified as John Doe, a Chinese intelligence personnel. The recent indictment answers several speculations among the cybersecurity experts, who have long tried to establish a connection between the hack at Anthem and the involvement of Chinese Intelligence.

In November, last year, Anthem announced that the victims of the data breach were going to receive payouts in the class action settlement. The American health insurance company stated that it has reached a settlement in the class action lawsuit.

“Anthem has reached a settlement to completely resolve the multidistrict class action litigation brought against Anthem and other defendants relating to the 2015 cyber-attack. Under the settlement, which the court granted final approval to on August 15, 2018, Anthem does not admit any wrongdoing or acknowledge that any individuals were harmed as a result of the cyber-attack. Nevertheless, we are pleased to be putting this litigation behind us, and to be providing additional benefits to individuals whose data was impacted in the cyber-attack,” Anthem said in a statement.


“As a CISO, most important is to leave your ego at the door”

Ben Aung

Ben joined Sage as Global CISO in 2018 after 16 years in the British Government. Sage is the UK’s largest technology company and Ben is responsible for protecting the global technology estate, products and cloud services for 3 million customers in 23 countries. Ben began his security career at the National Archives and finished as Deputy Government CSO, responsible for all aspects of UK government security. While in government Ben worked on numerous national crisis, such as the 2017 WannaCry outbreak, and led transformative security reforms to unlock access to public cloud and modernise decades old security practices.

It has been a year since the Global Data Protection Regulation came into effect. In what ways has GDPR affected businesses in the last year?

In practical terms many have adopted new data processes to meet the regulation’s requirements, some of those changes will have bedded in and others will still be a bit clunky but all will have impacted a lot of day to day operations. I’m sure that many organisations have ongoing data privacy programmes, either continuing to deliver GDPR compliance or moving beyond into other aspects of data governance and good housekeeping. Those unlucky enough to experience a breach will have worked in unfamiliar territory to meet new notification requirements.

More conceptually, GDPR will have elevated the way many businesses think about data from both a protection and exploitation perspective. Many will still consider it a Board issue. My sense is that this has driven the maturity and sophistication of the discussion forwards and will continue to do so into the coming years.

Read More

Turkey fines Facebook for $271,000

Facebook Data leak, Facebook bans cyber mercenary

The Turkish government’s watchdog, Personal Data Protection Authority (KVKK), recently fined Facebook a total of 1.65 million Lire ($270,976.01) in April 2019, for failing to protect its users’  personal information.

The fine comes after Facebook reported a data breach in December 2018, that exposed 6.8 million users’ private photos to third-party application developers. The social networking giant stated that its internal team discovered a photo API bug that allowed third-party apps to access users’ photos for 12 days between September 13 to September 25, 2018. The company declared that it has fixed the issue, but some third-party apps may have had access to a wider set of photographs which were uploaded/shared on the Facebook Stories.

KVKK stated that the data breach affected around 300,000 users in Turkey last year and Facebook not reacted in time with technical precautions regarding the issue.

Facebook has already faced severe criticism over privacy issues last year and in recent times. The company drew fire for not handling users’ sensitive information on its platform. In January 2019, the Ministry of Information and Communications (MIC) of Vietnam stated that Facebook has violated its new cybersecurity law by allowing users to post anti-government comments on its platform.

The concern was raised at a media conference held by MIC’s Authority of Broadcasting and Electronic Information (ABEI). The ABEI stated the social media giant had violated Vietnamese cybersecurity laws in three major areas: managing content, online advertising, and tax liability. This comes days after Vietnam lawmakers approved the controversial new cybersecurity law that took effect from January 01, 2019, that controls the Internet content and global tech companies operating in the country. The new cyber law requires Facebook, Google, and other international tech firms to store local users’ data on local servers and set up offices in Vietnam.

Recently, Researchers from the cybersecurity firm UpGuard discovered that Facebook user account information was exposed on Amazon cloud servers. The security team at UpGuard stated that they found two data breach incidents in different regions.

The first incident was originated from the Mexico-based media company Cultura Colectiva which exposed around 146 GB of data that contained over 540 million records detailing comments, likes, reactions, account names, FB IDs, and other sensitive information. The second was a separate database from a Facebook-integrated app named ‘At the Pool’ which exposed data via an Amazon S3 bucket. UpGuard stated the data was stored in Amazon’s cloud service without password protection and could easily be accessed by outsiders.

Cybersecurity Insurance startup Coalition secures $40 million

Startup funding

Coalition, a cybersecurity insurance provider, recently raised $40 million in a funding round led by Fintech investment firm Ribbit Capital along with the participation from Greenoaks Capital and Hillhouse Capital. The startup stated the new investment will be used to expand its data analytics platform, engineering, and incident response team.

Coalition helps small, medium, and large enterprises manage cyber risk by integrating technology and insurance. The startup claims that it provides free cybersecurity tools and up to $10 million in insurance coverage to companies globally.

Coalition’s insurance covers expenses incurred from liabilities like fines and penalties, fraud attack, breach response, extortion, ransomware recovery, device replacement, and more. The company also offers threat intelligence services and advice to help the U.S.-based customers improve their cybersecurity posture.

The growing threat landscape led to an increase in awareness and interest in cybersecurity insurance, globally and thereby driving the growth of the cyber insurance market. According to a research, the cybersecurity insurance market is going to witness over 20% CAGR in the coming years. Over the past few years, cyber analysts have been tracking the rapid increase in criminalization of the internet. Individual cyber criminals are uniting into international criminal groups to strengthen the impact of their attacks and activities against sensitive and critical business data.

Data protection and privacy is one of the key cyber risks faced by the emerging economies due to ample generation of online and offline data. With cyber security related legislations becoming tougher globally, more notifications of, and significant higher fine for data breaches are driving the growth in demand for cyber insurance across all sized enterprises. Legislations have already become much stronger and tougher in the U.S., Singapore, Hong Kong, and Australia, while the European Union (EU) is also looking to agree to Pan-European data protection rules and regulations. Thus, mandatory legalizations regarding cyber security is driving the growth of the cyber insurance market all over the world.

In 2018, a survey from analytics software company FICO revealed that 62 percent of UK firms lack complete cybersecurity insurance. According to the research, only 38 percent of UK firms surveyed have cybersecurity insurance that covers all risks. Telecommunications firms lag behind other industries regarding cybersecurity insurance, 17 percent of firms reported that they have no coverage. Most of the respondents stated that their premiums are based on an inaccurate analysis or unknown factors.

Amazon suffers ‘fraud attack’ from cybercriminals

Amazon

E-Commerce giant Amazon recently suffered a fraud attack in which hackers syphoned funds from its merchant accounts over six months last year. The Seattle-based e-tailer stated that unknown cybercriminals broke into around 100 seller accounts and syphoned money into their own accounts, the Bloomberg reported. Amazon said the hack took place between May 2018 and October 2018, and it’s unclear how much money was stolen in the incident.

According to Amazon’s legal team, the hackers managed to alter account details on the Seller Central platform to their own at Barclays Plc and Prepay Technologies Ltd. It’s believed that the accounts were compromised by using phishing techniques that deceived sellers into giving up sensitive information.

Amazon stated that its investigation is still ongoing and asked the London judiciary for approval of searching the accounts of hackers.

In a similar incident, Amazon suffered a technical glitch on its India portal that affected its sellers and vendors. The e-tailer stated that a bug in its website caused a data breach on January 08, 2019, that exposed sensitive financial information, including sales, category-wise split and inventory data of its sellers and vendors. Having around 400,000 online vendors and sellers across the country, Amazon said the issue was resolved within a few hours, but, the exact figure of affected members is not yet discovered.

The issue came to light after some Amazon vendors reported that they received incorrect data while downloading their Merchant Tax Reports (MTR) from the portal. It has been said that data of some sellers were visible to other competing sellers. An MTR statement holds information of all the other transactions processed by a seller on the e-commerce platform, which is usually downloaded from the portal between 8th-10th of every month.

Recently, a group of researchers from the cybersecurity firm UpGuard revealed that Facebook user account information was exposed on Amazon cloud servers. The security team at UpGuard stated that they found two data breach incidents in different regions. UpGuard stated the data was stored in Amazon’s cloud service without password protection and could easily be accessed by outsiders.

The first incident was originated from the Mexico-based media company Cultura Colectiva which exposed around 146 GB of data that contained over 540 million records detailing comments, likes, reactions, account names, FB IDs, and other sensitive information. The second was a separate database from a Facebook-integrated app named ‘At the Pool’ which exposed data via an Amazon S3 bucket. This database contained the backup information like fb_user_id, fb_user, fb_friends, fb_likes, fb_music, fb_movies, fb_books, fb_photos, fb_events, fb_groups, fb+checkins, fb_interests, and passwords, according to UpGuard.

ITC Expands Its Current Security Service Portfolio with the Launch of Six New 24/7 Managed Security Services

4 in 10 Organizations Struggle with SOC Staff Shortages: Report

Press Release contributed by Integrated Telecom Company

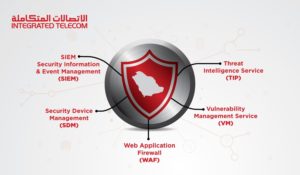
Integrated Telecom Company, a leader in Telecom and ICT services, announced that it expanded its portfolio of security services by launching a new suite of Managed Security Services (MSS)  to assist organizations with monitoring, threat detection, incident handling, and management of ongoing cybersecurity risks.

These MSS services provide proactive and comprehensive security monitoring of network devices, endpoints, Cloud and SAAS based environments. Leveraging extensive ICT industry knowledge, ITC will provide this service line to address the unique concerns and lack of security resources in the Saudi market, as well as provide visibility to threats in real time. Managing all of the security technologies deployed in the average enterprise has become a daunting task for many and staying well ahead of the threat originators to mitigate their impacts is considerably harder.

Integrated Telecom

“Many Saudi companies have expressed frustration with the fact that they don’t have adequate threat monitoring or the appropriate level of attention they need from their managed services provider. Moreover, many service providers don’t have the experience or know how to tailor their support for the Saudi market. Many organizations still struggle with managing risk because they can’t optimize all of the security tools or simply don’t have the resources to monitor their outputs,” said Ahmad Hasan, CCO of ITC. “Expanding our service offering with SIEM, Threat Intelligence, WAF, Vulnerability Management, Penetration Testing and Security Device Management, will significantly increase our ability to assist our clients with this challenge by providing real time 24/7 monitoring and 360° Cyber Protection in support of their program,” he added.

“We have developed multiple services as a trusted Telecom and ICT partner, so this was just a natural extension of our desire to help our clients identify and manage their security risks more effectively,” said Ghassan Itani, CEO of ITC. “We are especially excited to be able to provide an affordable alternative for the small, mid and large-enterprises who often cannot take advantage of this type of support for various reasons,” he added.

About ITC

Integrated Telecom Company (ITC) is a leading Saudi based telecom provider established in 2005. Since then, ITC has grown into one of today’s fastest-growing telecom companies offering next-generation solutions for broadband, connectivity, cloud computing, managed services, satellite services and internet services for businesses, wholesale and consumers’ segments.


CISO MAG does not evaluate the advertised product, service, or company, nor any of the claims made by the advertisement. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.

Hackers stole $40 million from cryptocurrency exchange Binance

Bitcoin hack

In a major security breach, hackers stole over $40 million worth of Bitcoin from the popular cryptocurrency exchange Binance. The Taiwanese company stated it discovered the breach on May 7, 2019, at 17:15:24 (UTC), in which hackers illegally obtained over 7,000 Bitcoins by using a variety of attack methods, including phishing, viruses, and other attacks.

According to Binance, hackers also accessed several user API keys, 2FA codes, and other information. Following the hack, the exchange suspended all the operations temporarily and assured that it will refund the affected customers in full.

“The hackers had the patience to wait and execute well-orchestrated actions through multiple seemingly independent accounts at the most opportune time. The transaction is structured in a way that passed our existing security checks. It was unfortunate that we were not able to block this withdrawal before it was executed. Once executed, the withdrawal triggered various alarms in our system. We stopped all withdrawals immediately after that,” Binance said in a statement.

“The transaction is structured in a way that passed our existing security checks. It was unfortunate that we were not able to block this withdrawal before it was executed. Once executed, the withdrawal triggered various alarms in our system. We stopped all withdrawals immediately after that,” Binance added.

There have been multiple breaches reported by cryptocurrency exchanges in recent times. In February 2019, crypto brokerage platform Coinmama notified users that it suffered a security breach which affected around 450,000 users’ emails and hashed passwords. The company stated that a few unknown intruders compromised customer data and kept for sale on a dark web registry.

Coinmama provides a cryptocurrency exchange platform for trading digital currency globally. The security professionals at Coinmama revealed the compromised data belonged to the users who registered until August 05, 2017. Coinmama also explained the security issue affected 30 companies and a total of 841 million user records.

Similarly, Cryptopia lost nearly 19,390 ETH tokens in a cyber-attack. According to reports, the hackers have been sending their loot to popular crypto exchanges with Bitbox, Binance, and Huobi seeing the most withdrawal volumes. It is estimated that out of the $16 million stolen by hackers nearly $900,000 have been withdrawn.

Cryptopia stated that the security breach resulted in a significant amount of losses to the firm. The company stayed tight-lipped about the amount of “significant losses” until cybersecurity firm Hacken discovered that there was an unauthorized transfer of ETH tokens.