Home Blog Page 319

Cybersecurity software maker MedCrypt raises $5.3 Million

MedCrypt, a maker of cybersecurity software for medical devices, recently announced that it has raised $5.3 million in a Series A funding round led by Section 32 along with the participation from the existing investors Eniac Ventures and Y Combinator. The San Diego-based company stated the new funds will be used to expand its sales and engineering teams while continuing the development of its software product.

Founded in 2016, MedCrypt offers cybersecurity software for medical devices, making them safe and secure technologically. The company has a team of medical device experts focused on bringing modern cybersecurity features to the healthcare technology.

“Internet-connected medical technology is entering the market at light speed, calling for devices to be secure by design, which leads to a heightened level of patient safety at all times,” Mike Kijewski, CEO and founder of MedCrypt, said in a statement. “We’re thrilled to see continued support from various groups in the industry, from the government to healthcare institutions and device vendors, along with support from our partners to help us further develop our technology and expand our team.”

“Patient data privacy has long been a concern, but the healthcare industry is just beginning to address patient safety risks presented by internet-connected healthcare technology,” Vidya Murthy, VP of operations at MedCrypt, said in a statement. “Research shows a 13.3% higher mortality rate for patients experiencing a cardiac arrest whose care was delayed by four minutes. While cybersecurity attacks to a device such as a pacemaker seem more dangerous, delays to patient care due to cyberattacks are much more real and likely.”

According to a market research report “Medical Device Security Market by Solution (Encryption, Antivirus, Identity & Acess Management), Services (Professional, Managed), Type (Network Security, Endpoint Security), Device Type, End User (Healthcare Provider) – Global Forecast to 2023”published by MarketsandMarkets, the global Medical Device Security Market is projected to reach USD 6.59 Billion by 2023 from 4.36 Billion in 2018, at a CAGR of 8.6%.

Factors such as increasing instances of healthcare cyberattacks and threats, growing geriatric population and the subsequent growth in chronic disease management, government regulations and need for compliance, growing demand for connected devices, and increasing adoption of BYOD and IoT are driving the growth of the Medical Device Security Market.

Global startups receive funding at ICE71 Accelerate Demo Day

Indian startups Seconize and Blue Phish are expanding to Singapore market through Innovation Cybersecurity Ecosystem at BLOCK71 (ICE71), a Singapore-based cybersecurity entrepreneur hub, and have also been in talks with several investors in the city-state. The companies received roughly US$22,000 each and were among 10 startups that got funding through the ICE71 Accelerator program. Other companies hailed from Singapore, Turkey, Vietnam, the UK, and the US.

Seconize, one among the Indian companies has already set up its office in Singapore for expansion in the APAC region and has already been supported by Singapore telecom giant Singtel and National University of Singapore (NUS) Enterprise. The company specializes in mitigating cyber risks through its continuous predictive risk intelligence product.

Chetan Anand, CEO and co-founder of Seconize, at the program highlighted that each cyber attacks cost businesses as much as $4 million while stressing on the fact that Seconize’s proof of concept has been tried out by a large Indian enterprise. The company has also been recognized by the Data Security Council of India.

Blue Phish was the second Indian startup that received funding at the accelerator program. The company provides an online platform of e-learning modules to drive cybersecurity awareness and play a part in reducing the number of cyber attacks that – 95% of the time – are caused due to human error. Founded by Narinder Kaur Bual and Sindhu Nair the company also trains the workforce in cybersecurity awareness.

ICE71 is a collaboration between Singtel Innov8 and NUS Enterprise, the entrepreneurial arm of the National University of Singapore (NUS). Singtel Innov8 chief executive officer Edgar Hardless, said, “Increasingly, enterprises and governments need to work more closely with startups to address the frequency, scale, and sophistication of cyber-threats globally. By bringing together these promising startups and connecting them with leading investors, enterprises and government agencies, we aim to accelerate their growth to the next stage.

“This strengthens Singapore’s cyber-security ecosystem and positions the country as the leading regional cyber-security hub. This also creates a conducive environment for the roll-out of new and innovative technologies which can power Singapore’s Smart Nation goals.”

Earlier, Europe’s intellectual property firm Zacco has acquired Lakhshya Cybersecurity Labs, India-based cybersecurity research and consulting services company for an undisclosed amount. The acquisition is part of Zacco’s plan of expanding its presence in the South Asian market.

“India is today a global hub for advanced digital technology. Lakhshya is adding unique expertise to our current R&D centre in Bengaluru,” said Mats Boström, CEO, Zacco Group. “In the digitalised world, cybercrime and digital threats are unfortunately an increasing challenge for many organisations and individuals. Data, algorithms and all types of digital technology are today significant intellectual property and strategic assets,” said Bostrom.

Psst: Your Cloud Utilization Sucks! Why Automation is Critical to Cloud Optimization

Cloud Security

By Jason Bloomberg, President, Intellyx

Nothing personal, but your cloud utilization sucks. Of course, so does everyone else’s.

Trying to manually select the perfect EC2 instance type (or similar for clouds other than AWS) is impossible.

There are many different permutations to consider. Application demands change based on customer whims, seasons, business cycles, and other external forces – and such change is incessant.

Simply put, manual cloud planning simply doesn’t work in today’s modern, cloud-first environments. It leads to massive over-provisioning. And remember, you don’t pay for what you use in the cloud, you pay for what you provision.

There is a better way, of course – leveraging machine learning to optimize instance type selections in real-time, automatically.

It’s time for your cloud utilization not to suck.

Why Your Cloud Utilization Sucks

Remember the good old days of capacity planning, circa 2002? Figure out the maximum load a server might have and size said server based on the assumption that the peak load could occur at any time.

Good old days for the server vendors and colocation facilities, to be sure. They loved selling you excess capacity your actual utilization would never consume. Easy money for them.

Then along came the cloud and changed everything, right? Now you could provision precisely what you needed. No more low server utilization numbers. Your cloud instances fit your traffic patterns like a thousand-dollar suit.

Only it didn’t work out like that. Sure, AWS and the other cloud providers offer auto-scaling, but which instance type is the right one for your workload?

AWS in all its wisdom now offers millions of potential EC2 configurations – and the other public clouds aren’t far behind. Unless the workload in question is completely well-behaved and predictable (yeah, right), then you have no choice but to pick an instance type based on an assumption of peak load.

You got it. 2002 all over again. Time to get out the DVD of Minority Report.

OK, you might be thinking – picking the right instance type for a particular workload isn’t all that difficult, at least for some of my workloads, right?

Perhaps – but what if you have hundreds or even thousands of workloads you want to run in the cloud. Now which instance types are right for each workload?

But wait, there’s more. What if all those workloads are changing? All of a sudden, picking the right instance type for each workload is a Sisyphean task.

Imagine yourself going into the largest Costco in the world. You are surrounded by huge aisles of goods and you don’t even know where to look for what you need. You probably don’t even know what exists. And even if you did, you couldn’t possibly match your complex 1000 row shopping list with the myriad of different products on the shelves.

Similarly, your cloud optimization is gonna suck no matter how you cut it. There’s no way you’ll pick the right instance type for each workload, considering how many variables you would have to take into account.

And you’re not alone. It’s not like anyone else has a clue how to do it either. Remember, in spite of all the hype, the cloud isn’t pay for what you use. It’s pay for what you provision.

Overprovisioning or provisioning the wrong things just runs up your bill. There’s got to be a better way.

The Double Whammy

In retrospect, it’s obvious that public clouds overpromised but underdelivered utilization-based provisioning. In the early days of the cloud it looked like a huge money-saver, but as any enterprise cloud manager can tell you, the spinning wheel that is your cloud bill just keeps spinning ever faster.

Poor utilization due to selecting oversized instance, however, isn’t the worst of it. Picking the wrong instance type can also adversely impact your performance – which of course, adversely impacts your customer as well.

You may have wanted an expensive suit, but perhaps that instance type is more like a T-shirt that’s two sizes too small. Not only is it uncomfortable, but its unsightly as well.

Remember, instance types vary in many ways: size, speed, and other special characteristics. Make the wrong choice, and you end up with all manner of nasty issues: performance slowdowns, out of memory issues, I/O bottlenecks, and thrashing – as resources move from VM to VM more than they should.

What do all these problems have in common? Poor customer experience. The last thing you want is your CEO knocking on your door, asking why your customers are pissed.

The bottom line: manual utilization planning simply won’t work – and it’ll only get worse as time goes on.

The Hard-Coded ‘Infrastructure as Code’ Trap

If manual utilization planning sucks, then the obvious choice is to automate it. So we select our ‘infrastructure as code’ tool of choice (such as Terraform) and write ourselves a script that selects instance types automatically. Done and done.

Just one problem: how does your script know which instance types to select? If you hardcoded any of the parameters into your recipe, well shame on you. Hardcoded infrastructure as code always leads to operational risks and high cloud costs.

You know what they say: good code never has any numbers in it other than zero and one. The same goes for all the instance type parameters you might like. They should all be abstracted away.

Welcome to next-generation infrastructure as code: an abstracted, declarative representation of infrastructure. Without such an abstraction, infrastructure as code allows for policy-based choices which still don’t provide an adequate control over dynamic environments.

But we have to get that abstraction right. What we really need: an ‘abstraction of the abstraction’ based on business intent. This level of abstraction requires machine learning-driven automation of the declarative representation.

At this level humans control the overall business parameters, and the infrastructure self-configures to meet the needs of the business. Machine learning-based automation is the only way to do this.

To Get It Right, You Need Machine Learning Powered Multi-Dimensional Permutation Analysis

Mouthful to be sure – but the permutations we must analyze are the usual suspects: CPU memory, and I/O parameters, as well as technical and business attributes of each workload.

The fact there are so many such permutations is what makes our analysis multidimensional – and the reason we need machine learning to automate the analysis is because each of these permutations is variable.

Each workload, in fact, has several dimensions of variability. In addition to the permutations listed above, policies and constraints may themselves be variable.

And then there’s the variability across environments. For example, in a hybrid environment, workloads may have certain characteristics when running in an on-premises VMware environment but different characteristics once you move them to a cloud.

There is also variability from one cloud to another, as well as the ever-changing demands of fickle customers. And every cloud’s instance types, pricing models, policies, and APIs are different, so our multidimensional permutation analysis – whack-a-mole to us mere mortals – must take all of those differences into account as well.

Assuming, of course, you want to use more than one cloud. Of course, multicloud is now an increasingly common scenario, given the price differences, bursting and backup options, and simply avoiding the ‘eggs in one basket’ principle that even your CEO will understand.

Optimization as Code – The Only Way to Achieve Full Automation

With all this talk about machine learning-driven abstractions of abstractions, you didn’t think I’d leave you hanging without a way for you to take my advice and make your cloud utilization suck less, did you?

As it happens, Densify – the sponsor of this paper, as luck would have it – offers just such a solution they refer to as optimization-as-code.

Densify’s Cloethe Cloud-Learning Optimization Engineenables your workloads to become self-aware of their resource requirements and to dynamically match their needs to optimal cloud supply.

Yes, self-aware. Not in the sense that Skynet is self-aware (thankfully), but in the sense that Densify enables your infrastructure-as-code code to query Densify for the correct instance type – dynamically, and in real-time.

With Cloe, the information about what each workload needs appears in the form of ‘tags’ in the AWS console. In other words, the application communicates its behavior and requirements via these tags.

Not only that, but said snippet of code is dead simple. See for yourself below.

3

A Snippet of Infrastructure-as-Code Showing off Densify’s Secret Sauce (Source: Densify)

Instead of hard-coding an instance type (shame on you if you’re still doing this), drop in a lookup of the ideal instance type. Slick, eh?

Once you have Cloe set up, you can sit back and let the application perfectly match itself, and take the action, without you having to do anything. Results include better performing application, perfectly matched to the right cloud workloads, at the lowest possible price.

There’s quite a bit of secret sauce going on behind the scenes here. Cloe is actually establishing predictive demand patterns, creating normalized models of cloud supply, optimizing supply and demand – and if that weren’t enough, Cloe even leverages real human experts to tune and manage all the settings.

With Cloe, Densify is blazing the path for how cloud optimization has to work. Go to Cloud Optimization as Code for more details on how it works. After all, manual cloud optimization will always suck.

One final word. Think picking the right instance type & size is hard? What about when we start talking about enterprise deployment of containers at scale? Fuhgeddaboudit. This is the only way to go, folks.

The opinions expressed within this article are the personal opinions of the author. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same. 

“I believe I am here because I did not fear being different”

Carolyn-Crandall

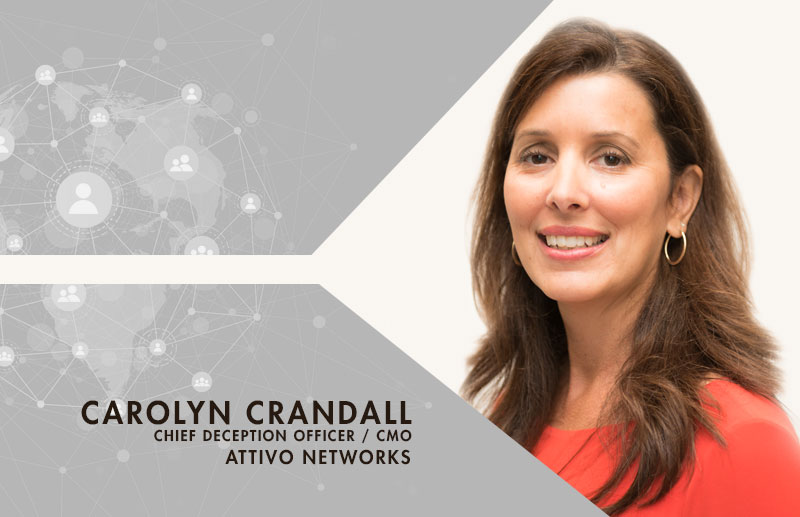
Carolyn Crandall is the Chief Deception Officer and Chief Marketing Officer at Attivo Networks. A technology-marketing executive with over 25 years of experience in building emerging technology markets in security, networking, and storage industries, Carolyn also has a demonstrated track record of successfully taking companies from preIPO through to multibillion-dollar sales, and has previously held leadership positions at Cisco, Juniper Networks, Nimble Storage, Riverbed, and Seagate.

In an exclusive interview, she talks about her journey, current role at Attivo, and how a company can build strategies that connect technology with customers to solve difficult information technology challenges.

You have helmed several leadership roles in several companies. Tell us a bit about your journey from the marketing space to starting Marticulate and then becoming a Chief Deception Officer at Attivo. What was the transition like from core marketing to core technology?

I didn’t originally start out thinking I was going to become a sales or marketing professional. If you have ever played Monopoly, think of the stigma they put on that profession, and as such it really wasn’t top of mind. That said, while I was going to Santa Clara University, studying both electrical engineering and computer science, I took a job as an assistant to the VP of Marketing. This was my first introduction to a high-tech workplace.  I ended up in sales based on a bet that I could outsell any of the sales reps in the office. I think my boss at the time thought it was never going to happen, but upon my achievement, he did honor the bet. My next two positions were exclusively sales and only after that did I become responsible for marketing programs.

My entrée into marketing was when I moved to Australia to set up an international office for my company, and then again when I took on a channel role, which exposed me to all facets of operations—sales, business development, product marketing and marketing demand generation, and communications. Channels is a less known role than traditional sales or marketing, but absolutely a fantastic way to learn multiple disciplines quickly. Throughout my career, I have had the opportunity to wear many hats in marketing, product marketing, channel marketing and sales for top tech brands including Cisco, Juniper, Nimble Storage, Riverbed, Seagate, and others. I started Marticulate as a means to do additional consulting and gain experience in other types of businesses; it also facilitated philanthropic work.

One of the most entertaining projects that I worked on was (early Groupon Days) helping a company start an ecommerce site that connected businesses with consumers. I helped them set up their marketing plans, business model, and launch. A technologist and innovator at heart, I love making markets for startups. I currently play a unique dual role at Attivo Networks serving as Chief Marketing Officer and Chief Deception Officer (think technology evangelist vs. marketing con) since 2014. I have been a leading technical and marketing speaker and educator of deception technology, not only for Attivo Networks, but for the industry at large.

Read More

Data breach affects over 1.5 million Freedom Mobile users

Freedom Mobile, a Canada-based mobile network company, recently suffered a data breach that exposed around 1.5 million of its customers’ personal information. According to the security researchers Noam Rotem and Ran Locar from the security firm vpnMentor, a technical glitch in an Elasticsearch server exposed five million logs that contained Freedom Mobile customers’ data. The researchers stated the server was left online without password protection, allowing anyone to access the data.

Freedom Mobile stated the unprotected server revealed its users’ sensitive information, including customer names, email addresses, phone numbers, postal addresses, dates of birth, customer types, Freedom Mobile account numbers, and credit card information.

The researchers said that it took around one week for them to report the issue to the owner of the server. “After discovering the data breach, we quickly alerted Freedom Mobile to the issue. When they didn’t immediately respond, we asked contacts at another security site help us reach them in case our emails went to spam. As they eventually replied, we know that this isn’t the case,” the researchers said in a statement. For ethical reasons, we didn’t download the database, so we don’t know exactly how many people were affected.

There are multiple data leaks reported due to unprotected ElasticSearch servers. Recently, an unprotected Elasticsearch server exposed more than 24 million financial and banking documents online. According to the security researcher Bob Diachenko, the exposed server contained highly sensitive data of thousands of individuals who took mortgages over the past decade with the U.S. banks and other financial institutions.

Bob Diachenko stated that he identified the unprotected server on January 10, 2019, which contained 24,349,524 credit and mortgages reports in 51 GB size. The server was taken offline and the data was secured on January 15, 2019, after Diachenko reported the incident to the server’s vendor.

The insecure server allowed open access to the documents that contained loan and mortgage agreements, repayment schedules, financial and tax documents, names, addresses, birth dates, social security numbers, and other sensitive information.

Proofpoint spends $120 million to acquire Meta Networks

Acquisitions

The enterprise cybersecurity and compliance company Proofpoint recently publicized about its definitive agreement to acquire Meta Networks, a technology expert in zero trust network access (ZTNA), in a cash deal of around $111 million and $9 million in common stocks and options. The latest agreement, which is expected to close in the second quarter of 2019, help Proofpoint strengthen its cloud-based architecture and people-centric security platform.

Aimed to integrate Meta Networks’ ZTNA technology with Proofpoint’s cloud access security broker (CASB), the acquisition will offer comprehensive cloud access and advance security platform to customers. The acquisition of Meta Networks will also help Proofpoint in expanding its presence in the Israel region.

Founded in 2016 by a group of cybersecurity experts, Meta Networks is a cloud-based startup that provides enterprise network for businesses globally. The company claims that its Network-as-a-Service (Naas) help enterprises connect people, applications, clouds, data centers, and offices to secure them with a software-defined perimeter.

Describing the latest acquisition, Gary Steele, the CEO of Proofpoint stated that, “As cyber-attacks primarily target people, and organizations continue to move their infrastructure to the cloud, the compromise of a single user all too often leads to a full enterprise breach. Limiting employee and contractor access to only authorized resources, rather than the entire corporate network, is a critical control in a people-centric security model. By combining Meta Networks’ innovative zero trust network access technology with our people-centric security capabilities, Proofpoint will make it far simpler for enterprises to precisely control employee and contractor access to on-premises, cloud, and consumer applications. We are thrilled to welcome Meta Networks employees to the Proofpoint team.”

“Protecting people and resources beyond the traditional perimeter is perhaps the most critical security requirement in the cloud era,” said Etay Bogner, Founder and CEO of Meta Networks. “Together with Proofpoint, we will continue to realize a security vision that adapts to the way both threats and infrastructure are moving: to the cloud. Proofpoint is at the forefront of this transformation and we are very excited to become a part of an incredible team.”

In its recent survey, Proofpoint revealed that threat actors are using previously stolen login credentials to launch brute-force attacks on high-profile cloud-based business systems that use multi-factor authentication (MFA). According to the research, hackers are using IMAP-based password spraying attacks to breach Microsoft Office 365 and G Suite accounts which are protected with multi-factor authentication. This technique allows malicious actors to perform credential stuffing attacks to compromise sensitive data.

In its six-month study on major cloud service tenants, the Proofpoint’s Information Protection Research Team stated that they’ve found around one lakh unauthorized logins across millions of monitored cloud user-accounts. The study revealed that around 60% of all Microsoft Office 365 and G Suite tenants have been targeted using IMAP-based password-spraying attacks and approximately 25% of G Suite and Office 365 tenants were experienced a breach.


Three ways cybersecurity generates business value

Global Cybersecurity Outlook 2022,Cybersecurity, CEO, CISO

Contributed by Steve Dickson, CEO of Netwrix

CISOs often struggle to convey the importance of security to executive leadership and justify additional investments for their projects, no matter how important they are. It is difficult to ingrain security principles into the wider business model, even though they are crucial for reducing the risk of incidents, such as costly data breaches.

So how can CISOs drive more attention to their security projects and build stronger communication with the board? For CISOs, this requires comprehending the challenges that the business movers and shakers are most concerned about, building discourse around these challenges, and convincing executives that the IT security team is capable of addressing them in concert with other departments.

By and large, there are three primary challenges that CISOs should keep in mind when talking to board members:

Business challenge #1: Increase revenue and velocity

Your responsibility as CISO is to defend the organization against cyber threats, while the board’s goal is to make the company grow and keep it away from regulatory and legal troubles. Although it is not always evident, these missions are interconnected, and you need to articulate how threat protection actually facilitates business growth. There are several arguments you can use.

First, no organization can grow without customer trust and loyalty, and a healthy security posture is a cornerstone of trust. In light of recent breaches compromising the sensitive data of millions of people, your clients and partners will surely value transparency into how your company uses and protects their sensitive data. By enabling you to do this job well, executives are giving themselves a powerful narrative for earning loyalty from a wide range of stakeholders.

Second, you should explain how you tackle security risks associated with compliance and legal issues that could hinder the organization’s growth.

Finally, you need to discuss how inability to respond promptly to incidents could damage the company’s revenue and reputation. The Netwrix 2018 IT Risks Report revealed that only 17% of organizations have an actionable incident response plan. This statistic is quite disturbing, since there is always the possibility of malicious actions and human errors. Therefore, you should develop a thorough incident response plan and explain to the board whether your organization is prepared to recover from incidents as soon as possible to minimize financial and reputational damage.

Business challenge #2: Build a solid business strategy

A strong business strategy must take into account the risks the organization faces, including the cyber risks. You are the one who should articulate how IT risk management can contribute to the company’s success.

First and foremost, you should conduct regular IT risk assessments to know the risks your organization faces and map them to business outcomes. When presenting the results of the assessment to the board, be ready to show a list of current and finished projects, summarize spending, and detail the return on the company’s investments in these projects (customer satisfaction, reduced costs, etc.).

Then you should highlight any risks that have not been properly addressed and suggest action plans for remediating them. Be sure to identify stakeholders from the board and explain their roles in executing these plans. This approach will likely enable you to gain support for your initiatives from the individuals accountable for risk, as well as nurture risk-based thinking among the leadership.

In the long term, board members will get used to making decisions in the context of the company’s cybersecurity risk exposure, rather than in the context limited by their separate functions. This means that security will no longer be an afterthought for them. Instead, when they develop a new project or product, they will ask for your expertise to ensure that their initiatives won’t pose unnecessary security risks to the company. This mindset is extremely important for having a healthy and risk-resilient business strategy.

Business challenge #3: Save time and cut costs

Being able to demonstrate how your security initiatives can help the business reduce time and slash costs on certain processes is the best way to show your department’s efficiency. It is especially important when you are asking for more budget. To support your argument, I recommend having a metrics-heavy dialogue.

For instance, suppose you plan to implement a solution for data discovery and classification in order to enhance the security of sensitive information. Explain how this solution will not only help the company avoid costly data breaches, but also refine data management processes and make data easily searchable, so employees will be able to perform certain routine tasks X times faster and the company will not have to hire additional employees. On top of that, the VP of marketing will be happy to hear that the investment will help their team purge lost and unengaged leads and focus their efforts on relevant leads, thus optimizing time and money spending across the department.

If you present the value of your current and future projects this way, the chances that you will get the investment you request will be very high. Moreover, you will demonstrate that you are not a geeky amateur, but a leader who knows how to count money and is eager to help the company optimize its budget spending.

By focusing on issues that matter to your board and presenting security as a business enabler, you will get executive buy-in for your initiatives. In the future, this approach will help you extend your influence beyond the server room and enable you to establish a solid security posture that ensures the company operates and grows in a risk-based way.

The opinions expressed within this article are the personal opinions of the author. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.

Cybersecurity firm Onapsis partners with Verizon Communications

Collaboration, partnership, alliance, KnowBe4 and Agari Partner to Prevent Identity-Based Email Attacks

Onapsis, a provider of business application cyber resilience, recently announced that it’s partnered with technology company Verizon Communications. The new alliance helps Onapsis to accelerate and protect SAP customers’ digital transformation initiatives.

Headquartered in Boston, Onapsis provides cybersecurity solutions to enterprises to protect their SAP and Oracle applications, keeping them compliant and safe from insider and outsider threats. The company claims that its security platform is the widely-used SAP-certified cybersecurity solution in the market. Onapsis cybersecurity solutions automate the protection of ERP business-critical applications to protect the vital information and systems. The company claims that its software platform is the most widely-used security solution that protects the ERP systems and business-critical applications.

Verizon Communications, the company that acquired Yahoo, operates wireless network and delivers integrated solutions to businesses worldwide.

Commenting on latest alliance, Mariano Nunez, the CEO and Co-founder of Onapsis said “SAP applications and systems are the heartbeat of our customers’ operations and house their most sensitive and regulated data, including financial records, personal data and intellectual property. Cyber-threats against these systems are increasing, as we saw most recently with the release of the 10KBLAZE exploits. As customers extend the edge of their networks and adopt cloud, IoT and mobility solutions, the security and compliance of SAP systems is growing in importance. We’re pleased to be working with Verizon to ensure our joint customers can benefit from Onapsis’ business application cyber resilience capabilities.”

“This relationship is about delivering the tools and practices required to de-risk the deployment of network-reliant applications. Today’s digital business environment, built on next-generation communications infrastructure, is all about gaining customer experience and operational insight at the edge. For many, SAP is the engine powering their mission-critical, day to day operations and any interruption could have a material impact on product delivery, customer support and revenue,” said George Fischer, President, Verizon Global Enterprise.

Recently, Onapsis made a technology partnership and product integration with security management platform Exabeam to give security teams access to ERP vulnerability logs in their security incident and event management (SIEM) for security monitoring.

The new alliance integrates Onapsis with Exabeam’s Security Management Platform (SMP) that allows security teams to detect and respond to threats by providing them with continuous visibility of ERP vulnerabilities. The association also offers enhanced security solutions including security monitoring, threat detection, incident response, and audit compliance.

Vietnam suffers 4,770 cyber-attacks in Q1 2019

Vietnam

The Ministry of Information and Communications of Vietnam stated that around 4,770 cyber-attacks were reported in the country in the first quarter of 2019. According to the Vietnam Computer Emergency Response Center (VNCERT), this number is more than half the figure for the whole of last year, which was 8,319 cyber-attacks. The center also stated that most of the attacks were reported against e-commerce, financial, and banking systems.

The most common infringements among the attacks were violations of information security policies (40 percent) and unauthorized information collection (39 percent). And, the other data violations included denial of service (8 percent), privilege escalation attacks (7 percent), and the spread and attack of malicious codes (6 percent), VN Express reported.

Nguyen Trong Duong, the director of VNCERT, stated that there were 124 cases related to on-site malicious code attacks, 2,245 interface breaches, and more than 1,000 websites that were attacked by phishing codes.

In January 2019, Vietnam lawmakers approved a new cybersecurity law that controls the Internet content and global tech companies operating in the country. The new cyber law, which came into effect on January 01, 2019, requires Facebook, Google, and other international tech firms to store local users’ data on local servers and set up offices in Vietnam.

The new law prohibits Internet users in Vietnam from spreading anti-government information and posting false information that could cause damage to the country. It also prevents the circulation of content that’s fake, slandering, or inciting violence.

In November 2018, the Vietnam government released a draft declaration on guidelines to implement the law to remediate the shortcomings in Vietnam’s legal corridors and ensure secure cyberspace. The draft recommended social media users to abide by the Constitution and legal regulations while voicing their opinion and discontent.

The Law also addresses the protection of human rights and civil rights, as well as protection of secrets of businesses, individuals and families. It also mandates domestic and foreign telecommunications service providers to keep personal information and accounts of users secured.

Exabeam raises $75 million to accelerate growth

Axis Security Raises US$17 Million Funding, Emerges from Stealth

Cybersecurity startup Exabeam recently secured $75 million in a Series E funding round jointly led by new investor Sapphire Ventures and Lightspeed Venture Partners along with the participation from other existing investors. The San Mateo-based startup stated the new funds will be used for expanding sales reach and accelerate new product lines.

Founded in 2013, Exabeam helps organizations by providing security intelligence and management solutions to strengthen their information security. The company claims that its Security Intelligence Platform leverages big data, machine learning, and analytics to detect and respond to cyber threats. It’s one among the number of security information and event management (SIEM) platforms that analyze companies’ log data sources to flag abnormal activities.

Commenting on the new investment, Nir Polak, the CEO of Exabeam said, “Over the last year, we’ve seen our strategic value increase, and our average deal size has grown by 100 percent from just two years ago. This is because we’re listening to our customers and delivering the innovative technologies they need, including, most recently, the ability to detect threats in the cloud. With the win rates we’re seeing and market opportunity in replacement business, we’re raising money to accelerate our go-to-market and enhance our products to bring additional innovation to modern SOC environments.”

“Having recently backed ground-breaking public companies like Box, DocuSign, MuleSoft, Nutanix and Square, both Lightspeed and Sapphire have an incredible combined track record of spotting up-and-comers that will ultimately dominate their markets. Their collective guidance and support will only further our mission to keep our customers out of the breach headlines and take over the SIEM market along the way,” Polak added.

Recently, Exabeam announced a technology alliance and product integration with Enterprise Resource Planning (ERP) cybersecurity solutions provider Onapsis to give security teams access to ERP vulnerability logs in their security incident and event management (SIEM) for security monitoring.

Headquartered in Boston, Onapsis provides cybersecurity solutions to enterprises to protect their SAP and Oracle applications, keeping them compliant and safe from insider and outsider threats. The company claims that its security platform is the widely-used SAP-certified cybersecurity solution in the market.

The new alliance integrates Onapsis with Exabeam’s Security Management Platform (SMP) that allows security teams to detect and respond to threats by providing them with continuous visibility of ERP vulnerabilities. The association also offers enhanced security solutions including security monitoring, threat detection, incident response, and audit compliance.