
Cybersecurity company FireEye, announced that it is making its private bug bounty program public, with a focus on business applications and corporate infrastructure security. The company stated the bug hunting event is open to all security researchers and ethical hackers who are willing to find vulnerabilities in FireEye’s services and domains including fireeye.com, fireeye.market.com, verodin.com, isightpartners.com, cloudvisory.com, fireeyecloud.com, and mandiant.com.
We provide the public research community the opportunity to engage, report, and receive credit for their work. While engaging with us, we ask that reporters honor responsible disclosure principles and processes and give FireEye an opportunity to evaluate, respond, and if necessary, remediate any confirmed security vulnerabilities prior to public disclosure
– FireEye
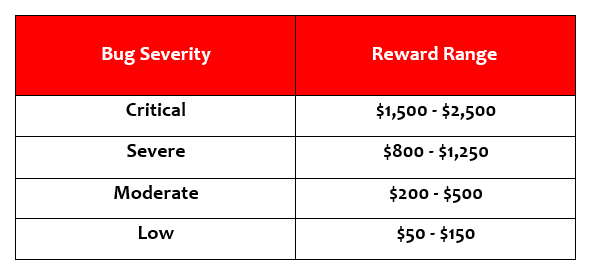
The bug hunting event, which will run via the Bugcrowd platform, will pay a bounty of $50 to $2,500 depending on the severity of the bugs discovered. In addition, FireEye also asked researchers to submit their vulnerability reports to the FireEye Responsible Disclosure program, if they are not willing to be compensated for their bugs discovery.
Bounty Range
“We understand that — despite our best efforts — we cannot eradicate all security vulnerabilities. The technology landscape is constantly expanding, and as such, there will always be emerging threats. While we have been heavily involved with responsible disclosure, including helping other companies set up and modify their own programs, we are taking the next step in this effort,” FireEye added.
Organizations usually conduct bug bounties to find potential vulnerabilities in their network systems or products, which can be fixed before attackers exploit them. The bug bounties offer fiscal rewards to ethical hackers for finding technical flaws, making it a win-win situation for both. The bug hunting programs also ensure that an organization is continually improving its security posture.
Big Rewards for Bug Hunters
Microsoft recently announced its bug bounty program, The Azure Sphere Research Challenge, which offers security researchers up to $100,000 bounty to break into its Azure Sphere Linux IoT OS platform and discover vulnerabilities. The duration of the Azure Sphere Research Challenge is three months (from June 1 to August 31, 2020), and security researchers are required to execute codes on Azure Pluton and Azure Secure World. Earlier, the tech giant paid around $4.4 million to researchers as bug bounties at the Black Hat USA 2019 security event in Las Vegas.

