
The Cybersecurity and Infrastructure Security Agency (CISA) in the U.S. issued security guidelines on how to mitigate cyber risks originating from anonymity networks like Tor. In collaboration with the FBI, CISA released an advisory explaining how attackers use Tor’s network infrastructure.
Tor, also known as the Onion Router, is a software that provides user anonymity by automatically encrypting and rerouting web requests through multiple layers of Tor nodes. Threat actors often use Tor services to hide their identity and IP locations when performing malicious activities.
“The risk of being the target of malicious activity routed through Tor is unique to each organization. An organization should determine its individual risk by assessing the likelihood that a threat actor will target its systems or data and the probability of the threat actor’s success given current mitigations and controls. This assessment should consider legitimate reasons that non-malicious users may prefer to, or need to, use Tor for accessing the network. Organizations should evaluate their mitigation decisions against threats to their organization from advanced persistent threats (APTs), moderately sophisticated attackers, and low-skilled individual hackers, all of whom have leveraged Tor to carry out reconnaissance and attacks in the past,” the advisory said.
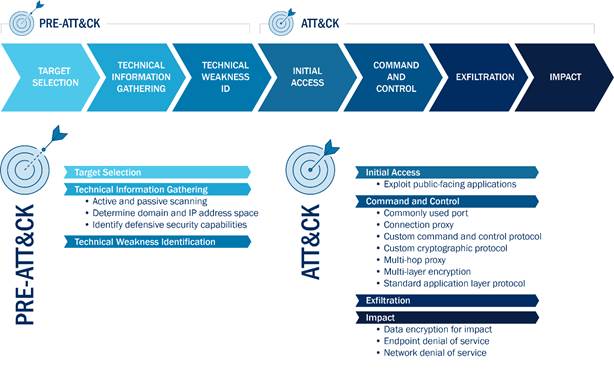
Security Guidelines
CISA recommended certain protective measures for organizations to reduce the risk posed by threat actors who use Tor. These include:
- Block all web traffic to and from public Tor entry and exit nodes. (It does not completely eliminate the threat of malicious actors using Tor for anonymity, as additional Tor network access points, or bridges, are not all listed publicly.)
- Tailor monitoring, analysis, and blocking of web traffic to and from public Tor entry and exit nodes: orgs that do not wish to block legitimate traffic to/from Tor entry/exit nodes should consider adopting practices that allow for network monitoring and traffic analysis for traffic from those nodes, and then consider appropriate blocking. This approach can be resource-intensive but will allow greater flexibility and adaptation of defensive.
- Block all Tor traffic to some resources, allow and monitor for others. This may require continuous re-evaluation as an entity considers its own risk tolerance associated with different applications. The level of effort to implement this approach is high.

