
Opening or downloading malicious links or attachments could result in severe security issues. With employees working remotely across the globe, corporate data security has become a challenge for organizations. A research from security firm NetMotion revealed that cyberthreats soared as remote workers visited risky websites outside of corporate networks. The analysis found that remote employees clicked on 76,440 links that redirected them to malicious websites.
NetMotion highlighted that they collected a sample of network traffic data to find users who accessed blocked URLs or risky content. All these sites were visited on office laptops while working from home via home or public Wi-Fi or a data network.
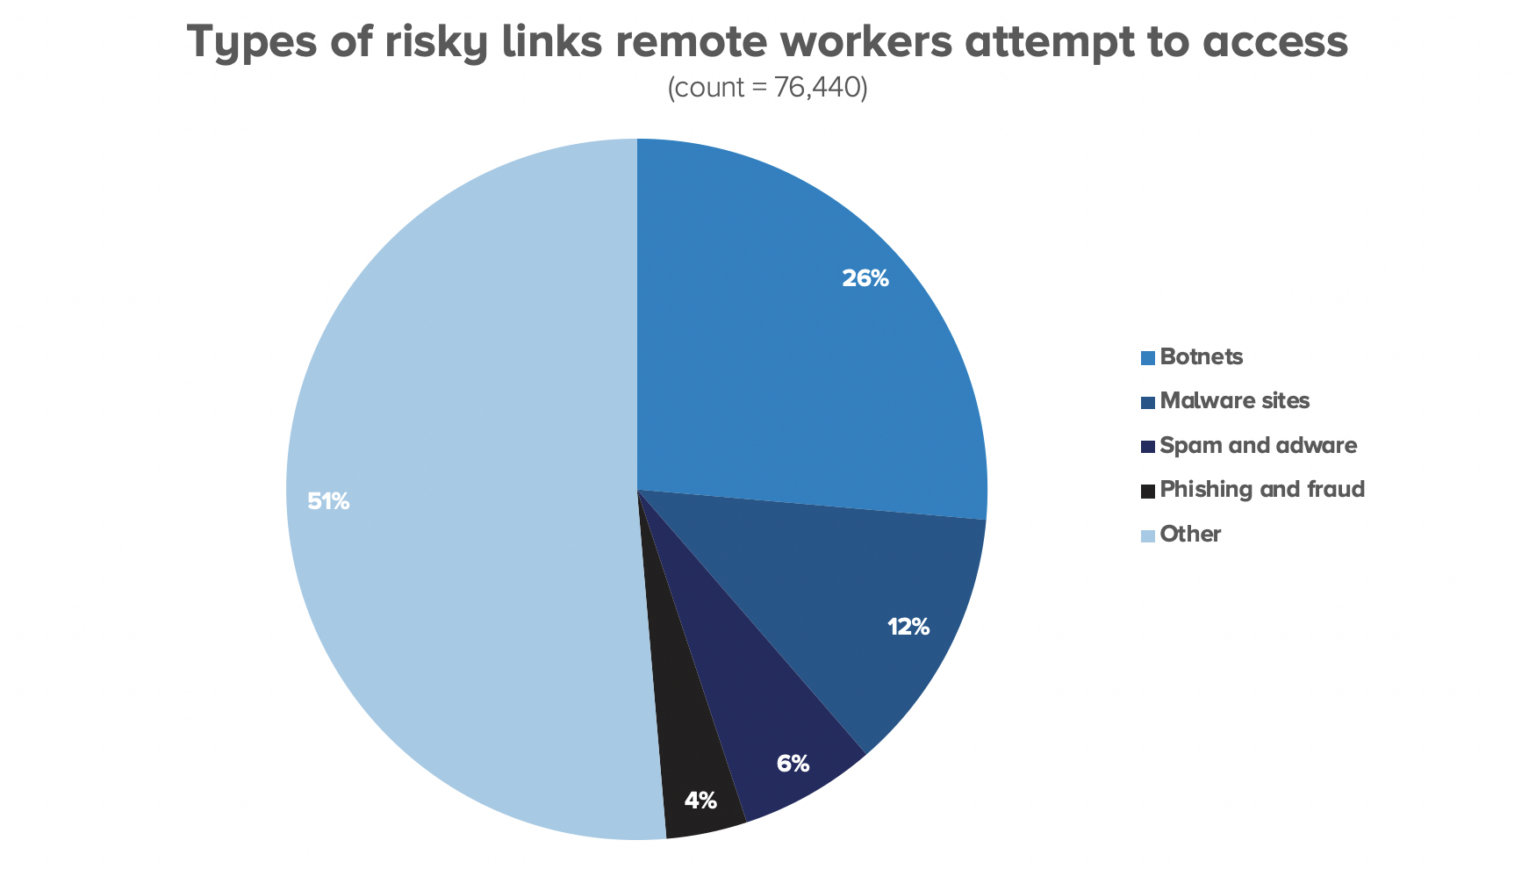
“Several primary risk categories, which were identified using machine learning and based on the reputation scores of over 750 million known domains, include more than 4 billion IP addresses and in excess of 32 billion URLs. The assumption is that a large number of employees connected to protected internal (non-public) networks would have been prevented from accessing this risky content,” the research stated.
Other notable findings include:
- Employees, on average, encounter 8.5 risky URLs per day, or 59 per week.
- Remote workers also access around 31 malware sites per month, and 10 phishing domains, that equates to one malware site every day, and one phishing domain every 3 days.
- The most common types of high-risk URLs encountered, in order of prevalence, were botnets, malware sites, spam and adware, and phishing and fraud sites.
- Over a quarter of the high-risk URLs visited by employees were related to botnets.
- Almost 1 in 5 risky links led to sites containing spam, adware, or malware.
- Phishing and fraud, which garner an outsized proportion of news, account for only 4% of the URLs visited.
- The other category, representing 51% of the data in the chart above, is made up of ‘low-severity’ risky content, such as websites that use proxies, translations and other methods that circumvent URL filtering or monitoring.
“Remote workers are frequently accessing risky content that would normally be blocked by firewalls and other security tools that monitor internal network traffic. Naturally, this poses an enormous threat to the enterprise. Added to this, many organizations have no visibility into the activity taking place on external networks, let alone any means to prevent it. With such a rapid shift to remote work, enterprise security teams have been left flat-footed, unable to adequately protect users in the face of increasingly sophisticated cyberattacks,” the research added.
The NetMotion analysis is based on the aggregated data sourced from anonymized network traffic gathered between May 30, 2020, to June 24, 2020.

