
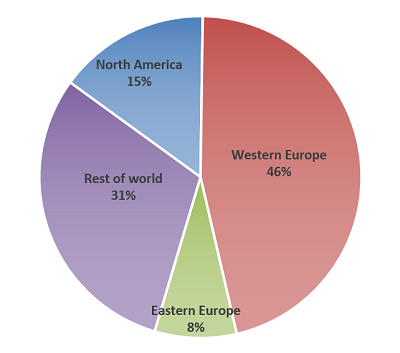
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) and the U.K.’s National Cyber Security Centre (NCSC) are investigating a data-stealing malware dubbed “QSnatch,” which is targeting Network Attached Storage (NAS) devices manufactured by QNAP (Quality Network Appliance Provider). In a joint security advisory, the agencies stated that the number of QNAP NAS devices infected with the QSnatch malware has reached 62,000 across the globe, of which 7,600 were in the U.S. and 3,900 in the U.K.
Once a device is infected with QSnatch malware, it enables hackers to prevent administrators from installing firmware updates by modifying the system’s host file, redirecting core domain names used by the NAS to local out-of-date versions. According to the advisory, all QNAP NAS devices are potentially vulnerable to QSnatch malware if not updated with the latest security updates. While it is unclear how the malware breaks into vulnerable devices, the agencies urged QNAP device users to upgrade to the latest firmware to prevent malware infection.
Locations of QNAP NAS devices infected by QSnatch are:
“The infection vector has not been identified, but QSnatch appears to be injected into the device firmware during the infection stage, with the malicious code subsequently run within the device, compromising it. The attacker then uses a domain generation algorithm (DGA)—to establish a command and control (C2) channel that periodically generates multiple domain names for use in C2 communications,” the advisory said.
QSnatch Malware Properties
The agencies stated that QSnatch malware contains multiple properties like:
- CGI password logger – This installs a fake version of the device admin login page, logging successful authentications and passing them to the legitimate login page
- Credential scraper
- SSH backdoor – This allows the attacker to execute arbitrary code on a device
- Exfiltration
- Webshell functionality for remote access
QSnatch Discovery
CISA and NCSC stated that they first spotted QSnatch malware in two campaigns — one in early 2014 which continued until mid-2017, and in late 2018 that was active till late 2019. “The two campaigns are distinguished by the initial payload used as well as some differences in capabilities. This alert focuses on the second campaign as it is the most recent threat. It is important to note that infrastructure used by the malicious cyber actors in both campaigns is not currently active, but the threat remains to unpatched devices,” the advisory added.
Malware Mitigation
CISA and NCSC recommended organizations to follow certain security measures to protect their devices against malware attacks. These include:
- Organizations need to ensure their devices have not been previously compromised. Organizations that are still running a vulnerable version must run a full factory reset on the device prior to completing the firmware upgrade to ensure the device is not left vulnerable.
- Verify that you purchased QNAP devices from reputable sources.
- If sources are in question, run a full factory reset on the device prior to completing the firmware upgrade.
- Block external connections when the device is intended to be used strictly for internal storage.

