
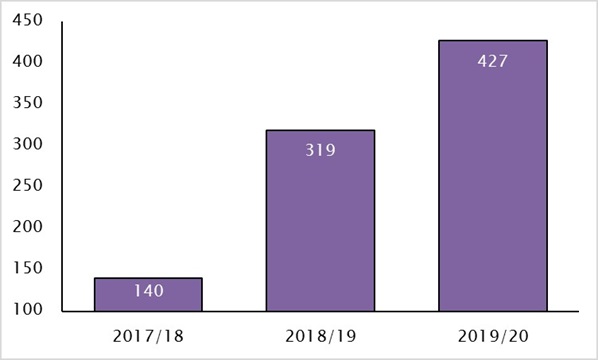
Ever since the GDPR was introduced, disclosure of security incidents via whistle-blower reports has increased significantly. According to a report from RPC, a legal and consultancy services firm, the increased awareness of online frauds and other malicious attacks led people to report organizations for not following required security measures with the customers’ data they hold. The report revealed that the number of whistle-blower reports disclosed to the Information Commissioner’s Office (ICO) about data breach incidents and the misuse of customer information by organizations jumped 34% to 427 in the last year, from 319 the previous year.
Out of the 427 whistle-blower reports, action was taken on 68 reports, including 23 being taken into consideration for investigations by the ICO. In the previous year, 55 whistle-blower reports were considered for investigation. In addition, the ICO issued over £282 million (US$ 370.253) in fines to a major airline and international hotel group, for having put millions of customers’ data at risk.
Whistle-blower reports on data breaches to the ICO
“Whistleblowing is now a major risk for businesses that fail to deal with a data breach properly, or who have failed to take reasonable steps to protect the data they hold on their customers. This makes it more important than ever for businesses who do fall victim to a data breach to respond quickly and to inform the ICO of the data breach if necessary, within the right deadline and ensure customers are informed when they are exposed to a major risk,” said Richard Breavington, Partner at RPC.
“Whilst the ICO has indicated that it is exercising forbearance during coronavirus, businesses would be wrong to think that is a free pass. With millions of employees continuing to work from home, businesses need to have clear practices in place. For example, recommending multi-factor authentication if employees are using their own devices for work and advising employees to update software regularly so it’s at a lower risk of being hacked into,” Breavington added.

 about data breach incidents and the misuse of customer information by organizations has jumped 34% to 427 in the last year, from 319 the previous year.)