
A recent survey from the Financial Services Information Sharing and Analysis Center (FS-ISAC), highlighted that rapidly evolving ransomware attacks have become a primary security concern for most financial organizations. In its latest report, “The Rise and Rise of Ransomware,” the FS-ISAC stated that, “While financial institutions remain resilient to ransomware attacks, they are not immune. Ransomware is a rapidly evolving threat that financial institutions globally and in the APAC region need to be vigilant against.”
The research indicated that ransomware operators have openly claimed successful attacks against eight financial institutions globally in 2020, three of which were banks. It was found that attackers targeted third-party vendors and suppliers used by firms in Asia. The FS-ISAC suggested that even organizations with robust cybersecurity defenses are still vulnerable to ransomware threats, especially through their third-party providers.
Ransomware: A Multi-Business Model
Hackers diversified ransomware attacks by incorporating new revenue streams like:
- Extorting victims by threatening to publicly name them and publish sensitive data online.
- Auctioning off victims’ data to other criminals on the dark web.
- Ransomware-as-a-service, where less technical criminals can buy sophisticated ransomware kits
Top Ransomware Variants
According to the report, the top five ransomware variants in the last 12 months include, Ryuk, Maze, WastedLocker, Troledesh, and Sodinokibi.
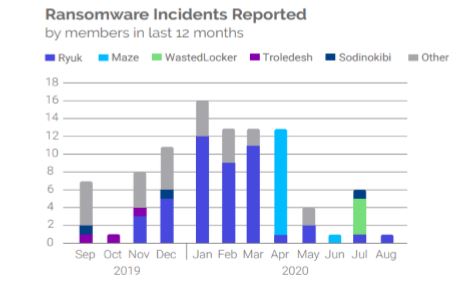
“FS-ISAC members regularly report on phishing campaigns sent to staff, including those which lead to ransomware. Ryuk largely dominated the first quarter’s notifications to FS-ISAC with 9 to 12 campaigns noted per month; however, Maze started in earnest in the second quarter with 12 campaigns observed in April,” the report said.
Preventive Measures:
FS-ISAC also recommended certain practices to help prevent ransomware attacks. These include:
- Regularly educate and train employees to maintain situational awareness and report any potential issues immediately.
- Provide real-world examples and repercussions of successful ransomware exploits.
- Perform regular phishing tests to assess your employees’ knowledge and ability to prevent ransomware attacks.
- Train cyber teams to coordinate a response with other parts of the organization including finance, communications, and the executive team to respond when ransomware hits.
- Ensure your incident response and business continuity plan includes ransomware response protocols.
- Include steps to isolate or power-off affected devices that have not yet been completely corrupted.
- Ensure ways to immediately secure backup data or systems by taking them offline and make sure backups are free of malware.

