Home Blog Page 224

Yellow Messenger Raises $20 Mn Series B Funding for Conversational AI Platform Expansion

Yellow Messenger, a conversational AI platform based on the cognitive engagement cloud technology, announced a $20 million Series B investment taking the total investment to $24 million to date. The funding round was led by Lightspeed Venture Partners and Lightspeed India Partners, who also led the Series A funding in 2019.

One in every three companies globally is implementing conversational AI and chatbots — the pull is irreversible.

– Dev Khare, Partner, Lightspeed India Partners

Yellow Messenger has over 120+ languages for voice and text support in its cognitive engagement cloud and thus, the fresh capital will be used to fuel its international expansion across the U.S., Europe, Latin America, and Asia-Pacific markets. In addition, the company will further invest in its product innovation roadmap, including the deepening of multi-lingual voice bot capabilities, expanding enterprise integrations, and launching a developer marketplace for virtual assistants.

Dev Khare, Partner, Lightspeed India Partners, said, “One in every three companies globally is implementing conversational AI and chatbots — the pull is irreversible. Yellow Messenger has taken advantage of this market pull with its rapid time-to-value, transactional platform and multi-language support for global rollouts.”

The Cognitive Engagement Cloud

Any cognitive system leverages the core skills of our brain — think, read, learn, remember, reason, and pay attention to. The cognitive engagement cloud uses chatbots that deliberate these actions and react by interacting through text and voice mediums across channels in a natural human-like manner. It enables enterprises to automate and orchestrate workflows for customer and employee engagement with minimal human intervention.

The chatbots can be integrated and used across multiple communication channels like Microsoft Teams, Slack, WhatsApp, telephony, digital assistants and with the enterprise’s existing System of Record and System of Engagement. By acting as a single source of intelligence across all channels, and across customer and employee conversations, this platform ensures smart, consistent and coherent customer and employee experience.

On similar lines, the Yellow Messenger platform is successfully powering around 30 million monthly conversations on chatbots, across more than 100 customers around the globe. Owing to this and the ongoing COVID-19 pandemic emergency in India, the company has also been appointed by the National Health Authority of India (NHAI) to provide chatbots to several state governments (Madhya Pradesh, Punjab, and Rajasthan), which will assist with citizen engagement over WhatsApp and Facebook Messenger. It has also deployed special chatbots for enterprises to deal with employee engagement, customer engagement, and ITSM automation, helping them drive business continuity.

Kenya Reports 37.1 Mn Cyberattacks in Q4 of 2019: Report

Kenya Reports 37.1 Mn Cyberattacks in Q4 of 2019: Report

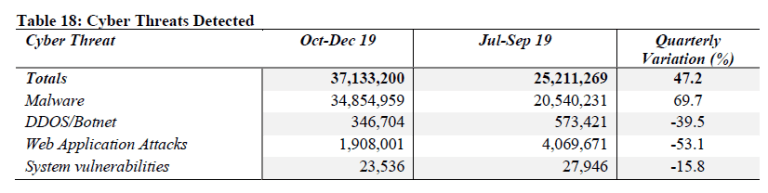
Cybersecurity analysts in Kenya discovered a total of 37.1 million cyberattacks in the Q4 of 2019, which is a 47.2% increase when compared to 25.2 million cyberthreats detected in Q3 of the same year.

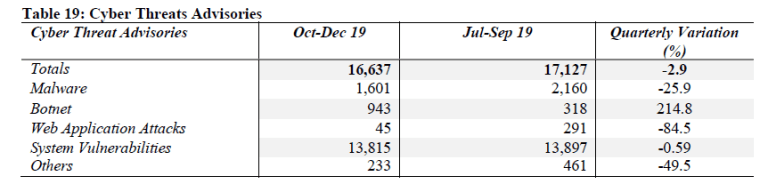
According to recent analysis by the Communications Authority of Kenya (CA), and derived from figures provided by the National Kenya Computer Incident Response Team (KE-CIRT/CC), researchers discovered a growing number of malware, web application attacks, system misconfiguration, and online abuse. The CA’s cyber experts team issued 16,637 cyber threat advisories to the affected, a 2.9% increase from the 17,127 alerts in Q3 of 2019. It is said that Kenyan businesses suffered billions of Shillings and a huge number of sensitive information to hackers every year.

Image Source: National KE-CIRT/CC

The KE-CIRT also stated that Kenya ranked amongst the top 10 countries in the continent with the highest number of people exposed to cyberattacks. The increase in cybercrimes led Kenyan organizations to invest more in cybersecurity products and services to prevent cyber risks.

Image Source: National KE-CIRT/CC

“Emerging telecommunication challenges such as cybersecurity incidents are likely to increase and evolve at a similar rate and therefore, the relevant government institutions and stakeholders will need to continuously review and where necessary, revise the existing national laws, policies and regulations in order to address these challenges, while enhancing innovation,” the report stated.

 CBK’s New Cybersecurity Guidelines

In order to fight against banking frauds and to get a better view of the new threats that payment service providers are facing, the Central Bank of Kenya (CBK) had proposed new guidelines for cybersecurity standards. According to the newly proposed guidelines, banks and mobile payment operators are required to file cybersecurity reports with the industry regulator. The firms are asked to notify the Central Bank of Kenya within 24 hours of any suspicious activity and submit a quarterly report with CBK on the incidents experienced and how they were resolved.

USAF Rewards Ethical Hackers $290,000 for Resolving 460 Vulnerabilities

bounty for DarkSide Ransomware Group, Microsoft Offers $100,000 Bounty

The U.S. Department of Defense (DoD) recently concluded the fourth edition of its venerated bug bounty program, “Hack the Air Force 4.0.”, which was intended to discover and disclose vulnerabilities within the Air Force Virtual Data Center. The four-week-long event, ran from October 23 to November 20, 2019, was jointly created by the DoD, the Defense Digital Service, and vulnerability disclosure company HackerOne. Around 60 ethical hackers reported over 460 vulnerabilities and earned more than $290,000 in the bounty challenge.

The bounty program also featured a specific asset from the U.K. Ministry of Defense, and gave hackers a chance to collaborate with peers and military personnel to discover vulnerabilities in the Virtual Data Center.

HackerOne has performed multiple hacking events with the U.S. government authorities. Earlier, HackerOne jointly ran a bug bounty program dubbed “Hack the Marine Corps”, a challenge focused on the Corps’ public-facing websites and services, with the DoD at the annual Black Hat and DEF CON conferences. The nine-hour program paid out $80,000 in prizes to the researchers for discovering 75 unique vulnerabilities. The researchers were also allowed to report flaws they discovered through the HackerOne-managed Marine Corps vulnerability disclosure program.

In a related development, the DoD, in 2018, launched the Hack the Pentagon hacker-powered security program to address security issues faced by the government bodies. The ethical hackers of the security program successfully resolved over 12,000 vulnerabilities.

Malicious Fleeceware Apps Affect 3.5 Mn iPhone Users

Apple App Store, Apple vulnerabilities

The researchers from SophosLabs revealed that fleeceware app developers are operating on Apple’s App Store for iPhones and iPads. They claimed that more than 3.5 million iPhone users have been impacted by the malicious fleeceware apps on their devices. The researchers observed 30 such apps in Apple’s official App Store, which are intended to make financial frauds.

What is Fleeceware?

“Fleeceware” is a term introduced by researchers at SophosLabs in September 2019. It has been named fleeceware due to its defining characteristic of overcharging users for functionality that is widely available in free or low-cost apps.

It is said that these app developers are taking advantage of Apple’s free trial period by charging an excessive amount from users when they don’t cancel the subscription. Usually, these apps charge subscription charges between $30 per month or $9 per week after a 3 to 7-day trial period. It is also suspected that these apps bought fake five-star reviews to boost their ranking on the App Store and used pay-per-install services to boost install counts to attract users.

According to the researchers, most of the fleeceware apps are image editors, horoscope/fortune telling/palm readers, QR code scanners, and face filter apps. “Many of these apps lack any extraordinary features that aren’t already present in many other apps, including truly free apps,” the researchers said in a blog post.

They also highlighted that some app developers intentionally didn’t cancel an app’s trial period when a user uninstalled the app. An excessive amount of service continuation charges ($360 or $468 per year) were debited from the users’ saved cards for basic functionality in the apps. It is also believed that these malicious apps are gaining popularity by advertising with various social media platforms like Facebook, Instagram, TikTok, and others. Sophos also published a complete list of the malicious fleeceware apps.

Not the First Time

Earlier, Sophos discovered a set of 25 fleeceware apps on Google Play Store having more than 600 million installs. Some of these apps have close to 100 million installs, which can rival even the legitimate apps on the Google Play Store.

Phishing Kits Become “Bestseller” in the Underground Market: Research

Phishing, phishing attacks

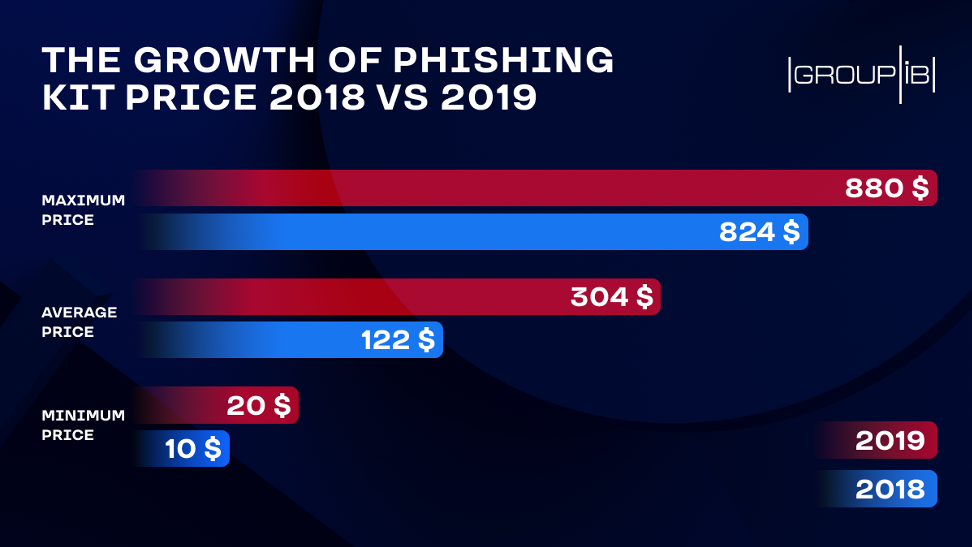
Researchers at Group-IB, a Singapore-based cybersecurity company, have found out that amid the rising concerns of restructuring and reuse of previously known malware families, phishing kits have become a popular choice for spreading them. Phishing kits have now gained the “Bestseller” tag in the underground market, with the number of ads and their sellers having doubled in 2019 as compared to2018. The growing demand for phishing kits is also reflected in its price that skyrocketed last year by 149% and exceeded $300 per item.

What’s in it for the Attacker and the Defender?

Phishing kits represent archive files with a set of scripts that ensure the work of a phishing website. This toolset enables attackers with modest programming skills to execute small to high volume malicious campaigns. This interests the attention of cybersecurity researchers. The detection of a phishing kit not only helps to discover hundreds or even thousands of phishing pages but also serves as a starting point of a cyber forensic investigation to identify and track down the operators and eventually the creators of the phishing kit.

We must seek to prevent the further spread of ‘disease’ and fight not against its symptoms – phishing pages, but against its causative agent – phishing kit makers.

– Dmitry Volkov

(Group-IB CTO and Head of Threat Hunting Intelligence team)

To collect data, phishing kits normally have a designated email address, to which the illegally exfiltrated data is sent. The number of unique email addresses detected in 2019 has seen an 8% growth over the previous year. The increased number of unique email addresses in phishing kits is another notable trend that suggests phishing kits’ expansion in the underground market and the rising number of their operators.

Other Findings related to Phishing Kits

Group-IB’s Threat Hunting Intelligence team has done extensive research of various underground forums and have found that:

  • Over 16,200unique phishing kits were detected in 2019.
  • Only 113,460 out of 7 million phishing pages detected contained a phishing kit, pointing out that hackers have now grown more cautious in their malicious activities.
  • The number of phishing kit sellers active on underground forums has increased by over 120%in 2019 Y-O-Y.
  • Relatively an equivalent growth percentage (%) has been seen in the number of online phishing kit ads posted on the dark web.
  • Amazon, Google, Instagram, Office 365, and PayPal were the most found brands in the 2019 phishing kits.
  • Top 3 “online markets” for trafficking in phishing kits last year were Exploit, OGUsers, and Crimenetwork.
  • In 2019, the average price of a phishing kit more than doubled compared to the year before and totaled $304, with the prices generally ranging between $20and $880.
  • In comparison, the prices for a phishing kit varied between $10and $824, while the average price stood at $122 in 2018.
Phishing kit statistic
Image Source: Group-IB

The researchers said the most remarkable gesture though was that some of the phishing kits were offered for free. This isn’t human generosity, but a possibility of backdoors hidden in these freebies, which would enable their creators unrestricted future access to all the exfiltrated data.

Group-IB CTO and Head of Threat Hunting Intelligence team Dmitry Volkov, said, “Phishing kit creators are the driving force of this criminal marketplace – one individual might be behind the creation of hundreds of phishing pages and, even worse, behind the compromise of the personal information of thousands of people. Therefore, the fight against phishing kit creators should be at the core of the struggle to eradicate phishing. In its practice, our team had several investigations that resulted in the deanonymization of phishing kit creators. By sharing such info with relevant law enforcers and ensuring the apprehension of cybercrooks, we seek to prevent the further spread of ‘disease’ and fight not against its symptoms – phishing pages, but against its causative agent – phishing kit makers.”

Equifax Settles Indiana Lawsuit Over Data Breach for $19.5 Mn

Equifax Settles Indiana Lawsuit Over Data Breach for $19.5 Mn

Atlanta-based consumer credit reporting agency Equifax has agreed to pay the State of Indiana $19.5 million to settle a class-action lawsuit, brought forward by the State’s Attorney General Curtis Hill.  The lawsuit concerns the 2017 data breach that leaked a massive amount of data of more than 147 million Americans, including 3.9 million Indiana residents. The lawsuit claimed that Equifax failed to protect its residents’ social security numbers and other private information. As per the settlement, Equifax is also required to correct Indiana’s security deficiencies and safeguard consumer information in the future.

Indiana and Massachusetts are the two states that did not participate in a multistate settlement in July 2019 that announced up to a $700 million settlement with the U.S. Federal Trade Commission, Consumer Financial Protection Bureau, and 50 states and territories.

Overview of the Data Breach

In September 2017, Equifax disclosed that its databases were hacked between May and June 2017, and attackers gained access to the company’s data that compromised sensitive information for 147 million American consumers, including social security numbers, credit card numbers, and driver’s license numbers. Equifax discovered the breach on July 29, 2017, but waited until after the close of trading nearly six weeks later to disclose the breach to its consumers and investors, after hackers exfiltrated data for 76 days.

A Series of Lawsuits

Equifax recently settled similar claims with the U.S. Federal Trade Commission. As per the settlement, Equifax will pay $380.5 million as a penalty from where the class action members can withdraw up to $20,000 as compensation. Additionally, the company may also require spending $125 million for out-of-pocket claims. Class action members will also receive 10 years of free credit monitoring services from Equifax.

Also, earlier, in September 2018, Equifax was charged with a fine of £500,000 (US$660,000) by the Information Commissioner Office (ICO) for failing to protect the personal and financial data of customers.  The ICO, which carried out the investigation, stated that the U.S. Department of Homeland Security warned Equifax about the vulnerabilities in its systems, in 2017. However, Equifax failed to take proper steps to fix the vulnerabilities.

Australian Cyber Security Centre Issues Guidelines for Home Workers

Remote Security Policy, Remote Work Jeopardizes Corporate Network Security: Report

Amid the COVID-19 pandemic, more employees in Australia are opting for self-isolation and choosing to work from home. But there are concerns about these users falling victims to phishing attacks. To protect users, the Australian Cyber Security Centre (ACSC) issued a new advisory containing tips to reduce the risks of phishing attacks and protect users from cyberattacks.

ACSC Head, Abigail Bradshaw CSC, said the dramatic increase in people working from home – many of them for the first time, and the increasing use of online systems to manage social distancing – creates opportunities for cybercriminals.

“The social distancing measures that help protect the community against COVID-19 can also make them more vulnerable to malicious cybercriminals,” said Bradshaw. “The unauthorized compromise of information can have a devastating impact on a person’s emotional, financial and working life.”

The ACSC’s new guidance outlines nine important but simple cybersecurity practices for people who are working from home to limit risks:

  • Beware of scams
  • Use strong unique passphrases
  • Implement multi-factor authentication
  • Update your software and operating systems
  • Use a virtual private network (VPN)
  • Use trusted Wi-Fi
  • Secure your devices when not in use
  • Avoid portable storage devices
  • Use trusted sources of information

The advice is part of the ACSC’s campaign to raise awareness of cyber threats and how to mitigate them during the COVID-19 pandemic.

Earlier this month, the government of Australia launched a cyber offence against offshore cybercriminals. In an official statement, Minister for Defense Linda Reynolds stated that the Australian Signals Directorate (ASD) has mobilized its offensive cyber capabilities to disrupt the cybercriminals behind the spate of Coronavirus-related attacks and malicious activities.

It’s said that cyber experts from ASD are tracking down state and foreign hackers who are targeting Australian households and businesses through devious scams and malicious websites.


Connected Cars From Ford and Volkswagen Have Security Flaws: Report

Connected Cars From Ford and Volkswagen Have Security Flaws: Report

Connected cars manufactured by Ford and Volkswagen have major security flaws which could put owners’ privacy and safety at risk, a new research found. An investigation from consumer group Which? exposed vulnerabilities in connected technology like media and computer systems in Ford Titanium Automatic 1.0L petrol and a Volkswagen Polo SEL TSI Manual 1.0L petrol car models.

Which? Magazine stated that it found vulnerabilities in a section of the car that can enable or disable traction control, a feature that helps drivers to control the vehicle, and in the infotainment unit that holds owner’s personal data, such as people’s phone contacts or location history. It also claimed that it was able to hack the infotainment system in the Volkswagen Polo.

The investigation also revealed that by lifting the Volkswagen badge on the front of the car gave them access to the front radar module. This could potentially allow an attacker to tamper with the collision-warning system, posing a safety risk. Which? warned that the security flaws expose the cars to malicious hackers who could steal data or send misleading information to the vehicle’s management system.

Lisa Barber, Editor of Which? Magazine, said, “Most cars now contain powerful computer systems, yet a glaring lack of regulation of these systems means they could be left wide open to attack by hackers – putting drivers’ safety and personal data at risk. The government should be working to ensure that appropriate security is built into the design of cars and put an end to a deeply flawed system of manufacturers marking their own homework on tech security.”

Connected Cars are Vulnerable to Attacks

A similar study by Consumer Watchdog, a non-profit organization, revealed that all advanced cars with internet connections to their safety-critical systems are apparently vulnerable to fleet-wide hacks. The survey report, “Kill Switch: Why Connected Cars Can Be Killing Machines And How To Turn Them Off”, revealed that automakers have disclosed the high risk of such hacks to their investors, but are keeping the public in the dark as they market new features based on internet connections.

According to the report, the infotainment system is connected to the internet through a cellular connection, and also to the vehicle’s CAN (Controller Area Network) buses. This outdated 1980s era technology links the vehicle’s most critical systems, such as the engine and the brakes. Experts agree that connecting safety-critical components to the internet through a complex information and entertainment device is a security flaw. This design allows hackers to control a vehicle’s operations and take it over from across the internet.

Security Tools to Identify Flaws in Connected Cars

Earlier, Cisco released an open-source hardware tool dubbed “4CAN” to find security vulnerabilities in connected cars. The newly launched security tool will allow automobile security researchers and car manufacturers to identify potential flaws in sensors and control systems in modern cars, to ensure vehicle security. Cisco stated that vulnerabilities in the control systems might cause serious threats in the cars, which allows attackers to get control of the vehicle’s system.

Apple Is Hackers’ Favorite for Brand Phishing Attacks

Apple Is Hackers’ Favorite for Brand Phishing Attacks, REvil gang threatens Apple blueprint leak

Apple was the most frequently used brand in phishing attacks during the first quarter of 2020, according to Check Point’s research. The research report “Brand Phishing Report” revealed that nearly 10% of all brand phishing attempts in 2020 so far were misusing the Apple brand.

The report stated that Apple is the primary target for cybercriminals to exploit its brand recognition, which soared from seventh place in Q4 of 2019 to the top this year in rankings. The report highlights various brands which were frequently imitated by hackers in their cyber activities to steal a victim’s sensitive information. According to the report, Netflix took the second position after Apple with 9% of all phishing attempts related to the company. The Chase Bank brand rose by 3% from Q4 2019 to the sixth position, with 5% of phishing attempts.

What is a Brand Phishing Attack?

In brand phishing attacks, attackers imitate the official website of a popular brand by creating a similar domain name or URL of the original site. The links to the fraudulent website will be sent to targeted individuals via email or SMS. Once a user clicks the link, it redirects to the fake website which often contains a form intended to steal users’ credentials, payment details or sensitive information.

Check Point stated that technology, banking, and media are the most targeted sectors in brand phishing attacks. The company also listed the top ten brands targeted in phishing attacks in Q1 2020, which include:

  1. Apple (with 10% of brand phishing attempts globally)
  2. Netflix (9%)
  3. Yahoo (6%)
  4. WhatsApp (6%)
  5. PayPal (5%)
  6. Chase (5%)
  7. Facebook (3%)
  8. Microsoft (3%)
  9. eBay (3%)
  10. Amazon (1%)

The research indicated that web phishing was reported as the most common attack vector with 59% of attempts in Q1 of 2020. While mobile phishing was second, with 23% of attempts and email phishing came in third with 18% of attempts.

Maya Horowitz, Director, Threat Intelligence & Research, Products at Check Point, said, “Cybercriminals continue to exploit users by adopting highly sophisticated phishing attempts via emails, web and mobile applications purporting to be from well-recognized brands which they know will be in high demand at the moment, whether that’s a high profile product launch or just generally tapping into behavioral changes we’ve seen during the Coronavirus pandemic. Phishing will continue to be a growing threat in the coming months, especially as criminals continue to exploit the fears and needs of people using essential services from their homes. As always, we encourage users to be vigilant and cautious when divulging personal data.”

How a Red Team Engagement Can Improve Your Security Preparedness

Red Teaming Blue Team Red Team

You may have a very mature security program for your organization with comprehensive technical and administrative security controls.  You have stopped a variety of dangerous events in the past 12 months and you can see things are going well overall. But there’s always room for improvement. The threats we can’t see and can’t plan for are still lurking. But you can check the maturity and strength of your security posture by conducting a Red Team engagement.

Contributed by Dick Wilkinson, IT Security Officer, New Mexico Judicial Information Division

Red Team engagements are a series of simulated attempts to breach your security perimeter. The concept can include physical attempts to enter secure spaces, social engineering on the phone and in person, technical attacks against your computer network or even a spear-phishing attempt at senior board and executive members. The team of people executing these attacks will be given some amount of limited knowledge about your organization and some clear boundaries on acceptable behavior.

Some considerations when planning a Red Team engagement:

  • No breaking windows to gain entry or physically damaging computer equipment to disrupt the network.
  • Capture the boundaries in your contract’s statement of work. The hope is to create a realistic dress rehearsal of attacks your organization may face.
  • Understanding your business market, the security practices of industry peers and the threats that face your industry as a whole are crucial to creating a realistic set of scenarios your security plan can defend against.
  • The previous experience of the red team will likely determine what techniques they find most useful.
  • Be open to suggestions from the team and listen to how they have helped previous clients.

This event can be a learning experience for your organization, even during the planning stages, before any offensive actions have taken place.

The Blue Team defends

The alternative to the red team engagement is the blue team. This is your team of network defenders, and they are probably already doing the job of protecting your network daily. These employees are crucial to help you define what the outcome of this special event should be. They should have the best insight to understand what the weakest parts of your security plan may be.

What a Blue team offers:

  • Advice from this group could range from very technical input to general anecdotes about previous security incidents.
  • The historical knowledge these employees have should be built into your requirements for your red team actors. That knowledge may not define the entire plan but it will give you very clear starting points.
  • The everyday network defenders will be your blue team during the engagement as well.

Some considerations for the Blue team engagement:

  • To maintain some realism to the penetration events, keep this team out of the meetings where you go over the plan with the red team.
  • You will want the defenders to use their real-world tools and sensors and execute real responses to the red team’s offensive actions.
  • They need to have some element of surprise to act the way they would in real scenarios.
  • Details to share with the blue team should be the rules of the engagement, what is and is not allowed; the start and end date of the event; the way to call a stop to the exercise if a real-world incident begins to impact business operations.
  • The blue team does need to be informed but they should not know the script the red team may follow.

Planning a Red Team Engagement

Several factors may lead to the decision to hold a red team engagement. Your industry regulations may require some type of adversarial event to prove your security plan is well designed. Your leadership may have heard about another organization’s event and wants to try it at your company.

A red team event could be self-directed because you and the IT staff know it is time to really push the limit and prove that your ideas work. Understanding why you need to do the red team will determine what you should expect to learn from the engagement. From the beginning of planning the event, the IT staff needs to create clear objectives to cover that help you learn the most about your gaps in the security plan.

Create a list of known threats and what controls you have in place to protect against those threats; refer to your risk registry to get you started. When you discuss the need and desired learning outcomes with the team that will engage in the penetration attempts, be very clear with your expectations.

Some red team events are conducted by internal audit teams, some by third-party security vendors; this can change the expected outcomes and that should be identified early in the planning process.

Some important items to consider in the plan could include:

  • Will there be a physical perimeter breach attempt?
  • Will we allow social engineering?
  • Could there be a punitive response from HR if an employee violates company policy during the test?
  • How much detail do you share with your executives and board if they are considered “in-scope” targets of the test?
  • How will you call an emergency stop to the event and how will that be communicated to all participants, vendors and company employees?
  • What laws may dictate how we execute the event? Physical security vendors have been arrested during scripted penetration events.

Most important of all, what are we going to do when we hear bad news? As the IT leader in this engagement you will feel responsible for the outcomes of this event. This is your plan, your defenses, and your security team; a failing grade may be hard to face. Talk openly before anything ever starts about where you think you might fail. Be clear with senior leadership that this event may lead to some outcomes that cost time and money to remediate.

In the course of one or two weeks you will learn more about the effectiveness of your program than you could in one or two years of regular operations having only minor incidents. The impact that this engagement can have on moving your security posture to a new level can’t be understated.

Create the narrative that this was not a failure but an accelerator to your next level of maturity. When you speak in those terms to your leadership and employees, they will take the deficiencies found by the red team as a plan to grow from, and not a report card that says you failed.

This article has been adapted for online reading. Read the complete article in the March issue of CISO MAG here.


About the Author
Dick WilkinsonDick Wilkinson is the Chief Information Security Officer on staff with the Supreme Court of New Mexico. He is a recently retired Army Warrant Officer with 20 years of experience in the intelligence and cybersecurity field. He has led diverse technical missions ranging from satellite operations, combat field digital forensics, enterprise cybersecurity as well as cyber research for the Secretary of Defense.

Disclaimer

CISO MAG did not evaluate/test the products mentioned in this article, nor does it endorse any of the claims made by the writer. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same. CISO MAG does not guarantee the satisfactory performance of the products mentioned in this article.