Home Blog Page 246

Philippines DICT Admits Using P300 Million for Cybersecurity and Surveillance

Following a memo from state auditors alleging the use of confidential funds that led to the agency’s underperformance, the Department of Information and Communications Technology (DICT) of Philippines admitted to using P300 million (nearly US$6,000,000) on sensitive matters including surveillance and cybersecurity, which the department deemed legitimate and necessary.

“Under existing laws, rules, and regulations, the Confidential Expense item is for lawful monitoring and surveillance of systems and networks to support the DICT’s functions, which include cybersecurity, the formulation and effective implementation of the National Cybersecurity Plan, and international cooperation on intelligence on cybersecurity matters,” DICT said in a statement.

It also stated that the amount was disbursed in three tranches and was liquidated with the Commission of Audit (COA). The DICT also added that the COA did not disallow the disbursements, and the recommendations made by COA was merely a procedure the department is adhered to follow to keep up with the timeframes of disbursement. However, a series of reports from Rappler suggests COA has contradicted statements from DICT stating that DICT underspent for projects from the budget as the funds allotted for the agency were used up as confidential funds.

“The information systems in our country [need] continuous monitoring so that both domestic and foreign cyber threats and cyberattacks can be identified, addressed, and promptly neutralized to protect the safety and security of our nation. These cybersecurity threat monitoring activities have a direct impact on national security,” DICT said. “As a member of the National Security Council, the DICT is mandated to protect the nation’s critical infrastructure, its government networks both civilian and military, its small-medium enterprises to large businesses, the corporations and its supply chains, and every Filipino citizen using the internet.”

After the memo was released by the auditors, DICT Undersecretary Eliseo Rio Jr. also resigned from his post citing that he was excluded from planning for the use of the confidential funds. “My position is that the DICT does not need intel or confidential funds because it is not [within] its mandate to conduct intel or surveillance activities. But the position of Secretary Honasan is that this is needed by him,” Rio told GMA News Online.
Japan Confirms Defense Data Breach After Cyberattack on Mitsubishi Electric

Japan restricts foreign equipment and tech, Japan Embraces AI Tools to Fight Cyberattacks with US$237 mn Investment

The Japan Ministry of Defense recently announced that defense-related sensitive data may have been breached after the cyberattack on Mitsubishi Electric Corp., a major supplier of the country’s defense and infrastructure systems. According to the Ministry, information related to bidding for contracts on defense equipment research, including evaluation criteria and required performances may have leaked in the incident. It’s claimed that Mitsubishi converted the government’s paper documents into PDF files and kept them on its internal network, even though it was not permitted to do so.

The Ministry stated that it’s still investigating the potential data breach to find out whether it will have an impact on national security. Initially, Mitsubishi Electric denied the possibility of a data breach of defense and infrastructure information when it first reported a cyberattack in January 2020. However, after further investigation, the Tokyo-based firm confirmed that the defense ministry’s data was included in the breach. It’s said that Mitsubishi discovered the cyberattack in 2019, but did not disclose it to the public for more than half a year.

Breach Overview

Mitsubishi Electric released a notice on January 20, 2020, detailing the cyberattack that occurred in June 2019. According to the source, a Chinese hacking group tracked as “Tick” was likely behind the attack. It’s said that Tick was active for a long time and is known for stealing sensitive data from the defense, aerospace, chemical, and satellite industries in Japan and China.

The unauthorized access began with compromising computer systems in Mitsubishi’s office located in China and spread to Japan. The attackers used the compromised accounts to infiltrate into the company’s internal network and gained access to server systems that had sensitive information. It’s believed that intruders managed to access computers, servers, and company sites.

Other Cyberattacks that Targeted Japan’s Defense Secrets

On January 31, 2020, NEC Corp., a Japanese IT and electronics company, accepted a data breach and stated that its network was penetrated and compromised to a cyberattack that occurred in December 2016. The attack was spotted in June 2017, following which all unauthorized communications detected were blocked by the IT teams. The encrypted communication information between the compromised server and the external exfiltration server was finally decrypted in July 2018 and it was found that the defense business division’s 27,445 files were accessed illegally.

Recently, Pasco Corp. and Kobe Steel, rendering services to the Japanese armed forces, disclosed a possible data breach that occurred in June 2015, followed by a second attempt in August 2016.

Pasco Corp. is an aerial image surveillance provider and has tie-ups with the Japanese Ministry of Defense for delivering latest satellite images to monitor the work and progress at various defense bases and other locations. As far as Kobe Steel is concerned, it manufactures underwater launch tubes for Japanese submarines and provides critical submarine spare-parts for the Japan Self-Defense Forces (SDF). Therefore, an attempt of intrusion or data breach by threat actors in both cases is thought to be targeted directly at acquiring defense secrets of the country.

U.S. Indicts Four Chinese Hackers Over 2017 Equifax Data Breach

Surveillance Legislation (Identify and Disrupt) Amendment Bill

The U.S. Department of Justice pressed charges against four Chinese nationals for hacking the Atlanta-based credit reporting agency Equifax in 2017. The four hackers, identified as Liu Lei, Wang Qian, Wu Zhiyong, and Xu Ke, are believed to be members of the People Liberation Army (PLA) of China.

The grand jury in Atlanta released a nine-count indictment against PLA operatives with wire fraud, economic espionage, conspiracy to commit computer fraud, and other offenses. Speaking at a press conference, U.S. General Attorney William Barr said the four hackers stole not only data of U.S. citizens, but also Equifax’s proprietary data. “For years we have witnessed China’s voracious appetite for the personal data of Americans. This data has economic value, and these thefts can feed China’s development of artificial intelligence tools as well as the creation of intelligence targeting packages,” Barr added.

Breach Overview

On September 7, 2017, Equifax disclosed that its databases were breached between May and June 2017, and hackers gained access to company data that potentially compromised sensitive information for 143 million American consumers, including Social Security numbers, credit card numbers, and driver’s license numbers.  Equifax discovered the breach on July 29, 2017. It waited until after the close of trading nearly six weeks later to disclose the breach to consumers and Equifax’s investors, after hackers exfiltrated data for 76 days.

Penalties Against Equifax

In 2018, Equifax was fined for £500,000 (US$660,000) by the Information Commissioner Office (ICO) for failing to protect the personal and financial data of 15 million customers in the 2017 data breach. The ICO, which carried out the investigation, stated that Equifax was warned about vulnerabilities in its systems by the U.S. Department of Homeland Security in March 2017. However, Equifax failed to take proper steps to fix the vulnerabilities. Later in July 2019, the Federal Trade Commission (FTC) and Consumer Financial Protection Bureau fined Equifax for US$ 650 million.

Recently, in January 2020, Equifax agreed to pay US$380.5 million to settle a class-action lawsuit, brought forward by the FTC. As per the settlement, Equifax will pay US$380.5 million as a penalty from where the class action members can withdraw up to US$20,000 as compensation. Additionally, the company may also require to spend US$125 million for out-of-pocket claims. Class action members will also receive 10 years of free credit monitoring services from Equifax.

Shadow IoT Devices Majorly Concern Enterprise Networks: Infoblox Research

Number of IoT Devices Expected to Reach 24.1 Bn in 2030: Report

As modern enterprises incorporate more BYODs (Bring Your Own Devices), shadow IoT devices will become an ever-growing risk factor to enterprise network security, suggested a new research from Infoblox, a provider of cloud-managed network services. The study stressed that enterprise networks pose potential cyberthreats by shadow IoT devices.

The report, “What’s Lurking in the Shadows 2020” surveyed 2,650 security professionals across the U.S., U.K., Germany, Spain, the Netherlands, and UAE to know the role of shadow IoT devices in enterprise networks. Infoblox claimed that its research will help gain a better understanding of the challenges faced by security leaders in managing shadow IoT devices across their networks.

What are Shadow IoT Devices?

Shadow IoT devices are internet connected devices or sensors used inside an organization without the knowledge of the IT team in a company. A shadow IoT device can be any smart device like personal laptops, smartphones, fitness trackers, and smart home gadgets.

According to research findings, 80 percent of IT professionals discovered shadow IoT devices connected to their company’s network. Nine in ten security leaders (89 percent) were worried about shadow IoT devices connected to remote or branch locations of their businesses. The research also revealed that 78 percent of global organizations found more than 1,000 personal devices like laptops, smartwatches, and mobile phones connected to their corporate network.

Organizations in the U.S. (46 percent), Spain (35 percent), and the U.K. (33 percent) believe that there are more than 1,000 non-business related IoT devices connected to their enterprise networks at a time. While 27 percent of organizations in the Netherlands see between 2,001 and 5,000 of shadow IoT devices and 29 percent of firms in the UAE claim to see between 1,000 and 2,000 such devices, according to research.

Malcom Murphy, technical director, EMEA at Infoblox, said, “As workforces evolve to include more remote locations and branch offices, and enterprises continue to go through digital transformations, organizations need to focus on protecting their cloud-hosted services the same way they do at their main offices. If not, enterprise IT teams will be left in the dark and will not have visibility over what’s lurking on their networks. With limited security in most IoT devices, organizations will continue to be a target for cybercriminals looking for a way to easily exploit the network. Ignoring these precautions will only leave them defenseless against evolving threats and can have a critical impact on their business network.”

Cybersecurity Awareness by Infoblox

Recently, Infoblox announced that it is hosting a cybersecurity roadshow in five cities across the Middle East and Africa (MEA). The roadshow, which goes by the theme “Take Network Security to the Next Level”, will commence on February 24, 2020, in Amman, Jordan and head to Johannesburg, and conclude on March 11, 2020, in Kuwait. The company will help regional organizations understand how to improve incident response capabilities at the upcoming roadshow.

Cybersecurity Decides on the Stability of Societies: Study

Top Cybersecurity Jobs in 2021

Testing, inspection, and certification services provider TUV Rheinland released its seventh annual report on Cybersecurity Trends for 2020. The report discusses several key cybersecurity trends such as attacks on smart supply chains, medical equipment and exploitation in real-time operating systems (RTOS).

The report also catalogued seven cybersecurity trends for 2020, which are gathered from leaders in the cybersecurity industry. These include:

Uncontrolled Access to Personal Data: The report points out the lack of transparency in securing and processing data that can be used to gain an accurate picture of an individual’s interests and behavior.

Unsecured Smart Consumer Devices: Proliferation of smart devices has led cybersecurity experts to protect one billion servers and PCs. With the new wave of smart devices, the attack surface could increase manifold to hundreds or thousands of times.

Increased Risk with IoMT Equipment: Proliferation of “Internet of Medical Things” (IoMT) has also opened a huge window of cyber vulnerabilities. Researchers have identified a growing number of software vulnerabilities and demonstrated the feasibility of attacks on IoMT devices such as insulin pumps, heart and glucose monitors, defibrillators and pacemakers. However, the complex task of maintaining and repairing IoMT equipment is also badly organized, inadequate or completely absent.

Cyberattacks on Vehicles and Transport Infrastructure: The development of software and technology has led to increased connectivity of autonomous vehicles however, cyberattacks targeting transport infrastructure could affect not only the safety of individual road users, but could also lead to widespread disruption of traffic and urban safety.

Hacking of Smart Supply Chains: Supply chains are also prone to disruptions in processes, and cyberattacks can manipulate information about deposits and financial information as it leverages Internet of Things (IoT) automation, robotics and big data management and also represents virtual warehousing.

Threats to Shipping:  The maritime industry is in a dire need of modern cybersecurity approach, as port logistics, ship navigation systems, and ship computer networks are vulnerable to cyberattacks.

Vulnerabilities in Real-time Operating Systems: The rising use of IoT (Internet of Things) is a growing concern as it potentially endangers real-time operating systems to cyberattacks, and installing the latest security updates will not always be an effective strategy.

“From our point of view, it is particularly serious that cybercrime is increasingly affecting our personal security and the stability of society as a whole,” explained Petr Lahner, Business Executive Vice President for the business stream Industry Service & Cybersecurity at TUV Rheinland in a release. “One of the reasons for this is that digital systems are finding their way into more and more areas of our daily lives. Digitalization offers many advantages – but it is important that these systems and thus the people are safe from attacks.”


Maastricht University Pays 30 Bitcoins as Ransom to TA505 Group

Maastricht University

Maastricht University (UM), in a press release, revealed that it has paid a ransom of 30 bitcoins for unlocking the servers and systems compromised during a  large-scale ransomware attack in December 2019.

Here’s What Happened

On December 24, 2019, Maastricht University woke up to the news of a huge ransomware attack that took down almost all the Windows systems on the University’s campus and particularly affected its email services. In order to contain the damages and complete the ransomware attack analysis, Maastricht University itself initiated a complete system and network blackout on the campus.

The University then appointed a digital security firm Fox-IT for their expertise and assistance in carrying out further investigation into the ransomware attack. At the time, the type of ransomware attack or its operator was not disclosed, but in a press conference held last week, the University revealed that Fox-IT found signatures of the hacker group TA505 in the files encrypted during the attack.

Maastricht University’s Ransomware Attack Timeline

A management summary of the Fox-IT report and Maastricht University’s response found that during the time frame of October 15 to 23 December 2019 (inclusive of both dates), the TA505 gained control over multiple servers. Following is the timeline of the events in the leadup to the final ransomware attack:

October 15 and 16, 2019: Attackers from the TA505 group gained access to University computers by means of two phishing emails opened on the mentioned dates.

November 21, 2019: TA505 then used a server with missing security updates to obtain complete access rights into the University’s network infrastructure.

December 23, 2019: After gaining extensive access and privilege rights over the network architecture of Maastricht University, TA505 finally deployed the “Clop Ransomware” on the 267 Windows servers marked as important by the group.

The report summary further gives detailed information that part of the technical infrastructure including 1,647 Linux and Windows servers, and 7,307 workstations were affected during the attack.

Maastricht University Pays the Ransom

After careful assessment and analysis of the Fox-IT’s cyber forensic team, an investigation report was submitted to the Maastricht University’s top management. The top management considered all the possibilities on offer and finally agreed to pay the ransom demanded by the TA505 group. According to Reuters, the University eventually paid a total of 30 bitcoins amounting to US$220,000 (€200,000) for unlocking the systems and servers compromised during the ransomware attack.

The Maastricht University spokesperson said, “It is a decision that was not taken lightly by the Executive Board. But it was also a decision that had to be made. We felt, in consultation with our management and our supervisory bodies, that we could not make any other responsible choice when considering the interests of our students and staff.

The fact that on January 6 and thereafter, we were able to have teaching and exams take place, more or less as planned, that UM researchers suffered little or no irreparable damage, and that we were also able to make the salary payments for 4,500 employees on time, strengthens our confidence that we made the right choice.”

Unit 42 Discovers Malicious Activity in Kuwaiti Organization’s Webpage

Compromised Email Accounts

Security experts from Unit 42, a threat intelligence unit of Palo Alto Networks, recently discovered a Kuwait organization’s webpage used in a security exploit. The researchers stated that the webpage contained a hidden image which was observed between June and December 2019.

According to the researchers, attackers compromised and injected a malicious HTML code into the website to obtain credentials like account names and password hashes from the website’s visitors. It’s believed that the attackers aimed to crack these hashes to get the visitors’ passwords or use the hashes to carry out relay attacks. Access to user account credentials allows the attackers to launch remote access trojan (RAT) attacks.

The researchers stated, “If successful in harvesting account credentials, the compromised data has a plethora of uses for the attackers and can allow them to breach an organization to steal sensitive information. Furthermore, because they’d be using trusted credentials, it can allow attackers to go undetected for long periods of time, enabling them to infiltrate other parts of an organization and even implement backdoors, like RATs, to get back into a system even after being removed. This can result in significant damage to an organization over a prolonged period of time.”

Unit 42 believes that the threat actor group “xHunt” is likely to be behind the malicious activity. Previously, xHunt hacking group targeted transportation and shipping organizations based in Kuwait between May and June 2019, in which the hackers installed a backdoor tool named “Hisoka”. Several custom tools were later downloaded to the system in order to carry out post-exploitation activities.

xHunt’s Hacking History

Earlier, in its research report, IBM revealed that “ZeroCleare” malware was a creation of two hacking groups—xHunt and APT34. It said that the malware was developed by Iranian state-sponsored hackers and used in cyberattacks against energy companies in the Middle East. It also added that the hackers launched brute-force attacks to gain access to weakly secured network systems. Once attackers infect the target device, they spread the malware across the company’s network as the last step of infection.

Mailto Ransomware Hits Toll Group, Deliveries Across Australia Affected

Toll Australia, ransomware

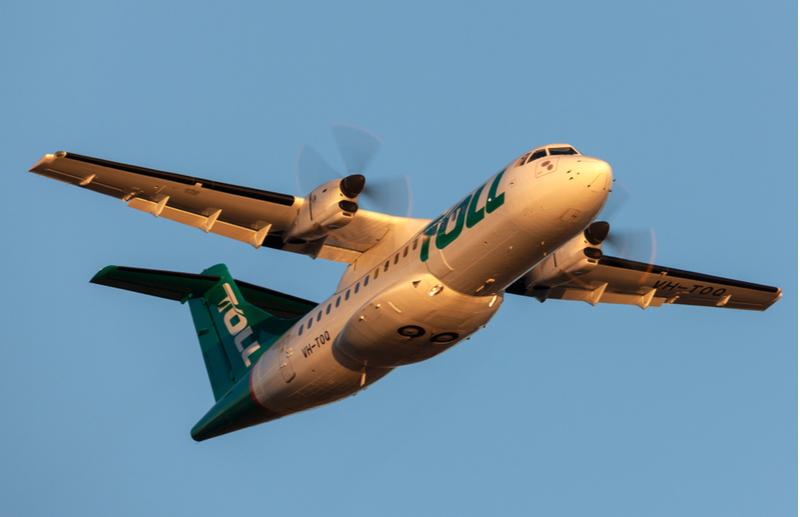
Toll Group, Australia’s logistics giant, was targeted by a cybersecurity incident that compromised around 1,000 systems affecting local and global deliveries across the country. As per the findings of the experts from the Australian Cyber Security Center (ACSC), the logistics company’s computer and network infrastructure was hit by the Mailto ransomware attack.

The report of Toll Group being affected by ransomware first surfaced when the company issued a press release on its website and Twitter handle, officially informing its users about the incident.

How Mailto Ransomware Affected Toll Group Australia

On January 31, post the attack discovery, Toll promptly shut down several systems across multiple sites and business units in Australia to contain the spread of the cyberattack. According to a report in iTnews, more than 1,000 servers (computers) were affected by the large scale Mailto ransomware attack. Thus, the incident resulted in Toll reverting to manual processes for clearing the backlog of undelivered local and international parcels across Australia. It continued to function its regular pickup, process and dispatch services but at a slow pace due to manual processing.

Giving updates on the current situation, Toll said, “There continues to be no indication that any personal data has been lost as a result of the ransomware attack on our IT systems. We continue to monitor this as we work through a detailed investigation. Based on a combination of automated and manual processes instituted in place of the affected IT systems, freight volumes are returning to usual levels. We have also increased staffing at our contact centers to assist with customer service.”

Toll also involved experts from various cybersecurity organizations, including the ACSC, for analyzing the impact and reach of the Mailto ransomware attack. These findings were further shared with other law enforcement departments and cybersecurity organizations to prevent future damages from a similar variant of Mailto ransomware.

Steps to Defend Against a Ransomware Attack: Australian Government

With a view to the increased number of Mailto and other forms of ransomware attacks targeted towards businesses in Australia, the government agency has released the following precautionary measures:

  • Keep your anti-virus software and other security tools installed on the systems updated for detection and prevention of the spread of Mailto ransomware.
  • Patch the servers regularly to restrict the lateral movement of ransomware attacks within a network and limit the number of hosts impacted post successful infection.
  • Maintain offline backups (eg. cloud backup) of critical data which allows faster recovery in case of a ransomware attack.
  • Apply content filters on email inboxes to prevent malicious content from reaching users and thus reducing the chance of a possible compromise.
  • Use network segmentation to partition the larger networks into smaller sections for segregating communications between specific hosts and services.
  • Draft an incidence response plan for quick response in the event of a ransomware attack.
  • Educate your employees and users to improve cybersecurity awareness and make them cyber ready.

83 percent of Cybersecurity Personnel Feel Overworked: Tripwire Survey

active directory
active directory

Cybersecurity firm Tripwire recently announced the results of its survey that examined how organizations and security pros are experiencing skills gap issues. The survey findings, based on the responses from 342 security professionals, revealed that 83 percent of respondents feel more overworked going into 2020 than they were in 2019. It’s said that 82 percent of security pros felt that their teams were understaffed.

According to the research, 85 percent of them acknowledged that it became more difficult over the past few years to hire skilled cybersecurity professionals. It’s said that only 19 percent of cybersecurity companies provide resources for managing the stress associated with the specific issues of security.  

Other Major Findings

  • Most companies (85 percent) believe managed services are a good option for addressing security skills gaps
  • Around 46 percent stated that they plan to use more managed services in 2020
  • Over 50 percent of respondents said they will invest more in cybersecurity training for its staff
  • The survey also highlighted that 40 percent of security pros believe their CISOs are not involved enough in day-to-day operations

Tim Erlin, the Vice President of product management and strategy at Tripwire, said, “It’s getting harder and harder for organizations to fill open positions on their security teams. Larger organizations, which you might assume have more resources, are experiencing the skills gap issue even more acutely than smaller organizations. It’s a challenge to hire the right skill sets – they keep changing along with security, which is always evolving. Nearly all of those we surveyed said the skills required to be a great security professional have changed over the past few years.”

“CISOs should be focusing on high-level strategy, but because their teams are understaffed and have an overwhelming volume of work on their desks, they may have to get involved in daily operations, if they haven’t already. To solve the problems caused by skills gap issues, training and managed services are both good approaches. By partnering with providers, organizations can free themselves from operational work and gain insights that will help inform decisions. And because recruiting and training isn’t always possible, managed services provide businesses a way to augment their teams,” Erlin added.

OurMine Group Hacks Facebook’s Official Twitter and Instagram Accounts

blockchain-based social media, Parental Consent for Minors, Iranian Facebook accounts

The social media accounts of social networking and technology giant Facebook were temporarily compromised by a hacking group named OurMine. The incident came to light after the hacking group posted on Facebook’s official Twitter and Instagram accounts, However,  it restored the social media accounts immediately after the news exposed it.

“Some of our corporate social accounts were briefly hacked but we have secured and restored access,” Facebook said in a media statement.

OurMine hacking group claimed that they attacked Facebook to expose potential vulnerabilities in the system. The group posted a statement on Facebook’s official Twitter account stating, “Hi, we are OurMine. Well, even Facebook is hackable but at least their security is better than Twitter.”

Twitter confirmed that the intrusion occurred through a third-party. The microblogging site stated, “As soon as we were made aware of the issue, we locked the compromised accounts and are working closely with our partners at Facebook to restore them.”

OurMine’s High-Profile Targets

Based out in Dubai, OurMine is an infamous cybercriminal group that attacked multiple social media accounts of high-profile individuals and enterprises in the past.

Recently, OurMine hacked 15 Twitter accounts of the U.S. National Football League (NFL) teams including NFL’s handle and posted a message, “Hi, we’re back. We are here to show people that everything is hackable.”

The details of the account hijacking remained unclear, however, most of the tweets posted by the OurMine operators on the hijacked accounts came from Khoros. It is a web-based third-party application used by the organization’s digital marketing and public relations departments to manage their social media accounts and gain useful insights into public engagements across different platforms.

In 2017, OurMine operators hacked Twitter handles of Futbol Club Barcelona and Real Madrid Club de Futbol. The hackers sent out tweets from Real Madrid Club de Futbol’s Twitter account in English and Spanish, which announced the joining of major rival player Lionel Messi. They also posted video footage from an earlier match, which showed Messi scoring for Barcelona against Real Madrid. The tweets were visible for almost 90 minutes on the football club’s handle but were later removed. The welcoming post of Messi had grabbed the attention of the fans by then, as the tweet received almost 2,800 likes and 3,100 retweets.