Home Blog Page 146

Why Insider Threat Presents a Big Risk to Financial Services Organizations

Insider Threats

In today’s highly regulated environment, financial services organizations are trusted with far more than just money; they are also responsible for keeping customers’ highly sensitive personal and financial data secure. And privacy legislation, such as GDPR and CCPA, has come into force to ensure that they are doing this diligently. Likewise, with all the publicity we’ve seen around data breaches, as individuals, we are far more aware of the growing value of our data and the need to protect it. So, unfortunately, are cybercriminals, which means financial organizations are prime targets for malicious cyberattacks. However, this isn’t the only threat they face. Not a day passes without these firms’ employees putting data at risk. The Insider threat is cited as having the potential to cause a lot of damage

By Adam Strange, Global Marketing Director, HelpSystems-Boldon James

When it comes to reducing overall breach risk, it is easy to assume that employees represent low-hanging fruit – based on the premise that it is easier to control the actions of a company’s employees than it is to defend against external attackers.

The Insider Threat is real

However, here at HelpSystems, we have recently undertaken some research, interviewing 250 CISOs and CIOs in financial institutions about the cybersecurity challenges they face. And the reality is that insider threat – whether intentional or accidental – was cited by more than a third (35%) of survey respondents as one of the threats with the potential to cause the most damage in the next 12 months. Likewise, phishing emails were cited by 20% of survey respondents. Add these two together and you can start to get a picture of the challenge these internal employee-centric risks present for financial services firms – perhaps a far bigger one than the external threat. While external attackers are always motivated by malicious intent, the employee population is far more mixed, and motivations are a grey area where the reasons behind breaches, whether through simple human error or deliberate actions, are harder to determine. This makes understanding and mitigating insider risk a far more problematic exercise.

Misdirected emails are also a big risk

 At the same time, the latest Information Commissioner Office (ICO) report has just been published and the data confirms that misdirected email remains one of the U.K.’s most prominent causes of security incidents. This report further demonstrates the need for all organizations to control the dissemination of their classified data as it states that misdirected email is, alarmingly, a 44% bigger risk to organizations than phishing attacks.

This is yet another area where organizations must ensure their data protection policies are robust enough to not only protect themselves but also their employees from the seemingly simplest of mistakes. Again, our research showed that increased remote working practices were a cause for concern, with 36% stating that they saw it as a cybersecurity threat with the potential to cause significant damage. Therefore, what remains paramount is that organizations provide their employees with the technology tools necessary to prevent the simple human errors that have the potential to result in data loss, and as a consequence, severe financial and reputational damage.

Understanding what protection your data requires

Financial services organizations must shift the dial on insider risk and reduce breach frequency because the penalties for failing to do so are becoming increasingly draconian, and the repercussions from customers much more severe. But put simply, before you can defend, you need to know what protection your data requires and you need to know what you’ve got, where it’s stored, why you have it, and who has access to it. Once you’ve got to grips with that, you can identify what is of true value to the organization – what’s business-critical and what’s sensitive – and then how best to treat it. To do that you need to think about what the impact would be if a piece of information was leaked or lost. If it was made public, would it harm the business, your customers, partners, or suppliers? Would it put an individual’s security or privacy at risk? Would you lose an advantage if a competitor got hold of it? Is it subject to any privacy or data laws, or regulatory compliance?

While this all sounds relatively straightforward, data visibility was another problematic area and subsequent threat emphasized in our research. Data visibility and knowing what data is where and who has access to it was highlighted as having the potential to cause the most damage by 14% of our survey respondents. Combine this with internal cybersecurity fatigue, which more than a quarter (28%) cited as potentially damaging, and you can start to appreciate the importance of providing tools and awareness training to help prevent those easily avoided mistakes from happening in the first place.

Employees need tools, training, education, and the right culture 

As I mentioned, it is a complex problem without a simple answer, and this is where employee education is the key.  Employees play a vital role in ensuring the organization maintains a strong data privacy posture. For this to be effective, organizations need to ensure that they provide regular security awareness training to protect sensitive information. In terms of how they go about doing this, they must invest in user training and education programs. Users are your most important security resource, so train them to be an asset rather than a liability. Users should be a critical part of an organization’s security posture, not excluded due to the associated risks.  

Likewise, the security culture of the firm must be inclusive towards employees, making sure they are continually trained so that their approach to security becomes part of their everyday working practice and security is embedded into all their actions and the ethos of the business.

All these best practices will keep the insider threat in check.

How data classification can help

One way to do this is through the implementation of data classification tools, which not only help organizations to protect their data by putting the appropriate security labels on it but also help educate users to understand how to treat different types of data with different levels of classification and sensitivity. Here at HelpSystems, our data classification solution enables users to classify both their emails and documents according to their sensitivity, using both visual and metadata labels. Once labeled, data can be controlled to ensure that emails, documents, and files are only sent to those you want to receive them, protecting your sensitive information from accidental loss.

It is a technology like this that leaders within financial services organizations should have in place to protect their employees, prevent misdirected emails, the inadvertent sharing of documents and files, and ensure that the organization is complying with data protection legislation. Remote working is likely to remain, regardless of any future regional or national lockdowns, therefore, making sure that employees have the tools to prevent mistakes and the accidental sharing of data is going to be more important now than it has ever been. The place to start is making sure that data is appropriately labeled so that the employee knows how it should be handled. And this is another best practice to keep the insider threat in check.

About the Author
Adam Strange, Why Insider Threat Presents a Big Risk to Financial Services OrganizationsAdam heads up the global marketing function at Boldon James, working to define and implement our strategic go-to-market campaigns. He brings a proven and successful record of managing integrated business-to-business marketing activity to both increase brand profile and capture leads and opportunities. Adam has a widespread understanding of enterprise IT infrastructure across areas such as Cybersecurity, Threat Intelligence, Cloud-based Services, Business Applications, Databases, and Hardware. Prior to Boldon James, Adam ran the marketing and alliances function at Becrypt, and has held former marketing and partnering positions at BAE Systems, Oracle, and Computacenter.

Disclaimer

Views expressed in this article are personal. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.

Details of 27.7 Mn Texas Drivers Exposed Due to Human Error

data integrity, website, security

Vertafore, a provider of insurance software, recently disclosed that an unknown threat actor group illicitly accessed personal information of 27.7 million Texas-based drivers who use Vertafore’s services. In its release, Vertafore admitted that the data breach was caused due to a human error after three data files were inadvertently stored in an unsecured storage unit.

The exposed information included drivers’ information like license numbers, names, dates of birth, addresses, and vehicle registration histories. However, Vertafore clarified that no social security numbers or financial information was compromised in the incident. While information about the attackers is still unknown, the company stated that there was no sign of data misuse.

“Immediately upon becoming aware of the issue, Vertafore secured the potentially affected files and has been investigating the event and the extent to which data may have been impacted. Vertafore has reported the matter to the Texas Attorney General, Texas Department of Public Safety, Texas Department of Motor Vehicles, and the U.S. federal law enforcement. Vertafore is actively assisting law enforcement,” the release said.

Vertafore also urged its users to monitor their account statements. The company is offering free credit monitoring and identity restoration services to the users whose data was affected in the incident.

Misconfigurations Increase Data Breaches

Inadvertent database exposure continues to be a major risk for organizations, with misconfigurations exploited in 66% of reported attacks. Besides, 33% of organizations reported that attackers gained access through stolen cloud provider account credentials.  A quarter of organizations stated that managing access to cloud accounts is a primary concern to them. Nearly 96% of respondents admitted that they face issues with their current level of cloud security, while 44% of respondents reported data breaches are the top security concern. For full story click here…

63% of U.S. Employees Reuse Work Passwords: Report

reusing passwords

According to a recent survey by Visual Objects, 63% of employees in the U.S. have reused their passwords on work accounts and devices. Older employees follow more reliable password protection practices than younger workers with only 2% of baby boomers always using the same passwords for work accounts, compared to 13% of millennials who always recycle work passwords. It was also found that millennial workers are 6.5 times more likely to reuse work passwords than baby boomers.

The survey highlighted that cyberattacks will remain a major concern in remote work conditions until employees’ behavior aligns with companies’ security protocols. “Millennials tend to trust that large services have their best interests in mind and that security is built-in. They are the first generation that had easy access to global information,” said Brad Bussie, vice president of Entisys360’s Advyz Cyber Risk Services.

Personal Work on Office Devices

Using work devices for personal use can only make corporate data more vulnerable to attacks. Most Baby Boomers neglect the importance of separating work and personal data. According to the survey findings, 63% of employees are not concerned about storing personal information on work devices. Nearly 27% of Baby Boomers are very comfortable with keeping personal information on work devices despite associated cyber risks.

Not My Responsibility!

Most of the employees believe that organizations hold the primary responsibility for cybersecurity, with 91% of surveyed employees stating that companies are at least slightly responsible for cybersecurity. However, organizations might be responsible for determining security protocols, but employees are in charge of execution. Nearly, 76% of U.S. workers feel somewhat accountable for ensuring cybersecurity measures at their company.

Related Story: 6 Practices to Strengthen Your Password Hygiene in 2021

Cybersecurity vs Remote Work

A similar research from Netwrix revealed the responses of several global security leaders about the current cyberthreat scenario and how the pandemic and remote working conditions changed their security landscape. The research “2020 Cyber Threats Report” revealed that every fourth organization is concerned that they are exposed to more cyberattacks than before the pandemic. Surprisingly, 85% of CISOs admitted that they had sacrificed cybersecurity due to a sudden shift to remote work conditions.

Click here to read more…

Use SOC 2 Examinations to Keep Your Security Program in “Chek”

SOC 2 Examinations, ByteChek

Protecting customers’ data is a concern for all organizations regardless of industry or size. Most organizations outsource key aspects of their business to third-party vendors such as Software-as-a-Service (SaaS) solutions or cloud hosting providers (i.e. Amazon Web Services or AWS). As companies continue to share the responsibility of protecting sensitive data, there is increased importance and scrutiny on the cybersecurity practices implemented at these organizations. But how can SOC 2 examinations help?

SPONSORED CONTENT

Third-party assessments are a common way in which organizations prove their cybersecurity practices to vendors, customers, and prospects. SOC  2 examinations have become one of the de facto standards for organizations to prove how they are securely managing their customers’ data to protect their interests and privacy. For most organizations conducting business with a SaaS provider, a SOC 2 examination is a minimum requirement. SOC 2 reports are also common for other service organizations as well such as law firms, marketing agencies, accounting firms, healthcare organizations, and more.

How do SOC 2 reports help?

According to the AICPA, these reports can play an important role in:

  • Oversight of the organization
  • Vendor management programs
  • Internal corporate governance and risk management processes
  • Regulatory oversight

ByteChek wrote a whitepaper to provide a simple understanding of SOC 2 and how to do SOC 2 examinations. Use this whitepaper and the ByteChek Learning Center as your source of truth for all things SOC 2.

SOC 2 is a report on a service organization’s controls relevant to Security, Availability, Processing Integrity, Confidentiality, or Privacy. SOC 2 reports are intended to inform users of detailed information and assurance about the controls at the service organization. These reports are provided by qualified CPAs, who form an opinion about the service organization’s system and the control environment.

SOC 2 reports are becoming more prevalent in the market and more companies are asking for them in order to meet contractual obligations, supply chain management, due diligence, or other requirements. For the service organization, the report becomes not just a means to deliver on these obligations, but also a way of showcasing your security posture, as well as improving it through making sure your controls will operate properly.

Read everything there is to know about SOC 2 in this whitepaper.

Related Story

Streamline Your Compliance Needs with ByteChek


Do You Have it in You to “Hack the Army”?

Russian hackers, Senate Homeland Security Report, Electronic Warfare Associates

The U.S. Army Cyber Command (ARCYBER) in association with the Defense Digital Service (DDS), the Army Network Enterprise Technology Command, and HackerOne, has launched “Hack the Army 3.0” bug bounty program. The bug hunting is set to begin on December 14, 2020 and is slated to last until January 28, 2021 or until allocated funds (of $100,000) are exhausted.

“Hack the Army” Bug Bounty Program

The U.S. Army initiated this program in late 2016, following the launch of DoD’s Hack the Pentagon program that was facilitated by the DDS earlier that year.  The first edition of Hack the Army challenge identified 118 unique and valid vulnerabilities from the 416 that were reported. A total of $100,000 was awarded in bounties to hackers for their legitimate findings. Nearly 400 hackers from around the world participated in this challenge, including government employees and military personnel.

The second edition of the challenge which included more than 60 publicly accessible Army web assets for penetration, saw more than 145 security vulnerabilities being identified. The army awarded a total cash prize of $275,000 in bounties, with the single largest bounty costing $20,000.

Primary Objective of the Program

According to HackerOne, which is responsible for running the program, this exercise primary serves four objectives:

  1. The Army wants to build bridges to the private sector and talented Hackers by “putting their money where their mouth is.”
  2. Make use of a diverse talent pool, many of whom would otherwise not work with the Army.
  3. Augment the incredible work the Army red teams and DDS workforce is already doing to help secure their systems and networks.
  4. Step-up mission-oriented systems’ and networks’ security.

A statement from the Army read: “The bug bounties aim to evolve the security of DoD and Army networks, systems and data by allowing skilled civilian and military security researchers to perform specific techniques against select public-facing websites, to find vulnerabilities in those sites.”

“This is an effort for DoD to explore new approaches to its security, and to adopt the best practices used by the most successful and secure software companies in the world. By doing so, the Army can ensure U.S. systems are as secure as possible.”

ARCYBER officials are hopeful of increased participation by military members and are finding ways to frequently conduct more bug bounty programs like these in the future.

Interested candidates can apply for the DoD Bug Bounty Challenge “Hack the Army 3.0” here.

Related News:

Tesla Offers US$1 Million and a Car as Bug Bounty Reward

Attention Bug Hunters! FireEye’s Private Bug Bounty Program Goes Public

Ransomware: A Lucrative Business Model for Hackers, says FS-ISAC

Ransomware Attacks, Graff ransomware attack

A recent survey from the Financial Services Information Sharing and Analysis Center (FS-ISAC), highlighted that rapidly evolving ransomware attacks have become a primary security concern for most financial organizations. In its latest report, “The Rise and Rise of Ransomware,” the FS-ISAC stated that, “While financial institutions remain resilient to ransomware attacks, they are not immune. Ransomware is a rapidly evolving threat that financial institutions globally and in the APAC region need to be vigilant against.”

The research indicated that ransomware operators have openly claimed successful attacks against eight financial institutions globally in 2020, three of which were banks. It was found that attackers targeted third-party vendors and suppliers used by firms in Asia. The FS-ISAC suggested that even organizations with robust cybersecurity defenses are still vulnerable to ransomware threats, especially through their third-party providers.

Ransomware: A Multi-Business Model

Hackers diversified ransomware attacks by incorporating new revenue streams like:

  • Extorting victims by threatening to publicly name them and publish sensitive data online.
  • Auctioning off victims’ data to other criminals on the dark web.
  • Ransomware-as-a-service, where less technical criminals can buy sophisticated ransomware kits

Top Ransomware Variants

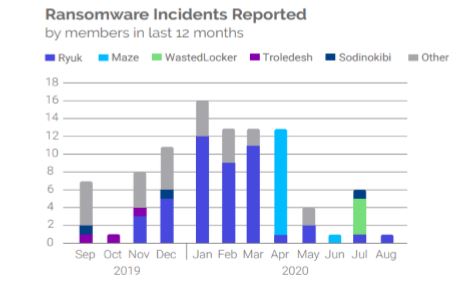
According to the report, the top five ransomware variants in the last 12 months include, Ryuk, Maze, WastedLocker, Troledesh, and Sodinokibi.

Image Courtesy: FS-ISAC

“FS-ISAC members regularly report on phishing campaigns sent to staff, including those which lead to ransomware. Ryuk largely dominated the first quarter’s notifications to FS-ISAC with 9 to 12 campaigns noted per month; however, Maze started in earnest in the second quarter with 12 campaigns observed in April,” the report said.

Preventive Measures:

FS-ISAC also recommended certain practices to help prevent ransomware attacks. These include:

  • Regularly educate and train employees to maintain situational awareness and report any potential issues immediately.
  • Provide real-world examples and repercussions of successful ransomware exploits.
  • Perform regular phishing tests to assess your employees’ knowledge and ability to prevent ransomware attacks.
  • Train cyber teams to coordinate a response with other parts of the organization including finance, communications, and the executive team to respond when ransomware hits.
  • Ensure your incident response and business continuity plan includes ransomware response protocols.
  • Include steps to isolate or power-off affected devices that have not yet been completely corrupted.
  • Ensure ways to immediately secure backup data or systems by taking them offline and make sure backups are free of malware.

Gamers on Target! Malicious Fleeceware Apps Affect Minecraft Gamers

Fleeceware Applications

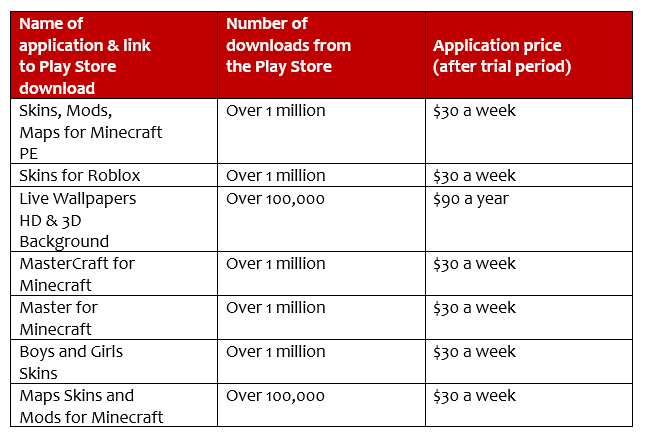
Avast, a provider of digital security and privacy products, disclosed a wave of malicious mobile applications in the Google Play Store targeting mobile gamers. These malicious apps, dubbed as “Fleeceware applications,” lure users with various offerings like new skins, colorful wallpapers, or modifications for the game, but excessively charge users after the free trial. In particular, the attackers target gamers of the popular Minecraft video game.

Fleeceware apps have characteristics of overcharging users for functionality that is widely available in free or low-cost apps. It is said that these app developers are taking advantage of the free-trial period by charging an excessive amount from users when they do not cancel the subscription. Usually, these apps charge subscription charges between $30 per month or $9 per week after a three to seven-day trial period. It is also suspected that these apps bought fake five-star reviews to boost their ranking on the Play Store and used pay-per-install services to boost install counts to attract users.

Related Story: How to Spot Malicious or Fake Apps

Fleeceware apps cannot be removed by simply uninstalling it from the device. You need to cancel the subscription directly in the Play Store (Play Store → Menu in the upper left corner → Subscription).

Avast said it reported seven such apps to Google, which include:

Ondrej David, malware analysis team lead at Avast, said, “Scams of this nature take advantage of those who don’t always read the fine print details of every app they download. In this case, young children are particularly at risk because they may think they are innocently downloading a Minecraft accessory, but not understand or may not pay attention to the details of the service to which they are subscribing. We urge our customers to remain vigilant when downloading any app from unknown developers and to always carefully research user reviews and billing agreements before subscribing.”

Related Stories:

Cyentia Institute’s Study Reveals Financial Loss of 100 Largest Cyberattacks

Vulnerabilities in Zimbra

An extensive analysis from cybersecurity research and data science firm Cyentia Institute revealed details about the financial impact of cyber incidents on organizations of all types and sizes. The analysis “Information Risk Insights Study (IRIS) 20/20 Xtreme” focused on the 100 largest cybersecurity incidents of the last five years and found that these incidents totaled $18 billion in reported losses and 10 billion compromised records. This may be a new record in the world of cybercrime.

Key Findings

  • The average loss is $47 million. With over one-in-four exceeding $100 million losses.
  • Response costs, lost productivity, and fines and judgements are the most common forms of loss in extreme events.
  • The likelihood of incidents varies up to 30x by industry. Government agencies, administrative support, information services, and financial firms, have the highest rates.
  • Firms that bungle the incident response process show costs that are nearly 2.8 times larger than those without signs of poor response.
  • The financial and information sectors, with their large holding of funds and data, have experienced the largest number of extreme loss events.
  • Data breaches, ransomware, fraud, and cryptocurrency theft are by far the most common and costliest types of extreme cyber events.
  • One in five of the largest losses over the last five years are attributed to state affiliated actors.

The current analysis report is a continuation of the Cyentia Institute’s IRIS 20/20 study from earlier this year, which is based on the information from insurance data group Advisen. “Our goal was to breakdown the costs, categorize incident types, identify the actors behind these events and the actions they employed, and better understand how these events impacted the organizations involved,” the study stated.

David Severski, Senior Data Scientist at Cyentia and lead IRIS Xtreme analyst said, “Continuing the data-driven exploration of loss events from the IRIS 20/20 report, this zeroing in on the largest of the large breaches reveals new information on the actors, magnitude, and forms of loss that make up the headlines in front of risk managers and organization leaders.”

Streamline Your Compliance Needs with ByteChek

cybersecurity compliance

Cybersecurity assessment is the need of the hour for all organizations as security breaches become daily news for organizations around the globe. But these assessments and audits are not a walk in the park. It can be very overwhelming, and many of the processes can be too laborious and time-consuming at times.

SPONSORED CONTENT

To resolve this issue and to speed up the process of proving compliance, ByteChek, a SaaS–based company, has been newly established to automate IT audits and streamline cybersecurity reporting. AJ Yawn, a former Captain in the U.S. Army and cloud security industry expert, along with Jeff Cook, a CPA with over 20 years of experience in accounting and auditing, describes the founding ideology behind ByteChek as: “Make Compliance Suck Less.”

What ByteChek’s Platform Offers

ByteChek’s platform is well suited for companies of all sizes. It provides security programs, automates cybersecurity readiness assessments, and completes SOC 2 audits faster – all from a single platform.

Related News:

Compliance: A Chief Tenet for the Future of Cybersecurity

The platform allows companies to quickly build their information security policy, ground up, utilizing the ByteChek information security policy generator. The ByteChek platform then connects with the applications companies use every day to eliminate evidence collection and vague auditor requests.

AJ Yawn - ByteChek

“We make it easier for companies of all sizes to achieve their cybersecurity compliance goals. With so many frameworks out there, compliance can be confusing, time-consuming, and too much paper pushing. By focusing on security instead of compliance frameworks, we eliminate the confusion, make compliance faster and ultimately more valuable to security practitioners and executives”

– AJ Yawn, Co-Founder, and CEO, ByteChek

Regulatory standards have become more complex, and thus maintaining compliance to pass audits has become more tedious. However, this platform helps automate the processes involved with maintaining compliance, saving companies some valuable time and money.

The ByteChek platform is powered by its proprietary “ByteChek Engine” that automatically assesses controls according to AICPA and audit standards. Additionally, ByteChek provides cybersecurity advisory and SOC 2 assessment services, which are based on the audit and cybersecurity experience of the ByteChek’s leadership team.

Jeff Cook - ByteChek

“Automation and AI is a big part of being future-ready in our industry. Thus, we designed our platform with an anticipatory mindset to make IT audits and reporting easier.”

– Jeff Cook, Co-Founder, and CFO, ByteChek


Microsoft’s November Patch Tuesday is Here! Know Which Flaws are Fixed

Brand Phishing Attacks

Microsoft released the official patches for over 112 newly discovered vulnerabilities as part of its November 2020 Patch Tuesday. The technology giant stated the latest fixes address 17 critical-rated flaws, 93 important, and 12 low-rated flaws, including an actively exploited zero-day flaw, which was disclosed by Google’s security team recently.

The security release consists of updates for various Microsoft products, which include:

  • Microsoft Windows
  • Office and Office Services and Web Apps
  • Internet Explorer
  • Edge
  • ChakraCore
  • Exchange Server
  • Microsoft Dynamics
  • Windows Codecs Library
  • Azure Sphere
  • Windows Defender
  • Microsoft Teams
  • Visual Studio

“The Microsoft Security Response Center has been scoring Windows and Browser vulnerabilities since 2016. Now we are scoring every vulnerability and displaying the details that make up that score in the new version of the Security Update Guide,” Microsoft said.

Last month Microsoft released updates to fix 129 vulnerabilities: 23 of which were deemed critical, 105 were important, and the rest were moderate in severity. The patches addressed vulnerabilities in Microsoft Windows, the Edge browser, ChakraCore, Internet Explorer, SQL Server, Office and Office Services and Web Apps, Microsoft Dynamics, Visual Studio, Exchange Server, ASP.NET, OneDrive, and Azure DevOps.

CISA Advice to Patch Microsoft Flaws

Recently, the U.S. Cybersecurity & Infrastructure Security Agency (CISA) issued an advisory for enterprises’ specifically asking them to apply required patches for the two Microsoft vulnerabilities – RCE Windows Codecs (CVE-2020-17022) and Visual Studio Code (CVE-2020-17023). With CVE-2020-17023 requiring an update, coupled with an out-of-band advisory, both CISA and Quinlan have encouraged administrators to patch this vulnerability quickly. While Microsoft stated that there is no exploitation observed in the wild, the follow up of the CISA advisory suggests that administrators should review the patches and apply the updates if necessary. Read the full story here…