Home Blog Page 292

Attackers are targeting Internet-Connected Gas Stations: Researchers

Superior Plus, Saudi Aramco data breach

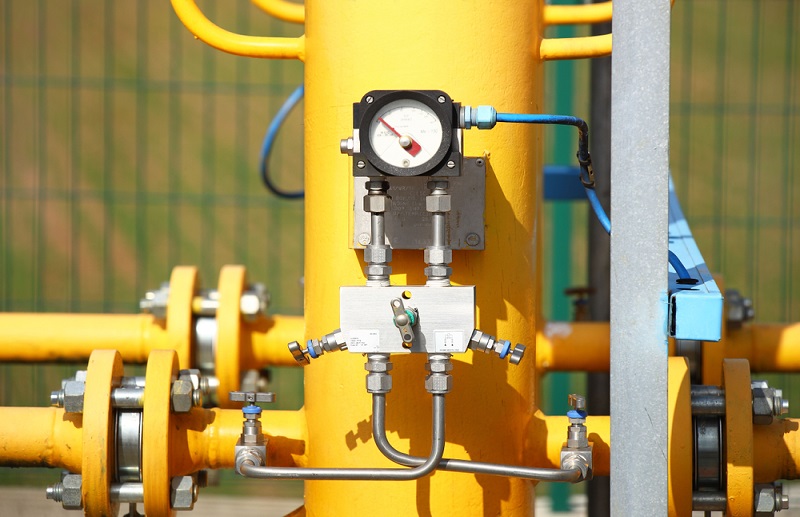
From smart speakers to connected automobiles, the Internet of Things (IoT) has become a primary target for cybercriminals. Security researchers discovered that hackers are targeting internet-connected Gas Stations to launch IoT-based cyber-attacks.

Researchers at Trend Micro discovered that internet-connected Gas Pumps are vulnerable to IoT-based attacks. In its recent report, the Internet of Things in the Cybercrime Underground, Trend Micro described how the Russian hackers are benefited from the Russian government’s new directive, which mandates to replace all electricity meters in the country with smart meters.

Trend Micro stated that it surveyed in dark web marketplaces in English, Spanish, Russian, Portuguese, and Arabic languages.

According to the researchers, hackers in Russian dark web forums are requesting information on how to exploit smart meters.  Some hackers are even selling altered smart meters in the underground market forums. Researchers also revealed that they’ve seen tutorials on gas pump hacking in Portuguese language forums, including step-by-step procedures on how to hack connected meters.

“Users in the Russian underground are interested to know the latest news about IoT attacks sourced from the information security world. The money-driven criminals make up a market thriving with exploits for routers, customized firmware for smart meters, talks of hacking gas pumps, and router-based botnets for sale. There is a variety of conversations taking place around devices, including fewer common platforms. Most of these talks have a monetization angle. In general, a Russian underground is a place for business where hacking and technical information is mere details,” researchers said in a statement.

“The Portuguese-speaking criminal underground is composed of web forums mostly populated by Brazilian users. These users also connect through some other private chat rooms, for example, Telegram, WhatsApp, and Discord. We saw requests for information and hacking tutorials. But the most interesting ads we saw are those for services that use infected routers and similar devices as the basis for further criminal services. This is the case for “KL DNS,” which is a kind of service sold on Brazilian forums to perform fool proof phishing campaigns combined with DNS redirection and, in some cases, SMS spamming,” the statement added.
Tel-Aviv based Cybersecurity Startup Kovrr raises US$5.5 Million

Cyber Risk Modeling firm Kovrr recently raised US$ 5.5 Million in a financing round led by venture capital firms StageOne Ventures and Mundi Ventures, along with the participation from Banco Sabadell and other private investors. The Tel-Aviv based company stated the new funding will help the company accelerate its product development and global expansion activities.

Founded in 2017 by security experts Yakir Golan, Shalom Bublil, and Avi Bashan, Kovrr delivers data-driven end-to-end insights to government and private insurance regulators, that enable them to calculate their cyber risk exposures. Kovrr claims that its end-to-end platform quantifies potential financial loss caused due to different types of cyber-attacks and helps in managing cyber risks.

Commenting on the new investment, Kovrr’s CEO, Yakir Golan, said, “Cyber-attacks cause billions of dollars of damage and currently affect every category of risk. Kovrr’s unique approach leverages data science and predictive analytics to deliver powerful and actionable capabilities that our clients need to grow their businesses and confidently act on their cyber risk management decisions. The recent funding allows us to further expand our commercial reach, data harvesting and predictive modeling capabilities.”

Today, the company provides the world’s leading insurance carriers, reinsurers & government regulators with an end-to-end platform that delivers transparent, data-driven insights that enable them to quantify and manage their affirmative and silent cyber risk exposures across all lines of insurance.

Kovrr accurately quantifies potential financial loss caused by various types of cyber events. The platform uses open-source, proprietary and third-party business and threat intelligence data to train predictive cyber risk models.

“Kovrr is one step ahead in modeling cybersecurity risks and has the potential to become the engine that powers cyber risk underwriting for the insurance industry,” said Javier Santiso, CEO and Founder of Mundi Ventures. “Their technology’s ability to give insights about existing silent cyber risk exposure combined with methods to measure risks from new policies, is superior to competing technologies. At Mundi Ventures we are delighted to take part in this journey with Yakir and his top-notch team of cybersecurity experts.”

Trend Micro reports 265% Rise in ‘Fileless Attacks’

BotenaGo, malware over encrypted connections

Cybersecurity and Defense company Trend Micro recently revealed a 265 percent increase in Fileless Attacks in the first half of 2019 when compared with the same period in 2018.

A Fileless Attack, also known as a zero-footprint attack or non-malware attack, will not install any malicious software on a user’s computer, as it exploits applications that are already installed in the device.

Trend Micro stated that cybercriminals are using sophisticated attack formats that aren’t visible to traditional security procedures.

In its Mid-Year Cybersecurity report, Trend Micro revealed that out of 1.8 billion ransomware threats, from January 2016 to June 2019, the highest number of ransomware threats (42.98 percent) are suffered by  businesses in Asia. And the companies in India reported around 23.88 percent of ransomware attacks in the first of 2019, the report stated.

“Sophistication and stealth are the name of the cybersecurity game today, as corporate technology and criminal attacks become more connected and smarter,” said Nilesh Jain, Vice President, Southeast Asia and India, Trend Micro. “From attackers, we saw intentional, targeted, and crafty attacks that stealthily take advantage of people, processes and technology. However, on the business side, digital transformation and cloud migrations are expanding and evolving the corporate attack surface. To navigate this evolution, businesses need a technology partner that can combine human expertise with advanced security technologies to better detect, correlate, respond to, and remediate threats.”

Along with the growth in fileless threats in the first half of the year, attackers are increasingly deploying threats that aren’t visible to traditional security filters, as they can be executed in a system’s memory, reside in the registry, or abuse legitimate tools. Exploit kits have also made a comeback, with a 136% increase compared to the same time in 2018.

Cryptomining malware remained the most detected threat in the first half of 2019, with attackers increasingly deploying these threats on servers and in cloud environments. Substantiating another prediction, the number of routers involved in possible inbound attacks jumped 64% compared to the first half of 2018, with more Mirai variants searching for exposed devices.

Additionally, digital extortion schemes soared by 319% from the second half of 2018, which aligns with previous projections. Business email compromise (BEC) remains a major threat, with detections jumping 52% compared to the past six months. Ransomware-related files, emails and URLs also grew 77% over the same period.

In total, Trend Micro blocked more than 26.8 billion threats in the first half of 2019, over 6 billion more than the same period last year. Of note, 91% of these threats entered the corporate network via email. Mitigating these advanced threats requires smart defense-in-depth that can correlate data from across gateways, networks, servers and endpoints to best identify and stop attacks.

Founded in 1988, Trend Micro holds a variety of cybersecurity merchandise for multiple operating systems, including threat detection, and antivirus products. Hybrid cloud security, network defense, user protection, and small business products are at the core of its product line.

Attackers use ‘Deepfake’ Voice Software to steal US$243,000

In what can be considered a sophisticated Vishing attack, cybercriminals used voice-mimicking software to imitate a company’s CEO voice to trick the other party into transferring €220,000 (US$ 243,000) to their account, the Wall Street Journal reported.

According to an official statement, the CEO of the UK-based energy firm believed that his boss, from the parent firm in Germany, was on the call and followed his instructions to send funds to an account in Hungary, which was later transferred to Mexico. But the UK CEO was actually taking instructions from a hacker who’d used the Deepfake Software Tool, an AI-powered voice technology, to mimic the German CEO’s voice.

The details of the attack were reported by the energy company’s insurer Euler Hermes Group. The insurer stated the transferred funds were distributed across multiple accounts in Hungary and Mexico.

“The software was able to imitate the voice, and not only the voice: the tonality, the punctuation, the German accent. The phone call was matched with an email, and the energy firm CEO obliged. The money is now gone, having been moved through accounts in Hungary and Mexico and dispersed around the world,” a Euler Hermes spokesperson said in a media statement.

“The money, totaling 220,000 euros, was funneled through accounts in Hungary and Mexico before being scattered elsewhere, Euler Hermes representatives said. No suspects have been named, the insurer said, and the money has disappeared,” the statement added.

Cybersecurity has now become a board room imperative

Cybersecurity in Board Room

Cybersecurity has now become a concern for the board room and the rest of the hierarchy. According to new research by Infosys Knowledge Institute (IKI), the research arm of Infosys, titled ‘Assuring Digital-Trust’ nearly half i.e. 48 percent of corporate boards and 63 percent of business leaders are actively involved in cybersecurity strategy discussions.

IKI surveyed 867 senior executives from 847 firms with annual revenues over US$500 million. These firms were from countries like the U.S., Europe, Australia and New Zealand (ANZ). The research points out that security has finally taken the center stage


“The outcome of the survey did not come as a shock or something that I hadn’t anticipated,” said Vishal Salvi, CISO and Head of Cyber Security Practice, Infosys in an exclusive interaction with CISO MAG. “The most important trend that is visible from the report is that security is becoming a mainstream issue. It is no longer an afterthought. The industry is aware of it and is taking their steps in precaution to avert cyber-attacks. I am glad to point out that the aspect of cybersecurity is no longer irrelevant, and it has become more fundamental than ever before,” said Salvi.

The report also pointed out that organizations are now finding it difficult to embed security in their enterprise IT architecture due to several factors like lack of cybersecurity talent, and inability to keep up with the technological advancements and evolving threat landscape.

Evolved Role

Salvi is of the opinion that the role of CISO has become more defined and dynamic than ever before. “If you think of it as a stage then the spotlight is on the CISO, even though there are many characters, the spotlight is on the CISO. Back in the day, we needed to be heard, and we had to tell everyone that security is important.”

He continued: “All of those were our issues and challenges maybe three or five years back. Today, all those challenges are no longer there because of the way the cybersecurity risks have manifested. You find that it is already the board topic because the spotlight is on the CISO. Now, the new challenge is the challenge to perform and deliver. And you are going to be held accountable for delivery. So, I think the CISO’s role is now moving from trying to influence and create of visibility toward relentless execution and making sure that there has been the right strategy and you have the right execution skills to be able to deliver that strategy. I think that’s how the role is changing at a broader level.”

Top Concerns

The study also points out that the top concerns of enterprises are Hackers/Hacktivists (84 percent), low awareness among employees (76 percent), insider threats (75 percent), and corporate espionage (75 percent).

“Even here, cyber espionage from state-back actors takes huge precedence. Corporate espionage is still secondary as many companies are also thinking about the risk of loss of reputation due to indulging in corporate espionage,” Salvi adds.

To combat security threats, over than half of the organizations are focusing on integrated security solutions. Several companies are also following a series of ‘soft’ methods which include training/certifications which is at 61 percent, enablement sessions at 54 percent and creating security awareness among employees at 51 percent.

“As enterprises continue to add new technologies to the business, it is crucial to defend themselves against a sophisticated threat environment,” Salvi said. “We believe a holistic approach to cybersecurity is what it takes to instill digital trust in companies, and this research offers a good understanding of the current cybersecurity landscape. The insights, if applied appropriately can accelerate the cyber defense of enterprises.”

Unprotected Database Exposes Millions of Facebook users’ Contact Numbers

Misconfigured AWS S3 Bucket Exposes PII of up to 350,000 SSL247 Customers

An unprotected server hosting a database leaked millions of Facebook users’ phone numbers online. According to TechCrunch, the server wasn’t password-protected, allowing anyone to access the Facebook database.

The database contained more than 419 million records of Facebook users across the globe, including 133 million records of U.S. users, 18 million records of the U.K. users, and more than 50 million records of Vietnam users. The exposed records contained users’ unique Facebook ID and the phone number linked to their accounts.

Facebook fixed the database after security researcher Sanyam Jain flagged the issue. The Social Media giant later claimed the unprotected database contained only 220 million users’ records.

This is the latest security incident in Facebook’s timeline of data breaches. Earlier, researchers discovered that Facebook user account information was exposed on Amazon cloud servers. The security team at UpGuard stated that they found two data breach incidents in different regions.

The first incident originated from the Mexico-based media company Cultura Colectiva, which exposed around 146 GB of data that contained over 540 million records detailing comments, likes, reactions, account names, FB IDs, and other sensitive information. UpGuard stated the data was stored in Amazon’s cloud service without password protection and could easily be accessed by outsiders.

The second was a separate database from a Facebook-integrated app named ‘At the Pool’ which exposed data via an Amazon S3 bucket. This database contained backup information like fb_user_id, fb_user, fb_friends, fb_likes, fb_music, fb_movies, fb_books, fb_photos, fb_events, fb_groups, fb+checkins, fb_interests, and passwords.

In a recent update, Facebook is set to pay the largest fine imposed on a technology company by the Federal Trade Commission. The social media giant was slapped with a massive $5 billion fine for allegedly violating privacy practices and mishandling user data during the infamous Cambridge Analytica scandal and other privacy breaches.

The FTC ordered Facebook to adopt new policies for protecting users’ data and expand these policies across Instagram and WhatsApp. Facebook has also been asked to create a new privacy committee that will have independent board members. Moreover, a third-party assessor approved by the FTC will be brought on board to conduct biennial assessments and monitor Facebook’s privacy-related decisions.

Four in Five Schools in the UK suffer Security Incident: Report

Insider attacker leak data

A recent cybersecurity audit revealed that four out of five schools in the United Kingdom have suffered a security incident like phishing, malware, and ransomware attacks. And many of these attacks were conducted by the schools’ students and staff.

The survey, which was carried out by the National Cyber Security Centre and the London Grid for Learning (LGfL), also highlighted that one in five schools stated that they’ve encountered illicit access to their networking systems by their students and staff.

Based on the responses from 430 schools across the UK, the findings revealed that 83 percent of schools reported at least one security incident every year, causing data leak and disruption to their IT services.

According to audit findings, around 69 percent of schools suffered a phishing attack, 35 percent had experienced periods with no access to information, 30 percent suffered malware infection or ransomware, while 20 percent fell victim to spoofing attacks.

“Budgets are tight, the curriculum is squeezed, and school is all about keeping children safe and providing the best possible education. So, you won’t often hear schools talking about their cybersecurity preparedness. Whilst it was hospitals rather than schools which suffered major disruption from the WannaCry virus, schools are just as likely as any organization to face DDoS and phishing attacks,” the report said.

Schools are often seen as a primary target for attackers, as they hold a huge amount of sensitive information.

Recently, a ransomware attack on Syracuse City School District and Onondaga County Public Library ceased their network systems and disabled the access to the catalogues and online accounts. The school authorities launched an investigation to determine the source and damage of the incident.

According to the official statement, the hackers infected the school’s network system with Ryuk Ransomware and demanded a ransom to set free. It’s believed that the attacker is linked to a criminal group known as Grim Spider based in Eastern Europe.

Also, the San Diego Unified School District reported a data breach that affected more than 500,000 students and staff members. According to the official statement, a phishing scam led to unauthorized access to the staff’s log-in information, including the network services and students’ database.

Millions of Android Phones vulnerable to ‘Provisioning Attack’

GO SMS Pro Android App Still Vulnerable to Data Exposure

Security experts revealed that more than half of modern Android smartphones, including models by Sony, LG, Samsung, and Huawei are vulnerable to a text-based phishing attack.

According to security firm Check Point Software Technologies, malicious actors are using fake phone provisioning messages to trick Android phone users into accepting new settings that provide access to attackers. The researchers stated that the phishing attack is performed through a process called over-the-air (OTA) provisioning.

Check Point detailed the attack process as OMA CP (Open Mobile Alliance Client Provisioning) instructions, which is a special SMS sent by a mobile operator to new devices for network connection. Attackers sending fake OMA CP messages to users, which allow them to allegedly access the victim’s email and web traffic, Check Point stated.

“The industry standard for OTA provisioning, Open Mobile Alliance Client Provisioning (OMA CP), includes rather limited authentication methods; a recipient cannot verify whether the suggested settings originate from his network operator or from an imposter. We found that phones manufactured by Samsung, Huawei, LG, and Sony allow users to receive malicious settings via such weakly-authenticated provisioning messages. Samsung phones compound this by allowing unauthenticated OMA CP messages as well,” Check Point said in a statement.

Check Point stated that it reported the discovered flaws to mobile manufacturers. “We disclosed our findings to the affected vendors in March. Samsung included a fix addressing this phishing flow in their Security Maintenance Release for May (SVE-2019-14073). LG released its fix in July (LVE-SMP-190006). Huawei is planning to include UI fixes for OMA CP in the next generation of Mate series or P series smartphones. Sony refused to acknowledge the vulnerability, stating that their devices follow the OMA CP specification. OMA is tracking this issue as OPEN-7587,” the statement added.

Google launches New Bug Bounty Program

cyberthreats, bug

Google recently announced the launch of its new Developer Data Protection Reward Program (DDPRP) and the expansion of Google Play Security Reward Program (GPSRP), which are intended to detect and mitigate data abuse issues in Chrome plugins, Android apps, and OAuth projects. Google started its vulnerability rewards program in 2010, which offers cash rewards to security researchers who report flaws in Google code.

The search engine giant stated that it’s joining hands with bug bounty platform HackerOne to launch the new bug bounty program. According to Google, bug hunters are required to identify situations like – selling user’s data or illegitimate use of it. The bug reporters will be rewarded with a maximum bounty worth US$ 50,000.

“We’re constantly looking for ways to further improve the security and privacy of our products, and the ecosystems they support. At Google, we understand the strength of open platforms and ecosystems, and that the best ideas don’t always come from within. It is for this reason that we offer a broad range of vulnerability reward programs, encouraging the community to help us improve security for everyone,” Google said in a statement.

Google recently raised bounties for Chrome and Google Play bugs, making them more lucrative to security researchers. The company stated that they’ve received around 8,500 vulnerability reports and paid rewards over US$ 5 million (£4 million).

According to Google’s Chrome security experts Natasha Pabrai and Andrew Whalley, the company has doubled the maximum reward on High-Quality Reports from US$15,000 (£12,000) to US$30,000 (£24,000) and tripled the baseline reward amount from US$5000 (£4 million) to US$15,000 (£12,000) for good measure.

IoT startup Astrocast raises US$ 9.2 million to develop IoT modules for Secure Communications

Internet of Things (IoT) startup Astrocast recently secured US$ 9.2 million (€8.3 million) in a Series A round of funding. The Swiss startup said the new proceeds will help it accelerate the production of IoT modules and the deployment of its Low Earth Orbit (LEO) IoT Network.  The company is developing an IoT Nanosatellite Network that provides bidirectional and highly secure connections to any IoT device on Earth.

Astrocast was founded in 2014 by security veterans Bertil Chapuis, Fabien Jordan, Federico Belloni, Jean-Michel Jordan, Julian Harris, and Nicholas Petrig.  It is partnering with the European Space Agency, Thuraya, and Airbus for the development of an advanced Nanosatellite network for IoT devices.

Speaking on the new investment, Fabien Jordan, the CEO of Astrocast, said, “We are excited to see the continued confidence of our investors and partners in the new space race and our company, as we make our mission of building the world’s first IoT network for the planet a reality. As we move toward our commercial launch in Q1 of 2020, we are further confirming our leadership as a fully integrated nanosatellite operator and our unique ability to deliver efficient IoT satellite coverage globally. Next steps with investors will be to secure an accelerated deployment of our global fleet of satellites.”

“It has been an amazing year for Astrocast. With the launch of two satellites and a growing number of pilot customers, the company has demonstrated its ability to bring IoT access to the world,” Jordan added.

In a similar funding news, IoT security startup VDOO secured US$32 million in a Series B financing round led by WRV and GGV Capital along with the participation from NTT DoCoMo. The Tel Aviv, Israel-based startup stated the new funds will be used to accelerate the development of its automated analysis capabilities and also expand the company’s partner and distribution network.

VDOO helps embedded device vendors increase the security level of their products by analyzing the security gaps of each device using the cloud or a closed local environment. The company claims that it uses advanced machine learning to build actionable security requirements. The startup helps vendors to take instant actions towards device runtime protection using a single platform.