Home Blog Page 243

Industry Certifications Aligned to Cyber-Affiliated U.S. Military Job Roles are Important when Hiring Candidates: Survey

Employee habits

A new survey from University of Phoenix and the International Council of E-Commerce Consultants (EC-Council) found that 59% of surveyed companies with 100 or more employees plan to staff information security professionals in 2020. However, candidates in the job market may not have the skills employers are seeking. According to the survey, 67% of IT executives at companies with at least 100 employees or more require industry certifications as a basic requirement for hiring considerations.

The joint survey aims to uncover IT employers’ perceptions during the hiring process. The findings highlighted the importance of cybersecurity degree programs paired with stackable credentials aligned to military job roles and occupations. Of the 256 IT employers who were polled, 86% said that industry certifications aligned to cyber-affiliated U.S. military job roles and occupations play an important role when hiring candidates. In fact, almost half (48%) agreed they are either very important or essential, and 84% consider them to be the “gold standard” when hiring.

“Cyber threats are growing exponentially, and IT employers must ensure that the candidates they are hiring possess the proper education and skills to take on these threats,” said Stephanie Benoit-Kurtz, Lead Cybersecurity Faculty at the University’s Las Vegas Campus. “Organizations often don’t have the time or funding to invest in developing employees, and these industry certifications often provide the minimum standards to prepare professionals to combat today’s cyberthreats.”

Highly regarded cybersecurity industry certifications with aligned job roles and outcomes may be easier to obtain than you think. The survey found that nearly all IT executives (91%) said that they would be likely to provide tuition assistance to an employee seeking to earn a degree that helps prepare for industry certification aligned to U.S. military job roles and occupations.

“We tend to look at the bigger picture of career opportunities as a nation, when we should be focusing on what skills and credentials employers’ value most when considering a candidate,” said Wesley Alvarez, director of academics, EC-Council. “As much as they love to hack, it is paramount that graduating students who achieved these challenging credentials understand how to harness their skills in a professional environment.”

To help prepare the workforce for today’s cybersecurity positions, University of Phoenix and EC-Council have worked together to provide students with opportunities that focus on degrees which help prepare students for industry certifications. The University offers an Associate in Cybersecurity and electives that are aligned to EC-Council certifications. In October, the University received the EC-Council Academia Circle of Excellence Award for its suite of EC-Council certifications. They include:

In addition to these offerings, University of Phoenix this month announced the launch of a certificate in cybersecurity policy and governance aligned to the Certified Chief Information Security Officer Certification (CCISO). The CCISO is an industry-leading certification that helps prepare professionals to succeed in the highest level of information security.

During the polling, IT employers were asked which industry certifications they believe employees should possess and 44% said the Certified Chief Information Security Officer certification. The Certified Network Defender received 38% and Certified Ethical Hacker received 23%.

“The College of Business and Information Technology is dedicated to providing working adult learners access to the education and skills that are in high demand in today’s industries. These certifications can help prepare professionals to stay one step ahead of cyberattackers,” said Kevin Wilhelmsen, Dean of the College of Business and Information Technology. “The CCISO and other certification aligned programs are designed to help working adults balance work and life. Not only will they receive the technical foundation but be able to continue to work in their industry while pursuing their program.”

To learn more about the cybersecurity degrees and certificates offered at University of Phoenix, visit phoenix.edu/degrees/technology/cybersecurity.

For more information on EC-Council offerings, visit http://www.eccouncil.org.

Survey Methodology

This survey was conducted online within the United States by The Harris Poll on behalf of the University of Phoenix from October 10–21, 2019 among 256 U.S. adults aged 18 and older who are employed full-time at a company with 100 or more employees, work in IT, and have the job titles of CTO, CIO, Chief Security Officer, Chief Information Security Officer, Information Security Manager, Director of Information Security, or Cybersecurity Manager. Data were weighted where necessary by employee size to bring them into line with their actual proportions in the population. For the purposes of this report, qualified respondents will be referred to as “IT executives.” For complete survey methodology, please contact [email protected].

About University of Phoenix

University of Phoenix is innovating to help working adults move efficiently from education to careers in a rapidly changing world. Flexible schedules, relevant and engaging courses, and interactive learning can help students more effectively pursue career and personal aspirations while balancing their busy lives. University of Phoenix serves a diverse student population, offering associate, bachelor’s, master’s and doctoral degree programs online and from select campuses and learning centers. For more information, visit phoenix.edu.

About EC-Council

EC-Council’s sole purpose is to build and refine the Cybersecurity profession, globally. We help individuals, organizations, educators, and governments address global workforce problems through the development and curation of world-class Cyber Security Education programs and their corresponding certifications and provide cybersecurity services to some of the largest businesses globally. Trusted by 7 of the Fortune 10, 47 of the Fortune 100, the Department of Defense, Intelligence Community, NATO, and over 2000 of the best Universities, Colleges, and Training Companies, our programs have proliferated through over 140 Countries and have set the bar in Cyber Security Education. Best known for the Certified Ethical Hacker program, we are dedicated to equipping over 230,000 information age soldiers with the knowledge, skills and abilities required to fight and win against their black hat adversaries. EC-Council builds individual and team/organization cyber capabilities through the Certified Ethical Hacker Program, followed by a variety of other Cyber programs including Certified Secure Computer User, Computer Hacking Forensic Investigator, Certified Security Analyst, Certified Network Defender, Certified SOC Analyst, Certified Threat Intelligence Analyst, Certified Incident Handler, as well as the Certified Chief Information Security Officer. We are an ANSI 17024 accredited organization and have earned recognition by the DoD under Directive 8570/8140, in the UK by the GCHQ, CREST, and a variety of other authoritative bodies that influence the entire profession. Founded in 2001, EC-Council employs over 400 people worldwide with 10 offices in USA, UK, Malaysia, Singapore, India and Indonesia. Our US offices are in Albuquerque, NM and Tampa, FL.
 

Mapua University Partners with Sophos to Offer Cybersecurity Courses

CynergisTek Partners with Awake Security to Boost Cybersecurity in Health Care

Mapua, a Philippines-based technology university, recently joined hands with the security firm Sophos Group to offer cybersecurity courses and training to university students. The new training alliance comes on the heels of a skills shortage in the cybersecurity sector and frequent data breaches in recent years. The partnership intends to enhance students’ skills and knowledge of cybersecurity.

Headquartered in the U.K., Sophos develops security products for communication endpoints, encryption, network security, email security, mobile security, and unified threat management. The company is primarily focused on providing security software solutions to mid-market businesses.

With the latest partnership, Sophos will offer train-the-trainer-style education on XG Firewall, which would earn Mapua faculty members the certification to teach the courses and embed these into the university curriculum. It also provides an option for students to obtain certifications from Sophos through an examination.

Commenting on the new alliance, Sumit Bansal, Managing Director, Sophos ASEAN, said, “The cybersecurity landscape is constantly evolving and cyberattacks are becoming more sophisticated every day. As a result, there is greater demand in the Philippines for cybersecurity professionals to keep the country safe from cyber threats as it continues its digital transformation journey. Through our partnership with Mapua, we hope to provide greater access to the right learning tools and experts in this field, so students can further optimize their employment opportunities upon graduation.”

Philippines is Vulnerable to Cyberthreats

The Philippines, for the second time in a row, is crowned number one in South-East Asia (SEA) and ranked seventh globally, in terms of the most attacked country by cyberthreats. According to a research from cybersecurity firm Kaspersky, Philippines registered a total of 3,906,410 cyberthreats in computers of Kaspersky users during Q4 of 2019, which is equivalent to 31.6% of the overall threats. Philippines also ranked third in the list of most Android mobile malware attacked countries in the SEA region during the first three quarters of 2019. A total of 134,556 Android malware attacks were recorded, which accounted for 12% of total attacks in SEA.

Tokyo Metropolitan Police Department and (ISC)2 Unite Against Cybercrime

Facebook Indicts Two Developers for Scraping Users’ Data, Europol

The second annual cybersecurity month in Japan kicked off in the first week of February 2019. Following this, a slew of four high profile companies including Mitsubishi Electric, Kobe Steel, Pasco and NEC, having contracts with the Ministry of Defense, reported respective data breaches. This gravely exposed and raised concerns over Japan’s readiness to tackle cyberthreats. Thus, to keep its forces updated with the latest cybersecurity trends and tactics, the Tokyo Metropolitan Police Department (TMPD) signed a Memorandum of Understanding (MoU) with the International Information System Security Certification Consortium(ISC)², a non-profit organization that imparts training for cybersecurity professionals.

A report from Cybersecurity Ventures suggests that cybercrime damages will cost the world US$6 trillion annually by 2021. Thus, law enforcement agencies like TMPD need to revamp their traditional law enforcement tactics and embrace the latest cybersecurity toolsets and expertise to counter the rising global cyberthreat scenario.

Wesley Simpson, COO, Chief Operating Officer of (ISC)², said, “It’s become increasingly important that we arm our law enforcement and government agencies with the tools they need to keep us safe and secure in digital environments, and the Tokyo Metropolitan Police Department is taking steps to grow cybersecurity competencies within Japan.” Matsushita Tokuya, Deputy Director of Cyber Security Control Task Force and Assistant Commissioner at the Tokyo Metropolitan Police Department further added that, “This partnership will help our men and women fighting on the front lines of cybersecurity. It will help our cause of better (cybersecurity) protection to the people of Tokyo.”

Earlier, during the launch of the annual cybersecurity month on February 3, 2020, Chief Cabinet Secretary Yoshihide Suga, emphasized that the government of Japan is making every possible effort to enhance its cybersecurity posture and called for greater awareness towards it. Japan also allocated 25.6 billion yen (approximately US$23.2 billion) in its defense budget for this fiscal year to improve its cybersecurity posture. Along with this, Japan also plans to increase the headcount of its cybersecurity unit, which was established in 2014, from 220 to 290 personnel.

Ryuk Ransomware Campaign Targets Port Lavaca City Hall

ransomware, fonix, fonix ransomware, Cybereason Partners with Intel for Hardware-Enabled Ransomware Prevention, Kronos

The Port Lavaca City Hall’s server was recently hit by Ryuk ransomware that apparently entered through the email system. The ransomware took down the local government’s server, the city’s billing and auto-pay systems, and disrupted other regular operations. However, water, sewer, and the police department’s systems remained unaffected in the incident.

According to the City’s Mayor Jack Whitlow, no information was stolen or compromised but the attackers encrypted the files to demand a ransom. The city officials are working on restoring their systems to get back into working order. It’s said that the attack already incurred a bill amounting to nearly US$50,000  to the City. Whitlow stated that hackers demanded US$200,000 ransom to decrypt the data.

The City officials reported the issue to the FBI for further investigation and confirmed that they’re not fulfilling any ransom demands. Whitlow said, “I’d rather pay the people in town to fix it and keep the money in the community. We’re going to be down for a little while. It may take a while to get completely up to date. We are getting most of our system up and running, but we are recovering some of that data right now.”

The Port Lavaca City Hall’s Manager William DiLibero stated, “The attack brought down our billing system. Our online and auto payment systems are out of service and we have gone back to our older collection and payment processes. Staff are collecting cash, check and credit card payments at City Hall. We will need to rebuild our database in order to get the payment system back to full operational status. The City has worked with State and Federal agencies to address this attack.”

Ryuk in the News

Recently, the officials of the U.S. Coast Guard (USCG) disclosed a Ryuk ransomware infection that took down the entire corporate IT network of a Maritime Transportation Security Act (MTSA) regulated facility for more than 30 hours. According to the USCG officials, the ransomware interrupted the camera and physical access control systems. It’s believed that a malicious email sent to one of the maritime facility’s employees was the entry point for the ransomware infection.

The ransomware corrupted the enterprise IT network files, encrypted them, and prevented the facility’s access to critical files. The officials stated that the incident affected the facility’s IT network and industrial control systems that monitor and control cargo transfer operations.

5G Networks Present New Risks and Security Challenges

5G, 5G Networks, 5g security

The talk of the town, the next big thing, a revolutionary breakthrough – the 5G technology lives up to all these clichés. It captures the imagination with potential use cases capitalizing on the impressively high speed, low latency, and mind-blowing network capacity.

Contributed by David Balaban

The state of 5G deployment currently ranges from large-scale field testing to commercial roll-outs in small portions around the world. Next-generation connectivity is already available in dozens of cities in the U.S.,  Europe, and East Asia. Moreover, these advanced telco systems are expected to become the backbone of digital economies soon.

Just like any new technology, 5G networks can be low-hanging fruit for threat actors who seek to expand their malicious reach. Therefore, it’s in the best interest of governments to assess and tackle the entirety of potential security issues prior to the ubiquitous implementation of the tech.

These concerns have recently incited some expert discussions in the EU. In October, EU member states released a report on “coordinated risk assessment of 5G networks security”. It came in response to a recommendation issued by the European Commission, the executive branch of the EU, in March 2019. Here are the key takeaways from the officials’ findings.

Supplier monopoly deemed as a major risk

The report emphasizes the possible pitfalls of using a single supplier of 5G equipment, namely the Chinese technology giant Huawei. Interestingly, the document contains no direct references to the company in question, although the collaboration is officially underway. Network infrastructure with the solo contractor at its core is susceptible to a number of issues, including a shortage of telecommunications gear, dependencies on the supplier’s commercial well-being, and primitive malware attacks.

Considering this paradigm, the researchers claim network operators will have to rely too heavily on the contractor that may undergo commercial pressure and therefore fail to carry through with its obligations. The adverse influence may stem from economic sanctions affecting the supplier, as well as from a merger or acquisition. Consequently, such cooperation has a single point of failure (SPOF) that might undermine the successful adoption of the technology and stability of the network down the road.

An extra factor is a strong link between the supplier and the government of the country it is based in. It means there is a chance of state-level interference with the equipment provider’s activities. Furthermore, a lack of democratic checks and balances and the absence of data protection agreements between the EU and the said country are serious roadblocks endangering the future partnership.

According to the officials, one more facet of the peril comes down to a tightening connection between the EU’s telco networks and third-party software systems. The elevated scope of access the supplier will have to the region’s 5G infrastructure and the transferred data is a lure for cybercriminals who may take significant efforts to exploit these systems.

Additional security challenges – the big picture

Aside from the obvious caveats arising from the increased role of hardware and software suppliers, the joint report provides a lowdown on other possible security effects of 5G network deployment across the EU. A summary of these challenges is as follows.

More entry points for attackers

The architecture of 5th generation wireless networks is largely based on software. This hallmark makes them particularly vulnerable to security imperfections resulting from vendors’ inappropriate software development processes. Critical flaws may allow malefactors to inject backdoors into the applications and thereby maintain long-lasting surreptitious access to different layers of the targeted 5G infrastructure.

5G network slicing issue

Given that 5G will enable numerous services and applications operating within different virtualized environments, such as enterprise and government networks, the importance of securing these logically segregated ecosystems is going to grow. Unless reliably isolated and protected, these network segments (dubbed “slices”) can be exposed to data leaks.

Scarce software update management

Different operational maintenance procedures come to the fore in 5G networks. This aspect is extremely relevant when it comes to software updates. Regular system patches are crucial for reducing the risk of malicious exploitation via security loopholes in applications. Software suppliers will need to focus on identifying new vulnerabilities and releasing appropriate fixes as fast as possible.

Compliance with the standards

There is a lack of clear-cut security regulations for mobile wireless communications based on 5G at this point. The current 3GPP (3rd Generation Partnership Project) standards mainly apply to earlier mobile telephony protocols and don’t fully address the emerging challenges. The new security requirements have yet to be researched, formulated, and adopted at the state level.

The talent gap

The advances of 5G networks and their mainstream use in the future will incentivize criminals to add more sophisticated attack vectors to their repertoire. The security industry should be prepared for increasingly complex TTPs (Tactics, Techniques, and Procedures) of the adversaries. Therefore, it’s critical to fill the void in terms of security personnel with sufficient skills and knowledge of 5G architecture and its potential weak links.

5G is here to stay. It introduces a bevy of benefits while being an unexplored territory that will make experts rethink the security paradigm.

About the Author

David BalabanDavid Balaban is a computer security researcher with over 15 years of experience in malware analysis and antivirus software evaluation. David runs the Privacy-PC.com project which presents expert opinions on contemporary information security matters, including social engineering, penetration testing, threat intelligence, online privacy, and white hat hacking. As part of his work at Privacy-PC, Mr. Balaban has interviewed security celebrities as Dave Kennedy, Jay Jacobs and Robert David Steele to get firsthand perspectives on hot InfoSec issues. David has a strong malware troubleshooting background, with the recent focus on ransomware countermeasures. 


Views expressed in this article are personal. CISO MAG does not endorse any of the claims made by the writer. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.

SHARE

Elastic Partners with Defending Digital Campaigns to Protect 2020 Elections

Amsterdam-California based firm Elastic partnered with Defending Digital Campaigns (DDC) to provide free endpoint security services to the upcoming 2020 U.S. presidential elections and congressional campaigns.

DDC is a non-partisan organization that provides low and no-cost security products and services to federal campaigns focusing majorly on cyberattacks and election interference.

“Campaigns have faced two significant barriers as they seek to better secure themselves from cyber threats: the high cost of quality cybersecurity products and the experience to organize an effective security strategy. The DDC helps them quickly overcome both, removing cost and expertise as barriers to security and allowing campaign staff to focus on what they do best,” said Devon Kerr, Intelligence & Analytics Team Lead, Elastic Security.

DDC not only facilitates information sharing but also enables security vendors to provide products and services directly to campaigns with the support of the U.S. Federal Election Commission.

“Increasing the cybersecurity defenses of political campaigns is one the most critical elements of protecting our democracy. Defending Digital Campaigns, with a mission to make campaigns more cybersecure, is proud to partner with Elastic Security on making endpoint protection, a core cybersecurity service, widely available to campaigns,” said Michael Kaiser, President and CEO, Defending Digital Campaigns.

Project Shield Anti-Hacking Technology

Earlier, search engine giant Google announced that it’s going to offer anti-hacking technology, named as Project Shield, to political organizations in Europe ahead of the EU elections in May 2019, the Telegraph reported.

The technology used in Project Shield is supposed to safeguard websites from DDoS attacks by using a technique called Reverse Proxy. This technique monitors the website traffic and scans it for malicious content.

Jigsaw, Google’s experimental incubator, said it will offer free cybersecurity protection to political parties and candidates to defend elections from digital attacks. Jigsaw was previously developed and used to protect news organizations and human rights groups in the U.S. midterm elections for a similar purpose.

Security Professionals are Overconfident in the Effectiveness of their Security Tools: Survey

Keysight Technologies, Inc., a technology company that helps enterprises, service providers and governments accelerate innovation to connect and secure the world, released the “Security Operations Effectiveness” survey showing that security professionals are overconfident in their tools with 50% of respondents reporting that they have experienced a security breach because one or more of their security products was not working as expected.

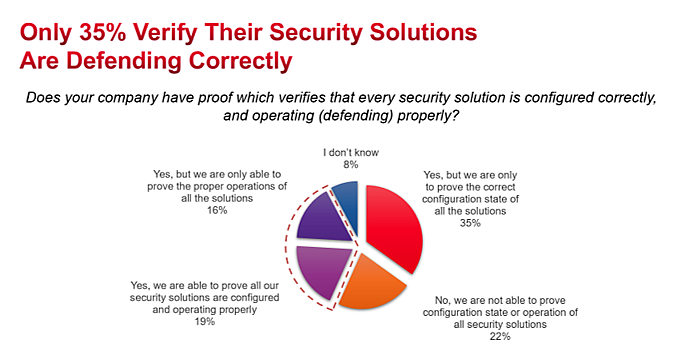
The “Security Operations Effectiveness” survey found that just over half (57%) of security professionals were confident their current security solutions are working as intended. Yet only 35% of survey respondents stated that they conduct testing to ensure their security products are configured and operating as they expect. To close this gap, 86% of respondents see strong value in security test solutions that can actively test their company’s security products and posture, using both internal and external attack vectors.

“Enterprises are faced with a continuous stream of cyberattacks that threaten their businesses, and in many cases, they attempt to deal with these by buying more security tools. Yet they don’t know whether these products are delivering the protection they expect,” said Scott Register, Vice President of security solutions at Keysight’s Network Applications & Security Group (formerly Ixia Solutions Group). “The disconnect is when good security tools are misconfigured, or security teams lack the skills to use their tools. This situation leads to overspending on overlapping tools and compromises an organization’s security posture. Ongoing testing of security solutions would give organizations the proof and confidence that they are protected, but also would provide the opportunity to save resources.”

Keysight Technologies, Inc.
Source: Keysight Technologies, Inc.

Key findings from the “Security Operations Effectiveness”’ survey include:

  • Organizations are breached often: 75% of respondents said their company had experienced a security breach (unauthorized intrusion, malware, hack, etc), and 47% have experienced three or more breaches in the last three years.
  • Good security tools don’t always protect as expected: 50% of survey respondents stated they found a security solution that was not working as expected after a breach had occurred.
  • Most organizations don’t verify their security is working as it should: Only 35% of respondents have test-based evidence to prove their security products are configured and working correctly.
  • Less than half of organizations practice breach responses: 49% of respondents stated they actively practice how to remediate and respond to security incidents.
  • Overlapping security product functions waste budgets and time: 66% of companies are using security solutions whose functions overlap, and for 41% of respondents this overlap is unintentional, wasting security budgets and management time without strengthening the organization’s security posture.
  • The value of security testing: 86% of respondents stated they would value a solution that finds and helps to remediate vulnerabilities in a company’s security posture. 79% of those surveyed would remove a security product from their infrastructure if they could prove it wasn’t effective.

The US$4.3 billion Keysight Technologies commissioned Dimensional Research to conduct the survey in November 2019. A total of 307 participants that strategize, architect, manage and operate enterprise security solutions completed the survey. Participants were from all five continents. They represented large (48%), medium (41%), and small (11%) organizations across a wide variety of industries.

GCC Countries to See Rise in State-Sponsored Cyberattacks: Experts

Qatar

Cybersecurity experts stated that the Gulf Cooperation Council (GCC) countries will see an increase in state-sponsored cyberattacks or APTs (Advanced Persistent Threats), compared to other criminal activities in this year. According to Simone Vernacchia, Head of Digital and Cybersecurity Resilience at PwC Middle East, the geopolitical tensions resulted in the rise of potential cyberthreats targeting critical national infrastructures. Vernacchia also opined that there will be threats from different global actors aimed at disrupting the main supplies in the region like oil and gas, petrochemical, and the electricity grid.

Malware attacks and compromising the systems by cyber warfare are the biggest issues in the Middle East region. The cybercriminal activities will keep growing in financial hubs like Dubai, Abu Dhabi, and Bahrain, but it will be less in number when compared to the West, according to Vernacchia.

Commenting on the current cyberattacks in the region, Vernacchia said, “We have found attackers putting comments in specific languages, or even coding at a specific time in the day to forge proof that a different nation-state is behind the attack. Everyone would try to disguise themselves as someone else and in some cases, it would be of vested interest in a bid to try to pretend it is someone else to ignite a reaction.”

Vernacchia also highlighted, “Electricity grid is important in this region compared to many other parts of the world. The stoppage of electricity and water supply would hit the economy hard in the region, especially in summer. It is cheaper and a way to disguise than sending an army, just by sitting in front of the computer. There have been cases already, and it will happen again next year.”

JhoneRAT in the Middle East

Recently, security researchers from Cisco Talos discovered a new version of Remote Access Trojan named “JhoneRAT”, which targeted a set of enterprises in the Middle East countries. According to the researchers, the Trojan was developed using Python and attacked the victim’s device via malicious Microsoft Office documents. It’s said that JhoneRAT targeted organizations that are based in countries including UAE, Saudi Arabia, Iraq, Libya, Algeria, Egypt, Morocco, Tunisia, Oman, Yemen, Syria, Kuwait, Bahrain, and Lebanon.

Growth of Cybersecurity Market  in the Middle East

The Middle East cybersecurity market is expected to grow at a compound annual growth rate (CAGR) of 22.5% between 2018 and 2024. It’s believed that public and private enterprises in this region are the most targeted verticals to cyberattackers. Hence, it’s important for enterprises in the Middle East to be able to identify security gaps in their systems.

Toll Faces Customer Fallout After Cyberattack

Toll Australia, ransomware

Toll Group, the Australian freight delivery service provider, is struggling to restore its services completely after being hit by the recent “Mailto” ransomware attack on its infrastructure. The incident compromised around 1,000 systems that affected local and global deliveries across the country, and forced Toll to take down many of its delivery and tracking systems. The officials at Toll stated that they have rolled out a cautious approach to restore its systems. The company removed over 500 applications that supported its international operations in 25 countries. Toll stated that its internal networks and user access are currently operational, and the company is continuing to resume the operations of its international air and ocean freight shipments.

Toll declined to reveal the ransom that was demanded. However, the company clarified that it’s not paying or has paid any ransom. Earlier, Toll said that it was working with the Australian Signals Directorate’s Australian Cyber Security Centre (ACSC) to identify the virus and how to respond. It has also been working with the Federal Police since the attack.

Toll received severe criticism over the time taken to investigate the incident and start restoring services back online. Toll is facing complaints from its customers and clients including Unilever, Adidas, Nike, Telstra, Optus, Footlocker, and Officeworks due to indefinite delays over deliveries.

“From the outset, we’ve prioritized customer-facing and other critical systems. We now have many of our customers back online and operating essentially as normal, including through large parts of our global cargo-forwarding network and across our logistics warehouse operations around the world. And, we’re progressively reactivating full services on the MyToll parcels booking and tracking portal,” a spokesperson from the Toll Group said in a media statement.

The statement also highlighted, “Core systems including email, phones and end-user devices have been tested, restored and are operating as normal. For all of that, we know that some of our customers continue to be affected. We’re working with them and we’re doing everything in our power to get them moving as a matter of priority and, importantly, when it’s safe to do so.”

How Mailto Ransomware Affected Toll Group

On January 31, 2020, post the attack discovery, Toll promptly shut down several systems across multiple sites and business units in Australia to stop the spread of ransomware. The incident resulted in Toll reverting to manual processes for clearing the backlog of undelivered local and international parcels across Australia. It continued to function its regular pickup, process and dispatch services, but at a slow pace due to manual processing.

Personal Information Belonging to 144,000 Canadians Breached

Canada Revenue Agency Shut Down Services after Cyberattacks

Several government departments in Canada have compromised the personal information of 144,000 individuals across 7,992 data breaches that occurred over the past two years, according to a report from the Canadian Broadcasting Corporation (CBC). The Canadian government stated that the information breached while answering to an order paper question filed by Conservative MP Dean Allison last month.

According to report findings, the Canada Revenue Agency (CRA) suffered a greater number of cyberattacks with 3,005 data breaches which affected 60,000 Canadians’ information. The CRA blamed the breaches on security issues, misdirected mail, and employee misconduct. Health Canada reported the second-highest number of data breaches with 122 breaches, affecting 23,894 individuals. The report also revealed that the Public Health Agency of Canada (PHAC) was responsible for seven breaches that affected 3,725 individuals.

Etienne Biram, CRA spokesperson, said, “We consider a single privacy breach to be one too many. Two-thirds of the total individuals affected were as a result of three unfortunate but isolated incidents.”

The other government entities that reported data breaches include the Public Services and Procurement, which experienced 164 breaches, with 5,149 affected; Employment and Social Development Canada suffered 1,421 breaches, affecting 3,586 individuals; Department of National Defence (DND) was responsible for 170 breaches, with 2,273 individuals affected; Immigration saw 3,005 breaches, affecting 4,268 individuals.

“As it stands, federal departments only have to alert affected individuals in the event of material breaches–cases involving sensitive personal information, which reasonably could be expected to cause serious injury or harm to an individual, or ones affecting large numbers of people,” CBC stated.

 Data Breaches Increased in Canada

 Earlier, the office of the Privacy Commissioner of Canada revealed that around 680 security breaches were reported in 2019, which is six times the volume received during the same period in 2018. It’s said that the number of Canadians affected by a data breach is more than 28 million, in which 58 percent of reported breaches involved unauthorized access.

The number of reported data breaches in Canada increased by six times after the country implemented a breach-reporting regulation. The new regulation, the Personal Information Protection and Electronic Documents Act (PIPEDA), went into effect on November 01, 2018. As per the regulation, Canadian companies are required to report all the details of data breaches that occurred within the organization. They also need to notify affected individuals and keep records of all data breaches.