Home Blog Page 180

4 in 10 Businesses in the U.K. Sacked Employees for Breaking Security Policy

data integrity, website, security

The global pandemic has turned the work-life-balance upside down. Concerns about job security and workplace policies grew exponentially in recent times. According to a survey from Centrify, a provider of Identity-Centric Privileged Access Management (PAM) solutions, nearly 39% of security leaders in the U.K. have admitted to sacking their workforce for breaching their company’s cybersecurity policy.

The survey also revealed that 65% of U.K.’s organizations made significant modifications to their cybersecurity policy in the wake of the COVID-19 outbreak and remote working conditions. Nearly 55% of businesses have a plan to officially prohibit employees from using personal devices when working remotely.

In addition, 58% of respondents agreed that employees are more likely to ignore security practices when working from home, owing to which, 57% of business leaders are currently implementing additional security measures to enhance employees’ remote security posture. Security measures include advanced authentication measures like biometric data checks, fingerprint, facial recognition technology, and multi-factor authentication procedures when accessing certain corporate accounts, applications, and files, which eventually help in mitigating the risk of phishing and identity theft attacks on employees.

Andy Heather, VP at Centrify, said, “With more people than ever working from home and left to their own devices, it’s inevitable that some will find security work arounds, such as using personal laptops and not changing passwords, in order to maximize productivity. It is also possible that the changes in security procedures are not being communicated well to employees, and many are practicing unsafe internet usage without even realizing.”

Heather added, “The reality is the weakest link in any organization continues to be the human element. Combatting this issue starts from the top. CIOs and business decision makers must implement strict and transparent, cloud enabled and identity-centric security solutions. This will allow companies to quickly and safely deploy scalable security privileged access management measures, which make it impossible for an employee to access company networks, applications and data, unless they are following correct procedures.”

Remote Work Threatens Businesses

A similar study from HiveIO revealed that nearly 85% of organizations anticipate a larger remote workforce will threaten operations because of new risks. “The IT departments are working at a deficit in their ability to support and maintain business continuity while optimizing IT support,” the report said. The study stated that several organizations are unable to introduce new security solutions designed to improve the efficiency of work-from-home employees. Around 70% of respondents admitted that they have suffered increased costs due to the ongoing pandemic. And 25% of respondents reported shrinking staff support, and another 18% fear additional staff reductions.
 

Binance and Ukraine Police Arrest Crypto Hackers in a “Bulletproof Exchanger Project”

Facebook Indicts Two Developers for Scraping Users’ Data, Europol

A collaboration between cryptocurrency exchange Binance and the law enforcement authorities in Ukraine helped identify a cybercriminal group that is involved in a $42 million money laundering scheme. Ukraine’s Cyber Police identified and arrested the hacker group in June 2020 for stealing millions of dollars in cryptocurrencies since 2018.

Earlier, Ukraine’s Cyber Police disclosed that the criminal gang was operating from Ukraine and engaged in several illicit activities globally. The hackers have been indicted for laundering crypto funds via 20 online cryptocurrency exchanges from 2018 to 2019. More than $200,000 worth of computer equipment, crypto assets, weapons, and cash were seized from the criminals.

“Officers of the Cyber Police Department, together with the Main Investigation Department, under the procedural guidance of the Office of the Attorney General, exposed the illegal activities of a group of people who organized online exchanges and provided illegal services. The defendants organized a criminal scheme to provide services for money laundering. Namely, money received from hacker attacks on international companies, distribution of malicious software, theft of funds from the bank accounts of foreign companies and individuals. In addition, they offered to exchange electronic money banned for circulation in Ukraine,” the Police said in a notice.

The Bulletproof Exchanger Project

The anti-fraud cyber operation was performed by Binance Sentry Security and Security Data Science analytics team, under its Bulletproof Exchanger project. “One of the Security Data Science team’s tasks is to identify transactions between Binance and high-risk entities, including what we refer to as Bulletproof Exchangers. These cryptocurrency platforms often serve as the cash-out points for cryptocurrency operations connected to financial crimes and other fraud. Similar to Bulletproof Hosting services, which are web hosting providers with more lenient rules regarding what can be hosted on their servers, Bulletproof Exchangers are well-known for their lenient know-your-customer (KYC) and anti-money laundering (AML) policies,” Binance said.

U.S. Disrupts Cyber-Enabled Terrorist Campaigns

Recently, the U.S. Department of Justice (DOJ) announced the seizure of three cyber-enabled terrorist financing campaigns, involving the al-Qassam Brigades, Hamas’s military wing, al-Qaeda, and the Islamic State of Iraq and the Levant (ISIS).  This is the U.S. government’s largest-ever disruption of cryptocurrency that was used for terrorist activities. According to the DOJ, the terrorist groups used multiple social media profiles and cryptocurrency accounts for their online presence to raise funds for their terrorist operations. The authorities detained over 300 cryptocurrency accounts, millions of dollars, four websites, and four Facebook pages related to the terrorist groups. 


Data Scraped from Instagram, TikTok and YouTube Exposes 235 Mn Social Media Profiles

blockchain-based social media, Parental Consent for Minors, Iranian Facebook accounts

Security researchers discovered a misconfigured database exposing over 235 million social media profiles online. According to the security researcher Bob Diachenko, who leads cybersecurity research team at Comparitech, the leaky database contained sensitive information that was taken from publicly viewable social media profiles on Instagram, YouTube, and TikTok.

Information Exposed

Diachenko found three identical copies of the scraped data from social media pages, which were hosted at three separate IPv6 addresses. The datasets include:

  • 96,714,241 records scraped from Instagram
  • 95,678,713 records scraped from Instagram
  • 42,129,799 records scraped from TikTok
  • 3,955,892 records scraped from YouTube

The records contain personal information like profile name, full real name, profile photo, account description, whether the profile belongs to a business or has advertisements. It also includes statistics about follower engagement, including number of followers, engagement rate, follower growth rate, audience gender, audience age, audience location, likes, last post timestamp, age, and gender.

The misconfigured database is said to have come from now-defunct company called Deep Social, however the database is presently owned by a company named Social Data. Social Data acknowledged the exposure but has denied any connection with Deep Social.

“Evidence suggests that much of the data originally came from a now-defunct company: Deep Social. The names of the Instagram datasets (accounts-deepsocial-90 and accounts-deepsocial-91) hint at the data’s origin. Based on this, Diachenko first contacted Deep Social using the email address listed on its website to disclose the exposure. The administrators of Deep Social forwarded the disclosure to Social Data. The CTO of Social Data acknowledged the exposure, and the servers hosting the data were taken down about three hours later,” Comparitech stated in its report.

Fate of the Exposed Data

Attackers could take advantage of the exposed data to launch credential stuffing attacks. “The information stored in this database is vulnerable to spam marketing and phishing campaigns. Users of Instagram and TikTok should be on the lookout for scams and phishing messages either sent directly or posted in comments. Even though the information is publicly available, the size and scope of an aggregated database makes it more vulnerable to mass attacks than it would be in isolation,” Comparitech added in its report.

While the unsecured database was discovered on August 1, 2020, the Comparitech researchers stated that they do not know how long the data was exposed before the disclosure, and it is unclear whether any unauthorized party accessed it or not.


The Emergence of the Zero Trust Concept in IT security

Cyber hygiene

Firewalls have been in use since the late 1980s to protect networks from external threats.  However, these traditional firewalls were only designed to segment the network into a few defined zones – the outside network where nothing is trusted, the inside network where everything is trusted, and perhaps one or more demilitarized zones (DMZs) for systems needing to communicate with the outside world and requiring a different set of rules to manage what traffic is allowed. These perimeter firewalls are like the walls of a castle but once an intruder is inside, they can run rampant and cause much destruction.

By Francis O’Haire, Group Technology Director, Data Solutions

More than 80% of network traffic in a data center is between internal systems – what is called “East-West” traffic.  This traffic generally does not get inspected by a firewall and poses a significant risk if an attacker gets through or bypasses perimeter security. There is nothing to stop the lateral movement from a compromised system or device to others. In today’s world where sensitive data and resources are spread across data centers, branches, clouds, and mobile devices, perimeter security is not enough.  There is no clearly defined perimeter anymore.

As things stand, there is no one security solution that is able to detect and counter every single threat. But what if you consider an entirely different way to approach security, one that prevents threats from exploiting a vulnerability? We are talking about controlling system access here. If you consider that threats and vulnerabilities are basically infinite, then you can think of system access as being finite, measurable, and provable. If you can control system access, then you have much more robust control over security. And this neatly introduces the concept of Zero Trust – the notion that restricting the access that threats have to your systems, involves implementing a Zero Trust environment.

The concept of Zero Trust security was first proposed in 2010 by Forrester Research and is an architecture whereby no system or user is trusted (whether inside or outside the corporate network) without being positively identified and authorized. To achieve true Zero Trust for traffic between all corporate systems, the use of traditional firewalls is not feasible as they are only designed to deal with a limited number of security zones or segments.  The concept of “micro-segmentation” is necessary and this can ultimately deliver visibility and control of network activity from, and to, every device. Micro-segmentation involves creating controlled segments of isolated workloads within a data center or cloud deployment which enables the network to become more granular. And by making network security more granular, you make it far more effective. Also, micro-segmentation provides a massive cost/benefit insofar as it enables security teams to deploy custom security policies inside a data center using network virtualization technology, rather than having to install multiple physical firewalls. That said, the use of network virtualization is not always necessary in every case.

There are different approaches to achieving micro-segmentation with some being more effective than others depending on the environment. Let’s examine each of these approaches in more detail:

1. Agent-based micro-segmentation:  As the name suggests, this uses an agent on each host or virtual machine to give very fine-grained visibility and control.  In effect, every host on the network or in the cloud can be inside its own protected bubble with its own firewall rules appropriate to its role within the infrastructure.  This approach is generally the easiest to deploy and manage and is hardware-independent being fully software-defined.

2. Hypervisor-based micro-segmentation: This achieves similar results but only for virtualized on-premise workloads. Under these conditions, all the workload traffic has to go through the hypervisor and network isolation and micro-segmentation can be done in the hypervisor itself. This approach leverages the functionality of the hypervisor’s virtual network components to provide visibility and micro-segment the workloads. It does not require an agent to be installed on each Virtual Machine (VM) and functionality typically depends on the hypervisor in use.

3. Network-based micro-segmentation: Network-based micro-segmentation is implemented using network devices as enforcement points. It relies on subnets, VLANs, or some other tagging technology to create segments. Essentially it relies on controlling network devices such as switches and firewalls to carve the network up into many segments. From there, policies are configured and enforced using IP constructs or ACLs. It is less granular than the other options but can be complimentary when needing to protect devices that cannot be virtualized or have an agent installed such as IoT devices, medical devices, or industrial control equipment.

While micro-segmentation is the foundation for achieving Zero Trust, it also involves other technologies such as strong identity management and authentication and a change in processes within the organization. But ultimately, Zero Trust is the way forward for security in this modern multi-cloud, multi-device, and highly dynamic modern IT infrastructure.

About the Author

Francis O’HaireFrancis O’Haire is the Group Technology Director at Data Solutions, a company renowned in the IT industry for bringing innovative new technologies to the U.K. and Irish markets. He has been with the company since its inception in 1991 and is responsible for Data Solutions’ product development including the identification and evaluation of new technologies. With over 25 years’ experience in the IT industry, including the virtualization, cloud, security, and data communications fields, O’Haire is a technology evangelist and thrives on finding solutions that address real market needs and deliver a return on investment, increased efficiency and lower cost to the end customer. He is a graduate of DIT Kevin Street and holds numerous vendor qualifications.
Disclaimer

CISO MAG did not evaluate/test the products mentioned in this article. The facts, opinions, and language in the article are entirely those expressed by the authors and do not reflect the views of CISO MAG.  


Only 3 in 10 Airlines are Protecting their Customers from Fraudulent Emails

93% of Global Airlines are Vulnerable to Email Fraud Risk: Report

An analysis from enterprise security firm Proofpoint highlighted that majority of airlines are exposing their customers to cyber risks, as cybercriminals are leveraging the global pandemic to deploy email frauds and phishing attacks. In a blogpost, Proofpoint revealed that 61% of airlines under the International Air Transport Association (IATA) do not have an active Domain-based Message Authentication, Reporting & Conformance (DMARC) record. IATA member airlines represent 82% of total air traffic.

Alarmingly, 93% of the global airlines have not implemented the recommended level of DMARC protection, known as Reject, which prevents dodgy emails from reaching users. And only 7% of airlines are proactively blocking fraudulent emails from reaching their customers’ inboxes.

What is DMARC?

DMARC is an email validation protocol intended to shield domain names from being exploited by threat actors. It authenticates the email sender before it reaches the receiver’s inbox. The protocol also verifies the domain of the sender as per the DKIM (Domain Keys Identified Mail) and SPF (Sender Policy Framework) standards to ensure the email is not spoofing the trusted domain.

“At a time when opportunistic cybercriminals may look to take advantage of such global uncertainty, the majority of international airlines are leaving their customers exposed to email fraud. making them potentially more susceptible to cybercriminals spoofing their identity and increasing the risk of email fraud targeting consumers,” Proofpoint said.

A Global Threat

Proofpoint stated that popular global airlines are failing to implement adequate email security measures, leaving themselves vulnerable to brand phishing and other fraud attacks. China and North Asia has the lowest level of DMARC adoption, with 85% having no published DMARC policy. This is followed by Asia Pacific (70%), Europe and Middle East & Africa (both regions at 57%) and the Americas (43%).

“When it comes to proactively protecting their customers against email fraud, China & North Asia fares the worst with 100% of its carriers not having the strictest DMARC policy in place (Reject). This is followed by Europe and the Middle East & Africa (both regions at 93%), and APAC and the Americas (both at 89%),” Proofpoint said.

“It is critically important that the communication methods used by airlines and every other industry is secure. We recommend implementing robust email defences and inbound threat blocking capabilities, including deploying DMARC email authentication protocols,” Proofpoint added.

Cyberattacks on Airlines

Keeping the growing cyberattacks on the Aviation industry in mind, ResearchAndMarkets.com released a report titled “Aviation Cybersecurity Market – Growth, Trends, and Forecast (2019 – 2024).” According to the report, the aviation cybersecurity market is expected to register a CAGR of around 11% during the forecast period of 2019-2024.

The industry relies heavily on IT infrastructure for its ground and flight operations. The security of these airline systems directly impacts the operational safety and efficiency of the industry, and indirectly impacts the service, reputation, and financial health. The report discusses cybersecurity in the aviation sector by solution and application spanning from airline management, air cargo management, air traffic control management, and airport management.


Cybercriminals are Becoming Creative with Canva

cybercriminal, music

Canva, an Australian online graphic designing platform, is a victim of a cyberattack after hackers compromised the platform to design and store malicious files into official-looking documents, which can be deployed in phishing emails to pilfer sensitive data. Canva lets users create graphical images, presentations, infographics, and other visual content on both web and mobile platforms.

Security firm KnowBe4, in its report said that several phishing emails were regularly reported using Canva to spread credentials phishes on users via a number of social engineering schemes.

The Canva-Based Phishing Attack:

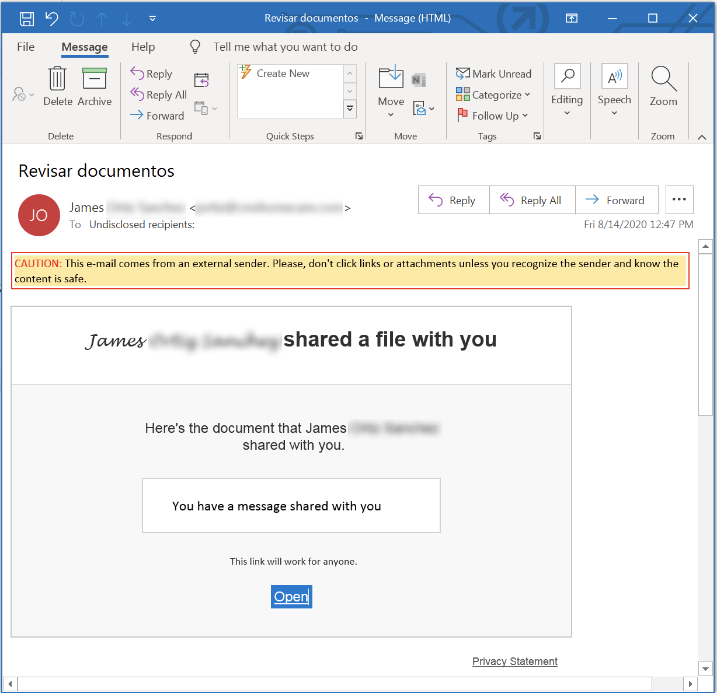
1. After creating a malicious document/file on Canva, the threat actors send an email to the targeted user with a link to this malicious file.

Image source: KnowBe4

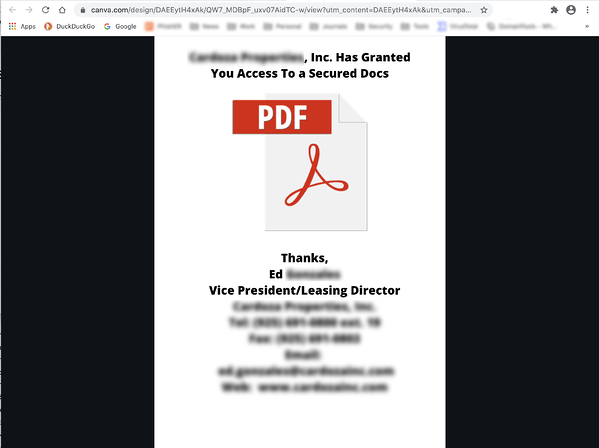
2. The dodgy email claims to be from a legitimate source and prompts the user to click on the link saying that it redirects to an important file.

Image source: KnowBe4

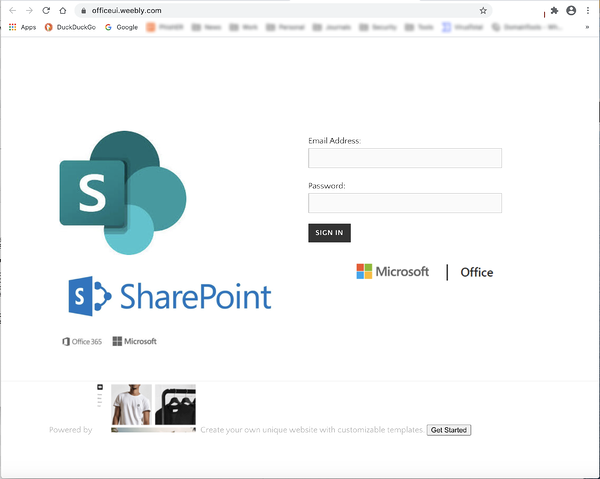
3. If the user clicks on the first link, it again prompts the user to click on another link to view the file in the email, but it actually redirects to a phony login page. The user is then asked to enter the login credentials, which can result into an account takeover by hackers.

Image source: KnowBe4

“The odd appearance of this document ought to alert users that something is amiss. If nothing else, this clearly is not anything hosted on Sharepoint. Users who elect to plow on in an attempt to access the Secure Document are shuffled off to a poorly spoofed Sharepoint login page hosted on Weebly,” the report stated.

“While spoofs of Microsoft and Docusign are common enough in Canva-based phishing attacks, the malicious emails sporting Canva links that we most frequently encounter are fake voice mail notifications — a genre that has been on the rise over the past few months. Strangely, the initial email in this particular attack immediately requires users to open yet another attached email,” the report said.

The report added, “The vast majority of these malicious emails lead to credentials phishes, some more credibly presented than others. Canva is being used to create and host files that are employed for some of the most common social engineering schemes that we see on a daily basis.”

Not the First Time

Earlier, Canva suffered a cyberattack in which hackers penetrated into its systems and stole data of nearly 140 million users. The company stated in a release that the usernames and email addresses of customers were accessed. On the bright side, the passwords remain encrypted, thereby being unreadable to external parties. A majority of Canva users use Google and Facebook accounts for social logins. According to the firm, even these credentials remain unreadable as they were encrypted like the former. Amid this, Canva has also been criticized by cybersecurity experts for the way it handled the attack and notified the customers.


IE Browser Will Not be Secure Post November 2020

Brand Phishing Attacks

Yes, it is official! Microsoft is getting ready to pull the plug on Internet Explorer 11 (IE 11) browser in a phased manner beginning November 30, 2020. In an announcement, it stated that the legacy Microsoft Edge browser and remaining Microsoft 365 apps and services will stop supporting IE 11 completely from March 9, 2021, and August 17, 2021, respectively. After the listed dates, new security updates for the IE 11 and legacy Edge browsers will not be available.

 Key Highlights 

  • Microsoft to phase out Internet Explorer 11 (IE 11) and the legacy Edge browsers.
  • It will not provide any security updates to the IE 11 browser from November 2020.
  • The new seven-month-old Chromium-based Microsoft Edge browser will replace the two.
  • The migration will not affect other IE11 legacy apps and they will continue to function properly on Microsoft Edge, which will have backward compatibility.

Why a Phased End of Support?

Microsoft critically answered this question by saying, “Customers have made business-critical investments in IE 11 legacy apps and we respect that those apps are still functioning. Our customers’ own legacy IE 11 apps and their investments need to continue to work.” However, speed, security, privacy, ease of use, manageability, and productivity are certain issues that IE has been facing since its IE 6 version. To address these issues and give ample time to its customers for the migration of their IE and Legacy Edge apps to the open-source Chromium-based Edge, Microsoft believes that a phased pull-out is the correct approach.

How IE Lost its Sheen

In a world that was changing in the blink of an eye, IE only had 11 versions released in its lifecycle of nearly 25 years. In contrast, the biggest competitor of IE, Google Chrome browser, released 80+ versions in just 12 years since its launch in 2008. Chrome received updates every six to eight weeks whereas IE received new features only with new major releases, which were separated by as many as five years (IE5 to IE6) and as few as one (IE10 to IE11). Thus, owing to the popularity scales tilting towards Chrome and other browsers like Firefox and Safari, Microsoft called it quits on IE with version 11, the one included with Windows 10.

Since the Windows 10 release in 2015, IE continued receiving security updates, but no new features have been added to it. Looking at the declining number of users, Microsoft instead diverted its attention to developing the Legacy Edge browser.

With native integration in Microsoft management, security, and productivity tools, we recommend the new Microsoft Edge to address our customers’ compatibility and secure remote work needs.

– Microsoft

It is now comfortable and confident about the security and privacy aspects of Edge and is all set to embrace it with open arms. Microsoft said, “The new Microsoft Edge is our best expression of a modern browser. It is a browser built on the Chromium open-source engine with the latest in Microsoft enterprise capabilities. Since its release in January, millions of users have upgraded their home and work browsers to the new Microsoft Edge. Additionally, new devices and future Windows feature updates (starting with Windows 10, version 20H2) will contain the new Microsoft Edge.”

“With native integration in Microsoft management, security, and productivity tools, we recommend the new Microsoft Edge to address our customers’ compatibility and secure remote work needs. Microsoft Edge has SmartScreen built-in and has the highest-rated phishing and malware protection as measured by two independent studies. We will also support our customers’ transition to the new Microsoft Edge with app and site compatibility assistance. As part of the App Assure promise, we have Microsoft engineers ready to help customers in case they run into compatibility issues,” Microsoft concluded.

Publicly Reported Data Breaches Stand at its Lowest Point in 5 Years

data breach

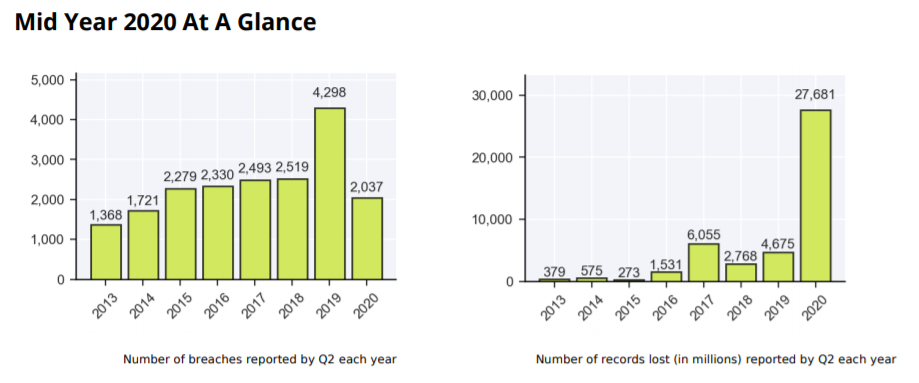
A research from Risk Based Security highlighted that the number of publicly reported data breaches  declined in the last five years, while the number of records exposed increased four-times more than any previously reported incident in the first six months of 2020. The “2020 Mid-Year Data Breach QuickView Report” revealed that around 2,037 data breaches were publicly reported till June 30, 2020, accounting for a 52% decrease compared to the first six months of 2019, and 19% below the same time period for 2018.

According to the research, the main cause of data breaches in the first half of 2020 were misconfigured databases and services. Around 27 billion records were exposed between January 1 and June 30, 2020, which exceeds the total number of records exposed during all of 2019 by more than 12 billion records.

Image Source: Risk Based Security

Inga Goddijn, Executive Vice President at Risk Based Security, said, “The striking differences between 2020 and prior years brings up many questions. Why is the breach count low compared to prior years? What is driving the growth in the number of records exposed? Perhaps most importantly, is this a permanent change in the data breach landscape?”

Who Was Breached?

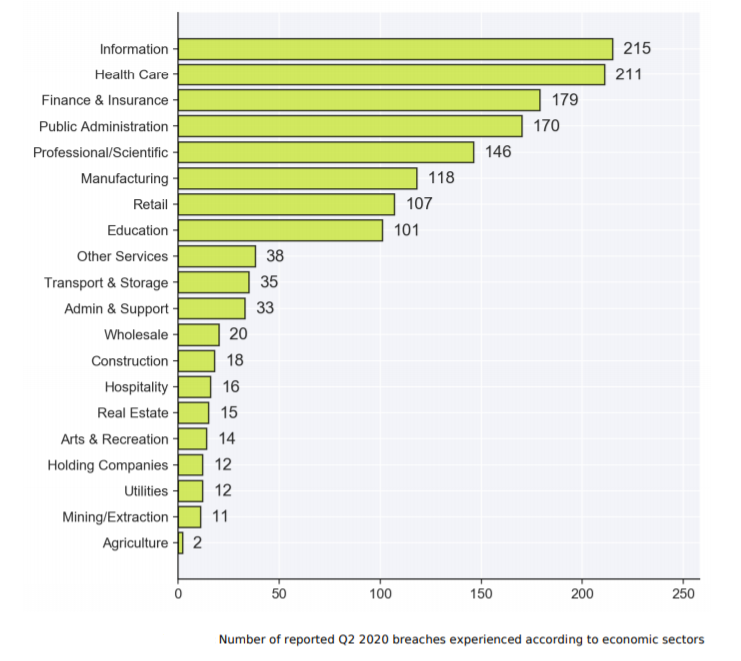
The research stated that the information technology and health care sectors reported the most number of breaches in the first three months of 2020. “In the first three months of the year Health Care services was the leader with 106 reported breaches with the Information sector in second place with 104 reported breaches. The difference between these two sectors is how the breach experience is divided among the sub-groupings that make up these sectors. In Health Care, breach activity is evenly distributed between hospitals, practitioners, and other facility or support service providers. In the Information sector, approximately 85% of the breaches originate from software publishers (which includes Software-as-a-Service) and other web-based services,” the report said.

Image Source: Risk Based Security

Key Highlights

  • The number of payment card details exposed in the first six months of 2020 surpassed 90 million records. Despite this, there were even more Social Security / national identity numbers, financial account numbers, and dates of birth exposed during this period.
  • Four economic sectors (Information, Health Care, Finance & Insurance, and Public Administration) accounted for more than half (52.5%) of reported breaches.
  • The information sector accounted for 14.5% of reported breaches, with software providers, hosting, and other online services accounting for 86.5% of the information sector breaches.
  • The health care sector nearly matched the information sector, accounting for 14.3% of the reported breaches.


Who’s Responsible for a Safer Cloud?

Cloud Security, 80% of Organizations Suffered a Cloud Data Breach in the Past 18 Months

With today’s explosion of remote workers, we’re seeing an overwhelming reliance on the cloud. Its agility, anywhere access, and dynamic scalability make the cloud ideal for this new working paradigm. But what about cloud security? Whose responsibility is it anyway?

By Phil Alberta, President and Chief Information Officer, IPM

With so much reliance on multiple cloud providers and solutions, from diverse locations and sources, protecting and securing the cloud has gotten much more complex, and in some cases even misunderstood. This leaves risky gaps and exposure. Yes, cloud providers including Microsoft Azure and AWS handle infrastructure security – including compute, storage, database, and networks. But it’s vital to understand that once your data arrives in the cloud, its full security fate rests in your own hands.

Embracing a Shared Responsibility Model

There is a duality to cloud security that requires deep understanding and strategic management in a practice that can be called a shared responsibility model. Here, the cloud provider is responsible for the secure infrastructure of the cloud. The customer on the other hand takes primary responsibility for protecting data in the cloud including user data, platforms, applications, identity access management, as well as the operating system, firewall configuration, and other components.

It’s important to note that this shared responsibility for security doesn’t fall into place automatically. It takes careful planning, precise implementation, and continuous monitoring to perfect. To build your secure cloud environment, consider the following five best practices:

1. Develop a comprehensive plan: Take another look at your cloud provider(s) agreement and identify where they can help you to improve security, and where you may need to add technology and solutions to your overall strategy. In the shared responsibility model, you need to know where the cloud provider’s agreed-upon responsibility ends and yours begins. Then you can better integrate your provider’s security controls into your overall security strategy.

Using this greater detail from your cloud provider, you can develop a plan to include:

  • An assessment of new assets that need to be budgeted for. i.e., threat detection and response software, automated patching updates, swapping out high-risk legacy hardware for more secure devices.
  • Forecasting of your organization’s potential workforce shift to determine the longer-term effects and needs of remote working and related devices.
  • Alignment between IT, security, and HR on a timetable to execute security improvements. This may entail giving employees new devices, training on new software and security protocols, and budgeting priorities.

2. Understand your compliance requirements: Reassess your compliance needs and then identify and use the tools your cloud provider makes available to help you monitor and prove compliance. Azure Policy is one tool offered to centralize compliance data for quicker auditing and tracking. It enables policy creation at the core of Azure and supports ongoing enforcement by setting guardrails on resources.

3. Know your risk tolerance: Fully understand what data you need to secure and what risks you are willing to accept for that data. Map out your data risk tolerance by data type and the strategy you will implement to protect it. By classifying your data based on its sensitivity such as personally identifiable information (PII) or HIPAA regulated health records, you’ll have a strong idea of which data sets you need to best protect.

4. Design and implement technology controls: Organizations can use managed services and solution providers to help design and execute a cloud security plan and help navigate the complexities of cloud data security protocols. This plan can include application and access controls needed to further ensure sensitive cloud data is not compromised and can be recovered. Given the expected increase in remote users, it is imperative to limit access to applications in accordance with work productivity needs. Phishing attacks and malware introduction into networks are a common result of inadequate control at the device endpoint.

5. Develop a continuous monitoring program: Security threats and risks function in a fluid environment. This demands regular assessment of the controls in place and the agility to adapt as situations change. It includes evaluation of your threat response system, secure onboarding and offboarding of employees’ devices, timeliness of all patching updates, and due diligence in making use of updated security controls across all major programs.

The responsibility for a secure cloud is a shared one. And as organizations continue to rely more heavily on cloud-powered workloads, your security strategy must be a priority that remains front and center. By inspiring collaboration and consensus between your cloud providers, solutions providers, and internal IT security staff, you’ll enable a more productive and secure environment in which workers will thrive.

About the Author

phil albertaPhil Alberta is President and Chief Information Officer for IPM, an IT consulting firm focused on supporting secure cloud transformations with field-proven expertise in planning, deploying, and supporting today’s hybrid IT infrastructure.
 

Disclaimer 

Views expressed in this article are personal. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.

Need for Automation! 93% of Firms Believe Human Error Causes Cloud Data Threats

93% of Organizations Believe Human Error Cause Cloud Data Breaches

A survey from Tripwire, a provider of security and compliance solutions, revealed that several organizations face shortcomings in securing their cloud environments. In its “Implementing Cloud Security Best Practices” report, Tripwire revealed that the majority of security professionals (76%) have difficulties in maintaining security configurations in the cloud. Nearly 37% of respondents said their risk management capabilities in the cloud are worse compared with other parts of the security landscape.

Almost 93% are concerned about human error causing accidental exposure of their cloud data. Despite concerns about human errors, 22% of organizations still assess their cloud security posture manually. The report stated, “Attackers are known to run automated searches to find sensitive data exposed in the cloud, making it critical for organizations to monitor their cloud security posture on a recurring basis and fix issues immediately.”

Other Notable Findings from the Survey include:

  • Only 21% of organizations assess their overall cloud security posture in real time or near real time. While 21% said they conduct weekly evaluations, 58% do so only monthly or less frequently.
  • While 91% of organizations have implemented some level of automated enforcement in the cloud, 92% still want to increase their level of automated enforcement.
  • Only 51% of organizations have automated solutions that ensure proper encryption settings are enabled for databases or storage buckets.
  • 45% of organizations automatically assess new cloud assets as they are added to the environment.
  • A slim majority (51%) have automated alerts with context for suspicious behavior.

Tim Erlin, Vice President of product management and strategy at Tripwire, said, “Security teams are dealing with much more complex environments, and it can be extremely difficult to stay on top of the growing cloud footprint without having the right strategy and resources in place. There are well-established frameworks which provide prioritized recommendations for securing the cloud. However, the ongoing work of maintaining proper security controls often goes undone or puts too much strain on resources, leading to human error.”

The survey findings are based on the responses from 310 security professionals surveyed on the implementation of cloud security best practices.

Cloud Security Risks on Rise

A similar survey, “State of Cloud Security,” conducted by Fugue revealed that IT and cloud security professionals are concerned about the security of their cloud environments as several organizations working remotely. The survey found that 96% of cloud engineering teams are at present 100% working from home, while 83% of them completed the transition or are still in the process. Around 84% (who are making the shift) are concerned about security vulnerabilities created during the swift adoption of new access policies, networks, and devices used for managing cloud infrastructure remotely.