Home Blog Page 160

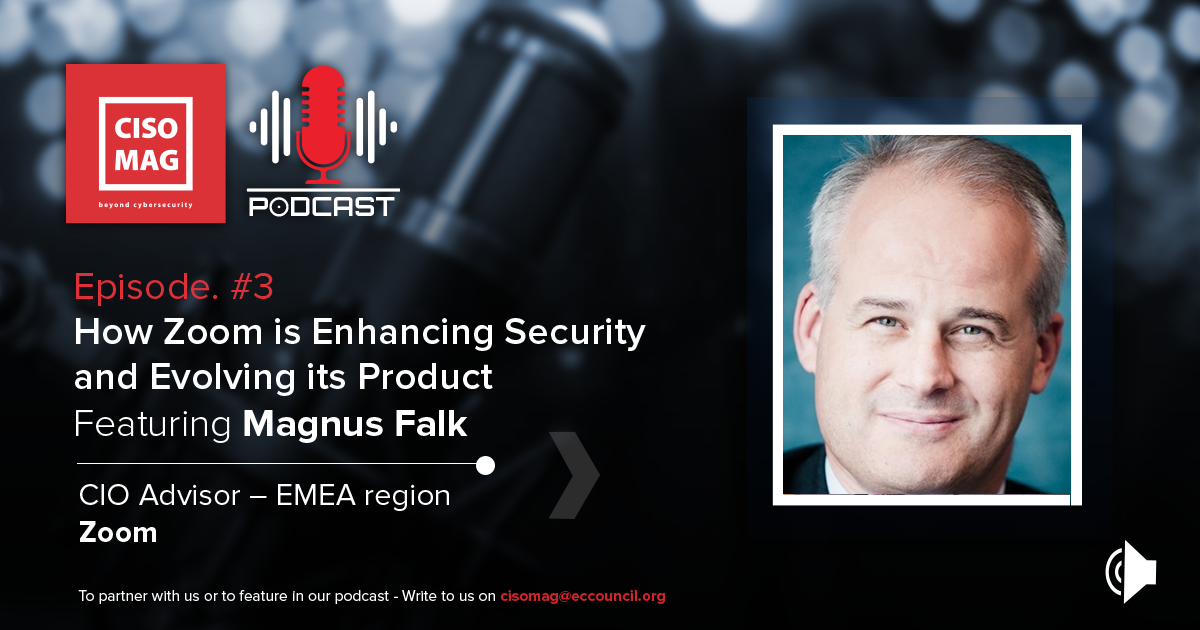
Episode #3: How Zoom is Enhancing Security and Evolving its Product

Zoom security

Zoom has now become an integral part of our lives in isolation — for our work, education, or just to meet up with friends and have “Zoom parties.” The pandemic was a blessing in disguise for Zoom and it saw 30X growth in a short span of a few months; before the pandemic, it had 10 million daily meeting participants but by the end of April that number shot up to 300 million. And these are official figures from Zoom.

While those in the corporate world were familiar with the use of Zoom, new users faced “video shock” and were not familiar with concepts like waiting rooms, virtual backgrounds, gallery/speaker views, meeting links, meeting IDs, and passcodes. But today it’s a different story, and we all are more confident in using this tool.

However, Zoom faced a setback earlier this year when its security was compromised leading to “Zoom bombing” attacks.

Thankfully, Zoom worked hard on its 90-day plan to fix those security issues and set up a CISO Council and Advisory Board. It now collaborates with CISOs, governments, and security agencies and experts across the industry to ensure that it is implementing security and privacy best practices. Zoom has also recruited hard-core security experts like Alex Stamos, who joined as an external advisor.

Listening time: 31 mins. 34 sec.

In this episode, Magnus Falk, Zoom’s CIO Advisor – EMEA region updates Brian Pereira, Principal Editor, CISO MAG about Zoom’s new security features like end-to-end encryption. He also talks about the accelerated growth and popularity of Zoom, and how the video platform is evolving.

With over 30 years in the industry, Falk brings a wealth of experience to the table and is an esteemed digital and technology leader.

His diverse experience includes a 16-year stint at Credit Suisse where one of his roles was CIO in EMEA, seven years in Accenture as well as holding the position of Deputy Chief Technology Officer for HM Government.

He has a Bachelor’s Degree in Mining Engineering from Imperial College London and was also a Captain in the British Army for nearly four years.


Listen to our previous podcast episodes here. 

Threat to Privacy! Corporate Credentials on Darknet Surge by 429%

BLAZINGSUN: A New Breach on Joker’s Stash Dark Web

Security operations provider Arctic Wolf observed a year-over-year decrease in publicly disclosed data breaches. However, in its “2020 Security Operations Report” Arctic Wolf revealed that the number of corporate credentials with plaintext passwords on the darknet market increased by 429% since March 2020.

According to the report, 17 sets of corporate credentials are available on the dark web that could be exploited by cybercriminals to easily execute account takeover (ATO) attacks by obtaining access to one single corporate account. Hackers can also monitor an organization’s corporate network and gain access to sensitive data, intellectual property, competitive information, or funds.

The report also highlighted that most of the high-risk cyberattacks (35%) occurred between the hours of 8:00 PM and 8:00 AM, and 14% occur on weekends, when most internal security teams go offline. “The sharp increase in corporate credential leaks underscores the need for organizations to have dedicated 24×7 monitoring of their network, endpoint, and cloud environments in order to prevent targeted attacks that could happen at any time,” the report stated.

Key Findings:

  • Phishing and ransomware attempts increased by 64%. Hackers have created new phishing lures around COVID-19 topics and adapted traditional lures seeking to take advantage of remote workers.
  • Critical vulnerability patch time has increased by 40 days. A combination of higher common vulnerabilities and exposures (CVE) volumes, more critical CVEs, and the emergence of a remote workforce have significantly slowed the patching programs at many organizations.
  • Unsecured Wi-Fi usage is up by over 240%. Remote workforces connecting to open and unsecured Wi-Fi networks outside of their office or home are now facing increased risks of malware exposure, credential theft, and browser session hijacking.

Mark Manglicmot, Vice-President, Security Services, Arctic Wolf, said, “The cybersecurity industry has an effectiveness problem. Every year new technologies, vendors, and solutions emerge. Yet, despite this constant innovation, we continue to see breaches in the headlines. The only way to eliminate cybersecurity challenges like ransomware, account takeover attacks, and cloud misconfigurations is by embracing security operations capabilities that fully integrate people, processes, and technology.”

“BAHAMUT” Swims into Legitimate Accounts to Spread Disinformation

BazaCall BazaLoader

Security experts from BlackBerry uncovered the cyber espionage group dubbed “BAHAMUT” targeting several government officials and major industries via various disinformation campaigns. In its research “BAHAMUT: Hack-for-Hire Masters of Phishing, Fake News, and Fake Apps,” BlackBerry found that the BAHAMUT group uses various attack vectors ranging from fake news campaigns, fraudulent social media personalities, to the development of entire news websites built to include disinformation.

BlackBerry’s research and intelligence team stated that the BAHAMUT group primarily targets human rights groups, influencers, high ranked government officials, and businesses in India, the Emirates, and Saudi Arabia.

Key Findings:

  • BAHAMUT actors use original, carefully crafted websites, applications, and personas to spread fake content focused on geopolitics, research, industry news about other hack-for-hire groups.
  • Nine malicious iOS applications in the Apple App Store are said to be linked to the BAHAMUT group.
  • Use of phishing and credential harvesting is aimed at very precise targets; concerted and robust reconnaissance operations are conducted on targets before the attack.
  • Clustered targeting in South Asia and the Middle East lends credence to a “hacker for hire” operation.
  • A range of tools, tactics and targets suggests the group is well-funded, well-resourced, and well-versed in security research.

Eric Milam, VP, Research Operations at BlackBerry, said, “The sophistication and sheer scope of malicious activity that our team was able to link to BAHAMUT is staggering. Not only is the group responsible for a variety of unsolved cases that have plagued researchers for years, but we also discovered that BAHAMUT is behind a number of extremely targeted and elaborate phishing and credential harvesting campaigns, hundreds of new Windows malware samples, use of zero-day exploits, anti-forensic/AV evasion tactics, and more.”

“This is an unusual group in that their operational security is well above average, making them hard to pin down. They rely on malware as a last resort, are highly adept at phishing, tend to aim for mobile phones of specific individuals as a way into an organization, show an exceptional attention to detail and above all are patient – they have been known to watch their targets and wait for a year or more in some cases,” Milam added.

Is Security a Blind Spot for Remote Employees?

Remote Work

A survey from cybersecurity firm NetMotion found that the majority of the remote workforce does not report system issues to their IT support team.  The survey findings, based on the responses from 500 IT professionals and 500 remote workers in the U.S. and the U.K., revealed that over 50% of workers admitted that they are not sharing their IT or security issues with their IT team.

While 66% of remote workers reported having faced an IT issue during the lockdown, 57.5% did not share their issues with their organization or IT team.

The survey also highlighted that most employees choose to resolve the issues themselves or choose to suffer in silence, with 25% of workers reporting that their IT department does not value their feedback. While the reason for why employees are doing this is unknown, the survey claims that some employees resolve issues by themselves.

Employees Using Shadow IT

As many remote workers prefer to not report issues to IT teams, the survey suspected that employees have adopted Shadow IT. According to the survey, nearly 62% of remote workers are using rogue applications, with 25% using a significant number of unapproved tools outside of the official IT policy. Only 38% of employees stick to their organization’s list of sanctioned IT software.

The most unsanctioned tools used by remote workers include productivity apps (38%) like Google Docs and Doodle, followed by communications software (32%) like WhatsApp and Zoom.

“It is clear that IT’s lack of complete visibility into the activity of millions of workers, their inability to diagnose all root causes and negative perception among some employee – due in part to unsatisfactory remediator of problems – is a huge part of the burgeoning IT-employee divide. The question thus becomes how to alleviate such constraints when knowing that remote work may be temporary for some but will remain permanent for so many others,” the report stated.

Also Read: CISOs Ignore Security Over Remote Working

Listen to the CISO MAG podcasts to catch the advice and best practices from security leaders.

Don’t Just be a Good CISO, Be a Successful CISO!

Global CISO Forum 2020, Becoming a successful CISO

Up until now, cybersecurity was often an afterthought for several organizations due to lack of mitigation measures. However, COVID-19 is accelerating digital transformation in decentralized locations. The state of security is getting better at building business resiliency, thanks to the evolving role of a CISO. CISOs are the assets and business enablers that give organizations a direction towards a safer and secured work environment. But a CISO’s role is critical in today’s fast-growing digital world. Just being a good CISO is not enough, you need a successful CISO. Why? Because an organization’s success invariably depends on a CISO’s success. So, how do you become a successful CISO? It is a phased process. Let us find out the good, the bad, and the ugly roadmap to success of a CISO from a veteran  CISO, Heath Renfrow

By Mihir Bagwe, Tech Writer, CISO MAG

Speaking at the EC-Council’s Global CISO Forum, Heath Renfrow said, “For too long people have feared us (CISOs) and stayed away from us. We are exactly the opposite of that. We are business enablers! We are there to educate people, tell businesses what their security risks are, and give them advice of how to up their defenses.” Renfrow added, “The success and reputation of an organization largely depends on the security of its employees, systems, and customers. And CIOs/CISOs of that organization have the responsibility of steering this ship.”

Related Story:

“AI has done a good job in securing the dynamic workforce” – Global CISO Forum 2020


Renfrow highlighted the fact that the position of a CISO is like the guy behind the curtains.  They are omnipresent and critical to the entire theatrical of running the business. And just like that guy who does his work in a mechanical manner, taking into consideration all the pros and cons associated with it, Renfrow says that there are five phases that every CISO needs to follow —  to not just be a good CISO, but a successful one.

The Five Phases to Become a Successful CISO

These phases and their respective timeframe differ from one organization to another. However, Renfrow notes that in the two decades of his working career in security, he’s followed this model and has had success across all the organizations he’s served.

1. Phase One: Company Meet and Greet

Global CISO Forum 2020, Becoming a successful CISO

Renfrow has been working in this field remotely for six years now because of the global supply chains of his associations. When you have a global network of employees, vendors, third-party suppliers, and customers, it becomes even more difficult to mark the starting point of this phase. However, this needs to be done and is essential. It is important to know your team and the business leaders, and understand your job profile, which includes definition and maintenance of physical and IT security, privacy and risk management, compliance, and disaster recovery.

Renfrow says, “Now in the COVID age, it is even more difficult to connect with the stretched resources of not just other teams but your own teams as well. We cannot meet them face to face, but we need to connect. Connect via Zoom, Teams, Slack, or any other tool with every important member possible and know what they expect, want, and whether they are happy with their roles. Build a relationship with your team and peers. This will go a long way.”

Renfrow specifically mentioned the need to find a “Cyber Champion.” Identify this person as quickly as possible. This person may not be wearing a cape, but he can be a CISO’s go-to guy who has the answer to all the network and security related queries.

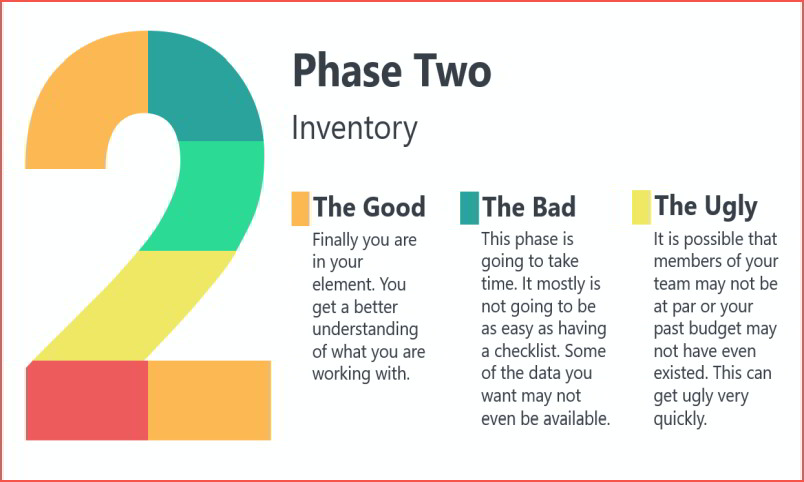
2. Phase Two: Inventory

Global CISO Forum 2020, Becoming a successful CISO

Renfrow quotes, “This could be an extremely time-consuming phase.” Why? Because of the number of people involved in this phase. A carpenter does not straightaway start making a bookshelf or that bunk bed for your kids. He first measures the dimensions of the room; he then decides upon the design taking into consideration his customer’s requirements; prepares a rough inventory of how much ply, varnish, nails and adhesives he requires, then goes and buys it from a third-party vendor, and finally starts preparing the shelf or the bed. If this so-called small piece of work requires so many stakeholders in between, then imagine how many does a CISO needs to interact with for preparing his inventory.

This process, like Renfrow explained, should include the following:

  • Skill sets of people involved (and required)
  • Audits and reports
  • Number of third-party and customer contracts
  • Budget – Past/present, IT and financial
  • Current processes
  • Current security strategies and posture
  • Network and security architectures in place
  • Regulatory and compliance requirements

3. Phase Three: Assessment

Global CISO Forum 2020, Becoming a successful CISO

It’s now time to prepare your to-do list. This is the phase where you sit back and assess your findings from the inventory phase and measure your organization’s security posture. Prepare a list of pros and cons of the various systems, processes, and strategies in place. Now understand the requirements of your business and its shortcomings.

Renfrow says that he has seen organizations having a lot of security tools but also found a shortage of skilled people manning these tools. In some cases, he also observed that certain security tools were implemented for specific tasks but 80% of  those tasks were being carried out by some other tool or manually by a person. Thus, there is a need to sit back, assess the ground reality against the actual requirements based on the findings of the first two phases, and then prepare a to-do list or the action plan to move forward.

Considerations for this stage include:

  • Review of technical requirements
  • Reviewing performance metrics
  • Assessment through a specialized third-party assessor
  • Review of vulnerability and penetration testing reports

4. Phase Four: Planning or Building a New Vision

Global CISO Forum 2020, Becoming a successful CISO

This is where you put your challenges into vision, says Renfrow. Understanding challenges like poor support, security governance, or compliance and audit gaps is very important. You may have support from the business team but maybe not from your executives or vice versa. You might have spent a lot of time in the first two phases by communicating, educating, and convincing your peers, but this can hamper your operations and can be a huge challenge to overcome.

At the same time, this is the phase where you must cross another impediment that CISOs face – the Budget. Based on the assessment done in the previous phase, it is quite clear what you need for taking your organization’s security game to the next level. So, start deducing a budget which can be presented to the business leaders in the next phase. Renfrow also suggested keeping this as a variable budget. Based on the risk decisions taken by the business leadership, the budget may swell.

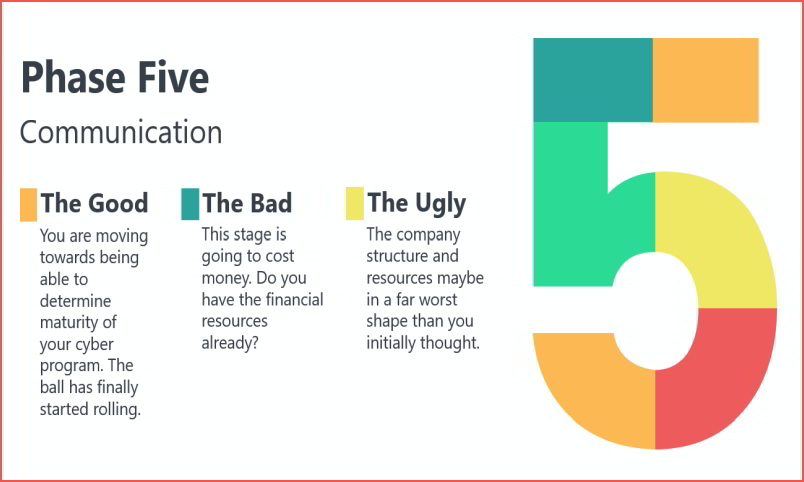
5. Phase Five: Communication

Global CISO Forum 2020, Becoming a successful CISO

Time to roll out that carpet, sit across the table, check those microphones, and talk! We have already built the vision in the last phase as to where our organization’s security posture needs to be against where it currently is. Now sit across the table to educate and make the business leaders understand what you have analyzed and what is the way forward on the security front.

According to Renfrow, another key element of this conversation is presenting business leadership with quantifiable risk analysis. The top suite better understands the language of numbers and statistics than just being presented with grey zones. Some methodologies like the Factor Analysis of Information Risk (FAIR) can come handy in doing so. It helps in establishing accurate probabilities of the frequency and magnitude of the risks.

And finally, it is time to discuss the Budget! Renfrow says, “You have laid the vision, shown the gaps, quantified the risks, and gotten the risk tolerance sorted for those risks. Just one thing remains, adjust your budget vision, take approval, and get out of that room!” Yes, it will be a difficult conversation, and you will be bombarded with tough questions and choices but remember the title of this phase – Communicate. You need to convey and convince your case. After all, the tag of being a successful CISO is a hard-earned one and lies just at the other end of this conversation.

6. About Global CISO Forum

Global CISO Forum

Global CISO Forum is an annual event that sees a confluence of the highest-level executives from across industries and countries who discuss the most pressing issues in information security. Now in its tenth year, the 2020 Global CISO Forum promises to be the best yet with an exciting mix of industries, formats, and interactive presentations.

In celebration of our 10 years of CISO events, EC-Council is giving its brand-new Risk Management Approach and Practices e-book to all attendees of the Global CISO Forum! Risk is at the heart of what a CISO does and EC-Council wants to create as many risk-smart executives to protect the world’s assets as possible.

EC-Council’s Global CISO Forum 2020 Virtual Conference was an invite-only, closed-door event gathering.

CISO MAG is the Content Editorial Sponsor for the Global CISO Forum.


U.K. Businesses Suffered a Cyberattack Every 45 Sec. During Lockdown!

cyberattacks on U.K. organizations

A research from business ISP provider Beaming revealed that the number of businesses in the U.K. that are affected by cyberattacks has increased after the country went into lockdown. The organizations suffered over 177,000 targeted attacks between April and June 2020, which means one cyberattack every 45 seconds.

While the volume of attacks increased by 13% in the first quarter of the year, the research revealed that cybercriminals used 3,41,000 unique IP addresses to attack businesses in the second quarter of 2020. It is found that 37,000 of these addresses were traced back to different locations in China, 32,000 in Taiwan, and 17,000 in the U.S.

The research also highlighted the volume of cyberattacks targeting file-sharing applications surged by 27%, accounting to 5,900 attacks per company. In addition, IoT applications like building control systems and networked security cameras remained the most common targets for threat actors, accounting to more than 14,000 online attacks per company.

Sonia Blizzard, Managing Director of Beaming, said, “We’ve all relied more on the internet to work, shop and communicate in the past few months, and our analysis shows that due to this change in circumstances this environment hasn’t just become busier – it’s required us to better protect ourselves too.”

“Businesses of all sizes need to take action today to improve their resilience to cyberattacks and keep their employees and data as secure as possible. Leaders must think beyond the basic protection most have today and boost business resilience with more sophisticated defenses that incorporate technology, training, and robust security policies,” Blizzard added.

U.K. Organizations Lost $108 Bn to Attacks

Earlier, Beaming claimed that the number of businesses in the U.K. affected by cyberattacks has doubled since 2015. The five-year cybersecurity research stated that 1.5 million businesses (25%) in the U.K. suffered cyberthreats in 2019, compared to 7,55,000 businesses (13%) in 2015, costing them £87 billion (US$ 108 billion). The research also highlighted that large-scale businesses were the most affected, with 9 in 10 companies (87%) reporting cyberattacks. Small and Medium Businesses (SMBs) have seen the steepest rise in attacks, compared to 28% of firms hit in 2015, to 62% in 2019.

Market Trends Report on Data Security – 2020

Data Security Report

Organizations around the globe are investing heavily in the cybersecurity quotient of its IT infrastructure to protect their critical assets. Arguably, with the unprecedented shift towards digitization and cloud technologies, data in any form is now considered “the new oil.” A 2019 Netflix documentary, “The Great Hack,” declares that personal data has surpassed oil as the world’s most valuable asset. It warned viewers that companies and governments are hacking more than computers, “it’s our minds that they are into.” CISO MAG editors wanted to probe deeper and offer its readers perspectives on the state of Data Security.

Data needs to be protected at rest, in transit, and even while it is being processed in memory. Today, GDPR, CCPA, and other regulations make data protection mandatory. Organizations have a responsibility to protect customer data, personally identifiable information, confidential data, intellectual property, and transactional data. Governments need to protect state secrets. Data sovereignty and data residency are on the compliance checklist.

CISO MAG 2020 Market Trends Report on Data Security - 2020

Governments, CISOs, and CDOs (Chief Data Officers) must take a holistic approach and ensure Data Security, Data Governance, and Data Integrity through compliance and policies. They must ensure that data access is strictly on a need-to-have basis. These are the tenets for customer trust, loyalty, and the reputation of an organization.

Data has become worthy, smart, and intelligent, however, with every set of pros come the cons. This CISO MAG Market Trends Report 2020, brings to the fore a viewpoint of the industry experts and their perspective from across the table.

To view the complete analysis and reportage, hit the download button now!

CISO MAG 2020 Market Trends Report on Data Security - 2020

Here’s the Top Security Threat for Educational Institutes

Institutes cyber security

A survey from cybersecurity firm Netwrix revealed that most educational institutions have become increasingly concerned about cyberattacks after the transition to online learning due to the pandemic. The survey “2020 Cyber Threats Report” sheds light on how the outbreak and e-learning initiatives changed the cybersecurity risk landscape.

According to the survey, over 33% of respondents said they are more vulnerable to cyberattacks than they were pre-pandemic. Nearly, 89% of them admitted they identified new security gaps due to the rapid transition to remote education, which is the highest finding among all sectors.

Key Findings:

  • Around 92% of educational organizations consider inappropriate data sharing to be a top security risk. While 41% of respondents reported that they had suffered such incidents in the first few months of the pandemic, making it one of the most common threat scenarios experienced. Other types of incidents reported included phishing (50%) and administrator mistakes (31%).
  • 78% of the educational institutions said they are at greater risk now than before the pandemic and are concerned that users may ignore security guidelines.
  • Concern about malicious actions by rogue admins dropped from 92% to 9%. Indeed, only 12% had such incidents, but they had the longest dwell time, 43% of respondents needed weeks or months to detect the issue.
  • Every fourth educational organization experienced misconfiguration of cloud services in the first few months of the pandemic.

“To minimize the risk and impact of human errors, we recommend investing in security training and easy-to-use collaboration tools. The latter will eliminate the temptation to share sensitive records through unsanctioned solutions, while giving the IT team enough control and auditability. Also look for ways to leverage automation to augment the IT team’s efforts. For instance, data classification will help them focus their security efforts on the most critical data, while automating audit trail collection and analysis will enable them to detect and investigate incidents faster,” recommended Ilia Sotnikov, VP of Product Management at Netwrix.

Cyberattacks on E-Leaning Platforms

There has been a surge in the usage of online learning platforms during the pandemic, which also attracted the cybercriminals to launch their malicious acts. In the recent past, hackers targeted multiple e-learning portals to steal users’ personal information. India-based online learning platform Unacademy suffered a data breach that exposed details of 22 million users. Cybersecurity firm Cyble revealed that the unknown hackers kept 21,909,707 user records for sale at $2,000 on darknet forums. The compromised information included usernames, hashed passwords, date of joining, last login date, account status, email addresses, first and last names, and other account profile details. Earlier, a Spanish e-Learning platform 8Belts suffered a data breach that exposed personal data of over 100,000 e-learners across the globe.

How Strong Cybersecurity Boosts Your Share Price

cybersecurity investment

Since the onset of the National Cybersecurity Awareness Month (NCSAM) for the U.S. starting October 1, on the theme “Do Your Part. #BeCyberSmart,” there has been a renewed interest in the space, thanks to the efforts by the Cybersecurity and Infrastructure Security Agency (CISA) and the National Cyber Security Alliance (NCSA). This week NCSAM emphasizes “If You Connect It, Protect It,” concurring a thought similar to the Hypponen Theory coined by Mikko Hypponen, a world-class cyber criminality expert and the Chief Research Officer of F-Secure. Taking it ahead, and to better elaborate the benefits of establishing a security-by-design architecture, BitSight, the Standard in Security Ratings, and Solactive, a German index engineering firm, have released research demonstrating how a company’s cybersecurity posture can become an indicator of business growth. According to the research, well-performing BitSight-rated companies outperform their respective benchmarks by 1% to 2% annually, and for certain sectors, such as U.S. Technology, several of these companies outperform the benchmark by 7% per year.

Good Cybersecurity Derives Better Investment

The research also highlighted that even investors are concerned about the cybersecurity posture of the company. Research by Solactive of BitSight also ascertained that there has been a shift in the approach for investors when it comes to cybersecurity. It notified that that share prices on average fall 7.27% in a two-week period after a publicly disclosed breach. In fact, cybersecurity was the #1 ESG risk for investors. It was also found that cybersecurity has remained the #3 threat to portfolio companies’ strategic success in the next three to five years.

Steve Harvey, Chief Executive Officer, BitSight, said, “BitSight is powering a new era, where cyber risk is integrated into every market decision and strong, measurable cybersecurity performance is a market differentiator.  This unprecedented research based on BitSight’s unique data will not only affect investors’ views on cybersecurity, but also the way that C-suite and security professionals manage and measure cybersecurity performance inside of their organizations.

In its recent analysis report “Global Cybersecurity 2020 Forecast” Canalys revealed that cybersecurity spending across the globe is estimated to grow between 2.5% ($43.1 billion) and 5.6% ($41.9 billion) in 2020, depending on the economic impact.

Organizations are investing to enhance their endpoint security, network security, web, and email security; data security, vulnerability detection, and security analytics — to boost their security defenses in the wake of present remote working conditions.

While network security remains the largest segment in cybersecurity spending at 36%, the research stated that the endpoint security segment will witness high growth rates due to remote working practices.

“AI has done a good job in securing the dynamic workforce”

PII for social engineering attacks

EC-Council is conducting its 2020 Global CISO Forum virtual event, October 5 – 7. The Global CISO Forum (GCF) is an annual event that sees a confluence of the highest-level executives from across industries and countries who discuss the most pressing issues in information security. Delivering a presentation titled “Securing the Future of Work with Cyber AI,” Marcus Fowler, Director of Strategic Threat, Darktrace, said the future of work is unpredictable and uncertain. He spoke about the rapid adoption of digital collaboration, the dynamic workforce, and the shifting threat landscape – which now extends to remote workers. Highlighting attacks like ransomware, crypto mining, SaaS account attacks, and banking Trojans, Fowler said that even bad actors work after hours and there is no longer a concept of fixed work hours (it’s now fluid work hours). Cybercriminals are now thriving on all the disruption and change around us. So, organizations must rethink their approach to security and rely on new technologies like Cyber AI to achieve much-needed adaptability and resilience.

By Brian Pereira, Principal Editor, CISO MAG

“Digital collaboration has exploded in the last six months. We are using many platforms for collaboration, and these platforms have vulnerabilities,” said Fowler. “The switch to work from home has caused us to lose visibility of users, etc. We ask ourselves if we have enough visibility to feel secure. There are gaps in security outside the corporate network. And there are things happening within the corporate network. (Prior to COVID) things were done to ensure business survival and business acceleration. But has security kept step today?”

He then spoke about the rampant and menacing threats that escalated in the past months, notably ransomware, crypto mining, insider threats, and SaaS account hijacks.

“They are going after sensitive IPs, sensitive communications, and information. And they are doing this to expedite payment, and how much they can ask for. There is lateral movement, crypto mining, and insider threats. We also see external data transfer, and what’s moving out of the corporate network on unofficial or unapproved cloud services or file-sharing services. There’s also SaaS account hijacks, due to an increase in SaaS dependency. Attackers are using brute force,” said Fowler.

Fowler mentioned key changes observed in recent months:

  • Digital transformation projects are being accelerated.
  • Fluid working environments and hours are here to stay.
  • Fragmented, staggered return to offices.
  • Employees may bring malware and vulnerabilities with them or inadvertently used unapproved technology.
  • Low-lying cyber-criminals thriving on disruption and change.

“Darktrace has gone from a time when we were thinking and talking about digital assets and digital environment to including that dynamic workforce — protecting them no matter where they are or what platform they are on and having that security and visibility and ensuring that that team is informed,” said Fowler.  “All the blueprints are constantly changing. So, you need a security technology that is going to adapt and be agile with your changes and decisions in terms of workforce and applications. And it needs to be hybrid and for a mix of industries.”

How AI Adapted

The technology he was referring to is Cyber AI, which proved to be highly agile and adaptable. For some companies, the changes were happening in hours and not even days. So, the technology had to adapt really fast to changing models.

“We did see that AI did a very good job in adapting to extreme changes in work from home. We used an unsupervised learning approach, which does not require an external training data set,” said Fowler.

Watching his presentation, it was interesting to learn how Darktrace’s AI Immune System is doing the “heavy lifting” for security analysts and augmenting humans who are burdened with threat fatigue and false positives. Fowler spoke about the Darktrace AI Immune System using deep learning towards autonomous response, stopping ransomware in seconds.

“Darktrace has gone from a time when we were thinking about digital assets and digital environment to including that dynamic workforce — protecting them no matter where they are or what platform they are on and having that security and visibility and ensuring that that team is informed,” he said.


Listen to the CISO MAG podcasts to catch the advice and best practices from security leaders.  Click here 


Cyber AI for the Dynamic Workforce

To secure the dynamic workforce, the AI solution should be able to provide full visibility and autonomously stop – and augment human teams, making up for the skills shortage. One example is Cyber AI for email. It should be able to detect spear-phishing attacks, for instance.

Fowler said the solution should provide these abilities:

  • Visibility into endpoints, email, and SaaS environments.
  • Contextual understanding across the entire digital organization.
  • Detects the full range of threats – from account takeover and malicious insiders, to critical misconfigurations.
  • Autonomously investigates and responds to attacks – wherever they are.

Fighting Back: Autonomous Response

Teams of security analysts are now complemented by the AI analyst, who moves past alert fatigue, a trait seen in humans. It can also mitigate false positives. It can prioritize triaged events. It will keep security teams informed so that they can take evasive action.

Some of the benefits of an autonomous solution are:

  • Autonomous response, surgical interruption of attacks
  • Reacts faster than human teams
  • No impact on normal, legitimate activity – business as usual
  • Improves functionality of other tools in a SOC
  • Frees up human teams to focus on what matters
  • Responds to a threat every three seconds

“So, this is really a war of the machines. And you can’t bring a human to a machine fight!” concluded Fowler.

About Global CISO Forum

Global CISO ForumGlobal CISO Forum is an annual event that sees a confluence of the highest-level executives from across industries and countries who discuss the most pressing issues in information security. Now in its tenth year, the 2020 Global CISO Forum promises to be the best yet with an exciting mix of industries, formats, and interactive presentations.

In celebration of our 10 years of CISO events, EC-Council is giving its brand-new Risk Management Approach and Practices e-book to all attendees of the Global CISO Forum! Risk is at the heart of what a CISO does and EC-Council wants to create as many risk-smart executives to protect the world’s assets as possible.

EC-Council’s Global CISO Forum is an invite-only, closed-door event gathering.


CISO MAG is Content Editorial Sponsor for the Global CISO Forum.