Home Blog Page 152

Rapid7 Nexpose Security Scanner’s Critical SQL Injection Vulnerability Fixed

microsoft, flaws in SonicWall SRA SMA

A vulnerability in a vulnerability scanner tool is as rare as hens’ teeth. However, researcher Mikhail Klyuchnikov of Positive Technologies achieved this rather rare feat by spotting a vulnerability in Rapid7’s Nexpose vulnerability scanner tool. The said vulnerability allowed attackers to perform certain SQL injection technique to obtain unauthorized access to the tool’s resources and data. The affected versions of the security console are v6.6.48 and earlier.

What are Vulnerability Scanners

Vulnerability scanners are automated tools that allow IT teams to manage their networks, systems, and applications for any security weaknesses that could expose them to attacks. Vulnerability scanning is a common practice across organizations and is often mandated by industry standards and government regulations to improve the organization’s security posture.

The Vulnerability in the Vulnerability Scanner

If exploited, the vulnerability in Rapid7’s Nexpose tool could allow attackers to escalate low system privileges. Leveraging this, the attackers could further obtain unauthorized access to the tool’s internal resources and data and move laterally. The vulnerability, which is recorded under CVE-2020-7383, is moderately severe with a CVSS severity score of 6.5. However, a low severity score does not mean that the damages forecast would be any less. This vulnerability enables attackers to perform an SQL injection technique, which can be used to access certain data stored in a database. This data may include information on detected vulnerabilities, past scans, and policies. An attacker could also perform SQL injection as part of the denial of service (DoS) attacks on the database to disrupt the normal functioning of the web interface.

This vulnerability enables a logged-in attacker to access and modify certain database records, as well as add new ones. Only a low level of system privileges is necessary to exploit this vulnerability and obtain access to data that should not be visible to a user with that level of privileges.

– Mikhail Klyuchnikov

Looking at its critical nature, the developers at Nexpose fixed the vulnerability and released the update to its users in its v6.6.49 version.

Related News:
Google Rolls Out Patch to Fix Zero-Day Vulnerability in Chrome
Netlogon Vulnerability: Patch Before Hackers Become Your Admin

Google Delists Fraudulent Gaming Apps Spreading “HiddenAds Trojan”

Mobile Apps Security, mobile apps

Tech giant Google has removed 21 malicious Android apps from its Play Store after discovering intrusive adware and Trojans in them. According to a report from security solutions provider Avast, the fraudulent apps were disguised as gaming apps and contained “HiddenAds Trojan.” Adware is a kind of software that hijacks mobile devices to spam the victim with unwanted ads and steals user data.

The security researchers from Avast stated that the HiddenAds malware disguises itself as a normal application. The malware can hide the app’s icon, evade security scans, and hide behind malicious advertisements. It is found that the malicious apps were downloaded nearly eight million times. Threat actors often use this technique to steal sensitive data/generate revenue by redirecting users to unwanted ads.

The 21 malicious apps include:


Shoot Them

Crush Car

Rolling Scroll

Helicopter Attack – NEW

Assassin Legend – 2020 NEW

Helicopter Shoot

Rugby Pass


Flying kateboard

Iron it

Shooting Run

Plant Monster

Find Hidden

Find 5 Differences – 2020 NEW

Rotate Shape

 Jump Jump

Find the Differences – Puzzle Game

Sway Man

Money Destroyer

Desert Against

Cream Trip – NEW

Props Rescue

Jakub Vávra, Threat Analyst at Avast, said, “Developers of adware are increasingly using social media channels, like regular marketers would. This time, users reported they were targeted with ads promoting the games on YouTube. In September, we saw adware spread via TikTok. The popularity of these social networks makes them an attractive advertising platform, also for cybercriminals, to target a younger audience.”

“While Google is doing everything possible to prevent HiddenAds from entering its Play Store, the malicious apps keep finding new ways to disguise their true purpose, thus slipping through to the platform and then to users’ phones. Users need to be vigilant when downloading applications to their phones and are advised to check the applications’ profile, reviews, and to be mindful of extensive device permission requests,” Vávra added.

Android Adware- A Rising Issue

Earlier, Avast revealed that Android adware is responsible for 72% of all mobile malware and the remaining 28% related to banking trojans, fake apps, lockers, and downloaders. Read the full story here.

Related Story:

Hackers Target Loyalty Programs to Obtain Users’ Sensitive Data

New Programming Language

A new research from security solutions provider Akamai revealed that cybercriminals launched credential stuffing campaign to target loyalty programs. Attackers took advantage of the pandemic and circulated password combination lists, targeting the retail, travel, and hospitality sectors with various cyberattacks.

In its report, “The State of the Internet / Security report: Loyalty for Sale – Retail and Hospitality Fraud” Akamai revealed several examples of criminal ads from the darknet websites illustrating how they cash in on the results from successful attacks and the corresponding data theft. Threat actors created fake loyalty programs and other crime-related ventures to obtain sensitive information from users.

Akamai found more than 100 billion credential stuffing attacks between July 2018 and June 2020. Over 4,375,711,860 web attacks were observed against retail, travel, and hospitality, accounting for 41% of the overall attack volume across all industries. Nearly, 83% of web attacks targeted the retail sector alone.

“Criminals are not picky — anything that can be accessed can be used in some way. This is why credential stuffing has become so popular over the past few years. These days, retail and loyalty profiles contain a smorgasbord of personal information, and in some cases financial information too. All of this data can be collected, sold, and traded or even compiled for extensive profiles that can later be used for crimes such as identity theft,” said Steve Ragan, Akamai security researcher and author of the report.

“All businesses need to adapt to external events, whether it’s a pandemic, a competitor, or an active and intelligent attacker. Some of the top loyalty programs targeted require nothing more than a mobile number and a numeric password, while others rely on easily obtained information as a means of authentication. There is an urgent need for better identity controls and countermeasures to prevent attacks against APIs and server resources,” Ragan added.

Fragomen’s Data Breach Exposes Google Employees’ Personal Data

Google

Fragomen, Del Rey, Bernsen & Loewy, an immigration law firm in the U.S., revealed a data breach that exposed personal information of current and former Google employees. In a security alert, Fragomen stated that an unauthorized third party compromised its network systems and illicitly accessed a file on September 24, 2020, which contained Googlers’ personal data.

Fragomen provides employment verification screening services to the organizations and is also responsible for providing Form I-9 compliance services to Google.

Employees use Form I-9 to declare their citizenship and eligibility to work in the U.S. These forms hold employees’ private information like full name, birth dates, address, email details, contact number, social security number, passport details, and other immigration identifiers, which can be easily misused by cybercriminals for various malicious activities.

While there is no information on how many Googlers were affected in the incident, Fragomen stated that it commenced an investigation with a digital forensic firm for further analysis. It also stated that it is offering complimentary identity theft protection and credit monitoring services to all the affected employees.

“We have no evidence at this point in time that your information has been viewed, we wanted to notify you of this incident and assure you that we take it very seriously. We have taken steps in response to this incident, including implementing enhancements to our IT Security infrastructure and detection capabilities,” Fragomen said.

Threat Actors Exploited Google

Recently, a threat intelligence team from GreatHorn uncovered a series of ongoing phishing campaigns targeting users of Google’s Gmail. The attackers used imposter open redirector domains and subsidiary domains of various popular brands and sent tens of thousands of emails to corporate account users globally. The comprehensive and multi-pronged attack campaign had multiple hosting services and web servers that were used to host fraudulent Office 365 login pages. It was also found that malicious links and fraudulent emails/attachments were bypassing users’ security controls and email security platforms.

It’s Cybersecurity Awareness Month

Now, unless you are in the industry OR associated with it, the chances are you’ve not got a clue that October is “click responsibly” or National Cybersecurity Awareness Month. After all, we share October with Breast Cancer Awareness, LBGTQ History, and 14 other notable causes. We are finally showing up in Wikipedia on their reference page for “month-long observations” alongside 100 other things jammed into each year. However, to the greater planet (around 7.6 billion folks at the moment), there’s little awareness that this month is THE month to think about all those digital safety things we keep bragging about.

And that’s a problem…

By Chris Roberts, Researcher, Hacker, CISO

Because let’s face it, we’d be in less of a mess if we gave kids a box of matches to play with than electronic devices. Sure, we’d have to ensure that the entire house was flame retardant and that we actually remembered where we put the extinguishers, but we’d have fewer kids being groomed online, less bullying, cyberstalking, fraud, and a whole lot more attentiveness in the world.

However, that’s NOT going to change, so what DO we do about it?

Firstly, we can talk about awareness and education from a younger age. Waiting until the kids are in high school and being handed a Chromebook or something similar, and then regretting about how the online world is dangerous, is far too late. How about we work on educating them from the crawl-stage onwards? After all, parents have been pampering kids with electronics since that point, so it makes sense to start the conversations about safety and what it means to be a good, upstanding digital citizen from that very age. There’s enough of us out there that can help, volunteer, educate, or come up with engaging material to bring a level of awareness from the K-onwards (Kindergarten). There are efforts underway, but they need all of our help in any way we can, after all THIS is the generation that’s going to be responsible for the Internet when we’re sitting in our retirement homes dribbling into the sunset.

Secondly, we’re going to have to have a conversation with the parents. We understand the menace that most digital systems are, the parasitic nature that many programs bring to those devices all wrapped up in seemingly innocent games and social interaction tools. However, despite all our best efforts, two things are apparent; the likes of exploitive software companies are here to stay until we can deal with them more efficiently, and most parents or guardians have absolutely NO clue as to the dangers of letting their kids online at an early age.  The first one’s going to have to be dealt with through legislation and other methods and the second (the parent/guardian) is again an education, awareness, and crucially accountability discussion.

At this point, I’m going to borrow from two good friends in the industry. Both Ryan Cloutier and Evan Francen talk at length about accountability in the context of our industry and those of us in it. They talk about how we need to hold ourselves and our technologies to higher standards and to actually be responsible for what we’re doing in this world, as opposed to simply going along like lambs to the digital slaughter on the alters of IPO or venture capitalism (as many folks are seemingly focused on).

Now, if we take some rough numbers, we have 2.2 billion kids in the world, around 800 million elderly, which means those of us in the middle have to step up and look after the rest. That’s 4.6 billion of us to look after 3 billion. So, all it takes is for one of us to tell two other people about HOW to become safer online, how to approach technology, and how to question more and believe less. 

That’s not too hard, is it? Seriously, each of us tells two other people. Preferably one person in the caring group and one in the crawler range. Crucially we also need to make sure we inform folks outside of our own comfort circle (including strangers). To pull another quote from another industry expert, Rachel Arnold,  “WE need to get off our own Island…”

Now, if we add to this equation, the simple fact that there are around 3.5 billion smartphones dotted around the globe, we have another way to influence. I’m not talking about everyone rushing out to start another education/awareness company OR another app to get lost in the mix; I am talking about driving quality content, consistent messaging, and reinforcing the desire to help those around us become a little safer and a lot less risky in how they approach the digital world we live in, preferably in a language other than English. (Newsflash: The U.S. only has 4% of the world’s population, they rank 3rd in mobile users, and let’s face it, we’ve only got around 15% of the population of the planet that speaks this language). So, let’s see if we can use our strengths and capabilities to influence others all over the globe?

I know that this line of thinking is radical, we’re back to putting people ahead in the equation, we’re using technology simply as a mechanism for carrying our message, and we’re engaging in processes, policies, and controls to help alleviate the issues. We’re NOT chasing down a technology solution, we’re not whiteboarding another widget that can translate, and we’re sure as hell NOT trying to explain to anyone how AI is going to solve this. It’s simply back to where we started thousands of years ago. We sat around the fire explaining to the kids what was good in our tribe, where we could go, and what would try to eat us if we wandered too far. Nothing’s really changed. The tribe is now global, and technology can take us anywhere, at any time, we just must respect it a lot more than we do.

So, please take the time to talk with others, in a language they understand, at a level they can absorb, and with simple, basic help that they can effectively utilize.


About the Author

Chris Roberts possesses a rich experience within the domain of information security and is globally recognized as one of the pioneering wizards on vulnerability research and counter-threat intelligence. He has worked on a multiplicity of projects specializing in intelligence gathering, DarkNet research, deception technologies, and cryptography with several organizations and has been credited by many of the top Information Technology and Security disciplines.

Disclaimer

Views expressed in this article are personal. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.


Related story: Cybersecurity Awareness – Act Now!

 

Take Our Endpoint Security Survey and Win These Freebies

endpoint security survey

In today’s cutthroat business world, data is considered an asset. Data loss or data breach could take down a business operation overnight, further leading to both financial and reputational damage. Hence, endpoint security is integral to securing modern enterprises.

Since endpoints range from mobile devices, tablets, ATMs, smartwatches, printers, and more, users can quickly connect to an organization’s network. They are playing a significant role in communicating back and forth during the current work from home (WFH) scenario.

These devices end up becoming threat points and a favorite target of hackers.

At CISO MAG, we nurture an Endpoint Security culture. We invite you, the readers, to participate in our year-end Endpoint Security Survey to help us gain an insight into the looming cyberthreats and the challenges in deploying endpoint security solutions.

Your responses will be confidential and aggregated results will be shared in our Endpoint Security issue in December. The survey questionnaire will be live until November 17, 2020.

Your feedback will help industry leaders create better Endpoint Security solutions.

We appreciate your time, cooperation, and engagement. And as a token of thanks, we are offering you a free annual subscription of CISO MAG worth $149. We are also offering 30-days access to CodeRed (EC-Council’s high-quality videos and courses on various topics of cybersecurity that will take your career to the next level!).

Sincerely,

Team CISO MAG


Sopra Steria Confirms Being Hit by New Variant of Ryuk Ransomware

Hive Ransomware

On October 21, 2020, French IT firm Sopra Steria released a statement informing that a cyberattack disrupted the operations of its IT network since the evening of October 20. The firm notified the required authorities and implemented emergency protocols to contain the damages. The source, type, and intent of the cyberattack were not known at the time; however, an updated statement issued by its sister company, Sopra Banking Software (SBS), has confirmed that a new Ryuk ransomware variant is behind the attack.


CISO MAG Endpoint Security SurveyTell us more about your Endpoint Security knowledge and win lots of amazing goodies!

Take the Survey Now!!!


According to Sopra Steria’s internal investigation, the ransomware operators had begun infiltrating its network and systems just a few days before the malicious activity was detected. Hence, the company confined it to a limited part of its IT infrastructure.

New Ryuk Ransomware Variant?

As per the claim of the group’s IT team, the latest versions of anti-virus and firewalls had been installed on the systems and networks, respectively; however, Ryuk ransomware signatures going undetected was a surprising factor for them. It led to a deeper investigation of the cyberattack, which revealed that the new signatures indeed belonged to the new Ryuk ransomware variant. This explained the inability of detecting the ransomware attack in the initial phase. The investigators and the IT team have shared their findings of the detected signatures with all known anti-virus providers so that their list of IOCs can be updated for Ryuk’s new variant.

The company said, “Having analyzed the attack and established a remediation plan, the Group is starting to reboot its information system and operations progressively and securely. However, having said that, it will take a few weeks for a return to normal across the Group.”

Related News:
Ryuk Ransomware Took Down U.S. Coast Guard Operations
Ransomware Attacks Continue to Loom Over Cyberspace

Global Endpoint Security Market to Witness Profitable Growth

Global Endpoint Security Market to Witness Profitable Growth

A new study from Persistence Market Research (PMR) revealed that the global endpoint security market is estimated to register a CAGR of 11.20% and reach a value of $27.83 billion by the end of 2025. The rising demand for advanced security solutions is expected to boost the requirement for endpoint security solutions. The study also highlighted that increasing awareness among consumers on cyberattacks triggers the need to install efficient endpoint security solutions to protect their businesses against evolving cyberthreats.

Prominent Markets for Endpoint Security 

According to the study, the Middle East, Africa, Europe, Asia Pacific, Latin America, and North America are the leading regional markets for endpoint security globally.  North America is likely to lead the worldwide market for endpoint security soon, with revenues increasing to $12.30 bn by 2025.

“The swift expansion of businesses in the Asia Pacific has spiked the usage of endpoint devices in enterprises and organizations. With the heavy utilization of these devices and increased uptake of IoT applications has made enterprise networks more complex in this region, creating a significant need for endpoint security, which is the main factor behind the rising market for endpoint security in the Asia Pacific. Europe is also reporting a healthy rise in its market for endpoint security, thanks to the progressive adoption of endpoint security solutions in order to eradicate spills of critical information in countries like the U.K.,” the study stated.

Endpoint Security

Endpoint Security in the Pandemic

Research from Cisco stated that organizations became most concerned about data sharing during the COVID-19 pandemic. The research highlighted that increasing cybersecurity spending will make organizations and consumers ready for the current working conditions. One in two respondents said endpoints, including corporate laptops (56%) and personal devices (54%), are a challenge to protect in a remote environment. Nearly, 85% of organizations said that endpoint security is extremely important or more important than before COVID-19. Secure access is the top cybersecurity challenge faced by the largest proportion of organizations (62%) when supporting remote workers.


Is Your Endpoint Device Secure? Take our Endpoint Security Survey and win exciting goodies. Don’t miss out! Take Survey Now!

Over 98% Organizations in India Have Shortage of Cybersecurity Talent

Arguments surrounding the cybersecurity skill gap often make a redundant appearance in every serious infosec discussion. And even though, it is a topic that has had its right share of the limelight, the infosec industry continues to be plagued by the talent shortage. The newest into this debacle is India — a country with one of the highest numbers of young population in the world and over 98% organizations in the country — has shortages in their security operations staffing.

A recent study by software firm Micro Focus indicates that India reports the strongest concern in comparison to its global peers when it comes to tackling the increased volume of cyber threats and security incidents. The study also noted that 96% of organizations use Cloud for IT security operations. It also highlighted the increased cyberattacks organizations had to face due to the onset of COVID-19.

“As a fast-developing economy, India is witnessing a rapid adoption of digital tools and services within its enterprise ecosystem. The unprecedented adoption of cloud is also giving rise to newer vulnerabilities and cybersecurity challenges,” said Praveen Patil Country Manager – Security, Risk & Governance Micro Focus, India. “Our latest State of Security Operations report highlights the key security issues faced by organizations across several industries, and requirements for advanced tools and capabilities to address the same.”

“The odds are stacked against today’s SOCs: more data, more sophisticated attacks, and larger surface areas to monitor. However, when properly implemented, AI technologies such as unsupervised machine learning, are helping to fuel next-generation security operations, as evidenced by this year’s report,” said Stephan Jou, CTO Interset at Micro Focus. “We’re observing more and more enterprises discovering that AI and ML can be remarkably effective and augment advanced threat detection and response capabilities, thereby accelerating the ability of SecOps teams to better protect the enterprise.”

It is alarming to find that cybersecurity, which offers one of the most lucrative job opportunities in tech, with literally zero percent unemployment, remains the one struggling to attract talent. There has been discussion around education being one of the dominant reasons. Talented professionals may not have access to the right kind of education that could help them land one of these lucrative opportunities.

There are many that believe the biggest threat to cybersecurity is the lack of talent. Without enough people to man the battle stations, it’s no wonder so many companies face a breach at one point or another. Earlier this year, a study by Ponemon suggested that the lack of skilled personnel has become the biggest barrier for cybersecurity in deploying security automation.

The picture isn’t so rosy in the C-suite either. Earlier, EC-Council surveyed its pool of Certified CISOs in regions spanning from South America, Europe, Asia, Middle East, the U.S., and Africa, to discover what is important to information security executives. The research pointed out that most CISOs have several job openings yet to be filled, and CISOs and the others involved in the recruiting process are looking for prospects with relevant certifications and experience.

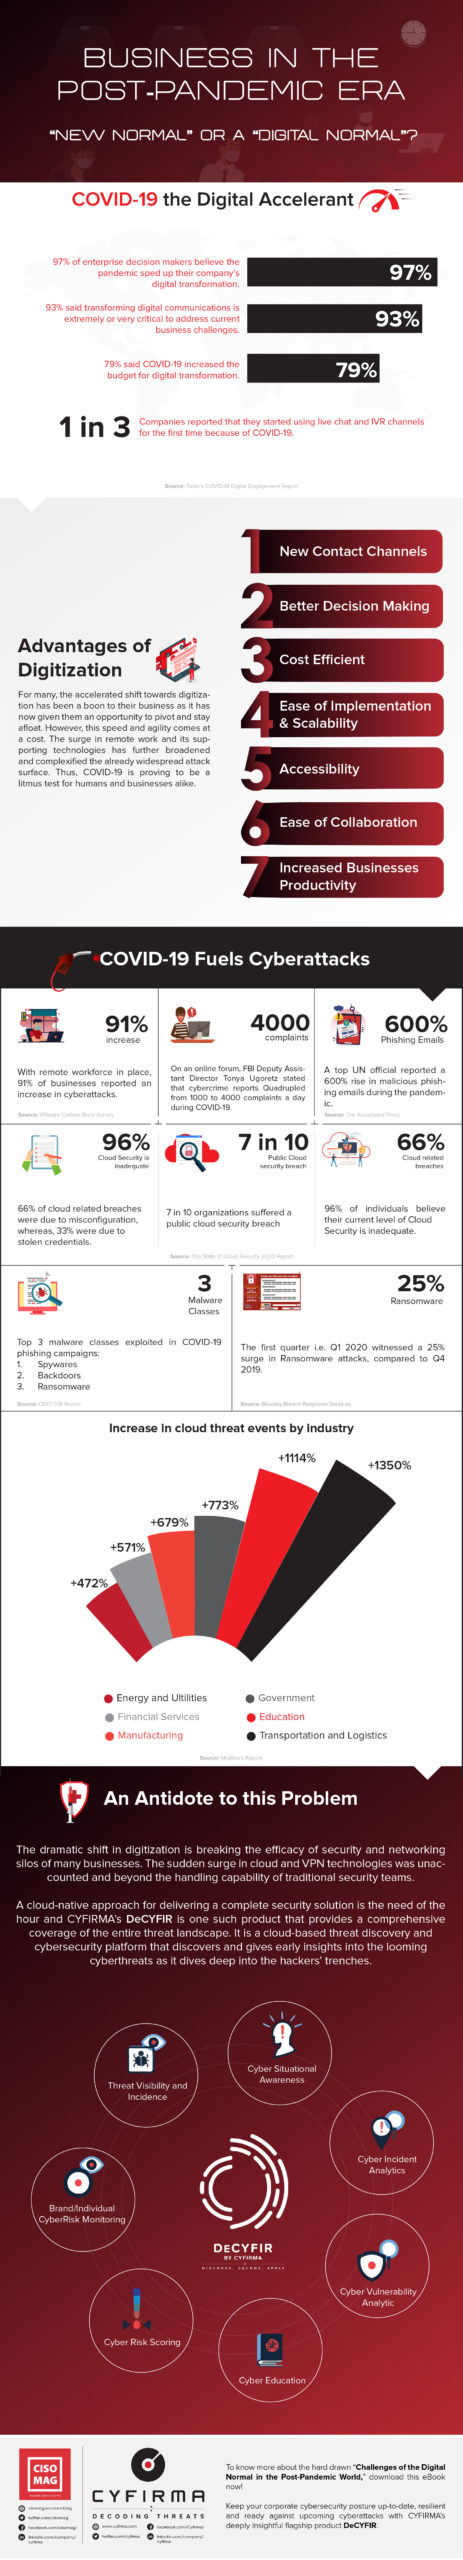
Time to Get Back to Normal Or Should We Say Digital Normal! [Infographic]

Since the onset of the pandemic, businesses have seen years-long digital transformation roadmaps being compressed into days and weeks to adapt to the new normal. Every Industry – from shopping to education and healthcare to hospitality – had to identify new ways to survive and be resilient. Thus, digitazation was no longer an option for businesses but the only option.

digital normal infograph

business in the post pandemic eraTo know more about the hard drawn “Challenges of the Digital Normal in the Post-Pandemic World,” download this eBook now!

Click to Download

Related Articles:

CYBER WARFARE: The Fight Beyond Enemy Lines [INFOGRAPHIC]