Home Blog Page 112

India Becomes the Second Most Cyberattacked Country in APAC in 2020

Acronis Cyber Readiness Report, cyberattacks in India, cybercrime in India, India’s Private Sector

The recent surge in technological innovations due to the Indian Government’s “Make in India” and “Atmanirbhar Bharat” (self-reliant India) campaigns along with a shift towards digital transformation due to the ongoing COVID-19 pandemic meant that a parallel surge in the number of cyberattacks was anticipated. However, the spike would be so high that India would grab the second spot in the list of “Most cyberattacked country in the APAC” was beyond expectation. IBM Security released a report titled the 2021 X-Force Threat Intelligence Index, which made the following key revelations highlighting the threat landscape in India:

  • India was the second most cyberattacked country in the APAC, only behind Japan.
  • 7% of all attacks, which X-Force (IBM’s proprietary security product) observed in Asia, were targeted towards India.
  • Finance and insurance industries were the most targeted industries (60%), closely followed by manufacturing and professional services.
  • Ransomware topped the attack type list in India, making up roughly 40% of the attacks.
  • India has been considering a digital currency of its own for some time now, however, X-Force observed that digital currency mining and server access attacks hit many Indian companies last year.
  • In 2020, most of the attacks on Indian companies occurred between May to July.

Talking about the findings from the study, Sudeep Das, Security Software Technical Sales Leader, IBM Technology Sales, India/South Asia, said “The 2020 threat landscape in India was largely shaped by the pandemic. As the pandemic’s timeline of events and progress unfolded, so did the attack trends. Ransomware was the top attack type in India with a 40% share in the overall threat landscape which although is not surprising yet, beyond expectation. We also witnessed cybercriminals using relief efforts and public health information as spam lures including targeted attacks on critical components of the vaccine supply chain.”

Related News:

IBM Fixes Critical Vulnerabilities in Java Runtime, Planning Analytics Workspace

When asked what Indian organizations expect in 2021 and how they can overcome threats, Das added, “All these issues will remain in 2021 as well.  Hence, organizations need to harden their cloud environments with a zero-trust approach to their security strategy and leverage AI to monitor, detect and contextualize dynamic behaviors and movements across hybrid cloud environments, to verify the legitimacy (or lack of) of a threat and automate a response.

Furthermore, we need to use Confidential Computing for a higher level of isolation for secure enclaves of data. It encrypts data during processing, whereas before, data had to be decrypted just before being processed, leaving it potentially vulnerable. In other words, even if cloud environments are compromised, the data would be futile/inaccessible to a malicious actor with technologies like Confidential Computing.”

Other Findings

The findings in this report are based on data analyzed from multiple sources within IBM, including IBM Security X-Force Threat Intelligence and Incident Response, X-Force Red, IBM Managed Security Services and additional data provided by Quad9 and Intezer. Some of the key findings from the global level analysis include:

  • Accelerated use of Linux Malware: An increase of 40% in Linux-related malware families was observed in 2020.
  • Shift in Top Spoofed Brands: Amid a year of social distancing and remote work, brands offering collaboration tools such as Google, Dropbox, and Microsoft, or online shopping brands such as Amazon and PayPal, made the top 10 spoofed brands in 2020. Adidas was another surprising entrant to this list at the No.7 spot.
  • Ransomware became a profitable business model: Ransomware was the cause of nearly one in four attacks that IBM’s X-Force responded to in 2020. The majority of them exercised double extortion tactics. Using this model, X-Force found that Sodinokibi operators – the most observed ransomware group in 2020 – had a very profitable year. The report estimates that the group made over $123 million in the past year, with approximately two-thirds of its victims paying a ransom.

To download the complete report, click here.

Related News:

Rushing to the Cloud to Support Remote Workers Poses New Security Risks: IBM Study

All You Need to Know About NCSC’s “Cyber Action Plan”

NCSC

With the surge in employees working remotely, cybersecurity for businesses globally has become critical. It has particularly become a challenge for small businesses to boost their cybersecurity standards against evolving cyberthreats.

With an aim to help small and medium-sized businesses combat rising cyberattacks, the U.K.’s National Cyber Security Centre (NCSC) has created the “Cyber Action Plan.The Cyber Action Plan is a digital cybersecurity self-assessment service for micro-businesses and sole traders to secure their digital landscape and defend against various cyber risks. It was created after the government’s survey, which revealed that nearly 50% of micro and small businesses reported cyberattacks and data breaches in the past year. Around 46% were victims of these cyber incidents – up from 31% the previous year.

The new action plan has been developed as part of the U.K.’s Cyber Aware campaign. Cyber Aware is a government advice platform helping individuals and organizations on how to stay secure online against different cyber frauds.

In addition, the NCSC will also advise and guide organizations of all sizes to move their physical operations online securely. The agency invited micro businesses and sole traders to complete a short questionnaire that generates a personalized list of actions linked to the Cyber Aware behaviors.

Jonathan Geldart, Director General, Institute of Directors, said, “We know from our members that cyber-crime is a top concern and priority for directors. The increase in flexible working patterns, which will continue beyond the pandemic, underlines the critical importance of cybersecurity. The practical support offered through the new Cyber Action Plan provides a framework for organizations to minimize the risks and recognize with confidence how and where their cybersecurity could be improved.”

NCSC’s New Vulnerability Reporting Toolkit

Earlier, the NCSC released a new “Vulnerability Reporting Toolkit,” which is intended to help organizations manage their vulnerability disclosure processes in a simplified manner. The Toolkit is helpful for all types of organizations that are planning to implement a vulnerability disclosure process in their system. Read more…

Here’s Why Security Programs Often Fail

why security programs fail

Helen Keller, a famous American author once said, Security is a superstition. It does not exist in nature. This quote references the security of the human mind, however, the same implies in cybersecurity. Recent security events like the SolarWinds and Accellion hacks are prime examples of loopholes in your security through a third-party service. You might have covered all your security bases, but what about others? Are others in your business ecosystem having your back covered? Risk assessments, top of line cybersecurity products, or the best-in-class cybersecurity practices, are not enough today. While businesses agree that cybersecurity is constantly evolving, many continue to use legacy frameworks that are decades old (the Accellion hack is a good example of this) — and then end up thinking, “We did all that we could to secure our periphery, but…”

“Why do security programs ultimately fail?”

The answer to this dilemma can be found in a strategic whitepaper published by a cybersecurity solutions firm, Praetorian.

SPONSORED CONTENT

The researchers at Praetorian, often came across this anomaly when they tore down the defenses of their customers during Red Team exercises. They noticed that despite technical innovations, trained assets, and billions being invested in security, many businesses still struggle and ultimately fail to keep an attacker at bay. In their words, Businesses end up losing their ‘Crown Jewels’ to the attacker, more often than not.

Why Security Programs FailThus, with a forward-looking view of showing the mirror to the businesses of where exactly they are going wrong and failing in the pursuit of becoming secure, Praetorian security engineers decided to help the community with their expertise through a whitepaper titled  “The Elephant in the Room: Why Security Programs Fail” 

The whitepaper is an outcome of three years of innumerable client discussions and meticulous research from Praetorians’ security engineers. It answers the myths and some burning questions like, how and why many security programs spend too much time and money on things that do not appreciably reduce their business risks. This document has been written to guide those responsible for setting security strategies and to understand the common root causes of security programs’ strategic failure. This will in turn help them take corrective steps to evolve into a more effective, risk-informed security program. Here are some of the key highlights covered in the whitepaper:

  • Factors leading to the misdirection of security programs.
  • Misapplication of frameworks.
  • The disturbance caused by compliance.
  • Tenets of designing effective security programs.
  • The economics of security effectiveness.
Why Security Programs FailLet’s address the “Elephant in the Room” by downloading the whitepaper here.


ADVERTORIAL

Facebook Bans Myanmar Military Accounts on its Platforms

Facebook bans Myanmar Military Accounts

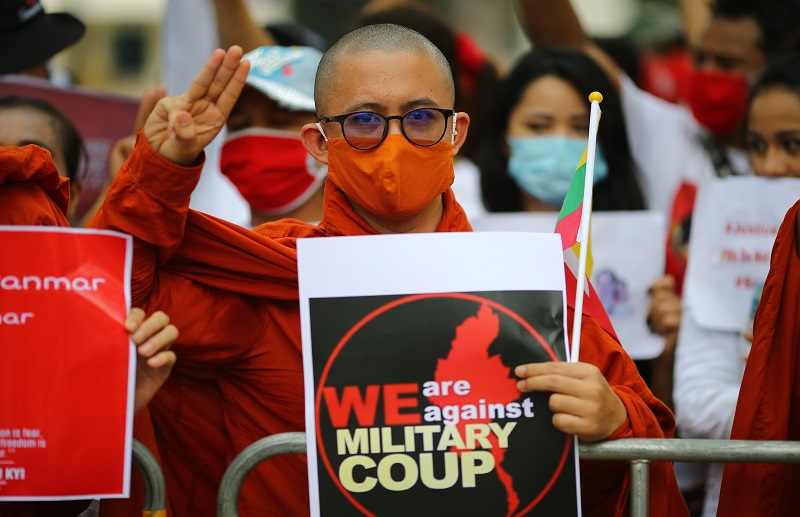
Facebook has banned Myanmar military (Tatmadaw) and military-controlled state and media entities from its Facebook and Instagram platforms. Facebook also prohibited Tatmadaw-linked commercial entities from advertising on its platforms. The ban comes after the Myanmar military seized power on February 1, 2021, from Aung San Suu Kyi’s National League for Democracy (NLD) by allegedly detaining her.

“Events since the February 1 coup, including deadly violence, have precipitated a need for this ban. We believe the risks of allowing the Tatmadaw on Facebook and Instagram are too great. We’re continuing to treat the situation in Myanmar as an emergency and we remain focused on the safety of our community, and the people of Myanmar more broadly,” Facebook said.

Why Facebook did this?

Facebook claimed that it removed military pages and accounts based on four guiding factors, which include:

  1. The Tatmadaw’s history of exceptionally severe human rights abuses and the clear risk of future military-initiated violence in Myanmar, where the military is operating unchecked and with wide-ranging powers.
  2. The Tatmadaw’s history of on-platform content and behavior violations led to us repeatedly enforcing our policies to protect our community.
  3. Ongoing violations by the military and military-linked accounts and pages since the February 1 coup, including efforts to reconstitute networks of Coordinated Inauthentic Behavior that we previously removed, and content that violates our violence and incitement and coordinating harm policies, which we removed.
  4. The coup greatly increases the danger posed by the behaviors above and the likelihood that online threats could lead to offline harm.

Since the coup, Facebook disabled the Tatmadaw True News Information Team Page and MRTV Live Pages for violating the platform’s policies. The social media giant also decreased the distribution of content on 23 pages and profiles operated by the Tatmadaw. However, the ban does not cover government ministries and agencies engaged in the provision of essential public services, which includes the Ministry of Health and Sport and the Ministry of Education.

“This action builds on the steps we have taken in recent years to prevent the Tatmadaw from abusing our platform. Among these are: banning 20 military-linked individuals and organizations in 2018, including Commander-in-Chief Min Aung Hlaing, for their role in severe human rights violations; and removing at least six Coordinated Inauthentic Behavior networks run by the Tatmadaw from 2018 to 2020,” Facebook added.

Tatmadaw’s Controversial Cybersecurity Bill

Recently, Myanmar’s military junta has drafted a cybersecurity bill that caused an uproar among human rights campaigners. According to several activists, the new law will grant authorities sweeping powers over the internet including allowing the military to ban content it dislikes, restrict internet providers, and even intercept data. They believe the cybersecurity bill will violate human rights, including the rights to freedom of expression, data protection, and privacy.

Newly Identified “LazyScripter” Hacking Group Phishing Users Since 2018

phishing, Telegram bots and Google Forms used for phishing

Security research by Malwarebytes uncovered a new threat group targeting the members of the International Air Transport Association (IATA), multiple airlines, and several individuals who are planning to emigrate to Canada for jobs. Dubbed “LazyScripter,” the hacking group is leveraging unusual phishing tactics and tools to target the victims.

Active since 2018, Malwarebytes discovered LazyScripter operators in December 2020. The research report suggests that LazyScripter deployed Powershell Empire on victims’ devices using a payload known as Emploader. However, the threat actors recently switched to Octopus and Koadic, which are installed using Kocktopus payload.

LazyScripter’s Phishing Baits

The operators behind LazyScripter used several techniques to trick users into clicking or downloading malicious URLs or attachments to infect their devices. The main intention of LazyScripter operators is to pilfer critical information and intelligence from the targeted victims. The phishing baits used by these actors include:

  • IATA security (International Air Transport Association security)
  • BSPlink Updater or Upgrade (BSPlink is the global interface for travel agents and airlines to access the IATA Billing and Settlement Plan (BSP)).
  • IATA ONE ID
  • User support kits for IATA users
  • Tourism (UNWTO)
  • COVID-19 related information
  • Microsoft Updates
  • Job information
  • Canada skill worker program
  • Canada Visa (CanadaVisa.com is the online presence of the Campbell Cohen Immigration Law Firm)

Malwarebytes’ researchers found 14 malicious documents used by the threat actors’ group since 2018, which carried embedded objects that are variants of the KOCTOPUS or Empoder payloads.

“We were able to collect some of the spam emails used by this actor over the past two years. In these spam emails, the actor used several methods to redirect the user to download a variant of KOCTOPUS. The latest campaign was spotted on February 5, 2021, in which the actor was distributing a variant of KOCTOPUS pretending to be ‘BSPLink Upgrade.exe’ and managed to drop a variant of Quasar Rat in addition to OCTOPUS and Koadic. Before that we have spotted another campaign on Jan 6th, 2021 in which the actors were distributing a variant of KOCTOPUS pretending to be ‘IATA ONE ID.exe’ software,” Malwarebytes said.

Twitter Discloses Four Networks of State-affiliated Information Operations

Twitter hack

From multiple data breaches to a series of celebrity account hacks, social networking giant Twitter suffered many challenges last year. Threat actors created fake accounts and misused legitimate accounts for their malevolent activities. Recent reports suggest that Twitter removed hundreds of accounts that are connected to government-backed threat actors from Armenia, Russia, and Iran. The networking giant claimed that it identified four networks of accounts of state-linked operators involved in disseminating disinformation and targeting the European Union, the U.S., and the NATO alliance. In total, Twitter permanently suspended 373 associated accounts across the four networks for violating its platform manipulation policies.

Fake Accounts Linked to Russian Actors  

Twitter disclosed two separate networks that have links with the Russian government. In its first investigation, Twitter found and removed a network of 69 fake accounts related to Russian state actors. While in its second investigation, Twitter removed 31 accounts affiliated with the Internet Research Agency (IRA) and Russian government-linked actors.

“A number of these accounts amplified narratives that were aligned with the Russian government, while another subset of the network focused on undermining faith in the NATO alliance and its stability. These accounts amplified narratives that had been previously associated with the IRA and other Russian influence efforts targeting the United States and European Union,” Twitter said.

Twitter removed over 130 accounts originating in Iran that disrupted the public conversation during the first 2020 U.S. Presidential Debate. In total, Twitter suspended 238 accounts linked to Iran-based actors for various violations.

In Armenia, the social networking company investigated and removed 35 accounts that had links to the Government of Armenia. Threat actors created these fake accounts to advance narratives that were targeting Azerbaijan and engaging in malicious activities to gain followers and further amplify this narrative.

Twitter stated that it disclosed information related to more than 85,000 accounts associated with platform manipulation campaigns from across 20 countries since October 2018.

“With every disclosure we make, we want to continue to educate people on the tactics used by state actors to manipulate or undermine the open democratic conversation that happens on Twitter,” Twitter added.

Dancing with the Elephants

cloud, cloud security

Undoubtedly, the year 2020 has been an inflection point for propelling increasingly more data to the cloud for superior management, predictive analysis, and secure data in a comprehensive manner. Reliable and meticulous, the top cloud providers offer top-notch security tools to manage customers’ workloads. However, this assurance brings a catch: these providers only gradually allowed transparency regarding their responsibilities versus customer responsibilities with respect to the management of customer workloads. The public cloud providers’ shared responsibility model declares the crucial specifics of the customers’ responsibility for the workload management that they operate in, while the providers fulfill the responsibility of protecting the ongoing security and upkeep of the cloud infrastructure. Considering the enormity of the responsibility that customers face on the cloud, let’s carefully examine the top challenges that come with this exercise.

By Raghunath Venkat Thummisi, Founder & CEO, Cannon Cyber

New organizational perimeter – Diversified workloads spanning across on-premise, public, and private clouds have extended the boundaries of the enterprise, prompting customers to scramble to grasp new organizational perimeters and deploy effective perimeter security.

Role played by Cloud Access Security Broker (CASB) – The organizations’ move to cloud services has triggered an increased opportunity for the deployment of CASB solutions. CASB is deployed to effectively monitor and understand the data flows to detect potential threats and stop a variety of breaches. CASB systems also find applications being deployed for inline data protection, with tokenization or encryption. The potential use cases for CASB solutions are many, but they are hindered by the lack of consistent technical standards for data protection that the cloud providers can follow.

The current systems fall short in addressing all these challenges.

Complexity through data overload and lack of visibility – Some customers lack a complete understanding of the cloud infrastructure services provided and their effective usage and associated challenges that hinder their organizational security compliance. One of the significant advantages of leveraging cloud-based technologies is that organizations do not have to manage the resources and workloads to keep it operational. Cloud control and triggers make it possible to have a set-up where this is addressed by the cloud provider. However, the very benefits to cloud operations have a negative impact to as well: losing the control and hence the visibility of the day-to-day tasks for managing, monitoring, and maintaining the systems. This presents a significant security risk in terms of not having a handle on the activities.

This poses an important cloud security risk that customers need to address as it affects their operations in the inability to validate the effectiveness of security controls and postures related to storage, network instances, and policy triggers. It also undermines threat remediation on account of the lack of control over cloud assets. This has a cascading effect in the inability to run predictive analytics and utilization to identify anomalies related to potential security Indicators of Compromise (IOCs) Cloud practitioners need to be cognizant of the impact of the addition of cloud services to existing workflows so as to have a granular view of data paths across applications such that they can be tracked in conjunction with the services made available by the cloud providers to protect data breaches. This is an important consideration towards evaluating and determining the level of visibility and control that organizations have to better protect themselves.

A detailed understanding of cloud providers’ logging and monitoring features can be leveraged along with the workflows, policies, and rules related to the application lifecycle; this will enhance visibility through a continuous view of application and asset health.

Multi-Cloud workloads – To an increasing extent, organizations embrace a diversified approach of guarding core assets and data through the adoption of a multi-cloud strategy, which prevents the compiling of all resources into one basket. Superior in nature, a multi-cloud strategy enables organizations to align application needs for resiliency, optimization, and performance. A distributed set of services poses a challenge for attackers to launch a DDoS. Additionally, this model becomes favorable as a means to prevent vendor lock-ins. While this model constitutes a sound business strategy, it invariably presents a multitude of challenges for deriving consistent security policies across all the environments, thereby exposing users to potential risks of unidentifiable threats, and risking inconsistent security posture.

Not Inherent to Cloud – Traditionally, many SaaS applications haven’t been designed for operating in cloud environments. They must be re-designed and made cloud-native. Some cut corners and take shortcuts to make their applications cloud-ready and this results in unexplored native security flaws in applications.

Workload lifecycle management and threats – Deceivingly, the ease of staging and de-staging virtual appliances on a cloud, accompanied by a warmer embrace of opensource invites, can create tremendous risks that may compromise the security of systems. Notably, the following responsibilities carry great importance: identifying and mastering an approach for Identity & Access Management (IAM) pertaining to roles, users, key management, RBAC policies, etc. — this is in addition to policies concerning workloads, instances, and specific services-based triggers. Consequently, organizations must devise a well-rounded, automated approach to the lifecycle management of control, application, and the data path.

Third-party security – RSA 2020 enlightened participants about a significant theme: third-party security (which has garnered attention alongside the increased progression of breaches related to third-party integrations). Managing third-party risk isn’t just a good to have a strategy; it’s mandated by regulatory controls to incorporate consistent management of third-party integrations (factoring in the multipath data flows that today’s applications orchestrate). Depending on industry and data privacy laws, organizations must contractually mandate security, privacy measures, and controls for third-party integrations. Establishing secure controls demands a very sound and resilient third-party security policy baked into the configurations. It must not only enable organizations to automatically identify their overall posture related to organizational and regulatory mandates, but also have remediation measures available to fix inconsistencies.

Secure your APIs – Most security products protect data and access through the lifecycle of the data-consuming process and report to several partner tools through SOAP or Rest APIs. Moreover, myriad public APIs document their implementation and inner workings of these APIs to launch attacks through message intercepts, packet injection, or man-in-the-middle threats. Therefore, most of these negative outcomes are attributable to the bad design of API constructs.

Shift Left – Traditionally, statistical and dynamic analysis security tools employed in tandem enable engineering teams to identify security vulnerabilities in the application source early in the lifecycle and ensure conformance to organizational coding guidelines. However, they present a challenging proposition when effectively managing run-time issues associated with inspecting application behavior, as well as the context around it. Consequently, Run-Time Application (RASP) tools are gaining ground. The increased hygiene of building secure products and environments focuses on preemption than remediation after the occurrence of the incident gains prominence.

5G Security – The emergence of 5G will define a new paradigm in the edge-cloud infrastructure with newer industries and use cases while redefining existing Industry applications. Along with it, 5G brings additional threat vectors to be addressed. According to the 5G PPP organization (https://5g-ppp.eu/), over 7 trillion wireless devices will be connected, opening new possibilities for security vulnerabilities. With the explosion of the edge-cloud infrastructure, researchers at Purdue University have identified 11 new vulnerabilities related to 5G locations of endpoint devices, thereby raising the specter of endpoint device attacks. Not only does 5G bring faster speeds to accelerate data movement to the cloud, but also arrives with a foreign set of challenges.

Is System Randomization the answer to next-gen Cloud Security? As various Industries look at handling the diverse sources of security breaches at a revolutionary pace, the continuous prospect of protecting static infrastructures against dynamic and ever-mutating threat vectors begs the question of how to make our cloud infrastructures more dynamic to prevent vulnerability to attackers. Major advances in the field of system randomization related to the concept called Moving Target Defense (MTD) focuses on the aspect of randomizing workload policies to minimize the information gained by adversaries. Moving Target Defense (MTD) has shown promise to be an effective security mechanism to secure the cloud by changing the attack surface to make uncertainties for the attackers.

Randomizing system attributes including policies, passwords, configuration, runtime configurations, memory locations, and dynamic compilation provides some answers and presents an orthogonal perspective of looking at security defense.

As industries across the spectrum embrace digital transformation and sprint towards an agile way of managing their enterprise workloads, public clouds, and the associated complexity offer a new frontier with protecting organizations’ core assets.

This story first appeared in the June 2020 issue of CISO MAG. Subsribe now!

About the Authors
Raghunath Venkat Thummisi is a passionate product builder, Security practitioner and Evangelist focused on building the next generation Security Products for businesses who are experiencing a rapid change in their Security perimeter. Venkat’s experience is in building scalable Infrastructure Cloud Native SaaS Products with a focus on Security across the landscape from Core to Edge. In doing so, he has built strategic ecosystems of Customer and Channel partnerships. His experience spans big companies such as EMC, RSA, Trizetto as well as his current startup (Cannon Cyber). He is a contributing member of Forbes Technology Council and CISO MAG, he loves to be in the midst of action advising emerging startups to foster innovation.

Disclaimer

The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same. 

APT32 Hackers Target Vietnamese Human Rights Defenders in Spyware Attacks

Vietnam

APT32, an infamous Vietnam-backed hacking group, is suspected to be behind a cyber campaign of spyware attacks targeting Vietnamese Human Rights Defenders (HRDs) between February 2018 and November 2020, an investigation by Amnesty Tech revealed.

Also known as Ocean Lotus and APT-C-00, the hacking group sent phishing emails to two popular Vietnamese human rights defenders, one based in Germany and another in the Philippines. Reportedly, the spyware used by APT32 operators allowed them to compromise systems, read and write victims’ documents, deploy malware, and monitor their victims’ activities.

“These latest attacks by Ocean Lotus highlight the repression Vietnamese activists at home and abroad face for standing up for human rights. This unlawful surveillance violates the right to privacy and stifles freedom of expression. The Vietnamese government must carry out an independent investigation. Any refusal to do so will only increase suspicions that the government is complicit in the Ocean Lotus attacks,” said Likhita Banerji, a researcher at Amnesty Tech.

The investigation also found that Ocean Lotus is linked to numerous cyberattacks since 2013, targeting the public, private, and civil society organizations in Vietnam. The group has enough capabilities including several variants of Mac OS spyware, Android spyware, and Windows spyware.

How to defend against Ocean Lotus

Amnesty Tech recommended certain security measures to defend against threats associated with Ocean Lotus:

  • Be careful when receiving emails with attachments or links. If you did not expect to receive the email or do not know the sender, do not click on the links in the email or open attached or shared files.
  • You should pay particularly close attention to shortened links, especially on social media.
  • Be careful when a website or application asks for access to your Google account. If it asks to access your emails (read, send, delete, and manage your email), do not accept unless you have full trust in the application getting access to it.
  • Enable two-factor authentication (2FA) on all your accounts, especially on your email.
  • Make sure your operating system and applications are up to date. Avoid using pirated system software and office tools, as serious damage can be caused to your PC by malware and spyware included within the copy of the pirated software you receive.

IBM Fixes Critical Vulnerabilities in Java Runtime, Planning Analytics Workspace

IBM released security fixes to patch high-and medium-severity vulnerabilities impacting its enterprise software solutions. The tech giant published a set of security advisories to address multiple vulnerabilities in IBM Java Runtime, IBM Planning Analytics Workspace, and IBM Kenexa LMS On-Premise.

The first advisory released fixes for two critical vulnerabilities CVE-2020-14782 and CVE-2020-27221 in IBM Runtime Environment Java 7 and 8 respectively, which are used by IBM Integration Designer enterprise software. IBM Integration Designer is used for end-to-end integration in service-oriented architecture (SOA).

  • CVE-2020-14782 is an unspecified vulnerability in Java SE related to the Libraries component that could allow an unauthenticated attacker to cause no confidentiality impact, low integrity impact, and no availability impact by compromising Java SE.
  • CVE-2020-27221 is a stack-based buffer overflow vulnerability in Eclipse OpenJ9 and could allow a remote attacker to execute arbitrary code on the system or cause the application to crash.

Affected Products include Integration Designer versions 8.5.7, 19.0.0.2, 20.0.0.1, and 20.0.0.2

Fixes:

IBM Integration Designer 8.5.7

IBM Integration Designer 19.0.0.2

IBM Integration Designer 20.0.0.1

IBM Integration Designer 20.0.0.2

The second advisory addresses bugs in IBM’s collaboration and management planning software IBM Planning Analytics Workspace. In total, the company resolved five vulnerabilities  CVE-2020-8201, CVE-2020-8251, CVE-2020-8252, CVE-2020-25649, and CVE-2020-4953 that impact the Planning Analytics software. If exploited, the vulnerabilities could allow an attacker to poison the web cache, bypass web application firewall protection, and conduct XSS attacks.

The affected product includes IBM Planning Analytics 2.0 Local and Cloud

Fix:

The recommended solution is to apply the patch as soon as possible.

IBM also described vulnerabilities affecting IBM’s enterprise learning management system IBM Kenexa LMS On-Premise. The company fixed five low-impact vulnerabilities which could allow unauthorized hackers to launch denial of service (DDoS) attacks.

The affected product includes IBM Kenexa LMS On-Premise of LMS 6.1 and lower versions.

Fix:

IBM recommended users to update to the latest release.

Russian Networks Accused of Carrying Out Massive Cyberattack on Ukraine

Ukraine accused Russia for Cyberattacks

A “Second Cold War” of sorts has been brewing between Ukraine and Russia ever since the latter annexed the Republic of Crimea in 2014 and subsequently also invaded Ukraine’s territory through Donbass. Russia was pushed back from Ukrainian soil, but Crimea became the 84th Federal Subject of Russia. The war has cost Ukraine more than 13,000 lives, including civilians, military personnel, and the 298 passengers and crew members who died when the Malaysia Airlines Flight MH17 was shot down on July 17, 2014 en-route to Kuala Lumpur from Amsterdam. However, this cold war has now entered cyberspace with Ukraine’s National Security and Defence Council accusing unnamed Russian internet networks of targeting multiple Ukrainian security and defense websites.

Why Ukraine accused Russia of the recent cyberattacks

Moscow has always denied Ukraine’s previous claims of targeted cyberattacks, but Ukraine persists that the former is using “hybrid war” tactics against their country. The recent wave of attacks, which was triggered on February 18, 2021, was specifically targeted towards Ukraine’s security services, other governmental offices, the Defence Council, and much more strategic in nature enterprises.

Related News:

Binance and Ukraine Police Arrest Crypto Hackers in a “Bulletproof Exchanger Project”

The Council stated that distributed-denial-of-services (DDoS) attacks were used to intrude and infect vulnerable backend servers of their targets with a virus. A formal statement from the council said, “It was revealed that addresses belonging to certain Russian traffic networks were the source of these coordinated attacks.” The Council however did not mention the success, impact, or the exact names of the attackers who attempted intrusion.

Ukraine’s Largest Commercial Bank Breached

Call it a connection or a mere coincidence, but Ukraine’s largest commercial bank – PrivatBank – suffered a data breach earlier in the month that affected nearly 40 million of its customers. The breach was discovered when an unknown cybercriminal was selling the PrivatBank’s hacked database on an underground forum for a mere $3,400 worth of Bitcoins. If confirmed, the data breach can go down as one of the worst in Ukraine’s history as it affects nearly 93% of the country’s population which is just over 44 million. Read the complete story here.

Related News:

Ukraine Police Busts “Megabreach” Cybercriminal, Sanix