Home Blog Page 111

Oxfam Australia Confirms Data Breached During Cyberattack

Remote Access Scams

Oxfam Australia, a non-profit charity working towards the eradication of poverty around the globe through humanitarian services, recently reported it was investigating a “data incident” which potentially affected 1.7 million registered supporters. The incident first came to light on January 27, 2021, following which a prompt investigation was launched with the help of forensic IT experts.

Evidence of Data Breach Confirmed

Post the breach, Oxfam Australia notified industry regulators, including the Office of the Australian Information Commissioner (OAIC) and the Australian Cyber Security Centre (ACSC). The thorough forensic investigation that began in January, ended on February 23, 2021, which confirmed that “unlawful” access to its supporters’ data did take place on January 20, 2021. As per the forensic analysis, the following PII data were accessed during the data breach:

  • Names and addresses
  • Dates of birth (D.O.B) and gender
  • Emails and phone numbers
  • Donation history (in some cases)
  • And for a limited group of supporters, the database contained additional information, for which Oxfam Australia is directly contacting these supporters to inform them of the specific types of information possibly compromised

According to Oxfam’s official update, no account passwords of its supporters were compromised but the bank name, account number, and BSB of a small group of individuals could have been accessed. Thus, to avoid scams like identity theft, phishing, and smishing, Oxfam has recommended its supporters to reset the passwords and look out for any malicious activities related to the data which was compromised. To get further advice on avoiding such scams, Oxfam Australia has asked supporters to refer to the suggestions posted on www.scamwatch.gov.au.

Oxfam Australia has maintained high transparency and abided by the widely accepted NIST framework in the current scenario. From the beginning, it has informed its users about the potential data breach, conducted a thorough forensic investigation, and then released its findings confirming the data breach occurrence. However, it has not mentioned the exact number of people affected.

Justifying this stance, Oxfam said,

Throughout our investigation, the privacy and protection of our supporters has been our top priority. In the interests of ensuring the ongoing security of our database and our supporters’ privacy and protection and to reduce the risk of attempts by scammers to target Oxfam supporters, we are not releasing details of the number of people who may have been impacted.

Related News:

Ripples of the Accellion Hack Reach Australia; QIMR Berghofer Confirms ‘Likely’ Data Breach

Australian Securities and Investment Commission Hit by a Cyberattack

Russian Hacker Misused Medal of Honor Holders’ Information

Nobelium

Any organization or individual may become a target for cybercriminals. From children to senior citizens, threat actors exploit all kinds of information to their advantage. According to an ongoing investigation, a Russian attacker allegedly stole the personal information of the U.S. Congressional Medal of Honor holders.

The Congressional Medal of Honor award is the U.S. government’s highest and most prestigious military decoration. It was found that the threat actor targeted 22 of 75 living Congressional Medal of Honor recipients and misused their data for fraudulent transactions.

The attacker created a fresh line of credits using the stolen identities to make purchases at the Air Force Exchange Service (AAFES). The fraudulent purchases include luxury watches and Apple products worth tens of thousands of dollars. The hacker allegedly obtained $54,530.92 via 50 separate fraudulent transactions.

“The U.S. Secret Service is currently investigating a matter in which the personally identifiable information (PII) of 22 of 75 living Congressional Medal of Honor recipients was used to create fraudulent lines of credit at the Army and Air Force Exchange Service (AAFES) to purchase items utilizing the newly created fraudulent lines of credit, all in violation of 18 U.S.C. § 1029 (access device fraud),” an affidavit from a Special Agent Matthew O’Neill read.

An Intelligent Device Fraud

The perpetrator shipped the fraudulently obtained goods to various commercial reshipping companies, which were eventually shipped to different locations across Russia. “An individual re-shipper named Kiril Motorin, located in Gaithersburg, MD advised that he became a re-shipper after responding to an employment advertisement on a website used by Russians living in the Washington, DC, area. Motorin provided me e-mails, sent to him from [email protected], which provided Motorin instructions such as where to send the merchandise and on how Motorin would be paid for re-shipping the merchandise,” O’Neill added.

Indian Vaccine Makers and Pharma Companies Attacked This Week: Cyfirma Research

India has a definite advantage today as it produces 60% of the world’s vaccines. Even developed countries are not producing enough for their own consumption and are reaching out to India for help. The latest country to do so is Canada. India has also distributed millions of doses to friendly countries, free-of-cost. Amid this, India’s lead in vaccine R&D and vaccine production has caught the attention of state-sponsored threat actor groups. Goldman Sachs-backed Cyfirma, a threat discovery and cybersecurity platform company headquartered in Singapore and Tokyo, notes that, in the last four days there have been a series of cyberattacks on pharmaceutical and healthcare companies in India. India has two main vaccine producers, SII (Serum Institute of India) and Bharat Biocon. According to a press release issued to Reuters this week, Cyfirma says cybercriminals from Russia, China, North Korea, and the Middle East have been targeting pharmaceutical companies, hospitals, and government health departments to carry out various malicious activities.

In the Reuters report, Kumar Ritesh, Chief Executive Officer of Cyfirma said, “The real motivation here is actually exfiltrating intellectual property and getting a competitive advantage over Indian pharmaceutical companies.” Kumar Ritesh was formerly a top cyber official with the British foreign intelligence agency, MI6.

He said APT10 was actively targeting SII, which is making the AstraZeneca vaccine for many countries, and will soon start bulk-manufacturing Novavax shots.

The researchers have observed that the hacking groups are aiming to steal COVID-19 vaccine-related data, which is highly sensitive in nature. This includes vaccine research, medical composition, clinical trials information, logistics and distribution plans.

“Our researchers have noticed an increased interest amongst state actors in India’s vaccine R&D. India was lagging in the COVID-19 vaccine research and started to catch up in the last couple of months. This has drawn the attention of Chinese state-sponsored threat actors whose intentions are to tarnish India’s reputation as well as to disrupt her national vaccination effort,” said Cyfirma.

While the Chinese government has vehemently denied these attacks, Cyfirma has substantial proof, by way of traced IP addresses, indicators of compromise, event logs, and other forensics data.

It is also sharing this data with Indian authorities like CERT-In. Cyfirma is also advising CERT-In to alert the targeted companies and take immediate measures to mitigate the attacks.

What is the motivation for cyberattacks on pharma companies?

According to Cyfirma, the motivation for such cyberattacks varies slightly among the nations identified by Cyfirma. Russian state-sponsored threat actors are seeking a combination of geopolitical gain as well as financial rewards while Korean threat groups are focused on financial gain.

And of course, the Chinese threat actors have multiple reasons. Following reports in the media, we see that Chinese hackers are not just after India’s R&D data on vaccines, but also intend to disrupt supply chains. India stepped up its vaccination drive on March 1, when it began administering vaccines for all above 60 years of age and those with comorbidities.

But Chinese state-sponsored actors have also been attacking other sectors in India, such as power and utilities. Research from security firm Recorded Future found a China-linked threat actors group dubbed RedEcho, targeting 12 Indian organizations, 10 of which are in the power sector. Recorded Future’s threat research team Insikt Group uncovered a subset of the servers that share some common tactics, techniques, and procedures (TTPs) with several previously reported Chinese state-sponsored groups.

Read the full story here.

It is being speculated whether the massive power outage in the Indian city of Mumbai last October, could have been caused by a cyberattack on the power grid. This attack was first reported in The New York Times. RK Singh, Minister of State for Power ruled out sabotage from China or Pakistan-supported hackers. A former energy minister said the power grid does not have such a sophisticated network and also ruled out hacking. However, evidence has been found about cyberattacks on India’s northern and southern load despatch centers, though the malware could not reach the controlling system.

The train system, which is considered Mumbai’s lifeline, was impacted by the power outage. Stock exchange trading was momentarily impacted, but many businesses could not operate for a few hours due to power loss.

But India is not the only nation under attack. Nations like the U.K., U.S. Japan, Australia, Italy, Spain, Germany, Brazil, South Korea, Taiwan, Mexico and others have also been targeted. The adversaries are after sensitive research data on vaccine trials, either for financial gain or business advantage. The impact of such attacks is reputation damage, supply chain disruption, and weakening of the economy.

What are the Target assets?

  • Pharma companies who are investing in medical research, clinical trials, and vaccine production
  • Vaccine supply chain, national vaccination campaign, individual and personal information
  • Government agencies in charge of approving vaccine, medicine, and related appliance
  • Vaccine development and implementation tracking systems
  • Clinical trial information
  • Hospital operating details, employee and patient information
  • Government health department and demographic details
  • Medical devices and appliance design and architecture

Who’s behind the cyberattacks?

CYFIRMA researchers have observed 15 active hacking campaigns (7 Russian groups, 4 Chinese, 3 Korean, 1 Iranian).

RELATED STORY

Chinese Hacking Group “RedEcho” Targets Indian Power Sector

Malaysia Airlines Discloses Data Breach that Lasted for 9 Years

Bangkok Airways

Most users have lately become cautious about sharing their personal information with airlines due to increasing security breaches. And Malaysia Airlines is the latest victim of a security incident that lasted for over nine years. The security breach affected the private data of members of its frequent flyer program, Enrich.

According to a report, the data breach occurred at a third-party IT service provider between March 2010 and June 2019. However, Malaysia Airlines clarified that the incident did not affect its IT infrastructure and network systems.

The information exposed includes user names, date of birth, gender, contact details, Enrich card number, status, and tier-level. However, flight itineraries, reservations, ticketing, ID card, and payment card were not exposed in the breach.

While there is no evidence that the information exposed in the breach was misused by attackers, the carrier recommended all its Enrich members change their passwords for further protection.

What Malaysia Airlines Says…

Though Malaysia Airlines did not make any public announcement on the security breach, it did confirm the incident on social media handles while responding to customers.

The Airlines did not disclose the incident on its official website citing it as a minor incident. But considering the fact that the breach lasted for nine years, it certainly poses a serious threat to its customers.

Cyberattacks on Airlines Soar!

Keeping the growing cyberattacks on the Aviation industry in mind, ResearchAndMarkets.com released a report titled “Aviation Cybersecurity Market – Growth, Trends, and Forecast (2019 – 2024)” which indicated that the aviation cybersecurity market is expected to register a CAGR of around 11% during the forecast period of 2019-2024. The report discusses cybersecurity in the aviation sector by solution and application spanning from airline management, air-cargo management, air traffic control management, and airport management.

Key excerpts from the report:

  • With the advancement of technology and connectivity, the market has become prone and vulnerable to cyber-attacks of malicious malware activities targeting the aviation sector.
  • Detection and prevention are the most sought-after solution as these threats are becoming more stealth with every attack. Owing to such instances the corporates are trying to utilize the services of domain experts thus, creating an opportunity for the market.
  • A key driver for the market is the need for technological advancements in order to prevent the aviation sector IT infrastructure and networks from cyber-attacks. Further, as the aerospace sector moves toward the autonomy of spaceflight and is investing billions in developing aviation technologies, the need to protect the infrastructure becomes critical.

“I think it’s important to remain pragmatic about foreign threats”

Rob Wiggan

Having a matured cybersecurity strategy from the ground up is pertinent for any enterprise to grow. This approach ensures an easy-to-maintain, long-term security posture, and builds a secure base for the applications. Apart from it, a matured cybersecurity strategy also translates to better future investments and initiatives.

In this exclusive interview with Augustin Kurian from CISO MAG, Rob Wiggan, Associate Director, Information Security at the Queensland University of Technology, talks about cybersecurity strategies that businesses must have. He also talks about the role of CISOs, understanding the responsibilities, and shares his tips for securing boardroom investment.

Wiggan is an accomplished IT professional with over 30 years of industry experience, specializing in providing strategic leadership to deliver mature information security programs and manage secure information security operations within complex working environments —  including banking, utilities, and higher education.

Since early 2018, he has held the role of Associate Director, Information Security at the Queensland University of Technology, where he is responsible for information security across all the business streams of Research, Learning and Teaching, and corporate applications.

From a CISO’s standpoint, how important is it to build a mature cybersecurity strategy from the ground up? With the surge in attacks during the lockdown, what were the newer and additional responsibilities that fell on the shoulders of the CISOs?

The CISO needs to take ownership of the Cyber Security Strategy early in their tenure. They should then aim to develop a mature strategy that defines the priorities and the focus areas for both future investments and initiatives. Without a mature strategy, important momentum could be lost by consuming effort in the wrong areas. It is important to stay focused on the strategic goals and ensure the ability to continually articulate progress and demonstrate benefits to the senior executives and the relevant board committees.

In our case, the lockdown coincided with our usual annual peak of security incidents. This meant that we spent a lot more time identifying the departures from the normal patterns and implementing new methods of informing the senior executive more regularly of the overarching trends. Interestingly, although there was an increase in the number of incidents during the early weeks of the lockdown, the types of incidents were consistent for this time of year, with the only material change being that many of the cybercriminal actors pivoted to using COVID-themed lures. After the first couple of weeks, the incident volumes returned to normal levels.

Additionally, there was increased internal sensitivity about the increased risk of large numbers of staff working remotely. It was considered that a material increase in risk could only be quantified if we took the view that nobody worked at home prior to the COVID-lockdown. While we added some additional VPN capacity due to the increase in remote access users and implemented heightened vigilance on our detection controls, there was no appreciable increase in incidents once that initial period passed.


For current and aspiring CISOs, understanding the responsibilities before they step into the role can save them from many issues, including personal liability and possible lawsuits. Do you think there is enough preparedness?  

The CISO role needs to be recognized as a key business role. Many CISOs come into the role of other disciplines that are not necessarily from security or governance backgrounds. Sometimes they can either lack the knowledge or be too technically-focused to understand the key accountabilities of the role. Generally, they are often unprepared for reporting and governance that is required. I think it is important that, as an industry, we must ensure that we are building a collaborative community that can mentor new CISOs into their role, to avoid some of the pitfalls of inexperience.


Apart from cyber warfare, and cyber espionage from state-sponsored actors, what are the other types of foreign interference that you have observed? Can you rank these from the most dangerous to the least dangerous ones?  

I think it is important to remain pragmatic about foreign threats. While I acknowledge that there is ample evidence to confirm that foreign actors are continuing to target weaknesses in infrastructure and processes, our experience is that the overwhelming majority of cyber incidents are still attributed to cybercriminals looking to gain credentials and access for financial gain. It is also important to note that foreign ‘influence’ is a normal activity conducted by governments of all countries. Foreign interference occurs when actors employ other methods to coerce or trick users into exposing systems. These methods can operate outside the realms of cyberattacks and can include bullying, coercion, user profiling as well as standard data exfiltration.


What is your take on Australia’s News Media Bargaining Code? Do you think Google and Facebook must pay news publishers for hosting their news links and snippets on their platforms?    

In recent years, the Australian government has implemented several pieces of legislation that have impacted technology industries. The News Media Bargaining code is primarily designed to protect traditional media companies, but I believe that it does not adequately consider different ways in which different platforms use and distribute content. That aside though, the recent decision by Facebook to block news content was deeply unpopular with the Australian public and was likely to create more imbalance in the publication of misinformation. I have an underlying concern that Australia lacks the media diversity to have a transparent public conversation, and I note that the tech companies are now negotiating payment arrangements with the Australian news providers. I think that it is important that both media organizations and tech companies continue to coexist in the Australian market.


Several pieces of research have pointed out that cybersecurity investment decisions are still more about insurance than about any desire to lead the field. Don’t you think this approach limits the industry’s ability to keep pace with cybercriminals?  

This is a difficult conundrum because corporate cybersecurity functions need to be able to prioritize initiatives and typically risk is used as a lever to assist with the prioritization of initiatives. As a result, the prioritization decisions are then largely driven purely by risk reduction. It is important that we still consider innovative approaches to complex problems. This is where a well-considered and thought-out Cyber Security Strategy can help frame some of the decisions. The challenge remains to enable our teams to experiment and “fail fast” when resourcing is so constrained and much of the available capacity is consumed in the BAU workload. The cybercriminals continue to develop new tools, tactics, and procedures at a pace while security practitioners can continue to take a more cautious risk-based approach to ensure that business continuity is not impacted.

What are your best tips for CISOs to secure Boardroom investment?   

In my experience, the best way to gain investment is by establishing as much transparency as possible. It is also important to understand that while a report from a consultancy appears to have the same advice that you may have been providing to the Board, it is that independent view that is likely to cut through. Secondly, Boards will always respond to issues articulated in risk terms because their primary responsibility is to provide oversight that organizations’ risks are being managed. Failure to do this can result in serious consequences for individual Board members, so expressing issues in risk terms appeals to their expertise. Finally, it is important not to go to the Board with a list of problems and a request for a lot of funding. However, if you go to the Board with a series of key risks and some reasonable steps, you can take to either, use existing controls, or implement some new cost-effective controls, you are more likely to succeed in getting the funding you need. I would also add that I don’t think there is any Cyber Security function anywhere in the world that is resourced to the degree that the CISO thinks it should be. Be very clear about what you can and cannot do and never over-promise.

Augustin KurianAbout the Interviewer

Augustin Kurian is part of the editorial team at CISO MAG and writes interviews and features.

Facebook Settles Photo-Tagging Class-action Lawsuit for $650 Mn

France Fines Facebook and Google,Russia fines Google, Meta heavily New York City Law Department Hit by a Cyberattack

In one of the largest data violation lawsuit settlements, Facebook has agreed to pay $650 million to users in Illinois who indicted the social media giant for using photo face-tagging and biometric information without their consent. Nearly 1.6 million users in the Prairie State filed a class-action lawsuit against Facebook in April 2015, for violating the Illinois privacy law. The claimants stated that Facebook used its facial-recognition technology to unauthorizedly scan and collect users’ photos from their profiles.

The U.S. District Judge James Donato approved the settlement deal in a class-action lawsuit and as a result, the claimants will receive at least $345 as compensation.

“It is one of the largest settlements ever for a privacy violation, and it will put at least $345 into the hands of every class member interested in being compensated. At the Court’s request, the parties jointly developed an innovative notice and claims procedure that generated an impressive claims rate. The settlement attracted widespread support from the class and drew only three objections out of millions of class members,” the lawsuit said.

Responding to the settlement, Facebook said, “We are pleased to have settled so we can move past this matter, which is in the best interest of our community and our shareholders.”

Facebook’s Timeline of Lawsuits

Facebook has already settled multiple fines imposed on it for various data violations. Last year, Brazil’s court fined Facebook for the misuse of personal data belonging to nearly half a million Brazilians during political campaigns. According to reports, a fine of 6.6 million Reais (US$ 1.6 million) was issued by the Ministry of Justice and Public Security of Brazil for the data misuse scandal by Facebook and consultancy firm Cambridge Analytica. It’s said that the social networking giant collected private data of around 87 million Facebook users via a personality quiz app – This Is Your Digital Life.

solarwinds123: Did a Weak Password Result in SolarWinds Hack?

SolarWinds Microsoft

As the investigations on the infamous SolarWinds supply chain attacks are ongoing, the top management of the company blamed an intern for the password “solarwinds123” lapse, which is believed to be the main cause of the recent chain of cyberattacks. Sources suggest that the password was publicly accessible via a GitHub repository since June 17, 2018, before it was addressed on November 22, 2019, after being reported by a security researcher.

As part of the ongoing investigation, several U.S. lawmakers questioned the Texas-based software firm on the password issue in a joint hearing by the official House Oversight and Homeland Securities committees. In his hearing, Sudhakar Ramakrishna, CEO of SolarWinds, confirmed that the password has been in use as early as 2017.

“I believe that was a password that an intern used on one of his servers back in 2017, which was reported to our security team, and it was immediately removed. That related to a mistake that an intern made, and they violated our password policies, and they posted that password on their own private GitHub account. As soon as it was identified and brought to the attention of my security team, they took that down,” Ramakrishna said in the hearing.

“I’ve got a stronger password than ‘solarwinds123’ to stop my kids from watching too much YouTube on their iPad. You and your company were supposed to be preventing the Russians from reading Defense Department emails,” said Representative Katie Porter of California.

Till now over 18,000 high-profile customers including multiple U.S. government agencies and tech companies like Microsoft, FireEye, Boeing, and many others have been affected by the SolarWinds hack. The White House acknowledged that a Russian state-sponsored group known as the Cozy Bear or APT 29 carried out the targeted cyberattacks on several U.S. government agencies through a vulnerability in its IT management software called SolarWinds Orion. It appears that a significant amount of investment was made to ensure that the code was properly inserted and that the presence of malware remained undetected in their build environment.

COVIDGuardian: A Guardian Angel for COVID-19 Contact Tracing Apps

COVIDGuardian, Covid-19 contact tracing app assessment tool

People around the globe have always been apprehensive about the implementation and usage of the COVID-19 contact tracing apps. They feared that cybercriminals could target and misuse their personal data through them. Their worst nightmares came true in September 2020, when a study from Intertrust stated that almost 85% of COVID-19 contact tracing apps leak data. However, things are about to change as researchers from Queen Mary University of London (QMUL) have developed an assessment tool – called COVIDGuardian – which will help analyze the security and privacy gaps in these COVID-19 contact tracing apps.

COVIDGuardian Assessment Tool

With the sudden uncontrollable spread of the COVID-19 pandemic, the contact tracing apps were hurriedly developed by governments around the globe on a constricted timeline. This meant that adhering to hardened security and privacy testing protocols would not have been possible, given the short release timelines. Taking these anomalies into consideration, researchers at QMUL decided to develop an assessment tool that would find potential threats such as malware, embedded trackers, and private information leakage through these contact tracing apps.

Related News:

Almost Half of U.K.’s Population Fears Abuse of NHSX COVID-19 Tracing App

Dr. Gareth Tyson, Senior Lecturer at the Queen Mary University of London said, “With the pandemic, there was a rapid need for contact tracing apps to support efforts to control the spread of Covid-19. Unsurprisingly, we found that this had resulted in some relatively mainstream security bugs being introduced worldwide. Some of the most common risks are related to the use of out-of-date cryptographic algorithms and the storage of sensitive information in plain text formats that could be read by potential attackers.

Our work is helping developers address these problems. Through COVIDGuardian we’ve produced a tool that can be used by developers to discover and fix potential weaknesses in their apps and share guidelines that will help to ensure user privacy and security is maintained.”

During their study of determining COVIDGuardian’s efficacy, 40 COVID-19 contact tracing apps from around the globe were assessed. The study showed the following results:

  • 5% of the apps use at least one insecure cryptographic algorithm.
  • Three-quarters of apps contained at least one tracker that reports information to third parties such as Facebook Analytics or Google Firebase.
  • Most of the 40 apps analyzed were malware-free, but the Kyrgyzstan app going by the name “Stop COVID-19 KG” was discovered to have malware.

Additionally, the researchers performed a survey on more than 370 individuals to find the likelihood of them using a COVID-19 contact tracing app. Not so surprisingly, they found that the biggest impact on whether individuals would use the app or not depended upon the privacy and accuracy of these contact tracing apps.

The research titled “An Empirical Assessment of Global COVID-19 Contact Tracing Applications” will be presented soon at the International Conference on Software Engineering, which will be held between May 23-29, 2021. However, a copy of this paper can be already found here.

Related News:

In a Sea of COVID-19 Tracer Apps Where Does Apple-Google Stand?

Don’t use these Android VPNs. They Leak Your Credentials!

Fortinet VPN, VPN, VPN devices

VPN applications that are meant to secure users’ privacy online are now found to be exposing their sensitive information to third parties. Security experts from Cybernews stated that cybercriminals are selling over 21 million users’ records on a hacking forum. It was found that they are trading three databases that contain user credentials and device data from three Android Virtual Private Network (VPN) services – SuperVPN (with 100,000,000+ installs on Play Store), GeckoVPN (10,000,000+ installs), and ChatVPN (50,000+ installs).

The other database contains information including users’ email addresses, usernames, full names, country names, randomly generated password strings, payment-related data, premium member status, and expiration date, along with users’ device serial numbers, phone types and manufacturers, device IDs, and device IMSI numbers.

“The threat actor claims that the data has been exfiltrated from publicly available databases that were left vulnerable by the VPN providers due to developers leaving default database credentials in use,” Cybernews said.

Threats from Unsecured VPNs

The primary reason for using a VPN is to improve a user’s data privacy and security on the internet. VPNs provide a secure connection for users when joining another network online. It also changes your IP address and location, making your browsing activity safe and private from threat actors.

Cybernews claims that the three VPN providers are likely logging in for more information about their users than required. It also suspects that cybercriminals might have gained full remote access to the VPN servers.

“If true, this is an incredible blow to user security and privacy on the part of SuperVPN, GeckoVPN, and ChatVPN. And, in the case of SuperVPN, this blow is not the first. With deeply sensitive device information such as device serial numbers, IDs, and IMSI numbers in hand, threat actors that have access to the data contained on the compromised VPN servers can get hold of that data and carry out malicious activities such as man-in-the-middle attacks and more,” Cybernews added.

SuperVPN – The Old Culprit

Various cybersecurity experts reported the issues with using SuperVPN.

The VPN has critical vulnerabilities and researchers deemed it dangerous.  Google removed the SuperVPN app on April 7, 2020, from its Google Play Store. CISO MAG also advises against using free and unknown VPN applications. It’s a safe bet to use established and paid VPNs.

BIoTs can alleviate security concerns for both owners and tenants

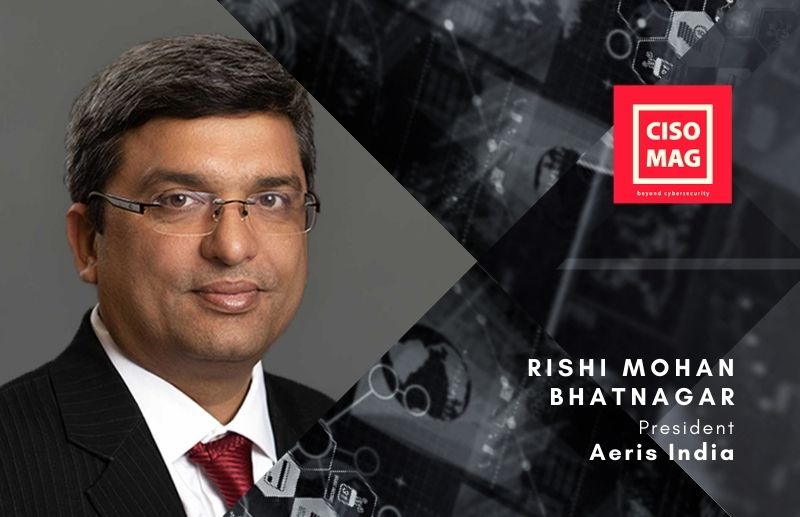
Dr. Rishi Mohan Bhatnagar is an international speaker and thought leader in the Internet of Things and digital space. He co-authored the book “Enterprise IoT” along with a team from Bosch. He is the recipient of the “ET Now Business Leader of the Year 2019,” Voice&Data “Leadership Recognition Award” – India 2019, Indian ISV “IoT CEO of the Year 2018” and BTVI “Business Leader of the Year 2018.” Currently, as President of Aeris Communications India Private Ltd. (100 % subsidiary of the privately held, Silicon Valley headquartered Aeris Communications Inc., pioneers in the m2m/ IoT business since 1992), Dr. Bhatnagar is leading the Aeris business in the Indian subcontinent, MEA, and the APAC region.

In an exclusive interview with Augustin Kurian from CISO MAG, Bhatnagar talks about his journey, the future of Building the Internet of Things, integrating IoT with farming in India, and also addresses the threats and concerns surrounding 5G.

Edited excerpts from the interview follow:

It has been nearly three decades since the inception of Aeris. Aeris evolved from being a cellular network to now a world-renowned IoT enabler. How has your journey with Aeris been and what were the key milestones for the company?

Aeris was founded in 1992 and is a cellular network designed and built exclusively for machines. Because it was made for machines, Aeris delivers the most reliable, flexible, and efficient global cellular network for M2M data transmission available today. The growth of Aeris mirrors the development and growth of M2M communications and the Internet of Things (IoT). It has operational reach in over 180 countries and has offices in the Americas (Chicago & San Jose), Europe (U.K.), and India (Delhi NCR). We announced our joint venture with Softbank in Japan in 2016 known as Aeris Japan K.K., to provide IoT and telematics services globally using the Aeris IoT solutions platform. We are also part of Ventic LLC, a joint venture that is the result of a long-term commitment between Volkswagen and Aeris in the development and operations of connected vehicle platform technologies.

Today we have 14 million devices managed on our IoT Platform, worldwide. Aeris is at the forefront of the technology industry, building networks and applications to enable Fortune 500 clients to fundamentally improve their businesses. We offer global connectivity for machines as well as IoT solutions and services to multiple sectors which include Automotive, Finance & Insurance, Telecom, Utilities, Manufacturing, Agriculture, and more. From telematics to medical devices to remote machines, Aeris’ customers enjoy solutions tuned for high performance and mission-critical reliability. We entered the Indian market in 2016, and with our joint go to market engagements, we have successfully established an end-to-end IoT ecosystem, cracked the IoT monetization code and today we provide flexible business and commercial models for IoT, for the price-conscious markets, going beyond India, and, creating our presence in SAARC, APAC, Middle East and the APAC region.

With no hardware choke points and several small-cell antennas relying on 5G’s Dynamic Spectrum Sharing feature enabling multiple data streams to share bandwidth partitioned in slices that may each introduce cyber risk, do you feel with 5G technology comes to the emergence of tens of billions of smart devices susceptible to cyberthreats related to IoT networks?

5G comes with the promise of download speeds of up to 10 times faster and there is a huge concern over this from a security perspective as faster speeds may present an opportunity for hackers to target more devices and launch bigger cyberattacks.

But let’s not forget that we witnessed similar concerns and threats when the Internet was growing and maturing to gain the critical mass and adoption. Similar concerns were raised when cloud technology was at its hype. Therefore, it is quite natural that any new and advanced technology will bring with it a gamut of new security challenges. We need to remind ourselves that the security of the “thing” is only as secure as the network in which it resides. This includes the people, processes, and technologies involved in its development and delivery. Managing the security of 5G networks and services requires a new approach, where security is an integral part of the end-to-end architecture and ‘security by design’ is a must.

You have spoken about integrating IoT with agriculture to revolutionize the landscape. What is the feasibility of that? What is your response to the apprehensions surrounding cyberthreats that may arise to unsuspecting farmers?

For IoT deployments, irrespective of the industry vertical whether it is manufacturing or finance or agriculture or even a social sector engagement, security should never be an afterthought.

Keeping connected devices and their data safe starts during device design and at device provisioning and deployment. Deploying IoT programs at scale calls for simplifying device onboarding processes and reducing manual steps. A common goal is to set up each deployed device to immediately be able to communicate over networks to the right destination in the cloud. But doing that securely requires examining all the steps in the process and setting the right parameters for those devices.
Farmers adopting connected technology can tie up with IoT solution and service providers who allow them to securely provision and connect their devices to the cloud with minimum (near zero) effort and help them do this securely with identity and access management best practices being deployed during the entire device deployment lifecycle.

When it comes to the concept of Building Internet of Things (BIoT), it is often said that immaturity and poor definition of the concept are a few of the biggest risks in smart buildings. Do you think there is still a need for a more comprehensive understanding of threats posed on BIoT?

The Commercial Real Estate (CRE) industry is perhaps uniquely positioned to implement the latest technologies using IoT-enabled building management systems (BMS) or BIoT to make building performance more efficient and also use sensor-generated data to enhance building user experience. The value created from the information generated by BIoT has the potential to widen the lens on value creation beyond location, and associated benefits of low-hanging fruit such as cost savings and operational efficiency through improved energy management increased level of efficiency with enhanced building performance and effectiveness that could distinguish buildings within a marketplace from a desirability and profitability standpoint.

BIoTs can alleviate security concerns for both owners and tenants. Real-time monitoring can bolster internal security, and specialized weather sensors provide advance warnings of adverse weather events. As the frequency and severity of hurricanes, floods, and tornadoes increase under a changing climate, so does the value of disaster preparedness and resilience.

From a security point of view, CRE companies can minimize the security and privacy risk that IoT technology presents by taking several measures mentioned below to become secure, vigilant, and resilient:

  • Use purpose-built BIoT devices or addons, rather than generic IoT solutions.
  • Define clear responsibilities for the players in the ecosystem and institutionalize data governance.
  • Selection of secure communication protocol is required for building automation systems, which can help integrate with enterprise management solutions.

When all these systems are unified to work together, we have a resilient Building Internet of Things (BIoT). In the security industry, the integration of the three major segments has been successful to a large extent. Physical Security Management Systems (PSIM) have been used for interoperability between safety & security systems including fire detection, extinguishing, evacuation, mass notification in both large and small projects.

With COVID-19 and employees working from home, there are even bigger threats from the IoT landscape. What are your thoughts surrounding that?

It is true that while the underlying network is relatively easy to secure, like the internet, smart devices and sensors create an ecosystem that is complex and widespread. IoT devices vary widely in their uses, and so do their security needs, which means it’s very easy to either overspend or underspend on the necessary precautions. Each component is vulnerable, and their internetworked communication is instantaneous. That means a hacker can take down an entire system in a second, long before any human or network fail-safes can respond. A disgruntled worker could sabotage devices during design or manufacturing. Criminals could steal a device shipment, reprogram the devices, and return the devices on their journey. A hacker could fake a device malfunction in an existing system, alter the device software, and then bring the device back online — security personnel would simply assume it was a minor glitch. In every case, the breaches might never be detected.

Knowledge and preparedness are key determinants for how successful any IoT security implementation will be, even when facing the unknown. By building comprehensive security measures into the ecosystem first, before a single device is activated, you can create a secure foundation that will last well into the future.

With increasing cyberattacks during the COVID-19 crisis, what are your thoughts on the need for asset inventory management?

For many enterprises, tracking an asset at every step of its journey, in real-time, is a business-critical requirement and the COVID-19 crisis reinforced this hard fact to enterprises of all sizes – big and small!

Connected asset tracking solutions provide compliance oversight, enhances owner/operator behaviors, improves productivity, and reveals granular insights for optimizing operational efficiencies. With remote tracking and monitoring, managers can make smart decisions based on factual data, driving performance, and creating significant competitive advantages for their companies.

Finally, what changes do you foresee in the post-COVID-19 world? Has the lockdown period been an enabler for security advancements in the IoT space or has it been an obstacle?

Having proper security in place makes common sense but too often this has been an afterthought. The outbreak of COVID-19 mandated remote working of the employees with country-wide lockdowns leading to an upsurge in the Bring Your Own Device (BYOD) trend, and, thus, higher vulnerability. The demand for endpoint security rose during the lockdown period. COVID-19 has accelerated the demand for managed IoT security services to safeguard the data of employees as well as organizations. In addition, regulations are now forcing device and sensor manufacturers to take security into account and not to ship without it – security by design.

This interview first appeared in the August 2020 issue of CISO MAG.Subscribe now!
Augustin KurianAbout the Interviewer

Augustin Kurian is part of the editorial team at CISO MAG and writes interviews and features.