Home Blog Page 333

Security breach affects Airbus employees’ data

Airbus

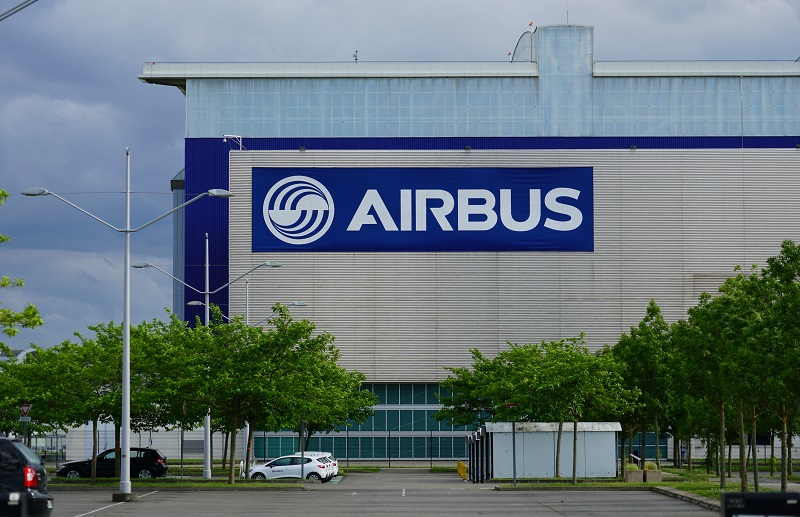
European aerospace corporation Airbus is the latest victim of a security breach. The aircraft manufacturer said it discovered a cyber incident on its commercial aircraft business information systems, which resulted in unauthorized access to its employees’ personal data. Airbus designs, manufactures, and sells thousands of civil and military aerospace products globally.

The company stated the majority of the accessed information was professional contacts and IT identification details related to Airbus employees in Europe. However, Airbus clarified that there was no impact on its commercial operations and also stated the incident was being investigated by its security professionals.

“This incident is being thoroughly investigated by Airbus’ experts who have taken immediate and appropriate actions to reinforce existing security measures and to mitigate its potential impact, as well as determining its origins. Investigations are ongoing to understand if any specific data was targeted, however, we do know some personal data was accessed. This is mostly professional contact and IT identification details of some Airbus employees in Europe,” Airbus said in a statement.

Airbus notified the data regulatory authorities about the data breach in accordance with the GDPR (General Data Protection Regulation). It also suggested its employees take the necessary precautions to prevent further loss.

In a recent similar incident, the Amadeus online ticket booking system exposed passengers’ private data due to a security flaw, allowing potential attackers to view and change information. According to the security researcher Noam Rotem at Safety Detective research labs, the security flaw could let anyone manipulate someone’s ticket reservation for any airline which has used the Amadeus reservation system.

Also, a software glitch possibly exposed personal information of 285 members who used the Singapore Airlines (SIA) services. The Singapore flag carrier stated that a bug in its website caused a data leakage of KrisFlyer, a regular flyer program of Singapore Airlines. The bug exposed KrisFlyer customers’ personal information, including the member’s full name, email address, membership tier, account number, the accumulated miles/rewards, travel history, passport, and flight information.
Baffin Bay Networks acquires Loryka

Acquisition

Baffin Bay Networks, a cloud-native cybersecurity startup, recently announced that it’s expanding its reach in the United States by acquiring data security provider Loryka. Founded in 2017, Baffin Bay Networks provides cloud-based threat prevention services to enterprises. The Stockholm-based company was established by a group of security experts from the major U.S.-based security firms and Nordic banks.

Launched as a research project in 2013 with a focus on botnet and IoT research, Loryka has grown into a research data platform that allows researchers to gain insights into cyber-attacks.  The U.S.-based startup provides useful data points for researchers to innovate and make technological advancements. With the latest acquisition, Loryka brings a team of developers, researchers, and security professionals who are recognized as early attack detection experts to Baffin Bay Networks.

Speaking on the collaboration Justin Shattuck, CEO and founder of Loryka commented “This move gives us a great springboard to take our research expertise and our philosophy of data sharing to new clients and markets. Joining forces with a cybersecurity platform like Baffin Bay Networks shows we have transitioned from a data collection company to a genuine threat prevention organization, providing solutions to corporate end-users at a larger, more significant level.”

“This is a big step for Baffin Bay Networks as we look to expand our reach and create even more value to customers. With this acquisition we will have a threat research team in the US with great local knowledge and experience, meaning we will be able to provide clients with unrivaled threat intelligence and services to help them protect their businesses,” said Joakim Sundberg, CEO, and founder of Baffin Bay Networks.

UAE spied on literally every expat just by sending a text

Smishing attacks

This might be a shocker for all the diplomats and expats entering the UAE. The emirate with the help of former U.S. government intelligence operatives have been hacking iPhones of activists, diplomats, and rival foreign leaders using a spying tool dubbed as ‘Karma’. We don’t know where the irony begins. The spying tool enters phone just through a text message and proven to be one of the most potent cyber weapons to be used in espionage.

According to a Reuters report, the tool lets spies steal photos, messages, emails and location data from iPhones by uploading victims’ email accounts or phone numbers to an automated system. What even worse was that the target did not even need to click or open the message. As soon as the text lands on the phone the phone is breached. The government targeted leaders of rival nations, political dissidents and human rights activists.

The existence of the tool or the hacking unit were never been reported. According to Reuters, the facility is based in Abu Dhabi and has been code-named Project Raven. An ex-Raven operative stated in the report that the tool gave remote access to iPhones by simply putting the email address or phone numbers of the target into the machine. The only limitation of the machine was its inability to hack into Android phones and also couldn’t intercept phone calls.

A former operative of  Raven, who used to be an ex-NSA operative as well told Reuters  “It was like, ‘We have this great new exploit that we just bought. Get us a huge list of targets that have iPhones now. It was like Christmas,” sharing her excitement back in the day when Karma rolled out.

Neither the NSA or the government of UAE have commented on it. Except, the NSA states that “all their ex-employees are subject to the same post-employment restrictions that govern other former civil servants employed by the intelligence community” and that “under no circumstance would the agency request that an individual, contractor, foreign government or other US government agency engage in activities on its behalf that the NSA would not itself be authorized to undertake.”

Well, that seems to may have been highly unlikely.

Singapore announces new initiatives to boost cybersecurity

Singapore Government

In order to boost cybersecurity and tackle next-generation cyber threats in the telecommunications sector, the Singapore government recently formed Telecom Cybersecurity Strategic Committee (TCSC), a committee that is expected to publish a strategy for telecommunication operators to develop cybersecurity capabilities. It would also give other recommendations, including capability development, technology innovation, regulation, and international partnerships.

While addressing at the inaugural of Infocomm Media Cybersecurity Conference, Senior Minister of State for Communications and Information Janil Puthucheary announced the road map to secure Singapore’s telecommunications infrastructure.

“Today, we need to consider the future, as these risks are magnified by new technologies, products, and platforms. Advancements in cyber threats are ever present, such as Ransomware-as-a-service, and the weaponization of AI and use of machine learning. The pace of acceleration and the threat around cybersecurity is just as rampant. Opportunities are also created by the disruption and transformation of businesses. Everything is evolving at a pace in which technology needs to keep up through deeper, richer connectivity networks and new technologies,” Janil Puthucheary said in a statement.

“This Strategic Committee is a partnership between government and the industry to better secure our connectivity infrastructure, involving global cybersecurity experts and key telecommunication operators in Singapore,” Puthucheary added.

Janil Puthucheary also announced two initiatives to enhance security capabilities in the telecom industry. One of them is an electronic Know Your Customer guide that enables mobile operators and their customers to perform secure online verifications for mobile services. And the other is a cybersecurity guide on using Internet-of-things (IoT) devices with recommendations and checklists on how to secure their connected devices and networks.

In order to strengthen the country’s financial sector technology, the Monetary Authority of Singapore (MAS) recently announced the launch of S$30 million (US$22 million) cybersecurity capabilities grant.  The new allocation helps Singapore’s financial institutions strengthen their cyber resilience and upskill local talent through cybersecurity-related training programs like security operations, cyberthreat surveillance, computer forensics, malware analysis, and cyberthreat hunting.

Also, the governments of Singapore and the United States joined hands to strengthen their collaboration in the infrastructure sector, digital economy, and cybersecurity. Both countries renewed their Collaboration Platform Memorandum of Understanding (MOU) and signed a Declaration of Intent (DOI) to work together on a Singapore-US Cybersecurity Technical Assistance Program for ASEAN.

GDPR-compliant companies suffer fewer data breaches: Survey

GDPR fines in 2020

A recent study revealed that the introduction of the European Union’s General Data Protection Regulation has resulted in a significant decrease in data leaks and thefts.

The study dubbed Data Privacy Benchmark Study from networking company Cisco Systems stated that nearly three-quarter of GDPR-ready companies suffered fewer data breaches in the last year than organizations that have not been GDPR compliant.

The survey report, which is prepared based on data from more than 3,200 security professionals in 18 countries and across all major industries worldwide, also found that approximately 60 percent of companies have met most of the GDPR requirements, with nearly 30 percent more expected to do so within a year.

Country wise, the research stated the level of GDPR-readiness increased from 42 percent to 76 percent, stating that the European countries (Spain, Italy, UK, France, and Germany) were on the higher end of the range. Data security, internal training, evolving regulations, and Privacy by Design requirements were the major challenges faced by organizations while getting ready for GDPR, the research stated.

“These results highlight that privacy investment has created business value far beyond compliance and has become an important competitive advantage for many companies. Organizations should, therefore, work to understand the implications of their privacy investments, including reducing delays in their sales cycle and lowering the risk and costs associated with data breaches as well as other potential benefits like agility/innovation, competitive advantage and operational efficiency.” the report stated.

The EU’s GDPR became enforceable on May 25, 2018, and privacy laws and regulations around the globe. The regulation aims to harmonize the fragmented data privacy framework across the European Economic Area (EEA), and ensure that fundamental rights are protected in the digital economy.

Recently, Search engine giant Google fined for 50 million euros (around $57 million) by the French data regulator CNIL (National Data Protection Commission) for violating the General Data Protection Regulation. The data protection watchdog stated it had levied the fine for Google’s lack of transparency and valid agreement regarding ads personalization. The regulator also said that Google didn’t sufficiently inform the people about how it collected the users’ data to personalize ads.

Cybersecurity startup Cato Networks raises $55 million

Startup funding

Cybersecurity startup Cato Networks raised $55 million in an investment round led by Lightspeed Venture Partners along with the participation from existing investors Aspect Ventures, Greylock Partners, Singtel Innov8, and USVP.

The Tel Aviv-based startup provides network security services to enterprises by integrating secure web gateway, advanced threat protection, next-generation firewall, and global SD-WAN (software-defined WAN) into a single cloud service called Cato Cloud. Cato Networks claims that enterprises rely on its cloud security platform to connect and secure their corporate networks globally.

Co-founded by Shlomo Kramer, a network security expert and the innovator of the Web Application Firewall, Cato Networks stated the new investment will support its vision to become a global cloud-native carrier, protecting all enterprises, mobile users, and cloud resources.

“We are excited to have Lightspeed join our journey to build the new network for the business,” said Shlomo Kramer, CEO, and co-founder of Cato Networks. “Cato goes beyond edge SD-WAN, MPLS, and network security point solutions, to offer a full WAN transformation platform. Cato closes the huge gap between the needs of the digital business, and the rigid, slow, and expensive networks provided by legacy telcos, using a groundbreaking cloud-native carrier architecture. Cato is powered by cloud-scale software, self-service management, and elastic compute and bandwidth to provide the new foundation for the growth of the business.”

Speaking on the investment move Yoni Cheifetz, partner at Lightspeed, said, “Cato is a transformative force in the stagnant managed network services market. Businesses are looking for an affordable, agile, and scalable network to drive strategic initiatives like global expansion, hybrid cloud, and workforce mobility. Today’s rigid networks aren’t built to support this growth, and this is the multi-billion-dollar market opportunity Cato is going after.”

Unprotected database of an Indian bank leaks millions of customers’ financial data

State Bank of India (SBI), the government-owned banking network in India, is the latest victim of a massive data breach which exposed millions of customers’ financial information.

According to online publisher TechCrunch, an unprotected SBI’s server allowed potential attackers to view the data of millions of SBI account holders. It’s believed that the back-end text message system of SBI’s mobile banking services exposed the sensitive information, including customers’ phone numbers, partial account numbers, balance details, recent transactions, and other sensitive information.

It’s unclear that how long the insecure database, that store data from SBI’s Quick, YONO app, and other cell-based banking services, exposed the customers’ data online. Millions of customers use SBI’s Quick and YONO services to retrieve their account information.

“The passwordless database allowed us to see all of the text messages going to customers in real time, including their phone numbers, bank balances, and recent transactions. The database also contained the customer’s partial bank account number. Some would say when a check had been cashed, and many of the bank’s sent messages included a link to download SBI’s YONO app for internet banking,” a media statement read.

Recently, the Reserve Bank of India (RBI) imposed a fine of 10 million rupees ($1.4 million) on Indian Bank, a public-sector bank based out in the Indian state of Tamil Nadu, for violating cybersecurity norms. The central bank stated that the monetary penalty was imposed by an order dated November 30, 2018, for flouting of the Circular on Cyber Security Framework in banks.

In order to advance the preparedness of Indian banks against cyber-attacks, the RBI is working on enhancing cybersecurity mechanisms. The central bank announced an enhanced security mechanism as part of its agenda for the fiscal year 2018-19 to provide high-level protection against cybersecurity threats.

Iranian hacking group stealing people’s personal data: FireEye

Iran Hacker Group

An undetected hackers group from Iran is allegedly stealing travel and mobile data of individuals in the Middle East region, cybersecurity research firm FireEye claimed.

According to FireEye, the Iranian group dubbed APT39 has targeted a number of people in the Middle East, especially in the Gulf region. It’s believed that the espionage group is allegedly providing information to the Iranian government. The researchers at FireEye stated that they had been tracking APT39 activities since 2014 to protect organizations from cyber incidents.

The researchers said the group uses phishing emails that target specific people and include malicious attachments or links resulting in a POWBAT infection. FireEye also observed that the group uses Persian language words in encrypting data. APT39’s activities are reportedly focussed on the telecommunications sector, the travel, and IT industry, and allegedly represent Iran’s potential global operational reach and how it collects key data.

“In December 2018, FireEye identified APT39 as an Iranian cyber espionage group responsible for widespread theft of personal information. We have tracked activity linked to this group since November 2014 in order to protect organizations from APT39 activity to date. APT39’s focus on the widespread theft of personal information sets it apart from other Iranian groups FireEye tracks, which have been linked to influence operations, disruptive attacks, and other threats. APT39 likely focuses on personal information to support monitoring, tracking, or surveillance operations that serve Iran’s national priorities, or potentially to create additional accesses and vectors to facilitate future campaigns,” FireEye stated in a post.

“We believe APT39’s significant targeting of the telecommunications and travel industries reflects efforts to collect personal information on targets of interest and customer data for the purposes of surveillance to facilitate future operations,” FireEye added.

Security vulnerability exposes users’ credentials on LocalBitcoins.com

Cryptocurrency

LocalBitcoins, a cryptocurrency exchange portal, stated that it suffered a security breach on January 26, 2019. The breach, which lasted for almost five hours, was countered by the company after some users reported that they’re redirected to a fake website while accessing the LocalBictoins login page.

Describing the incident as a third-party software related problem, LocalBitcoins stated that some unknown intruders tried to illegally collect the login credentials from users to exploit their digital assets. The trading platform was taken down temporarily disabling all the transactions to prevent hackers from stealing bitcoins from the users’ accounts. The company took the necessary measures to address the issue and secure the accounts that might have been at risk.

The Finland-based bitcoin startup is a person-to-person bitcoin trading platform that allows users from different countries to exchange their local currency to bitcoins. The company claims that its trading site allows users to post advertisements where they can provide exchange rate and payment methods for buying or selling bitcoins.

“We would like to inform that today 26.01.2019 at approximately 10:00:00 UTC, LocalBitcoins has detected a security vulnerability – an unauthorised source was able to access and send transactions from a number of affected accounts. Outgoing transactions were temporarily disabled while we investigated the case,” LocalBitcoins stated in a post. “We were able to identify the problem, which was related to a feature powered by a third-party software and stop the attack. At the moment, we are determining the correct number of users affected – so far six cases have been confirmed. For security reasons, the forum feature has been disabled until further notice.”

“Your LocalBitcoins accounts are currently safe to log in and use – we encourage you to enable Two-factor authentication, if you have not yet,” LocalBitcoins added.

Cybersecurity startup Medigate raises $15 million

Startup funding

Medical cybersecurity startup Medigate Tech raised $15 million in a series A funding round led by the U.S. Venture Partners along with the participation from existing investors YL Ventures and Blumberg Capital. The Israel-based startup stated the new investment will be used to accelerate its growth and increase the personnel across its research and development, marketing, and sales units.

Founded in 2017, Medigate helps manage and secure connected medical devices like patient monitors, MRIs, and CAT scanners from evolving cyber threats. The company claims that its security solutions platform allows healthcare organizations to identify all devices connecting to their network, manage security updates, and monitor for any suspicious activity.

“The trend towards connected medical devices poses two challenges to hospitals: protecting these devices, which treat people, and managing the large numbers of such devices on the hospital network. Medigate provides a solution for both problems. We identify the devices and also protect them very precisely,” said Medigate co-founder and CEO Jonathan Langer.

“Every manufacturer of medical devices uses a different communications network protocol. We learned how to read hundreds of different protocols and to handle most of them. That is what enables us to be much more precise than our competitors. In order to understand how a protocol is constructed, it is necessary to decode it – reverse engineering. This requires very specific expertise. All of the company’s employees worked in cyber during their army service and have this type of expertise,” Langer added.

According to a market research report, the Medical device security market is projected to reach USD 6.59 Billion by 2023 from 4.36 Billion in 2018, at a CAGR of 8.6%. Factors such as increasing instances of healthcare cyber-attacks and threats, growing geriatric population and the subsequent growth in chronic disease management, government regulations and the need for compliance, growing demand for connected medical devices, and increasing adoption of BYOD and IoT are driving the growth of the Medical Device Security Market.