Home Blog Page 326

Open source service provider Buoyant raises $10 million

Buoyant, a provider of open source mesh for cloud applications, recently announced that it has raised $10 million in a funding round led by GV (previously known as Google Ventures) along with the participation from existing investors Benchmark and A Capital. The San Francisco-based company stated the new investment will be used to further develop its solution’s features and business reach.

Founded in 2015 by former Twitter’s engineers William Morgan and Oliver Gould, Buoyant builds open source service platform ‘Linkerd’ for critical applications. The company claims that its software platform Linkerd provides reliability, security, and observability at the platform layer, and also powers the cloud-native infrastructure of global businesses. It’s said that Linkerd was designed to manage cloud applications with network meshes. Companies use Buoyant solutions for managing, controlling, and monitoring interservice communication within cloud applications.

William Morgan claims that its Linkerd’s supports the infrastructure of firms like Ticketmaster, Comcast, Salesforce, Monzo, PayPal, CreditKarma, OfferUp, NextVR, Chase Financial institution, and Expedia’s HomeAway.

Speaking on the new investment William Morgan, the CEO and co-founder of Buoyant said, “Linkerd momentum has never been higher than it is now, in large part because of users who are frustrated by the complexity and big-vendor nature of other service mesh projects. Our focus with Linkerd is 100 percent on solving real problems and minimizing complexity, not on pushing a particular cloud provider agenda or building technology for technology’s sake.”

“Linkerd’s widely-used service mesh is multiplatform, ultrafast, and proven at scale,” said Dave Munichiello, General Partner at GV. “The project’s focus on simplicity, speed, and scale has driven rapid adoption among both startups and large enterprises. We’ve been impressed by Buoyant’s execution to date and are excited to help as they enter their next phase of growth.”
Onapsis partners with Exabeam to offer enhanced ERP cybersecurity

Enterprise Resource Planning (ERP) cybersecurity solutions provider Onapsis recently announced a technology alliance and product integration with security management platform Exabeam to give security teams access to ERP vulnerability logs in their security incident and event management (SIEM) for security monitoring.

Headquartered in Boston, Onapsis provides cybersecurity solutions to enterprises to protect their SAP and Oracle applications, keeping them compliant and safe from insider and outsider threats. The company claims that its security platform is the widely-used SAP-certified cybersecurity solution in the market.

The new alliance integrates Onapsis with Exabeam’s Security Management Platform (SMP) that allows security teams to detect and respond to threats by providing them with continuous visibility of ERP vulnerabilities. The association also offers enhanced security solutions including security monitoring, threat detection, incident response, and audit compliance.

Founded in 2013, San Mateo-based Exabeam helps organizations by providing security intelligence and management solutions to strengthen their information security. The Exabeam Security Intelligence Platform leverages big data, machine learning, and analytics to detect and respond to cyber threats. The company claims that it’s one among the number of security information and event management (SIEM) platforms that analyze companies’ log data sources to flag abnormal activities.

“InfoSec professionals today work in a threat environment where they face adversaries with unprecedented sophistication, persistence and technology,” said Ted Plumis, VP of Worldwide Channels at Exabeam. “We are excited to work with Onapsis to deliver a streamlined security solution for ERP systems. This partnership ensures that our mutual customers can quickly identify suspicious activity and remediate threats in their environment.”

“We are excited to be onboard as a partner of Exabeam and combining our product offerings. With the growing trend in attacks targeting the organization’s core applications, it is imperative that security teams understand and evaluate the logs and events of their ERP systems. Our partnership with Exabeam will allow companies to gain awareness into the security posture of their ERP business applications as it will now be fed into and displayed on their SIEM dashboard,” said Darren Gaeta, VP of Worldwide Alliances and Channels, Onapsis Inc.

Medical cannabis users’ suffer data breach

Medical Cannabis Users Suffer Data Breach

Natural Health Services, the operator of Canada’s largest referral network of medical cannabis patients, recently suffered a data breach that exposed customers’ personal information like medical diagnoses, referrals, encounter notes, and allergies.

The Calgary-based health center stated that unknown intruders allegedly accessed personal health records between December 4, 2018, and January 7, 2019. However, the company clarified that patient prescriptions, financial, credit card or social insurance numbers weren’t compromised in the incident.

“NHS identified that a number of records containing personal health information in the electronic medical record (EMR) system we use were accessed without the authorization of NHS physicians for purposes that may be unrelated to providing medical care,” the company said in a statement. “NHS is working with law enforcement and the Information and Privacy Commissioner of Alberta to investigate this matter. NHS is undertaking all necessary steps to work with the respective provincial privacy commissioners to ensure that this does not happen again.”

The company stated that it notified the affected clients and suggested them to monitor for any unusual activity in their transactions with financial institutions.

In a similar incident, the University of Connecticut Health Center recently suffered a breach that potentially compromised personal data of around 326,000 individuals. In an official statement, the health center stated that unknown intruders accessed the email accounts of several UConn Health employees on December 24, 2018, affecting 326,000 patients’ information.

UConn Health provides health services to the citizens of Connecticut through innovative integration of research, education, and clinical care. The Connecticut-based academic medical center stated the breached data includes, names, dates of birth, addresses, social security numbers, billing and appointment information, and other medical information.

The health center stated that it’s enhancing the security of the impacted accounts to prevent further unauthorized access. It also notified the law enforcement and retained a forensic security firm to investigate for any personal information in the impacted email accounts.

Hackers using steganography to spread Powload Malware: Research

A recent survey revealed that the uptick of macro malware in the first half of 2018 was due to Powload malware, which was circulated via spam emails. The researchers from the security firm Trend Micro stated that threat actors are using various techniques such as the information-stealing Emotet, Bebloh, and Ursnif to spread Powload malware.

The research also stated that cybercriminals are using steganography, a unique way to spread Powload malware, to infect the targeted systems. It’s believed that Powload campaign activity was distributing since 2018 through fileless methods, steganography techniques, and hijacking email accounts to deliver the information-stealing malware such as Emotet, Bebloh, and Ursnif.

Steganography is a technique used by attackers to hide malicious code within the image that is mainly employed by exploiting kits to hide their malvertising traffic. The attackers use a publicly available script called Invoke-PSImage that helps to embed malicious scripts in the pixels of a PNG file. Later, the attackers approach the victims via spam email campaigns that contain a document with an embedded malicious macro code.

If the victim clicks the document, the script will execute and downloads the image hosted online that contains the malicious code. Once the user downloads the malware, it connects to the remote server and downloads the malicious code to infect the user’s device and encrypt the files and demand the ransom to provide the file access back. The report also stated that the main motivation of the attackers was to steal the victim’s sensitive information and also to perform other malicious operations.

“In some of the recent Powload-related incidents we saw, we noticed significant changes to some of the attachments in the spam emails: the use of steganography and targeting of specific countries. The samples we analyzed in early 2018 had more straightforward infection chains. These updates added another stage to the execution of malicious routines as a way to evade detection,” the report stated.

The use of steganography technique isn’t new, recently a security researcher Matthew Rowen from Bromium discovered ransomware embedded into a downloadable Super Mario image using steganography method. The attackers send emails with an attached spreadsheet that has an embedded malware and a macro. The attachment prompts the user to click on enable content link in order to deploy the malware.

The researcher stated the malware firstly checks the region to make sure that the device is based out in Italy relying on the administrative language of the operating system. The malware will not deploy if the device is not based in Italy.

Online financial fraud surge to 27% in 2018: Report

Digital Fraud

According to the latest report published by financial services trade association UK Finance, consumers in the United Kingdom lost £393.4m in 2018 to Internet and e-commerce fraud. The report titled Fraud: The Facts 2019 stated the surge in financial fraud was increased to more than £80m or 27% in 2018. The report stated the sudden rise is a result of the increase in data breaches that was seen in 2018.

“Fraud losses on UK-issued cards totaled £671.4 million in 2018, a 19 per cent increase from £565.4 million in 2017. At the same time, total spending on all debit and credit cards reached £800 billion in 2018, with 20.4 billion transactions made during the year,” the report stated.

It’s believed that most of the data stolen in these data breaches were peddled on the dark web forums, where cybercriminals purchase huge data sets using untraceable cryptocurrencies and begin stealing money from the accounts.

“Our Fraud the Facts 2019 report lays bare the extent of the challenge. Last year the advanced security systems and innovations in which the finance industry invests to protect customers stopped more than £1.6 billion of unauthorised fraud. But despite this, criminals successfully stole £1.2 billion through fraud and scams in 2018,” the report added.

According to a recent report from Symantec’s Internet Security Threat Report (ISTR), cybercriminals are doubling down on alternative methods, such as formjacking, to make money. The ISTR provides an overview of the threat landscape, including insights into global threat activity, cybercriminal trends, and motivations for attackers.

The report analyzes data from Symantec’s Global Intelligence Network, the largest civilian threat intelligence network in the world, which records events from 123 million attack sensors worldwide, blocks 142 million threats daily and monitors threat activities in more than 157 countries.

CISO MAG Awards to honor excellence in cybersecurity

With the fabric of our society now defined by the technology we use, the issue of cybersecurity has become more important than ever. Time and again, major cybersecurity breaches have shaken up the world, serving as wake-up calls for authorities and individuals to initiate measures to improve the security and stability of the cyberspace.

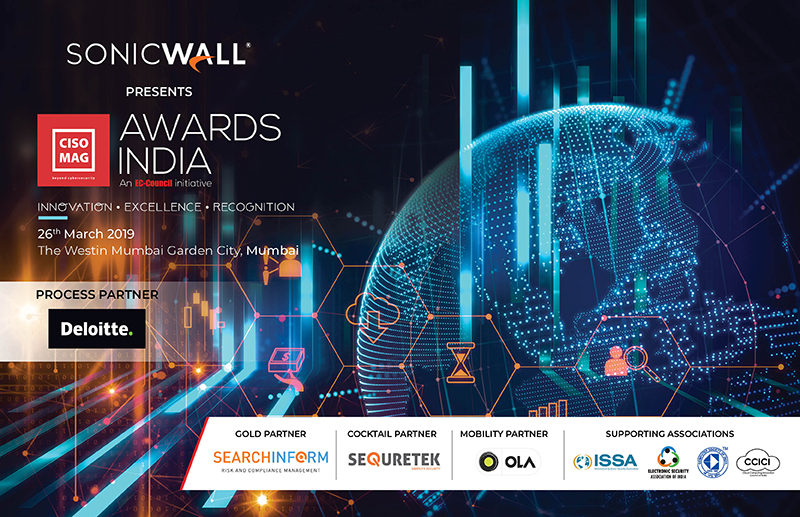
CISO MAG, a cybersecurity magazine from EC-Council, realizes there is a continuous need to honor the leaders who have dedicatedly worked to thwart the cyber threats. This is where CISO MAG Awards intervene as a significant game changer in the cyberspace security. The event would celebrate the spirit of excellence in the Cyber Security domain and recognize the innovation, commitment, leadership, and sound business strategies of distinguished professionals and organizations.

CISO MAG Awards, presented by SonicWall, a company that has been fighting the cybercriminal industry for over 27 years defending small and medium businesses, enterprises and government agencies, will be held on March 26, 2019, at The Westin Mumbai Garden City in Mumbai from 5.30 pm. This invite-only event would be preceded by an elite roundtable session hosted exclusively by SearchInform, a leading risk management product developer. The session would include various leaders and achievers in cybersecurity who would discuss some pressing issues in the domain.

To ensure fair, transparent, and robust award selection and recognition, CISO MAG has tied up with Deloitte as the process partners. Over the last two months, CISO MAG Awards received 130 nominations from close to 100 top-notch companies. All the entries are evaluated by an elite jury panel comprising:

  • Bharat Anand, CIO & CTO, Ministry of Home Affair, Government of India
  • Brijesh Singh, Secretary & Director General, Information & Public Relations Secretary & Special Inspector General of Police Cyber Maharashtra State, Mumbai
  • Kanchana TK, Director General, Organisation of Pharmaceutical Producers of India (OPPI)
  • VG Kannan, Chief Executive Officer, Indian Banks Association
  • Anuprita Daga, President, Risk, Yes Bank
  • Amit A. Pradhan, CTSO & SVP, Technology Security, Vodafone Idea Limited

The CISO MAG Awards has been received excellently in the market with almost a dozen well-known organizations agreeing to come on board as partners. Some of our partners include SonicWall (Presenting Partner), SearchInform (Gold Partner), Sequretek (Cocktail Partner), Ola (Mobility Partner) among others.

So, get ready for a night that cybersecurity industry would remember, and rub shoulders with the best in business.

To attend the event as a guest, please contact Riddhi Chandra (+91 8454826593). To partner with us, contact Jayesh Bohara (+91 9930819319).

Blockchain startup Bison Trails raises $5.25 million

Startup funding

Bison Trails, a new blockchain startup, recently raised an investment of $5.25 million in a seed funding round led by two early-stage venture capital firms Initialized Capital and Accomplice along with the participation from Notation Capital, Homebrew, Galaxy Digital, Distributed Global, Charge Ventures, and other angel investors. The funding round was also backed by Mike Novogratz’s crypto merchant bank Galaxy Digital.

Founded in 2018, the New York-based startup offers blockchain related services for next-generation infrastructure, including staking, validating, voting, transacting, and securing blockchain protocols. The startup claims that its platform is the easiest way for enterprises to launch secure, highly-available, and geographically distributed nodes on a participatory blockchain network. It also said that its blockchain infrastructure is designed to offer a way to launch secure, available and geographically distributed nodes on a participatory blockchain network.

Recently, Mike Novogratz’s Galaxy Digital invested in blockchain security firm CipherTrace, which raised $15 million to improve tools for crypto intelligence, anti-money laundering solutions, blockchain analytics, and forensics and compliance. The other investors included Aspect Ventures, Neotribe Ventures, and WestWave Capital from top Silicon Valley and New York venture capital firms with deep cybersecurity and crypto asset expertise.

Founded in 2015 by veteran security professionals, CipherTrace develops Anti-Money Laundering (AML) cryptocurrency, cryptocurrency forensics, and blockchain threat intelligence solutions. The company claims that banks, investigators, regulators, and other digital asset businesses use its security platform to comply with regulatory anti-money laundering requirements and to mitigate threats related to the customer cryptocurrency activity. The CipherTrace’s products are also used by government regulators, law enforcement investigators and auditors to enforce AML laws, combat crime and reduce fraud.

Pakistani hacker puts 26 million user records on dark web for sale

Compromised Email Accounts

The content of nearly 26.42 million stolen online records from six different companies was kept for sale on the dark web for 1.2431 bitcoin (around $4,940). A Pakistani hacker, with an online name Gnosticplayers, compromised the data by hacking dozens of popular websites from various companies, the Hacker News reported.

The hacker stated this would be his last batch of the stolen database that contained nearly 27 million users’ records stolen from 6 different websites- Youthmanual (1.12 million accounts), GameSalad (1.5 million accounts), Bukalapak (13 million accounts), Lifebear (3.86 million accounts), EstanteVirtual (5.45 million accounts), and Coubic (1.5 million accounts).

It’s believed the hacker previously kept three rounds of stolen accounts up for sale on the popular dark web market called Dream Market. Previously, the hacker exposed the details of around 620 million accounts stolen from 16 websites in the first round, 127 million records from 8 sites in the second, and 92 million from 8 websites in the third.

According to a report from threat intelligence firms Anomali and Intel 471, the content of voter databases of around 35 million US citizens was peddled on a hacking forum in October 2018. The researchers revealed that cybercriminals have obtained unauthorized access to the U.S. voter registration databases and put them for sale in dark web forums.

The database holds personal information like names, phone numbers, address details, and voting history, according to the researchers. They also said the data is priced between $150 and $12,500. The report stated the disclosure affected 19 states, including Georgia, Idaho, Iowa, Kansas, Kentucky, Louisiana, Minnesota, Mississippi, Montana, New Mexico, Oregon, South Carolina, South Dakota, Tennessee, Texas, Utah, West Virginia, Wisconsin, and Wyoming.

The researchers stated the sellers received updated voter registration data across the states via their close contacts within the state governments. It was specified that voters’ information disclosure is not a technical breach but a targeted operation by threat actors to perform malicious activities.

Blood donors in Singapore victims of data breach

Blood donor

A leaky database, which is connected to an internet-facing server, exposed personal information of over 800,000 blood donors in Singapore. According to the Health Sciences Authority (HSA), the database was exposed to the Internet for nine weeks starting in January 2019. The incident was discovered by a cybersecurity expert and alerted Singapore’s Personal Data Protection Commission (PDPC), Channel Asia reported.

HSA stated the server was maintained by a third-party contractor Secur Solutions Group for services like developing and maintaining blood donor’s e-registration, re-booking, feedback, and queue management systems.

The data was exposed while the contractor was working on a database containing the registration-related information of 808,201 blood donors. HSA stated that the exposed data belong to the visitors of HSA’s blood banks, which included names, NRIC, gender, number of blood donations, dates of the last three blood donations, blood type, height, and weight. However, HSA clarified that no other sensitive, medical or contact information was exposed in the incident and there was no unauthorized access to the exposed data so far.

“We sincerely apologize to our blood donors for this lapse by our vendor,” said Mimi Choong, CEO of HSA. “We would like to assure donors that HSA’s centralised blood bank system is not affected.

“HSA will also step up checks and monitoring of our vendors to ensure the safe and proper use of blood donor information,” Choong added.

A recent report revealed that health care organizations suffered the highest number of data breaches in 2018 across any sector of the U.S. economy. According to Beazley Breach Response, a breach response management and information security insurance solutions provider, the healthcare entities have reported the highest number of data breaches, at 41 percent.

The report, dubbed as Beazley Breach Insights Report, stated that direct hacking, the presence of malware, or due to human error were the causes of data breaches in healthcare organizations.

The report also revealed the percentage of breaches in other sectors of the economy. The education sector accounted for 10 percent of security issues, financial institutions reported 20 percent of incidents, and professional services represent 13 percent of cases.


Threat actors using stolen email credentials to breach cloud accounts: Survey

cyber attack

A recent survey revealed that threat actors are using previously stolen login credentials to launch brute-force attacks on high-profile cloud-based business systems that use multi-factor authentication (MFA).

According to the research by enterprise security firm Proofpoint, hackers are using IMAP-based password spraying attacks to breach Microsoft Office 365 and G Suite accounts which are protected with multi-factor authentication. This technique allows malicious actors to perform credential stuffing attacks to compromise sensitive data.

“This study demonstrates the increasing sophistication of threat actors around the world who are leveraging brute force methods, massive credential dumps, and successful phishing attacks to compromise cloud accounts at unprecedented scale. Service accounts and shared mailboxes are particularly vulnerable while multifactor authentication has proven vulnerable. Attackers parlay successful compromises into internal phishing attacks, lateral movement in organizations, and additional compromises at trusted external organizations,” according to a statement in the report.

In its six-month study on major cloud service tenants, the Proofpoint’s Information Protection Research Team stated that they’ve found around one lakh unauthorized logins across millions of monitored cloud user-accounts. The study revealed that around 60% of all Microsoft Office 365 and G Suite tenants have been targeted using IMAP-based password-spraying attacks and approximately 25% of G Suite and Office 365 tenants were experienced a breach.

Stating that the attacker’s primary goal is to launch internal phishing, the survey also found that most of the attackers logins originated from Nigerian IP addresses which are accounted for 40% of all successful malicious efforts, followed by logins from Chinese IP addresses accounted to 26%. And other major sources of successful attacks noticed in the United States, Brazil, and South Africa.

The report concluded that organizations need to implement intelligent security measures to combat the evolving threats which are potential risks to user cloud accounts.