Home Blog Page 282

Around 26 Million Stolen Cards Rescued from “BriansClub” Hack

one million card data exposed

BriansClub, a black-market website for buying stolen credit card data, has been hacked by unknown intruders and extracted around 26 million credit and debit card records. According to cybersecurity journalist Brian Krebs, the website sold more than 9.1 million stolen card data and earned over US$ 126 million.

According to a report published on the site KrebsOnSecurity.com, the exposed information included credit card data uploaded from 2015 to 2019. It’s found that BriansClub added 1.7 million card records for sale in 2015, and 2.89 million in 2016.. In 2019 (between January and August), BriansClub added nearly 7.6 million cards.

Brian Krebs complained that the BriansClub site is using his name and his image on their ads to carry their activities.

“Last month, KrebsOnSecurity was contacted by a source who shared a plain text file containing what was claimed to be the full database of cards for sale, both currently and historically, through BriansClub[.]at, a thriving fraud bazaar named after this author. Imitating my site, likeness, and namesake, BriansClub even dubiously claims copyright with a reference at the bottom of each page: “© 2019 Crabs on Security,” said Brian Krebs.

“The stolen card data from BriansClub was shared across multiple sources who work with financial institutions to identify and monitor or reissue cards that show up for sale in the cybercrime underground. An extensive analysis of the database indicates BriansClub holds approximately $414 million worth of stolen credit cards for sale, based on the pricing tiers listed on the site,” Krebs added.

Brian Krebs helped several organizations by reporting potential vulnerabilities to them. In August 2019, Krebs reported about a state-sponsored phishing attack launched against the Indian IT outsourcing and consulting giant Wipro. He stated the company was dealing with a multi-month intrusion from an assumed state-sponsored attacker.

According to reports from Krebs On Security, “One source familiar with the forensic investigation at a Wipro customer said it appears at least 11 other companies were attacked, as evidenced from file folders found on the intruders’ back-end infrastructure that were named after various Wipro clients.”
Cookery Writer Jack Monroe Loses £5,000 in SIM-Swap Attack

SIM Swapping

Jack Monroe, a popular food blogger and activist, recently revealed that she lost about £5,000 (around US$ 6,395) from her bank account after being hit by a SIM-Swapping attack. The British-based writer stated that her phone number was seized and re-activated on another SIM card, despite using two-factor authentication (2FA).

Monroe stated the attackers were able to receive her two-factor authentication messages and access her bank and payment accounts.

“It seems my card details and PayPal info were lifted from an online transaction. The phone number was ported to a new SIM, meaning crims access/bypass authentication and authorize payments. I’m an autistic, methodical, ruthless investigator, and I have a LOT of info to go on,” Jack Monroe tweeted.

“The money stolen has run into thousands of pounds–I’m a self-employed freelancer and I have to absolutely hustle for every single pound I earn. And someone has just HELPED THEMSELVES to around five thousand of them. The total figure not in yet. I’m so white-hot angry,” Monroe added.

SIM Swapping fraud is one of the simplest ways for cybercriminals to bypass users’ 2FA protection. Recently, unknown hackers used SIM Swapping Attack technique to take over Jack Dorsey’s, Twitter’s CEO & Co-founder, Twitter account by exploiting the cell carrier vulnerability, which enabled them to post anti-Semitic comments in his account feed.

According to an official report, Dorsey’s account was compromised by a hacking group named Chuckle Squad. However, Twitter officials clarified that Jack’s account is now fixed and there is no sign that Twitter’s systems have been hacked.

Describing how the account got hacked, Twitter said, “The phone number associated with the account was compromised due to a security oversight by the mobile provider. This allowed an unauthorized person to compose and send tweets via text message from the phone number. That issue is now resolved.”

Security Flaw in Sudo allows Users to Run Commands on Linux Systems

Security Flaw in Sudo allows Users to Run Commands on Linux Systems

Security researchers discovered a security bypass vulnerability in one of the most widely used Linux commands, the Sudo.

According to researcher Joe Vennix, who discovered the vulnerability, the Sudo security bypass flaw can allow a malicious user to run random commands as root on a targeted Linux system. The researcher stated the vulnerability, named as CVE-2019-14287, works even when the Sudoers configuration forbids root access.

Sudo, which stands for Superuser Do, is one of the most important and commonly used utilities that comes as a core command, installed on almost every UNIX and Linux-based operating system.

Vennix stated the flaw can be exploited by specifying the user ID “-1” or “4294967295”, which manipulates the flaw in the conversation function. It’s also said the vulnerability affects all Sudo versions, except the latest version 1.8.28.

“Exploiting the bug requires that the user have Sudo privileges that allow them to run commands with an arbitrary user ID. Typically, this means that the user’s sudoers entry has the special value ALL in the Runas specifier,” the bug report said. “Sudo supports running a command with a user-specified username or user ID if permitted by the sudoers policy. For example, the following sudoers entry allows the ID command to be run as any user because it includes the ALL keyword in the Runas specifier.

Linux users encountered a similar security issue in 2017, after they discovered a massive vulnerability in the open-source Samba server of Linux that could have triggered a mass predicament. The Samba flaw was noticed and announced by a researcher with the alias “steelo”.

“All versions of Samba from 3.5.0 onwards are vulnerable to a remote code execution vulnerability, allowing a malicious client to upload a shared library to a writable share, and then cause the server to load and execute it,” stated the Samba Project advisory.

“Invest in Employee Education rather than buying Protective Software and Hardware”

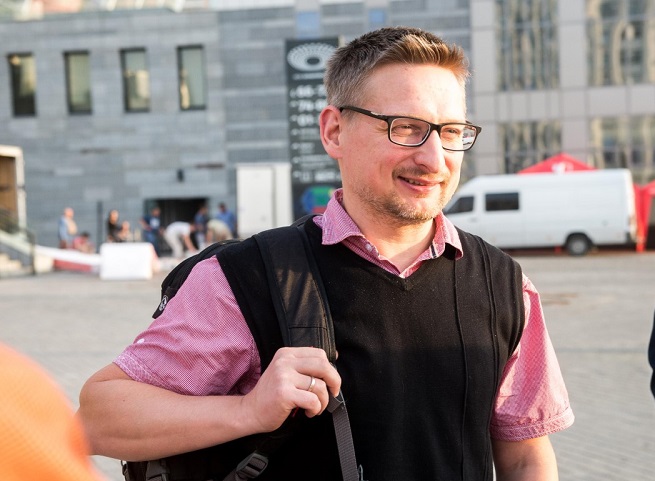
Bob Diachenko

Bob Diachenko is a Cyber Threat Intelligence Director and journalist at SecurityDiscovery.com, a cybersecurity research blog. Bob has over 12 years’ experience working in corporate/product/internal communications with a strong focus on Infosecurity, IT, and technology.

In an exclusive interaction with CISO MAG’s Rudra Srinivas, Bob explains his mission to make the cyber world safer by educating businesses and communities worldwide.

1. Tell us about your journey. What was your idea behind founding SecurityDiscovery.com?

It all started with a data breach. I worked in a company in the PR & Comms department and had little to no knowledge about cybersecurity and how the IoT world works. But when we received a notification from a security researcher who found our database sitting in a publicly accessible server online, I started to learn more about how and why it happened. I was surprised to hear that nobody was able to explain the reasons behind the exposure: “It was just a human error, it happens sometimes”.

Now I understand it was a breaking point in my career. I decided to explore how your corporate and personal data might end up online, and started exploring IoT search engines (Shodan, BinaryEdge, Censys, ZoomEye). Then I started sending my first alerts to the companies whose data I was able to identify. First, I acted on behalf of my company where I worked, then I was just Bob Diachenko, and then it all went down to a platform which we now know as SecurityDiscovery.com. It is not a company, but a non-profit initiative and place to publish public disclosures, and also represent me in emails.

2. What was your transition from an Account Manager at a PR firm to a Security Researcher like? How did you prepare for a complete role transformation?

It did not happen in a day. It took me almost a year to understand that I need to grow and work independently, not just as a representative of my employer. During this time, I never stopped learning and searching for exposed things online.

3. As a security researcher and cybersecurity consultant, what are the challenges you face while reporting the potential vulnerabilities to business owners in organizations?

Challenge No.1 – not all businesses have a proper contact point for communication of security issues–and even if their Privacy Policy contains something like privacy@companyname it does not necessarily mean that this email works or somebody check it.

Challenge No.2 – no replying or no communicating to security researchers, but simply rectifying the issues only with the aim to deny everything later on.

Threats are no longer an issue for me – they were once when I had no name or reputation, but today companies are much more open than before.

4. According to you, how can Artificial Intelligence help in detecting and mitigating cyber threats?

AI can be helpful, but I would not rely on it 100 percent. Even from my experience, I don’t fully automize the search for vulnerable/exposed endpoints and always leave places for manual analysis.

5. With cybercriminals using sophisticated methods to steal data, what can organizations do to stay ahead in the security race?

I always highlight that nothing can be better that an educated employee. An employee who follows cyber hygiene rules (that I promote every time I get an opportunity to speak publicly), and manages data responsibly–in the office and at home. So, the main advice from me to organizations is: invest into education! Even more than you invest into buying protective software and hardware.

6. As a security expert you’ve disclosed numerous critical vulnerabilities. Which one among them do you consider as the most significant discovery?

Really hard to highlight the one but I would consider the most significant are those belonging to criminal or malicious actors: spam cartels, Gootkit trojan, Clash of Clans digital laundry was also a big one. (https://www.vice.com/en_asia/article/xwkyb3/scammers-are-using-clash-of-clans-to-launder-money-from-stolen-credit-cards)

7. As a security researcher at Hacken, what were the security challenges you observed with Blockchain? Tell us about the work you did at Hacken.

I was not that much involved in blockchain while working at Hacken, and it really took me three months to get there. My work and research did not change much while I was there.

Michael Montoya Joins Equinix as Chief Information Security Officer

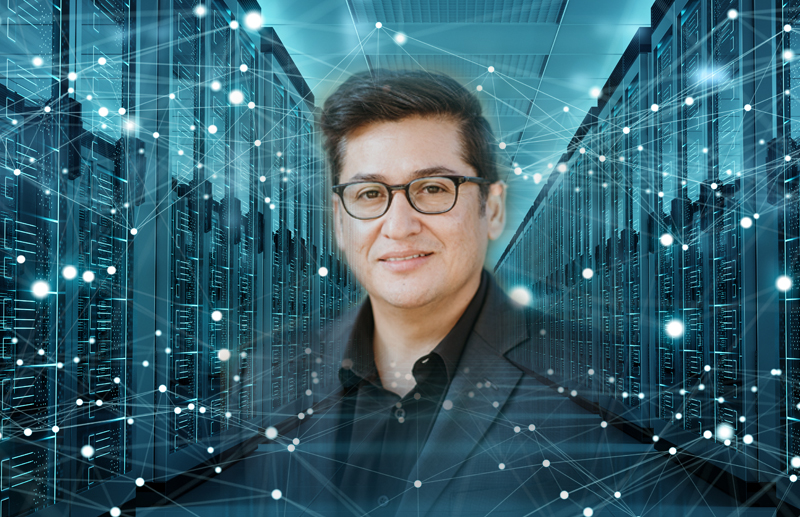
Michael Montoya

Global interconnection and data center company Equinix recently announced the appointment of Michael Montoya as its Chief Information Security Officer (CISO) to further boost the company’s commitment to security. Equinix develops robust data center solutions connected with world-class interconnection services that adapt to the ever-changing requirements of the businesses.

Previously, Montoya worked for Digital Realty as Senior Vice President and Chief Information Security Officer. He holds extensive experience overseeing global cybersecurity programs and advising large enterprises, governments, and regulators globally.

Montoya also held several leadership roles at Microsoft, including the Chief Cybersecurity Advisor, where he led security initiatives and operations for the development and delivery of Microsoft cloud security products and services.

In his new role, Montoya will lead Equinix’s global cybersecurity risk program, including evolving the company’s information security program and defining the company’s future cybersecurity roadmap. Montoya oversees Equinix’s product development, Operations, IT, compliance, and business continuity teams to help ensure the company has a world-class approach to securing its global assets.

“Equinix is a leader helping the world to connect, protect and power their digital transformation. The complexities surrounding cybersecurity continue to evolve and increase in complexity. I am humbled by the opportunity to join a technology leader and build upon all the great work accomplished to help protect Equinix customers from the rapidly changing challenges in cybersecurity and data privacy,” Michael Montoya said in a statement.

“We are extremely pleased to have Michael join our leadership team. Michael is a recognized security leader with deep expertise in information security, risk governance, data privacy, and technology deployment. We are excited about his vision stemming from his deep expertise in the security field providing both operational leadership and strategic guidance to enterprise organizations. At Equinix, security and data privacy are key embedded tenets of our overall technology service delivery, both for our internal employees as well as our customers. Michael’s leadership will further position us for continued success in this domain,” said Milind Wagle, Chief Information Officer at Equinix.

Australian C-suite in the Dark About Cybersecurity Threats

Whistle-Blower Reports to ICO Increase by 34% in the Last Year

A new research revealed that most of Australia’s Chief Executive Officers are unaware of cybersecurity threats to their organizations.

According to a research report from information technology company Unisys, around 88 CEOs and 54 CISOs across the private and public sector found that only 6 percent of CEOs said their organizations had suffered a cyber-attack in the last 12 months, compared to 63 percent of CISOs who reported attacks in their organizations.

The research highlighted that there is a lack of communication between the CEOs and CISOs from Australia’s companies. It also stated that cybersecurity is still considered to be an IT concern.

“Sixty-nine percent of CISOs believe that cybersecurity is viewed as part of the organization’s business plans and objectives; however, just 27 percent of CEOs agree with this statement,” the report stated.

Half of the CEOs (44 percent) that were surveyed believed that their organizations can respond to cyber incidents, but only 26 percent of CISOs feel the same way. The report also revealed that 51 percent of CEOs felt that their data collection policies are clear to users, but only 26 percent of CISOs agreed to it.

“The survey reveals that awareness of what information is being collected, and how, is not necessarily understood at a leadership level. There is a clear disconnect between the way CEOs and CISOs view the business risk of data security and their ability to prevent or manage data breaches,” said Gergana Kiryakova, industry director, cybersecurity for Unisys Australia and New Zealand.

“Information security professionals must start speaking the language of business to position cybersecurity as a way to mitigate risk and add value to the organization. For business leaders, cybersecurity is a clear competitive advantage in the new data economy,” Kiryakova added.

The report comes after multiple cyber-attacks on various organizations in Australia. Recently, the parliament of Australia suffered a security incident after an unknown intruder tried to hack their computer systems. According to the official statement, hackers tried to break into the parliament’s computer network that includes lawmakers’ email archives. However, the parliament officials clarified that there were no indications of data theft so far.

In June 2009, the Australian National University discovered a major data breach that affected students’ and University’s sensitive information. According to the University’s Vice-Chancellor Brian Schmidt, unknown cybercriminals attacked University’s systems and accessed personal information late in 2018, which was discovered by the University authorities on May 17, 2019. It’s believed that the hackers had unauthorized access to 19 years of significant amounts of information related to personal staff, students, and visitors.

Lazarus Group Using Fake Site to Hack MacOS

Apple Notarization, operational technology

Security researchers recently disclosed another potential attack from the North Korea-linked hacking group named Lazarus. It’s said the recent attack is a rework of the hacking group’s previous exploits.

According to Apple Mac security specialist Patrick Wardle, the hacking group is using fake cryptocurrency trading software to break into MacOS systems.

Wardle said the hackers created a fake company JMT Trading with an official-looking website and wrote an open-source cryptocurrency trading code, which was hosted on GitHub.

Hackers inserted a piece of malicious code in the open-source code that gives access to remotely execute commands on the victim’s device. The malicious code enables attackers to get control over the infected MacOS system, according to Patrick Wardle.

“While investigating a cryptocurrency exchange attacked by Lazarus, we made an unexpected discovery. The victim had been infected with the help of a Trojanized cryptocurrency trading application,” the researcher said in a statement.

Lazarus Group is repeatedly trying to find a way into cryptocurrency funds. In 2018, Kaspersky Lab uncovered AppleJeus, a malicious operation by Lazarus group to intrude on cryptocurrency exchanges and applications.

According to an official report, Kaspersky Lab’s Global Research and Analysis Team (GReAT) discovered the unusual activity of attackers who penetrated into the network of an Asia-based cryptocurrency exchange using Trojanized trading software to steal cryptocurrencies. Vitaly Kamlut, the head of GReAT, stated that the cryptocurrency exchange did not encounter any financial losses during the incident.

Kaspersky stated the incident occurred after an employee downloaded a cryptocurrency application from a look-a-like website of a company that is dedicated to crypto trading. The malicious update installs a Trojan known as Fallchill that provides the hackers unlimited access to the compromised computer network system, allowing them to steal sensitive information or to deploy other viruses for exploitation.

Survey Reveals 269 Percent Rise in Business Email Compromise Attacks

Business Email Compromise Attacks

A research report from email and data security company Mimecast revealed that there is a significant increase in Business Email Compromise (BEC) attacks. Mimecast, a cybersecurity and compliance provider, helps global enterprises make their email system safer, restore trust, and strengthen cyber resilience.

In its report, Email Security Risk Assessment (ESRA), Mimecast stated that emails containing viruses and malware attachments are being delivered to users’ inboxes from incumbent email security systems.

The ESRA highlighted that BEC attacks have increased to 269 percent when compared to the same findings in the last quarter’s report. Mimecast stated that they’ve found 28,783,892 spam emails, 28,808 malware attachments, and 28,726 dangerous file types that are delivered to users’ inboxes.

Mimecast opined that the rise in BEC attacks emphasizes the need for organizations to strengthen their email security capabilities to protect against potential attacks.

“This ESRA report pointed out that impersonation attacks continue to menace all types of organizations, but I think the real issue is that there are tens of thousands email-borne threats successfully able to bypass the email security systems that organizations’ have in place, effectively leaving them vulnerable and putting a lot of pressure on their employees to discern malicious emails,” said Joshua Douglas, vice president of threat intelligence at Mimecast.

“Cybercriminals will always look for new ways to bypass traditional defenses and fool users. This means the industry must focus their efforts on investing in research & development, unified integrations and making it easier for users to be part of security defenses, driving resilience against evolving attacks,” Douglas added.

A similar survey revealed that threat actors are using previously stolen email login credentials to launch brute-force attacks on high-profile cloud-based business systems that use multi-factor authentication (MFA).

According to the research by enterprise security firm Proofpoint, hackers are using IMAP-based password spraying attacks to breach Microsoft Office 365 and G-Suite accounts, which are protected with multi-factor authentication. This technique allows malicious actors to perform credential stuffing attacks to compromise sensitive data. The study revealed that around 60% of all Microsoft Office 365 and G-Suite tenants have been targeted using IMAP-based password-spraying attacks and approximately 25 percent of G-Suite and Office 365 tenants experienced a breach.

Hackers Rewarded with US$ 33,750 in DoD Bug Bounty Program

Bug, vulnerability, zero-day

Around 81 ethical hackers from the U.S., India, Ukraine, Turkey, and Canada participated in the recently concluded bug bounty program organized by the U.S. Department of Defense (DoD) with the participation from bug bounty platform HackerOne.

The bounty program, named Hack the Proxy with HackerOne, was sponsored by the U.S. Cyber Command with a focus on content intermediaries, like proxies, VPNs, and virtual desktops. “Hack the Proxy program was the first initiative that’s focused on securing content intermediaries for publicly accessible proxy servers owned by the government,” DoD said in a statement.

The Department of Defense stated that security researchers around the world submitted 31 valid vulnerabilities from September 3, 2019, to September 18, 2019. The hackers are rewarded US$ 33,750 for their findings.

“With each new initiative, the Department of Defense further bolsters its cyber defenses against rogue enemy actors thanks to white hat hackers from across the globe,” said Alex Romero, Digital Service Expert at the Department of Defense Digital Service. “As our adversaries become more sophisticated in their tactics, we must stay one step ahead to protect our citizens and defense systems. HackerOne’s global community of vetted hackers have helped us discover and remediate vulnerabilities that represent a real risk to national security.”

“Since 2016, the DoD has embraced hacker-powered security with open arms by consistently collaborating with hackers worldwide to help them find areas where they can be vulnerable to attack,” said Marten Mickos, CEO at HackerOne. “Each initiative has not only bolstered the DoD’s cybersecurity posture but also served as an example of how trusting hackers can improve the defense system on an ongoing basis.”

Earlier, the Department of Defense ran a bug bounty program, a challenge focused on the Corps’ public-facing websites and services. The nine-hour program paid out $80,000 in prizes to researchers for discovering 75 unique vulnerabilities. The researchers are also allowed to report flaws they find through the HackerOne-managed Marine Corps vulnerability disclosure program until August 26, 2018, but without earning a prize.

Sectigo and SPYRUS Joins Hands to Prevent Ransomware Attacks

Google’s Project Nightingale

Sectigo, a provider of automated PKI management solutions, recently announced a partnership deal with cryptographic operating systems provider SPYRUS to help enterprises and universities protect against ransomware attacks.

The new alliance allows SPYRUS and Sectigo to offer fully automated management of all digital identities like banking and financial transactions. The partnership also enables both companies to provide computing and IoT device authentication services using modern industry standards.

SPYRUS delivers encryption, authentication, and digital content security products to government, financial, and healthcare organizations. The company claims that its solutions enable customers to meet the regulatory requirements for data protection.

Sectigo’s purpose-built and automated PKI management solutions secure connected devices, websites, applications, and digital identities. It’s said that companies rely on Sectigo’s solutions for multi-layer defense against rising web-based threats across websites, devices, infrastructure, and cloud.

“It is increasingly important for enterprises to manage and secure digital identities properly,” said Damon Kachur, Vice President, IoT Solutions, Sectigo. “The collaboration between Sectigo and SPYRUS combines purpose-built PKI solutions with cryptographic operating systems to fully automate digital identity management, helping to assure organizations that their sensitive data is protected from cybercriminals.”

“Given the openness of American society, particularly in academic and scientific communities, costly incidents of ransomware continue to grow. By partnering with Sectigo, we can comprehensively address the security challenges universities and enterprises face in managing digital identities,” explained Grant Evans, CEO, SPYRUS. “Our partnership with Sectigo enables enterprises across sectors to address device identity, authentication, and access to combat these attacks.”