The usage of video conferencing and calling applications has skyrocketed since the beginning of the pandemic, which has drawn eyeballs of threat actors towards this new attack surface. This inadvertently means that video calling platforms have been on the radar, and Zoom just happened to walk into their trap as it previously did not support end to end (E2E) encryption for free users. It received a lot of flak, especially from the infosec community. It, however, rectified the mistake and provided E2E encryption to all its users. Yet, it lacked some basic security features like the two-factor authentication (2FA). It seems that it has finally obliged and has now introduced the two-factor authentication for its users, reassuring them of an added jacket of safety over the existing ones.
How Does 2FA Help Zoom
Zoom’s 2FA adoption primarily provides the app an added layer of security and helps prevent potential security breaches. Other benefits include:
Improved security: It reduces the risk of identity theft and security breaches by preventing bad actors from accessing accounts by guessing passwords, or credential stuffing or gaining access to employees’ or students’ devices to get into the main network.
Reduced costs: SSO or other forms of login and authentication can punch a hole in the pocket for smaller organizations. However, Zoom’s 2FA provides a free and effective way to validate users’ authenticity.
Enhanced compliance: 2FA implementation helps organizations fulfill compliance and regulatory needs for sensitive data and customer information.
Easier credential management: Password management can be a task especially in this digital normal where you have online accounts for even ordering your daily veggies and groceries. Thus, a 2FA provides an additional level of security without the hassles of constant password management.
Enabling Zoom’s 2FA for Your Organization
As per Zooms blogpost, Zoom not only offers 2FA but a host of other authentication methods such as SAML, OAuth, and/or password-based authentication, which can be enabled or disabled for an account based on user/admin preference. To enable the 2FA at account-level for password-based authentication, the admins need to follow these steps:
Sign into your Zoom Dashboard.
Go to navigation menu, first select Advanced, and then click on Security.
Make sure the Sign in with Two-Factor Authentication option is enabled.
Select one of these options to enable 2FA for:
All users in your account:Enable 2FA for all users.
Users with specific roles:Enable 2FA for specific user roles. Click Select specified roles, choose the roles, then click OK.
Users belonging to specific groups:Enable 2FA for users in a specific group. Click pencil icon, choose the groups, then click OK.
5. Finally, once you are done click ‘Save’ to confirm your changes made to the 2FA settings.
Several organizations are concerned about human errors that cause accidental exposure of a company’s critical data. A joint study from Stanford University Professor Jeff Hancock and security firm Tessian revealed that nine in 10 (88%) data breach incidents are caused by employees’ mistakes. The study “Psychology of Human Error” highlighted that employees are unwilling to admit to their mistakes if organizations judge them severely.
Understanding the psychology behind human errors helps organizations to know how to prevent mistakes before they turn into data leaks. According to the study, nearly 50% of the employees stated that they are “very” or “pretty” certain they have made an error at work that could have led to security issues to their company.
Young v/s Old Employees
The study also revealed that younger employees are five times more likely to admit to errors, while 50% of employees aged between 18-30 years stated they have made mistakes compared to 10% of workers aged over 51.
“For older generations, self-presentation and respect in the workplace is hugely important. They may be more reluctant to admit they have made a mistake because they do not want to lose face. Businesses, therefore, need to deshame the reporting of mistakes,” Hancock said.
Young Employees are Easy to Phish
The study highlighted that one in four employees (25%) said they have clicked on a phishing email at work. Men are twice as likely as women to fall for phishing scams, with 34% of male respondents stating that they have clicked on a malicious link in a phishing email compared to 17% of women.
Surprisingly, older employees are less vulnerable to phishing scams. Only 8% of workers aged over 51 said they clicked on a phishing link. Around 32% of 31-40-year-old employees admitted the same. “The older generation have, in many ways, the potential tools and mindsets needed for detecting phishing attacks. They have more life experience, and they tend to have strong, close networks, which means they are good at detecting when something does not ‘feel’ quite right. But if you are less experienced with these kinds of attacks, they are going to be harder for you to spot,” Hancock added.
Other Findings include:
Nearly 45% of respondents cited distraction as the top reason for falling for a phishing scam.
57% of remote workers admit they are more distracted when working from home.
The top reasons for clicking on phishing emails are the perceived legitimacy of the email (43%) and the fact that it appeared to have come from either a senior executive (41%) or a well-known brand (40%).
“Your employees are focused on the job you hired them to do and when faced with to-do lists, distractions, and pressure to get things done quickly, cognitive loads become overwhelming and mistakes can happen,” the study report concluded.
Cryptocurrencies have always been a primary target of cybercriminals. Recently, Slovakia-based Eterbase Exchange admitted that it became a victim of a security incident in which unknown hackers accessed its network systems and stole $5.4 million worth of crypto funds. In an official notice it stated that hackers compromised Eterbase’s six hot wallets that held multiple cryptocurrencies including Ether, Bitcoin, ALGO, Tezos, Ripple, and TRON riches. However, most of the crypto funds stolen were in the form of Ether.
We have reported the matter to law enforcement and we are cooperating closely in the investigation. We want to assure our clients that we are taking all necessary steps to ensure that the amount of their deposit does not suffer any damage as a result of a hacker attack. https://t.co/x7nAgGGeod
Following the incident, Eterbase suspended its operations temporarily and reported the attack to law enforcement authorities for further investigation. In a tweet, the company said that it noticed the movement of stolen funds transferring into other exchanges including Binance, HitBTC, and Huobi.
“Law enforcement authorities have been informed and we will assist as much as we can in the ongoing investigations. We want to inform our users that we have enough capital to meet all our obligations. After the security audit of renowned global companies, our operations will continue. We will announce the date of the re-opening of the Eterbase exchange platform as soon as possible,” the company said in the notice.
Cryptocurrency Heists Continue to Rise
In a similar security incident, attackers nabbed $25 million worth of cryptocurrency from Uniswap exchange and the Lendf.me lending platform. The hacker took advantage of a known vulnerability that concerned the ERC777 token standard in the Ethereum blockchain technology. Experts believe that the two attacks could have been carried out by the same hacker as a similar exploit termed as a “reentrancy attack” was used in both the cases. Lendf.Me faced a major blow with 99.95% of funds or 24.5 million dollars being stolen. The attack involved the theft of imBTC, an ERC-20 token that was designed by the dForce Foundation but is now run by a separate company called Tokenlon.
When the pandemic came along earlier this year, more businesses increased their reliance on digital infrastructure. Today, businesses rely heavily on digital processes to run their operations. Clearly, the risk has shifted to digital platforms and DRM is the next evolution in enterprise risk and security for organizations.
The ultimate objective of digital risk management is to build digital resiliency, where an organization’s systems and operations are designed to detect digital threats and respond to events to minimize business disruption and financial losses.
“Sameer Saxena, Business Development Head- Cybersecurity & MSSP, Inspira Enterprise India Pvt. Ltd. discusses the evolution and future of Digital Risk Management with Brian Pereira, Principal Editor, CISO MAG.”
Sameer is a Cyber Security practitioner with over 20 years of industry experience of which 10 years has been in the Cybersecurity Education, Skill Development, Awareness function. He has led organizations to develop and strengthen cross-functional teams and establish relationships with the Industry ecosystem. Sameer is the winner of the Cyber Security Social Media Influencer of the Year 2020 by CISOMAG, an EC-Council Publication.
Being an outlier, he had been instrumental in creating the need for an Indian version of the Information Assurance Workforce Skills Framework, which was the only one approved by the National Skills Development Corporation (NSDC).
The world-renowned cybersecurity certification body, EC-Council, has teased what is touted to be the “new methodologies to revolutionize the future of cybersecurity education.” The official announcement will be made on September 16, 2020.
The cybersecurity certification giant detailed on how even failing economies due to COVID-19 did not deter cybersecurity aspirants from learning. In fact, the demand for Certified Ethical Hacker (CEH) skyrocketed during the pandemic. It also shed light on the surge in cyberattacks owing to the new work from the home format.
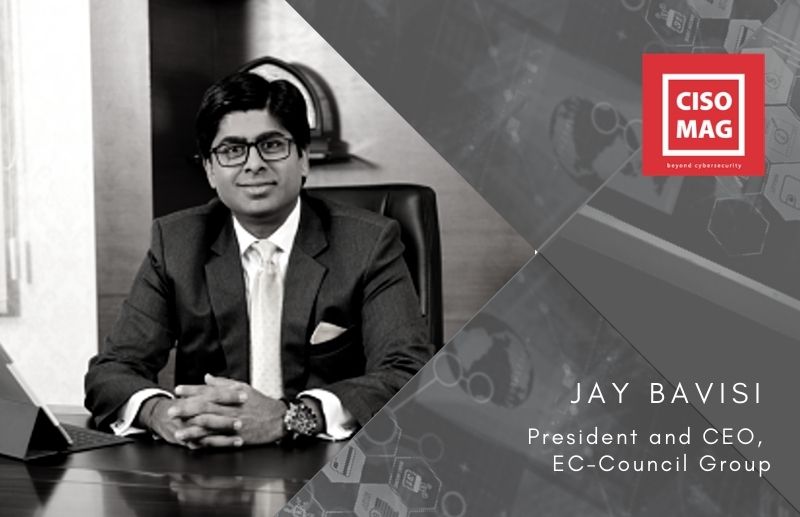
“Our Certified Ethical Hacker certification continues to be the gold standard, particularly during these changing times,” said Jay Bavisi, President and CEO of the EC-Council Group. “We have learned from its increased demand and are working to up our game even further to create a cyber training platform like no other.”
The cybersecurity market is projected to reach $258.99 billion by 2025, and a lot of it is due to the newer, innovative routes hackers are adopting, making it a bigger concern for the future. Cybersecurity experts also have raised the alarm that dangers like insider threats such as voice and video spoofing, including by those impersonating C-level management, may go undetected. To counter this issue, EC-Council launched its CEH Master Scholarship Program in May 2020 to support national and global security efforts to combat cyber-terrorism. The initial program included total scholarships valued at $550,000 for the ethical hacking community. But as cybersecurity professionals and enthusiasts across the globe began applying for the scholarship in large numbers, the EC-Council Award Committee raised the scholarship cap, awarding over $1 million in scholarships, covering the CEH Practical Exam fee for 1,900 recipients in under 60 days.
With more than 5,500 scholarship applications worldwide, it is clear there is an increased demand for the CEH as cybercrime remains on the rise. Applicants from countries around the world have included the U.S., Singapore, South Africa, India, Philippines, Turkey, and Nigeria, as well as Uruguay, Rwanda, Vietnam, and Slovenia, which are some of lowest ranked countries on the Global Cybersecurity Index.
EC-Council is an ANSI 17024 accredited organization and have earned recognition by the DoD under Directive 8140/8570, in the U.K. by the GCHQ, and a variety of other authoritative bodies that influence the entire profession. Founded in 2001, EC-Council employs over 400 people worldwide with 10 global offices in the USA, Canada, U.K., Malaysia, Singapore, India, and Indonesia. Learn more at http://www.eccouncil.org.
Security researchers Mikhail Klyuchnikov and Nikita Abramov from Positive Technologies uncovered four severe vulnerabilities in Palo Alto Networks’ PAN-OS, a software that runs on the company’s next-generation firewalls used by over 66,000 companies in 150 countries. Cybercriminals could exploit the vulnerabilities to obtain sensitive corporate data or compromise internal network systems.
“The vulnerabilities could be leveraged by attackers to obtain maximum privileges in the OS, perform any actions on behalf of an administrator within the Palo Alto application, run arbitrary system commands with maximum privileges, or cause a denial of service for the product’s management web interface,” the researchers said.
Out of four security flaws, three vulnerabilities are rated as high severity and one as medium severity. These include:
This is a Reflected Cross-Site Scripting (XSS) vulnerability that exists in the PAN-OS management web interface. A remote attacker can convince an administrator via social engineering to click on a malicious link to potentially execute arbitrary JavaScript code in the administrator’s browser and perform administrative actions.
This is a Command Injection vulnerability in the PAN-OS management interface that allows authenticated administrators to execute arbitrary OS commands with root privileges. Attackers could exploit this flaw to access a special firewall section, inject malicious code in one of the web forms, and obtain maximum privileges in the OS.
This is a PAN-OS Command Injection vulnerability in the management web interface. It allows authenticated administrators to execute arbitrary OS commands with root privileges.
This vulnerability allows an unauthorized user to upload arbitrary files of any size to a certain directory on the server, which might lead to Denial of Service (DoS). Palo Alto Networks remediated all the four vulnerabilities in PAN-OS and urged users to update to the latest version to fix the flaws.
Klyuchnikov said, “We performed black-box testing of the NGFW management web interface to detect this vulnerability, which results from the lack of user input sanitization. During a real attack, hackers can, for example, brute force the password for the administrator panel, perform RCE, and gain access to the Palo Alto product, as well as the company’s internal network. The administrator panel may be located both inside and outside the corporate network, whichever is more convenient for the admins. But, of course, for security reasons, it is better to have it inside. And therefore, such attacks may be conducted both from the internal and external networks.”
It is not every day that you witness a star-studded lineup of CISOs and cybersecurity veterans come together on one platform with a common agenda–collectively shaping the OT/ICS security landscape –but this unbelievable feat was achieved at the inaugural edition of the OT-ISAC Virtual Summit 2020.
Since the last decade, Cyber-Physical world damages have become more real, relevant, and predominant. In fact, the recent attacks on the administrative network of Kudankulam Nuclear Power Plant (KKNPP) in India and the one at Iran’s Natanz nuclear facility on July 2, 2020, which inflicted physical damage to the facility, are prime examples of how state and threat actors are taking the game a notch higher by attacking OT/ICS for bringing down nations and businesses.
To address these issues and help build a resilient OT/ICS cybersecurity posture, OT-ISAC decided to conduct a virtual meet where experts from the infosec community could come together and share their thoughts, expertise, and analysis for the collective good of the industry.
Keynote at OT-ISAC Virtual Summit 2020
The keynote for the event was jointly given by David Koh, Commissioner of Cybersecurity & Chief Executive of Cyber Security Agency of Singapore (CSA); William Nelson, Chair & CEO of Global Resilience Federation (GRF); and Dale Peterson, CEO, Digital Bond.
David Koh said, “OT cybersecurity is an increasingly pressing issue with the growing convergence of OT and IT. Regardless of the seniority or the domain (engineering or IT) we all need to work together for defending the OT environment from cyberthreats.”
David Koh, Commissioner of Cybersecurity & Chief Executive of CSA Singapore
“Cybersecurity is like a seat belt in the car. It has to be there, and it is mandatory for your safety.”
OT systems were traditionally considered as solid entities, which could not be penetrated without a physical access to it. However, this is not the case anymore. Explaining the cause of this scenario, Koh explained, “OT systems in the past were often isolated from business networks and the internet, which allowed the OT systems to remain secure by obscurity as they were typically air-gapped from other systems. Therefore, a possibility of a cyber incident was deemed to be remote. However, then came the digitalization wave and the industrial processes started to shift from the systems based on the proprietary computing to those based on open source IT computing platforms. OT and IT began to converge and there was no longer an air gap between the two. This evolution has dramatically changed the OT cyberthreat landscape. With increased interconnectivity between OT and IT systems comes large attack surfaces for malicious cyberattackers who are always looking out for these gaps.”
He further informed the attendees about three specific security challenges to OT systems:
Poorly authenticated remote access.
Exploitation of known vulnerabilities in OT systems.
Malicious activity that can go undetected as system operator can mistake anomalous behavior for system error as OT systems are not regularly patched and rarely have a centralized dashboard.
Keynote speaker, Bill Nelsen, before joining the GRF, worked as the President and CEO of FS-ISAC for 12 years. He is well-versed with the importance of working together and thus shared his thoughts on the need for collaboration in the ICS Community. If adversaries can share their attack tactics and promote their tools as a service, then why should we not collaborate? Bill stressed, “This is the key to cyber resilience.”
Similarly, Dale Peterson, a veteran with over 20 years of experience in ICS security, gladly shared his thoughts on “The future of ICS security products.”
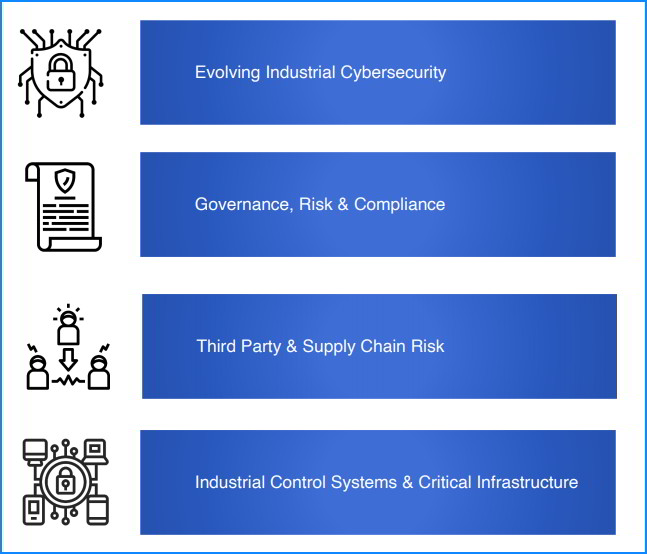
The key topics related to OT/ICS security covered during the event included evolving industrial cybersecurity, governance, risk and compliance, third-party and supply chain risk, and ICS & CIIs.
Key Touchpoints of OT/ICS Security in OT-ISAC Virtual Summit 2020
Fireside Discussion
Based on the key touchpoints related to OT/ICS security, panelists in a fireside discussion spoke about the need for cross-pollination of OT and IT realms.
Del Rodillas, Director of OT Industry Solutions at Palo Alto Networks
“There is no miracle box to protect your OT. It needs different technologies and collaboration between OT and IT teams.”
Gary Kessler, President of Gary Kessler Associates, suggested how engineers need to adopt a “Security by design” approach at the very beginning, and not as an afterthought post a breach or security lapse. Kessler also stressed on the need to equally focus on inside vulnerabilities rather than only on outside threats. He added, “Threats come from the outside which are uncontrollable in nature. However, vulnerabilities are already present in the systems and processes. Thus, we need to equally see on both sides of the spectrum.”
Moving towards the touchpoints of governance, third-party risks, and its associated compliances, Dr. Ong Chen Hui, CTO in Trustwave, said, “The supply chain in OTs these days are beyond control. Thus, vendors and third parties need to have their vulnerability assessments and monitoring systems. Collaboration and partnership at all levels is the key to securing critical information infrastructure (CII).”
Shawn Thompson, CISO, Dept. of Transport, seconded Chen Hui and highlighted the need for a practical or risk-based approach for strengthening an organization’s cyber defense posture.
Shawn Thompson, CISO, Dept. of Transport
“Organizations and their supply chains should adopt a risk-based approach rather than a compliance-based approach. Risks are different for different industries and there is no ‘one size fits all’ rule.”
The APT Threat
Due to the lack of hardened security measures and fragmented operations, OT/ICS systems are also predominant targets of APT attacks. Victims of such attacks include power plants, chemical manufacturers, seaports, and military objects. APT groups often have the backing of nation-states and are therefore more interested in analyzing and exfiltrating specific confidential data rather than penetrate networks and systems for monetary gains.
Anastasiya Tikhonova, Head of APT Research at Group-IB
“APT attacks on critical infrastructure can start with small things, as small as an employee connecting an MP3 player to a critical system.”
Referring to the origin and duration for which threat actors can stay hidden in the network to only analyze what’s worth, Anastasiya Tikhonova, Head of APT Research at Group-IB said, “APT attacks on critical infrastructure can start with small things, as small as an employee connecting an MP3 player to a critical system. It has happened before and provided threat actors a free entry into the victim’s network. APTs also stay in the system for a longer period, sometimes as long as four years to analyze, penetrate, and exfiltrate targeted data.”
Conclusion
OT-ISAC’s efforts of hosting this event and bringing the top OT security experts together on a virtual platform is noteworthy. The main intent of the event, as its name suggests, was information sharing. Attacks and attack vectors targeted towards OT/ICS industry have spiraled upwards, especially since the onset of the pandemic; however, discussions like these help in shaping the security posture of the OT/ICS infrastructure.
CISO MAG was the official Media Partner of the OT-ISAC Virtual Summit 2020, and had exclusive access to the content. We take this opportunity to thank Image Engine, the event producer and organizer, for providing the required technical assistance for event registration.
About the Author
Mihir Bagwe is a Tech Writer and part of the editorial team at CISO MAG. He writes news features, technical blogs, and conducts interviews on latest cybersecurity technologies and trends.
The surge in remote work brought a new wave of security concerns, as many organizations believed that cyber habits of employees could compromise business systems or make corporate data vulnerable to cyberattacks. According to a new survey by the Cyber Readiness Institute, small and medium-sized businesses (SMBs) are concerned that their employees’ social media activities may bring security risks to organizations.
The survey revealed that 56% of SMBs believe that their employees’ social media use poses a cybersecurity threat to their business. Around 64% stated that more than 50% of their employees have social media applications on devices they use for work. Despite these concerns, 82% of employers allow their employees to use personal devices to access work email or other data.
While 56% of employees admitted that they have social media applications on their work devices, only 30% said their organization has issued regulations on the use of personal social media accounts on office devices. Nearly, 22% of employees ignore their company’s cybersecurity guidelines on a daily or weekly basis.
Most used Social Media Apps
According to the survey, 50% of employees used Facebook on their work devices. It is the most used social media app on organizational devices, followed by Instagram (39%), Twitter (26%), LinkedIn (22%), Spotify (19%), TikTok (13%), and Snapchat (15%).
Other Findings include:
67% of business owners allow employees to use social media applications on work devices.
42% of business owners say that more than 75% of their employees have social media applications on devices they use for work.
36% of employers are considering adding new policies regarding social media apps or modifying existing policies as employees have had to work from home.
46% of employers say they are not sure or have no clue what social media apps their employees are using on work devices.
Mitigation Measures
The Cyber Readiness Institute recommended certain measures for organizations to protect their employees, customers, and businesses’ critical information. These include:
Provide company-owned devices to all employees.
Develop comprehensive policies that address the personal use of work devices.
Conduct ongoing employee education initiatives focused on the risks of using social media applications on work devices.
The findings are based on the responses from 400 SMB owners and 1,059 employees working across the U.S.
Kiersten Todt, Managing Director of the Cyber Readiness Institute, said, “It is clear that small business owners are fully aware of the cybersecurity risks associated with mixing personal and work activities on the same device. SMBs now need to issue policies that address these risks. More than 4-in-5 owners allow employees to use personal devices for work and only about half have policies regarding the apps that can or cannot be on devices used. It is a recipe for cyber insecurity.”
After VR, AR, and Mixed Reality (MR), Extended Reality (XR) and Spatial computing are gradually becoming the newer frontiers of advancements in the space of information technology and going by the Hyponnen Theory, anything connected to the internet is vulnerable to cyberattacks. Privacy is among the major concerns raised on XR.
XR expands the definition of personal information that must be protected, including biometrically-inferred data, which is especially prevalent in XR data pipelines. You need to consider new rights for data subjects — the people whose information is collected and used—to know what’s being collected, how it is used, and how it is shared. Immersion into XR experiences often calls for a breadth of sensitive information to be available to XR hardware, and here informed consent is of paramount importance.
To address this growing concern, the XR Safety Initiative (XRSI), an organization dedicated to help build safe immersive environments, has released the XRSI Privacy Framework Version 1.0. to help individuals and organizations address a comprehensive set of privacy needs, enabling more innovative and effective solutions to improve privacy in the Extended Reality (XR) and Spatial Computing domain.
“Emerging technologies, such as XR and Spatial computing, are transforming the way humans connect, create, commerce, and heal. This technological shift has the potential to expand our capabilities, enhance wellbeing, and influence every aspect of our lives. We must proactively address the privacy, safety, and deeper societal risks it brings along,” Kavya Pearlman, Founder and CEO of XRSI, told CISO MAG in an exclusive interaction.
“While we have not even fully addressed the cybersecurity challenges with existing technologies, a whole new wave of emerging technologies including virtual augmented and mixed reality (collectively known as XR), Brain-computer Interface (BCI) and rollout of 5G communication infrastructure is bringing a whole new set of novel cybersecurity challenges that we need to address as soon as possible,” she had suggested in an earlier interview with CISO MAG.
The framework is a free, globally accessible baseline rulebook built by bringing together a diverse set of experts from various backgrounds and domains, including privacy and cybersecurity, cloud computing, immersive technologies, artificial intelligence, legal, artists, product design, engineering, and many more.
Setting a Baseline
The privacy framework also incorporates privacy requirements drawn from the General Data Protection Regulations (GDPR), National Institute of Standards and Technology (NIST) guidance, Family Educational Rights and Privacy Act (FERPA), Children’s Online Privacy Protection Rule (COPPA), and other evolving laws. It is designed to adapt and include novel requirements as new regulations come into effect.
Google has always believed in abiding by its users’ confidentiality concerns and rights. However, when it comes to data in its cloud, Google found its customers worrisome with the company’s confidentiality quotient. How can someone be confident about something they cannot see? To answer this, the technology giant launched its Confidential Computing Portfolio in an attempt to ensure data security. The first offering of Google Cloud’s Confidential Computing Portfolio – Confidential VMs – was launched in July 2020 as a beta. Google Cloud has now taken a step ahead and expanded its portfolio by introducing the beta version of the Confidential Google Kubernetes Engine (GKE) Nodes and made the previously launched beta of Confidential VMs generally available.
Key Highlights
Confidential GKE Nodes is the second product in Google Cloud Confidential Computing portfolio and will enable users to configure and run the entire GKE cluster using Confidential node pool. The GKE cluster will support all existing GKE features utilizing hardware memory encryption with AMD SEV hardware, leveraging Confidential VMs capability underneath.
Confidential VMs will become generally available soon and will include new product updates, including audit reports, new Identity and Access Management (IAM) tools, integrations with other enforcement mechanisms and vTPM support.
Making the Container Workloads Confidential
Google has notably seen its customers modernizing their existing applications and build cloud-native ones whose foundation is based on GKE. Thus, Google thought of delivering a new level of confidentiality and portability for containerized workloads. Google Cloud Confidential GKE Nodes are built on the same foundation as Confidential VMs. It allows users to keep their data encrypted in memory with a dedicated node-specific key that is generated and managed by the AMD EPYC processor.
Confidential GKE Nodes enable users to configure their GKE cluster to only deploy node pools with Confidential VM capabilities underneath. Google Cloud explains, “Clusters with Confidential GKE Nodes enabled will automatically enforce the use of Confidential VMs for all your worker nodes. GKE Confidential Nodes will use hardware memory encryption powered by the AMD Secure Encrypted Virtualization feature used by AMD EPYC™ processors, which means that your workloads running on the confidential nodes will be encrypted in-use. “
Making Confidential VMs Generally Available
Google Cloud already employs multiple isolation and sandboxing techniques as part of their cloud infrastructure and architecture security. However, with Confidential VMs, users can now protect the confidentiality of their most sensitive data in the cloud even while it is being processed. Confidential VMs leverage the Secure Encrypted Virtualization (SEV) feature of 2nd Gen AMD EPYC™ CPUs. With this technology adoption, the users’ data stays encrypted while it is being used, indexed, queried, or trained on.
Google has also reportedly worked closely with the AMD Cloud Solution engineering team to ensure that the VM’s memory encryption does not interfere with its performance metrics and instead match up with those of the non-confidential VMs.
With features such as real-time encryption, lift and shift confidentiality, detection of APT attacks, and optimized performance, the possibility of expansion of Confidential Computing technology has broadened.
Ensuring that you get the best experience is our only purpose for using cookies. If you wish to continue, please accept. You are welcome to provide a controlled consent by visiting the cookie settings. For any further queries or information, please see our privacy policy.
This website uses cookies to improve your experience while you navigate through the website. Out of these, the cookies that are categorized as necessary are stored on your browser as they are essential for the working of basic functionalities of the website. We also use third-party cookies that help us analyze and understand how you use this website. These cookies will be stored in your browser only with your consent. You also have the option to opt-out of these cookies. But opting out of some of these cookies may affect your browsing experience.
Necessary cookies are absolutely essential for the website to function properly. These cookies ensure basic functionalities and security features of the website, anonymously.
Cookie
Duration
Description
cookielawinfo-checkbox-analytics
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Analytics".
cookielawinfo-checkbox-functional
11 months
The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category "Functional".
cookielawinfo-checkbox-necessary
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category "Necessary".
cookielawinfo-checkbox-others
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Other.
cookielawinfo-checkbox-performance
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Performance".
viewed_cookie_policy
11 months
The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data.
Functional cookies help to perform certain functionalities like sharing the content of the website on social media platforms, collect feedbacks, and other third-party features.
Performance cookies are used to understand and analyze the key performance indexes of the website which helps in delivering a better user experience for the visitors.
Analytical cookies are used to understand how visitors interact with the website. These cookies help provide information on metrics the number of visitors, bounce rate, traffic source, etc.
Advertisement cookies are used to provide visitors with relevant ads and marketing campaigns. These cookies track visitors across websites and collect information to provide customized ads.