Home Blog Page 154

New Normal Effect! 85% of Organizations Say Cybersecurity is More Important than Ever

Penetration Testing, continuous testing, security testing

Networking and hardware company Cisco stated that organizations became most concerned about data sharing during the COVID-19 pandemic. In its dual research studies, the company revealed the security challenges that organizations face while supporting employees and customers in remote working conditions. It also highlighted that increasing cybersecurity spending will make organizations and consumers ready for the current working conditions.

According to Cisco’s Future of Secure Remote Work Report, most organizations across the globe are only somewhat prepared to support a remote workforce environment. The report also found:

  • 85% of organizations said that cybersecurity is extremely important or more important than before COVID-19.
  • Secure access is the top cybersecurity challenge faced by the largest proportion of organizations (62%) when supporting remote workers.
  • One in two respondents said endpoints, including corporate laptops (56%) and personal devices (54%), are a challenge to protect in a remote environment.
  • 66% of respondents indicated that the COVID-19 situation will result in an increase in cybersecurity

Cisco’s second annual Consumer Privacy Survey revealed that consumers globally are worried about the privacy of remote working tools and are uncertain about organizations data security policies. Findings include:

  • 60% of respondents are concerned about the privacy of remote collaboration tools.
  • 53% want privacy laws maintained, with little or no exception for pandemic-related data.
  • 48% feel they are unable to effectively protect their data today, and the main reason is that they cannot figure out what companies are doing with their data.
  • 56% believe governments should play the primary role in protecting consumer data, and consumers around the world are highly supportive of the privacy laws enacted in their country.

Jeetu Patel, SVP and GM of Cisco’s Security & Applications business, said, “Security and privacy are among the most significant social and economic issues of our lifetime. Cybersecurity historically has been overly complex. With this new way of working here to stay and organizations looking to increase their investment in cybersecurity, there’s a unique opportunity to transform the way we approach security as an industry to better meet the needs of our customers and end-users.”

Harvey Jang, VP, Chief Privacy Officer, Cisco, “Privacy is much more than just a compliance obligation. It is a fundamental human right and business imperative that is critical to building and maintaining customer trust. The core privacy and ethical principles of transparency, fairness, and accountability will guide us in this new, digital-first world.”

Google Rolls Out Patch to Fix Zero-Day Vulnerability in Chrome

Google Announced US$1 Million for its “Be Internet Awesome” Initiative

An actively exploited zero-day vulnerability put many Google Chrome users at a very “High” risk. Taking note of the severity of the vulnerability and the subsequent damages caused if exploited successfully, Google has released an emergency patch to fix it. The stable version of Chrome 86.0.4240.111 is now available for Windows, Mac, and Linux, which also consists of four other medium to high severity vulnerabilities.

Chrome’s Zero-Day Vulnerability

The vulnerability, which was reported by Sergei Glazunov of Google Project Zero on October 19, was said to be an arbitrary code execution (ACE) vulnerability that was actively exploited in the wild. Going through the brief technical details made available by Google, it can be said that the zero-day being tracked under CVE-2020-15999 is a heap buffer overflow bug in the FreeType font rendering library that’s included with standard Chrome distributions.

Related News:
Hackers use Firefox ‘Zero-day’ bug to attack against Coinbase employees

Talking more about the seriousness of damages that the bug could potentially cause, Rody Quinlan, Security Response Manager at Tenable, said, “The zero-day is a memory corruption flaw [CVE-2020-15999] described as a ‘heap buffer overflow in FreeType.’ Successful exploitation of heap buffer overflows could lead to memory leakage which could potentially be used to lead to arbitrary code execution. As the Chrome flaw is being actively exploited in the wild, users are urged to update their browsers as soon as possible to reduce the risk of compromise.”

Other Fixes

Along with the CVE-2020-15999 high priority security fix, which had a turnaround time of less than 24 hours, Google also fixed four other – medium to high severity – vulnerabilities in Chrome’s 86.0.4240.111 version. Here is the complete list:

  1. CVE-2020-16000, Severity – High: Inappropriate implementation in Blink. Reported by amaebi_jp on 2020-09-06.
  2. CVE-2020-16001, Severity – High: Use after free in media. Reported by Khalil Zhani on 2020-10-05.
  3. CVE-2020-16002, Severity – High: Use after free in PDFium. Reported by Weipeng Jiang (@Krace) from Codesafe Team of Legendsec at Qi’anxin Group on 2020-10-13.
  4. CVE-2020-15999, Severity – High: Heap buffer overflow in Freetype. Reported by Sergei Glazunov of Google Project Zero on 2020-10-19.
  5. CVE-2020-16003, Severity – Medium: Use after free in printing. Reported by Khalil Zhani on 2020-10-04.
Related News:
Researcher Discovers Unpatched Zero-Day Flaw affecting Latest Android Phones

CERT NZ Warns About Kiwis’ “Complacency Behavior” Towards Cybersecurity

New Zealand Reserve Bank hacked

The Cyber Smart Week for New Zealand, which started on October 19, continues to raise awareness on the importance of security in protecting personal data. CERT NZ, a government entity that supports organizations and individuals affected by cyberattacks, emphasizes on the security measures Kiwis (New Zealanders) need to take to be more cyber resilient.

According to a research by CERT NZ, the volume of financially motivated cyberattacks surged over the last six months in the country. While 87% of New Zealanders agree that security of their personal information is important to them, 40% said that taking the necessary precautions to safeguard their data online is inconvenient. Nearly, 32% of Kiwis do not check the privacy settings on their social media accounts. And 30% do not use two-factor authentication (2FA) when logging into an online account.

CERT NZ urged individuals to follow certain security steps to build cyber resilience. These include:

  • Use a password manager to keep track of each strong and unique password you have for every online account.
  • Turn on two-factor authentication to add an extra layer of security to your logins and accounts.
  • Update your devices and operating systems to defend against bugs and viruses.
  • Check your privacy settings to know and control who sees your stuff.

Related Stories:

CERT NZ Director Rob Pope, said, “CERT NZ’s incident data, and information provided by our global partners tells us that cyberattacks have become more sophisticated, persistent and harder to detect than ever before. Your personal information is highly valuable to attackers regardless of who you are, so it is important that more Kiwis get serious about protecting themselves online. Steps like using a password manager, two-factor authentication, updating devices and checking privacy settings are the basics to building your cyber defense.”

“It appears that the majority of Kiwis know they should be cyber smart, but some are not acting on it. The results are concerning. They reveal approximately a third of New Zealanders are more vulnerable to a cyberattack, meaning their data could be accessed and their identity stolen, enabling the attacker to conduct a range of criminal activities, including online fraud. We all lock our homes to stop burglars from stealing our valuable possessions. It is no different in the online world,” Pope added.

To address the surge in malware, phishing, and DDoS attacks, EC Council’s CISO MAG has planned a crisp half day virtual engagement, The Australia CISO Confluence, to create more awareness on the need for cybersecurity and its related implications in these testing times. Register here.

Credential-based Attacks are on the Rise: Is Your Organization Prepared to Fight Them?

credential-based attacks

Every year, National Cyber Security Awareness Month provides organizations with the opportunity to examine the major issues faced by security teams and arm themselves against potential threats to their business. As much of the workforce traded the traditional four walls of the office for at-home setups earlier this year, and COVID-19 provided nation-state actors with ample opportunities to expand credential theft. They particularly homed in on organizations in government, health care, and education with an intense focus on those working towards vaccine research.

By Trevor Daughney, VP, product marketing, Exabeam

In our modern remote work landscape, new issues have emerged as employees connect to sub-par security on home networks, share their corporate devices among household members and engage in other risky behaviors that would not normally draw concern within the confines of traditional office space. This distributed enterprise forces organizations across sectors to ask themselves whether or not they’re prepared to combat credential-based attacks.

As recent headlines can confirm, credential-based attacks don’t discriminate based on industry or company size. In April, Nintendo experienced credential-stuffing attacks, and in September, the United States Cybersecurity and Infrastructure Security Agency (CISA) published an analysis report detailing the malware attack on a federal agency’s enterprise network. In the report, CISA noted the threat actor leveraged compromised credentials to exploit weaknesses in the agency’s firewall. Just as NCSAM began, Microsoft published the Digital Defense Report showing the increasing sophistication of cyberthreats, which confirmed the effects of the pandemic on targeted industries and provided additional evidence pointing to a rise in credential-based attacks.

Credential-based attacks make it harder for a SOC to detect and respond to attackers, allowing adversaries to access private data and high-value assets. We’ve also seen credentials impacted mid-way through the attack by switching between user accounts or by escalating the privileges of a compromised user. Looking to remain one step ahead of security teams, hackers utilize these attacks to make it more difficult to detect and respond to their activity and to access other areas of the network.

Traditional cybersecurity investigation techniques are no longer enough to place organizations ahead of bad actors looking to compromise their systems and attack their data. Thus, more advanced approaches are needed today to prevent this dangerous lateral network movement. Organizations looking to modernize their systems and counter credential-based attacks can find success by adding intelligence to their SIEMs and implementing machine-learning-based analytics. The static rules of a SIEM will typically not fire if an attacker logs into a network – using stolen credentials, or as a malicious insider. Moreover, even if the SIEM provides an alert, without context, the security team is not able to tie the events together to provide the security team with a full picture of the attack chain. Threat actors can wait days, weeks, or even months before making their first lateral movement, which makes them extremely hard to detect without all the details.

By relying more on data analytics and machine learning, security teams are able to identify a user’s intent. Behavioral analytics starts with first establishing a baseline of a user’s typical behavior, comparing typical behavior to that which appears out of the norm, such as anomalous lateral movement. Security teams can then automatically stitch together various log sources into a timeline to detect anomalous behavior. In this fashion, behavioral analytics can also help combat insider threats, who may be engaging in permitted, but unusual, activity.

Employees outside of the SOC also have a role to play. In this year’s Verizon Data Breach Investigations Report, credential theft accounted for 67% of breaches and raised concerns around the vulnerability of remote workers. Therefore, security teams must continue to stress and repeat best password practices such as never using the same password twice, using complex passwords, and turning on multi-factor authentication.

As credential-based attacks gain notoriety and organizations become increasingly aware of the risks and consequences associated with them, security teams have responded by establishing baseline industry best practices to arm employees with the knowledge required to combat these threats. These include continuous employee education around good password hygiene, reminders to look for suspicious links or email addresses and an emphasis on the importance of avoiding the co-mingling of personal and professional email accounts. For security teams, prevention also involves closely monitoring user behaviors, allowing for early detection of malicious events, and establishing rigorous access controls, especially for users with privileged access.

By implementing a combination of behavioral analytics and smart password practices, security teams will be better prepared to thwart current and future credential-based attacks across the organization.


About the Author

Trevor DaughneyTrevor Daughney is an executive with a track record of building high performing teams to take enterprise cybersecurity SaaS and software technology and turn them into successful global businesses. Prior to Exabeam, he led enterprise product marketing at McAfee, Ping Identity, and Symantec. Trevor approaches marketing with a global mindset and builds on his experiences living and working in the US, Canada, and Asia. He has an MBA from the University of California, Berkeley.

Disclaimer

Views expressed in this article are personal. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.


Related story: Media Industry Becomes a Common Ground for Credential Stuffing Attacks


Cyber Risks During a Merger and Acquisition

U.S. and Australia to Jointly Develop Cyber Training Platform

TikTok was recently in the news as it was on the verge of being acquired by a U.S. company or a consortium for billions of dollars. What potential cyber risks are there for the acquiring U.S. company?  Tons. The wildly popular social media video sharing service is a Chinese company accused of purposefully undermining the security of U.S. citizens, and could potentially be influenced by its foreign government intelligence apparatus. If there was ever a case that exemplifies the justifications for having a bullet-proof merger & acquisition cybersecurity plan, it would be TikTok.

By Matthew Rosenquist, CISO, Eclipz

Although such potentially scandalous deals highlight the security concerns, nowadays every merger and acquisition brings with it many potential digital risks.  From small to large, simple to complex, all M&A deals involving technology have cybersecurity baggage and challenges.

Security does not happen by default


Mergers and Acquisitions represent a significant risk to organizations as integration and data sharing can expose assets to confidentiality, integrity, and availability threats. Security must identify the risks across a broad scope of areas. 

Connecting the networks could open a plethora of new dangers, especially if the acquired network is vulnerable or already compromised, as it puts at risk all the digital assets and services from the acquiring company.  If any of the new personnel, suppliers, partners, or vendors are disgruntled or working on behalf of external parties seeking to gain leverage, there can be serious insider risks.  Lack of security, process, oversight, and controls can undermine the value of the acquiring assets, diminishing the return-on-investment.  If the integration isn’t done well, valuable assets including talent, operational stability, and future generation of intellectual property can rapidly diminish.  If things go sideways, an acquisition can create a situation for the acquiring entity of regulatory non-compliance that brings with it an erosion of customer goodwill, negative press, lawsuits, legal injunctions, and other serious penalties.

Years ago, I built and led Intel Corporation’s M&A cybersecurity capability and processes. Throughout my career, I have been involved in over one-hundred and twenty mergers, acquisitions, divestitures, site closures, and joint ventures. I have published a variety of articles and presentations on this topic, spoken to many audiences, and advised other organizations on best practices.

M&A cybersecurity work is typically frantic, unpredictable, and oftentimes ambiguous. It demands executive sponsorship, strong leadership, great flexibility, and a willingness to rapidly adapt to emerging problems. It can press the boundaries of good security practices and test the mettle of the strongest cybersecurity organizations.

It is often dreaded by traditional security operations folks who are entrenched in the comfort of controlling a consistent, predictable, and structured environment.  M&A’s are chaotic and rarely comply with corporate security policies.  It is an art as much as it is a science when considering the technical, behavioral, and process aspects that must be comprehended and addressed.

Top 8 Key Learnings for M&A Cybersecurity

1. Security does not happen by default. As the complexities of M&A deals emerge, those involved move aggressively to solve problems. In the rush and pressure, security is often deprioritized in tactical decisions that eventually manifest into strategic issues. Cybersecurity must be involved both at the early planning stages, and stay engaged until the last closure maneuver is completed.

2. The unwavering support of executive management is crucial. A set of risk objectives must be defined, and the security team should be communicating the progress and necessary controls to meet those goals. Cybersecurity flows across all domains of the entire M&A team, and therefore must be a part of the leadership team.

3. Understanding the value proposition and goals of the M&A is crucial to identifying risks, knowing what to evaluate, and strategically planning the right balance of controls.

4. For regulated industries and sensitive intellectual property related acquisitions, profiling the data is key. Knowing what data is involved, its sensitivity, who has logical/physical access, and where it is physically located is necessary. It will be needed to ensure regulatory, legal, and IP confidentiality protection.

5. To prevail, both technical and behavioral security considerations must be incorporated into the business transition plan. Neither must be ignored and in most cases, the combination must be applied to every issue where cybersecurity is at risk. A security-savvy M&A team is the first step to highly effective results.

6. Logical and physical security aspects cannot be separated. Cybersecurity professionals can easily overlook the physical security factors which can jeopardize the confidentiality, integrity, and availability of the business.

7. Great attention must be paid to data retention, transfer, and destruction. “Deal data” can be a vague and changing concept that may be interpreted differently over time, especially in larger transactions. Understanding the scope, expectations, and commitments is a necessity.

8. Managing digital risks requires a community effort. Effective M&A cybersecurity requires a knowledgeable team, good leadership, and broad support to efficiently achieve the stated goals with consistency and comprehensiveness.

Conclusion

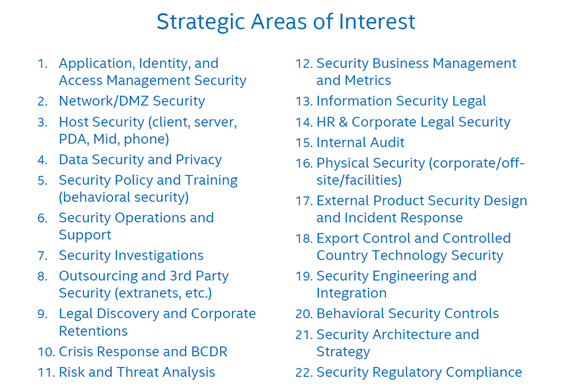
The range of tactical issues that an M&A cybersecurity team must understand and explore for each deal is wide and deeply complex.  For a quick overview, I published a reference years ago which highlights the most significant Areas of Interest for internal cybersecurity.  For acquisitions with products and services, there are a few more aspects to consider.

The complete presentation of M&A Areas of Interest can be found here: https://www.slideshare.net/MatthewRosenquist/mergers-and-acquisition-security

About the Author

Matthew Rosenquist is the Chief Information Security Officer (CISO) for Eclipz, the former Cybersecurity Strategist for Intel Corp, and benefits from 30 diverse years in the fields of cyber, physical, and information security. Mr. Rosenquist specializes in security strategy, measuring value, developing best-practices for cost-effective capabilities, and establishing organizations that deliver optimal levels of cybersecurity, privacy, ethics, and safety.  As a cybersecurity strategist, he identifies emerging risks and opportunities to help organizations balance threats, costs, and usability factors to achieve an optimal level of security.  Mr. Rosenquist is very active in the industry.  He is an experienced keynote speaker, collaborates with industry partners to tackle pressing problems, and has published acclaimed articles, white papers, blogs, and videos on a wide range of cybersecurity topics.  Mr. Rosenquist is a member of multiple advisory boards and consults on best-practices and emerging risks to academic, business, and government audiences across the globe.

Disclaimer

All views are personal and attributed to the author(s). The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.

Lapse in Security! Pfizers Inadvertently Exposes PII of U.S. Prescription Drug Users

Lapse in Pfizer’s Security Exposes PII of U.S. Prescription Drug Users

Global pharmaceutical company Pfizer inadvertently exposed Personal Identifiable Information (PII) of hundreds of prescription drug users in the U.S. after its misconfigured Google Cloud Storage bucket was left online. According to security experts from vpnMentor, the bucket contained prescriptions and transcripts between users of various Pfizer drugs like Lyrica, Chantix, and cancer treatments Ibrance, and Aromasin, and the company’s interactive voice response (IVR) customer support software.

The misconfigured bucket leaked hundreds of transcripts including their personal data like full names, home addresses, email addresses, phone numbers, partial details of health, and medical status. The misconfigured cloud bucket is now secured after vpnMentor’s researchers reported the issue. 

What’s the Impact?

While there is no information on whether any threat actors accessed the leaky database, vpnMentor’s researchers stated that cybercriminals could exploit the leaked data by targeting drug users in phishing campaigns and other fraudulent schemes.

“If cybercriminals succeeded in tricking a victim into providing additional PII data, they could use this to pursue various forms of fraud, including total identity theft. In doing so, they could destroy a person’s financial well-being and create tremendous difficulty in their personal lives. Furthermore, there is a high probability the people exposed in these transcripts are experiencing ill health, physically, and emotionally,” the researchers added.

Worth of Medical Data

A survey from cybersecurity firm Carbon Black stated the rate of cyberattacks on the health care industry appears to be increasing exponentially. Carbon Black disclosed what is happening to the Personal Health Information (PHI) that was stolen by cybercriminals. The survey, which involved 20 of the health care industry’s Chief Information Security Officers (CISOs), found the health care sector being targeted because of how lucrative PHI is when compared to other personal data like credit card numbers. It is said that personal health information is worth three times more than other personal information since the health information never changes and can be used by cybercriminal groups for extortion or compromise.

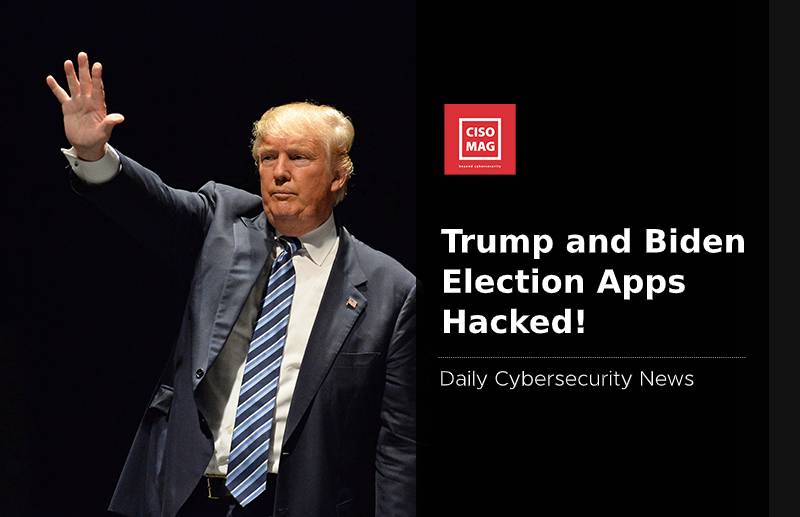
Promon Proves Trump and Biden’s Election Apps are Easy Targets of Cyberattacks

Trump and Biden Election Apps hacked

The U.S. Presidential Elections will be held on November 3, 2020. The two candidates, President Donald Trump and Republican candidate Joe Biden are going head-to-head in many states, so much so that even the exit polls present uncertainties. The two have made many public appearances during their presidential campaigns to reach out to the masses and address their concerns. During one such campaign rally held in Tucson, Arizona, Trump sadly played down the grievousness of hacking, stating, “Nobody gets Hacked.” However, days later, Promon, a Norwegian cybersecurity firm, hacked both Trump and Joe Biden’s election apps to prove: “Everything can be hacked.”

 Key Highlights 

  • At a campaign event in Tucson, Arizona on October 21, President Trump made a false claim that “Nobody gets Hacked.”
  • Promon cybersecurity firm’s white hat hackers used a well-known Android vulnerability to alter President Trump’s and his rival Joe Biden’s election apps to show nothing is safe.
  • Experts at Promon said that the same weakness could be used to steal personal data of app users.
  • The claim shocked everyone as President Trump’s Twitter account and hotel chain have both been hacked previously.

What is the Vulnerability?

The white hat hackers at Promon were analyzing the election apps of the two candidates when they discovered that both apps were highly vulnerable to a known and critical Android vulnerability known as StrandHogg. This vulnerability allows malware gangs to hijack legitimate apps and perform malicious operations like phishing. In fact, the 2.0 version of this vulnerability enables cybercriminals to hijack nearly any app running on Android 9.0 devices and below. This further enables stealing of user credentials without any fuss.

Related News:
StrandHogg Vulnerability Hunting All Android Versions
StrandHogg 2.0 Impersonates Real Android Apps to Steal User Data

Promon’s Chief Technology Officer, Tom Lysemose Hansen said, “The president’s statement sadly reflects a widely believed sentiment that secure passwords will protect you from hackers and that hacking, in general, doesn’t affect the average citizen. Sadly, this isn’t the case. Absolutely nothing is ‘unhackable’ and even the most secure, high profile accounts are vulnerable should the user fall victim to a phishing attack which seeks usernames and passwords.” He added, “The claim that ‘nobody gets hacked’ is simply untrue and — given the influence of the president — can have dangerous impacts on the behavior of hundreds of thousands of people.”

So, the bottom line of the entire episode is that “Everything can be hacked,”— yes, even POTUS apps and accounts. So no one should be complacent when it comes to their personal online cybersecurity.


CISO MAG Endpoint Security SurveyTell us more about your Endpoint Security knowledge and win lots of amazing goodies!

Take the Survey Now!!!


Dr. Reddy’s Lab Attacked Days After India Approves Russia’s COVID-19 Vaccine Trial

Dr. Reddy’s Lab Attacked Days After India Approves Russia’s COVID-19 Vaccine Trial

Indian pharmaceutical company Dr. Reddy’s Laboratories Ltd. (DRL) was forced to shut down its operations temporarily after a cyberattack hit its data center services, which are located in India, the U.S., the U.K., Brazil, and Russia. While the information on whether any data or facilities have been affected is unknown, the company said it had isolated all of its data center services as a precautionary measure.

Chief Information Officer Mukesh Rathi at DRL, said, “In the wake of a detected cyberattack, we have isolated all data center services to take required preventive actions. We are anticipating all services to be up within 24 hours, and we do not foresee any major impact on our operations due to this incident.”

Target on COVID-19 Vaccine Research?

The security incident occurred after Dr. Reddy’s received approval from the Drugs Controller General of India (DCGI) to conduct clinical trials of the Russian COVID-19 vaccine in India.

Ever since the pandemic began, several attacks have been reported on organizations that are conducting research on COVID-19 vaccine. Recently, the FBI stated that certain state-backed threat actors broke into the U.S. research institutions, which are working on COVID-19-related research. Tonya Ugoretz, Deputy Assistant Director at the FBI and head of the bureau’s Cyber Readiness and Intelligence Branch, warned that foreign government-sponsored hackers have targeted the U.S. in different ways, including attempts to steal information from the national health care sector and COVID-19 research centers.

The U.K.’s National Cyber Security Centre (NCSC), Canada’s Communications Security Establishment (CSE), and the U.S. National Security Agency (NSA) stated that a cyber espionage group APT29 is trying to steal information and intellectual property related to the testing and development of Coronavirus vaccines.

Google is the Monopoly Gatekeeper to the Internet, says DoJ

Google

The U.S. Department of Justice (DoJ) filed a civil antitrust lawsuit against Google for unlawfully maintaining monopolies via anticompetitive practices in the search and search advertising markets. The lawsuit, filed in the District Court of Columbia, alleged that the search engine has reported over 90% of all search queries in the U.S. and used anticompetitive techniques to retain its monopolies in search and online search advertising.

“Google is the monopoly gatekeeper to the internet for billions of users and countless advertisers globally,” the DoJ said.

The lawsuit also claimed that Google has undergone several agreements that closed new opportunities to other search engine companies. Google has set as the preset default general search engine on billions of mobile devices barring its competitors.

According to the DoJ, Google illicitly maintained monopolies in search and search advertising by:

  • Entering into exclusivity agreements that forbid preinstallation of any competing search service.
  • Other arrangements that force preinstallation of its search applications in prime locations on mobile devices and making them undeletable, regardless of consumer preference.
  • Entering into long-term agreements with Apple that require Google to be the default – and de facto exclusive – general search engine on Apple’s popular Safari browser, and other Apple search tools.
  • Generally using monopoly profits to buy preferential treatment for its search engine on devices, web browsers, and other search access points, creating a continuous and self-reinforcing cycle of monopolization.

Attorney General William Barr, said, “Millions of Americans rely on the Internet and online platforms for their daily lives.  Competition in this industry is vitally important, which is why today’s challenge against Google — the gatekeeper of the Internet — for violating antitrust laws is a monumental case both for the Department of Justice and for the American people. Since my confirmation, I have prioritized the Department’s review of online market-leading platforms to ensure that our technology industries remain competitive.  This lawsuit strikes at the heart of Google’s grip over the internet for millions of American consumers, advertisers, small businesses, and entrepreneurs beholden to an unlawful monopolist.”

“As with its historic antitrust actions against AT&T in 1974 and Microsoft in 1998, the Department is again enforcing the Sherman Act to restore the role of competition and open the door to the next wave of innovation this time in vital digital markets,” said Deputy Attorney General Jeffrey A. Rosen.

Take a Unified Approach to Secure Your Software

Your software defines your business. It’s what sets you apart, but it’s also what can bring your organization down if it’s not secure. There’s a constant conversation around the need for a unified approach to software security. That’s really what DevSecOps is all about—and yet, the current AppSec model is anything but collaborative.

By John Worrall, CEO, ZeroNorth

This schism between security teams and developers, this cultural divide, comes into play primarily in the way it affects our ability to rapidly build and deliver secure products. CISOs and product security leaders must be able to answer the question, “Who owns security?” And the answer can’t just be “I do.” Even though DevSecOps promotes a mindset of shared responsibility, without accountability and executive-level support, “everyone” owning security can quickly lapse into “no one.”

And without this critical piece lodged firmly in place, there’s still lots of work to be done.

Dealing with Misalignment

Some valuable data has recently come out on this cultural divide between security and development. 77% of developers say this existing gap affects their ability to meet deadlines, while 70% of AppSec professionals say this misalignment puts the security of applications at risk.[1]

Both teams admit that working together is a challenge. When asked to rate the difficulty in working together on a scale of one to 10, 69% of developers and 66% of AppSec professionals rank it as 10 — extremely difficult. Their differences don’t end there. They don’t agree on the scope of the problem. Only 35% of developers say application risk is increasing, while 60% of AppSec professionals believe this to be true.

Different teams, different priorities, different perspectives. This means it’s not technology or even systems getting in the way — but people. Before you can even think about investing in new technology or expanding your AppSec program, you need to get your people aligned.

This starts by bringing business, security, and product team lead together to lay the groundwork. Level-set on the need for an alignment plan focused on collaboration and accountability to ultimately ensure secure software development. Discuss the importance of clearly defined and aligned objectives, ways to achieve them through incentives and SLAs, and how technology can support this people-centric approach. Then, you’re ready for step one: figuring out exactly who owns what.

Governance and Operations (Who owns what?)

Much of today’s fragmentation stems from a fundamental disagreement around responsibility for application security. The same industry study found 39% of developers believe their security is responsible, while 67% of AppSec practitioners say they are responsible. Who’s going to set up the policy? Who’s going to measure its performance? Who’s going to drive continuous improvement?  And then, who’s actually going to create secure code?

Who does what is important. This may look different from organization-to-organization, but the majority of businesses I’ve spoken with have adopted a hybrid model, where security is responsible for governance; development is charged with implementation. Security teams set standards, measure performance to standards, and work with all levels of the organization to communicate the current risk status and the progress of improvement initiatives. The most mature security teams have evolved the role of security champions from blockers to enablers, becoming advisors and coaches to the development teams.

In regulated industries with heavy compliance requirements, the governance function is particularly critical. Yet in many companies, DevOps and security teams still operate in isolation until the very end of the software development lifecycle, with developers moving fast to push out new code, only to be stopped in their tracks due to late-breaking reports from security on discovered vulnerabilities or quality issues.

With so much at stake, these regulated industries must adopt a governance model that gives security teams enterprise control and a global view of risk to meet consistent security and compliance standards. Yet these centralized policies must be enacted locally to empower developers to rapidly and securely deliver innovation. This flexibility makes it easier to incorporate tools that allow developers to fix issues while they’re coding.

Within this framework, developers can operate within their existing, preferred workflows (or choose their own security tools, if they want), while ensuring all tools and workflows contribute to a centralized, prioritized view of risk across the entire application portfolio. With one source of truth that is reported on, and trusted by, all parties, organizations can pinpoint key gaps and continuously improve the enterprise security posture.

Unification is the Key

Research tells us, there’s much work to be done to tear down siloes, reshape mindsets and unify teams. As companies accelerate their shift toward DevOps, this cultural disconnect will continue to expand until organizations find a way to bring security into the DevOps world. I believe unification is the only way organizations can make this reality.

Embracing the right technology platform will help accelerate this unification effort and make a shared responsibility model work in three key ways:

  • Provides the necessary structure. By activating unified, enterprise standards, policies, and analytics that power continuous risk and compliance enforcement, organizations can innovate with confidence.
  • Accelerates pipeline velocity. By orchestrating the continuous discovery and remediation of vulnerabilities across the SDLC, security and product teams can collaboratively accelerate application delivery.
  • Unburdens developers. By making AppSec programs transparent and friction-free, developers can meet corporate standards without changing their workflows or being flooded with non-priority tickets and issues.

Security Leaders at the Finish

You’ve aligned on objectives, crystallized responsibilities, and established a framework. Now, where do you go from here?

All team leads must agree to do their prescribed parts to make DevSecOps a reality. This requires a unified management approach, based on a shared desire to deliver secure software, define and support software security standards and hold themselves, and their teams, accountable. Yet every major organizational change initiative must have a champion.

CISOs are uniquely positioned to spearhead this unification effort at the management level and serve as “coach” for development teams, motivating them to prioritize security, improve practices, and embrace a more collaborative culture.

It will take more than good intentions, however, to move the needle. The same research shows lip service won’t get you far: nearly half (48%) of developers say their leadership teams are already trying to improve teamwork. An organizational shift of this magnitude also requires the right tools and processes in place to centralize AppSec management, orchestrate disparate security tools, automate manual processes, surface actionable intelligence, streamline remediation and deliver robust analytics and reporting. This is where CISOs need to take the reins, architecting an AppSec program that enables developers to drive security within their teams on a continuous basis and aligns security with the pace of development. In doing so, they will bring value to the executive leadership team and the business as a whole.

Software security is too important to get wrong. The time is now to get it right. It will take a commitment from all sides to build this type of shared vision for the future. Once all parties realize application security vulnerabilities put the business at risk in the same way as financial or market risk, they’ll hopefully begin to see the light — and to promote a vision of shared responsibility for the good of software.


References: [1] Revealing the Cultural Divide Between Application Security and Development


About the Author
John Worrall is CEO of ZeroNorth in 2019 as chief executive officer, leading the company in its delivery of the only platform for risk-based vulnerability orchestration across applications and infrastructure. As CEO, John heads up all aspects of the company’s strategy, product, operations, and go-to-market functions. In addition to leading ZeroNorth, John serves on the Board of Directors at FamilyAid Boston, a nonprofit that helps children and their parents facing homelessness in Greater Boston. He holds a bachelor’s degree in economics from St. Lawrence University.

Disclaimer

Views expressed in this article are personal. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.