Home Blog Page 331

Symantec announces acquisition of Luminate Security

Symantec

Symantec Corporation recently announced the acquisition of Software Defined Perimeter and Zero Trust Innovator Luminate Security. Symantec, better known for its Norton security software suite, stated the acquisition reinforces the company’s leadership in cloud security. Its integrated Cyber Defense Platform combines cloud and on-premises security across endpoints, networks, email, and cloud protecting organizations against evolving cyber threats.

Luminate Security, an Israel-based startup, allows security and IT teams to create Zero Trust Application Access architecture without traditional VPN appliances. Founded in 2017, Luminate Security claims its technology platform Secure Access Cloud can securely connect users from any device to corporate applications on-premises and in the cloud. The startup says its cloud technology extends the power of Symantec’s Integrated Cyber Defense Platform to users to access the specific applications and resources for which they are authorized.

“Now and in the future, we anticipate more and more corporations will operate their business on infrastructure that is managed by multiple third parties such as Azure, AWS and Google. In this rapidly evolving world, trust in external infrastructure must be carefully considered as corporations can outsource infrastructure but must also remain responsible for data and users. Luminate incorporated into Symantec’s Integrated Cyber Defense puts us at the forefront of security in the cloud era,” said Greg Clark, president and CEO, Symantec. “Secure and private access is a cornerstone of cyber defense. We are excited to partner with the Luminate team and look forward to rapid delivery of this unique capability to our customers and continuing to provide quantifiable value to their cloud journey.”

Speaking on the acquisition, Ofer Smadari, CEO of Luminate Security said, “As a partner, our integrations with Symantec were successful in reducing complexity and increasing security for joint customers. With this next step, we look forward to fully integrating across the entire portfolio and delivering even more innovation to offer complete security for the Cloud Generation.”

In 2018, Symantec acquired Appthority and Javelin Networks to strengthen its mobile and enterprise security products and services. Appthority offers comprehensive Mobile Application Security Analysis services, including automated app-vetting, app-threat scoring, and continuous app analysis. The acquisitions allow Symantec to use Appthority’s technology to analyze mobile apps for malicious threats and defend organizations against Active Directory-based attacks.

“Best way to handle malware attacks is automation and continuous monitoring”

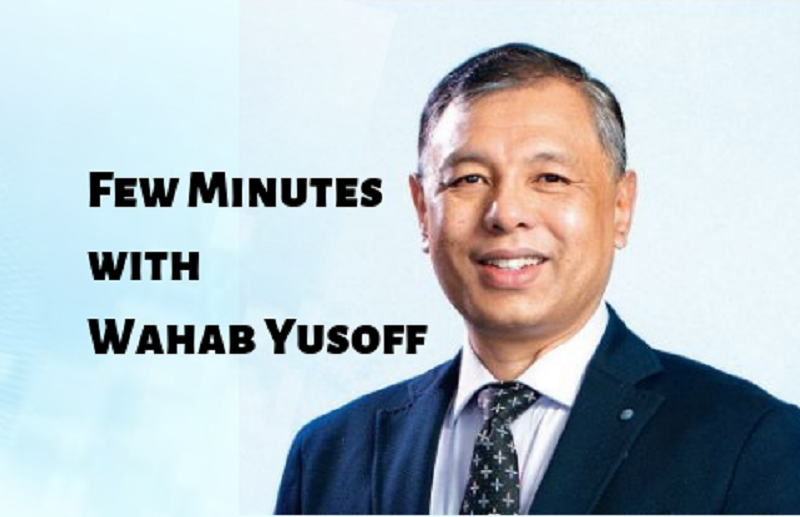
Wahab Yusoff

Wahab Yusoff is a veteran in the information technology industry. The Vice President, Asia, of ForeScout Technologies Inc. has assisted a number of organizations in establishing and growing their operations in the Asia Pacific Region. In an exclusive conversation with CISO MAG’s Rudra Srinivas, Yusoff talks about his role in the organization, the rapidly expanding Internet of Things market, and the need of implementing cybersecurity measures during a technology partnership.

First of all, I would like to congratulate you on your appointment as a member of the Future Economy Council’s leadership team. How has been the journey in the field of information security so far?

My journey in cybersecurity has been very rewarding. For over 25 years, I have been focused on helping businesses secure themselves and grow in the Asia Pacific region. Technology is advancing rapidly, and the threats that come along with it are constantly evolving. It’s a very fast-paced industry that has kept me on my toes.

In addition to my position as Vice President of Asia at Forescout Technologies, I have also been appointed as a member of Singapore’s Future Economy Council in November last year. As technology has a key role to play in charting the direction for Singapore’s future, I hope to share my expertise, particularly in the realm of cybersecurity, and ensure the protection of assets as the government looks to leverage advanced technologies to propel Singapore’s economy forward.

As a security leader, what are the challenges you face while enforcing cybersecurity strategies at ForeScout Technologies?

Visibility remains a top cybersecurity challenge for businesses across the globe. Malicious actors are constantly evolving and will try to find a way in through any device, known or unknown, as long as they are connected to the network. In many instances, attacks take place because an organization lacks visibility and is unable to protect assets that they don’t realize are connected to their network.

According to a research from McAfee, there is an increase of 73 percent in malware targeting IoT devices. Do you think that the businesses in the Asian countries are prepared to handle malware attacks?

Asia is highly complex and diverse in terms of their cybersecurity preparedness. On one end of the spectrum, there are developing countries that are just starting on their digitalization journey. On the other hand, we have countries that have already set up government agencies dedicated to overseeing the country’s cybersecurity strategy, operations, education, outreach, and ecosystem development, such as the Cyber Security Agency of Singapore and CyberSecurity Malaysia.

On a corporate level, the best way for businesses to effectively handle malware attacks is to leverage automation and continuous monitoring to minimize the likelihood of such attacks and ensure good execution of cybersecurity best practices. Automation will enable businesses to offload time-consuming and unnecessarily burdensome tasks and retool a portion of their workforce, resulting in stronger cybersecurity programs.

The proliferation of IoT devices has led to complexity and newer threats to several businesses. How can the IoT devices be protected from new and evolving threats?

The growth of enterprise IoT devices and operational technology (OT) is tremendous. This adds a layer of complexity, as businesses need to ensure that all of their devices are compliant with cybersecurity measures set out by the business. As the use of network-connected devices grows, businesses also need to ensure that all of their devices are secure to prevent malicious actors from accessing their entire network infrastructure – and it only takes one device and one attempt for a breach to be successful.

Cybersecurity will therefore become an integral component. Businesses will have to ensure that they, first and foremost, have device visibility and control across their entire network in order to mitigate cyber-attacks. This way, businesses have the ability to see devices the instant they connect to the network and assess for vulnerabilities and malicious activity. After which, businesses can also classify these devices and validate their identities. This key capability is essential for improving compliance as well as defining your enforcement policies.

According to you, how the Internet of Things (IoT) is going to change the cybersecurity landscape in 2019?

In 2019, we can anticipate that the use of IoT devices will continue to flourish in enterprises. However, in addition to this, we can also expect to see the convergence of IT and OT environments. Given the rapid rate at which these devices are being leveraged by businesses, interconnectivity is continuing to prove itself valuable for business efficiency.

Although these devices operate differently, they must not be treated in isolation. We predict that attacks by malicious actors will increase in frequency and intensity, forcing the enterprises to either invest in newer, more secure systems, or reevaluate their entire security architecture and reassess the manner in which IoT, OT and IT devices interact.

Recently, ForeScout partnered with Respond Software to strengthen Industrial Control System (ICS) cybersecurity programs. How do you intend to boost cybersecurity through this partnership?

The complexity of industrial environments has led to an increasing number of ICS-specific cyber threats, in which asset owners have no visibility. This is further compounded by the challenge of finding skilled security personnel.

There is a need for a solution that enables businesses to continuously monitor and analyze key networks and quickly make appropriate decisions. To address this, we have partnered with Respond Software to roll out a new technical integration called Virtual ICS Threat Analyst Logic (VITAL), which allows ICS asset owners to automate threat analyst decision-making processes. The integration streamlines ICS security operations for critical infrastructure by escalating and prioritizing critical incidents, while eliminating false positive alerts. On a broader scale, this partnership strengthens our joint customers’ ICS security teams by allowing them to focus on the serious security issues.

Any piece of advice for budding security professionals?

Malicious actors are constantly evolving and will continue to find new ways to break through the network. The best way to be prepared for such an instance is by employing a three-step defense strategy – see, control and orchestrate.

See: Lack of device visibility and control continues to be top concerns for IT and security team as well as risk management leaders. Oftentimes, organizations lack a complete, up-to-date inventory of the devices and assets they have. Visibility and intelligence of network-connected devices is therefore essential in helping organizations effectively manage security risks.

Control: To reduce the attack surface and risk, it is important to have the security tools that can control the level of access provided to any device on the network. Once an organization has the ability to see all of the activity on a network, they can then manage risk more effectively by applying the appropriate network controls. Through this process, organizations can decide to allow, deny or limit network access based on device posture and the organization’s security policies.

Orchestrate: Organizations need the ability to align network controls as well as automate and orchestrate information sharing across all network environments in order to identify, prioritize and mitigate cyber threats quickly and effectively. This enables the ability to enforce consistent network security policies and mitigate risk effectively.

Axonius raises $13 million to accelerate its security platform

Axonius Raises US$58 Million to Accelerate its Security Management Tool

Cybersecurity asset management firm Axonius recently raised $13 million in a series A funding round led by Bessemer Venture Partners along with the participation from existing investors YL Ventures, Vertex, WTI, and Emerge.

The New York-based startup stated that it will utilize the new funds to accelerate its customer growth, further develop product innovations, and to expand the offerings of its flagship product—Cybersecurity Asset Management Platform. As per the investment deal, Axonius also added Bessemer’s partner Amit Karp to its board of directors.

Axonius provides cybersecurity asset management services to the public and private enterprises with its Cybersecurity Asset Management Platform that integrates information from connected devices to manage and secure them constantly. Its asset management platform creates a single point of view into connected devices, including desktops, laptops, servers, cloud instances, mobile devices, and other IoT on a company’s network and automatically detects whether those assets fit within the stipulated security policies or not.

Founded in 2017, Axonius claims that it’s the only cybersecurity platform to provide organizations with an up-to-date inventory and automated policy validation. The company also says it holds a wide range of client base, including The New York Times, AppsFlyer, and Natera.

Speaking on the new investment round Dean Sysman, co-founder and CEO of Axonius, said, “Asset management is the most fundamental requirement security teams need to enhance security operations amidst expanding threats they face daily. A security team’s job is already difficult enough, yet they’re still spending time trying to figure out what assets and devices actually exist on their networks and if they adhere to their company’s security policies. This investment enables us to advance Axonius’ technology and help enterprises to confidently manage and secure all known and unknown devices on their network.”

Hackers cashed out $3.2 million worth tokens from Cryptopia attack

Cyrptocurrency

In what was dubbed as the first cryptocurrency hack of 2019, Cryptopia had lost nearly 19,390 ETH tokens in the cyber-attack on January 13. Blockchain analytics firm Elementus recently tweeted that the hackers have cashed out $3.2 million from the stolen tokens. “As of this morning, the hackers have liquidated $3.2m in tokens, with the bulk of that going to Etherdelta,” read the tweet.

According to reports, the hackers have been sending their loot to popular crypto exchanges with Bitbox, Binance, and Huobi seeing the most withdrawal volumes. It is estimated that out of the $16 million stolen by hackers nearly $900,000 have been withdrawn.

Earlier in January, the cryptocurrency exchange announced unscheduled maintenance. With several eyebrows raised on it, Cryptopia admitted to having fallen prey to a cyber-attack on January 15 and stated that the security breach had resulted in a significant amount of losses to the firm. The company stayed tight-lipped about the amount of “significant losses” until cybersecurity firm Hacken discovered that there was an unauthorized transfer of 19,390 ETH tokens. But the buck didn’t stop there. The company continues to fail in regaining control over its wallets, and another incident occurred where hacker left with 1,675 ETH tokens. It was Elementus which notified that the hackers have syphoned nearly 16 million from the first attack.

According to a research study by cybersecurity firm Ciphertrace, over $1 billion have been lost to cryptocurrency hacks. It stated that hackers had stolen $927 million only in the first nine months of 2018. “These cyber attacks bring the total amount of cryptocurrencies reported as stolen in 2018 through the end of Q3 to $927 million. CipherTrace estimates this trend will bring the total stolen and reported in 2018 to well over $1 billion by the end of the year,” the report notes.

Qatar MoTC launches new cybersecurity framework

Qatar

The Ministry of Transport and Communications (MoTC) of Qatar have launched a cybersecurity framework for establishing mechanisms for compliance with the national standards. Minister of Transport and Communications Jassim Seif Ahmed al-Sulaiti pointed out that the need for the new framework revolves around the technology that has been provided by international suppliers, which often need varying levels of skill and security. As the owner of these systems, it is the duty of the government to ensure its safety and protection against cyber attacks.

“To this end, we are pleased to announce the launch of the national information security standards framework, which is our approach to aligning ICT programmes, systems and services with best practices for the protection of digital information and data in accordance with our laws and regulations, through the issuance of licence certificates, documentation and accreditation in accordance with our national standards to help institutions from all sectors to secure information systems and improve maturity in the implementation of information security policies leading to the creation of a safer and more vibrant cyber environment,” he said at an event in Doha.

The mechanisms of compliance will see setting new standard for security, ensuring the quality and security of government systems which will including launching an IT audit certification program which will enable companies to obtain certification of compliance through an accredited control service provider. These mechanisms revolve around making sure that the government deploys sophisticated technological solution for its citizens.

“The ministry’s mission is to provide all the tools and knowledge that will help to ensure the safety of our country, but we have a responsibility to use those tools and knowledge to make sure that all our government systems are secure, and we fully understand the difficulty of compliance, but, as in all areas, many important things are difficult and require more effort and joint action,” he added.

Researcher finds GandCrab ransomware in Super Mario image

Ransomware, supply chain and ransomware

A researcher discovered a ransomware embedded into a downloadable Super Mario image using steganography method. Matthew Rowen, a security researcher from Bromium, an advanced malware protection services provider, stated he encountered a spreadsheet that contained a trojan sample during his analysis.

“A few days ago, I was investigating a sample piece of malware where our static analysis flagged a spreadsheet as containing a Trojan, but the behavioral trace showed very little happening. This is quite common for various reasons, but one of the quirks of how we work at Bromium is that we care about getting malware to run and fully detonate within our secure containers. This enables our customers to understand the threats they are facing, and to take any other remedial action necessary without any risk to their endpoints or company assets. Running their malware actually makes our customers more secure,” Matthew Rowen stated in a post.

“Steganographic techniques such as using the low-bits from pixel values are clearly not new, but it’s rare that we see this kind of thing in malspam; even at Bromium, where we normally see slightly more advanced malware that evaded the rest of the endpoint security stack. It’s also pretty hard to defend against this kind of traffic at the firewall,” Rowen added.

The attackers send emails with an attached spreadsheet that has an embedded malware and a macro. The attachment prompts the user to click on enable content link in order to deploy the malware. The researcher stated the malware firstly checks the region to make sure that the device is based out in Italy relying on the administrative language of the operating system. The malware will not deploy if the device is not based in Italy.

Once the user downloads the malware, it connects to the remote server and downloads the Gandcrab ransomware to infect the user’s device and encrypt the files and demand the ransom to provide the file access back, according to Rowen.

API-driven cloud security company vArmour raises $44 million

Startup funding

vArmour, a cloud security company, recently raised $44 million in a series E funding round led by AllegisCyber and NightDragon along with the participation from existing investors. The Mountain View-based company stated the new investment will support to further develop its security solutions that protect data and applications across the public and private cloud environments.

Founded in 2011, vArmour is an API-driven cloud security company that helps companies to consistently apply security controls across hybrid clouds. Its security approach includes auto-discovering hybrid cloud applications, computing infrastructure-independent communication policies, and measuring effective enforcement to maintain continuous compliance. vArmour claims its core technology Conform bridges security and compliance policy requirements for public and private cloud.

“Security and IT pros are having a difficult time maintaining consistent security policy across their private and public cloud environments, so we’ve designed Conform to help these teams manage the numerous compliance requirements they have to deal with. By taming the cloud, vArmour brings peace of mind all the way to the board room, enabling further cloud adoption and aiding with regulatory compliance,” said Tim Eades, CEO of vArmour

Speaking on the new investment Bob Ackerman, Founder and Managing Director at AllegisCyber, said, “Organizations are deploying multiple clouds for business agility and reduced cost, but the rapid adoption is making it a nightmare for security and IT pros to provide consistent security controls across cloud platforms. vArmour is already servicing this need with hundreds of customers, and we’re excited to help vArmour grow to the next stage of development.”

Parliament of Australia reports cyber incident

Australia to Spend $1.19 Bn to Boost Cybersecurity

The parliament of Australia recently stated that they’ve noticed an unknown intruder apparently tried to hack their computer systems. According to the official statement, hackers tried to break into the parliament’s computer network that includes lawmakers’ email archives. However, the parliament officials clarified that there were no indications of data theft so far.

They also stated that they’re updating all the passwords of its network systems and started an investigation. It’s believed that a foreign government was behind the attack, possibly China, ABC.net reported.

“Following a security incident on the parliamentary computing network, a number of measures have been implemented to protect the network and its users,” Parliament’s presiding officers, Tony Smith and Scott Ryan said in a joint statement. “All users have been required to change their passwords. This has occurred overnight and this morning.”

“There is no evidence that any data has been accessed or taken at this time, however this will remain subject to ongoing investigation,” the statement added.

Prime Minister Scott Morrison made clear that no Federal Government departments had been targeted in the attack. “I don’t propose to go into any sort of detailed commentary on the source or nature of this. Once further information is available then we will be in a position to provide further detail,” Scott Morrison added.

The Australian government faced a number of criticisms on its cybersecurity landscape in recent years. An inspection by the Australian National Audit Office (ANAO) exposed the failure of government organizations to implement cybersecurity requirements. The ANAO’s fourth report on the cyber resilience of government departments and agencies states that except the Treasury Department both the National Archives and Geoscience Australia failed to implement the top four mandatory cybersecurity strategies instructed by the Australian Signals Directorate (ASD).

In order to promote cybersecurity systems across government, business, and academia, the Australian government launched a new Joint Cyber Security Center (JCSC) in Adelaide, South Australia. The facility is a part of the government’s $47 million JCSC program that bridges the gap between several public and private companies in sectors such as defense, finance, transport, energy, health, mining, and education.

The new facility launched by the Minister for Defense Christopher Pyne is aimed to be a central hub for the cybersecurity information, advice, and assistance for Australians. The Center joins the list of other JCSC Centers located in Brisbane, Perth, Canberra, Melbourne, and Sydney.

Over 59,000 data breaches reported since introduction of GDPR: Survey

GDPR Fines

European companies experienced thousands of data breaches since data protection laws were brought in last year, according to a survey conducted by a law firm DLA Piper. In its survey dubbed GDPR Data Breach survey, DLA Piper stated that over 59,000 data breaches have been reported across the European Economic Area (EEA) by the public and private organizations since the General Data Protection Regulation (GDPR) came into effect on May 25, 2018.

Of the 26 EEA countries, Netherlands topped the list with 15,400 data breach notifications followed by Germany and the United Kingdom with 12,600 and 10,600 reported breaches, respectively. Whereas the lowest number of reported breaches were made in Liechtenstein, Iceland, and Cyprus with 15, 25 and 35 breaches respectively, the survey revealed.

Till date, around 91 fines have been reported which are related to personal data breaches and GDPR infringements, according to the survey. The highest GDPR fine imposed to date is €50 million (around $57 million), which was made against the search engine giant Google on January 21, 2019, by the French data regulator CNIL (National Data Protection Commission) for violating the General Data Protection Regulation (GDPR) law. The data protection watchdog stated it had levied the fine for Google’s lack of transparency and valid agreement regarding ads personalization. The regulator also said that Google didn’t sufficiently inform the people about how it collected users’ data to personalize ads.

“The GDPR completely changes the compliance risk for organizations which suffer a personal data breach due to revenue-based fines and the potential for U.S. style group litigation claims for compensation. As we saw in the U.S. when mandatory breach notification laws came into force, backed up by tough sanctions for not notifying, the GDPR is driving personal data breach out into the open. Our report confirms this with more than 59,000 data breaches notified across Europe in the first 8 months since the GDPR came into force,” said Ross McKean, a partner at DLA Piper.

Recently, The European Commission (EC) stated that data protection regulators in Europe have received more than 95,000 complaints about potential data breaches, after the implementation of the General Data Protection Regulation (GDPR). The commission also said that most of the complaints are focused on telemarketing, promotional emails, and video surveillance.

Palo Alto Networks partners with IBM Canada and British Columbia

Palo Alto

Cybersecurity firm Palo Alto Networks recently announced the launch of Palo Alto Networks Cybersecurity Academy in collaboration with IBM Canada and the British Columbia Ministry of Education. The Santa Clara-based company stated the latest facility is intended to bridge the skills gap by preparing students for careers in cybersecurity.

The 12-month academic program gives students, across selected high schools in British Columbia, hands-on training on evolving cyber threats and how to prevent them. The special curriculum, jointly designed by Palo Alto Networks, British Columbia’s Ministry of Education and IBM Canada, focuses on firewall installation, antivirus software, zero-day vulnerabilities, and other security skills.

Founded in 2005, Palo Alto Networks covers several segments like firewalls, cloud-monitoring and compliance, endpoint protection, and threat detection services.

Speaking about the new initiative, Dan Myers, senior manager of Palo Alto Networks Cybersecurity Academy said, “Providing these students with foundational cybersecurity knowledge and skills will give them a leg up when applying for an entry-level IT position and the opportunity to grow from there. While we can’t close the cybersecurity workforce gap overnight, we’re dedicated to helping students of all ages understand the cyber risks out there and educating them on the best ways we can all protect our way of life in the digital age.”

“IBM is committed to innovation and STEM education, and we see effective, high-quality STEM education as a key driver of the nation’s economic vitality. Public-private partnerships such as these are a testament to what can be achieved to support learning in high skill areas, such as cybersecurity. We are helping prepare the Canadian youth for new collar jobs. Nothing is more critical to our nation’s economic success,” said Krista Shibata, women in technology and STEM education lead at IBM Canada.

Recently, Palo Alto Networks extended its partnership with Google Cloud, a cloud service platform from Google, to help organizations scale cloud services and accelerate cloud adoption. The extended cooperation allows Palo Alto Networks to use the Google Cloud Platform (GCP) for providing continuous enterprise security solutions to its clients. Google stated the partnership enables Palo Alto Networks to run its Application Framework and GlobalProtect cloud service on the Google Cloud Platform.