Home Blog Page 266

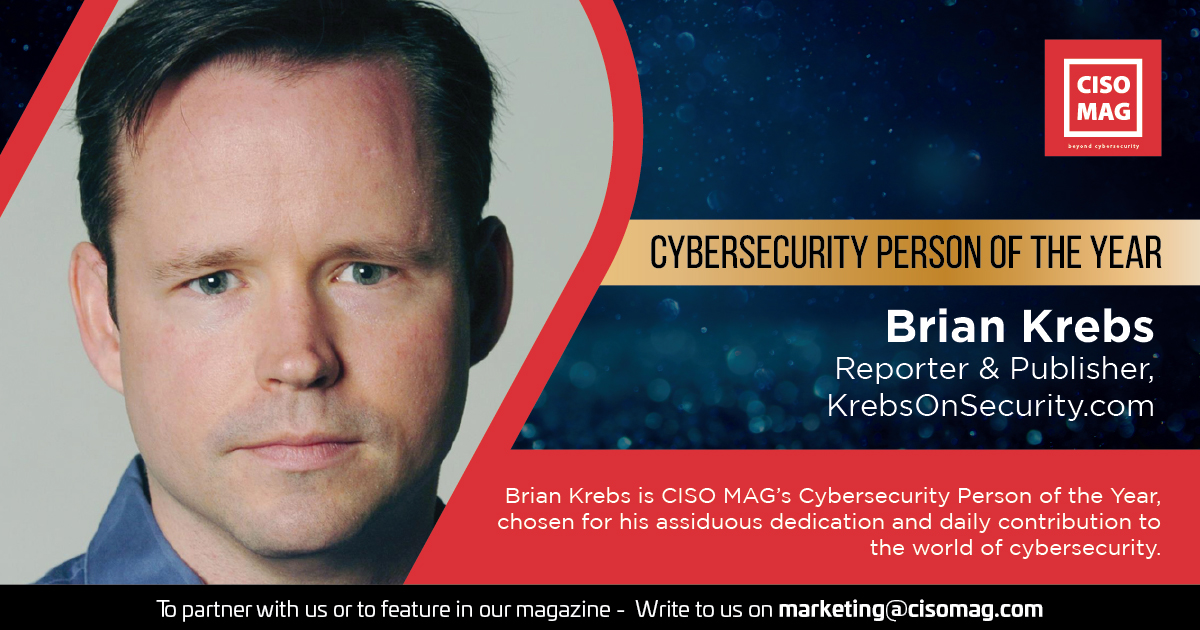
Brian Krebs is the CISO MAG Cybersecurity Person of the Year

Brian Krebs

It’s that time of the year when CISO MAG editors get together to reminisce about all the big news and events that occurred during the year. Last month, our editors created a rundown on everything that happened—the good and the bad. In the December issue, we present one quick read on the year at its entirety with a focus on what made 2019 different from past years. In addition to focusing on the most prominent attacks of the year, we also talk about the biggest fines of the year, the mega cybersecurity acquisitions of the year, the most promising startups of the year, and the best cybersecurity solutions of the year. For the first time, we named the Cybersecurity Person of the Year. It’s a person who has over the years been committed to bringing awareness into the realm of cybersecurity–to whom the information security industry is profoundly indebted.

Drumroll…

Brian Krebs is CISO MAG’s Cybersecurity Person of the Year, chosen for his assiduous dedication and daily contribution to the world of cybersecurity.

Thanks for informing us daily, Brian!

Brian Krebs is one of the most venerated cybersecurity influencers in the world. Krebs is the editor of a daily blog, KrebsOnSecurity.com, covering computer security and cybercrime. A journalist by profession, Brian worked as a reporter for The Washington Post from 1995 to 2009, authoring more than 1,300 blog posts for the Security Fix blog. He also wrote hundreds of stories for washingtonpost.com and The Washington Post newspaper, including eight front-page stories in the dead-tree edition and a Post Magazine cover piece on botnet operators.

His noteworthy reportage includes the Target Corporation breach, where 40 million credit cards of users were compromised. He was also instrumental in identifying the Ukrainian man who was behind a primary black-market site selling Target customers’ credit and debit card information. His book Spam Nation: The Inside Story of Organized Cybercrime – from Global Epidemic to Your Front Door won the PROSE Award in 2015.

In 2019, Brian Krebs’ Krebs on Security broke the news about one of the biggest data leaks. He reported about insurance giant First American Financial Corp., which leaked hundreds of millions of documents related to mortgage deals going back to 2003. The leak included digitized records of almost 885 million people, “including bank account numbers and statements, mortgage and tax records, Social Security numbers, wire transaction receipts, and drivers’ license images—were all available without authentication to anyone with a Web browser.

CISO MAG also recognizes two other persons for their tremendous contributions to cybersecurity. They are Rik Ferguson, Vice President Security Research at Trend Micro and Troy Hunt, an expert on web security and author of the data breach search website Have I Been Pwned?

Download CISO MAG December 2019 to read about the CISO MAG Editor’s choice for the best security technology, the Cybersecurity Persons of the year, and the biggest news events of the year.
Around 100 Dentist Offices Affected by Sodinokibi Ransomware

biggest data breaches in India,data breach, Aptoide Android App Admits Data Breach, Suspends Sign-Up Option Temporarily, Panasonic

Complete Technology Solutions (CTS), a Colorado-based IT services provider to oral-care practices, have reportedly been affected by a “Sodinokibi” ransomware attack.

According to security researcher Brian Krebs, attackers installed Sodinokibi on computers at more than 100 dentistry businesses that rely on CTS for IT services, including network security, data backup, and voice-over-IP phone service.

The researcher stated the attack occurred on November 25, via a compromised remote administration tool. Many of CTS’ clients are struggling to recover their data and business operations, as CTS declined to pay the US$ 700,000 ransomware demand.

According to sources, few individual dental offices have opted to pay the ransom in smaller amounts to decrypt their own data. It’s said that the dental offices received multiple ransom notes and asked to purchase multiple decryption keys in order to salvage all their data.

Many of CTS’s customers took to social media handles to post about the attack and discussed steps they’ve attempted to recover their files. “I would recommend everyone to reach out to their insurance provider,” said one dentist based in Denver. “I was told by CTS that I would have to pay the ransom to get my corrupted files back.”

Gary Salman, CEO of Black Talon Security, assisted several CTS clients in the recovery process.

“For one network we recovered, that had 50 devices in total, they had to turn in more than 20 ransom notes to fully recover. Attackers may just be hedging against the possibility that different affected practices could save money by sharing the same decryption key. In the end, the attackers are going to walk away with a lot more money than they would have gotten had [CTS] just paid the $700,000,” Salman said.

In a similar security incident, Virtual Care Provider, a technology services provider for nursing homes and acute care sites, was hit with a ransomware attack that seized access to patients’ health records.

The Milwaukee-based company reported that unknown attackers injected ransomware known as “Ryuk” inside its network systems. The company stated that hackers demanded US$ 14 million to restore access to its hijacked servers. Virtual Care Provider said around 110 nursing homes across the country are unable to access their patient records, use the Internet, pay employees, and order crucial medications.

According to the Chief Executive and owner of Virtual Care Karen Christianson, the incident had affected 80,000 computers and other facilities, including Internet service and email, access to patient records, client billing, phone systems, and payroll operations.

6 Times Data Regulators Churned Out High Penalties in 2019

By Rudra Srinivas

Data breaches and security incidents are becoming increasingly expensive. The risk of data breaches got higher after introducing the European Union’s General Data Protection Regulation (GDPR) on May 25, 2018.

The year 2019 has already seen organizations slammed with sizable fines and settlements for security incidents or misusing customers’ information. Ever since GDPR was launched, data regulators are getting more serious about companies that are not serious about consumer data protection.

According to a report from IBM, the average cost of a data breach has increased to US$ 3.92 million, which is a 1.6 percent increase in costs in 2018 and a 12 percent rise over the last five years.

Cyber-attacks, data thefts, weak security, mistakes, and cover-ups have cost these companies a huge fortune.

1. British Airways

The UK’s data protection watchdog ICO (Information Commissioner Office) fined British Airways on July 08, 2019, with £183.39 million (around US$ 230 million) after the airline failed to protect its customers’ data. The fine was related to a data breach that occurred in September 2018, exposing around 500,000 customers’ personal information.

The ICO said its investigation found the breach compromised customer details, including login, payment card, name, address, and travel booking information which is collected after being diverted to a fraudulent website. The data breach, which began in June 2018, occurred due to the poor security measures to protect customer information, ICO stated.

2. Yahoo

In one of the biggest class-action lawsuit settlements in the United States’ history, Yahoo Inc. has agreed to pay US$ 117.5 million over a series of data breaches that affected its users between 2012 and 2016. The affected users will likely get US$ 100 in compensation or two years of credit monitoring services for free.

Yahoo urged the Settlement Class Members to claim for the reimbursement. In case users already hold credit monitoring services, they can opt for cash payment, which is less than US$ 100 or more (up to US$ 358) per user, depending on how many users are claiming for the settlement, Yahoo said in a statement.

According to Yahoo, anyone who had a Yahoo account between January 1, 2012, and December 31, 2016, and is a resident of the United States or Israel is eligible for the settlement.

3. Uber

In 2016, taxi aggregator Uber had 600,000 drivers and 57 million user accounts breached. Instead of reporting the issue, the company paid the perpetrators, Glover and Mereacre, US$ 100,000 in ransom to keep the hack a secret. These actions cost the company deeply. Uber was fined US$ 148 million in 2018 for violation of state data breach notification laws.

In October 2019, the two hackers pleaded guilty for their extortion scheme to steal sensitive information of 57 million Uber passengers and drivers. According to the statement from the Federal Court, California, the hackers admitted stealing personal information from the ride-hailing service provider that was stored on Amazon Web Services from October 2016 to January 2017 and then demanded a ransom.

4. Marriott International

In July 2019, popular hospitality group Marriott International was charged with £99,200,396 (around US$ 123,705,870) fine by ICO for the data breach reported in 2018. The ICO stated that Marriott failed to protect its customers’ information, thus violating the GDPR regulations.

Marriott faced a massive data breach affecting up to 500 million guests last year. Hackers extracted people’s personal data as well as a loyalty program, payment, and reservation information. That’s not all, encrypted credit card data of 100 million customers was also stolen.

5. Facebook

Facebook is set to pay the largest fine imposed on a technology company by the Federal Trade Commission (FTC). On July 24, 2019, the social media giant was slapped with a massive US$ 5 billion fine for allegedly violating privacy practices and mishandling user data during the infamous Cambridge Analytica scandal and other privacy breaches. The FTC ordered Facebook to adopt new policies for protecting users’ data and expand these policies across Instagram and WhatsApp.

Facebook has also agreed to pay £500,000 (around US$ 645,000) penalty imposed by ICO for failing to safeguard the users’ data gathered by political data firm Cambridge Analytica.

According to the settlement deal, Facebook has agreed to drop its legal appeal against the penalty. The ICO stated that Facebook can retain some documents that the ICO disclosed during the appeal process to use for its own investigation into issues around Cambridge Analytica.

6. Equifax

In July this year, the Federal Trade Commission (FTC) and Consumer Financial Protection Bureau fined Equifax around US$ 700 million following a massive data breach in 2017 that leaked a massive amount of information of more than 143 million people in the U.S. alone.

According to the official reports, the proposed penalty could be between US$ 650 and US$ 700 million. It’s said that the final amount could vary depending on how many people file claims and their expected compensation.

On September 7, 2017, the Atlanta-based consumer credit reporting agency disclosed that its databases had been breached between May and June 2017, and hackers had gained access to company data that potentially compromised sensitive information for 143 million American consumers, including Social Security numbers, credit card numbers, and driver’s license numbers.  Equifax discovered the breach on July 29, 2017. It waited until after the close of trading nearly six weeks later to disclose the breach to consumers and Equifax’s investors, after hackers exfiltrated data for 76 days.

Rudra Srinivas is part of the editorial team at CISO MAG and writes on cybersecurity trends and news features. 

Honeypots: Best Bet for IoT Security?

Number of IoT Devices Expected to Reach 24.1 Bn in 2030: Report

Electronics manufacturer Panasonic recently described how it boosted its Internet of Things security by connecting them to internet honeypots. The company stated that it’s using two specially developed honeypot sites to lure cybercriminals into attacking its connected home appliances like fridges and other kitchen products and watch how they attempt to attack them.

What are Internet Honeypots?

A honeypot is a decoy program designed to look like a legitimate system to trap intruders who are trying to attack the system. During the process, the attackers are being stealthily observed, without the intruder’s knowledge.

However, honeypots are considered controversial. Several security pros define it as unfair entrapment tools while others see it as a useful data gathering and preventive mechanism.

Security officials at Panasonic stated that they have been using this technique to understand the IoT threat landscape and how to counter them.

In a recent presentation at Black Hat Europe in London, security researchers from Panasonic, Hikohiro Y Lin and Yuki Osawa, detailed that how they’re executing honeypots.

“We have developed a system where information is collected through the honeypot is sent to a Sandbox for automated analysis, to address our concern for having a limited number of security experts. What this system allows Panasonic to do is collect “malware targeting/exploiting Panasonic IoT devices” for quicker remediation, in addition to “popular malware” targeting a wide-range of IoT devices,” the researchers stated in a post.

Panasonic stated that it has been able to find around 179 million attack cases and nearly 25,000 malware samples, of which 4,800 were targeting IoT.

IoT devices often cake a large slice from the cake when it comes to targetted attacks. In fact, for several cybercriminals, IoT devices are the primary target. A research named Internet of Things in Underground Communities by Trend Micro detailed the rising trend for IoT attacks. It explained how online intruders exploit vulnerabilities in connected devices

According to the research, the Russian and Portuguese-speaking forums are more prominent in financially driven attacks than other cybercriminal markets. It’s said that one of the main activities of these forums are selling access to compromised devices such as webcams, routers, and printers. In order to mitigate cyber risks from the design phase itself, the researchers at Trend Micro urged the IoT manufacturers to partner with security experts.

Airtel Accepts Security Flaw, Says, “We’ve Fixed it”

Airtel

They say “Bad things come in threes.” Well, its 300 million in the case of Airtel, India’s third-largest Telecom Network provider. Airtel said that it has fixed a serious security flaw present in its mobile app’s API that allowed potential threat actors to fetch sensitive user information of any Airtel subscriber.

This security flaw was discovered by a Bengaluru-based independent security researcher named Ehraz Ahmed. He said, “The flaw existed in one of their APIs that allows you to fetch sensitive user information of any Airtel subscriber. It revealed information like first & last name, gender, email, date of birth, address, subscription information, device capability information for 4G, 3G & GPRS, network information, activation date, user type [prepaid/postpaid] and current IMEI number.”

Airtel is yet to confirm whether there was an actual data breach or not, but a spokesperson told BBC, “There was a technical issue in one of our testing APIs, which was addressed as soon as it was brought to our notice. Customer privacy is of paramount importance to us and we deploy the best of solutions to ensure the security of our digital platforms.”

In a similar finding last month Ahmed had found a security flaw in a popular caller-identification app Truecaller. This bug could have exposed sensitive user data, location, and system information to attackers. The globally available platform is popular in India with 500 million downloads and 150 million active users. According to Ahmed, the malicious script would have allowed execution without user consent.

Truecaller thanked the researcher for reporting the vulnerability and urged all the users to update with the latest version.

“We have partnered with a community of researchers and will shortly announce a bounty program where we, as a transparent and responsible organization, will also reward researchers for their contributions,” the company said in a statement.

APT Hacker Group Targets BMW and Hyundai Networks

BMW Data Breach

A notorious APT hacker group “OceanLotus” compromised the network systems of automobile giant BMW and installed a hacking tool known as “Cobalt Strike” to spy and control the systems.

According to a research report from Bayerischer Rundfunk, the attack was traced back to state-sponsored hackers from Vietnam.

Security analysts from BMW stated that they identified the hacker’s penetration into their company’s network system. It’s believed that attackers were active since March 2019.

BMW has taken down the compromised computers recently and blocked the path that was used by hackers to penetrate the network. The report also claimed the hackers behind the BMW attack also targeted the South Korean automotive manufacturer Hyundai.

Created Fake Websites

To get access to other computers, the hackers created a fake website that gave the impression of belonging to the BMW branch in Thailand, as they can monitor networks and find out which folders and files that users logged in.

Hackers Observed for Months

The security team at BMW allowed hackers to stay active with an intention to know more details like, who they were, how many systems they managed to compromise, and what kind of data they were after.

Based on sources, no sensitive information was accessed by hackers during the incident and no primary computers were compromised.

BMW declined to provide additional information on the attack.

“We have implemented structures and processes that minimize the risk of unauthorized external access to our systems and allow us to quickly detect, reconstruct, and recover in the event of an incident,” BMW said in a statement.

 In a recent security incident, security pros at Blackberry Cylance observed an unknown hacking group used the same hacking tool Cobalt Strike to trojanize aTetris game to spread malware, targeting healthcare and educational institutions for credential stealing.

Blackberry Cylance stated that threat actors are trying to distribute ransomware with a malware named “PyXie”. It’s said that PyXie, which is written in Python programming language, has been in the wild since 2018.

Buer, a New Loader Discovered in Several Malware Campaigns

BLAZINGSUN: A New Breach on Joker’s Stash Dark Web

Since the end of August 2019, researchers at Proofpoint have been tracking a new loader dubbed as ‘Buer’. It is said to use C and .NET Core programming languages for improved client and server exploitation. This downloader is sold on various dark web forums and contains a feature set like that of the Smoke Loader. Smoke Loader is known to have downloaded various banking trojans such as Ursnif and The Trick, whose main aim was to steal financial and banking credentials.

Noticeable Campaigns

  • Proofpoint researchers first observed malicious email messages on August 28. These email’s contained Microsoft Word attachments that used Microsoft Office macros to download the next stage payloads from URLs including:
  • hxxp://jf8df87sdfd.yesteryearrestorations[.]net/gate.php
  • hxxp://93345fdd.libertycolegios[.]com/gate.php

The dropped payload was named verinstere222.xls or verinstere33.exe, which was an undocumented payload back then.

  • On October 10, another instance of a malvertising campaign in Australia was discovered. It redirected to the Fallout Exploit Kit (EK) dropping the Buer loader that in turn dropped several second-stage malware payloads like KPOT stealer, Amadey, and Smoke Loader.
  • The third appearance of this loader was detected on October 21, when Proofpoint researchers observed another malicious email message campaign containing Microsoft Word attachments with macros that, if enabled, would execute Ostap. Ostap was downloading this loader from the following URL: hxxps://185.130.104[.]187/nana/kum.php?pi=18b&[redacted]

The downloaded loader further loaded a secondary loader, The Trick “ono22”.

Features of Buer Loader

The Buer loader has been marketed on the dark web by a Russian author who seems to be selling the malware cheaper than an iPhone. For a mere US$ 400, the author is providing services of setting up the software and rendering free updates and bug fixes. Let’s have a look at its features now:

  • The author emphasizes on high performance in both the client and server due to the choice of programming language. He states that the modular bot is written entirely in C and uses a control panel that uses .NET Core as its base language.
  • As per the description, the bot has a total payload of 55 to 60 kilobytes, functions as a native Windows executable and dynamic link library, runs entirely in resident memory, and is compatible with 32-bit and 64-bit Microsoft Windows operating systems.
  • The bot communicates over an HTTPS connection and can be updated remotely from the control panel after the decrypt as well as the rebuild.
  • The author also notes that the loader runs as a surrogate process of a trusted application, and functions using User level privileges.
  • Most notably, the software will not run in the CIS (former Soviet states, such as Russia).

This loader is evolving at a rapid pace and it is evident from the fact that even if the first two steps of loading are unsuccessful, Buer loader now has started executing its own process. This means it no longer depends on other payloads for the infection. Although researchers have not yet found evidence, but the authors advertise that Buer has built-in support for Docker containers that will further facilitate its proliferation on rented hosts used for malicious purposes. Buer, is a robust, geotargeting, system profiling, and anti-analysis loader deemed as the “Rising Star of the Dark Web”.

Lazarus Hacking Group Strikes Again with Fileless Malware

Apple Notarization, operational technology

Researchers discovered a new kind of “Fileless Malware” distributed by the infamous Lazarus APT Hackers Group.  According to a security researcher from K7 Labs, the hacking group was spreading malware targeting MacOS users, to create fake cryptocurrency trading applications.

The researcher stated that the hacking group was targeting several cryptocurrency trading applications by trojanising a Mac application to steal cryptocurrency.

 Malware Infection Process

According to researcher, the attackers infect a backdoor resource directory of an open-source trading application and leverage the post-install script to trigger their backdoor via a legitimate installation process. Once infected, the malware collects the Mac’s serial number and OS information and transfers this data to attackers.

“Lazarus has been targeting many cryptocurrency exchanges using malicious trading applications. Their usual method of trojanising a Mac application is quite simple. The threat actors place their backdoor and its persistence file in the resource directory of an open-source trading application, and then leverage the post-install script to trigger their backdoor. The post-install script present within the application installer package is usually meant to aid the legitimate installation process, but is abused by Lazarus to execute their backdoor,” the researcher said in a post.

The researcher also discovered a trojanized version of UnionCryptoTrader.dmg file, which is a container of the cryptocurrency trading application. It’s believed the campaign could have been active since June 2019.

Lazarus Group was involved in various cyber-attacks that were reported earlier. The group is repeatedly trying to find a way into cryptocurrency funds. In 2018, Kaspersky Lab uncovered AppleJeus, a malicious operation by Lazarus Group to intrude on cryptocurrency exchanges and applications.

According to an official report, Kaspersky Lab’s Global Research and Analysis Team (GReAT) discovered the unusual activity of attackers who penetrated the network of an Asia-based cryptocurrency exchange using trojanized trading software to steal cryptocurrencies.

Kaspersky stated the incident occurred after an employee downloaded a cryptocurrency application from a look-alike website of a company that is dedicated to crypto trading. The malicious update installs a Trojan known as Fallchill that provides hackers unlimited access to the compromised computer network system, allowing them to steal sensitive information or to deploy other viruses for exploitation.

Hacker Hacks Hacking Platform HackerOne

bounty for DarkSide Ransomware Group, Microsoft Offers $100,000 Bounty

It may sound like a tongue-twister. Bug bounty platform HackerOne recently revealed that one of its security analysts inadvertently sent a session cookie to a bug hunter on November 24 this year, which allowed the bug hunter to access the analyst’s account and company’s vulnerability reports.

The bug hunter, known as haxta4ok00 in the HackerOne community, promptly reported the error to the company, for which he/she received a reward of US$ 20,000.

The company stated that sensitive data of multiple objects were exposed in the incident. It’s said that the hacker had accessed information related to vulnerability reports like title, state, severity, and assignee.

HackerOne helps organizations find and fix the potential vulnerabilities before they can be exploited by cybercriminals.

Cut-and-Paste – the Root Cause

The issue occurred when HackerOne’s researcher cut-and-pasted a cURL with haxta4ok00 along with his session cookie details.

With these details, haxta4ok00 was able to view HackerOne’s vulnerability reports and other records that are supposed to access only by its staff members. It could potentially have exposed the vulnerabilities of many large organizations, according to HackerOne.

“When a Security Analyst fails to reproduce a potentially valid security vulnerability, they go back and forth with the hacker to better understand the report. During this dialogue, Security Analysts may include steps they’ve taken in their response to the report, including HTTP requests that they made to reproduce. In this particular case, parts of a cURL command, copied from a browser console, were not removed before posting it to the report, disclosing the session cookie,” HackerOne said in a post.

Resolution

HackerOne revoked the session cookie on November 24, 2019, two hours after it was shared.

“Revoking the session cookie rendered it useless to anyone using it. The subsequent investigation focused on affected customers, vulnerability data, intent, communication, and preventative measures, which concluded on November 26, 2019,” HackerOne concluded.

Contractor Leaks Personal Data of AT&T, T-Mobile, and Verizon Subscribers

vishing attacks

An error from a third-party contractor has led to a massive data breach where personal information of hundreds of thousands of AT&T, Verizon, and T-Mobile subscribers was exposed on unprotected public cloud servers. According to a TechCrunch report, around 261,300 documents were exposed on the server hosted by Amazon Web Services (AWS).

The leaked information included phone bills, subscriber name, address, phone numbers, call histories, bank statements, screengrabs of usernames, passwords, and PIN numbers.

The incident came into light after the penetration testing company, Fidus Information Security, discovered that a marketing agency Deardorff Communications, one of the contractors of the telecom company, [Sprint], collected the documents of Sprint’s customers and stored them on AWS buckets without proper password protection.

The bucket was only secured after Fidus Information Security notified Amazon, which then informed Jeff Deardorff, the president of Deardorff Communications.

“The contractor collected the subscriber’s data as part of a marketing effort to persuade rival company’s customers to switch to Sprint,” said Jeff Deardorff, in a media statement. “I have launched an internal investigation to determine the root cause of this issue, and we are also reviewing our policies and procedures to make sure something like this doesn’t happen again,” Deardorff added.

Both the telecom companies, AT&T and T-Mobile, have been marred by several security incidents in the recent past.

According to the United States Department of Justice (DOJ), Muhammad Fahd, a recruiter in AT&T, was arrested in Hong Kong on February 4, 2018, for committing unauthorized access. The DOJ declared that Fahd has employed several paid insiders and provided them with credentials to inject malware.

Apart from that, recently, T-Mobile’s cybersecurity team detected a malicious attack by hackers that gave them unauthorized access to customer information. The company stated that none of the customers’ financial information, social security number (SSN), and passwords were compromised.