Home Blog Page 234

Argus Partners with NXP to Strengthen Automotive Ethernet Networks

Automotive cybersecurity

Argus, an Isarel-based provider of automotive cybersecurity, partnered with automotive semiconductors provider NXP to build a new integrated solution that allows car manufacturers to protect Ethernet network communications. The Israel-based company stated that its Ethernet Intrusion Detection System (IDS) will be integrated with NXP S32G vehicle network processors that enable mobility innovations and protect in-vehicle Ethernet networks from cyberattacks to keep drivers connected and safe. Argus further added that its Ethernet IDS will also detect malicious activity at the network and application layers.

The alliance offers combined security solutions that enable car makers to comply with current guidelines and upcoming UNECE regulations on vehicle type approval with regard to cybersecurity, and ability to detect and respond to security incidents. The partnership will also see the companies co-operate on further integration of advanced, multi-layered cybersecurity solutions for the fast-growing automated mobility on-demand (AMoD) market.

Argus is known for its advanced in-vehicle solutions professional services, and an automotive security operation center (ASOC). Its security products and services help protect, detect, and respond to cyberattacks targeting any vehicle component, network, or post-production fleet.

Speaking on the new partnership, Nir Rozen, VP Product at Argus Cybersecurity, said, “With Argus Ethernet IDS integrated with the NXP S32G processor car makers can accelerate the development and deployment of advanced driver assistance systems (ADAS), modern service-oriented gateways, and other mobility innovations, with the assurance of the best in cybersecurity. Together with NXP, we are protecting some of the most critical components of a vehicle.”

“With our combined expertise, we offer automotive customers a differentiated IDS solution that can increase the security and safety of future connected vehicles,” said Brian Carlson, Director of Product Line Management for Vehicle Network Processors at NXP.

Earlier, Argus partnered with Renovo, a mobility software technology company, to incorporate Argus’ patented Intrusion Detection and Prevention System (IDPS) technology into Renovo’s AWare automated mobility operating system.
UK’s Super Cop Department Prevents £31.2 Million Worth Fraud

Infraud, DCPCU fraud police

U.K.’s specialized fraud-fighting police force, Dedicated Card and Payment Crime Unit (DCPCU) has been able to ward-off fraudsters and prevent fraud losses amounting to nearly £31.2 million (approximately US$39.4 million) in 2019. The group has been specifically vigilant towards Organized Crime Groups (OCG) targeting the financial and banking industry.

DCPCU Fraud Fighting Police Force

DCPCU is a proactive task force formed as a collaborative effort between UK Finance, the City of London Police and the Metropolitan Police together with the Home Office. Headed by the Detective Chief Inspector, the task force includes highly skilled officers from the Metropolitan and City of London police forces. DCPCU works closely with the support staff of banks and financial institutions along with private and local fraud investigators to investigate, arrest and successfully prosecute fraudsters responsible for card, cheque and payment crimes.

DCPCUs 2019 Fraud Prevention Efforts

2019 has been a great year for DCPCU particularly because it has successfully disrupted 23 OCG activities including the “Money mules” gang whose attempted fraud accounted for over £1.2 million (approximately US$1.52 million). The operators of this gang have been sentenced for seven years in prison.   Other key highlights from DCPCUs 2019 performance report are as follows:

  • Assets worth £1.65 million (approximately US$ 2.08 million) seized
  • Fraud accounting to £31.2 million (approximately US$39.4 million) successfully prevented
  • 23 Organized Crime Groups (OCGs) successfully disrupted
  • Over 1,600 social media accounts responsible for fraudulent activities removed
  • 75 fraudsters convicted post DCPCU prosecution
  • Total of 100 years in prison handed out to fraudsters

Earlier in January 2020, an East London’s Dagenham district duo, Oluwaseun Ajayi (39 years) and Inga Irbe (49 years), were convicted for committing more than 700 banks and mobile accounts frauds. The police investigation suggested that the accused placed fraudulent orders for upgraded phones from the victim’s mobile phone accounts. This fraud amount exceeded nearly £12,000 (approximately US$ 15,770). The Croydon Crown Court’s sentencing for the two accused included five and a half years of imprisonment and community service of twelve months along with 170 hours of unpaid work.

60% of Security Pros Trust Cyberthreat Detections Verified by Humans over AI

Artificial Intelligence, AI, neural, machine learning

WhiteHat Security, an application security provider for enterprises’ businesses and an independent subsidiary of NTT Ltd., stated that over half of organizations globally use artificial intelligence (AI) or machine learning in their security operations, however, 60% of them are more confident in cyberthreat detections verified by humans over AI.

In its research, “AI and Human Element Security Sentiment Study”, WhiteHat Security highlighted the need for security organizations to incorporate both AI- and human-centric offerings, especially in the application security space.

According to research findings, based on the responses of 102 professionals in the cybersecurity industry, 45% of respondents opined that their companies lack a sufficiently staffed cybersecurity team. Over 70% of respondents agreed that AI-based tools made their security teams more efficient by eliminating over 55% of everyday security operations. Incorporating AI tools into security operations decreased employees’ stress levels, according to 40% of respondents. And, 65% claim that AI tools allow them to focus on cyberattack mitigation and preventive measures.

Despite the advantages AI-based technologies offer, the majority of respondents stressed that there are skills and benefits the human element provides cybersecurity teams that AI and machine learning cannot match.

WhiteHat provides services that are required for organizations to secure the entire software lifecycle (SLC) from the development through deployment and operation. Its Application Security Platform technology solutions include Software Composition Analysis (SCA), Static Application Security Testing (SAST), and Dynamic Application Security Testing (DAST). WhiteHat was acquired by end-to-end cybersecurity solutions provider NTT Security last year.

Commenting on the survey results, Anthony Bettini, CTO at WhiteHat Security, said, “With the growing cyberthreat landscape, it is imperative for security tools and organizations to have a combination of both AI and the human element so there can be continuous risk evaluation with verified results. For all its advantages, AI is still heavily reliant on humans to be successful. Human monitoring and continuous input are required if AI software is to successfully learn and adapt. This is why the human element will never be completely eradicated from the security process.”

Microsoft Along with Global Internet and Law Enforcement Agencies Come Together to Disrupt Necurs

Microsoft and its partners across several countries went all guns blazing against the nefarious botnets called Necurs. The infamous Necurs is touted to be the world’s most prolific botnet and has infected more than nine million computers, with victims in nearly every country in the world.

According to Microsoft, the disruption will ensure the criminals behind the Necurs botnet network would no longer be able to use key elements of its infrastructure to execute cyberattacks.

The disruption of Necurs was caused by coordinated legal and technical steps by Microsoft and its partners—a result of eight years of tracking and planning. The Digital Crimes Unit of Microsoft along with other firms in the security community first observed the Necurs botnet in 2012 and witnessed it distribute several forms of malware with the most infamous one being the GameOver Zeus banking trojan. The researches also observed that, during a 58-day period in investigation, Necurs-infected computer sent a total of 3.8 million spam emails to over 40.6 million potential victims.

Believed to be operated by Russia-based cybercriminals, Necurs has been used for an array of cybercrime including fake pharmaceutical spam email, online dating scams among several others. Apart from this, the botnet is also sold in the black market as part of a botnet-for-hire service.

The disruption took place after a U.S. District Court for the Eastern District of New York issued an order enabling Microsoft to take control of Necurs infrastructure. Following which, Microsoft analyzed a technique used by Necurs to systematically generate new domains through an algorithm.

“We were then able to accurately predict over six million unique domains that would be created in the next 25 months. Microsoft reported these domains to their respective registries in countries around the world so the websites could be blocked and thus prevented from becoming part of the Necurs infrastructure. By taking control of existing websites and inhibiting the ability to register new ones, we have significantly disrupted the botnet,” Tom Burt, CVP, Customer Security & Trust, Microsoft wrote in a blog post.

“For this disruption, we are working with ISPs, domain registries, government CERTs and law enforcement in Mexico, Colombia, Taiwan, India, Japan, France, Spain, Poland and Romania, among others. Each of us has a critical role to play in protecting customers and keeping the internet safe,” Tom added.

Countering Necurs in India

The breakdown by countries for the first seven days of March 2020 showed 13.59% of the distinct infected IP addresses coming only from India. India is also home to one of the largest number of super-nodes, also known as P2P (peer-to-peer) communication channels, which is created by cybercriminals in order to prevent botnet disruption by law enforcement, network operators and researchers.

In India, the Microsoft Digital Crimes Unit partnered with the Computer Emergency Response Team (CERT-IN) and National Internet Exchange of India (NIXI) to disrupt cyberattacks led by the botnet. This effort prevented the criminals behind Necurs from registering new domains to execute attacks in the future in India.

Avast Says 72% of Mobile Malware is Due to Adware

Malware and Vulnerability Trends Report, Mobile malware threats

Avast, a provider of digital security products, revealed that Adware (advertising-supported software) is responsible for 72% of all mobile malware and the remaining 28% related to banking trojans, fake apps, lockers, and downloaders. Adware is a kind of software that hijacks mobile devices to spam the victim with unwanted ads.

Threat intelligence team from Avast stated that Android adware is a rising issue with its number increased by 38% in the past year alone. According to Avast, Adware disguises itself in the form of gaming and entertainment apps to infect the devices when a user clicks on ads. These apps appear genuine while installing, but once opened, they start spamming the user with ads (mostly with malicious content). This happens when a user downloads apps that run stealthy activities without the user’s knowledge like downloading an encrypted .dex file in the background of a device.

Avast recommended few tips to help prevent mobile adware attacks, which include:

  • Only download apps from official app stores, like Google Play, as they have security measures in place to check apps before developers upload them, or from the app’s website directly for extra assurance
  • Check app ratings of other users in the store, as it’s still important to watch out for fakes. If an app has few stars and many negative comments, something might be amiss
  • Carefully review the permissions an app requests before downloading an app; if an app requests access to data that it doesn’t need in order to function, it might be fraudulent
  • Check your banking and credit card statements to identify any unauthorized payments. Cybercriminals will select low cost subscriptions so they’re hard to spot
  • Use an antivirus solution on your phone to identify and stop any attempted attacks

Commenting on the findings, Nikolaos Chrysaidos, Head of Mobile Threat Intelligence & Security at Avast, said, “No one likes getting served with incessant ads; they’re often unwanted and can ruin our enjoyment of an app. They could also pose a threat to users as cybercriminals can use them as a backdoor to a device – whether it’s to make money from advertisers or steal your personal information. We’ve been tracking this issue for a number of years and the increased use of mobile devices is likely fueling its growth.”

Johns Joins Parsons’ Cybersecurity Leadership

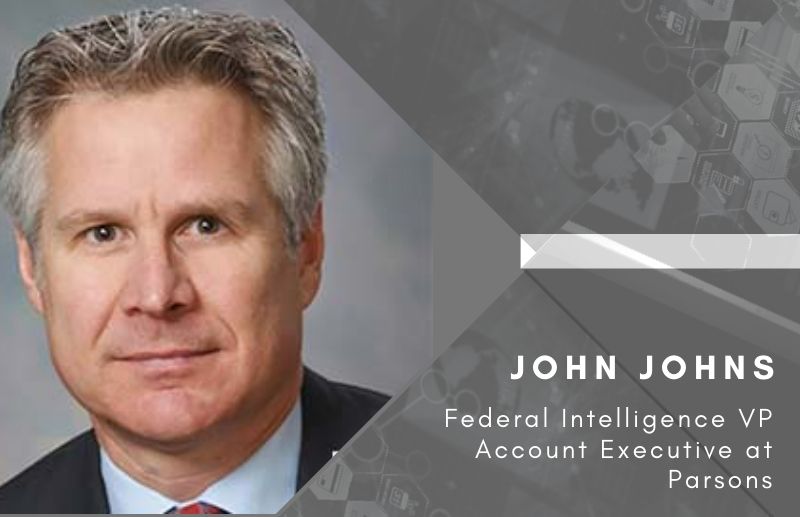
Cybersecurity technology provider Parsons Corporation named John Johns as vice president account executive of the company’s federal intelligence operating unit under the Parsons’ cyber and intelligence market.

Previously, John served as vice president and account executive in Culmen International and also held various leadership roles at KEYW, SIX3 SYSTEMS, and CACI. He holds more than 25 years of work experience in business development, pipeline development, strategic partnering, and campaign strategy development. In his new position, Johns will lead account management and customer engagement to grow Parsons’ long-standing support to the U.S. Intelligence Community.

Parsons provides next-gen technology to global defense, intelligence, and critical infrastructure markets, with capabilities across cybersecurity, missile defense, space, connected infrastructure, and smart cities.

Commenting on the new appointment, Robert Miller, senior vice president of Parsons’ cyber and intelligence market, said, “John is a proven business executive with total commitment to serving the sophisticated and dynamic technology needs of government agencies charged with national security missions. We will look to John to accelerate our support to the next level, advancing their missions with state-of-the-art technology solutions that deliver insights essential to ensuring strategic advantage.”

6.9 Million Dutch Donors Face Identity Theft Scare

identity theft

Earlier this week, BRIC, an implementing body of the ministry that manages the Dutch donor register, informed Hugo de Jonge, the Dutch Minister of Health, Welfare, and Sport, of the physical loss of two external backup hard drives (HDD). The Minister, in turn, wrote a letter to the Parliament informing them that these hard drives contained 6.9 million donor records registered from 1998 to 2010. The physical loss of these drives has sparked concerns of identity theft among registered Dutch donors.

BRIC began digitizing the donor records in 2011, wherein, the paperwork was replaced by a digital version. The backup of these records is maintained in external HDDs which are kept in a highly secured and guarded vault. BRIC recently started disposing of the paper archive of the Donor Register as part of their physical document clean-up process. The cleanup guidelines suggested to check for a corresponding digitized copy of the donor record and only then proceed with the physical destruction of the paper record.

While doing so, the agency discovered that two backup HDDs were missing from the vault. To make it worse, BRIC’s spokesperson confirmed that the drives were unencrypted. The donor details in these drives include donor details such as first and last name, gender, date of birth, the then-address, organ donation choices, identification numbers and a copy of the user’s signature.

However, BRIC has maintained that the data stored on the drives do not contain “special personal data” as mentioned under GDPR and thus the risk of identity theft is very low. The loss of drive and corresponding Dutch donor records has already been reported to the Dutch Data Protection Authority and, as of now, the investigation revealed no incidents of identity theft.

Researcher Found Malicious “Coronavirus Maps” that Infects and Steals Data

COVID-19 Cyberthreats Spike in India, Brazil, and the U.K.: Google

Cybercriminals never leave an opportunity to exploit any vulnerability or situation to prey on users online. Even, they are taking advantage of the fear and panic caused by the spread of the 2019 Novel Coronavirus (2019-nCoV).

Shai Alfasi, a security researcher at Reason Labs, discovered that threat actors are spreading malware disguised as “Coronavirus map” to steal personal information like usernames, passwords, credit card numbers, and other sensitive information that is stored in the users’ browser. Attackers use the stolen information for illegal activities like gaining access to bank accounts or selling it on the deep web.

Attacking via Malicious Coronavirus Map

Attackers designed multiple websites related to coronavirus information to prompt users to click/download an application to keep updated on the situation. The website displays a map (looks like a genuine one) representing COVID-19 spread. It generates a malicious binary file and installs it on victims’ devices.

AZORult Malware

According to Alfasi, the new malware triggers a malicious software tracked as “AZORult”, which is an information stealer first discovered in 2016. Attackers use AZORult to steal users’ browsing history, cookies, ID/passwords, cryptocurrency, and is also able to download additional malware onto infected devices. Describing AZORult, Alfasi said, “AZORult is commonly sold on Russian underground forums for the purpose of collecting sensitive data from an infected computer. There is also a variant of the AZORult that creates a new, hidden administrator account on the infected machine in order to allow Remote Desktop Protocol (RDP) connections.”

“As the coronavirus continues to spread and more apps and technologies are developed to monitor it, we will likely be seeing an increase in corona malware and corona malware variants well into the foreseeable future,” Alfasi added.

Coronavirus Propagates Emotet Malspam Campaign in Japan

An Emotet malware spam (malspam) campaign, disguised as official notifications related to coronavirus from disability welfare service providers and public health centers was observed targeting audiences in Japan including the prefectures of Osaka, Gifu, and Totori.

Analysts from IBM X-Force and Kaspersky along with infosec community experts found that Emotet operators used previously compromised account templates to target potential victims for the Emotet malspam campaign. According to IBM, the attackers seem to be geo-targeting the email content and language to inflict fear among audiences in these areas, thus, making them more likely to click on the malicious attachment.

EC-Council Hosts Certified Ethical Hacking Bootcamp To Provide State-of-the-Art Cyber Security Education for U.K. University

Certified Ethical Hacker

The two-day Certified Ethical Hacker course will teach attendees how to test for weaknesses in online security systems that could be exploited by malicious hackers. The aim is to ensure teachers at schools, colleges, and universities in the U.K. have the very latest cybersecurity skills and can pass these onto their students.

The course is being organized by EC-Council and the cybersecurity educators’ community organization CISSE UK, in partnership with Northumbria University. It will take place at Northumbria’s award-winning Computer and Information Sciences building this weekend. Northumbria has a strong reputation in the field of cybersecurity and is an academic partner of the EC-Council, as well as an accredited examination center for the Certified Ethical Hacker exam – an internationally recognized qualification. All final year students on Northumbria’s Computer Networks and Cyber Security B.Sc (Hons) degree are given the opportunity to undertake the Certified Ethical Hacker exam, receiving a separate qualification from the EC-Council alongside their degree if successful.

Dr Neil Eliot is a Senior Lecturer within Northumbria’s Department of Computer and Information Sciences and has coordinated the University’s partnership with CISSE and the EC-Council which led to this weekend’s boot camp event. A certified ethical hacker since 2014, Eliot believes giving teachers the latest cybersecurity skills is essential to ensuring students have the skills needed to stay safe in an increasingly digital world. He said, “So much of our lives are conducted online these days, and while this is often more convenient it also means our personal information is at risk from hackers.

“It is vital that we teach young people about the risks of sharing information online, how to spot a potential threat and what to do if they suspect they are being targeted. The best time to do this is while they are studying at school, college, or university, before they enter the world of employment, but this means ensuring their teachers are up to date with the latest cybersecurity developments,” Eliot further added.

Philip Blake, EC-Council Regional Director (Europe), said, “EC-Council’s Academia division strongly believes in supporting faculty, students, and Cybersecurity ecosystems across the world. Groups such as CISSE, in partnership with higher education, industry, and government have also been instrumental in influencing Cybersecurity program expansion and development. In addition to supporting CISSE (USA), EC-Council Academia is now pleased to support CISSE UK as they partner with Northumbria University to implement EC-Council’s tactical Cybersecurity program tracks.”

Dr Charles Clarke of CISSE UK said, “We are delighted to be collaborating with both Northumbria University and EC-Council, on what is a unique and valuable opportunity for academics. The cybersecurity sector evolves both rapidly and continuously, impacting the culture of how this subject is taught and experienced by students in universities. This CEH Weekend Boot Camp at Northumbria University is the first of an anticipated series of such events and is representative of a broader CISSE UK strategy to establish a culture of outstanding, innovative and state-of-the-art cybersecurity education, in the UK.”

Eliot has now applied for grant funding to carry out a survey of teachers at schools, colleges, and universities to find out the level of cybersecurity education currently being provided across the North of England. This will identify gaps in provision, raise awareness of the importance of teaching these skills, and shape the planning of future training events.

Eliot said, “The young people of today are the business owners of tomorrow and it is essential that they understand how to keep their own information, and that of their future customers and employees, safe from malicious hackers. “By understanding the current state of play when it comes to cybersecurity education in schools and colleges, we can suggest improvements and design training which will give teachers and academics the skills required.”


SentinelOne Partners with Lenovo for Enhanced ThinkShield Protection

NCSC and Microsoft Cyber Accelerator program

Endpoint protection firm SentinelOne announced a strategic partnership with Lenovo. The California-based company stated the new partnership integrates its autonomous endpoint protection platform with Lenovo’s ThinkShield security portfolio to deliver AI-powered cloud protection, real-time prevention, ActiveEDR, and IoT security.

Founded in 2013, SentinelOne provides autonomous endpoint protection services to organizations to help them prevent, detect, respond, and hunt attacks across all major vectors. The company claims that its security platform is designed to save customers time by applying AI to automatically eliminate threats in real-time for both on-premise and cloud environments.

The partnership enables SentinelOne to become a core component of Lenovo’s ThinkShield security offerings, empowering workstations, servers, cloud workloads, and IoT devices to autonomously defend themselves in real-time.

Speaking on the new partnership, Tomer Weingarten, CEO and Co-founder, SentinelOne, said, “With the leading PC market share, Lenovo is the global choice for enterprise computing and datacenter needs. They need the very best in protection and visibility as their devices are the front lines in the fight against cybercriminals. We are excited to equip Lenovo with technology to deliver a security advantage, hardening endpoints to autonomously prevent, detect, and respond to modern-day risks and threats without impacting device performance.”

“The endpoint has increasingly become the preferred vector of cyberattack; this is especially true as digital transformation continues to accelerate where and how work is done. Inherent to our strategy of ‘Smarter Technology for All’ is secure endpoint solutions. This strategic partnership between Lenovo and SentinelOne means that our enterprise customers can now take advantage of the combined power to deliver industry-leading endpoint protection that leverages true, contextual AI,” said Nima Baiati, global director and GM, Cybersecurity Solutions, Intelligent Devices Group, Lenovo.

Recently, SentinelOne raised US$200 million in Series E funding led by private equity firm Insight Partners along with participation from Tiger Global Management, Qualcomm Ventures LLC, Vista Public Strategies of Vista Equity Partners, and Third Point Ventures. The company stated the new investment will be used to accelerate the company’s next-gen endpoint, cloud, and IoT protection platforms through its autonomous AI mechanism.