The increase in remote workforce encouraged several organizations across the globe to embrace the Bring Your Own Devices (BYODs) concept. However, using personal devices for official work also brought in various kinds of data security and privacy risks, as organizations lacked visibility to secure these unmanaged BYODs. With the rise in the security issues related to BYODs, the U.K. government recently released guidance for organizations on enabling staff to use their personal devices such as smartphones, tablets, laptops, and desktop PCs to access corporate data.
Released by the National Cyber Security Centre (NCSC), the guidelines are aimed at helping organizations deploy and manage BYODs. The BYODs guidance is primarily intended for large and medium-sized organizations and companies allowing their employees to use personal devices for office work.
Per NCSC, here are some of the questions organizations need to consider:
Is BYOD right for me?
What type of BYOD deployment method is right for me?
Do I need anything else?
How do I use BYOD appropriately (and legally!)?
Security Challenges of BYOD
As companies deploy more and more BYODs to corporate networks, shadow IoT devices continue to be a growing risk factor to enterprise network security. Shadow IoT devices are internet-connected devices or sensors used inside an organization without the knowledge of the IT team in a company.
The BYOD concept brings several security challenges to organizations, including:
Ensuring personally owned devices and their owners comply with company policies and procedures
Increased support for a wide range of device types and operating systems
Protecting corporate data and infrastructure
Protecting the personal privacy of the end-user/device owner
Ensuring legal compliance and meeting contractual obligations
BYOD Risks
The NCSC recommended organizations consider the associated risks with BYODs, which include:
Easier user-initiated deliberate loss of data
Less trust in a BYOD device at the point of enrolment
Employees having access to more resources and services than required
Higher likelihood of unsupported or out of date devices
Users being less willing to report security incidents
Malicious exploitation of devices because of weak security configuration
Actions Before Deploying BYODs
The NCSC also recommended five actions that will help enterprises choose and implement the right BYOD solution, in the right way. These include:
“The security challenges of BYOD should not be played down. However, with the right technical controls and policies in place, the risks inherent with BYOD can be minimized. Organizations should be mindful of the potential impact BYOD may have on the work/life balance of their employees. A BYOD scheme requires careful design in order to ensure that it works well for employees. If the system makes life difficult, or leads to a poor work/life balance, you could end up with your employees rejecting the approved approach for BYOD. They may even find other ways to do their job using ‘shadow IT’ that are likely to increase your security risk,” the NCSC said.
For organizations of all sizes across the globe, 2020 and 2021 were undoubtedly unprecedented years in many ways. Companies were forced to adopt remote workforce, digitalizing all operations. Notably, the rise of cybercriminal activities leveraging the pandemic made organizations consider cybersecurity a top priority. Several organizations, regardless of size and industry, have increased their cybersecurity budgets to defend against new security threats.
Despite being a primary target to cyberattacks, small-to-medium businesses (SMBs) have embraced new work environments and invested in new security technologies to prevent hacker attacks, a report from Untangle revealed.
Untangle provides comprehensive network security for SMBs and distributed enterprises. In its annual SMB IT Security Report, the company stated that SMBs implemented foundational strategies to address network security issues even with limited budgets and resources. Around 80% of respondents shared that they are more secure now than last year.
Key Findings
Surveyed SMBs have increased their annual IT security budgets compared to 2020. More small businesses – those with under 25 employees – are making investments in IT. Only 28% had annual budgets of $1,000 – $5,000, compared to 35% in 2021.
50% of SMBs now have the majority of their employees working back in the office. However, 41% have permanently transitioned a quarter or more of their workers to hybrid work, keeping with the current workplace transformation trend. Because of this, 20% of SMBs have implemented some SD-WAN technology, with another 19% having plans to implement or are looking into it.
While companies have been investing more in IT security, there continue to be barriers. Employees who do not follow guidelines have become the top barrier to IT security (28%). Despite some budget increases, many organizations still struggle with budget constraints (27%) and the lack of workforce to monitor and manage security (18%).
Recognizing the need for digital transformation, 58% of SMBs have deployed more than 10% of their IT infrastructure in the cloud – a 32% increase from 2020.
SMBs realize that they are also targets of cyberattacks and look at IT security from a problem/solution standpoint. 64% name breaches as their top security concern, it is understandable that most companies recognize firewalls (73%) and antivirus/anti-malware protection (62%) as top IT security solutions.
The findings are based on the responses of more than 740 SMBs surveyed.
“With a changing workplace landscape, and a continued rise in cyberattacks, SMBs have shifted their mindset from ‘it can’t happen to me’ to taking security threats seriously. To that end, they have increased their focus on IT Security, they have stronger networks than a year ago, and they have plans for further attack prevention in the future. There’s a definite trend towards putting more IT in the cloud and following a multi-layered security approach. By making this data available, we’re giving SMBs the ability to learn from each other, see what other similar businesses are concerned about and see how other SMBs are adapting,” said Scott Devens, CEO at Untangle.
A torrent link to a 125GB file with source code and business data of the video streaming platform Twitch has been leaked and published on the 4chan discussion board.
An unknown hacker, who premeditated the attack, permeated the streaming platform with intentions to disrupt the services and cause reputational harm.
The leaked link contains items like Git repository history, subscription rates, payments made to creators, and an unreleased game distribution service from the parent company Amazon.
We can confirm a breach has taken place. Our teams are working with urgency to understand the extent of this. We will update the community as soon as additional information is available. Thank you for bearing with us.
We can confirm a breach has taken place. Our teams are working with urgency to understand the extent of this. We will update the community as soon as additional information is available. Thank you for bearing with us.
Reports revealed that the hack did not include Twitch user information like login details or personal information, the target was the creator community whose pay-out details were made public.
The leak includes:
Entirety of Twitch, with its Git commit history going all the way back to early beginnings
Payments for the top Twitch creators
Every property that Twitch owns, including IGDB and CurseForge
Mobile, desktop, and video game console Twitch clients
Proprietary SDKs and internal AWS services used by Twitch
Though there has been no evidence of user data being abused or leaked, as a preventive measure, all Twitch account users are advised to activate two-factor authentication and change their passwords with immediate effect.
In response, Twitch on its blog shared an update on the incident, “Out of an abundance of caution, we have reset all stream keys. You can get your new stream key here: https://dashboard.twitch.tv/settings/stream.”
Social media platforms and streaming platforms are a source of entertainment, communication, and income to billions of users around the globe. Any kind of disruption has huge ramifications on the service provider and the user community. The recent Facebook outage is an example of the fragility of the virtual world. Sponsored attacks, hate attacks, technical vulnerabilities, and cyber espionage, to name a few, are variables that need to be treated with precaution and a well-thought incidence response approach.
With the volume of attacks on enterprises increasing by the day, it is no longer sufficient to do occasional or manual penetration testing. Organizations usually test “some” of their assets “some of the time,” whereas hackers are attacking “all of the assets” all of the time. Today, it’s quite common for enterprises to be attacked thousands or even millions of times a day. Red Teaming and Blue Teaming exercises, and frequent audits help check the risk profile of an organization. However, new techniques like Continuous Automated Red Teaming (CART) and Attack Surface Management (ASM) have proven to be more effective in blocking attacks. A Bangalore and Boston-based startup named FireCompass, which was part of the NetApp Excellerator Cohort 8, is helping organizations with continuous testing. FireCompass is included in Gartner’s Hype Cycle for Security Operations, 2021. Apart from Autonomous Penetration Testing and Red Teaming, FireCompass is also mentioned in the EASM market within the Hype Cycle report. FireCompass also received similar recognitions from IDC and RSA.
By Brian Pereira, Editor-in-Chief, CISO MAG
FireCompass was founded in 2019, and its offices are located in Bengaluru, Boston, and New York. Its co-founders are Bikash Barai, Priyanka Aash, and Paul Dibello. They have yet to publicly announce their recent funding series.
The Indian co-founders met at IIT Kharagpur (as students) and their idea took root there, with the launch of their first venture. Bikash Barai, Co-founder of FireCompass spoke to CISO MAG and revealed how the company was founded, and its journey through the years.
Automating Ethical Hacking
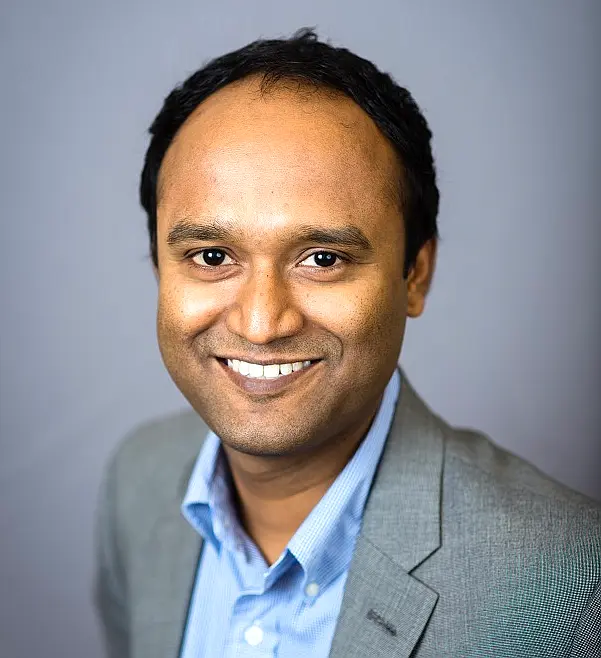
Bikash Barai, Co-founder of FireCompass
“In those days, hacking was about people writing scripts, and it was more of a manual process. Few people were into hacking, so this activity was confined to small groups,” said an amused Barai. “And we launched a company with the vision to automate ethical hacking. After we built this automated ethical hacking product, we began receiving awards from Intel, UC Berkeley, Homeland Security, U.S. Navy, etc. So, we got a lot of recognition. But we faced a challenge; we noticed that not too many people were buying our product. We realized that it was much ahead of the times in terms of automating ethical hacking. And this was two decades ago.”
The irony was that the product was receiving many awards, but there were few customers for it. So, the co-founders reached out to the alumni for advice. The response they received gave them a business idea.
“An alumni member said, I would love to buy this product, but I don’t have anyone to run it for me,” said Barai. “So, we thought, why not we run it for you. Instead of giving away the product, we can host it and run the product for our customers. And that’s how it became a SaaS offering. In fact, we were one of the first SaaS companies from India.”
That move paid off, and the response improved. The company raised a round of funding from IDG Ventures. It grew steadily soon after and bagged 100 global customers. Cigital then acquired it. The co-founders continued to run the business, which continued to grow. Barai informed us that 18 out of the top 20 U.S. banks were using its products and services. Eventually, Cigital was acquired by Synopsis. Their product became the engine for Synopsis’ cloud-based testing. And that was the first innings for FireCompass and its co-founders.
The Next Phase
After spending two years at Synopsis, they were again bitten by the entrepreneurial bug and started thinking about their next product. What was the next problem to solve?
“We noticed something very interesting, and very strange. We saw a top financial services company getting breached because they had an open database without any password. And we were very intrigued because we knew that this particular company is highly mature. They have the best tools and the best folks working for them. We wondered why they missed that. Moreover, many other such companies were getting breached. We noticed the same pattern – they were getting breached because of some very simple stuff. And once we dived deeper, we noticed that this particular database that they were using, which got compromised, was made online by the marketing team, without the knowledge of the central IT.”
Well, doesn’t this problem sound familiar? They call it shadow IT. Business units helping themselves to cloud services or creating their own products without the approval of the IT team. That’s a recipe for a security disaster.
“This new problem was not there a decade ago (before the cloud era). And you have to blame it on rapid cloud adoption, digital transformation, distributed teams, and agile teams who have got this autonomy to create things on their own. Ten years ago (before cloud), anything that had to go online had to go through IT; you did not get access to a public IP easily. But today, anybody can spin up a new asset (virtual machine), there can be new API integrations, and many new applications getting created,” said Barai.
This was clearly a problem to be addressed, and an opportunity for Barai and his company. The second problem was the limitation of the first-generation testing tools.
First generations tools or Testing 1.0 Tools could only test known systems. One had to input the IP addresses or the application URLs to test assets. So, in plain speak, these tools can’t test what they can’t see. If you do not have complete visibility of all your assets, you can’t test them.
And then there was another problem with testing, or rather, the shoddy manner in which organizations were testing their assets.
The Need for Continuous Testing
“Red teaming or penetration testing exercises are done intermittently, a few times a year. And not all the assets were tested. So, organizations are testing some of the assets some of the time, whereas hackers, the ransomware guys, the nation state actors — they’re attacking all the assets all of the time,” said Barai.
To add to that, there is inadequate cybersecurity talent in the industry. Organizations cannot scale up their testing or do continuous testing just by hiring more people.
“We believe Testing 2.0 is the future of testing, where we are continuously discovering all our assets. And we are continuously testing all our assets. So, testing has to move from that point in time to continuous. Continuous discovery of assets and continuous testing has to be automated. And it has to be continuous,” said Barai.
And it is with that vision that they founded FireCompass.
How Continuous Testing Guards Against Attacks
FireCompass offers solutions for Continuous Automated Red Teaming (CART), External Attack Surface Management (EASM) & Ransomware Attack Surface Testing (RAST). It enables organizations to map out their digital attack surface, including shadow IT blind spots, by continuously discovering, indexing, and monitoring the web. The platform then automatically launches safe multi-stage attacks, mimicking a real attacker, to help identify attack paths before hackers do, continuously and proactively providing security. And that’s how continuous testing makes an organization more secure.
The Attack & Recon Platform of FireCompass continuously indexes and monitors the deep, dark and surface webs using nation-state grade reconnaissance techniques. The platform automatically discovers an organization’s external attack surface and launches multi-stage safe attacks, mimicking a real attacker, to help identify and prioritize vulnerabilities that are most likely to be attacked.
“We first go and index the entire internet, and we index the deep dark surface web, collect all that data and put it into a big data platform. And then, we analyze that data automatically using various algorithms. From absolutely zero knowledge, we build the hackers’ view of the attack surface or the map of the attack surface of all these organizations, and we do it on a near real-time basis,” informed Barai.
FireCompass is continuously monitoring its customers’ assets and discovering their attack surface. They look for new assets that are going online, such as databases or VMs, new open ports, new APIs, etc.
“We mimic various threat actors and do a mock ransomware attack or other types of attacks on an organization. This is a red teaming and pen test exercise. Finally, we give real-time alerts,” said Barai.
So, this goes much beyond offering reports, as we saw in first-generation testing. This is really the future of testing.
NetApp Excellerator Program
NetApp, a global cloud-led, data-centric software company, announced the graduation of its eighth cohort of the flagship startup accelerator program, NetApp Excellerator, on July 23. The eight business-to-business (B2B) tech startups, which all share a focus on deep tech, including artificial intelligence (AI), machine learning (ML), cloud, and data, graduated via a virtual demo day event yesterday.
Since its inception in 2017, the award-winning NetApp Excellerator program has received over 1,700 applications.
FireCompass was one of the eight startups in the eight cohort. Speaking about his experience in the program, Barai said, “The global exposure that you can get and the access to such great minds and their knowledge within NetApp, is very special. The knowledge that you can gain from the experts at NetApp is immense. The team has been very supportive and helps you come out of the program as a better & more efficient version of you. One of the key highlights of the program that we were personally excited about was the joint GTM opportunity along with NetApp. This program introduces us to their experts globally in NetApp and getting their help to create a strong combined GTM is very exciting for us. Also, the paid proof of concept, which was an integral part of the program, helped in fine-tuning the offerings.”
The NetApp Excellerator program now moves forward with its ninth cohort.
About the Author
Brian Pereira is the Editor-in-Chief of CISO MAG. He has been writing on business technology concepts for the past 27 years and has achieved basic certifications in cloud computing (IBM) and cybersecurity (EC-Council).
As the world celebrates Cybersecurity Awareness Month, Google announced new security precautions to make users’ sign-in process more secure. The search engine unveiled its plan to auto-enroll 150 million Google users in a two-step verification (2SV) process and it requires two million YouTube creators to turn it on by the end of 2021.
Google claims that it verifies the security of one billion passwords to protect user accounts from unauthorized intrusions. In addition to having strong passwords, Google encourages users to have a second form of authentication to reduce the chance of an attacker gaining access to an account. Two-step verification, also known as two-factor authentication (2FA), is a reliable way to prevent unauthorized access to accounts and networks. The 2SV process combines both “something you know” (like a password) and “something you have” (like your phone or a security key) for better authentication security.
“2SV has been core to Google’s own security practices and today we make it seamless for our users with a Google prompt, which requires a simple tap on your mobile device to prove it’s really you trying to sign in. And because we know the best way to keep our users safe is to turn on our security protections by default, we have started to automatically configure our users’ accounts into a more secure state,” Google said.
Rolling Out 2SV
Currently, Google is auto-enrolling accounts with proper backup mechanisms to make a seamless transition to 2SV. Users can check whether their account has the right settings to use 2SV at Security Checkup. Google is also advancing the current 2SV options to make them suitable for everyone. The company is working on technologies that provide a convenient, secure authentication experience and reduce the reliance on passwords in the future.
Google’s Sign-In Advancements
Google introduced multiple forms of authentication to provide the highest level of sign-in security to users. The company launched Security Keys — an authentication procedure that requires the user to tap a key during suspicious sign-in attempts.
The company also launched One Tap and Google Identity Services, which uses secure tokens, rather than passwords, to sign users into partner websites and applications.
“These new services represent the future of authentication and protect against vulnerabilities like click-jacking, pixel tracking, and other web and app-based threats. Ultimately, we want all of our users to have an easy, seamless sign-in experience that includes the best security protections across all of their devices and accounts,” Google added.
The attack vector of Russian state-sponsored advanced persistent threat (APT) attackers is extended across various countries. Multiple cybercriminal groups from Russia have targeted several international critical agencies across the globe. But surprisingly, security researchers from Positive Technologies uncovered a new APT group targeting the fuel, energy, and aviation industries in Russia. Tracked as ChamelGang, the threat actor group also targeted critical agencies in other countries, including the U.S., India, Nepal, Taiwan, and Japan.
ChamelGang Phishing Attacks
ChamelGang was found using phishing domains and features of operating systems to disguise their malicious activities. The attackers have registered various phishing domains impersonating popular brands, including Microsoft, TrendMicro, McAfee, IBM, and Google. The researchers found different phishing domains like newtrendmicro.com, centralgoogle.com, microsoft-support.net, cdn-chrome.com, and mcafee-upgrade.com.
Exploiting Vulnerabilities
Researchers analyzed two recent cyberattacks by ChamelGang. In one attack, ChamelGang was found exploiting vulnerability CVE-2017-12149 to compromise a web application on the open-source JBoss Application Server platform. The attackers were able to execute commands on the node remotely and obtained the dictionary password of the local administrator on one of the servers. The attackers remained unnoticed in the corporate network for three months and compromised critical servers and nodes in different segments.
In another incident, ChamelGang exploited multiple ProxyShell vulnerabilities (CVE-2021-34473, CVE-2021-34523, CVE-2021-31207) in Microsoft Exchange. The attackers reportedly gained access to the corporate mail servers using a backdoor that most antivirus tools had not detected during the attack.
Using New Malware Variants
In most attacks, ChamelGang leveraged new malware variants such as ProxyT, BeaconLoader, and the DoorMe backdoor to hide its identity and complicate its detection. However, the group also used better-known malware variants such as FRP, Cobalt Strike Beacon, and Tiny shell.
Commenting on the new malware campaign, Denis Kuvshinov, Head of Threat Analysis at Positive Technologies, said, “Targeting the fuel and energy complex and aviation industry in Russia isn’t unique — this sector is one of the three most frequently attacked. However, the consequences are serious. Most often, such attacks lead to financial or data loss — in 84% of all cases last year, the attacks were specifically created to steal data, and that causes major financial and reputational damage. Also, industrial companies often can’t detect a targeted cyberattack on their own. But in practice, attackers can penetrate the corporate network of an industrial enterprise more than 90% of the time, and almost every such invasion leads to complete loss of control over the infrastructure. More than half of these attacks lead to the theft of data on company partners and employees, mail correspondence, and internal documentation.”
The spread of mobile malware has become rampant in the cyberthreat landscape. More threat actor groups are leveraging mobile malware to infect handsets and to compromise personal data. Security researchers from Proofpoint recently uncovered a new mobile malware, distributed via SMS, targeting Android users in the U.S. and Canada. Tracked as TangleBot, the malware is designed to infect Android devices and steal sensitive information stored on them. The researchers stated the TangleBot campaign leveraged COVID-19-themed phishing lures to trick users into installing malware on their devices.
TangleBot via Phishing SMS
Threat actors distributed TangleBot malware via multiple phishing SMS related to COVID-19 vaccine updates or a potential power outage. Attackers placed malicious URLs within the text messages, which, when clicked, redirect the victims to hacker-operated sources to install malware.
The phishing messages read:
New regulations about COVID-19 in your region. Read here: https//covid19*****
A power outage will occur in your area. More info here: https://hydro-ca.link**
“Unsuspecting users have presented a series of dialogue boxes requesting acceptance of the permissions and installation from unknown sources. Proofpoint analysts counted no less than nine dialogue boxes that users must click prior to the full installation of the malware. While this may seem like a lot, the lesson learned from the FluBot outbreak over the summer is that users tend to disregard the multiple warnings and permissions and still download and install software from unknown sources,” Proofpoint said.
After infecting the victims’ devices with TangleBot, attackers can
Make and block phone calls
Send, obtain, and process text messages
Record the camera, screen, or microphone audio or stream them directly to the attacker
Place overlay screens on the device covering legitimate apps and screens
Implement other device observation capabilities
Risks Involved
In addition to compromising users’ personal and banking details, TangleBot also leverages the text messaging service on the victim’s device to spread the malware throughout the mobile network. TangleBot can also steal private data using the camera and microphone app on the targeted device to spy on the victim.
Mitigation
Security experts from Proofpoint recommended mobile users to be vigilant while attending SMS warning messages and follow certain security practices, including:
Be on the lookout for suspicious text messages. Criminals are increasingly using mobile messaging and SMS phishing as an attack vector.
Carefully consider before providing your mobile phone number to an enterprise or other commercial entity.
If you receive a message from any enterprise, including some sort of warning or package delivery notification that contains a web link, use your device’s browser to access the enterprise’s or service’s website directly.
Do not use the web link provided in the text message. Do this as well for any offer codes you receive by entering them directly into the enterprise’s or service’s website from your browser.
Don’t respond to any unsolicited enterprise or commercial messages from a vendor or enterprise you don’t recognize. Doing so will often confirm that you’re a “real person.”
Don’t install software on your mobile device outside a certified app store from the vendor or Mobile Network Operator.
Be careful when downloading and installing new software to your mobile device and read install prompts closely, looking for information regarding rights and privileges that the app may request.
“Harvesting personal information and credentials in this manner is extremely troublesome for mobile users because there is a growing market on the dark web for detailed personal and account data. Even if the user discovers the TangleBot malware installed on their device and can remove it, the attacker may not use the stolen information for some period, rendering the victim oblivious of the theft,” Proofpoint added.
Social media platforms are ingrained into the lives of billions of people across the globe and the unavailability of any one of them brings their life to a grinding halt. This is what billions of users of Facebook and its products like WhatsApp, Messenger, and Instagram experienced on Monday, October 4, when their pages displayed an error message. The Facebook systems were down, and all their services and apps were unavailable for over five hours.
One was not sure about the reason behind the outage, and with cyberattacks being the order of the day, there was high speculation of a possible cyberattack responsible for disrupting the services.
Competing platforms like Twitter, Snapchat, Telegram witnessed a traffic surge with people seeking clarification, poking fun, and sharing updates on the outage.
Facebook itself had to resort to tweeting to reach out to its user base and update on the unavailability of the service.
We’re aware that some people are having trouble accessing our apps and products. We’re working to get things back to normal as quickly as possible, and we apologize for any inconvenience.
Facebook soon came up with an apology and an update on the technical reason behind the outage. The company said the problem was due to faulty configuration changes made to Facebook routers. These are the routers that coordinate the network traffic between their data centers. The routers could not communicate and hence caused the services to halt. In technical terms, this concerns the Border Gateway Protocol (BGP).
What is BGP?
Border Gateway Protocol is a standardized exterior gateway protocol designed to exchange routing and reachability information among autonomous systems (AS) on the Internet. BGP is classified as a path-vector routing protocol, and it makes routing decisions based on paths, network policies, or rulesets configured by a network administrator.
In plain English, BGP routes information between networks across the Internet. BGP interconnects various networks and facilitates communication between networks and the rest of the Internet.
Santosh Janardhan, VP Infrastructure, Facebook, shared on his page, “Our services are now back online and we’re actively working to fully return them to regular operations. We want to make clear that there was no malicious activity behind this outage — its root cause was a faulty configuration change on our end. We also have no evidence that user data was compromised as a result of this downtime.
We’ve been working as hard as we can to restore access, and our systems are now back up and running. The underlying cause of this outage also impacted many of the internal tools and systems we use in our day-to-day operations, complicating our attempts to quickly diagnose and resolve the problem.”
Industry experts and sources are voicing it as a DNS issue where BGP routes (or maps) have vanished.
Cloudflare, an American web infrastructure and website security company, in its blog described it as a BGP problem.
From trusted source: Person on FB recovery effort said the outage was from a routine BGP update gone wrong. But the update blocked remote users from reverting changes, and people with physical access didn’t have network/logical access. So blocked at both ends from reversing it.
“During one of these routine maintenance jobs, a command was issued with the intention to assess the availability of global backbone capacity, which unintentionally took down all the connections in our backbone network, effectively disconnecting Facebook data centers globally. Our systems are designed to audit commands like these to prevent mistakes like this, but a bug in that audit tool prevented it from properly stopping the command,” Facebook shared.
There has been an internal and an external view of the reason behind the outage and this instance leads to numerous other issues related to security and vulnerability.
Per Forrester Senior Analyst, Alla Valente, Security & Risk (Risk Management), “In Facebook’s quest to integrate its products and underlying technical infrastructure into a single platform is the concentration risk it creates for the company, where a single risk event that produces a cascading effect – in this case, the inability of their machines to talk to one another brought the company to a standstill. Concentration risk is one of the top systemic risks for 2021 that Forrester identified early this year. And Facebook’s size, market share, and ubiquity make it a system into itself. If the company doesn’t get better at managing its risks across the organization, it stands to lose its tight hold it’s been struggling for years to maintain.”
While IT leaders believe they have strong security practices in place, their continual search for additional network security capabilities suggests that this confidence may be tentative, according to new research from Forward Networks, a provider of network assurance and intent-based verification solutions. Data from a commissioned survey conducted by IDG on behalf of Forward Networks, in July 2021, shows that 70% of IT leaders strongly agree that their network architecture follows a zero-trust approach, compared to just 53% of IT managers who feel the same.
The disconnect between executives and front-line IT managers was also apparent in responses related to network security initiatives and overall security health. For example, while 59% of executives said their organizations were building or already employing zero-trust architectures, just 39% of IT managers said the same. In addition, more than half (58%) of executive respondents rated their overall network security as ahead of the curve compared to their competitors, while another third (37%) said it was on par with others. At the same time, only 48% of managers rated their security ahead of competitors, while nearly half (47%) rated it on par.
“The disconnect between the perceptions of security executives and practitioners highlights the lack of visibility into the network and security policy adherence,” said Chiara Regale, Vice President, Product Management, Forward Networks. “Without a single source of network truth, practitioners and executives are forced to make inferences. Having the ability to prove compliance and easily visualize security policies in action can eliminate the disconnect and ensure that the bulk of engineering effort is directed toward proactively improving the network security posture instead of fighting fires or clarifying confusing data.”
Network Security Landscape: A Mixture of Confidence and Challenges
Despite their high confidence levels, IT decision makers report widespread challenges when ensuring that their network is secure.
81% struggle to identify the depth of a breach
69% are unable to quickly identify when something is out of compliance
71% cited the inability to obtain endpoint-to-endpoint connectivity analysis
68% indicated knowing what devices are in the network and its topology is challenging
Survey respondents also said they are seeking to improve multiple areas of network security management for greater efficiency.
88% want real-time monitoring capabilities
85% are seeking diligent compliance with all security protocols
73% want validation that their network architecture follows a zero-trust approach
85% are seeking improvement in network-breach response times
“In a perfect world, IT could spend all of its attention coming up with innovative ways to stay ahead of technology’s evolution while also making sure that their organization has the optimal IT and network infrastructure to support the business,” added Regale. “But this is not the world we live in. IT leaders spend a lot of time putting out fires related to increasingly sophisticated cyberattacks, and the only way to minimize the risks associated with these breaches is to have full visibility across the entire IT infrastructure.”
More information about the research is available here.
Popular cryptocurrency exchange Coinbase admitted that unknown intruders bypassed its multi-factor authentication (MFA) mechanism to steal crypto funds from over 6,000 users.
“Unfortunately, between March and May 20, 2021, you were a victim of a third-party campaign to gain unauthorized access to the accounts of Coinbase customers and move customer funds off the Coinbase platform. At least 6,000 Coinbase customers had funds removed from their accounts, including you,” Coinbase said in an official notice sent to its customers.
Vulnerability in MFA Feature
Threat actors reportedly exploited a bug in Coinbase’s SMS MFA feature to compromise user accounts and pilfer cryptocurrency. The flaw reportedly allowed hackers to receive the victims’ 2FA tokens via SMS. Third parties require prior knowledge of the email address, password, phone number associated with the Coinbase account, as well as access to the customer’s email account. While it’s still unknown how the hackers obtained the user credentials, Coinbase stated that attackers could have leveraged phishing or social engineering techniques to trick victims into unknowingly disclosing login credentials.
“We have not found any evidence that these third parties obtained this information from Coinbase itself. Even with the information described above, additional authentication is required to access your Coinbase account. However, in this incident, for customers who use SMS texts for two-factor authentication, the third-party took advantage of a flaw in Coinbase’s SMS Account Recovery process to receive an SMS two-factor authentication token and gain access to your account,” Coinbase added.
Information Exposed
The intruders who have accessed Coinbase accounts can view sensitive user information such as full name, email address, home address, date of birth, IP addresses for account activity, transaction history, account holdings, and balance. They may also alter users’ account details like email, phone number, or other information associated with their account to transfer funds illicitly. Coinbase clarified that it is working to restore any changes made by attackers to customer accounts.
Mitigation
Coinbase immediately updated its SMS Account Recovery protocols to prevent further bypassing of the authentication procedures. The company also announced that it deposited funds into the affected user accounts along with free credit monitoring services. While the threat actors behind the security incident are unknown, Coinbase stated it’s closely working with law enforcement authorities to investigate the incident.
Meanwhile, the company urged its customers to update their account login credentials and use a robust authentication procedure such as a time-based, one-time password (TOTP) or a hardware security key.
Ensuring that you get the best experience is our only purpose for using cookies. If you wish to continue, please accept. You are welcome to provide a controlled consent by visiting the cookie settings. For any further queries or information, please see our privacy policy.
This website uses cookies to improve your experience while you navigate through the website. Out of these, the cookies that are categorized as necessary are stored on your browser as they are essential for the working of basic functionalities of the website. We also use third-party cookies that help us analyze and understand how you use this website. These cookies will be stored in your browser only with your consent. You also have the option to opt-out of these cookies. But opting out of some of these cookies may affect your browsing experience.
Necessary cookies are absolutely essential for the website to function properly. These cookies ensure basic functionalities and security features of the website, anonymously.
Cookie
Duration
Description
cookielawinfo-checkbox-analytics
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Analytics".
cookielawinfo-checkbox-functional
11 months
The cookie is set by GDPR cookie consent to record the user consent for the cookies in the category "Functional".
cookielawinfo-checkbox-necessary
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookies is used to store the user consent for the cookies in the category "Necessary".
cookielawinfo-checkbox-others
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Other.
cookielawinfo-checkbox-performance
11 months
This cookie is set by GDPR Cookie Consent plugin. The cookie is used to store the user consent for the cookies in the category "Performance".
viewed_cookie_policy
11 months
The cookie is set by the GDPR Cookie Consent plugin and is used to store whether or not user has consented to the use of cookies. It does not store any personal data.
Functional cookies help to perform certain functionalities like sharing the content of the website on social media platforms, collect feedbacks, and other third-party features.
Performance cookies are used to understand and analyze the key performance indexes of the website which helps in delivering a better user experience for the visitors.
Analytical cookies are used to understand how visitors interact with the website. These cookies help provide information on metrics the number of visitors, bounce rate, traffic source, etc.
Advertisement cookies are used to provide visitors with relevant ads and marketing campaigns. These cookies track visitors across websites and collect information to provide customized ads.

 Brian Pereira

 Per Forrester Senior Analyst, Alla Valente, Security & Risk (Risk Management), “In Facebook’s quest to integrate its products and underlying technical infrastructure into a single platform is the concentration risk it creates for the company, where a single risk event that produces a cascading effect – in this case, the inability of their machines to talk to one another brought the company to a standstill. Concentration risk is one of the top systemic risks for 2021 that Forrester identified early this year. And Facebook’s size, market share, and ubiquity make it a system into itself. If the company doesn’t get better at managing its risks across the organization, it stands to lose its tight hold it’s been struggling for years to maintain.”