Home Blog Page 367

Infosec Superwoman: Preeti Palanisamy

Preeti Palanisamy

By Renee Small

When Preeti Palanisamy was offered a position in Information Security, she turned it down. Then she learned how to hack and decided to go for the Information Security position – a move which led her to the deputy position she holds today.

“I’m the first generation educated person in my entire family,” Preeti remarks. Originally from India, Preeti got a degree in Computer Science and was doing coding when she was offered the position in Information Security. Although she initially turned it down, the offer piqued her interest in how to hack into a friend’s account as a prank, and as she explored hacking she became more interested in information security – so much so that she decided to reapply for the position and was accepted.

When first emigrating from India to the U.K. and then to the U.S., she experienced all of the struggles associated with being an immigrant and starting a new life. This included 20-hour days in information security. “I started from the ground up,” she remarks of her experience.

“I would not do something that I’m not passionate about,” Preeti says of why she would take on a challenge. She also notes that her job entails protecting not only the data but also the people behind the data. “I have a younger sister. Ever since I was a child, I was protecting her. Just the fact about protecting somebody, like my family, was always what I will love to do,” she enthuses.

One of the challenges, Preeti notes, that she faces when bringing more women into security is that women go over the details of a job description, “line by line”; and if a woman sees a line which details a requirement she doesn’t have, women will tend to not apply. “I don’t try to find women through just people who apply through resumes,” she remarks. “Most of the times I find these people in conferences or at hackathons.”

Preeti supports internship programs. “The amount of things that change on a daily basis is going to be so vast that its automatically going to interest you,” she says of these interns. An intern’s level of enthusiasm is also a good indicator for her, as Preeti prioritizes enthusiasm over knowledge where hiring at that level is concerned.

“It’s important to also train the people who are looking for talent as well,” Preeti also notes, where the hiring side of the equation is concerned.

“I feel it is very important to find the right kind of boss,” Preeti remarks, adding that she would always choose the person she deals with over a position, even if the latter paid more. “A lot of what I am today [is] because of him,” Preeti adds, remarking on her present boss, Keith O’Sullivan.

Renee Small is the CEO of Cyber Human Capital, a human resources business partner in the field of cyber security, and author of the book, Magnetic Hiring: Your Company’s Secret Weapon to Attracting Top Cyber Security Talent.


Amid protests and ambiguity, Vietnam announces new cyber law

Vietnam government

The Vietnam government has adopted a new Cybersecurity Law at the fifth session of the 14th National Assembly. The law aims to remediate the shortcomings and loopholes in Vietnam’s legal corridors and ensure a secure and safe cyberspace.

The Law which will take effect on January 1, 2019, will focus on social media usage, data localization, cybersecurity audit of information systems of agencies and organizations, handling illegal content, and protection of children.

According to the new law, social media users will have to abide by the Constitution and legal regulations while voicing their opinion and discontent on the platform. According to the law’s Article 15, “information on cyberspace classified as illegal includes anti-state information; information that excites violent disturbance, undermines security and deranges public order; information that causes defamation and slander; information that violates economic management order; and false information that causes public panics, damages socio-economic activities, hampers state agencies’ activities and on-duty persons, and violates rights and benefits of other organizations and individuals.”

The specialized force for cybersecurity of the Ministry of Public Security (MPS) can carry out an audit of information systems that are not in the “List of Information Systems Critical to National Security” in the following circumstances: There is an act violating the laws on cybersecurity that prejudice national security, or causes serious harm to social order and safety; or there is a request from the information system owner.

The Law also addresses the protection of human rights and civil rights, as well as protection of secrets of businesses, individuals and families. It also mandates domestic and foreign telecommunications service providers to keep personal information and accounts of users secured.

“The new law’s introduction will cause certain difficulties for online service providers and their customers, such as higher costs and less privacy. But with it, state agencies and enterprises will be more responsible for preventing and combating the bad on the internet and they will do it better,” a former senior editor of Vietnam’s leading daily newspaper Tien Phong (Pioneer) told Xinhua. “Meanwhile, individuals will behave in a more responsible manner on cyberspace. Crimes and wrongdoings committed online will fall.”

According to several reports, representatives from Google and Facebook have raised no objection to the new law. According to Lieutenant-general Hoang Phuoc Thuan, director of the ministry’s Cybersecurity Department, as the law was being drafted the lawmakers reached out to representatives from the tech giants. “They said that this [law] was appropriate and that they will research to modify their companies’ strategies accordingly,” Thuan told VnEpxress. “Providing customers’ data to security authorities is not a violation of privacy,” he added.

When it comes to data localization personal information; data about users` relationships; and all other data generated by users in Vietnam must be stored in local servers. But, it is still unclear whether data must be stored exclusively in Vietnam, and so are several other aspects of the new law.

The proposed Law has also drawn flak from several human rights activists across the globe. “The goal of Vietnam’s proposed cybersecurity law appears as much to protect the party’s monopoly on power as to protect network security,” said Brad Adams, Asia director at Human Rights Watch. “This bill, which squarely targets free expression and access to information, will provide yet one more weapon for the government against dissenting voices. It is no coincidence that it was drafted by the country’s Ministry of Public Security, notorious for human rights violations.”

Huawei blasts Australian government over 5G ban

Huawei

In response to Australia’s Shadow Minister for Defence Richard Marles’s apprehension and a possible ruling toward Huawei ban from 5G networks citing cybersecurity concerns, the Chinese networking giant recently published a letter that would be sent to Australian members of Parliament over the comments made. The company vehemently stated that the recent rumors and comments were ill-informed and have no factual basis.

In the letter, Huawei points out that it is Australia’s largest wireless technology provider, and that more than half of the nation relies on Huawei for communication. “Our telecommunications equipment connects millions of Australian businesses and consumers every day on the Vodafone, Optus, and TPG mobile networks,” it reads. “As focus turns to investment in the next generation of telecom technologies in Australia, cybersecurity is a key consideration for Australian policymakers … with our 5G investments in the United Kingdom, Canada, and New Zealand, the respective governments have taken up our offers for evaluation of our technology to ensure it abides by its cybersecurity protocols. We have an open invitation for Australian officials and security agencies to meet with our world-leading research and development teams to better understand our technology.”

A recent conference was also held between Huawei’s global CEO, Ken Hu, and the company’s Australian board and management, where he instructed the management to feel free to take whatever action they thought required to “combat the building momentum in Australia against Huawei’s involvement.”

This isn’t the first time Huawei has come under the radar of the Australian government. Back in 2013, during Abbott’s regime, Huawei was banned from providing any kit to the country’s national broadband network citing concerns over security and labor laws. The ban had come after Barack Obama and his entourage’s visit to the nation, which was then apparently followed by several meetings with the U.S. intelligence.

“Given that it replicates a decision that was made under the Labor government, the answer was yes,” Richard Marles said in a recent conference. “Certainly when we were in government that’s what we did, and a call of that kind was previously made in relation to Huawei and national security clearly matters. This is a fundamental piece of infrastructure. If we were in government we’d be listening to those national security agencies to get their advice on this.”

Appian fined $513,769 for cyber fraud

Central Bank of Ireland

Irish asset management Appian has been fined by the Central Bank of Ireland a total of €443,000 ($513,769) for a string of cyber breaches in the company which resulted in a significant loss to client funds. The company admitted that breaches occurred in three regulatory regimes — client asset, anti-money laundering and fitness and probity. According to the Central Bank of Ireland, the company’s failures left it exposed to a cyber fraud by a third party, which resulted in the loss of €650,000 from a client’s funds.

“This is the first time the Central Bank has imposed a sanction on a firm where there has been a loss of client funds from cyberfraud as a direct result of the firm’s significant regulatory breaches and failures,” said Seána Cunningham, the Central Bank’s director of enforcement and anti-money laundering to Irish Times.

Even though the company has fully reimbursed the client fund, the bank in a statement stated that it had reprimanded the company for “significant breaches across three regulatory regimes: client asset, anti-money laundering, and fitness and probity,” adding that “had it not been for the financial position of the firm, the Central Bank would have imposed a financial penalty of €825,000.”

Patrick Lawless, the chief executive officer of Appian, informed that the breach occurred outside of Appian, and the company took the responsibility on itself for failing to notice the “red flags” which enabled hackers to succeed in the fraud. The company formally apologized to the Central Bank and accepted the sanction imposed. “Following this incident, Appian has remediated its failings, complied with the Risk Mitigation Programme issued by the Central Bank, introduced new client asset and AML/CFT policies and procedures and introduced new controls in respect of the management of client assets,” he said.

5 Key Security Responses from Massive New CIO Study

CIO survey

By SecureWorld

The Harvey Nash/KPMG survey of Chief Information Officers bills itself as the largest IT leadership survey in the world.

And its CIO respondents report spending more time, money, and resources on cybersecurity than ever before. Here are some key findings from 2018.

5 facts about how CIOs see security

  • Combined annual cybersecurity spending of respondents is up to a record $46 billion
  • 23 percent more IT leader respondents than last year are prioritizing improvements in cybersecurity
  • 12% more than last year say managing operational risk and compliance is a significantly increased priority
  • Cybersecurity and risk/compliance represent the fastest growing IT priorities of company boards
  • Only one fifth (22 percent) state they are well-prepared for a cyber attack.

Akhilesh Tuteja, Global Cyber Security Services Co-Leader at KPMG, puts a punctuation mark on the fact that corporate leadership cares much more now about cybersecurity: “Protecting the business from a cyber attack has jumped further up the boardroom agenda than any other item.”

Changing role of the CIO

The survey certainly drives home another point: It’s getting more complicated to be a CIO. Big changes are happening right along with the changing role of the CISO.

“CIOs have a really difficult tight rope to walk,” said Albert Ellis, CEO, Harvey Nash Group.

“On one hand the board is asking them to drive innovation, promote transparency and following recent high profile data breaches, ensure the responsible use of customer data throughout the organization.

On the other hand, the board is increasing scrutiny and demanding improved reporting on cyber security, data integrity and resilience, as regulators and consumers become much more demanding on personal data.

The organizations that can get this balance right, between innovation and governance, are in the strongest position to compete in an increasingly complex technology environment.”

This article was originally published by www.secureworldexpo.com, and is posted here with their permission. 

Thwarting email bomb attacks

Business Email Compromise Attacks

By Center for Internet Security

An email bomb is an attack against an email server designed to inhibit the server’s normal function or render it unresponsive, preventing email communications, degrading network performance, or causing network downtime. An attack’s intensity can range from an inconvenience to a complete interruption of service. Some email bombs are accidental or self-inflicted, such as when automatic replies sent to a distribution list cause a cascade of emails. Additionally, cybercriminals sometimes use email bomb attacks to mask other attacks and prevent users from receiving notices about account activity.

  • Mass mailing attacks occur when actors intentionally or unintentionally send large quantities of email traffic to targeted email addresses.
  • List linking attacks involve malicious actors signing targeted email addresses up to numerous email subscription services. Many of these services do not ask for verification or if they do, they send confirmation requests via email. This type of attack is difficult to prevent because the traffic originates from various legitimate sources.
  • ZIP bomb attacks consist of malicious actors sending malicious archive files designed to decompress to very large sizes. When the email server decompresses the file, significant server resources are consumed, potentially causing the server to slow down or stop responding.
  • Attachment attacks occur when malicious actors send multiple emails with large attachments, intending to overload the storage space on a server and cause the server to stop responding.
  • Reply-all email bombs occur when dissemination list members reply to all members of the list instead of just the original sender. This inundates inboxes with a cascade of emails, which are compounded by automated replies, such as out-of-office messages. This type of attack also occurs when a malicious actor spoofs an email and the automatic replies are directed toward the spoofed address.

Recommendations:

Prevention

  • Ensure email delivery software is up-to-date, patched, and includes anti-virus capabilities.
  • Employ “tarpitting” to block or slow traffic from a sending IP address if the traffic from that address exceeds a predefined threshold (e.g. greater than ten emails per minute).
  • Consider blocking file attachments used in email bomb attacks, such as .zip, .7zip, .exe, and .rar.
  • Limit the maximum email attachment file size.
  • Ensure out-of-office, bounce back, and other automatic messages are only sent once to prevent an endless loop of recurring automatic replies.
  • Where possible, limit send permissions so that only internal and authorized users may send to distribution lists.
  • Avoid posting plain text email addresses online as malicious actors are able to scrape webpages for email addresses allowing malicious actors to target them for spam campaigns.

During an attack

  • If your inbox is overloaded, avoid mass deleting emails and instead using email rules to filter spam.
  • Ensure critical inboxes use failover services and notification options to safeguard against deletion.

Avoid Unwitting Participation

  • Implement CAPTCHA on user subscription forms to prevent bots from using your service.
  • Send verification emails to newly subscribed users to prevent sending unwanted emails.

This was originally published by https://www.cisecurity.org/ and is posted here with their permission.

Infosec Superwoman: Candice Camp

Candice Camp

Contributed by Renee Small

Theater major Candice Camp didn’t think she had what it took to succeed in a highly technical field. After going back to school to try her hand at getting a network security degree, she is now the leader of the Insider Threat program at GE.

Getting into a technical profession was the farthest thing from Candice’s mind when she got a degree in theater. “I was not one that grew up thinking I was great at math or science, so I didn’t think of technology career growing up,” she admitted.

Working at the theater did expose her to the engineering and technical side of theater production, and after going through a “rough patch” in her twenties she decided to make a career switch. After scouting out several different programs, Candice found IT programs interesting and settled on getting a degree in network security.

“I did have a strong aptitude for it,” Candice said, adding that she was attracted to the course because it enabled her to use creative and investigative thinking. She was also excited with the possible future opportunities offered, particularly the opportunity to make a meaningful impact in the future.

Over the years, after getting her network security degree, Candice has since gained experience in various aspects of IT, such as data loss prevention, firewall audits and vulnerability management. She joined GE when it opened a cybersecurity headquarters in her area, and after starting out by building a DLP program she progressed, over time, to her present position of being the leader of the Insider Threat program at GE.

“I’ve had great luck in having amazing leaders throughout my career,” Candice enthuses. Her mentors are both men and women, which gives her different perspectives, and not only mentor her on the technical aspects but also on such aspects as decision making and business executive concerns.

Where mentoring is concerned, Candice notes that GE has a good mentoring program that she has taken advantage of, whether it is to be a mentor to others or to receive mentoring herself. “I have the best circle of women peers,” she also remarks, adding that the strongest women she knows are those who would help others.

“The adversary’s big and the adversary works together,” Candice notes about cybersecurity threats. Working with others outside GE is necessary, as the cybersecurity industry needs to figure out such security issues as a whole to provide better protection.

Most of the members in Candice’s present team have backgrounds in both physical and IT security. “We try to get a diverse mix of backgrounds and train each other on their own strengths,” she pointed out, adding that, “We do a lot of cross training on the team.” The retention rate in her team is high, which makes her life easy. “Transparency with your team is important,” she notes. “I feel building a relationship of trust is important for ensuring satisfaction. I can trust my team, they can trust me and that makes our lives easier when we can rely on each other.”

Renee Small is the CEO of Cyber Human Capital, a human resources business partner in the field of cybersecurity, and author of Magnetic Hiring: Your Company’s Secret Weapon to Attracting Top Cybersecurity Talent.


GDPR: An opportunity in disguise

GDPR

Contributed by Deepak Maheshwari, Director of Government Affairs in India & ASEAN, Symantec.

When Infosys co-founder and then CEO Nandan Nilekani told New York Times columnist and author Thomas Freidman that “The World Is Flat,” he was talking about the increasingly equal opportunity around the world no matter where you were. Those four words became the title of Freidman’s 2005 bestseller and have come to haunt the Indian IT industry over the past few years. The country’s annual growth rate has slowed according to NASSCOM, with more than two-third of it coming from exports.

The previous business model of the country has been one that thrived on high headcounts in line with the revenue growth. This model is being challenged by the era of cloud computing and artificial intelligence. In addition, most multinational companies have already invested in their own captive development centers in India, slowing new business in this sector.

As the Indian IT industry is looking for new ways of revitalizing, it needs to look beyond just efficient, quality coding to contextual appreciation of business processes and practices to become an even more valued partner for its global and domestic clientele.

Read more

Cryptos plunge after South Korean exchange hack

Bitcoin

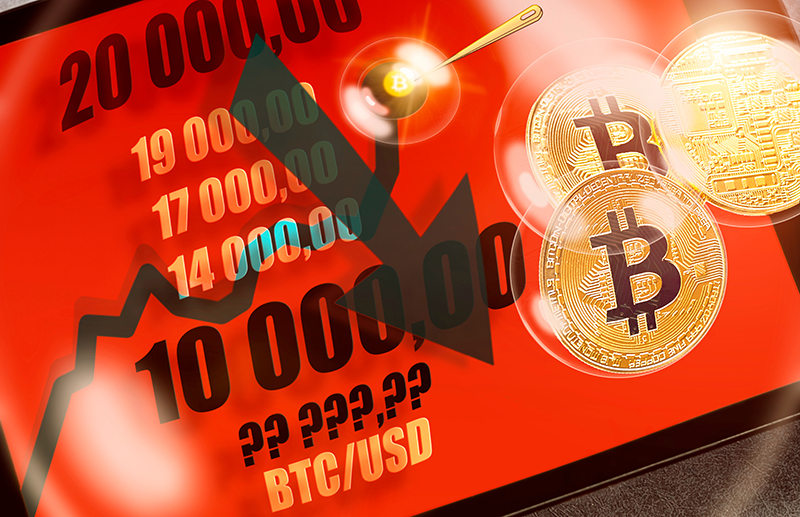
In the aftermath of the hack of the South Korean cryptocurrency exchange, Coinrail, on Sunday, June 10, 2018, the value of bitcoin dipped an all-time low of at $6,790.88, a 10.8 percent slump in a week and a massive dip from its December 2017 peak, where the coins recorded an all-time high of almost $20,000.

The currency exchange lost about 30 percent of the coins it traded. Its website has temporarily suspended trading and is currently working with investigators. The site reassured users that remainder of the coins were “safely stored.” Although the exchange is relatively a small firm, the news of the hack has tumbled the bitcoin value and several other virtual currencies to two-month lows of $294 billion. According to reports, the hack jolted holders of digital assets fueling a $46 billion selloff.

The recent string of cyber thefts has impacted the value of several cryptocurrencies. Earlier this year, Japanese exchange Coincheck Inc lost $500 million worth cryptocurrency. According to Stephen Innes, head of Asia Pacific trading at Oanda Corp. in Singapore. “This is ‘If it can happen to A, it can happen to B and it can happen to C,’ then people panic because someone is selling,” Innes said to Bloomberg. “The markets are so thinly traded, primarily by retail accounts, that these guys can get really scared out of positions. It actually doesn’t take a lot of money to move the market significantly.”

In late May 2018, Cryptocurrency startup Taylor faced a cyber heist when hackers stole nearly S$1.5 million cryptocurrencies along with nearly seven percent of the total supply of its own tokens forcing the company to launch a “survival fund token sale.” The only tokens left with the startup were those belonging to the Founders’ and Advisors’ pool which were held in an inaccessible vesting contract.

“In 2014, Tokyo-based Mt. Gox, which once handled 80 percent of the world’s bitcoin trades, filed for bankruptcy after losing around half a billion dollars worth of bitcoins. More recently, South Korean cryptocurrency exchange Youbit last month shut down and filed for bankruptcy after being hacked twice last year,” states a report on CNBC.

Meanwhile, global policymakers have warned investors to be cautious in trading the digital currency. “Coinrail is not a member of the group that promotes self regulations to enhance security. It is a minor player in the market and I can see how such small exchanges with lower standards on security level can be exposed to more risks,” Kim Jin-Hwa, a representative at Korea Blockchain Industry Association in an interview with Reuters.

Few minutes with Curtis Dalton

Curtis Dalton

An industry thought leader, security subject matter expert, a published author, speaker and guest lecturer, Curtis Dalton is North America Managing Director, Security Strategy & Risk, at Accenture. An executive with over 25 years of experience, including managing budgets in excess of 100M and teams in excess of 85 people within the technology, financial services, and health industries.

His exposure to top-tier organizations has helped him become adept at establishing and conveying a fit-for-purpose vision and approach for the business. Curtis possesses a strong, first-hand international business experience with particular experience within the U.K., Germany, China (mainland), Hong Kong, Japan, Singapore, India and Australia. I understand the cultures, the people, the business environment and how to successfully navigate within them.

What are some of the popular and effective techniques that security leaders generally use to assess a threat landscape? What are the kinds of tools and techniques that are often used?

Well, I can’t mention anyone else’s tools, but I can mention some of things that we do. To assess threats and the threat landscape, we use i-Defense (a company we acquired). What i-defense does, is provide our clients with threat intelligence into what their indicators of attack are, what their indicators of compromise are within the environment.  We then leverage that to better understand where certain incident response procedures should be augmented, where better detection is needed, and where better visibility is needed. All these technologies in the threat intel space are about improving visibility and improving your response capabilities. Everyone has already agreed that, eventually, someone who has enough time, resources, and skills will get in. There are certainly plenty of factions in the criminal world that have the capability, the skills, and the time. They can spend a year and a half trying to ascertain how best to breach a particular target. So, really our fall back mechanism is more visibility. That means better detection, better understanding, better context about what’s going on in the environment and correspondingly, being able to quickly respond. You want to minimize that threat window. The threat window stretches from the time you become vulnerable to something, to the time in which you are able to respond and address it. You want to minimize that threat window as much as possible and without threat intelligence, that job is very difficult.

Do you believe i-Defense nullifies the intervention of any human is possible?

No, absolutely not. No solution nullifies the need for a person. You always need people. This is why it’s great to be in security field. Security keeps stepping up. Attackers become more and more savvy, and their attack capabilities become more and more dangerous. The well-used paradigm where all attackers have to do is be right one time, while defenders have to be right every time. So comparatively, it’s relatively easy for them and difficult for us. With the advent of machine learning and artificial intelligence, we are better able to defend ourselves, but frankly the attackers are using these as well. There have been studies in the last handful of years which indicate that attackers actually collaborate better than defenders. The bad guys collaborate better than we do. They are more willing to share information and work together. That’s a problem because collaboration really leads to things like innovation. We are seeing lots of attacks today that are highly innovative.

How important are application security engineers to any organization?

I actually wrote a paper about this a few years ago. The whole point is that information security is really about protecting the data. If you think about it, what medium is closest to the data? The application collects the data, processes it, and shares it. The application is the closest medium that we have aside from the data itself. Eventually, we’ll get to the point where data can protect itself, and that will be a great moment, but we are not there yet. As long as the data can’t protect itself, the closest medium that has most context about the data is the application. So application security is critically important because that is the component that collects the data, moves the data, makes decisions about where to send the data, makes decisions about who has access to the data. So application security is really critical. This could become a whole conversation in and of itself. This involves the SDLC process, all the best practices that we should follow throughout the SDLC process, training of developers, validating third party libraries, etc. Third party code is an interesting one because they are represented heavily in applications today. The reality is that approximately 80% of an application’s library set is third party code. So, while we stress the importance of application developers becoming well versed in secure coding practices, the reality is that most of their job is not actually about writing code any more, it’s about assembling code. Software developers have strict schedules. They have to develop code very quickly to get something patched, add new features, get to the next release, etc. Under all of these pressures, they need to get that code over the line when it’s due. In today’s world with continuous integration and deployment methodologies, these things are very rapid.

When a developer sits down to write a code, do you think there is more focus on speed at which the code is deployed or the security portion occupies substantial importance there?

I guess it depends from organization to organization. A lot of application developers these days, for example, use a DevSecOps model. When it’s done properly, both speed and security are baked in. I think there are still many application security developers who haven’t been trained properly in secure coding practices. Despite the fact that so many libraries that end up in the application weren’t even written by your developers, they still need to be trained to identify weak code and know how to fix it.

What kind of financial impact do you think an organization will expect if they don’t follow a secure SDLC process vis-a-vis they are following it?

The facts and figures indicate that retrofitting security into an application could cost upwards of 300% more than if you did that way initially. You have to think about how complex apps are these days. It’s even complicated sometimes to identify really what an app is. You have all kinds of technologies that have pieces of the application all over the place, so it’s complicated.

Do you think that there is a dearth of application security engineers in the industry today?

It’s a function of what an application security engineer does. I would say SAST testing and largely even DAST testing can be done quite quickly if you do it right, so they really don’t need to know a lot about how these tools work. What is more important is to make sure they understand secure coding practices. Now a very important piece of this is when software developers are writing the code, it’s really useful to have SAST testing done in real time, so as the developers are writing their code, they can test it and immediately see the results. This becomes a valuable learning exercise to see the results from a SAST test and to make those adjustments right away while things are fresh.

Are you saying that there is very less need of app security specialists who can work towards a secure SDLC?

No, I think it’s more of the opposite. You should have a security architect involved in the SDLC process to think about the bigger picture, and how everything fits together. The security architect is basically the security champion for a given project. This is someone with IT skills, application security architecture skills as well as a good understanding of SDLC processes. This person is kind of a liaison that overlaps between Dev and the Ops. He or she provides the right level of security expertise, and will work with the software development team from the beginning. They begin by making sure that what they are going to develop is going to be architected with security in mind and as certain milestones are achieved/ about to be achieved. It is important to have continuing security architecture reviews to make sure that what was intended in the design has been fulfilled in the code. So, I am not saying don’t train your software developers in application security architecture and testing, but don’t expect software developers to be IT security experts capable of Pen testing and DAST testing. Let them focus on writing their code in a secure fashion. They are already heavily taxed with the heavy workload and timelines. Let them focus on learning secure coding practices. I have in the past created a belt system of training in application security. Automatically, you start off at white belt and after taking certain trainings and conducting certain experiential exercises, you achieve more belts and that is how you move from white to yellow belt, to green belt, to purple belt, to brown belt, and ultimately black belt. The idea there is to build a doctrine and program that steers you towards security improvements. What I did was institute a requirement that for example only people with the highest levels of secure coding practices got to work on projects that handled sensitive information. These in effect are the most interesting and cool projects. If you don’t have the required belt level, you would not be able to work on that cool project and instead they would work on the more mundane projects. You should build your program in such a way that it inspires the software community to become more security minded and that is one of the CISO’s top responsibilities —  to build a security mindset throughout the organization, imbedding it within the culture itself.

What kind of training programs are generally conducted in Accenture or in your past organization toward ensuring that aspiring security analysts can be trained?

Accenture has a vast amount of internal trainings that cover a wide topic base, and also a good mixture of industry training as well. In a way, attending the key conferences like RSA, BlackHat, Defcon, etc., and networking with people outside your organization are very important too. It’s about sharing information, and getting different perspectives.

Is there any specific set of skills which according to you is a must have for somebody to be Application Security Engineer?

So again, when you say Application Security engineer, I am imagining that that person is going to be really a security person at heart. You can take an application developer and teach them security more easily than you could take a security person and teach them application development.

In an ideal scenario, if someone were to become an app security engineer, what are the skills you would expect him to have at your level?

They have to understand how applications function, application architecture, the different tiers, etc. They have to understand those basics, SDLC, and then on top of that, they need to have some past skills in software development. Enough experience just to get their feet wet effectively. Understanding of the SAST toolsets and the DAST toolsets, all the different open source application security testing tools, and understanding also how to eradicate false positives from your test results is the key. And understanding how to security test applications and systems without impacting productivity when it is not appropriate is also important

How someone at your level will rate a course on AppSec training? We are rolling out a course which is called CASE, so if I tell you about these courses what are the necessary skills you think should be in a course like this?

Well I think fundamentals of application architecture to my point earlier understanding how they are architected, how do you do an application architecture review that’s important for understanding the inputs and outputs, how the application should process things, have to understand obviously encryption, how to use it, how to apply it, have to understand SDLC as a whole, understanding when to plug in and what to plug in for certain testing and what the end results would be.

When it comes to safeguarding companies from cyber threat from the outside we see a lot of menace in the form of insider threats, what does a large company like Accenture do to counter these threats?

In general, what you want to do is implement a zero-trust model, as much as possible. In zero trust, there are basically four pillars: validate the user’s input into the application, validate the user’s device, and control the user’s access throughout their session. Creating an active authentication scheme like this is really valuable. This is related to an ability Accenture has within its identity management practice – where we can actively authenticate and authorize a user. Effectively, we can monitor the user session for abnormalities and quickly take the needed actions such as terminating their access.

Traditionally, the security department in an organization reports to IT. However, we are now seeing a trend where IT reports to security. Do you think the latter is the right approach?

Frankly, I have never seen that but in general the world of the CISO has evolved. When I was global CISO at a previous company, I was hired in to work for the COO. Two years later, with the rise in the importance of privacy, I began reporting to the General Council. Security enables privacy, so it made a lot of sense to make that shift. At another previous company, I reported to the President/CEO. In both of my CISO roles, I was a peer to the CIO.

Do you think the cyber security practices followed today would be relevant in the next two years, what would your advice be to a budding infosec professional of today?

Yes largely they will. As much as we say that security in particular moves rapidly, application security has not changed so rapidly. We have relatively new forms of testing, such as IAST, but that has been around for several years and there are still many companies that don’t use it.

To a budding infosec professional, my advice would be to understand DevSecOps, understand the agile environment, types of security testing that should take place within the SDLC, know when to implement those tests and how to reduce false positive within those test sets.