Home Blog Page 343

Voith partners with Kudelski Group to deliver end-to-end cybersecurity solutions

CynergisTek Partners with Awake Security to Boost Cybersecurity in Health Care

The technology company Voith joined hands with digital security provider Kudelski Group to deliver new end-to-end cybersecurity solutions for industrial markets in North America. Voith stated the partnership provides end-to-end products and services by using Industrial Internet of Things (IIoT) to bring secure connectivity across the business operations.

Voith claims that it sets standards in energy, oil & gas, paper, raw materials, and transport & mobility markets. The partnership combines Voith’s knowledge of the operational technology (OT) and IIoT domain with Kudelski’s expertise in hardware and software-based cybersecurity solutions.

“This partnership will bring added protections to Voith’s customers,” said Michael Rhodes, Senior Vice President Sales North America, Voith Digital Ventures. “Both Voith and Kudelski have deep expertise in IIoT systems and bringing the two companies together in a partnership strengthens that knowledge base. With Voith’s unique expertise in OT and Kudelski’s dominating cybersecurity experience, this team will deliver a world-class cybersecurity offering to businesses as they embrace digitalization and automation.”

Headquartered in Cheseaux-sur-Lausanne, Switzerland, and the USA, Kudelski Group offers cybersecurity solutions and services to help organizations assess risks and vulnerabilities. Kudelski stated the aim of the partnership is to develop tangible products and services to support customers in their digital transformation journey and protect them from emerging cybersecurity threats.

“As companies around the world seek the benefits of connecting their OT systems to their enterprise IT infrastructure, the focus must move from air-gapped, physical security to a holistic, end-to-end, security-by-design approach,” said Jean-Michel Puiatti, Senior Vice President of IoT security at Kudelski. “Voith is driving digital innovation across many different industries, and we look forward to supporting customers in achieving their long-term objectives with device and data protection, access management, active security and managed services that will help them create sustainable growth and success.”
Panorays partners with Japanese insurer for cybersecurity management

96% of Cybersecurity Professionals are Happy With Their Roles

Israel-based startup Panorays recently partnered with Japanese insurance giant Sompo to expand its business platform throughout Japan. The third-party security management provider stated that it will cooperate with Sompo’s risk management and the cybersecurity business units.

“We are proud of this partnership and offering the Panorays platform to tens of thousands of businesses that are among our customers in Japan,” said Yoshi Miyazaki, who leads the cyber unit at Sompo Risk Management.

Founded by Matan Or-El, Meir Antar and Demi Ben-Ari, Panorays automates third-party cybersecurity management. The company claims that SaaS-based platform allows organizations to easily view, manage, and engage with their business partners on cybersecurity resilience. Companies use Panorays’s platform to gain continuous visibility and evaluate their third-party security.

“We’re honored to be one of Sompo Risk Management’s first cybersecurity partners. There is enormous potential for third-party security in the Japanese market and our partnership with Sompo Risk Management signals a key milestone in our global reach, giving a huge range of organizations in Japan the ability to manage and automate their whole third-party risk evaluation process,” said Matan Or-El, CEO of Panorays.

Panorays has several InfoSec behemoths in its executive team who have held leadership roles in companies like Imperva, AVG, ironSource, Windward, WalkMe and enSilo. In June of this year, the startup closed an early stage funding round of $5 million led by noted venture capital fund, Aleph and had Amichai Shulman, co-founder and former CTO of Imperva, Elevator Fund, Moshe Lichtman and Michael Dolinsky, and several cybersecurity veterans. The company also launched its flagship automated platform that secures and strengthens the security of organizations in the supply chain.

Cisco to train 120,000 UK police officers on cybersecurity

CISCO

Cisco recently announced that it’s partnering with the United Kingdom police forces to provide them cybersecurity training through the Cisco Networking Academy. The California-based company stated that it’s going to train more than 120,000 police officers across England, Scotland, Wales, and Northern Ireland to help make the UK the safest cyberspace.

The latest training partnership between the National Police Chiefs’ Council and Cisco’s Networking Academy mark the first anniversary of Cisco’s digital skills manifesto in the United Kingdom. The nationwide cybersecurity training will help the police officers develop their knowledge in emerging cybersecurity trends.

Speaking on the new initiative, Andy Beet, National Police Chiefs’ Council, said “We are very pleased to be working with Cisco Networking Academy. By joining the programme, forces can access training designed to raise awareness and increase their understanding of cybercrime and cyber threats, while also gaining insights into the procedures used to defend networks. It’s important for all police officers to understand cybersecurity as fully as possible; by doing so they can develop their knowledge in this increasingly important area, improving security in both their professional and personal lives.”

“The UK is one of the world’s most digitally active nations, and with that comes the ever-increasing opportunity for cybercriminals to exploit individuals and organizations. We’re extremely proud to be working with the Police in their efforts to help make the UK a safer place to be online. Through the Cisco Networking Academy, our ambition is to help ensure that people around the world have the digital skills they need to be successful in any profession,” added Scot Gardner, Chief Executive, Cisco UK, and Ireland.

Earlier this year, Cisco joined hands with Apple, Aon, and Allianz to develop a new cyber risk management solution for businesses. The new solution is designed to help a wider range of organizations better manage and protect themselves from the cyber risk associated with ransomware and other malware-related threats, which are the most common threats faced by organizations today.


Unprotected ElasticSearch server exposes data of 57 million Americans

An unprotected Elasticsearch database exposed personal details of 57 million U.S. citizens for almost two weeks. Bob Diachenko, Director of Cyber Risk Research at Hacken, discovered that the unsecured server was left visible online without a password exposing customers’ personal data.

ElasticSearch, an enterprise search engine, provides technology solutions for powering search functions.

“An open ElasticSearch instance exposed personal info of 56,934,021 US citizens, with information such as first name, last name, employers, job title, email, address, state, zip, phone number, and IP address,” Diachenko stated in a blog post.

The researcher also stated he found another index of the same database that contained 25 million additional data records holding sensitive information, including names, company details, zip address, carrier route, latitude/longitude, census tract, phone number, web address, email, employees count, revenue numbers, NAICS codes, and SIC codes.

The database was not password protected and could be accessed by anyone with an Internet connection. The issue was spotted during a security audit of publicly available servers with the Shodan search engine, according to the researcher.

“As of today, the database is no longer exposed to the public, however, it is unknown for how long it has been online before Shodan crawlers indexed it on November 14th and who else might have accessed the data,” Diachenko added.

The researcher specified the source of the leak was not identifiable and he’s not able to get in touch with ElasticSearch representatives.

While speaking about the disclosure, Bob said, “Our goal is to help protect data on the Internet by identifying data leaks and following responsible disclosure policies. Our mission is to make the cyber world safer by educating businesses and communities worldwide on ethical vulnerability disclosure policy (VDP).”

A couple of weeks back, Diachenko had unearthed another unprotected server hosted by MongoDB that exposed hundreds of thousands of American Express (Amex) India customers’ personal data. Most of the exposed data were encrypted but included 2,332,115 records with customers’ names, addresses, Aadhar numbers, PAN card numbers, and phone numbers hosted on the domain americanexpressindia.co.in.

Amazon warns technical error exposed customers’ information

Amazon

Amazon recently reported a technical error that exposed users’ personal information like names and email addresses. In an email sent to its customers, Amazon Customer Service cautioned that the company unintentionally exposed the users’ data due to a technical error, The INQuirer reported. However, the Seattle-based e-tailer has not yet disclosed any details about the error.

“We’re contacting you to let you know that our website inadvertently disclosed your name and email address due to a technical error. The issue has been fixed. This is not a result of anything you have done, and there is no need for you to change your password or take any other action,” the email read.

Most of the customers who received the email speculated it was a scam or some kind of a phishing attack until Amazon’s UK press office confirmed the incident. “We have fixed the issue and informed customers who may have been impacted,” Amazon stated in a press note.

Recently, a security team from Tencent Blade exposed security vulnerabilities in Amazon Echo smart speakers. The researchers Wu HuiYu and Qian Wenxiang gave a live demonstration at the DEFCON security conference on how to hack a smart speaker.

The researchers hacked the speaker by adding a malicious device embedded with an attack program.  “After several months of research, we have successfully broken the Amazon Echo by using multiple vulnerabilities in the Amazon Echo system, and achieve remote eavesdropping,” the researchers said in a media report. “When the attack succeeds, we can control Amazon Echo for eavesdropping and send the voice data through a network to the attacker.”

The researchers notified Amazon of their findings before the presentation, and Amazon has already pushed a security patch to fix the issues.

Cybersecurity startup Censys raises $2.6 million

Startup Investment

Censys, a cybersecurity startup recently announced that it has raised $2.6 million in a funding round led by GV (formerly known as Google Ventures), Greylock Partners, and several other angel investors. The Michigan-based startup stated it will use the new investment to collect more data and provide additional actionable insights for its clients. The startup is also planning to expand its engineering and product teams.

“In the same way you think of a search engine like Google or Bing being a view into every web page, our goal is to index the world’s infrastructure information,” says Censys CEO Brian Kelly.

Started as a research project at the University of Michigan in 2015, Censys helps organizations by providing visibility to find where the information may be exposed and assess security risk. Founded by a group of security researchers, Censys’s foundational technology acts as a custom search engine that monitors all the IoT devices to look for existing vulnerabilities.

“Censys provides information security practitioners with critical data-driven insights to prevent cybersecurity threats and better understand network attack surfaces,” said GV General Partner Karim Faris. “Driven by a highly technical founding team with a deep security expertise, Censys creates a fuller picture of the security risk for researchers, enterprises, and government customers.”

Censys’s clientele includes government and private agencies, including the U.S. Department of Homeland Security, FireEye, Google, the North Atlantic Treaty Organization (NATO), and the Swiss Armed Forces. Censys’s technology solutions enable organizations to monitor and protect their servers and devices on corporate networks and to gain a visibility of their public-facing attack surface.

“Prior to moving to the cloud, business data could be tucked safely within a managed, corporate network,” added Greylock partner Asheem Chandna. “The journey to the cloud introduces new security challenges and risk. Censys provides enterprises moving to hybrid IT and cloud with a map of their external attack surface, allowing IT teams to fully comprehend and manage their security risk and exposure.”

ICO fines Uber over data protection failings

Uber Data Breach

The United Kingdom’s Information Commissioner’s Office has fined Uber £385,000 ($491,284) for failing to protect customers’ personal data during a cyber-attack in 2016, and not reporting the breach in a timely manner. The taxi-aggregator was also slammed by the Dutch Data Protection Authority with a fine of €600,000 ($679,257) for the same reason.

The ICO stated the breach allowed hackers to illegally access personal data, including names, email addresses, and phone numbers of 2.7 million Uber customers in the U.K. and 174,000 in the Netherlands.

After hiding the incident for more than a year, Uber admitted last November that hackers did manage to steal personal data of 57 million customers and drivers worldwide.  The company alleged that two hackers gained unauthorized access to information on Github and stole Uber’s credentials for a separate cloud-services provider where they were able to download driver and rider data.

It is reported that Uber paid hackers $100,000 to keep data breach a secret and failed to inform its customers and drivers about the incident. The compromised customer information included names, phone numbers, email addresses, and their location. And, the driver information included their weekly pay, trip summaries, and their car license details, according to the ICO statement.

“This was not only a serious failure of data security on Uber’s part, but a complete disregard for the customers and drivers whose personal information was stolen,” ICO Director of Investigations Steve Eckersley said. “At the time, no steps were taken to inform anyone affected by the breach, or to offer help and support. That left them vulnerable.”

“Paying the attackers and then keeping quiet about it afterwards was not, in our view, an appropriate response to the cyber-attack. Although there was no legal duty to report data breaches under the old legislation, Uber’s poor data protection practices and subsequent decisions and conduct were likely to have compounded the distress of those affected,” Eckersley added.

On November 28, 2017, the Washington State Attorney General Bob Ferguson filed a multimillion-dollar lawsuit against Uber, alleging that ride-sharing company violated the state’s revised data breach notification norm. Ferguson alleged that names and driver’s license numbers of at least 10,888 Uber drivers in Washington state were stolen without their being notified as state law requires.

Anthem settles Data Breach lawsuit

Surveillance Legislation (Identify and Disrupt) Amendment Bill

The victims of the Anthem’s data breach are going to receive payouts in the class action settlement. The American health insurance company stated that it has reached a settlement in the class action lawsuit.

“Anthem has reached a settlement to completely resolve the multidistrict class action litigation brought against Anthem and other defendants relating to the 2015 cyber-attack. Under the settlement, which the court granted final approval to on August 15, 2018, Anthem does not admit any wrongdoing or acknowledge that any individuals were harmed as a result of the cyber-attack. Nevertheless, we are pleased to be putting this litigation behind us, and to be providing additional benefits to individuals whose data was impacted in the cyber-attack,” Anthem said in a statement.

In July 2017, the company reported a massive data breach that resulted in an identity theft of more than 18,000 Anthem’s Medicare members. In April 2017, the company discovered that an employee who worked for one of the Anthem’s healthcare consulting firms was stealing and misusing the information of Medicaid members since July 2016.

The employee illegally sent a file containing the company’s data to his personal email address. The stolen data included Medicare ID numbers, social security numbers, health plan ID numbers, names of members, and dates of enrollment. The employee was suspended from the services and placed under the investigation.

As part of the settlement, Anthem agreed to pay a total of $115 million to resolve the litigation. The final resolution also pays for credit monitoring and identity protection services to all the victims for two years, including the costs of sending notice to class members, administering claims, and the attorneys’ fees. Anthem also clarified that there is no evidence of any fraud or misuse of the compromised data.

Ohio Hospital System suffers ransomware attack

Ransomware attacks, ransomware, Sinclair Broadcast group

A ransomware attack forced East Ohio Regional Hospital (EORH) and Ohio Valley Medical Center (OVMC) to divert its emergency squad patients to other area hospital emergency rooms. The malicious software infected the computer systems and disrupted the hospital emergency rooms, the TimesLedger reported.

According to Karin Janiszewski, the director of marketing and public relations for EORH and OVMC, the attack occurred on November 23, 2018, making the hospitals unable to accept ER patients via emergency responders. Janiszewski clarified that the issue was resolved on November 25, and there is no sign of patients’ information breach.

“At the moment, our emergency rooms are unable to take patients by E-squads, but we can take patients by walk-in,” Janiszewski said. “Our IT team is working around the clock right now and we expect to have the issue resolved by (Sunday).”

“We have redundant security, so the attack was able to get through the first layer but not the second layer. There has been no patient information breach. The hospitals are switching to paper charting to ensure patient data protection,” Janiszewski added.

Explaining the impact of the incident, Daniel Dunmyer, CEO of OVMC, said, “The OVMC-EORH employees and medical staff have been very adaptive and supportive and we are able to continue with quality patient care.”

In a similar ransomware attack almost two months ago, cybercriminals targeted Health Management Concepts (HMC) with a ransomware that quickly turned into a major data breach that compromised the patient’s personal data like names, social security numbers, and health insurance information.

HMC notified the New Hampshire Attorney General that it has discovered, on July 16, a ransomware attack on its server which is used to share files with the clients. The healthcare management vendor provides chronic condition management to IBU (Inlandboatmen’s United of the Pacific National Benefit Funds).

Australia launches new Joint Cybersecurity Center in Adelaide

Adelaide

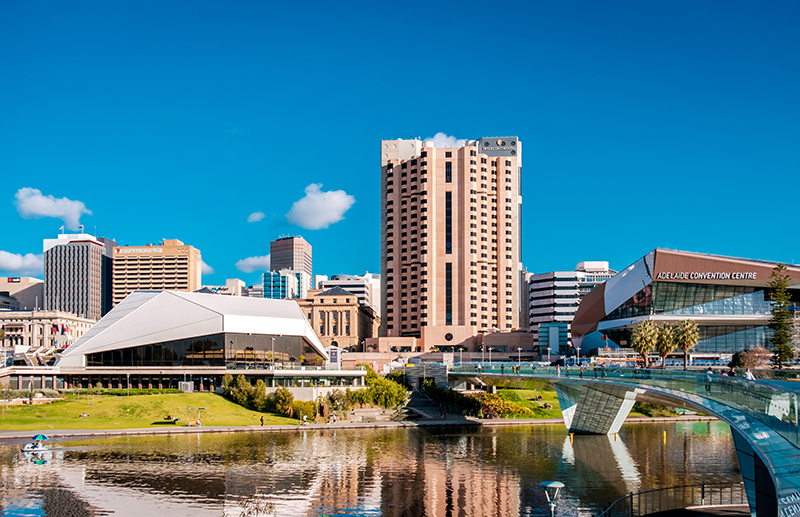
The government of Australia has launched a new Joint Cyber Security Center (JCSC) in Adelaide, South Australia, to promote cybersecurity systems across government, business, and academia. The facility is a part of the government’s $47 million JCSC program that bridges the gap between several public and private companies in sectors such as defense, finance, transport, energy, health, mining, and education.

The new facility launched by the Minister for Defense Christopher Pyne is aimed to be a central hub for the cybersecurity information, advice, and assistance for Australians. The latest Center joins the list of other JCSC Centers located in Brisbane, Perth, Canberra, Melbourne, and Sydney.

“South Australia hosts some of the nation’s most important energy, infrastructure, and defense assets,” Minister Pyne said. “This Centre is crucial to protecting our national assets including the wider Defence industry we depend on.”

The Center provides a unique offering to the South Australian community with AustCyber (the Australian Cyber Security Growth Network), locating a Cyber Security Innovation Node within the JCSC. The new facility will strengthen the cybersecurity infrastructure of the country and will also be involved in sharing sensitive information, including actionable cyber threat intelligence among myriad bodies in both public and private spaces.

“The ACSC will strengthen its collaboration with business, government, and researchers through an expanded program of support and services and deepened expertise in the Centres,” said Alastair MacGibbon, the Head of the ACSC. “Locating the JCSC and the AustCyber Node together demonstrates our commitment to growth and innovation in cybersecurity while also providing South Australians access to a range of dedicated cybersecurity professionals in one location.”

The Minister for Home Affairs, Peter Dutton, stated the government is working together with the cybersecurity industry experts to protect Australian businesses and the community from the increasing threat of cybercrimes, malicious actors, and hacker groups.

“The ACSC’s continuing expansion supports this Government’s national security agenda by giving Australians, be it small business owners and operators or large corporate and critical infrastructure companies, access to a broad range of services from cybersecurity experts around the country,” Dutton stated.