Home Blog Page 226

80% Security Practitioners Perceive Cyberattack Prevention as Most Difficult: Survey

BlackMatter Group, Volvo Cars ransomware attack

A latest survey “The Economic Value of Prevention in the Cybersecurity Lifecycle” from the Ponemon Institute revealed that the economic value of cyberattack prevention ranges from US$396,675 to US$1,366,365. The survey, sponsored by cybersecurity company Deep Instinct, took into account the entire cybersecurity lifecycle, which includes detection, containment, remediation, and recovery.

The study found that the majority of cybersecurity professionals (70%) felt the ability to prevent attacks to improve their cybersecurity posture and reduce the cost of an attack, however only a small budget (21%) is allocated to cyberattacks prevention. It also highlighted that 79% of budget allocation is delegated for detection, containment, recovery, and remediation activities.

Nearly 50% of respondents admitted that their organizations are wasting budgets that don’t improve their cybersecurity posture, while 40% of them stated that their budgets are sufficient. According to 80% of respondents, the prevention of cyberattacks is perceived as the most difficult task to achieve in the cybersecurity lifecycle, for the reasons cited–that it takes too long to identify, insufficient technology, and lack of in-house expertise. 55% of respondents feel their organizations can contain cyberattacks after they happen.

The study revealed that efficient adoption of preventative security solutions, compared to the current spending of security departments and the cost of attacks, will result in significant cost reductions.

Attack Type

Average Total Cost of Attack
(USD)

Percent of Total Cost Spent
On Preventing an Attack

Average Cost Savings
Resulting from The Ability To
Prevent an Attack (USD)

Phishing US$832,500 18% US$682,650
Zero-day US$1,238,000 12% US$1,089,440
Spyware US$691,500 26% US$511,710
Nation-state US$1,501,500 9% US$1,366,365
Ransomware US$440,750 10% US$396,675


The findings are based on the responses of 600 IT and security practitioners who are responsible for maintaining and implementing security technologies, conducting assessments, leading security teams and testing controls in their organizations.

“What this study shows is that most companies are still operating under a policy of ‘assume breach,’ believing that it is more pragmatic to contain a cyberattack after penetration. This is no longer an economically viable long-term strategy,” said Guy Caspi, CEO and Co-founder of Deep Instinct. “The value of prevention is clear–for any type of attack, prevention saves significant time and money. Deep learning-powered cyber solutions, which are uninhibited by the human limitations that define machine learning-driven solutions, are uniquely suited to provide preventative protection for enterprises and drive down the costs of attacks.”

General Electric Data Leak Exposes Personal Data of Thousands of Employees

Panasonic network breach

Technology service provider General Electric (GE) is a recent victim of a data breach that exposed personal data of thousands of its former and current employees. According to the official statement, the data breach occurred at Canon Business Process Services Inc., a service provider of GE, which is responsible for processing GE’s documentation on current employees, former employees, and beneficiaries entitled to benefits. The breach occurred when an unauthorized party gained access to one of Canon’s employees email account that contained documents of GE employees that were maintained on Canon’s systems.

 Massive Data Exposed

The sensitive information obtained by the unauthorized party includes names, addresses, Social Security numbers, passport numbers, driver’s license numbers, bank account numbers, dates of birth and other information of GE employees and their beneficiaries. According to Canon, the other documented information that exposed in the incident includes direct deposit forms, driver’s licenses, passports, birth certificates, marriage certificates, death certificates, medical child support orders, tax withholding forms, beneficiary designation forms and applications for benefits such as retirement, severance and death benefits with related forms and documents.

The company stated the identity of the hackers is unknown and there is no sign of any misuse of the data at present. GE also clarified that personal information in its systems has not been affected due to the Canon data security incident.

However, cybercriminals do take advantage of stolen data for phishing attacks, identity theft incidents, or selling it on hacker forums. GE stated that Canon will be offering free identity protection and credit monitoring services to the affected employees.

“After learning of the issue, we quickly began working with Canon to identify the affected GE employees, former employees and beneficiaries. We understand that Canon took steps to secure its systems and determine the nature of the issue. Canon also retained a data security expert to conduct a forensic investigation,” the company said in a statement.

Magecart Hackers Strike Again! Compromise 19 E-Commerce Websites

New Programming Language

Cybersecurity researchers from threat intelligence firm RiskIQ uncovered a new Magecart campaign dubbed as “Magecart Group 7” that compromised over 19 e-commerce websites to steal customers’ payment card data. According to RiskIQ’s report, the researchers discovered a software skimmer “MakeFrame,” which injects HTML iframes into the targeted websites to obtain payment information.

Explaining their discovery, the researchers said, “On January 24th, we first became aware of a new Magecart skimmer, which we dubbed MakeFrame after its ability to make iframes for skimming payment data. We initially flagged it with our machine learning model for detecting obfuscated code. Since then, we have captured several different versions of the skimmer, each sporting various levels of obfuscation, from dev versions in clear code to finalized versions using encrypted obfuscation.”

What is Magecart Attack?

Magecart attack, also known as web skimming or e-skimming, is a form of cybercrime where attackers plant malicious JavaScript code on online stores. In a Magecart attack, hackers gain access to a company’s online store website by compromising and hiding malicious code in it. The malicious code then collects the payment card information from users while making purchases on the infected site. It’s said that hackers either sell the stolen card data on the darknet or use it to make fraudulent purchases.

How MakeFrame Skimmer Works?

The researchers stated that they’ve observed different versions of the Makeframe skimmer that exhibit various levels of obfuscation to avoid detection. It’s said that attackers used MakeFrame on compromised sites for hosting the skimming code, loading the skimmer on other compromised websites, and exfiltrating the stolen data.

Once the skimmer is added on the target site, MakeFrame emulates the payment method, uses iframes to create a fake payment form, and detects the data entered into the form. Upon submitting the payment, it exfiltrates the card information in the form of “.php files” to another compromised domain.

“This method of exfiltration is the same as that used by Magecart Group 7, sending stolen data as .php files to other compromised sites for exfiltration.”Each compromised site used for data exfil has also been injected with a skimmer and has been used to host skimming code loaded on other victim sites as well,” RiskIQ said in the report.

Magecart Hackers Arrest

Recently, Indonesian Police and Interpol arrested three men who belong to Magecart hacking group for their involvement in Magecart attacks. The police officials stated that it’s the first arrest of Magecart gang members. The suspects, identified by initials ANF (27 years), K (35 years), and N (23 years), were accused of injecting JavaScript sniffers into websites to capture information entered by the site visitors. It’s said that the suspects allegedly used the stolen payment card data to purchase electronic and luxury goods.

What Every Employee Can Do Now to Strengthen Security at Home (Part-1)

Remote Security Policy, Remote Work Jeopardizes Corporate Network Security: Report

With more than half the world now working from home, the home network and its devices become an extension of the corporate network. From the organization’s point of view, the attack surface is expanded to include points of exposure on home Wi-Fi networks, access points, home routers, mobile devices, workstations, and laptops. IT administrators take steps to mitigate risks through security policies that enforce security controls (Windows UAC and Group Policy, for instance) and mandate the usage of corporate VPNs. Additionally, there are certain things that employees can do themselves to tighten security. In a remote working scenario, security is a shared responsibility between the organization and its employees.

By Brian Pereira, Principal Editor, CISO MAG

Here are 4 things to secure in your IT infrastructure while working from home:

Secure network connections

Home network connections are mostly wireless, and we know that wireless connections are not as secure as wired (Ethernet) connections. If your home router has a weak password or the default one, it could be hacked by a tech-savvy neighbor. Even Bluetooth connections can be hacked (Bluesnarfing attacks).

To secure your home Wi-Fi, get out the router manual (or download it from the Internet). Look for the default router ID and password. The ID could be “Admin” and the default password could also be “admin”. Now load your browser and type the following in the address bar: 192.168.1.1  You should then see your router’s login page. Log in using the default credentials. Then head to the “change password” section and type in a new password. Read the guidelines for the password as mentioned in the manual. Also opt for strong wireless security standards like WPA-2 and AES.

Use strong passwords

Users tend to use a common password across services. If even one of those services is hacked, then the user’s account on the other services becomes vulnerable. So, maintain different passwords.

According to Microsoft, 30 percent of reused or modified passwords can be cracked within just 10 guesses.

If the browser (or an extension) offers to “remember” passwords, decline that request. Should you opt for a password manager then do keep a different master password.

When creating a new password, do not include a complete word in the password string. Hackers use password dictionaries that run multiple word combinations until the real password is matched. This is called “brute force” hacking. Passwords should be a minimum of 8 characters. Use a mix of upper- and lower-case letters, numbers and special characters.

And if the service offers the option for password thresholds, then use it. That’s the number of tries you can attempt for entering a password. Notice that online banking services already enforce this. If you forget your password and enter it wrong three times, you are locked out of your bank account. A call to your bank, with authentication checks will reset the password. But that’s a process implemented by the bank. Windows 10  also offers account lockout thresholds.

Use multi-factor or two-factor authentication

Email services like Gmail offer multi-factor authentication and two-factor authentication (2FA) for verification, but few Gmail users make use of this feature.

A Google report in 2018 suggested that less than 10% of Gmail users employ two-factor authentication, which is considered one of their best security features.

An organization can also set two-factor authentication for services on the company portal, or for corporate email.

With 2FA, you can opt to receive an SMS code on your mobile device whenever you try to log in. Gmail also lets you use one of your devices for authentication. For instance, you can tap your mobile phone screen (Push to Verify) after receiving an authentication message from Google. A third way is to use a hardware token like Google Titan Security Key or Yubikey (Yubico). And a fourth method is to use an authentication app like Google Authenticator. There are other methods for 2FA and it depends on what the service offers. Even social media sites like Twitter, LinkedIn and Facebook offer multi-factor authentication. Banks have enforced 2FA for many years (mainly through hardware tokens).

Secure mobile devices

There are four main things to secure: the mobile OS, the apps, the data and the device itself (physical security). Potential threats include data theft, stolen user credentials, malicious apps, inadequate user configurations, security vulnerabilities in the mobile OS and apps – and stolen devices.

You’d be shocked to learn about the things mobile malware can do – a hacker can activate your phone’s microphone and eavesdrop on conversations, for instance.

To secure the apps and the OS, update these often. Download apps only from authorized marketplaces (Google Play Store or Apple App Store). And ensure that the apps are verified (look for the “Verified by Google Play Protect” badge on the Play Store when downloading apps for Android phones). You can also scan all your installed apps later to verify them.

Don’t try to jailbreak your Apple phone or “root” your Android device. If you do that, the device becomes a threat to the networks and other devices it connects to. Malicious or unauthorized apps set up “backdoors” on jailbroken devices.

Mobile devices do not have firewalls, so install a firewall app (or a mobile security suite) to scan all traffic between the apps and their corresponding servers.

Disable the Bluetooth visibility/discovery mode. Use a Bluetooth PIN when pairing your phone with another user’s phone in public. And keep a watch on all the devices that have paired with your phone via Bluetooth. Remove old or unknown devices from the list.

Backup your contacts and data to an online service like Google Drive, Apple iCloud, or Microsoft Onedrive.

Physical security – Your mobile phone and laptop are likely to contain important data related to your work, your company’s policies, product information, email, customer data and other sensitive data.

To protect mobile phones, note down the IMEI number and install a SIM Lock (ask your service provider about this). Also, enable the device tracking feature – for Apple devices it is Find my iPhone and for Android, it is Android Device Manager. Encrypt your phone by putting a screen lock and enabling the encryption features.

For laptops, encrypt the drive using Bitlocker (Windows) or FileVault (Apple). Store the recovery key outside the device (on a pen drive or online).

Conclusion

Data security is a shared responsibility — both the employee and the organization are custodians of an organization’s data. Employees working from home need to take adequate steps, like those described in this article, to protect data and endpoints. There are other security measures to be taked, such as operating system and application security, both of which will be discussed in the next article. Meanwhile, stay indoors and stay safe.

Part-2: Application and OS Security

Crossword Cybersecurity Partners with Satisnet for Rizikon Assurance

Abnormal Security Partners with Microsoft to Boost Cybersecurity

Security firm Crossword Cybersecurity announced its collaboration with managed security services provider Satisnet Ltd., as part of the expansion of Crossword’s partner program. The new partnership allows Satisnet to help its customers take control of third-party risks by using Crossword’s Rizikon Assurance third-party risk management platform.

Crossword Cybersecurity develops university research-based cybersecurity and risk management related software and consulting services.

Satisnet focuses on leveraging technologies that enable cybersecurity to evaluate and keep pace with evolving threats. The company delivers security services including SIEM, threat hunting, incident response, detection & response, vulnerability and patch management from its Security Operations Centers.

Sean Arrowsmith, Group Sales Director at Crossword Cybersecurity, said, “Rizikon Assurance compliments Satisnet’s existing portfolio and will allow their clients to really take control of their supply chain assurance programs.”

U.K.’s Cybersecurity Industry worth £8.3 Billion

According to the U.K.’s Department for Digital, Culture, Media, and Sport (DCMS), the number of active cybersecurity firms in the country increased by 44%, up from 846 firms in 2017 to over 1,200 in 2019, indicating a growth in the cybersecurity industry. In its report, “The U.K. Cybersecurity Sectoral Analysis 2020”, DCMS stated the security industry in the U.K. seen a significant surge in security investments, annual revenue, and employment. It also highlighted that around 43,000 full-time employees are currently working in the industry.

The annual revenue in the cybersecurity sector rose by 46% to an estimated worth of £8.3 billion (approximately US$10.8 billion). The sector received more than £348 million (approximately US$452.4 million) of investment last year.

“Security has to be intrinsic and baked in at the time the application is born”

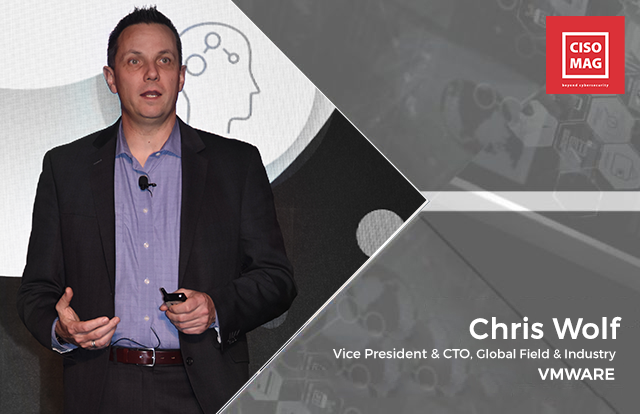
Chris Wolf, Vice President, and CTO, Global Field & Industry, VMware

Chris Wolf serves as CTO, Global Field, and Industry at VMware. In that role, he is responsible for shaping VMware’s long-term technology vision while ensuring that Research and Development priorities align with customer and industry needs. Wolf’s team drives thought leadership and industry alignment in a number of emerging areas, including cloud, Edge, IoT, server platforms, HPC, and NFV. Chris also leads VMware’s 140+ member CTO Ambassador program, which further scales VMware R&D to customers and the technology community at large.

Prior to joining VMware, Chris was a Research Vice President for Gartner’s Technical Professionals service where he managed the data center and private cloud research agenda. Before that, Chris was a founding member of the Data Center Strategies team at Burton Group, an independent virtualization consultant. Wolf holds a Master of Science degree in Information Technology from the Rochester Institute of Technology and has authored several technology books.

Brian Pereira, Principal Editor, CISO MAG met Wolf to discuss how the Carbon Black acquisition will strengthen the security of VMware’s offerings. Carbon Black is a leading cloud-native endpoint protection vendor and was on Gartner’s magic quadrant 2019 as a Visionary company for endpoint protection. Post the acquisition, we will see Carbon Black’s security technology integrated into VMware’s security products and platforms.

Wolf told us that on average, every week, the VMware R&D team is provisioning 500,000 containers and more than one million VMs. With that level of agility, security has to be part of the CI/CD (Continuous Integration Continuous Delivery) pipeline, he says.

Wolf talked about the emergence of intrinsic security models. Security has to be built into the application at the very beginning, he insists–and not done as an afterthought.

Excerpts from the interview follow: 

How is the approach to security changing today? Why is the old approach inadequate to counter the volume and sophistication of today’s threats? 

There’s recognition from our CISOs and security leaders that the security fabric needs to be more dynamic than the threats we face. Our threats are highly sophisticated and continually evolving every second. There’s a recognition that we have to invest in new ways of doing things.

Enterprises need to invest in transformational architectures–they can start with a greenfield project, build new skills internally, and train their staff on new ways to operate security, which is purely software-defined.

At VMware, we believe that security has to be intrinsic and baked in at the time the application is born. On average every week, our R&D team is provisioning 500,000 containers and more than one million VMs. With that level of agility, security has to be a part of the CI/CD (Continuous Integration Continuous Delivery) pipeline. It can’t be something that is done as a manual process. It has to be ingrained in the DevOps processes.

The current approaches to security are unsustainable, costly, impractical, and not as efficient as they should be.

What can we expect in 2020? How will the cyberthreat landscape evolve? What are the new attacks that we should expect? How should we be preparing?

The problem is going to get worse. The proliferation of ransomware is becoming an increasing problem as well. I think 2020 becomes a transitional year for security. We’ll see organizations start to move towards far more scalable and dynamic architectures and new ways to solve problems.

If you start with network security–today for securing a packet, that packet is passing through a firewall, it is getting inspected, and there are multiple layers; there’s multiple places where that packet is being routed to be inspected, and there could be a policy applied.

We flip that model–now the actual server that’s running the application is scaling out and doing all of that work. So it looks at the packet one time and it can apply network policy, security policy, firewall policy–all with a single pass of that packet. That’s a far more scalable architecture. The notion of having these physical taps on the network goes away.

Today, if you write the firewall rules, it is independent of the application. In many cases, the application might retire, and the firewall rules might persist–depending how strong the process and automation might be.

So, security becomes an attribute of the application. That’s far more intrinsic than what you had today.

It means that 2020 is the time when enterprise customers start to invest in architectures that support these intrinsic security models.

We don’t assume that enterprises are going to replace their existing fabric. But they can take a few greenfield applications and start to apply these models and train their teams to operate them. We expect to see significant investments in that space in 2020.

We have apps everywhere today and on different clouds. How does one reduce the attack surface, understanding application behavior? The whole security paradigm changes when you move from client-server to the cloud. 

We provide a significant amount of context around the application with our AppDefense technology. We can understand how the application accesses the processor and what processes the application spins up or how it is accessed in physical memory. What is the app writing to the file system? What is the app trying to do over the network?

By creating all this context around the application, we can understand how the application is supposed to behave. And in doing so, we can then create a security policy and firewall rule that distinguishes a known state of the application. When I see anomalies or deviations to that known state, I am going to act. This is how you counter a zero-day attack.

By having that end-to-end context of the application, we can start to do far more interesting things from a security perspective.  

What trends are you seeing in the adoption of endpoint security solutions?

We’re seeing significant traction in terms of organizations looking for holistic solutions rather than pieces and parts. A good example of that is Workspace ONE. If we went back a few years ago, we saw many of our customers trying to piece these parts together themselves, and we’ve seen a significant trend heading in the other direction over the last 18 months. Organizations can now have access management across all the different services and can connect their end-users from a single console.

How will the acquisition of Carbon Black help VMware become a security leader? And how will you integrate Carbon Black technology into VMware products and platforms?

With Carbon Black coming into the fold, we have formed a new security business unit. We see forces come together–Workspace ONE, Trust Network API sets. We have a number of leading security vendors that have already committed to providing feeds into that platform. We are trying to enforce conditional access policy, and we need to understand all the context right from all of the different security feeds, inclusive of the ones that aren’t related to VMware or Carbon Black.

So that’s really the key in terms of getting all of these data sources into the platform and then being able to do actionable automation based on the feeds from those sources.

The second part of the strategy, which is really important, is baking this technology into our vSphere hypervisor (ESXi). So now our security stack is going to be a part of VMware tools that gets installed with every virtual machine. This gives us a way to do true agentless security across our entire portfolio.

From a customer perspective, you are going to have an end-to-end view of security policy. And we have an end-to-end way to enforce the policy–from the application running on the server all the way up to the endpoint.

Data Breach Exposes 14 Million Key Ring Users Data

70 Mn Records Exposed After AFL Fan Website Leaks Users’ Data

Key Ring, a digital wallet application provider, is the latest victim of a data breach that exposed nearly 14 million Key Ring app users’ data.  Security researchers Noam Rotem and Ran Locar from vpnMentor found a misconfigured Amazon Web Services (AWS) S3 bucket, owned by Key Ring, that holds users’ personal details. The researchers stated that most of the exposed information belongs to users across North America.

The Key Ring application enables users to upload and save photos/scan copies of membership and loyalty cards to a digital wallet in their smartphones.  The exposed personal data included government IDs, NRA membership cards, medical marijuana ID cards, credit card numbers, CVV numbers, and medical insurance cards.

Other information exposed in the data leak included CSV files of membership lists for North American retailers which contained the personally identifiable information (PII) data of millions of people. It’s also discovered that over 44 million images uploaded by Key Ring users were also exposed in the incident. Companies whose customers’ data exposed in the data leak include Walmart, Foot Locker Kleenex, La Madeleine Bakery, and Mattel.

vpnMentor stated that it discovered the data leak in January 2020, and immediately contacted Key Ring officials. The database is now secured.

“We can’t confirm how long the buckets were open, but the first was picked up by our web scanning tools in January. At the time, we were undertaking numerous investigations into other data leaks and had to complete these before we could analyze Key Ring’s S3 buckets. Once the details of the leak were confirmed, we immediately contacted Key Ring and AWS to disclose the discovery and assist in fixing the leak. The buckets were secured shortly after,” the researchers said in a statement.

In a similar database leak incident, thousands of baby videos and images were being left unsecured and exposed online by a mobile app called Peekaboo Moments. Peekaboo’s app developer, Bithouse, left the Elasticsearch database open and without password protection. The database contained more than 70 million log files comprising nearly 100 GB data stored from March 2019. The exposed data includes detailed device data, links to photos and videos, and around 800,000 email addresses.

Peekaboo stated that it’s still unclear for how long the server has been exposed to the data and who might have accessed it. The data breach news comes even after Peekaboo Moments promised to safeguard the data and information it stores.

67% Victims Paid Ransom to Recover Encrypted Data: Cyberthreat Defense Report

Ransomware Attacks, Graff ransomware attack

Hackers are more encouraged than ever, and the number of ransomware attacks is increasing. That’s because more victims are willing to pay the ransom to recover their encrypted data, new research shows.

According to Cyberthreat Defense Report (CDR) from the security firm CyberEdge Group, only 49% of ransom payers recovered their data in 2018, which rose to 61% in 2019. At present, around 67% of ransomware victims have reported that they’ve recovered their encrypted data by paying ransom.

The report also found an increase in ransomware victims who are willing to pay hackers’ demands to recover their data. It stated that 39% of ransomware victims actually paid ransom in 2018, which rose to 45% in 2019. Today, a startling 58% of ransomware victimized companies have paid ransoms.

It also revealed that data recovery rates for ransom payers have increased, which in turn stimulated ransomware attacks. The report said that, in 2019, 56% of organizations were affected by ransomware attacks, which are now increased to 62%.

Steve Piper, Founder and CEO of CyberEdge Group, said, “This year, both good news and bad news are stimulating growth of the multi-billion-dollar ransomware industry. To combat ransomware and other threats, I advise IT security organizations to invest wisely in products that continuously discover and patch vulnerabilities, uncover advanced threats using machine learning and artificial intelligence, and continuously back up their data everywhere. I also recommend organizations invest more in their people, including training and certification for IT security personnel and ongoing security awareness training for all employees. Never underestimate the value of the human firewall.”

New Bill to Ban Ransomware Payments

Recently, two senators of New York, Republican NY Senator Phil Boyle and Democrat NY Senator David Carlucci, proposed two bills to ban government agencies and local municipalities from using public money for paying ransomware to cybercriminals. Apart from ransomware payments, the proposed bills also recommended the creation of a state fund to aid government entities improve their cybersecurity capabilities. Several industry experts opined that this is the first time the state authorities have proposed a law that bans paying the ransom.

NCSC Appoints IASME as the Sole Cyber Essentials Certification Body in the U.K.

UK Government, NCSC

With a view to streamline the customer experience and improve consistency throughout, U.K.’s  NCSC (National Cyber Security Centre) has announced a partnership with the IASME Consortium making it the sole certifying body for Cyber Essentials Certification. The changes came into effect on April 1, 2020.

Since its inception in 2014, the Cyber Essentials Scheme has helped protect over 34,000 U.K. businesses from the most common cyber and commodity threats. Initially there were multiple accreditation bodies and their respective certification bodies, however, this hampered customer experience and consistency. Thus, after holding a tender process, the NCSC zeroed onto a single Cyber Essentials Partner – The IASME Consortium.

What’s Cyber Essentials?

Cyber Essentials is a Government-backed scheme designed to protect organizations of various domains and sizes (small, medium and large) against a host of most common cyberattacks. As per the NCSC, these cyberthreats come in varied shapes and sizes, but most of them are very basic in nature. Cyber Essentials helps protect and prevent these basic attacks with its two levels of certifications, Cyber Essentials and Cyber Essentials Plus. The Cyber Essentials group stresses that the cybersecurity of any organization depends on the implementation of five key technical controls:

  • Firewall usage to secure internet gateways
  • Using best-suited security configurations and settings for all your devices and software
  • Have access control. Implement RBAC to control your data and services more efficiently
  • Use anti-virus and anti-malware software and applications to better protect your devices and corresponding networks
  • Regularly check and update your devices and software to protect against the latest form of common cyberthreats

Cyber Essential Certificate: A Cybersecurity Badge

This certificate scheme most importantly acts as a certified cybersecurity badge. It assures customers that you take your own and their IT security seriously. This attracts new businesses and helps you gain insights over your organization’s cybersecurity posture. Moreover, if your organization is involved or planning to bid for central government contracts across various government departments, which involves handling sensitive and personal information or the provision of certain technical products and services, then you will mandatorily require Cyber Essentials Certification.

Japan Embraces AI Tools to Fight Cyberattacks with US$237 Million Investment

Japan restricts foreign equipment and tech, Japan Embraces AI Tools to Fight Cyberattacks with US$237 mn Investment

Japan’s Ministry of Defense (MoD) confirmed that it’s going to invest nearly ¥25.6 billion (approximately US$237.12 million) to develop AI-based security tools to defend cyberattacks. In addition, the MoD also dedicated ¥30 million (approximately US$277,711) to build a Cyber Information Gathering System, which gathers information on the tactics, techniques and procedures (TTPs) of cyberattacks on government and private entities in the country, expand the Cyber Defense Group from 220 to 290 personnel; and perform research on cybersecurity measures for network devices used by the Japanese military. The Cyber System is intended to detect malicious emails and respond to cyberattacks automatically through machine learning skills.

Industry experts opined that the Government of Japan started this initiative in the wake of a massive cyberattack on Mitsubishi Electric by a hacking group, named Tick, from China. It’s said that Tick was active for a long time and is known for stealing sensitive data from the defense, aerospace, chemical, and satellite industries in Japan and China.

After Mitsubishi disclosed the attack on January 20, 2020, the Japanese MoD announced that defense-related sensitive data may have been breached. Information related to bidding for contracts on defense equipment research, including evaluation criteria and required performances may have leaked in the incident. According to the MoD, Mitsubishi converted the Government’s paper documents into PDF files and kept them on its internal network, even though it was not permitted to do so.

In order to prevent such data breaches in the future, the Government has now initiated additional cybersecurity infrastructure to thwart security incidents from local and foreign threat actors.

Cyberattacks  on Japan’s Defense Secrets

On January 31, 2020, NEC Corp., a Japanese IT and electronics company, accepted a data breach and stated that its network was penetrated and compromised to a cyberattack that occurred in December 2016. The attack was spotted in June 2017, following which all unauthorized communications were blocked by the IT teams. The encrypted communication information between the compromised server and the external exfiltration server was finally decrypted in July 2018 and it was found that the defense business division’s 27,445 files were accessed illegally.

Recently, Pasco Corp. and Kobe Steel, rendering services to the Japanese armed forces, disclosed a possible data breach that occurred in June 2015, followed by a second attempt in August 2016.