Home Blog Page 198

3 Signs That Your Company Has A Security First Mindset

cloud, cloud security

As organizations consider moving to the cloud or architecting their applications in the cloud, security is top of mind. In the June 2020 cloud security survey, 68% of respondents stated that security, privacy, and compliance should be built in as foundational principles when migrating to the cloud. This finding is consistent with the rise of DevSecOps over the past couple of years and the “shift security left” mindset.

By AJ Yawn, Cloud Security Expert

This finding from the survey may sound a lot like DevSecOps, a concept in the security industry that is gaining more and more traction as teams embed security into the software development lifecycle. DevSecOps is Security + DevOps (Development + Operations) running together as a single, cohesive unit. The underlying principle of DevSecOps is to unite security teams and application developers, creating a collaborative environment where security is a shared responsibility in the continuous integration/continuous deployment (CI/CD) pipeline. DevSecOps is often focused on adding new security tools to integrate security in the software development lifecycle. The DevSecOps mentality does not have to be restricted to just the development teams, this mentality shows itself through three cultural security shifts in organizations.

Integrating Security Early

As security practitioners, we should aim to add security as a cohesive component of every part of the organization. The results of this survey show that technologists understand the benefits of integrating security and privacy at the beginning of the cloud migration process. Early inclusion of security and privacy will ensure infrastructure choices, availability planning, and compliance risks are examined before any business decisions are made.

It can be argued that cloud migration should not be the trigger to integrate security as an integral part of all organizational processes. Adopting a security-first culture allows organizations to implement the DevSecOps culture whether they are migrating to the cloud or not. There are a couple of actions that organizations can implement to ensure that security, privacy, and compliance are embedded in all organizational processes.

Making Security Everyone’s Responsibility

One of the reasons organizations implement DevSecOps is to prevent a security incident or event from occurring. DevSecOps is a cultural shift, not just a series of tasks or checkboxes to complete as you move through your CI/CD pipeline. This requires organizations to adopt the mind of a security practitioner which means everyone in the organization acknowledges that it is not a matter of if a vulnerability or flaw will be identified, but a matter of when. Assuming you will be breached or hacked changes the conversation internally and influences decision making on tools, technologies, and migration strategies. This shift in thinking will encourage security-conscious individuals outside of the security team to look forward to finding flaws and reporting them to the security team.

The development and growth of security-conscious employees in every department is an indicator of a strong security culture.

A security-first culture eliminates the blame game from cybersecurity-related issues and encourages a culture of fact-finding, issue-spotting, and investigation. We are no longer asking “who wrote this code?” when a vulnerability is discovered. This cultural shift means we are now asking:

  1. How do we fix this?
  2. How do we stop this vulnerability from occurring in the future?
  3. Can we automate the fix?

Those questions are application security specific however it is important to reiterate this is much more than just securing your application and integrating security tools into your CI/CD pipeline. A cultural shift involves all employees and departments considering the security implications of their processes and actions. For example, in a mature cybersecurity environment, the human resources (HR) team is educated on the implications of onboarding processes and procedures on your cybersecurity compliance assessments. This understanding facilitates an open line of communication between HR reps and security team members. This open line of communication facilitates collaboration on potential solutions that can alleviate the manual aspect of HR teams monitoring and proving compliance with cybersecurity regulations and frameworks. With the end goal of an automated security and compliance monitoring process that ensures new hires are onboarded according to your applicable compliance standards (i.e. background checks performed, access request created, security awareness training completed, etc.).

Automating Everything

Security automation has become increasingly important due to the thousands of threats facing organizations daily. It is virtually impossible to manually identify, protect, detect, respond, and recover to security events or incidents.

Automation will not work without a deep understanding of the business processes and risks security professionals are trying to automate. For this reason, the cultural shift described above is imperative to begin before implementing automation strategies. Automation makes security easy and reduces the burden on understaffed and under-resourced security teams.

When considering automation strategies, security practitioners must adapt security to the business processes and not expect business units to adapt to security. Security must remain an enabling function not a blocking function for automation to work. Security in the cloud requires and encourages automation of key security controls.

As organizations undergo annual compliance assessments, they should aim to make security controls programmable and automated wherever possible. Multifactor authentication (MFA) flaws and public storage services (specifically AWS S3 buckets) are two common risks facing organizations that would best be addressed through automation. For example, on AWS a simple, automated Force MFA and S3 Bucket Security configuration would significantly reduce two key security risks facing the organization without requiring the security team’s manual intervention.

An “automate everything” mentality encourages your organization and security professionals to consistently identify simpler and better ways to perform key functions.

Making Security Easy

Implementing security, privacy, and compliance earlier in the process for all projects, including cloud migrations, makes security easier for everyone involved. It makes sense that over two-thirds of survey respondents believe this is a top security concern when migrating to the cloud. It also makes sense to begin taking the initial steps to integrate security within your overall organizational culture encouraging a relentless focus on automating security.

About the Author
AJ Yawn, Cloud securityAJ Yawn is a cloud security subject matter expert that possesses over nine years of senior information security experience and has extensive experience managing a wide range of compliance assessments (SOC, ISO 27001, HIPAA, etc.) for a variety of SaaS, IaaS, and PaaS providers. He has earned several industry-recognized certifications, including the CISSP, AWS Certified Security Specialty, AWS Certified Solutions Architect-Associate, and PMP. AJ is involved with the AWS training and certification department, volunteering with the AWS Certification Examination subject matter expert program.

Disclaimer

CISO MAG did not evaluate/test the products mentioned in this article, nor does it endorse any of the claims made by the writer. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same. CISO MAG does not guarantee the satisfactory performance of the products mentioned in this article.
50% of Users Online Fall Victim to Cyberattacks: Report

cyberattacks on U.S. and U.K., Barnes & Noble cyberattack, zero trust

Threat actors are using sophisticated hacking methods to target users online. It’s not just about taking advantage of Coronavirus-related anxieties, but attackers are using every single opportunity to steal personal and financial information from users online. According to a NordLocker cybersecurity survey report, 50% of computer users admitted that they have fallen victim to cybercrimes, with virus attacks, phishing scams, and stolen passwords reported as the most common security incidents. The report revealed that 55% of Britishers and 67% of Americans have fallen prey to malicious cyber activities while using their connected devices.

According to the survey, 33% of respondents in the U.K. suffered malware attacks compared to 46% of respondents in the U.S. Nearly, 20% of respondents in the U.K admitted that they fell victim to email scams, while 32% respondents  in the U.S. admitted the same. 14% of the respondents in the U.K., compared to 23% of U.S. respondents, claim to have had their passwords stolen.

“In the U.S., less than half (45%) of computer users don’t share their personal computers. In comparison, the number is slightly higher (49%) in the U.K. However, 52% of users in the U.S. and 50% in the U.K. do use a computer that’s also used by someone else. This is usually a spouse (around 40% in both countries), children (around 20%), parents (6%), and coworkers (3%). Only 3% of respondents said they used a public computer,” the report stated.

“The two countries are quite different when it comes to tax records. The American tax filing system requires individuals to store their tax information, causing 33% of users in the U.S. to store this information on their personal computers. In comparison, it’s only 17% in the U.K. The users in the U.S. also store more medical records (23%), compared to the U.K.’s 15%,” the report added.

U.S. and U.K. Jointly Fight Cyberthreats

Cybersecurity officials in the U.K. National Cyber Security Centre (NCSC), the U.S. Department of Homeland Security (DHS), and the Cybersecurity and Infrastructure Agency (CISA) stated that cybercriminals and advanced persistent threat (APT) groups are targeting individuals and organizations with a variety of ransomware and malware attacks, thereby exploiting the COVID-19 outbreak for their personal gain. The security agencies have released a joint advisory describing the growing number of attackers and other malicious groups in the U.K. and the U.S.


An Organization’s Ability to Contain a Cyberattack has declined by 13% Over 5 years: IBM Study

median dwell time, Supercharged AI Cyberattacks are Unavoidable

IBM Security today announced the results of a global report examining businesses’ effectiveness in preparing for and responding to cyberattacks. While the organizations surveyed have slowly improved in their ability to plan for, detect and respond to cyberattacks over the past five years, their ability to contain a cyberattack has declined by 13% during this same period. The global survey conducted by Ponemon Institute and sponsored by IBM Security found that respondents’ security response efforts were hindered due to the use of too many security tools, as well as a lack of specific playbooks for common attack types.

While security response planning is slowly improving, the vast majority of organizations surveyed (74%) are still reporting that their plans are either ad-hoc, applied inconsistently, or that they have no plans at all. This lack of planning can impact the cost of security incidents, as companies that have incident response teams and extensively test their incident response plans spend an average of $1.2 million less on data breaches than those who have both of these cost-saving factors in place. IBM Security and Ponemon Institute: 2019 Cost of a Data Breach Report

The key findings of those surveyed from the fifth annual “Cyber Resilient Organization Report” include:

Slowly Improving:  More surveyed organizations have adopted formal, enterprise-wide security response plans over the past 5 years of the study; growing from 18% of respondents in 2015, to 26% in this year’s report (a 44% improvement).

Playbooks Needed: Even amongst those with a formal security response plan, only one third (representing 17% of total respondents) had also developed specific playbooks for common attack types — and plans for emerging attack methods like ransomware lagged even further behind.

Complexity Hinders Response: The amount of security tools that an organization was using had a negative impact across multiple categories of the threat lifecycle amongst those surveyed. Organizations using 50+ security tools ranked themselves 8% lower in their ability to detect, and 7% lower in their ability to respond to an attack, than those respondents with less tools.

Better Planning, Less Disruption: Companies with formal security response plans applied across the business were less likely to experience significant disruption as the result of a cyberattack. Over the past two years, only 39% of these companies experienced a disruptive security incident, compared to 62% of those with less formal or consistent plans.

“While more organizations are taking incident response planning seriously, preparing for cyberattacks isn’t a one and done activity,” said Wendi Whitmore, Vice President of IBM X-Force Threat Intelligence. “Organizations must also focus on testing, practicing, and reassessing their response plans regularly. Leveraging interoperable technologies and automation can also help overcome complexity challenges and speed the time it takes to contain an incident.”

Updating Playbooks for Emerging Threats

The survey found that even amongst organizations with a formal cybersecurity incident response plan (CSIRP), only 33% had playbooks in place for specific types of attacks. Since different breeds of attack require unique response techniques, having pre-defined playbooks provides organizations with consistent and repeatable action plans for the most common attacks they are likely to face.

Amongst the minority of responding organizations who do have attack-specific playbooks, the most common playbooks are for DDoS attacks (64%) and malware (57%). While these methods have historically been top issues for the enterprise, additional attack methods such as ransomware are on the rise. While ransomware attacks have spiked nearly 70% in recent years, IBM Security, 2020 X-Force Threat Intelligence Index, (2020), p. 15 only 45% of those in the survey using playbooks had designated plans for ransomware attacks.

Additionally, more than half (52%) of those with security response plans said they have never reviewed or have no set time period for reviewing or testing those plans. With business operations changing rapidly due to an increasingly remote workforce, and new attack techniques constantly being introduced, this data suggests that surveyed businesses may be relying on outdated response plans which don’t reflect the current threat and business landscape.

More Tools Led to Worse Response Capabilities

The report also found that complexity is negatively impacting incident response capabilities. Those surveyed estimated their organization was using more than 45 different security tools on average, and that each incident they responded to required coordination across around 19 tools on average. However, the study also found that an over-abundance of tools may hinder organizations ability to handle attacks. In the survey, those using more than 50 tools ranked themselves 8% lower in their ability to detect an attack (5.83/10 vs. 6.66/10), and around 7% lower when it comes to responding to an attack (5.95/10 vs. 6.72/10).

These findings suggest that adopting more tools didn’t necessarily improve security response efforts — in fact, it may have done the opposite. The use of open, interoperable platforms as well as automation technologies can help reduce the complexity of responding across disconnected tools. Amongst high-performing organizations in the report, 63% said the use of interoperable tools helped them improve their response to cyberattacks.

Better Planning Pays Off

This year’s report suggests that surveyed organizations who invested in formal planning were more successful in responding to incidents. Amongst respondents with a CSIRP applied consistently across the business, only 39% experienced an incident that resulted in a significant disruption to the organization within the past two years compared to 62% of those who didn’t have a formal plan in place.

Looking at specific reasons that these organizations cited for their ability to respond to attacks, security workforce skills were found to be a top factor. 61% of those surveyed attributed hiring skilled employees as a top reason for becoming more resilient; amongst those who said their resiliency did not improve, 41% cited the lack of skilled employees as the top reason.


RELATED STORY

Rushing to the Cloud to Support Remote Workers Poses New Security Risks: IBM Study


Technology was another differentiator that helped organizations in the report to become more cyber resilient, especially when it comes to tools that helped them resolve complexity. Looking at organizations with higher levels of cyber resilience, the top two factors cited for improving their level of cyber resilience were visibility into applications and data (57% selecting) and automation tools (55% selecting). Overall, the data suggests that surveyed organizations that were more mature in their response preparedness relied more heavily on technology innovations to become more resilient.

About the Study- Conducted by the Ponemon Institute and sponsored by IBM Security, the 2020 Cyber Resilient Organization Report is the fifth installment covering organizations’ ability to properly prepare for and handle cyberattacks. The survey features insight from more than 3,400 security and IT professionals from around the world, including the United States, India, Germany, United Kingdom, Brazil, Japan, Australia, France, Canada, ASEAN, and the Middle East.

Review the full report here: https://www.ibm.com/account/reg/us-en/signup?formid=urx-45839

California Consumer Privacy Act Puts Additional Pressure on Financial Organizations

California Consumer Privacy Act, Hanna Andersson to Pay $400K to Settle CCPA-related Class-Action Lawsuit

A survey from cybersecurity firm Netwrix revealed that the execution of the California Consumer Privacy Act (CCPA) will put additional pressure on IT resources and expenses, and especially on financial organizations. The survey “2020 Data Risk & Security Report” stated that 32% of financial organizations witnessed an increase in data subject access rights requests (DSARs) since the CCPA came into effect, which was on January 1, 2020.

According to the survey, nearly 73% of financial organizations are already under pressure to satisfy data subject rights requests, and 27% of them reported these requests have increased their expenses. It takes more than two weeks for organizations to fulfill a single data subject request and costs an average of $1,400, if done manually. This brings many financial organizations to put additional workforce and budget to ensure compliance with the CCPA.

“Organizations are investing more than ever in cybersecurity, yet data breaches and other security incidents are continuing to increase in both number and size. First, while security professionals successfully mitigate security issues at some of the six stages of the data lifecycle, they often overlook other stages, leaving their organization’s content vulnerable. In addition, security professionals generally know very little about what data they have, how sensitive it is, where it is stored, and who has access to it,” the report said.

Other findings from the research include:

  • 33% of financial organizations discovered sensitive or regulated customer data outside of designated secure locations.
  • 40% of respondents admitted their IT teams granted direct access to sensitive data based solely on a user’s request in the past 12 months.
  • 75% of financial organizations that classify data can detect data misuse in minutes, while those who don’t usually need days (43%) or months (29%).
  • 61% of organizations that are subject to the GDPR collect more customer data than the law permits.
  • 54% of organizations ignore the security best practice of reviewing access rights to data on a regular basis.
  • 70% of incidents of unauthorized data sharing within this vertical led to data compromise.
  • 44% of CISOs and CIOs don’t have or don’t know whether they have KPIs for IT security and risk.

Steve Dickson, CEO of Netwrix, said, “While organizations are unlikely to be flooded with data subject access requests on July 2, they do need to be prepared to process requests accurately and promptly. One missed deadline or incompletely fulfilled request could result in a thorough audit from the authorities and sizable fines. To ensure compliance while controlling costs and relieving the burden on IT, financial organizations need to automate the DSAR process.”


U.K.’s Computer Misuse Act Turns 30; Security Professionals Call For Reform

Computer Misuse Act

A coalition of cybersecurity businesses and professionals in the U.K.  wrote a letter to the Prime Minister Boris Johnson urging him to reform the Computer Misuse Act 1990 (CMA). The coalition includes major cybersecurity firms like NCC Group, F-secure, McAfee, and Trend Micro, international accreditation body CREST, and several leading lawyers in the field came together to urge the Prime Minister for cybersecurity law reforms.

What is the Computer Misuse Act?

The Computer Misuse Act (CMA) 1990 came into effect 30 years ago to prevent computer hacking before the emergence of the internet and the concept of cybersecurity. Industry experts stated that Section 1 of the CMA prevents unauthorized access to computers and unintentionally criminalizes cybersecurity researchers and their investigations.

Letter to Prime Minister

The letter published by CyberUp,  a campaign working towards cybersecurity reforms in the U.K., stated that the outdated CMA prevents security researchers from finding out malicious activities.

“In 1990, when the CMA became law, only 0.5% of the U.K. population used the internet, and the concept of cybersecurity and threat intelligence research did not yet exist. Now, 30 years on, the CMA is the central regime governing cybercrime in the U.K. despite being originally designed to protect telephone exchanges. This means that the CMA inadvertently criminalizes a large proportion of modern cyber defense practices. In particular, Section 1 of the Act prohibits the unauthorized access to any program or data held in any computer and has not kept pace with advances in technology,” the letter stated.

“With the advent of modern threat intelligence research, defensive cyber activities often involve the scanning and interrogation of compromised victims’ and criminals’ systems to lessen the impact of attacks and prevent future incidents. In these cases, criminals are obviously very unlikely to explicitly authorize such access,” the letter added.

Earlier, a joint research by Criminal Law Reform Now Network (CLRNN), scholars from Birmingham and Cambridge universities stated that the U.K.’s CMA needs an update, as it has jeopardized the country’s cybersecurity. The research report, “Reforming the Computer Misuse Act” revealed how the CMA is preventing security professionals from performing threat intelligence researches. It also stated that the Act restricts journalists and scholars from researching potential cyberthreats.


Cyber Warfare: The Battle Tact of the Digital Age

cyber warfare, cyber warfare whitepaper

Border disputes between countries are common these days. But these very countries engage in another kind of warfare, where there are no “boots on the ground” planes in the air or warships in the sea. Instead, it’s a war that involves different kinds of soldiers and spies – all highly adept in computer and cybersecurity skills. This “cyber army” has a mission to “attack” the information assets of the “enemy” – to take down servers belonging to governments and private organizations and destabilize the economy. They look for state secrets stored in digitized form. And they are trained to launch cyberattacks with a different type of weaponry – hacking tools and technologies.  The threat actors and the attack surfaces have evolved, expanded, and now replace traditional combat warfare with a new tack – the age of  Cyber Warfare.

SPONSORED CONTENT

The ethics of cyberweapons used in warfare has always been a debatable question. People have often downplayed them as benign weapons that do not really have the potential to cause major collateral damage. However, since the turn of the century, a wide range of state actors including the United States, Russia, China, North Korea, Iran, and Vietnam have outgrown their offensive and defensive cybersecurity operations and capabilities. Actors often leverage these cyberthreats to indirectly support more traditional means of warfare like espionage, sabotage, propaganda, etc.

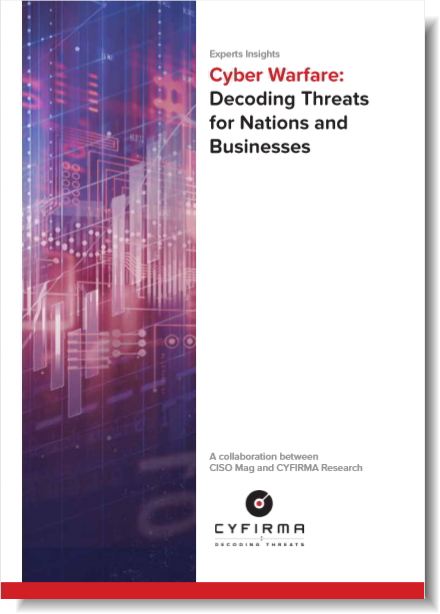
Cyber Warfare, Cyber Warfare WhitepaperA new whitepaper produced by CISO MAG titled “Cyber Warfare: Decoding Threats for Nations and Businesses”, sheds more light on this latest form of warfare and the techniques used. The paper includes the latest case studies relative to the subject and answers FAQs about Cyber Warfare.
Download your copy now to know the underbelly of Cyber Warfare! 

This highly engrossing and informative whitepaper is a collaborative work of industry experts from CYFIRMA and cybersecurity editors at CISO MAG. Their combined effort in bringing out a fact-based and data-backed whitepaper unravels some amazing facts; although there is a country vs country angle to Cyber Warfare, yet enterprises and businesses in these countries are caught in the crosshairs of their respective governments and decision-makers.

CISO MAG editors closely analyze and dissect the latest incidents in the Cyber Warfare space and how threat actors leverage other countries geographical, political, and health emergencies like an epidemic or pandemic to their advantage. Lastly, we introspect the future of Cyber Warfare and how having a cyber threat intelligence helps in not only identifying the threats and respective threat actors but also in gaining an outside-in perspective to your organization’s cyber posture.

Cyber Warfare, Cyber Warfare WhitepaperRead about “Cyber Warfare” and CYFIRMA’s pledge towards protecting your businesses, enterprises, and governments from such attacks.

Australia Fortifies Cyber Defense by Investing in AUSHIELD

Cryptocurrency scams in Australia

Few weeks back, the Australian Prime Minister Scott Morrison briefed the nation about sustained cyberattacks carried out by a sophisticated state-sponsored actor. To fortify the cyberspace, the Australian Cyber Security Centre (ACSC) has been ever since taking counter measures and giving advisories to businesses around the country to defend themselves form cyberattacks. In continuation, Australia has now decided to add yet another defensive shield in the cyberspace–the AUSHIELD.

Cybermerc, the cybersecurity company who developed the Aushield Defend cyberthreat intelligence platform, has secured a $1.22 million funding from AustCyber. Cybermerc plans to use this investment in further developing and implement the Aushield platform in protecting Australian industry, researchers, and academia from cyberattacks. It also plans to partly use these funds towards a TAFE cybersecurity education project, which is a University of Adelaide project to provide schools with cyber resources, and a cyber security job platform.

What is Aushield Defend Platform?

Aushield Defend is a threat sharing platform developed by Cybermerc partnered by the Australian National University, Anomali, Vault Cloud and startups SecureStack and CounterSight. AustCyber, a non-profit organization established by the Australian Government, has recognized its importance in these critical times and under its $15 million quota as Projects Fund, it has further sponsored this threat sharing platform to enable Australian businesses to defend each other.

Aushield Detect and Protect

Aushield has two separate modules – Detect and Protect. Detect is a community of threat professionals and researchers who detect rulesets (STIX/TAXII) and reports concerning specific Malicious Cyber Actors and campaigns. When private businesses subscribe to a STIX/TAXII feed from Aushield Detect, the alerts can be directly integrated with their Intrusion Prevention and Detection Systems. Each industry is encouraged to upload their own STIX/TAXII rulesets for the benefit of the AUSHIELD community.

In the Aushield Protect module, there is a repository that collects data of various cyberattacks and malwares carried out on the worldwide network. This data can then be used by the community subscribers to train their artificial intelligence (AI) engines for future attacks and use machine learning (ML) to test the algorithms and implement them against latest attacks on Australian networks.

Philips Release Patches for Vulnerabilities Affecting its Medical Devices

Medical Devices

Electronics and health technology provider Philips has reported a vulnerability to the Cybersecurity and Infrastructure Agency (CISA) in its ultrasound medical devices, which allows threat actors to take control of the medical devices, remotely.

In an official statement, CISA stated that the vulnerability “CWE-288” was identified in Ultrasound ClearVue, Ultrasound CX, Ultrasound EPIQ/Affiniti, Ultrasound Sparq, and Ultrasound Xperius devices. “Successful exploitation of this vulnerability may allow a non-authenticated attacker to view or modify information. An attacker may use an alternate path or channel that does not require authentication of the alternate service login to view or modify information,” CISA said in a statement.

Mitigation

Philips corrected the flaws for Ultrasound EPIQ/Affiniti Version VM6.0 and is planning to release patches for Ultrasound ClearVue Version 3.3, Ultrasound CX Version 5.0.3, and Ultrasound Sparq Version 3.0.3 in Q4 2020.

To mitigate the risk of exploitation of the vulnerability, CISA recommends a few  preventative measures, these include:

  • Implement physical security measures to limit or control access to critical systems
  • Restrict system access to authorized personnel only and follow a least privilege approach
  • Apply defense-in-depth strategies
  • Disable unnecessary accounts and services
  • Where additional information is needed, refer to existing cybersecurity in medical device guidance issued by the FDA

Health Care Devices at Cyber Risk

A research from Atlas VPN revealed that majority of health care organizations in the U.S. are running their medical devices on outdated software and operating systems, leaving them vulnerable to cyberattacks. The research found nearly 83% of health care providers in the U.S. that are running on outdated software. More than 40% of health care providers stated that they were planning to enhance their cybersecurity measures this year. The research also revealed that 27% of medical devices are still running Windows XP or old versions of Linux OS. Nearly 16% of imaging systems are at 51% risk of getting hacked.

Due to the severity of the Coronavirus threat, the health care sector leaves several connected medical devices vulnerable to potential cyberthreats.


GDPR Data Breach Notifications Rise by 66% Across Europe

GDPR fines in 2020

A survey by multinational law firm Linklaters revealed that GDPR-related data breach notifications across European countries have increased by 66%, compared to the first year of the GDPR (from May 25, 2018 to May 24, 2019). However, the U.K. witnessed a decline in notifications, with a 17% drop compared to the notifications reported in the first year of the GDPR (11,499 notifications). The numbers doubled in France, with a total of 2,287 notifications (97% increase). Spain reported 1,608 data breach notifications, with a 58% increase. It is also found that Poland reported a high number of notifications when compared to other EU countries with 6,039 data breach notifications in 2019.

The analysis stated that the surge in data breach notifications in both France and Spain is because the companies were aware of their data security obligations. The reasons for  the decline in data breach notifications in the U.K. include:

  • Organizations over-reporting data breaches after the initial implementation of the GDPR
  • The U.K.’s Information Commissioner’s Office (ICO) issued a warning on the over-reporting of data breaches
  • The U.K. is having high breach notifications compared to other countries in the first year of the GDPR

Most of the data breach notifications stemmed from breach of confidential data or access by unauthorized third parties. The survey also highlighted that attackers mostly targeted on clients and employees to steal data with various hacking activities like malware attacks, phishing e-mails, and compromising victims’ unsecured devices.

In addition, the analysis also highlighted the number of fines ordered under the GDPR in the last year. It said that only one fine was reported in the U.K., while 112 fines were ordered by the Spanish DPA, 10 by the Italian DPA, 9 by the Belgian DPA, 6 by the CNIL in France, 13 in Germany, and 5 in Poland. The findings are based on the data analysis across seven European countries, namely Belgium, France, Germany, Italy, Poland, Spain, and the U.K.

Tanguy Van Overstraeten, Partner and Global Head of Linklaters’ Privacy and Data Protection Practice, said, “The harmonization of data protection rules across the EU has been largely successful under the GDPR; however, there are still significant differences among Member States – impacting uniformity of enforcement across the EU. Only harmonizing the approach towards the determination of sanctions will not be sufficient, the interpretation of the rules should also be common to all the Member States. Businesses need certainty and a more unified approach across the EU.”

Overstraeten added “There is also a danger of GDPR fatigue amongst businesses and the Covid-19 crisis is impacting budgets which could limit resources to ensure compliance going forward. The further simplification and harmonization of data protection rules across the EU will be key to ensure companies can sustain this effort.”


Data Breach Affects PII of 1 Mn OneClass App Users Across North America

School apps sharing students’ data

OneClass app, a Canada-based online learning platform, suffered a data breach after an unsecured Elasticsearch database exposed personal information of over 1 million students across North America. Security researchers at vpnMentor discovered the leaky database sized over 27GB that contained PII and educational data of the students. The researchers detected the data breach on May 20, 2020 and reported it to OneClass authorities. The database is now secured.

“By not securing its users’ data, OneClass has created a goldmine for criminal hackers, jeopardizing the privacy and security of over a million young people and their families,” the researchers said in a statement.

The exposed information included full names, schools and universities attended, email addresses, phone numbers, school and university course enrollment details and OneClass account details. It is estimated that around 8,972,251 student records may have been exposed in the data breach.

“OneClass users are very young – including minors – and will generally be unaware of most criminal schemes and frauds online. This makes them particularly vulnerable targets. It is also likely many of them use their parent’s credit cards to sign up, exposing their whole family to risk. It is also possible that some of the data belongs to minors, as OneClass includes resources for high school students and accepts users from 13 years old and above. Many records also included additional information on individual students and their courses, including faculty details and access to otherwise protected textbooks and question and answer exercises,” researchers added.

Cyberattacks on E-Learning Platforms

There has been a  surge in the usage of online learning platforms during the ongoing pandemic. Hackers targeted multiple e-learning portals to steal users’ personal information. In a  similar incident, India-based online learning platform Unacademy suffered a data breach that exposed details of 22 million users. Cybersecurity firm Cyble revealed that the unknown hackers kept 21,909,707 user records for sale at $2,000 on darknet forums. The compromised information included usernames, hashed passwords, date of joining, last login date, account status, email addresses, first and last names, and other account profile details. Earlier, a Spanish e-Learning platform 8Belts suffered a data breach that exposed personal data of over 100,000 e-learners across the globe. According to an investigation report, the 8Belts database was stored on a misconfigured Amazon Web Services (AWS) S3 bucket which resulted in the data leakage.