Home Blog Page 142

State Actors Using MobileIron’s Vulnerability to Target UK Organizations: NCSC

NCSC

In June 2020, MobileIron reported a critical RCE vulnerability registered under CVE-2020-15505. The vulnerability was fixed in its security update released on June 15, 2020.

However, the NCSC has now released an advisory that the same vulnerability is being targeted by multiple state actors against U.K.-based organizations.

The Vulnerability

MobileIron is a provider of mobile device management (MDM) systems. These systems enable administrators to manage an organization’s mobile devices from a central server, thus, making them a hot favorite among threat actors. MDM systems are generally highly secured, but the CVE-2020-15505 vulnerability allowed remote attackers to execute an arbitrary code via unspecified vectors. This was a serious threat, and the criticality of the vulnerability can be gauged by its CVSS v3 score, which stood at 9.8.

Related News:

NCSC and CISA Release Joint Advisory on COVID-19 Cyberthreats and Malicious Groups

The Recent Spike

Although a security update was released earlier, it has been observed by the NCSC that various state-sponsored threat actors are still actively exploiting this vulnerability in systems that have still not been patched. The U.K.’s cybersecurity watchdog said, “The NCSC is aware that Advanced Persistent Threat (APT) nation-state groups and cybercriminals are now actively attempting to exploit this vulnerability to compromise the networks of U.K. organizations.” NCSC noted that the increased exploitation of this vulnerability in recent months could be because a proof of concept exploit became available in September 2020 on a popular open-source forum.

The U.S. cybersecurity agency, CISA, already issued an alert in early October about the same vulnerability being used in tandem with the Netlogon/Zerologon vulnerability CVE-2020-1472 in a single intrusion attempt.

Versions Affected

As per MobileIron’s website, following are the versions affected by the vulnerability:

  • 10.3.0.3 and earlier
  • 10.4.0.0, 10.4.0.1, 10.4.0.2, 10.4.0.3, 10.5.1.0, 10.5.2.0 and 10.6.0.0
  • Sentry versions 9.7.2 and earlier
  • 9.8.0
  • Monitor and Reporting Database (RDB) version 2.0.0.1 and earlier

Both NCSC and MobileIron have urged its users to apply the latest patches, which are available here.

Related News:

Vulnerability Alert: NCSC Warns U.K. Organizations About SharePoint Flaw

Mobile Malware Skyrockets in Asia, 97% of Transactions Found Fraudulent

Rootkits, Mobile Malware in Asia

A new report from Upstream’s Secure-D highlighted the consistent increase in mobile malware activity in Asia in Q3 2020. It revealed that 97% of all mobile transactions in the region were reported as fraudulent, with 50% of the activity found in Indonesia. The top fraudulent apps worldwide appear to either have a direct link with the app store or a specific handset manufacturer.

According to the report, Indonesia saw 98% of fraudulent transactions from a total of 164 million processed transactions. Over 310,000 users in Indonesia were found carrying malware infected devices, equating to one fifth of all infected users, Secure-D detected globally. The number of suspicious mobile apps in the country also doubled when compared to Q3 2019, jumping from 3,129 to 6,288.

Other Findings:

  • Data for the penultimate quarter of 2020 shows that Thailand, United Arab Emirates and Malaysia have also experienced increase in fraudulent malware activities.
  • Malaysia saw a 30% increase in the number of transactions blocked, and the UAE experienced a 16% increase.
  • In Thailand, the number of infected users has increased by 700% from 23,275 in Q3 2019 to 178,857 in Q3 2020. The number of blocked apps also increased from 157 in Q3 2019 to 1,459 in Q3 2020.
  • Russia also suffered an increase in fraudulent transactions, with the block rate (the number of transactions barred, divided by the number of transactions processed) rising from a 66% in Q2 2020, to 94% in Q3 2020.
  • In South Africa, more than 460,000 infected users were detected in Q3, a 70% increase compared to the same period last year.
  • In Ivory Coast, mobile malware spiked in comparison to the previous quarter, with fraudulent transactions jumping from 72,361 to 156,885. The number of malicious apps increased from 406 to 520, and the number of infected devices from 7,269 to 19,220.
  • More than 76 million transactions were identified and blocked in Brazil in Q3 2020, a 77% increase in the previous quarter, while the number of suspicious apps detected rose by 30%, from 3,974 to 5,167.

“An increasing number of people are opting to stay at home due to the pandemic, and many have become dependent on their mobile phones for entertainment, news and socializing. We are noticing a sharp increase in malicious activity from bad actors publishing apps, even on the Google Play Store, that blindside users, purchasing subscriptions and premium content without their consent,” Geoffrey Cleaves, Head of Secure-D at Upstream said.

With Cyberwars, Cyber Espionage has Reached New Level

Cyber war

Even though cyber espionage has often sounded like something straight out of a James Bond flick, it continues to be one of the most realistic threats that have marred government agencies and industries alike. In fact, in several ways, it is even difficult to weigh if corporate espionage is bigger than state-sponsored espionage.

By Augustin Kurian, Senior Feature Writer, CISO MAG

“There is a significant crossover in attackers. It’s not very often you will see state entities subcontracting the online illegal activities to independent hackers. A lot of the Russian military capability around cyber, was actually recruited directly from criminals,” Rik Ferguson, world-renowned cybersecurity expert and Vice President of Security Research at Trend Micro,  told CISO MAG.

He continued, “And their problem is that they then expect these criminal recruits to stop being criminals while they’re now in the army, and that’s an unrealistic expectation to have. So, there is and always has been a significant crossover between patriotic hackers and nation-state employees. But I would argue that, from a victim perspective, victims of criminal attacks are far more than victims of nation-sponsored attacks. It is much more numerous because the aim of a nationally aligned attack, whether it’s sponsored or not, are much more restrictive than the aims of a financially motivated attack. So, your potential victim pool is much smaller.”

Verizon recently released its Cyber-Espionage Report (CER), which is their first-ever data-driven publication on advanced cyberattacks. The report asserted that in 85% of cyber espionage breaches, threat actors were state-affiliated, while 8% were nation-state affiliated, and just 4% were linked with organized crime. The report also noted that 2% of breaches were by former employees. When it comes to overall breaches by Incident Classification Pattern for the 2014-2020 Data Breach Investigation Report (the seven years of the reports which has been the basis for CER) timeframe, it was seen that Cyber Espionage ranked sixth (10%) — albeit within close striking distance of fourth: Privilege Misuse (ranked fourth at 11%) and the sagging Point of Sale intrusions (ranked fifth at 11%).

“Unsurprisingly the top industries targeted are Public Sector (31 percent) followed by Manufacturing (22 percent) and Professional (11 percent), this is due to the fact that they hold the majority of secrets, sensitive information, and intellectual property which are most desired by cyber espionage criminals,” Ashish Thapar, Managing Principal and Head – APJ, Verizon Business Group, told CISO MAG.

Thapar added, “Cyber espionage, like other cyber-attacks, has become more sophisticated over time. However, many don’t realize their role in geopolitical conflicts and has been regarded like any other type of cyber-attack for far too long. With nation-states now waging almost-constant cyberwars, cyber espionage has reached a new level of strategic value — and enterprises have to give it significant attention.”

For the percentage of cyber espionage breaches within all breaches by industry, manufacturing topped the list at 35%, it was followed by mining and utilities at 23%, public enterprises at 23%, professional sector at 17%, education at 8%, information at 7% and financial sector at 2%.

It was noted that financial motivations were higher (between 67-86%) and those by Cyber Espionage were comparatively lower (between 10-26%). When asked about why such a huge disparity, Thapar said, “Given their nature (e.g., stealthy tactics, specific targeting), espionage attacks can be difficult to detect and identify as an actual espionage-related attack (given scant IoCs and other details). Whereas financial attacks — if not detected while occurring or soon thereafter — eventually become apparent when money goes missing. At that point, the financial motive, if not already ascertained, can be determined.”

He concluded, “Cyber Espionage breaches pose a unique challenge. Through advanced techniques and a specific focus, Cyber Espionage threat actors seek to swiftly gain access to heavily defended environments, laterally move with stealth and efficiently obtain targeted assets and data.”

Augustin Kurian

About the Author 

Augustin Kurian is part of the editorial team at CISO MAG and writes interviews and features.


“Proprietary aviation systems are getting commoditized, which opens up security risks”

Security Risks in Aviation

The aviation industry has been heavily impacted during COVID-19 and has already lost $8 billion in revenue this year. Airlines and airports cannot afford to have more losses due to cyberattacks or fines imposed by regulators.

In an exclusive interview, Ravinder Pal Singh (Ravi), Chief Information & Innovation Officer at Vistara (Tata Singapore Airlines Limited), tells Brian Pereira, Principal Editor, CISO MAG how technologies like AI, machine learning, and robotics could be used to secure both traditional and modern infrastructure – and make airline travel safer for passengers today. Ravi talks about the security weaknesses at airports and mulls on potential hacking threats to aircraft.

Ravi is a Harvard alumnus and award-winning technologist with several global recognitions. He has been acknowledged as a leading Robotics Designer, a top 25 CIO, and an AI leader in Asia. He is known for his research work, which continues to make a difference globally, across multiple businesses and public domains.

Ravi is one of the speakers at the Cybersecurity in Aviation virtual event, which begins on November 25, 2020.

Edited excerpts of the interview follow:

Could you tell us about your day-to-day role in the operations at Vistara?

Vistara is a joint venture between Tata Sons Limited and Singapore Airlines Limited (SIA).  It is a full-service carrier. It has a remarkable history of two institutions — Tata and Singapore Airlines. It is now moving from domestic to international. We have two types of fleets — widebodies (787 Dreamliner) and narrow-body (A320) aircraft. We are a tech-driven airline. Thoughtfulness and innovation are our core values. And my role revolves around it — to ensure that systems are built — all kinds of systems of records from revenue to costs to engineering, to flight operations, to people.

The idea is to introduce the convergence of technologies ranging from data, which originates from objects, beautiful machines (aircraft), to people who fly those aircraft, to people who manage those aircraft, and consumers and customers who are using services provided by Vistara ecosystem. It’s about how all that information is converted to intelligence, through various systems of records, based on intelligence that comes through machine learning code, IoT, Big Data, and in certain cases, nodes are distributed using blockchain.

Fundamentally, I am a person who designs and builds robots, I write code, and I have to ensure that information is safe and secure. I ensure that prudent intelligence comes out of data and information which flows through convergence between humans and machines within Vistara.

I see that you have a background in AI and Robotics. How are you applying that knowledge to make air travel safer?

There are many ways of looking at it. One way is the current situation — how do we ensure that people who are traveling are safe from COVID? How do you ensure that their information is shared with the government and regulatory bodies associated with COVID? And you have to develop this framework in systems quickly.

This is already happening because Vistara’s systems are built on stacks, where you can track information and create intelligence. Less machine learning is used in this particular aspect.

We have this concept called “Counter in a box” where we can quickly create safe counters. And hence we can associate the PNR information of our customer with the health information that the government requires.

The second part is information with respect to flight safety, operations, and engineering. For instance, our 787 aircraft are based on an e-enabled platform. This aircraft is driven by software. Right from information that comes out of engines, information from the cockpit, and information related to all parts of the aircraft — that information is associated with flight safety, through engineering. So, if a part has to be changed, it has to be changed through our software. We have information for each part, in terms of health, longevity, and the overall environment and circumstances of this machine.

The third aspect is our e-commerce channels in the B2B and B2C spaces, where information is kept within the perimeter. Outside the perimeter, it is about how do you ensure that the state of information which is used for a particular e-commerce transaction, is safe and secure, while it creates revenues.

We are passionate about protecting the privacy and the transactional integrity of anything that happens through our e-commerce platform — either with travel agents or with consumers.

The last piece is our core systems — a system of records for people, for cost, revenue, network planning — how all these systems can talk while maintaining integrity both from the audit trail perspective and the overall infosec perspective.

There are four layers for how security frameworks ensure not only integrity of information, both data in flight and data at rest, but also ensuring that it helps to fly aircraft safely while managing revenues in a cost optimum way.

Aviation systems have been very closed and proprietary. These are largely isolated or closed systems. Today, these systems are being connected to the Internet. Even the ATC is embracing digital technologies. That presents new risks. How do you see the protection of legacy aviation systems that are integrated with modern digitally-enabled systems?

First, I’ll talk about proprietary. Let’s not limit this to only to aircraft, and also look at aviation and aerospace as a whole. It costs tons of money to build an aircraft, a rocket, a satellite, or even a launchpad. Look at Aerospace overall — a part of it is getting into the commodity space. For example, Low Earth Orbit (LEO) satellites are getting into a commodity zone.

Today, it is far easier to access launchpads across the world and launch rockets. 3D printing is coming into the manufacture of rockets in a much more powerful way. Instead of building a rocket with millions of parts, you can reduce the complexity through 3D printing.

So, the trend is moving towards commodity. Will it be an absolute open source? I don’t see that happening. It won’t happen because of the way the industry works and the different standards. What is the complexity of building and what is the capital to build a particular machine? That’s why they are proprietary.

Now we see software coming in and networks are getting software-defined. I see aircraft as a set of network devices that come together to fly. One day, a computational network engineer will come close to an aircraft maintenance engineer — or the other way around. They have to deal with routers, switches, and data flow that happens between them. And parts will become sensor-based; and sensors are now part of software-defined networks.

Does this increase vulnerability? It does. Is commodity software security typically known as infosec, geared for that? No. How to deal with this, in the mid-term, is to deal with proprietary software. Part of that proprietary software is getting into a commodity software through certificates, PKI — if you look at e-enabled aircraft, security is dictated by PKI platform (public and private key).

How does the Aviation industry view compliance and testing, particularly for infosec industry standards? 

More needs to be done in this area. But I give the benefit of doubt to associated agencies. For example, there are specific IATA standards for the safety of an aircraft. There are FAA standards, data protection standards, the data that originates from the aircraft. So, I am satisfied with those standards. But the overall framework, say, how an airport should be secured, how overall an airline should be secure, how airports and airlines along with aircraft lessors — how these three things should be secured, just as it happens in Financial Services and Insurance sector. There’s a lot of work has to be done here.

But for an airline business, the primary focus is passengers and aircraft. And then everyone else. I think the safety of both these parts is addressed.


About the Interviewer
Brian PereiraBrian Pereira is the Principal Editor of CISO MAG. He has been writing on business technology concepts for the past 26 years and has achieved basic certifications in cloud computing (IBM) and cybersecurity (EC-Council).


Disclaimer

Ravinder Pal Singh spoke to CISO MAG in a personal capacity and his comments should not be attributed to Vistara, Tata Singapore Airlines Limited, or Tata Sons Limited.

Find the Fake! FBI Warns About Spoofed Website Domain Names

FBI warns about fake domains

The FBI is warning users to be vigilant about fraudulent websites impersonating FBI-related domain names. In a security release, the FBI stated that it identified cybercriminals registering various lookalike domains to misguide users seeking information about the FBI’s mission, services, and news.

Cybercriminals create spoofed domains by changing characteristics of original domains slightly, like altering the spelling of a word or changing a domain from legitimate [.]gov version to [.]com. Besides fake domains, attackers also use malicious lookalike emails to lure users into clicking on malicious email attachments or links. The FBI urged users to evaluate the websites they visit, and crosscheck the messages received to their personal and business email account.

Find the Fake

The FBI recommended certain security precautions to identify fake websites and links. These include:

  • Verify the spelling of web addresses, websites, and email addresses that look trustworthy but may be imitations of legitimate election websites.
  • Ensure operating systems and applications are updated to the most current versions.
  • Update anti-malware and anti-virus software and conduct regular network scans.
  • Do not enable macros on documents downloaded from an email unless necessary, and after ensuring the file is not malicious.
  • Do not open emails or attachments from unknown individuals. Do not communicate with unsolicited email senders.
  • Never provide personal information of any sort via email. Be aware that many emails requesting your personal information may appear to be legitimate.
  • Use strong two-factor authentication if possible, using biometrics, hardware tokens, or authentication apps.
  • Use domain whitelisting to allow outgoing network traffic to websites that are deemed safe.
  • Disable or remove unneeded software applications.
  • Verify that the website you visit has a Secure Sockets Layer (SSL) certificate.

“Spoofed domains and email accounts are leveraged by foreign actors and cybercriminals and can easily be mistaken for legitimate websites or emails. Adversaries can use spoofed domains and email accounts to disseminate false information; gather valid usernames, passwords, and email addresses; collect personally identifiable information; and spread malware, leading to further compromises and potential financial losses,” the FBI said.

Turkish Hackers Deface Joe Biden’s “Vote Joe” Website

Joe Biden's election campaign website defaced, Joe Biden website defaced, Joe Biden website subdomain defaced

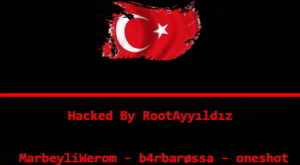
Turkish cybercriminals going by the name, “RootAyyildiz,” defaced Joe Biden’s official campaign website’s subdomain, “vote.joebiden.com.” The incident that took place just a few weeks ahead of the official change of guard in the White House has made experts believe this will act as a strict reminder to Biden to prioritize securing the cyberspace once he settles in office.

The Hack and the Message

Joe Biden Website Defaced by Turkish Hackers
Image Credit: Web Archive

Biden’s official campaign website JoeBiden.com had a subdomain, vote.joebiden.com. This was used by Biden and Harris as a part of their official campaign to help voters find polling centers, campaign events whereabouts, and offered state-specific voter guides. Post the elections, which took place in the first week of November, the traffic from this subdomain was redirected to the Democratic party’s “I WILL VOTE” website. However, on November 18, this website displayed a message in the Turkish language with the country’s flag placed at the top and aliases and usernames such as “MarbeyliWerom,” “b4rbarøsas,” and “oneshot,” below it.

The message when converted to English read:

We took ablutions and started our journey. We made our funeral prayer for our brother.

We made a promise to the Great Hakan, we will kill for the chief.

Damn those who live for money and fame, greetings to those who live for the cause of Islam.

Here I warn the US backed so-called political parties like chp hdp good party, if you don’t take your hands off my state, my nation, we’ll be a nightmare.

We will now decipher your most private conversations and take you around on the street.

RootAyyıldız is not a Group or an Organization, but a Vatan Lover who Fights alone.

At the end of the note, a photo of the 34th Sultan of the Ottoman Empire, Abdul Hamid II, was also placed with a footer note saying, “We; We are the ones who stopped the tanks with their bare hands on the night of July 15. We are those who killed death that night. We have been waiting for Archers Hill for 15 centuries! We are the keepers of that golden banner that will never miss its shadow on us.”

As per the note, this hack does not seem to be the work of a threat group, however, it is still not certain as to which vulnerability led to the defacement of Joe Biden’s website.

Biden and Trump’s Apps were Hacked Earlier

At a campaign event in Tucson, Arizona, on October 21, President Trump made a false claim that “Nobody gets Hacked.” However, days later, Promon, a Norwegian cybersecurity firm, hacked both Joe Biden and Donald Trump’s election apps to prove: “Everything can be hacked.”

Related News:

Promon Proves Biden and Trump’s Election Apps are Easy Targets of Cyberattacks

The white hat hackers at Promon were analyzing the election apps of the two candidates when they discovered that both apps were highly vulnerable to a known and critical Android vulnerability known as StrandHogg. This vulnerability allows malware gangs to hijack legitimate apps and perform malicious operations like phishing.

Hanna Andersson to Pay $400K to Settle CCPA-related Class-Action Lawsuit

California Consumer Privacy Act, Hanna Andersson to Pay $400K to Settle CCPA-related Class-Action Lawsuit

Hanna Andersson, U.S.-based kids wear retailer, has agreed to pay $400,000 to settle a data breach lawsuit related to the California Consumer Privacy Act (CCPA). The class-action lawsuit, which is the first monetary settlement under CCPA, was filed in the U.S. District Court for the Northern District of California in February 2020. The lawsuit claimed that Hanna Andersson and its third-party vendor Salesforce violated the CCPA by exposing customers’ personally identifiable information (PII) in a 2019 data breach.

As per the settlement, more than 200,000 U.S. customers, who made purchases from the Hanna Andersson online store from September 16 to November 11, 2019, will receive $500 to $5,000 compensation.

How Hanna Andersson got Hacked

According to a statement from Hanna Andersson, unknown threat actors hacked Hanna’s retail website during the holiday season of December 2019. The attackers stole the credit card details, including customer name, payment card number, CVV code, expiration date — along with billing and shipping addresses of its customers from the checkout and payment page of the online portal. The hackers also sold credit card details of the customers on the dark web.

The cyber forensic team’s investigation confirmed that Hanna Andersson’s third-party eCommerce platform, Salesforce Commerce Cloud, was infected with malware that may have scraped information entered by customers into the platform during the purchase process.

In addition to the settlement, Hanna Andersson also agreed to enhance its security posture to prevent future security incidents by conducting a risk assessment of its data assets; enabling multi-factor authentication; hiring a new director of cybersecurity; conducting phishing and penetration testing; and deploying additional intrusion detection, prevention, and monitoring applications.

“Plaintiffs strongly believe the settlement is fair, reasonable, and adequate and that the court should grant it preliminary approval and notice distributed to class members. The settlement provides quick relief for class members, including compensation for the alleged unauthorized dissemination of their PII,” said the attorneys for the class-action plaintiffs in the settlement agreement.

Third-Party Risk: Reactive to Predictive

Endpoint Security

Third-party risk management: the process, technology, and people whose goal is to lower the risk created by third-parties (vendors).  Surveys of a wide range of companies, across multiple industries, routinely find that less than 50% have a program to manage this risk. Those that do perform it, do it minimally: part of a compliance exercise, designed to keep the regulators and oversight bodies satisfied.  After COVID-19 sent many onshore and offshore resources to work from home and cyber-threats exploded over 800%, this lack of a serious approach to third party risk (when compared to how firms perform their own internal security controls) became apparent in the corresponding explosion of third party breaches and security incidents.

By Gregory C. Rasner, CISSP, CIPM, CCNA, ITIL

Many firms rely on point-in-time assessments.  These are typically classified as remote or onsite assessments.  Remote assessments are questionnaires sent to a vendor with relevant questions that are reviewed for any items that do not meet your firm’s security requirements.  Remote assessments are a great way to perform intake security reviews for new vendors or new services.  The weakness of remote questionnaires is they typically cannot share sensitive documents or data because of their restrictive classification.  For example, viewing a third-party’s access management policy documentation will not typically be allowed.

Onsite assessments are performed at the vendor’s location.  These allow for a more transparent sharing of data because anything sensitive is not leaving the room where the assessment is taking place.  In addition, being onsite allows a more direct conversation with the vendor about their security and any potential gaps.  The weakness of onsite assessments is they take more time to plan, execute, and complete.

Both types of assessments, remote and onsite, are valuable and have excellent use-cases.  First, understand the limitations of each type: a remote assessment is akin to asking your children if their room is clean.  If going to their room is physically challenging, getting their feedback on clean status is acceptable; however, that definition of clean is likely not the same as your definition of clean. The onsite is similar to going to your kids’ room to validate that their room is actually clean.  As most of us can attest, the results of the two types of assessments are different.  Remote assessments are effective on time-sensitive, higher volume processes as found on new vendor security evaluations.  The results need to be taken with a lower level of confidence, given the vendor is attesting to their security controls.  Onsite assessments will find security gaps that provide a very high confidence level, but due to their higher resource cost, should be done on vendors with a risk level that warrants that extra cost.

If your organization isn’t performing these types of security evaluations, begin by reviewing third parties at the highest risk.  This can be done by the number of records and/or a connection to your network.  Send out a remote assessment questionnaire to get a level-set; follow this activity up with a review of those remote assessments with a look at those with the most concerning responses for an onsite assessment.  In this time of inability to travel and gather, leverage collaboration tools to do these virtually, until they can be performed safely at the vendor location.

Cybersecurity Third-Party Risk

Many companies focus on all the third-party risk domains, not cybersecurity risk.  There is a financial risk, reputational risk, country risk, and many others.  However, cybersecurity risk is most often the largest financial and reputational risk to your firm.  Countless public breaches that are associated with large, well-known companies were the result of a cybersecurity breach at their third party.  While there are other domains for review with third-party risk management, it is cybersecurity risk that involves the most frequent and public breaches.  Focusing on the cybersecurity domain requires the third-party risk team has information security expertise.

Third-party risk management organizations do not often have this level of experience or expertise.  Many companies compensate for this by creating a checklist for the assessor to follow.  There are two major problems with this approach: first, without that expertise, it is very unlikely the assessor will recognize any inconsistency or illogical answer from a vendor; second, the checklist approach does not allow for follow-ups that provide a more complete picture of the security at the vendor.

Continuous Monitoring

As mentioned in the first section, point-in-time security evaluations are common and necessary.  However, there is a need to perform something more ongoing and active; this is called Continuous Monitoring.  It is designed to fill in the gap between the point-in-time assessments discussed above.  This activity has typically been reliant solely on vendor reputation software: the tool sends an alert of a bad score on a particular third party, and the third-party risk team member will engage with the vendor about the alert. This has resulted in a lot of fatigue among third-parties and often is a conversation that does not change the risk.  There is a need to change this approach and can be accomplished by correlating the alerts from vendor reputational software with internal due diligence and the nature of the threat in the alert.

An example of how this would be an alert from a vendor reputation software is seen for open port detected on FTP at a vendor who maintains ten-thousand confidential customer records.  Diving into the existing due diligence or risk acceptance at the firm is the next step; this example finds a risk acceptance performed on this vendor for inadequate Data Loss Prevention (DLP), providing more context about the alert.  All this data combined and provided to the vendor is more complete about the alert combined with known gaps.  Now the conversation with the third party is about the alert in context with their risk acceptance and a high number of protected records for your customers.

Moving to Predictive

Almost every third-party risk management organization is reactive: reliant on a breach or security incident notification from a vendor.  As due diligence efforts, point-in-time assessments, and Continuous Monitoring, produce results and data, it becomes possible to change into predictive.  Use the data to change to a predictive model. Much like vulnerability management, this approach allows CISOs and their teams to focus on what is the highest risk, not the totality of all vendors.

The vendor due diligence results, risk acceptances, contract deviations, threat intelligence engines, vendor reputation tools, and other data sources are all inputs to this updated approach.  The front-end can be a Business Intelligence or Analytics engine, but the algorithm is the key.  For example, confidence levels for the data are part of the consideration: due diligence findings from an onsite assessment have higher confidence than remote.  An open risk acceptance has high confidence, but the vendor reputation tool is lower.  The higher the confidence of the data, these have a higher weight in the algorithm.

In a dashboard view, the simplest form for this predictive model is a stoplight approach: red, yellow, green.  Vendors who have no open findings, no open risk acceptances, no alerts would be shown as green. Vendors with low to medium risk findings and/or risk acceptances could be yellow. Those with higher risk findings, risk acceptance, and an alert show up as red.  At a high level, this allows staff to focus on the highest risk for engagement. A further example is a vendor who is yellow, with an open finding for not allowing admin access of laptops by standard users; there are ten thousand confidential customer records at their site, and there is an alert that shows botnets coming from their network that are known browser add-ins with key-logging capabilities: this bumps them up in the dashboard to red. Now the conversation with the third party is proactive: going to them with this level of detail in a system that provides alerting changes the timing of the conversation.

Timing is Everything

The number of firms that need to perform third party risk still needs more adherents; however, due to COVID-19 and the increased cyberthreats, there is an obvious need to change the approach to include and improve Continuous Monitoring.  Firms that get to this level of due diligence on their third-parties can then begin to benefit from a predictive, near-real-time engagement with vendors on a risk-based approach. Getting ahead of the risk leads to lowering the risk.


About the Author

Gregory C. RasnerGregory Rasner leads Corporate Cyber Security Third-Party Risk at Truist Financial Corp. Prior, he held cybersecurity and information technology leadership roles in technology, biotech, and finance. Teaching part-time at local community colleges and volunteering time for veterans’ causes are his passions. He is proud of his service in the U.S. Marines and is also a father of five children along with a beautiful, smart wife who also is a cybersecurity professional. He can be reached at [email protected]

Disclaimer

Views expressed in this article are personal. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.


Related story: The Role of Third-Party Management in Cybersecurity