
A latest research from domain security provider CSC revealed that security gaps in enterprise domain security procedures expose organizations’ networks to cyber risks and vulnerabilities such as domain name system (DNS) hijacking, data fraud, and phishing attacks.
According to the research “2020 Domain Security Report: Forbes Global 2000 Companies”, 83% of global 2000 organizations have not adopted basic domain security practices. It was found that IT, media, and entertainment sectors are implementing sophisticated security measures towards domain security, while industries like materials and real estate are most vulnerable to attacks.
Other notable findings from the research include:
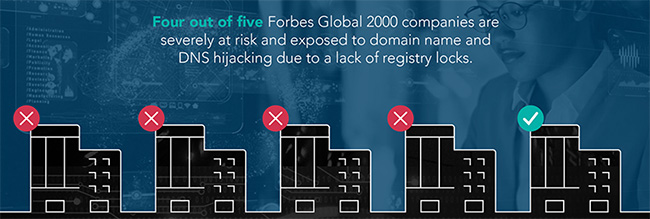
- 4 in 5 global 2000 companies are severely at risk and exposed to domain name and DNS hijacking due to a lack of registry locks. Unlocked domains are vulnerable to social engineering tactics, which can lead to unauthorized DNS changes and domain name hijacking.
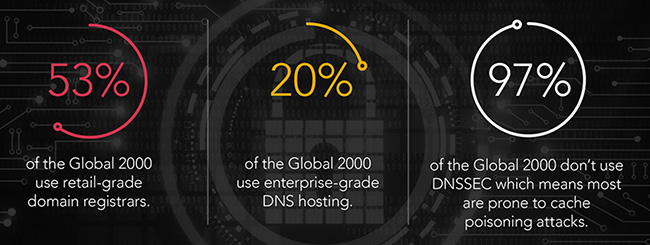
- 53% of the Forbes Global 2000 use retail-grade domain registrars, putting them at greater risk for phishing, social engineering, and attacks while complicating compliance demands.
- Only 20% of global 2000 companies use enterprise-grade DNS hosting. Lack of DNS hosting redundancy and using non-enterprise-level DNS providers poses potential security threats like resiliency to Distributed Denial of Service (DDoS) attacks, as well as downtime, and revenue loss.
- 97% of the global enterprises do not use DNS security extensions (DNSSEC), which means a majority of companies are prone to cache poisoning attacks. Lack of deployment of DNSSEC leads to vulnerabilities in the DNS, which could include an attacker hijacking any step of the DNS lookup process.
- Domain-based message authentication, reporting, and conformance (DMARC) use is only at 39% for the global 2000 companies. DMARC is an email validation system designed to protect a company’s email domain from being used for email spoofing, phishing scams, and other cybercrimes.
“These security shortfalls are the direct result of not executing proper domain security techniques. Domain security cannot be an afterthought, and there needs to be a conscious effort to make this an intentional and critical part of every company’s overall cybersecurity posture, especially as criminals evolve their attack methods. As companies move to more online business models, it’s essential to use defense-in-depth practices to proactively manage, secure, and defend the foundational internet-facing components of digital brand presence,” said Mark Calandra, Executive Vice President for CSC.

 hijacking, data fraud, and phishing attacks.)