Home Blog Page 66

Attackers Get Cannier; Found Targeting Non-C-Suite Employees via Spear Phishing

xss vulnerability in UPS, Phishing Attack, spear phishing, phishing mails

2021 has been witnessing phishing or pretexting — types of social engineering attacks, leading all Data Breach Reports. The fraudulent practice of sending emails to incite targeted individuals to divulge confidential information and make wire transfers is no more a C-Suite privilege. With attackers getting cannier in their approach, employees in sales, project management, human resources, and admin are on the hit list. With WFH being the norm and employees banking on virtual communication channels, cyberattackers have widened their target spectrum where impersonation is more convincing.

Barracuda, a provider of cloud-enabled security solutions, has released Spear Phishing: Top Threats and Trends Vol.6, highlighting the way spear phishing attacks are evolving and who cybercriminals are targeting with these attacks.

Key findings

  • An average organization is targeted by over 700 social engineering attacks in a year.
  • 1 in 10 social engineering attacks is a business email compromise (BEC).
  • 77% of BEC attacks target employees outside of finance and executive roles.
  • An average CEO will receive 57 targeted phishing attacks in a year.
  • 43% of phishing attacks impersonate Microsoft brands.
  • 1 in 5 BEC attacks target employees in sales roles.
  • IT staffers receive an average of 40 targeted phishing attacks in a year.
  • Cryptocurrency-related impersonation attacks grew 192% between October 2020 and April 2021.

According to the report, an average organization is targeted by over 700 social engineering attacks each year, and 77% of BEC attacks target employees outside of financial and executive roles, including personnel working in roles like sales (19%), project management (10%), human resources (10%) and admin (9%).

Revealing trends on targeted spear phishing attacks, the report talks about CEOs attracting an average of 57 targeted attacks per year, and IT professionals who too are under fire, attract an average of 40 targeted spear phishing attacks per year.

“Cybercriminals are getting sneakier about who they target with their attacks, often focusing on employees outside of the C-Suite, looking for a weak link in your organization,” said James Wong, Regional Director for Southeast Asia, and Korea, Barracuda. “Targeting lower-level employees offers cybercriminals a way to get in the door and then work their way up to higher-value targets. That’s why it’s important to make sure you have protection and training for all employees, rather than just focusing on those you think are the most likely to be attacked.”

43% of Phishing Attacks Impersonate Microsoft

Communication from known sources, brands, services, and e-commerce portals are old tricks used by cyberbullies as they are more likely to be trusted and invoke a response.

According to the report, nearly half of all phishing attacks impersonate Microsoft (43%), followed by WeTransfer (18%), DHL (8%), and Google (8%) to lure unsuspecting victims.

With 79% of organizations using Office 365, and many more looking at migrating in the immediate future, it’s not surprising that Microsoft brands remain a top target for cybercriminals.

Cryptocurrency — The Currency of Choice for Cybercriminals

Cryptocurrency continues to be a favorite with cybercriminals due to its decentralized nature and lack of regulation. Being a digital format and increasingly getting accepted in businesses, cryptocurrency has seen an increase in value. Its price increased by almost 400% between October 2020 and April 2021. Hackers impersonated digital wallets and other cryptocurrency-related apps with fraudulent security alerts to steal log-in credentials.

Best practices to Protect Against Spear Phishing Attacks

Technology

  • Take advantage of artificial intelligence
  • Deploy account-takeover protection
  • Implement Domain-based Message Authentication, Reporting, and Conformance (DMARC)

People

  • Train staffers to recognize and report attacks
  • Review internal policies
  • Maximize data-loss prevention

As the vulnerabilities take innovative forms, organizations need to constantly keep vigil and invest in an inclusive approach to secure their last line of defense, ‘the employees,’ along with the business. Judicious use of technology and training can mitigate risk to a large extent and help avoid phishing attacks.


CISA Launches New Vulnerability Disclosure Policy to Boost Cybersecurity

CISA VDP platform, U.S. export ban on cybersecurity items

Despite regular security audits, attackers continue to intrude on business and government networks by exploiting unpatched vulnerabilities. To help federal civilian agencies in the U.S. manage their vulnerability disclosure process, the Cybersecurity and Infrastructure Security Agency (CISA) unveiled a new vulnerability disclosure policy (VDP).

The VDP program enables security researchers and bug hunters to report any unpatched vulnerabilities in the federal systems to fix them before attackers exploit them.

Launched with the help of cybersecurity firms Bugcrowd and Endyna, the VDP platform offers an official website for agencies to list their vulnerability disclosure policies and bug hunters can post their vulnerability reports for analysis. BugCrowd and EnDyna will conduct the initial assessment of the vulnerability reports submitted by the researchers and later report it to the agencies. Various government agencies including the Department of Homeland Security (DHS), the Department of Interior (DoI), and the Department of Labor (DoL) are planning to leverage the new platform.

The crowdsourcing platform will give a clear picture to the Federal Civilian Executive Branch (FCEB) agencies on the potential vulnerabilities, which will eventually help enhance their overall cybersecurity posture.

The new platform will also help the government curb unnecessary expenses on cybersecurity, as agencies no longer need to introduce separate vulnerability disclosure programs. CISA estimates over $10 million in government-wide cost savings will be attained by leveraging its Cyber Quality Services Management Office (QSMO) shared services approach.

“CISA’s VDP Platform will help the FCEB improve day-to-day operations when managing vulnerabilities in their information systems. Agencies have the option to utilize the platform to serve as the primary point of entry for intaking, triaging, and routing vulnerabilities disclosed by researchers. Our goal is for the platform to act as a centralized vulnerability disclosure mechanism to enhance information sharing between the public and federal agencies. This approach will improve agencies ability to analyze, address, and communicate disclosed vulnerabilities,” said Eric Goldstein, Executive Assistant Director for Cybersecurity, CISA.

CISA’s Cyber Action Plan

CISA always alerts organizations to address any critical bugs in their system to avoid potential cyberattacks. Recently, the federal agency warned organizations to fix multiple vulnerabilities affecting Ivanti Pulse Connect Secure (PCS) VPN appliances on their network systems. The agency warned about the actively exploited vulnerabilities: CVE-2019-11510, CVE-2020-8260, CVE-2020-8243, and CVE-2021-22893. Read More Here…

Ransomware Continues its Marathon to New Records: Report

Ransomware Attacks, Graff ransomware attack

Cybercriminals always aim high when targeting organizations and demanding ransom. The pandemic has given opportunistic hackers time to come up with innovative phishing attacks and extortion schemes. And ransomware, in particular, has continued to reach unprecedented heights since the beginning of 2021. According to the 2021 Cyber Threat Report from SonicWall, ransomware attacks have increased rapidly, surpassing the number of attacks in 2020 and the first half of 2021.

The report revealed that over 304.7 million ransomware attacks were reported globally in H1 2021, exceeding 304.6 million attacks in 2020, which is a  151% increase. High-profile extortion attacks on Colonial Pipeline, JBS Foods, health care, energy sectors, and the recent Kaseya attack have severely disrupted operations of organizations across the globe.

Commenting on the rising ransomware trend, Bill Conner, SonicWall’s President and CEO, stated that threat actors are taking advantage of the security gaps in the network systems and the remote work environment. “In the past 15 months, the world has endured an unprecedented degree of change. As the disruption of a global pandemic impacted everything from the highest levels of the federal government down to the way kindergartners learned to read, cybercriminals seized upon the changing environment to institute the new business normal they wanted,” Conner said.

Key excerpts from the report:

  • The top five countries impacted by ransomware attacks include the U.S., the U.K., Germany, South Africa, and Brazil. Within the U.S., the five hardest-hit states were Florida (111.1 million), New York (26.4 million), Idaho (20.5 million), Louisiana (8.8 million), and Rhode Island (8.8 million).
  • Ransomware attackers surged across primary business sectors, including education (615%), health care (594%), government entities (917%), and retail organizations (264%).
  • The highest number of ransomware attacks (78.4 million) were reported in June 2021.
  • The top three ransomware families include Ryuk, Cerber, and SamSam, accounting for 64% of all reported ransomware attacks in 2021.
  • While malware attacks fell in 2021 (-22%) after reporting 2.5 billion attacks in 2020, the cryptojacking malware continued to rise (23%) in 2021 with 51.1 million attacks.
  • In total, 2.5 trillion intrusions attempts (9% rise), 2.1 million encrypted threats (26% rise), and 32.2 million IoT attacks (59% rise) were reported in 2021 so far.

“In a year driven by anxiety and uncertainty, cybercriminals have continued to accelerate attacks against innocent people and vulnerable institutions. This latest data shows that sophisticated threat actors are tirelessly adapting their tactics and embracing ransomware to reap financial gain and sow discord,” Conner added.

Why are ransomware attacks increasing?

Various reasons lead to the surge in ransomware attacks; however, victims’ willingness to pay up for their compromised data has been the primary reason. According to a recent survey from IDC, nearly 44% of the organizations admitted that they are willing to pay ransom to restore their files and operations in the event of a ransomware attack. The survey also revealed that Australia (60%) and Singapore (49%) are the top-most ransom paying countries.

Pegasus Spyware – The Ghost in the Machine

Pegasus Spyware, Mobile Security, spyware

The most trending cybersecurity news last month was about the Pegasus Spyware incident. This isn’t the first time we’ve heard about Pegasus; remember the 2019 incident where Pegasus was infecting phones through WhatsApp? However, the issue garnered a lot of importance this time as journalists, activists and politicians are also affected with spyware.  In India, the news of Pegasus caused mayhem and disruption as the monsoon session of Parliament began; politicians accused the government and opposing political parties of snooping on their phone messages and conversations. The phone numbers of senior Indian journalists are also on the dreaded Pegasus surveillance list, making them possible victims of spyware.

By Brian Pereira, Editor-in-Chief, CISO MAG

Snooping is fairly common in the digital world. Do you remember how whistleblower Edward Snowden revealed the snooping exploits of the U.S. National Security Agency (NSA), back in 2014? Welcome to the era of mass surveillance.

CNBC TV18 reports that the French government is in discussions with the Israeli government over concerns that President Macron’s phone may have been targeted for surveillance. The Israeli authorities are now scrutinizing the operations of NSO Group Technologies that created Pegasus spyware.

When the Pegasus incident hit the headlines, NSO vehemently denied any involvement. It said it just creates this tool and sells it to governments and intelligence or security agencies. It says it cannot be held accountable for how its customers use this tool.

So, the licensees should be held responsible – the State in particular. But then, there is a thin line between what one deems as “surveillance for security reasons” and snooping. Who decides what is legal and permissible and what violates a citizen’s privacy?

The State needs to take a call on such issues and revise its IT laws and Acts if necessary.

A few questions about Pegasus Spyware

This incident also raises a few questions:

  • Is it possible to get infected by spyware without clicking on any links (zero click)?
  • Can someone plant spyware on your phone just by knowing your number and sending you a message?
  • How does one know if they have been infected by Pegasus spyware?
  • And how do you remove and block this spyware from your phone?

I am hoping the answers to these questions will emerge soon. Because if it doesn’t, a lot of people may get paranoid with this Orwellian approach of governments.

Will this be 1984 all over again?


About the Author

Brian PereiraBrian Pereira is the Editor-in-Chief of CISO MAG. He has been writing on business technology concepts for the past 27 years and has achieved basic certifications in cloud computing (IBM) and cybersecurity (EC-Council).


Cloud-Native Security – Should Organizations Be Wary of the Hype?

Cloud Forensics

By 2022, 90% of new enterprise applications will be cloud-native. Yet, 50% of organizations find that native security controls are inadequate and have added third-party solutions to fully meet their needs. While cloud-native security is on the rise, does it do enough to cover enterprises that are leveraging complex, hybrid and multi-cloud environments? With 81% of organizations currently working with two or more cloud providers already, that answer is now more important than ever.

By Keith Neilson, Technical Evangelist, CloudSphere

While cloud-native services present some customer-friendly benefits, organizations must recognize that the built-in measures typically lead to more security misconfigurations, less network visibility, and overprovision access.

What is Cloud-Native Security?

To fully understand cloud-native security strategies, we have to first understand what it means and how configurations are established.

Cloud-native defense structures are specifically designed for the cloud for enterprises to leverage built-in capabilities as part of the overall architecture. Applications are commonly influenced by microservices and a container-based approach. This means that they’re built to be lightweight and flexible with portability at top of mind. To accomplish this, a cloud-native approach relies heavily on automation processes that are designed by vendors for end IT users to manage into adapting and scaling environments. As a result, this enables cloud services to be managed and operated with containers, microservices, immutable infrastructure, and APIs, without any server involved whatsoever.

Traditionally, organizations’ digital applications would be monitored via on-premises security systems that were largely deployed and monitored. Now, networks are configured on externalized data centers like public clouds that tap into open data centers that are using third-party source code. The result is a vastly more complex infrastructure that has dramatically expanded enterprises’ attack surfaces. To handle rapidly growing digitization and expanding operations, companies are looking to cloud-native applications as a way to integrate workloads on AWS, Microsoft Azure, and Google Cloud platforms.

Organizations that utilize a cloud-native architecture often reap the rewards of improved network elasticity in continuous deployment. Ultimately, this is able to vastly expand the horizon of system scalability and business agility. But, it leaves one glaring hole in the security framework that cannot be overlooked by companies leaning on the posture.

Enter the Security Dilemma

To properly defend cloud environments, vendors and end-user companies must navigate a shared responsibility model where the provider and customer are each responsible for specific security measures.

Most often, the provider is responsible for the security of the cloud from physical access through to the infrastructure, while the end-users secure the interior applications and data. With the vendor drafting code and building the infrastructure, IT managers and CIOs are left in the dark on how to properly fit existing, evolving, and new applications into a foreign environment with a more expansive attack surface. As 99% of security failures typically fall squarely on the customer’s shoulders, this doesn’t position the two groups to work cohesively.

According to a 2020 IDC survey, over two-thirds of CISOs are concerned with security misconfigurations. While architecture for cloud-native applications requires heavy input from the customer’s end, the incredible pace to shift to the cloud has led many organizations to prioritize speed of the transition over associated processes, sweeping security issues under the rug in the process.

Recent research also indicates that 56% of companies have some roles and access rights that are improperly entered in cloud environments. With cloud-native security, customers are often charged with running containers, which can lead to an array of access issues and over privilege. While this can be restricted, additional measures must be implemented to avoid common pitfalls that typically occur to companies who adopt an out-of-date or generic security implementation.

Additionally, cloud-native configurations tend to lean on identity and access management policies (IAM) to further define roles, permissions, and access. While IAM is necessary to hash out responsibilities, it isn’t without flaws as 69% of enterprises have reported that IAM policy enforcement issues have led to unauthorized network access.

Security misconfigurations are the Achilles heel for cloud infrastructure, but this is typically magnified in a native security setup. Public and open cloud storage buckets are irregularly monitored as information and storage expands. Further, weaving in encryption, authentication and secure access credentials are increasingly difficult to cover with automation and don’t provide the unique protocols that each application fundamentally requires.

Lastly, visibility is crucial to properly oversee a secure network. This is very difficult to establish in hybrid or multi-cloud environments with expansive data and information, but the issue can be further magnified in a cloud-native security approach. Oversaturated access, poorly established IAM policies, and inconsistently monitored platforms are all factors that make it difficult to outline a holistic system view.

While there are several challenges associated with cloud-native security controls, there are ways to build in additional strategies to make it a more effective solution.

Making Cloud-Native More Secure

When addressing cloud-native security, it’s important to take a centralized approach that leverages automation wherever possible to control, enforce, monitor, and manage identities consistently across your cloud environment. This will limit crossover between vendor and customer teams, inherently minimize credentialed access and provide a rigorous, consistent method of monitoring potential security vulnerabilities. This reduces issues with IAM automation and enables the client to move from a reactive manual state to a proactive approach.

Prioritizing security teams to focus on the container and microservices level will also shore up defenses. From the start, containers must be designed with security in mind otherwise the entire bucket is vulnerable. This is best established right at cloud development, where the corresponding code can be uniquely created.

Threats don’t sleep and neither should security. As developers expand and build out the cloud environment, security policies must be continuously programmed, monitored, and regulated to identify potential gaps and mitigate unauthorized access. Customers, therefore, need to make this a habitual action as information, storage and applications expand.

A shared responsibility model is also essential for cloud-native organizations, and by taking a DevSecOps approach, organizations can better monitor and construct containers, ensure data and applications are safeguarded, and better oversee their sensitive data. When security is the core of the container life cycle, it yields fewer vulnerabilities for threat actors to take advantage of.

Without proper awareness in the cloud environment, any unnoticed change or update in policy puts customer data at risk. To minimize the attack surface and prevent hackers from accessing private data, businesses should focus on creating a platform with complete visibility into the cloud environment and real-time security monitoring.

Cloud-native security services possess some distinct advantages in terms of flexibility, portability, and speed to scale cloud infrastructure. Yet, there are some glaring issues that are prevalent if cloud-native security measures are not properly addressed. This in turn can lead to issues in visibility, misconfiguration, and access that can magnify security vulnerabilities for threat actors to maliciously exploit.

To bolster cloud-native security, organizations need to create a centralized approach that enhances control, visibility and also lean on automation to better distribute and actively monitor attack surfaces. Ultimately, organizations that take a cloud-native approach need to prioritize security ahead of speed and growth to build a properly configured IT environment.


About the Author

As CloudSphere’s Technical Evangelist, Keith is responsible for the company’s analyst and cloud provider relationships and strategy with a focus on ensuring the wider market understands the business and technical value proposition of the CloudSphere platform. In addition to helping create collateral and messaging that supports the company’s go-to-market, Keith ensures that customer use cases are documented back into the various internal teams to ensure product advancements are geared towards real-world scenarios and contribute to the company’s vision. Prior to CloudSphere, Keith held senior lead pre-sales engineering and management roles at Optibus, Cloudhouse, and Sourcebits with a successful reputation for creating and defining compelling product positioning, advocating product advancements internally, leading strategic partner & customer engagements, and creating and executing GTM strategies that attributed to significant growth. He has a broad and strong multi-discipline skillset with a focus on cloud migration, modernization, and management.

Disclaimer

Views expressed in this article are personal. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.

“I believe in building products and teams that are obsessed with customer success”

API

API security has often been a blind spot for enterprises. In fact, it’s very common to see unauthenticated APIs. In most cases, these mostly occur due to overlooked authentication and authorization protection for the APIs in the development process. Sometimes, APIs are left without protections to be integrated with Authorization controllers in API gateways, which is another step for misconfiguration. From incidents like mHealth APPs, Panera bread, Fiserv, LifeLock, Kay Jewelers, and several others, API security had remained a crucial factor.

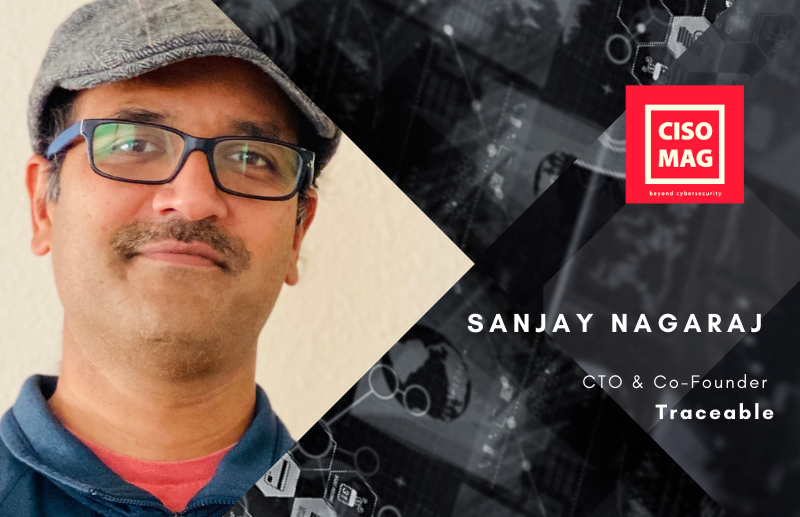
To dive deeper into the subject, CISO MAG interviewed Sanjay Nagaraj, CTO and Co-Founder of Traceable. Nagaraj is an entrepreneur and a Silicon Valley engineering leader. He believes in building products and teams that are obsessed with customer success.

Nagaraj discusses his entrepreneurial journey, API security and the potential risks associated with it, and the future of AI and ML in cybersecurity.

You have had quite a remarkable journey. From AppDynamics, to then staying in stealth mode with Traceable for a significant part of the time, to coming out with a $20 million investment. I think Traceable was born a unicorn. Can you summarize your entrepreneurial journey? Where did it all begin?

I believe in building products and teams that are obsessed with customer success. Prior to co-founding Traceable, I was VP Engineering for AppDynamics/Cisco. At AppDynamics, I was responsible for product teams for Application Performance Management and Database Monitoring products. Additionally, I was responsible for scaling teams across different geographic locations. The innovation that my team and I built was critical in helping DevOps teams to lead the digital transformation at many of the Fortune 100 companies. With the customer obsession of my team, and the products at AppDynamics, I was responsible for generating over half a billion dollars in revenue during my tenure. As a senior engineering leader, I have been building complex enterprise software solutions for over 20 years. Prior to AppDynamics, I worked at various companies including Hyperion Solutions (Oracle) and Philips. I am an inventor credited with several U.S. Patents.

According to major industry analysts, IT organizations struggle to evolve their processes for developing, delivering and managing APIs for integration and digital business transformation. Do you feel API security has become a blind spot for several businesses? How instrumental can a CISO be in this regard?

Yes, absolutely. Many organizations don’t have security practitioners as part of their developer cycle, and developers are not being trained on how to secure their APIs. APIs come in many forms:

  • APIs that you expose to your clients can be applications (mobile or Single page apps).
  • APIs that developers who are B2B customers or internal dev teams using them.
  • APIs that are third-party or B2B APIs where requests and responses are expected from.

CISOs can be instrumental in putting the focus on their API security by asking some simple questions: “Do we know where our APIs are? How many APIs are internal vs. external? What types of users/roles access our APIs? Where is the sensitive data accessed?”

To get better at API security, development teams need to understand what we call their application DNA, understand how it is changing, and be able to identify anomalies to detect and block legacy and new threats. These new threats require an understanding of the application context and user behavior to really distinguish the bad actors from the regular users. Can you elaborate on “application DNA?” What is that and why is it important for application teams to understand?

Sure. Application DNA is what we call the collection of data that defines what an application is made up of, how those parts interact, how each of those parts behaves, and how the different users of the application interact with each of those parts. Knowing this data is vitally important to be able to effectively secure modern applications. But in these modern applications, this data is continuously changing, so it is not only challenging to collect this data but even harder to keep it updated. This is why we created Traceable, to use distributed tracing and AI to make it possible for teams to create and maintain secure applications in these challenging environments.

Cloud-native applications have clearly become hackers’ favorite targets. These applications are all API-driven, with APIs exposing business logic to the outside world. Do you think the current application security approaches are built for modern application architectures?

With the explosion of cloud-native apps and services, we now have an explosion of services and microservices, all talking to each other using different APIs. This has also drastically grown the number of unique APIs that are being used. As such, the number of clients has exponentially grown, between mobile, IoT, and other services calling each other, and data has become the new gold. So, the data, this precious thing, we are constantly handling it, manipulating it, and passing it off to other services which might or might not be safe. In general, there’s now a lot more to keep track of, and the interactions between everything are now more varied, more complex, and harder to keep track of. This is serious. Today’s app architectures have added a whole new attack surface at the API level.

One of the fundamental problems is that people don’t even know what APIs are being used and which APIs have a potential security risk, or which APIs could be used by attackers in bad ways. How can we get better visibility?

Better visibility is a must to be able to secure today’s cloud-native apps. To accomplish this, I believe the industry needs to shift to what we call Security Observability. Security Observability is the combination of service relationships, API DNA, data flow and risk, and user behavior analytics. Together, these give the visibility that is so critical for securing today’s apps.

Traceable extensively leverages AI and ML. But it can also be safely said that AI and ML are still evolving in several functionalities. Historically, one of the biggest difficulties for AI has been to distinguish between legitimate users and malicious ones. How does Traceable solve this problem differently?

One primary challenge for us when we were developing Traceable AI was developing algorithms to efficiently analyze massive amounts of data to trace user activities and detect anomalies and potential threats (traditional tools often focus on IP addresses – Traceable works with user identity). Our data science team developed advanced methods and algorithms to extract the accurate identity of the user from the data stream. They also developed unsupervised AI models to detect changes and anomalies, which are often indicators of malicious activity or attacks. As a result, our AI algorithm can continually learn and determine the difference between nominal and abnormal activity.

More specifically, AI has been adopted heavily and successfully where image processing or natural language processing (NLP) can be applied. This mostly applies to domains where the data on which models are built are mostly static and deterministic and large amounts of supervised data exist. The challenge in cybersecurity is that every environment is different. Similar to applications and APIs evolving, hackers are continuously evolving as well. So, fixed rules or static models don’t work. Instead, the predominant strategy used is anomaly detection, which is a strategy to discover the proverbial needle in the haystack. However, anomaly detection has been plagued with issues of false positives, primarily due to the algorithms lacking context. Traceable addressed this by building the Traceable platform that helps gather as much application context as possible.

The second issue plaguing solutions that use anomaly detection for cybersecurity is poor correlation capabilities. It is very hard to track the attacker’s path within a gamut of time-varying data of high statespace complexity. Traceable has taken a unique approach leveraging graph learning algorithms by breaking down the problem in a unique way to constrain the statespace thereby enabling these algorithms to become viable. I think the future of AI in cybersecurity is in leveraging graphs and understanding users within an application context. Graphs are hard to work with, but by constraining the state-space they become a viable solution to an otherwise complex problem. I think this fundamental change in thinking is what is needed to address the cybersecurity issues of the future. Using graph machine learning to track users and their data and how data flows through the system is the key.

Cybersecurity and legal teams have often been operating in silos, but this needs to change. Several times, inhouse legal teams handle some of their company’s most sensitive and confidential data, and law firms face an even more daunting security challenge, having to manage the highly confidential and privileged data of all their clients. How can you eliminate these silos?

More than with every company that collects sensitive data from their customers, law firms and legal departments especially need to make sure they are protecting their client’s data. The API vulnerabilities that lead to data breaches in all companies are equally as effective in software used by legal organizations. The difference is that in certain instances the legally sensitive data might be considered a more valuable target. But there is another part to this, which is the importance of being able to prove that the sensitive data is not being leaked. Auditing sensitive data flow was challenging before so many applications became cloud-native. Now, where this sensitive data can be handled by tens or hundreds of microservices distributed around the globe, tracking the flow of sensitive data is even more difficult. Keeping in compliance with sensitive data requirements now requires holistic visibility of how the sensitive data flows across the entire distributed application landscape.

Where is the future of AI and ML in cybersecurity headed?

In general, regarding AI and ML’s role in cybersecurity, I think today we still get a lot of eyes rolling up when we talk about this, because unfortunately there has been a lot of AI-washing, where companies have latched on to AI and ML as buzzwords, but never really deliver using it. But just like with cloud and cloud-native, there was a time earlier in the cloud hype cycle where this also happened (cloud-washing, cloud as a buzzword, cloud-everything without true customer value, etc). Eventually, cloud technology and the values it provides became real and clearly defined. The same thing will happen with AI/ML for cybersecurity, and I am proud that our team at Traceable is advancing the science and art to evolve this space towards that clearly defined state.

What is in store for Traceable?

Traceable will continue its mission to make businesses and the software they rely on more resilient, and we will continue to bring our expertise to the table to rethink how modern applications and APIs can be secured, both in production and preproduction. We have a lot of exciting capabilities on the way, which I don’t believe anyone else can do, and I look forward to being able to share them with everyone.

This interview first appeared in the July 2021 issue of CISO MAG. Subscribe now!

Data Breach Affects 300,000 Reindeer Customers Data

data breach

While cloud computing is helping organizations in advancing their operations, data leaks due to cloud misconfigurations are giving nightmares to businesses. A threat analysis from cybersecurity research firm WizCase revealed a data breach that affected Reindeer, an American marketing enterprise. The now-defunct company provides digital marketing services to a vast number of clients across the globe. The security incident could have affected thousands of users’ sensitive information.

Information Exposed

Security experts at WizCase discovered a misconfigured Amazon S3 bucket that belonged to Reindeer, which contained over 50,000 files, totaling 32GB of data. The bucket is not password protected, allowing anyone to access the data. The exposed information included usernames, surnames, date of birth, email addresses, profile pictures, hashed passwords, Facebook IDs, residential details, and contact numbers of over 300,000 customers from various Reindeer clients. Most of the affected users in the breach are from the U.S., Canada, and the U.K.

“We reached out to Amazon regarding the breach. As the bucket is owned by a now-defunct company, the web host is the only contact we could find to help secure the breach. We also informed the US-Cert, hoping they would be able to reach out to the previous company owner,” WizCase said.

Accidental or Pure Negligence

Organizations should protect their customers data in the cloud even if they are going out of business. The sensitive information should be taken off from cloud infrastructures to avoid potential risks.

“This breach shows a concerning lack of due diligence on Reindeer’s part. While they seemed to have ceased working with these brands by 2014 at the latest, they still had access to all this sensitive information from hundreds of thousands of users and did not sufficiently secure it after the company’s closure. Even when a company goes out of business, it still possesses responsibilities to its users and its client’s users to keep their data safe,” WizCase added.

Risks Associated with the Data Breach  

Cybercriminals could leverage the leaked data to launch various cyberattacks including:

  • Vishing and Phishing attacks
  • Identity theft
  • Social engineering attacks
  • Brute force attacks
  • Trading the leaked data on darknet markets

Threat actors are always on the lookout for sensitive information online. It’s recommended to give only the required information on social media handles and while making online purchases.

Related Story:

3 Steps to Boost Your Enterprise Cloud Security

Alert! Fraudulent Call Centers Tricking Users to Download BazaLoader Malware

BazaCall BazaLoader

Microsoft 365 Defender Threat Intelligence Team uncovered an ongoing malware campaign tricking victims into downloading malware on the targeted systems. The campaign, dubbed as BazaCall, is reportedly leveraging bogus call centers and duping social engineering victims to download BazaLoader malware. Once deployed, the malware enables a remote attacker keyboard access to the infected system.

How does BazaCall Campaign work? 

The BazaCall campaign begins with an email sent from a compromised email account impersonating tech support and mimicking legitimate business names. The attackers usually create a sense of urgency in the email body, making the potential victims call the fraudulent call centers. Whenever users call, the scammers instruct them to install BazaLoader malware into their devices.

“Each wave of emails in the campaign uses a different theme of subscription that is supposed to be expiring, such as a photo editing service or a cooking and recipes website membership. In a more recent campaign, the email does away with the subscription trial angle and instead poses as a confirmation receipt for a purchased software license,” Microsoft said.

BazaLoader Capabilities 

The BazaLoader malware is capable of performing data exfiltration, credential theft attacks, and even deploy ransomware on the infected systems within 48 hours of compromise. Unlike traditional social engineering tactics, BazaLoader malware is not distributed via malicious URLs or files in the message body, allowing the malware to evade malware and phishing detections.

“BazaCall campaigns require direct phone communication with human and social engineering tactics to succeed. Moreover, the lack of obvious malicious elements in the delivery methods could render typical ways of detecting spam and phishing emails ineffective. Because the malware isn’t distributed via a link or document within the message body itself, the lures add a level of difficulty that enables attackers to evade phishing and malware detection software. This campaign is part of a broader trend in which BazaLoader-affiliated criminals in which they use call centers — the operators seemingly non-native English speakers — as part of an intricate attack chain,” Microsoft added.

System Administrator Appreciation Day 2021: Together for Better Security

System Administrator Appreciation Day

If your office computer is working fine under a secure network, it is because your system administrators work relentlessly to keep the organization running securely. The system administration personnel are responsible for various operations in an organization, such as software installations, updating computers and network systems, addressing vulnerabilities, troubleshooting, and building a security posture to provide a secure work environment.

By Rudra Srinivas, Senior Feature Writer, CISO MAG

System administrators are some of the most important employees in an organization.  And today, July 30, is celebrated as System Administrator Appreciation Day to honor and appreciate their continuous efforts towards business security.

System Administrator Appreciation Day

Ted Kekatos, a Systems Engineer at Netrix LLC, introduced the idea of System Administrator Appreciation Day after getting inspired by an advertisement in which a group of employees greets a system administrator for installing their new printer. Also known as SysAdmin Day, the System Administrator Appreciation Day is observed on the last Friday of July every year.

“Consider all the daunting tasks and long hours (weekends too.) Let’s be honest, sometimes we don’t know our System Administrators as well as they know us. Remember this is one day to recognize your System Administrator for their workplace contributions and to promote professional excellence. Thank them for all the things they do for you and your business,” says Kekatos.

Challenges Faced by System Admins

System admins, IT, and security professionals across the globe constantly face severe challenges in their daily work life. The emergence of remote work made the situation even more difficult. It has become a challenge for system admins to secure the distributed networks amid rising cyberattacks.

According to the 2021 Netwrix Sysadmin Report, 68% of system admins stated that they are worried about the increasing number of cyberattacks and data breaches, and 66% said their workload increased as a result. Over 38% of system admins admitted that there is a lack of tools to support remote work.

Other Challenges Include:

  • 40% of system admins admit that remote work diverted their attention away from security tasks.
  • 29% said that they are more focused on cybersecurity than they were pre-pandemic.
  • 79% of admins from the financial, retail, and health care sectors work more than 40 hours a week.
  • 51% of respondents say that the average salary for system admins in the U.K. and the U.S. is lower than expected.
  • 73% say their life would be easier if users would stop clicking on suspicious links or attachments.

Help Your System Admin

System administrators play a crucial role in protecting an organization’s digital infrastructure and sensitive information from threat actors. As a responsible employee, helping system admins by following basic cyber hygiene and learning how to spot potential security risks will boost the company’s security posture, eventually making the admin’s job easy.

How to Become a System Administrator

Currently, it’s hard to imagine a company without computers, and it’s also impossible to find an organization without a system administrator. Organizations value real-world knowledge and practical IT experience. And there is no substitute for diversifying skill sets. One should not limit their knowledge to help desk and desktop support but also train in areas such as database administration, scripting, and IT security.

Skills Required:

  • In-depth knowledge of various computers and operating systems
  • Familiarity with all hardware units
  • Cloud administration skills
  • Sound knowledge of different networks
  • Troubleshooting expertise
  • Incident response handling skills
  • Good communication skills to present the issue to the management

In addition to these, relevant certifications will also help individuals excel in the field. One can get started with EC-Council’s certifications like:

Not just today, let’s appreciate our system admins every day for their valuable contribution to the cybersecurity community.

About the Author:

Rudra Srinivas

Rudra Srinivas is a Senior Feature Writer and part of the editorial team at CISO MAG. He writes news and feature stories on cybersecurity trends.       

Read More from the author.


Iran Leak Hints at Second Tier Targets as Next Terror Gateway

Log4j, Iranian Ransomware Actors, SpoofedSccholars, second-tier targets, NIOPDC

In May 2020, CISO MAG reported about Project Signal, an Iranian state-sponsored ransomware operation.  State-sponsored actors from Iran have often been linked to various cyberespionage campaigns targeting organizations globally. A recent report by Sky News exposed a trove of documents that appear to be from a branch of the Islamic Revolutionary Guard Corps (IRGC), Intelligence Group 13. These findings show a coordinated attempt to collect information on the vulnerabilities of second-tier targets, including those that can capsize merchant vessels, the remote control of electrical controllers used in building management systems, and the ability to tamper with fuel pumps triggering spills or explosions.

Since 2019, hundreds of U.S. companies and local government agencies have fallen victim to cyberattacks. Now, leaked documents outline Iran’s intentions to gather information meant to attack Building Management Systems (BMSs) that are notoriously overlooked when setting up cybersecurity programs. BMSs are easy targets for two reasons. One, reliance on connecting building devices via the internet, even connecting to a remote facility that may operate vulnerable devices. Second, they are attractive to attackers since buildings rely on contractors to maintain facilities that may not follow proper cybersecurity practices, such as authentication and secure access.

Why second-tier targets are valuable

Ilan Barda, Founder and CEO of Radiflow“Many of these second-tier targets seem irrelevant at first,” said Ilan Barda, Founder and CEO of Radiflow, a cybersecurity company that focuses on securing OT facilities. “What makes them so valuable is their potential to be used as a gateway to building systems. Once inside, a hacker can manipulate air circulation units, elevators, and any other critical infrastructure to carry out physical attacks.”
Another concern in the Iranian cyber report is their intention to find vulnerabilities in specific satellite communication (SATCOM) gateways. In some countries, poorly protected wireless networks can be exploited by attackers, allowing them to access vulnerable Satcom terminals on the network. While some of the reports focused on hypothetical attacks, this piece showcased their potential for data collection and potential coordinated attacks.

A few questions to be answered

Michael Langer, a renowned cyberwarfare expert and CPO of RadiflowSome questions remain regarding the intention of the Iranian military hacking group. Upon reviewing the report, Michael Langer, a renowned cyberwarfare expert and CPO of Radiflow, believes that this report may only specify their intent to pursue cyber terror further. “Iran is looking to expand the outreach and objects of their cyber-attacks,” said Langer. “Their history of disruptive cyber offensives on Saudi Arabian oil refineries and Israeli water management facilities are to be taken seriously. The Iranians mapping of BMS vulnerabilities may indicate a shift to target more easily exploitable sites. It’s time to think differently.”

How can organizations defend themselves?

While these attacks are causing CISO and cybersecurity teams to take notice, the tools most companies need to secure their systems already exist. “Familiar basic-hygiene practices are common tools that a growing number of the population recognize,” said Barda. “Segmentation, password validation, two-factor authentication, and cyberthreat detection mechanisms can act as a deterrence for attackers.”

Many companies have seen recent headlines surrounding cyberattacks without realizing they may be next. However, simple precautions may be the difference between another day at the office or a cyberattack that deploys ransomware or exfiltration of sensitive data.

Radiflow is an OT Cybersecurity company that has unique tools to protect and manage digital assets for the long term. They work directly with Managed Security Service Providers to oversee the discovery and management of all relevant data security points.