Home Blog Page 324

Blockchain startup Provenance.io raises $20 million

Startup funding

Provenance, a blockchain technology services provider, recently secured $20 million in a funding round led by both blockchain and traditional technology investors to accelerate the development and expansion of its ecosystem. Established by Figure Technologies, Provenance.io is a fintech company that provides blockchain services to the financial services industry.

Provenance leverages the security, efficiencies, and cost advantage of blockchain for loan origination, financing, and sales. The company claims that it holds a diverse set of financial institutions, banks, and dealers are active on its blockchain platform.

“This is a seminal moment for the blockchain industry in financial services,” said Sheila Bair, former Chairwoman of the Figure Technologies. “Provenance.io has the potential to bring massive improvements to the industry, across asset originators, the buy and sell side, as well as regulatory benefits and better consumer protections. In particular, it will provide loan-level transparency around the quality of securitized assets and a clear, unalterable record of ownership—two things that were sorely missing during the financial crisis.”

“Blockchain technology will disrupt financial services in ways that unlock tremendous value through improving current processes but also introducing new ways to do business,” said Jenny Johnson, President and COO of Franklin Templeton, a founding node manager for Provenance. “We are excited to facilitate and support blockchain adoption because change will happen when the technology is embraced by the market. The technology platform combined with the ecosystem makes Provenance stand out.”

RiskLens secures $20 million to expand its leadership in CRQ

Funding

RiskLens, a provider of Cyber Risk Quantification (CRQ) and cyber risk management software solutions, recently secured $20.55 million in a Series B funding round led by Paladin Capital Group along with the participation from the existing investors Dell Technologies Capital, Osage Venture Partners, F-Prime Capital, and MassMutual Ventures. The startup stated the new investment will accelerate its Sales, Marketing, Engineering, Professional Services departments, and expand its market reach in the cybersecurity industry.

Founded in 2011, RiskLens provides cyber risk management software solutions that enable organizations to manage risk and measure it in monetary terms. The company claims its software is the most comprehensive suite to enable security and risk teams to quantify, manage, and report on cyber risks from the business perspective.

Commenting on the new investment Nick Sanna, Chief Executive Officer at RiskLens, stated, “RiskLens has forever changed the way large organizations assess, manage and report on cyber risk, by translating the impact of threats and vulnerabilities into the financial language of the business that everyone understands: dollars and cents. We’re giving Boards of Directors, CISOs and Cyber Risk teams what was once thought impossible – a decision-support platform and a system of record that allows them to make cost-effective decisions regarding the prioritization of security initiatives and the rightsizing of those investments.”

“As early believers in RiskLens since our participation in the Series A funding, we’ve seen first-hand the rapid shift of market momentum towards cyber risk quantification and the capabilities of its experienced management team in driving growth,” said Mourad Yesayan, Principal at Paladin Capital Group and RiskLens Board Member. “We believe that RiskLens is poised to become the de-facto standard in how enterprises around the globe assess, communicate and manage cyber risk.  We’re delighted to be partnering with a syndicate of top investors to continue fueling the company’s success.”

National Cybersecurity Center and Space ISAC partner to boost cybersecurity

Collaboration, partnership, alliance, KnowBe4 and Agari Partner to Prevent Identity-Based Email Attacks

The National cybersecurity solutions provider Kratos Defense & Security Solutions recently announced its partnership with the Space Information Sharing and Analysis Center (Space ISAC), which was unveiled at the 35th Space Symposium in Colorado Springs.

Kratos is a technology-focused, mid-sized defense and communications solutions firm that develops technology, security platforms, and systems for United States National Security and for private enterprises. The company claims that it’s specialized in cybersecurity, unmanned systems, satellite communications, microwave electronics, missile defense, hypersonic systems, training, and combat systems.

The new Space ISAC is dedicated to protecting the security landscape across the country’s infrastructure like aviation, financial services, and defense. The Center’s goal is to enhance the country’s cybersecurity abilities to prepare and respond to vulnerabilities, incidents, threats and serve as the primary communications channel for the sector.

Phil Carrai, President of Kratos Technology & Training Solutions Division, stated the formation of the latest partnership supports the White House’s National Cyber Strategy.

“The Administration will enhance efforts to protect our space assets and support infrastructure from evolving cyber threats. With industry and international partners to strengthen the cyber resilience of existing and future space systems. It is an honor for Kratos to support such an important initiative. Protecting space assets is becoming an increasing challenge, both from cybersecurity threats and from the increasing challenges in the RF domain in the form of jamming, unintentional interference, Space Situational Awareness and other growing threats. Only by sharing data and experiences across government and industry will we be able to counter them effectively,” Carrai added.

Facebook closes around 74 illicit groups that offered phishing services

Security researchers at Cisco Talos discovered 74 Facebook cybercrime groups with 385,000 members that offer hacking tools and email phishing kits on Facebook. According to the researchers, the groups were selling/buying stolen bank/credit card information, and phishing services. However, Facebook confirmed that it took down all of the groups after Talos reported the issue. The researches stated that criminal Facebook groups can be found by anyone with a Facebook account by searching with keywords like spam, carding or CVV.

“These Facebook groups are quite easy to locate for anyone possessing a Facebook account. A simple search for groups containing keywords such as “spam,” “carding,” or “CVV” will typically return multiple results. Of course, once one or more of these groups has been joined, Facebook’s own algorithms will often suggest similar groups, making new criminal hangouts even easier to find. Facebook seems to rely on users to report these groups for illegal and illicit activities to curb any abuse,” the researchers said in a blog spot.

Cisco Talos stated they’ve been tracking several illegal groups on Facebook for the past several months. It stated that most of the groups use names like Spam Professional, Spammer & Hacker Professional, Buy Cvv On THIS SHOP PAYMENT BY BTC, and Facebook hack, etc.

The news came after security experts from the cybersecurity firm UpGuard recently discovered that Facebook user account information was exposed on Amazon cloud servers. The security team at UpGuard stated that they found two data breach incidents in different regions. The first incident was originated from the Mexico-based media company Cultura Colectiva which exposed around 146 GB of data that contained over 540 million records detailing comments, likes, reactions, account names, FB IDs, and other sensitive information.

The second was a separate database from a Facebook-integrated app named ‘At the Pool’ which exposed data via an Amazon S3 bucket. This database contained the backup information like fb_user_id, fb_user, fb_friends, fb_likes, fb_music, fb_movies, fb_books, fb_photos, fb_events, fb_groups, fb+checkins, fb_interests, and passwords, according to UpGuard.

90 percent of Singapore businesses suffered data breaches last year: Report

Singapore cybersecurity

A recent research stated that cyber-attacks are increased in the last 12 months, causing security breaches affecting 96 percent of organizations surveyed. According to the research report from endpoint security firm Carbon Black, 90 percent of the Singapore businesses have been breached in 2018. In its report named Singapore Threat Report, Carbon Black examined the survey results from different industries, organization sizes, and IT team sizes to show modern attacks and cyber defense landscape in Singapore region.

According to the research findings, 96 percent of surveyed Singapore-based companies reported breaches last year and 92 percent of them said they’ve seen an increase in attack volumes. Also, 95 percent of the organizations stated the attacks have become more sophisticated and 97 percent of them stated they’ve planned to increase spending on cyber defense.

As per the findings, Ransomware is the most high-volume attack type in Singapore with 28 percent of the organizations stated they frequently encountered it. The Malware and Google Drive (cloud data breach) attacks were in second and third place at 25 percent and 11 percent respectively. However, the research also stated that human errors played a big part in the attacks that lead to breaches.

“Our first Singaporean threat report indicates that organisations in Singapore are under intense pressure from escalating cyber-attacks,” said Rick McElroy, Head of Security Strategy for Carbon Black. “The research indicates increases across the board in attack volume and sophistication, causing frequent breaches. In response, an encouraging number of Singaporean organisations are adopting threat hunting and seeing positive results. As threat hunting strategies start to mature, we hope to see fewer attacks making it to full breach status.”

The Singapore government recently formed Telecom Cybersecurity Strategic Committee (TCSC), a committee that is expected to publish a strategy for telecommunication operators to develop cybersecurity capabilities. It would also give other recommendations, including capability development, technology innovation, regulation, and international partnerships. While addressing at the inaugural of Infocomm Media Cybersecurity Conference, Senior Minister of State for Communications and Information Janil Puthucheary announced the road map to secure Singapore’s telecommunications infrastructure.

Security startup Aqua Security raises $62 million in funding

startup funding

The cloud-native applications provider Aqua Security recently announced that it has closed a Series C round of $62 million led by Insight Partners along with the participation from the existing investors Lightspeed Venture Partners, M12 (Microsoft’s venture fund), TLV Partners, and Shlomo Kramer.

Headquartered in Israel and the United States, Aqua Security provides a platform designed to help organizations secure cloud native, container-based and serverless applications. The startup claims that its Cloud Native Security Platform provides full visibility and security automation across the application’s entire lifecycle.

Aqua Security stated its solutions are available on the AWS Marketplace for Containers, the Google Kubernetes Apps Marketplace, and the Azure Marketplace. It holds a customer base in various sectors like in the energy, internet, aerospace, travel, media, hospitality, retail, and pharmaceutical sectors.

Commenting on the new investment, Dror Davidoff, the CEO and co-founder of Aqua Security said, “We are thrilled to have Insight Partners as investors to propel Aqua’s next phase of growth. The adoption of cloud native technologies provides an opportunity for security to be redefined, addressing the chronic cybersecurity skills shortage through automation, and creating applications that are secure by design. With this significant investment and our focus on the needs of enterprise customers and product innovation, we can take the next step to realize our vision.”

“As investors in several leading cloud technology providers, we were impressed by Aqua and its track record as a security leader in this hyper-growth space,” said Jeff Horing, co-founder and managing director at Insight Partners. “Aqua’s vision, their unrivaled investment in open source technologies, and deep relationships with strategic partners have created a tremendous opportunity as customers accelerate their move to cloud native platforms. We look forward to Aqua joining the Insight portfolio and seeing their continued growth.”

5 Questions CISOs Should Ask Themselves

active directory
active directory
aContributed by Hani Mustafa, CEO, Jazz Networks

CISOs are the cornerstone for managing the high-level risks of data security, which means they’ve got a lot on their plates. Detecting, responding, and protecting against threats requires them to maintain compliance standards and select a strategic mix of technologies to manage a strong security team and empower the company’s broader workforce to act effectively. (No pressure, right?)

The good news for CISOs is they’re not alone; there are tools that can help. Here are five questions CISOs should ask themselves to make sure they have the right tools and systems in place to better protect their company’s data people and reputation.

How much of our cyber approach is dedicated to proactive threat hunting vs. ongoing response?

As any C-level executive working in 2019 can tell you, the days of simply waiting for incidents to bubble up no longer holds water. Organizations are realizing that proactive threat hunting is the key to stronger protection and better understanding vulnerabilities. But for many, dedicating headcount to threat hunting versus incident response is not always possible. Putting out the biggest fires will always be necessary, but when these fires consume the majority of a team’s time, there are limited resources left to proactively look for potential weaknesses in the organization.

“More than a quarter of security practitioners interviewed by Intel Security report continuing to operate in reactive mode with a mostly ad hoc approach to security operations, threat hunting and incident response.”

Having a security platform that consolidates and contextualizes all endpoint and server events can enable smaller teams to tackle both threat hunting and quick incident response.

How often does alert fatigue impact our team’s ability to fully investigate events?

Alarm fatigue is real. We see it in our personal lives, healthcare, and just about all modes of transportation, and the consequences can be dire. Cybersecurity is not immune. As sophistication grows in UBA, DLP, and EDR technologies, the number of alerts, false positives, and notifications will continue to overwhelm security teams (nine out of 10 security practitioners report an inability to triage all potential threats). In an IT security survey by the Ponemon Institute, more than 37 percent reported facing more than 10,000 daily alerts; more than half of those alerts were false positives. What happens when there’s not enough time in the day to address every alert and an actual attack is overlooked?

Have we asked vendors the hard questions about their machine learning and AI? 

If you’re playing buzzword Bingo while reviewing your vendors, it won’t take long to hit a winner. But differentiating between who’s slapping machine learning onto their platform vs. who’s building tools that allow machine learning to continually improve efficiencies are two very different things.

“Demand a demonstration, not a presentation.” – Gartner

Ask your vendors the hard questions. Please explain your algorithms in detail. What are the specific trends and patterns targeted? Does the tool capture its own data? If not, how do you determine the reliability of the data? How do your algorithms react to data imperfections? And, can you show me how it really works? Dig deeper and it will quickly become clear when machine learning is going to offer true value and when it’s simply marketing speak.

Have I checked all of the boxes for GDPR compliance? 

The last year has been the most compliance-focused in the industry’s short (albeit intense) history. As such, security teams have had to shift time and resources to keep pace with new regulations. No longer do fellow executives ask their CISO ‘Are we secure?’ They’re now asking ‘How much will we be fined if we’re breached?’ GDPR has brought an additional set of regulations, expectations, and opinions to the industry.

“Quietly working out a plan will no longer be an option.” – Jacek Materna, on GDPR

In the case of a breach, Article 30 states that you need to have adequate data records for real-time auditing by a supervisory authority. And the 72-hour rule adds to the urgency of identifying the who and the what in a short amount of time. This means two things: you need to collect a lot of data on your users and you need to be able to find it quickly. Can your team do both today?

When (not if) a breach occurs, how quickly could we respond and control damage? 

Managing day-to-day threat response across numerous platforms is a headache. When a breach occurs, that headache becomes a migraine.

“There are only two types of companies; those that have been hacked and those that will be.” – Robert Mueller, former director of the FBI

If you’re one of the companies suffering from the growing security talent shortage, allocating additional resources to respond to a breach is not always an option. Consolidated endpoint and server visibility is crucial in minimizing the time to resolution and containing the impact of the breach. But above all else, technologies must enable you to get the most out of the resources you have available today to ensure the fastest recovery.

The opinions expressed within this article are the personal opinions of the author. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same. 

Cybersecurity firm Deepwatch secures $23 million investment

Startup Investment

Security services provider Deepwatch recently raised $23 million in a Series A funding round led by ABS Capital Partners.  The U.S.-based startup stated the new investment will be utilized to accelerate research and development for its machine learning security analytics platform and market expansion. Deepwatch offers intelligence-driven managed security services to enterprises with advanced cybersecurity team and SecOps platform.

Founded in 2015, Deepwatch delivers the differentiated security services to cybersecurity leaders, including exclusive maturity models, cloud SecOps platform, data-centric deployment models, named delivery squads, real-time collaboration, and portability and access.

Deepwatch claims that its cloud-based SecOps platform continuously evaluates, integrates, and tunes leading technologies into its platform to ensure the ability to support business requirements.  As per the investment deal, Michael Avon, a venture partner with ABS Capital, will be joining the Deepwatch board of directors.

Commenting on the new investment round, Deepwatch Founder and CTO Justin Morehouse, said, “When starting vSOC, our goal was to disrupt the managed security services industry. We succeeded through our relentless focus on customers, as well as providing a flexible, transparent, and carefully curated platform. Our vision is to redefine the industry, realizing the promises of data analytics and machine learning for our customers.”

“Cybersecurity leaders immediately recognize Deepwatch’s truly revolutionary approach to managed security services. Cybersecurity teams are overwhelmed, and Deepwatch is the answer as demonstrated by our 3,631% growth rate over the last 3 years, which places us among the Top 100 fastest growing companies,” added Deepwatch CEO, Charlie Thomas.

Data breach at Georgia Institute affects 1.3 million users

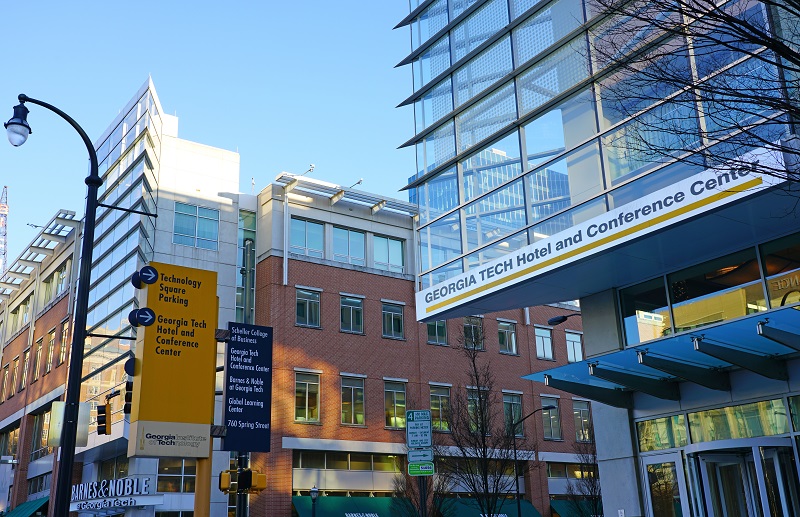
The Georgia Institute of Technology revealed that it suffered a data breach that exposed personal details of 1.3 million current and former faculty members, students, and applicants.

The Atlanta-based institute stated that the central Georgia Tech database was accessed by unknown intruders and compromised the school’s web application. The incident exposed personal information of up to 1.3 million individuals, which may include names, addresses, social security numbers, and birth dates. The institute also said its security officials are conducting a forensic investigation to determine what information was extracted from the system.

“A central Georgia Tech database was accessed by an unknown outside entity. Georgia Tech’s cybersecurity team is conducting a thorough forensic investigation to determine precisely what information was extracted from the system, which may include names, addresses, social security numbers and birth dates,” the school stated in a statement.

The institute notified the United States Department of Education and University System of Georgia about the incident. The affected users will be contacted as soon as possible regarding available credit monitoring services, the institute said.

Recently, the San Diego Unified School District also reported a data breach that affected more than 500,000 students and staff. According to the official statement, a phishing scam led to unauthorized access to the staff’s log-in information, including the network services and students’ database.

The security officials at the school district stated they discovered the breach in October 2018. It’s believed that the incident occurred between January 2018 and November 2018. The school district declared the compromised students’ information included social security numbers, names, date of birth, mailing address, home address, attendance records, ID numbers, and phone numbers. Some staff members’ information like payroll, deduction information, tax information, direct deposit financial institution name, account number, salary, and leave information was also compromised.

Millions of Facebook user data exposed on Amazon cloud server

Researchers from the cybersecurity firm UpGuard recently discovered that Facebook user account information was exposed on Amazon cloud servers. The security team at UpGuard stated that they found two data breach incidents in different regions.

First incident was originated from the Mexico-based media company Cultura Colectiva which exposed around 146 GB of data that contained over 540 million records detailing comments, likes, reactions, account names, FB IDs, and other sensitive information. The second was a separate database from a Facebook-integrated app named ‘At the Pool’ which exposed data via an Amazon S3 bucket. This database contained the backup information like fb_user_id, fb_user, fb_friends, fb_likes, fb_music, fb_movies, fb_books, fb_photos, fb_events, fb_groups, fb+checkins, fb_interests, and passwords, according to UpGuard.

UpGuard stated the data was stored in Amazon’s cloud service without password protection and could easily be accessed by outsiders.

“The public doesn’t realize yet that these high-level systems administrators and developers, the people that are custodians of this data, they are being either risky or lazy or cutting corners,” said Chris Vickery, director of cyber risk research at UpGuard. “Not enough care is being put into the security side of big data.”

A couple of months ago, the Ministry of Information and Communications (MIC) of Vietnam stated that Facebook violated its new cybersecurity law by allowing users to post anti-government comments on its platform. The concern was raised at a media conference held by MIC’s Authority of Broadcasting and Electronic Information (ABEI). The ABEI stated the social media giant had violated Vietnamese cybersecurity laws in three major areas: managing content, online advertising, and tax liability.

The new cyber law requires Facebook, Google, and other international tech firms to store local users’ data on local servers and set up offices in Vietnam. It prohibits Internet users in Vietnam from spreading anti-government information and posting false information that could cause damage to the country. It also prevents the circulation of content that’s fake, slandering, or inciting violence.