Home Blog Page 289

Around 50,000 Cyber Frauds reported in India during 2018-19: RBI

Threat Alert! Attackers Use Malicious Email Accounts to Launch BEC Attacks

India’s central bank, the Reserve Bank of India (RBI), has revealed that it discovered around 50,000 cyber frauds in the country’s Scheduled Commercial Banks (SCB) in 2018-19 fiscal.

In reply to an RTI (Right to Information) query, the RBI stated that cybercrimes are related to ATM, debit and credit cards, and internet banking. It notified that over 50,547 banking frauds occurred in the SCBs that resulted in a loss worth of Rs. 145.08 crore in the last fiscal.

According to the RBI, the total number of banking frauds, including cyber, detected in all the SCBs are 59,826 and the loss incurred is around Rs. 67,432.26 crore. More than 4,269 frauds occurred due to insiders in the banks, involving Rs. 1,014.97 crore loss during the period, RBI added.

In order to curb rising cyber incidents on monetary transactions, RBI recently announced an enhanced security mechanism as part of its agenda for the fiscal year 2018-19. The newly proposed mechanism is intended to provide high-level protection against cyber-threats.

“In an endeavor to strengthen the cybersecurity posture of Indian banks, focused and theme-based IT examinations are planned during 2018-19. Targeted scrutiny, as and when required, would also be conducted for appropriate policy and supervisory intervention,” RBI stated in its annual report.

The RBI’s report said the new agenda includes taking effective steps to initiate the process of developing a cybersecurity culture, endeavor to make cybersecurity a responsibility, and ensure confidentiality, integrity, and availability of information system and resources. According to the report, the new private sector and foreign banks accounted for 36 percent each of all cyber frauds reported in debit, credit, and ATM cards.

With digital transactions witnessing a significant rise, the Indian central bank stated that it’s reinforcing data protection, cybersecurity, and Know Your Customer (KYC) norms to make them more effective.

“With the emerging threat landscape, where organized cybercrime and cyber warfare are gaining prominence, the Department (of Information Technology) is working towards ensuring continuous protection against changing the contours of a cybersecurity threat,” the RBI added.

Cyberinc partners with InfiniVAN

Collaboration, partnership, alliance, KnowBe4 and Agari Partner to Prevent Identity-Based Email Attacks

Cybersecurity startup Cyberinc recently announced its partnership with InfiniVAN to provide local web isolation cloud solutions in the Philippines. The alliance integrates Cyberinc’s Isla Isolation Cloud with InfiniVAN to bring a fully isolated secure internet connection for the users in the region.

Based in California, Cyberinc helps public and private enterprises get a safer internet by proactively preventing email, web, and document-based threats. The company claims that its Isla Isolation Platform uses cutting-edge isolation technology to defuse threats.

Commenting on the new partnership, Samir Shah, CEO at Cyberinc, said, “The InfiniVAN approach to delivering business internet service at par with global standards with world-class fiber optic network infrastructure perfectly aligned with the Cyberinc vision of providing completely secure browsing experience to our customers. Together, we can help our customers scale their cyber defenses and safeguard against an increasingly relevant global problem. We see that Remote Browser Isolation can reduce the attack surface against web and email-based attacks, making the endpoints and networks safer. Our partnership with InfiniVAN will deliver next-generation security solutions to our customers.”

Koji Miyashita, Chairman InfiniVAN, said, “Choosing to partner with Cyberinc was an easy choice for InfiniVAN. Cyberinc’s Isla Isolation Platform provides the security our customers want, in a way that allows them to obtain a secure connection faster by selecting it as a part of their subscription to our internet services or as an add-on functionality. It’s simple to deploy, easy to use, always-on security, that makes cyber defense easy for our large and small customers.”


1,000 percent increase in DNS amplification attacks since 2018

Digital Transformation

By Augustin Kurian

The second quarter of 2019 saw a major swelling of DNS amplification attacks reaching a whopping 1,000 percent spike. The report titled “Nexusguard’s Q2 2019 Threat Report” points out that increasing adoption of Domain Name System Security Extensions (DNSSEC) highlights the massive surge in DNS amplification attacks. The report also highlighted how several government domains and even Paypal.com, became victims of DNS abuses.

To delve deeper into this, CISO MAG had an exclusive interview with Tony Miu, research manager at Nexusguard. Tony comes in with more than 12 years of experience in cybersecurity, including nine years’ experience in network security and DDoS mitigation technology.  As a battle-hardened veteran in the DDoS battlefield, he has garnered invaluable experiences and secrets of the trade, making him a distinguished thought leader in DDoS mitigation technologies. At Nexusguard, Tony leads the “Red Team” to find and fix vulnerabilities of the defense system from the attacker’s perspective and contributes to system and feature upgrades. As a dedicated researcher, he keeps an eye on the DDoS landscape focused on the researching of attack methods, patterns and defense techniques.

The revelation highlighted an alarming trend. Within a year there has been a massive surge. Did the report come as a shock to you that DNS amplification attacks are up by 1,000%?

Since Q1 2018, we have observed the tendency of attackers to use new, more advanced and stealthy methods to generate amplification attacks on their victims. In doing so, they have been constantly on the lookout for new methods that allow them to boost attack firepower at the highest amplification efficiency possible by taking advantage of, or exploiting vulnerable, ill-designed, badly configured or unsecured network devices or resources. As a result of this trend, amplification attacks skyrocketed 660.92% year on year in Q1 2019. Indeed, their pursuit of more cost-effective, stealthy and potent attack methods never ends. Now taking advantage of the additional response packet size generated by DNSSEC-enabled servers to reflect amplified attack is their latest favorite, which has proved to be successful as the DNSSEC implementation finally takes off.

DNSSEC has been around since 2010 but were not widely deployed in the first few years. Back to as early as 2013, we were aware of the potential of DNSSEC-enabled DNS servers being abused to launch DDoS attacks, in particular, reflection/amplification attacks, owing to the fact that DNS responses for a DNSSEC-signed domain are much larger than those for an unsigned domain. Due to the addition of a few new record types to DNS servers implemented with DNSSEC, the extra response size is large enough to contribute to attack traffic. So, this comes as no surprise to us at all that DNSSEC-aided DDoS attacks are now on the rise. It is just a matter of time for the wider industry to acknowledge it.

Over the years DNSSEC has been gaining acceptance as the patch, it is now causing a new set of problems for organizations. How is the cybersecurity industry responding to this?

DNSSEC provides a solution to DNS cache poisoning, which could spell big trouble for website owners by making their domains completely inaccessible and/or redirecting innocent visitors to malicious phishing sites. Therefore, it is understandable and necessary for ICANN and regulatory bodies to call for full deployment of DNSSEC across all unsecured domain names.

According to our Q2 findings, multiple government websites and paypal.com fell victim to rampant abuses. We then found out that many of these domains had actually deployed DNSSEC to the top-level .gov domain as required by the US government’s OMB mandate. So it leads us to believe that their DNSSEC implementation was one of the major causes of the sharp rise in DNS amplification attacks in the quarter. Now that with less than 20 percent of the world’s DNS registrars having deployed it, according to the Regional Internet address Registry for the Asia-Pacific region (APNIC), the continued implementation of DNSSEC will cause DNS amplification attack activities to continue to grow exponentially.

The abuse of DNSSEC-enabled servers once again demonstrates attackers’ pursuit of more stealthy, resource-effective tactics. Against this background, service providers and enterprises MUST prepare their networks for the continued rise of DNS amplification attacks. The effectiveness of DNS amplification attack mitigation hinges on whether the bandwidth capacity is large enough. However, as DNS amplification attacks continue to increase and as more DNS servers are likely to be abused to amplify malicious traffic, the asymmetry between attackers and defenders will only widen as time goes by.

One traditional mitigation method used by the industry is to drop abnormal DNS requests originating from the most frequently abused domains, such as 1×1.czcpsc.gov, etc. In doing so, the number of requests to the same domains or source IPs also has to be limited. Another commonly used method is to block all “ANY” queries outright. But given the growing DNS security risk, which even exposes government networks to abuses, the old way of protecting the DNS used by the industry is no longer sufficient. Attackers can evade these simple protections by sending small requests to a large number of different domains. The industry must, therefore, ensure that advanced protection is in place to safeguard their DNS servers.

There has been a lot of talks about the need for DNSSEC. The abuse of DNS was not something that was anticipated. Is the cybersecurity industry even aware of such a problem?

Over the past few years, a dozen other security vendors/researchers have also published reports/papers to shed light on the potential DDoS problem caused by the increased response size due to the longer records generated by DNSSEC-enabled servers. But the sharp rise in DNS amplification attacks in Q2 2019 and their causal relation with the implementation of DNSSEC by a number of government domains is largely unnoticed at the time of our report.

For perpetrators, the cost of launching DNS amplification attacks is and will remain low as long as they keep using the simple “ANY” query. Whereas in the past they needed to identify domains with DNS records that are long enough so that they could leverage the amplification power to boost firepower. Now as the implementation of DNSSEC is gaining momentum, more domains are equipped with an unintended capability that can be exploited to amplify malicious traffic by 36-72 times, making them an ideal launchpad to generate powerful attacks.

In the case of Memcached attacks (which we also reported in March 2018), attackers abused the publicly accessible Memcached servers (which however were supposed to be closed to the public) deployed by thousands of organizations ranging from universities and government agencies to leading ISPs, hosting providers and domain registrars. Our discovery of the piecemeal method used to carry out the “bit-and-piece” attack on ASN-level networks also suggests that attack methods have been evolving and remain so in the years to come.

How can a CISO or the head of security/technology respond to attacks like this considering the fact that a major part of DDoS attack occurs from mobile devices? How does he/she safeguard employees?

Mobile devices are not directly relevant to the rise of DNSSEC-aided amplification attacks. But the rise of mobile botnets DOES deserve the industry’s attention. Botnets have traditionally sought to compromise desktop computers, but our findings confirm the continued shift to mobile devices, creating a new breed of botnets.

According to our findings in Q2 2019, application attacks were more prevalent than network attacks. After tracing the source IPs of some of the application attacks, we found that most source IPs originate from mobile gateways. In other words, mobile devices were responsible for most of the application attacks captured in the past three months.

By OS, about 4.3 percent of the application attacks originated from Android devices, while about 20 percent came from IOS devices. Other platforms such as BlackBerry contributed to an insignificant share. Of course, we are not talking about how insecure mobile devices are, because we believe a lack of security awareness among end-users is the greatest inhibitor to defending against DDoS threats.

Smartphones and connected devices have already become an inevitable part of our fast-paced lives, but they also come with security vulnerabilities. From our observation, IoT botnets have been advanced to mount more complex, destructive DDoS attacks since December 2018. The upcoming 5G will further increase their firepower. As we move forward in the 5G era, make sure your system is thoroughly protected from DDoS threats so that mission-critical services are always available. Employees, as with all smartphone users, are advised to keep their OS up-to-date at all times, set secure passcodes, vet apps before installing them, etc.

For DNS owners, in particular, protecting their servers from being abused to reflect attack traffic is an integral part of their DDoS mitigation strategy. Because attack sources can easily be traced back to the owner’s hosting DNS server, the organization’s reputation is severely undermined if it is found that it is behind DDoS attacks unknowingly or due to negligence. As said, DDoS attack methods will always evolve, the DNS as an organization’s critical network service requires dynamic protection that adapts to actual requirements and evolving threats. Log reviews, security checks, auditing, as well as security posture, infrastructure and governance reviews, for example, must also be included as part of one’s security measures.

Augustin Kurian is part of the editorial team at CISO MAG and writes interviews and features.

Data Breach Exposes Almost Everyone’s Information in Ecuador

Ecuador Data Breach

Almost everyone in Ecuador became a victim of a massive data breach that exposed the personal information of over 20 million individuals, including the country’s president and WikiLeaks founder Julian Assange, who was granted asylum by Ecuador in 2012.

Security firm vpnMentor discovered the breach on a Miami-based Elasticsearch server owned by an Ecuadorian company Novaestrat. It’s said that the exposed data appears to have come from various sources, including the Ecuadorian national bank, Ecuadorian government registries, and an automotive association called Aeade. The exposed information includes names, date of birth details, contact information, National identification numbers, bank account details, taxpayer-identification numbers, and driving records.

The unprotected database was taken down on September 11, after vpnMentor notified Ecuador’s CERT (Computer Emergency Response Team). vpnMentor opined that the breach could bring some severe ramifications in the future. In case the data was obtained by cybercriminals, they could use it to launch phishing attacks, scams, identify theft, and fraud.

“In addition to personal information, the data breach also revealed details related to various companies in Ecuador. Some of the exposed information may be sensitive. We were able to view many companies’ Ecuadorian taxpayer identification number (RUC), along with each company’s address and contact information. The database also listed each company’s legal representative and provided their detailed contact information,” vpnMentor said in a statement.

Ecuador isn’t the only country to suffer a data breach like this. Recently, the Bulgarian tax agency suffered a breach that affected around 5 million Bulgarians of the country’s 7 million population. The Bulgarian police have arrested the suspected hacker who allegedly stole the data and emailed download links to local media agencies. The police launched an investigation to know the damage occurred due to the incident.

It’s believed that the compromised data belonged to the country’s National Revenue Agency (NRA), a department of the Bulgarian Ministry of Finance. Boyko Borissov, the Bulgarian prime minister, called an emergency meeting after the cyber-attack.

Google Discovers ‘built-in security key’ Flaw in Chromebook 2FA

Chromebook vulnerability

Search engine giant Google is asking Chromebook users to update their devices after discovering a critical vulnerability in its two-factor authentication procedures. The vulnerability, named ‘built-in security key’, affects the Chrome OS feature, which allows the users to use the Chromebook device like a USB device or a Bluetooth security key. The attacker can exploit the flaw to compromise the private key and obtain users’ passwords and usernames.

With the Chrome OS feature, the Chromebook users can process the authentication with just a short press of the power button instead of waiting for onetime 2FA code. “We confirmed that the incorrect generation of the secret value allows it to be recovered, which in turn allows the underlying ECC private key to be obtained,” Google said in a statement.

Google stated that Chrome OS v75 will release a new version 0.3.15 of the firmware to fix the issue.

Recently, Google revealed that scammers are making phishing attacks, by abusing Google Calendar services, to trick users into giving away sensitive information like passwords, card details, and other financial data. The threat intelligence and cybersecurity firm Kaspersky stated that it detected many unsolicited pop-up calendar notifications sent to Gmail users by cybercriminals as a sophisticated spam email attack.

“Spam and phishing threats that exploit non-traditional attack vectors can be lucrative for criminals, as they can often successfully trick users who might not fall for a more obvious attack. This is particularly true when it comes to trusted legitimate services, such as email calendar features, which can be exploited through so-called “calendar phishing,” Kaspersky explained.

The calendar phishing emails exploit the automatic addition and notification of calendar invitations feature for people using Gmail on their mobiles, according to Kaspersky.

Traditional user awareness model is doomed to fail

user awareness

By Sarb Sembhi

If current user awareness is still relevant today, why is every security event full of CISOs complaining about users or passwords? After 20 years of user awareness, discussing passwords, and not clicking on links in emails the security industry is still talking about these as if they are new requirements. Where are the results which prove that the current model has worked, and will continue to work?

What is wrong with the current model?

The current model was for yesteryear not for today and it certainly is not fit for purpose for tomorrow. Here are some of the reasons that make it unfit for purpose to continue to use it in the way it has been.

1. The world view of the current model is inadequate for today’s requirements

The traditional model for user awareness is based on the users having 90 percent of their usage and computing behavior developed in the workplace. This is no longer true today as the total time employees spend on a computing device / online at work may amount to 30 percent or less. This means employee behavior is more likely to be as a result of what they do and how they do outside of work.

Although the existing model relies on changing employee behavior during work time the reality is the other way around now.

2. The user awareness model of changing behavior is flawed

Marketing training and books often state that it takes 15-20 views of a single ad before it invokes action. Public awareness campaigns often assume years of promotion; however, many have often been backed by legislation with advertising before and after. Examples of these include, wearing seatbelts, drunk drive, use of mobile phones whilst driving, etc.

The advertising profession has shown that it is unreasonable to expect any action from individuals by showing them a message less than 15-20 times over a short period of time. User awareness programs cram and fire out several key messages throughout the year.

3. The current model assumes it is the sole provider of security information

Any service or project that is implemented as if it has a monopoly on providing that service but falls short of providing it, is going to fail both the user and by itself. Providing security information is not, and should not, be the sole responsibility of the enterprise. Enterprises of all sizes are responsible for their role in educating users, but the program should not be the only source of information.

4. Vendor resources are not utilized or leveraged adequately

Enterprises invest in lots of tools from vendors on everything from anti-malware, to threat intelligence to firewalls, email filtering, etc. Almost every single vendor allocates funding to produce resources, most of them would be happy to produce resources for users.

5. The focus of impact are only the enterprise’s priorities

Most user awareness programs focus on mandatory regulatory topics and the current flavor of the month for the top threat. A wider approach would work better, e.g. the success of cybercrime has led to its increase, so to not include the reduction of cybercrime as an objective is a mistake, as it would to not focus on what users want to, or need to learn, to encourage them to learn about protection independently.

6. User awareness topics and resources often lead to negative follow-on conversations

For example, the most common conversation about GDPR after training is: “What a big pain it is having to work on it, with it, around it,” etc. If GDPR is taught well, it could lead to continuous conversations about the rights of individuals and whether or not the enterprise is respecting them. Positive conversations are more likely to extend to contacts outside the enterprise where people have a real and meaningful dialogue. Conversations which extend beyond the enterprise may lead to further dialogue within the enterprise on practices and processes. All effectively covered topics should lead to extended discussions beyond the training.

7. The lack of leading research into what works or works well

When it comes to risk, enterprises can refer to frameworks and standards for reference and determine what should be included and what may or may not work for the enterprise. There is a lack of quality research challenging user awareness. Information and articles are mostly self-perpetuating the current model (to sell more services), rather than challenging it. Most user awareness approaches tend to impart lots of messages in the cheapest and quickest way possible, and in the least number of times possible, but without research on whether it is an effective approach.

8. The concept of the user as a control is limited due to the model’s narrow view of the world

Most users are non-malicious, responsible and conscientious about getting their work completed to keep their job (and perhaps develop a career). In theory, due to their good intentions, most employees should be excellent at taking all actions necessary to restrict malicious acts, actions, and consequences. In practice, most employees have more work than the time available to do it. This means they need to develop skills to skim read everything, even when they open fraudulent emails and links to vulnerable websites.

The requirement for employees to develop skills to achieve results are in contradiction to those taught in awareness training, and thus leaves employees as unreliable control mechanisms to limit mistaken clickthrough’s. Employees cannot be alert and vigilant at all times, especially when they are given demanding workloads.

9. Right tool for the right job

User awareness is a tool, and experts often recommend using the right tool for the right job. The unexplored questions are: What is the correct job for user awareness? What should it be used for and why? Is it the only tool that should be considered for the job?

If the tool that enterprises are using (user awareness) to change behavior is flawed because of the way it is deployed in the enterprise, then should it still be used?

10. Where users spend their online time and develop their lasting behavior habits

Twenty years ago, employee time on the Internet for work was research related rather than personal browsing. At home, they probably had one connected device for the whole household. Since then mobile phones, tablets, and other devices have come into our work and home lives. Today’s households may have at least one but up to three or more devices per person.

People are not only connecting more devices and doing more on the internet, but they are spending more time online out of work than at work. Today, employees may spend 30 percent or less time online at work and 70 percent of online time outside of work.

The behavior habits of employees are being formed outside of work, and then brought into the workplace. Since they can form these habits uninhibited and uncontrolled, these are the habits that are likely to stick with them more permanently.

11. Threat and risk behaviors outside of work will be brought into work

Employees often trust the security of their work environment more than their home environment; consequently, they were happier to do their personal online banking at the workplace. As smart devices can be connected to any wireless network anywhere, people have connected to them anywhere, and do not worry enough about security and the threats that they may be exposing themselves to. There are several mistaken beliefs behind this, including the thought that they don’t have anything criminals would want. This has had the effect of people connecting to anything and accessing anything, because the harm may not be apparent, immediately.

The threat of oblivious employee behavior outside of work reflects their behavior at work.

12. Devices, connections and interconnectivity

The threats are compounded by the recent onslaught of new consumables—the health, home and surveillance devices and services now available. The media has highlighted several examples of the lack of basic security in many devices with little impact on sales of those devices. With the average home expecting to have around 30-80 connected devices in the next few years, there are concerns that secure devices are made vulnerable by other vulnerable devices.

The habits that people form when purchasing, installing and using these new devices will form the basis of how they respond to and deal with new technologies at work–this is apparent in the reports of shadow IT in the workplace.

13. Defenses required to stay safe

The defense mechanisms people needed to stay safe and secure 20 years ago were just an anti-malware package. This is not true today where people need so much more, not only due to the vast range of devices that they will misconfigure for their home network but also because organized crime has realized that cybercrime is more profitable than other forms of crime.

Devices and the threats in the home have increased, but education and prevention tools have not. Therefore, employees working from home may be exposing their devices to more threats than ever.

14. Metrics for User awareness

Articles on user awareness do not consider it as a tool for the job. If it is not the right tool for all that it is used for, then is the metric still relevant?

When your only tool is a hammer and the only metric you have is how well you’ve hammered something into something else, should you not be re-examining the situation to redefine the response required and additional tools required for the toolbox?

15. Metrics obsession have driven vendors into dumbing down

The obsession CISOs have with metrics and in using them is well known. When a vendor has approached them with good solutions that don’t check the traditional user awareness box, or the related metrics for it, the vendor has had to dumb down their product and services to make them saleable. This drives market innovation down, not up, and will continue to do so unless the model changes.

Insanity

Insanity is to keep doing the same things and expecting different results. User awareness models have duped the security industry into believing that it is the only tool for the only job that needs to be done.

User awareness training models used 20 years ago, when users spent all their online time at work, could have achieved the behavior changes required from the training. But today, when a majority of the time spent online, and online habits are likely to be developed outside of the work environment, user awareness on its own is not going to achieve the desired behavior changes required by regulators and legislation.

New approach

We need an alternative approach which incorporates the way that the world, devices, e-commerce, the internet, people and people lives have changed over the last 20 years, and one that tries to foresee upcoming developments.


With inputs from Sarah Janes, Director Layer8 Limited, Liz Fenton, Director Urban IQ Limited, and Flavius Plesu, CEO OutThink Limited.

Sarb Sembhi CISM is the founder of Security2Live and CTO & CISO of Virtually Informed.

The Black Hat Hackers who Turned Over a New Leaf

Ethical Hackers

By Rudra Srinivas

Ever since IBM’s John Patrick coined the term ‘Ethical Hacking’ in 1995, the profession has grown to become a much-needed aspect in security programs. The growing popularity of certification courses on ethical hacking and bug bounty programs illustrates the importance of ethical hackers for today’s businesses.

But still, the term ‘Ethical Hacker’ conflicts with the image of hackers, which is portrayed as cybercriminals. Apart from data security personnel and government regulators, most people might not be familiar with ethical hacking. A look at the history of some notable ethical hackers possibly mitigates the negative connotations around it. Below are some of the famous ethical hackers around the world:

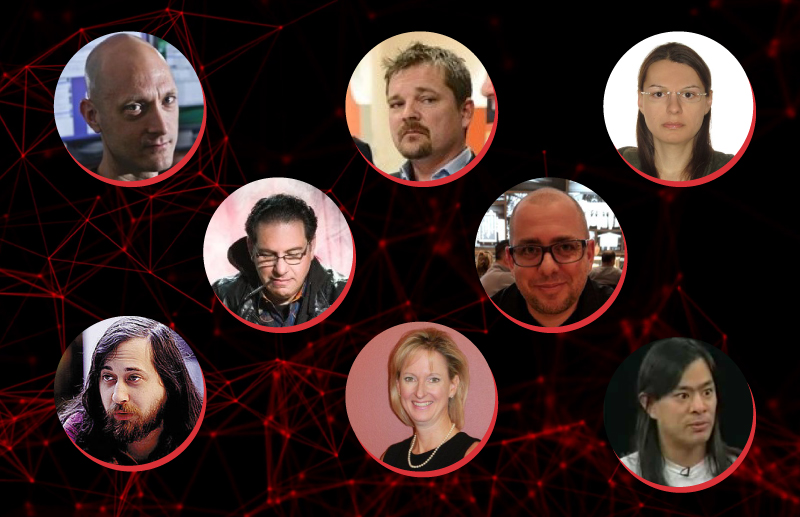
Kevin Mitnick

Kevin Mitnick is an American computer security consultant, author, and a black hat turned white hat hacker. He’s best known for his high-profile arrest in 1995 by the FBI for his various black hat escapades. Kevin Mitnick was an inveterate hacker since he was 13, using his social engineering skills to trick people into giving up passwords and other security information. His black hat escapades included stealing software from DEC systems and obtaining unauthorized access into Pacific Bell voice mail computers. He holds the distinction of being the first hacker to make the FBI’s Most Wanted list, but he’s now using his skills to do good. Kevin Mitnick is now a trusted security consultant helping consumers protect their information against threats. He also runs his computer security consultancy firm, Mitnick Security Consulting LLC.

Tsutomu Shimomura

Tsutomu Shimomura is a cybersecurity expert, physicist, and is credited with tracking down Kevin Mitnick. Being a computational physics research scientist, Shimomura also worked for the National Security Agency (NSA). He was known to be one of the leading researchers who raised awareness of the lacking security and privacy of cellular phones at that time. The founder of Neofocal Systems used his security skills for ethical purposes and played a key role in bringing Kevin Mitnick to justice. His book Takedown was later adapted to a film called Track Down.

Richard Stallman

Richard Stallman is an American free software movement activist, software developer, noted hacker, and founder of the GNU Project. Stallman was a programmer at MIT’s Artificial Intelligence Labs, where he constantly engaged in hacking activities. The creative computer programmer who strongly believed in freely modifying and sharing computer codes left MIT over concerns about software copyright rules.

According to him, a hacker means someone who enjoys playful cleverness. Stallman invented the concept of Copyleft, a legal mechanism that allows all programmers to use, modify, and redistribute a program’s code.

Charlie Miller

Charlie Miller, a security researcher, is best known for exposing vulnerabilities in Apple products. His most famous white hat achievements include discovering a critical MacBook Air bug at a Pwn2Own contest in 2008, from which he pocketed a $10,000 prize, beating the Safari security system in 2009, and finding security flaws in Apple’s iPhone and iPad.

Miller worked for the National Security Agency for five years as a computer hacker. He then worked for Twitter’s information security team as well as the autonomous vehicle security team at Uber. He currently works as a security researcher for Cruise Automation.

Greg Hoglund

Greg Hoglund is a specialist in computer forensics who worked with the U.S. Government and the Intelligence Community, providing his white hat capabilities to the pursuit of justice. He’s best known for his work in physical memory forensics, attribution of hackers, and malware detection.

In 2003, Hoglund founded HBGary, a company focussed on security, which later joined the McAfee Security Innovation Alliance in 2008. He also founded multiple security companies and is a frequent speaker at computer security conferences like Blackhat, DefCon, Infosec, and SANS in the U.S., EU, and Asia.

 Joanna Rutkowska

Joanna Rutkowska is a computer security expert and the founder of Qubes OS, a security-focused desktop operating system. She’s best known for her research on low-level security and stealth malware. Rutkowska became known after she presented the vulnerabilities in the Vista kernel at the Black Hat conference in Las Vegas in August 2006.

Her fame as a whitehat hacker grew after she exposed numerous attacks on virtualization systems and Intel security technologies, including the famous series of exploits against the Intel Trusted Execution Technology (TXT). Her skills earned many invitations to speak at prominent conferences like RSA, RISK, Black Hat, the Gartner IT Security Summit, and others.

Sherri Sparks

Like Joanna Rutkowska, Sherri Sparks is a security researcher and made rootkits and stealth malware her pursuit. Sparks is the President of Clear Hat Consulting, specialized in Windows kernel and hypervisor development, which she co-founded in 2007 along with Shawn Embleto.

Her ethical hacking skills became known after she exposed how operating system-independent rootkits, such as the proof-of-concept System Management Mode-based rootkit she built could be used to compromise computer networks at Black Hat Conference 2008. She has given various demonstrations at RSA, Black Hat, and other IT security summits on her research interests which include offensive, defensive stealth code technologies, and digital forensics.

Marc Maiffret

A high school dropout, once the bad boy in a hacking group called Rhino9. After being raided by the FBI at the age of 17, Marc Maiffret realized that his hacking skills could be used for good.

He started his new beginning by co-founding security software company eEye Digital Security, which was credited for exposing vulnerabilities in Microsoft products such as the Code Red worm. The renowned security researcher and entrepreneur went on to create vulnerability management products and web application firewall products, which have been recognized with numerous awards.

“For much of my career I’ve had an opportunity to help technology vendors stay ahead of the bad guys through vulnerability research that identified potential weaknesses in the IT infrastructure before they could be maliciously exploited,” said Maiffret.

Maiffret served as Chief Technology Officer at vulnerability management firm BeyondTrust, which acquired eEye Digital Security. He also served as a Chief Security Architect at anti-malware firm FireEye. In 2015, Maiffret left BeyondTrust to embark his second security venture.

Rudra is part of the editorial team at CISO MAG and writes on cybersecurity trends and news features. 

Security Researcher Discovers Vulnerability in New iPhone 11 Series

apple vulnerabilities

It has just been unveiled and already security researchers have already figured out the flaws in the new iPhone 11, 11 Pro, and 11 Pro Max.

Security expert Jose Rodriguez stated that he discovered a Zero-Day Exploit in the newly launched (yet to launch in some places) iPhone 11 series. Rodriguez revealed, in a tweet, that an attacker can exploit the bug in the new devices and their operating system iOS 13 to bypass the lock screen and access the phone’s contact information. Rodriguez even published a video demonstrating how to crack the device.

“With No Enter the Passcode you can see contact info. Will Apple change this feature before the release of iOS 13?” Rodriguez tweeted.

However, Apple may not fix the exploit before the release, but only with the iOS 13.1 update. Hope the researcher gets an official bounty for his discovery.

Recently, a Google Project Zero researcher discovered that an iPhone could be turned into a surveillance tool that can expose the victim’s sensitive information, including contacts, Live Location, chat history, emails, photos, and passwords.

According to the security expert Ian Beer, a number of flaws in iPhones could enable attackers to set Monitoring Implants in the devices. The researcher said that they’ve found Fourteen security flaws that existed in iPhones from the past two years.

“Visiting hacked sites was all that is needed for a server to gather users’ images and contacts. A user only had to visit a website to potentially give hackers access to messages, photos, contacts, and location information,” Ian Beer said in a statement. Apple stated that it fixed all the flaws in a software update released in February 2019, after confirming Google findings.

ITC Honors the Winners of Cyber Saber Hackathon 2019

Cyber Saber Hackathon 2019

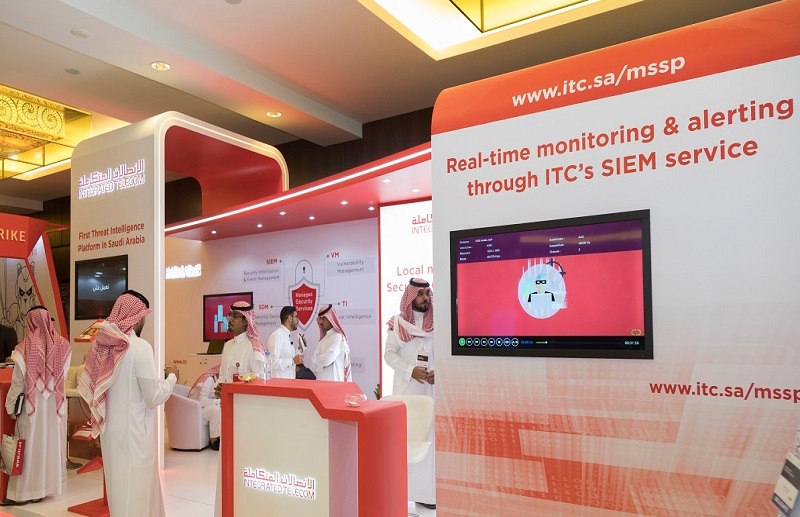
Cyber Saber Hackathon 2019, the popular competition held alongside the 7th #MENAISC2019 conference at Crowne Plaza Riyadh RDC Hotel & Convention, was concluded recently.

ITC, the Exclusive Sponsor for the Hackathon, honored the winning universities and the first place was awarded SAR 25,000 while the Islamic university was awarded SAR15,000 after coming in second place. Imam Abdulrahman Bin Faisal University was awarded SAR10,000 for coming in the third place. King Abdulaziz University won the first place, with a total number of 46 male and 80 female participants.

The Saudi Electronic University came in fourth place with a prize of SAR 10,000, while two teams from Imam Abdulrahman bin Faisal University came in fifth and sixth places respectively, with a prize of SAR 10,000 for each.

Eng. Ghassan Itani, CEO of Integrated telecom (ITC), the exclusive sponsor of the Hackathon, explained ITC’s commitment for the IT Security community to enable and uplift the Saudi talent in one of the most vital sectors in the Kingdom. Also, he stressed the company’s priority to deliver the aspirations of the Human Capital Development Program part of Vision 2030.

Cyber Saber Hackathon 2019
Cyber Saber Hackathon 2019                             

Itani further highlighted “Being a technology company, we believe that the future will be more connected, integrated and smarter, which presents an added IT security challenge for which we must be prepared for”. He went on to say, “It is for this reason that we sponsored the #Cyber_Saber hackathon as it represented an exciting opportunity for students to apply what they learned and gain new and hands-on experiences.”

Samer Omar, CEO of VirtuPort which organized the Cyber Saber Hackathon, stated that the third edition of the Hackathon has witnessed a strong competition among Saudi students from both public and private universities. He highlighted that the competition will contribute to increasing the competencies in the field of cybersecurity in the Kingdom of Saudi Arabia, in line with the National Transformation Program 2020 and the Saudi Vision 2030.

ITC and VirtuPort will present all the students with vouchers for access to CYBRScore labs and assessment valued at SAR 1,200. It is worth noting that Cyber Saber Hackathon, in its third consecutive edition, is considered to be one of the most important competitions in the region that includes one of the most advanced smart cities which gives the students an unprecedented experience to develop their skills. Moreover, this year’s conference, the MENAISC2019 has attracted delegates from around the globe and has brought worldwide experience right at home in Saudi Arabia.

Cybersecurity is a Topmost Investment Priority for Banks in the UK

Banks in United Kingdom

Cybersecurity has emerged as a primary investment priority for financial firms in the United Kingdom. According to a survey report from Lloyds Bank, cybercrimes have jumped to the fourth position from the eighth place since 2018. The banks are increasing their budget allocation to enhance cybersecurity capabilities at their organization, Computer Business Review reported.

The research surveyed 100 senior business decision-makers from financial organizations in the UK. According to the survey report, in 2018 over 46 percent of respondents stated their top three technology investment agendas were to improve customer satisfaction, enhance cybersecurity, and reduce operating costs. But, in 2019, investment on cybersecurity products and services became the topmost agenda, with 70 percent respondents now focussing on it.

“Against a backdrop of on-going global economic turbulence, it is unsurprising that sentiment among financial institutions towards the sector and the wider economy is lower than in previous years. That said, the responses to this survey show the sector’s resilience during difficult times and it is especially encouraging to see that firms plan to continue investing in the UK,” said Robina Barker Bennett, head, financial institutions, Lloyds Bank Commercial Banking.

“In 2019, firms are arguably more dependent than ever on technology. With this rapid advancement, the risks from cybercrime are increasing, placing extra pressure on financial institutions to change the way they operate,” Bennett added.

A similar survey revealed that more than half of financial firms in the UK experienced a security incident over the past 12 months. According to a survey from data security firm Clearswift, around 70 percent of financial firms in the UK reported security incidents last year, in which half of the incidents occurred due to internal errors.

The research highlighted that most of the attacks have originated due to employees who failed to follow proper data protection policies. Apart from employees’ errors, the survey also revealed other reasons, that led to attacks, including downloads of Malware or Viruses from third-party devices like USBs, and file transfers to unsecured sources.