Home Blog Page 125

EU Regulators Imposed over €272.5 Mn in GDPR Fines to Date

GDPR fines in 2020

Ever since the GDPR guidelines were launched (May 25, 2018), the data regulators in European Union (EU) have imposed sizable penalties on various organizations that misused customer information or failed to maintain the required cybersecurity standards. The EU has issued over €272.5 million (approximately $332.4 million) in fines since the GDPR was initiated, according to research from international law firm DLA Piper. Along with the surge in fines, the number of data breach notifications have also increased by 19% compared to last year.

In total, there have been more than 281,000 data breach notifications since the initiation of GDPR, with Germany (77,747), the Netherlands (66,527), and the U.K. (30,536) topping the list. Italy tops the list in aggregate fines with more than €69.3 million (about $84.5 million) in fines imposed since the initiation of GDPR. Germany and France stood second and third with aggregate fines of €69.1 million and €54.4 million, respectively.

Key Findings

  • Around €158.5 ($192,80) of fines have been imposed since January 28, 2020, a 39% increase on the previous 20-month period since the application of GDPR.
  • Double-digit growth for breach notifications for the second year running with 121,165 breaches notified since January 28, 2020, compared to 101,403 breaches notified in the previous year, a 19% increase.
  • Denmark tops the rankings for data breach notifications.
  • Italy has imposed the highest aggregate fines and France has imposed the highest individual fine to date.
  • Regulators have not had everything their own way this year with several multi-million-euro fines being successfully appealed or significantly reduced.
  • The highest GDPR fine to date remains the €50 million (about $61 million) imposed by the French data protection regulator on Google, for alleged infringements of GDPR’s transparency principle and lack of valid consent.

The research findings are based on the latest GDPR fines and data breach reports from the EU, the U.K., Norway, Iceland, and Liechtenstein.

Ross McKean, Chair of DLA Piper’s U.K. Data Protection and Security Group, said, “Fines and breach notifications continue their double-digit annual growth and European regulators have shown their willingness to use their enforcement powers. They have also adopted some extremely strict interpretations of GDPR setting the scene for heated legal battles in the years ahead. However, we have also seen regulators show a degree of leniency this year in response to the ongoing pandemic with several high-profile fines being reduced due to financial hardship.”

Related Story: Four Biggest GDPR Fines of 2020
ShinyHunters Leak 1.9 Mn Pixlr Users’ Records Online

Patchwork BADNEWS, APT31 threat group

Pixlr, a free online photo-editing platform, is the latest victim of a data breach after the notorious threat actor group “ShinyHunters” leaked over 1.9 million users’ records online, as reported by SiliconAngle. The exposed information included usernames, hashed passwords, email addresses, country of origin, and other personal data. It’s suspected that the hacking group illicitly obtained access to Pixlr user records by exploiting an unsecured AWS S3 bucket.

The Impact

ShinyHunters distributed the stolen information on various hacking forums for free, allowing other cybercriminals to access the data. The leaked data can be misused to launch a variety of cyberattacks against Pixlr users. Attackers can also compromise users’ accounts by committing spear-phishing or credential-stuffing attacks on users whose data was exposed in the incident.

Link to 123RF.com Data Breach

ShinyHunters operators claimed that they stole Pixlr’s database while they were breaking into 123RF.com user records. 123RF.com is a royalty-free image website. Both Pixlr and 123RF.com are owned by Inmagine company. According to a report, malicious actors leaked 123RF.com users’ data (3GB in size) on a Russian hacker forum.  The company stated that the exposed database holds over 8,500,246 user records including users’ full names, email addresses, IP addresses, Facebook IDs, locations, and passwords that have been hashed using the MD5 hashing algorithm.

ShinyHunters Continue to Strike

Recently, the operators of ShinyHunters traded databases of three India-based enterprises – ClickIndia, ChqBook, and WedMeGood – on Darknet forums. The data dump contained over 8 million records of ClickIndia (name, email, mobile and other personal details), 1 million records of ChqBook (name, email, mobile, full address, and other personal details), and 1.3 million from WedMeGood (name, email, hashed password, other sensitive personal information).

Google Chrome 88 To Fix Weak Passwords for Better Online Security

reusing passwords

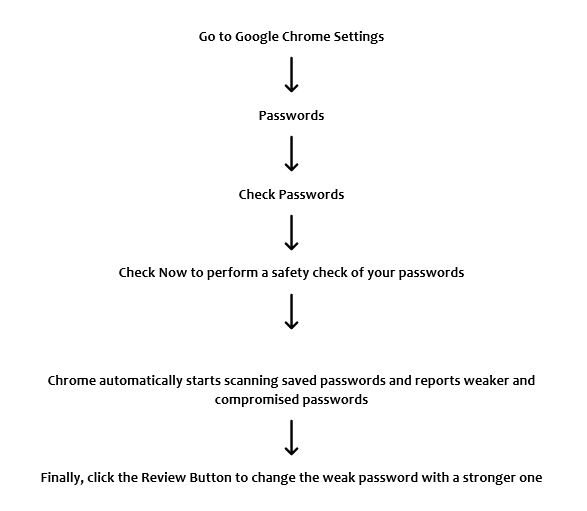
Google Chrome has introduced a new password security feature to prevent users from using weak and compromised passwords online. The new feature will be rolled out with the upcoming Chrome version 88. The feature automatically detects and reports weak or easy-to-guess passwords by performing a quick safety check scan. A similar feature was introduced to Chrome Canary in December 2020.

Improved Password Protection

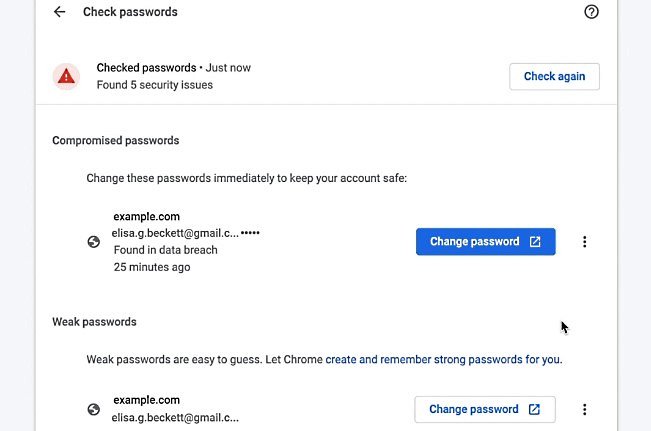
Google Chrome can now create, store, and fill in saved passwords and warn users if their passwords were compromised in any past data breaches. With Chrome 88, users can perform a simple check to identify passwords that are not strong enough and can take quick action by changing them.

How to find weak passwords using Chrome’s password safety check?

How to edit weak and compromised passwords in Chrome settings?

Image Courtesy: Google

Vulnerable Login Credentials!

Earlier, a study from Google revealed that 1.5% of all logins used across the Internet are vulnerable to credential stuffing attacks. Based on the data collected from February 5 to March 4, 2019, Google found that 1.5% of the 21,177,237 monitored logins were identified in data breaches.

“Nearly 670,000 users from around the world installed our extension over a period of February 5–March 4, 2019. During this measurement window, we detected that 1.5% of over 21 million logins were vulnerable due to relying on a breached credential — or one warning for every two users. By alerting users to this breach status, 26% of our warnings resulted in users migrating to a new password. Of these new passwords, 94% were at least as strong as the original,” the study revealed.

Malwarebytes Reports Being Hacked by SolarWinds Attackers

SolarWinds Microsoft

When we first reported about the SolarWinds attack in December 2020, we said it was just the tip of the iceberg, and now a month later, organizations around the globe can see what lies beneath. Malwarebytes, a U.S. – based cybersecurity firm, has reportedly been intruded on by the same nation-state actor behind the SolarWinds cyberattack.

In an official release, Marcin Kleczynski, CEO of Malwarebytes, stated that although the same threat actors were involved in this breach, it was not related to the SolarWinds supply chain attack. Instead, Kleczynski said that the intruders abused privileged access to Microsoft Office 365 and Azure environments to breach their network.

Related News:

SolarWinds Hack Affected Yet Another Tech Giant – Microsoft

What was Hacked in the Incident?

The Malwarebytes security team received security notifications from the Microsoft Security Response Center (MSRC) on December 15, 2020, about suspicious activity on one of its dormant Microsoft Office 365 apps. After comparing the vectors, the security team found them consistent with the tactics, techniques, and procedures (TTPs) of the threat actor involved in the SolarWinds attacks. Thus, from that day on, Malwarebytes’ researchers carried out extensive research and found the following:

  • Attackers breached Malwarebytes’ internal systems by exploiting a dormant email protection product within its Office 365 tenant.
  • The attackers only gained access to a limited subset of internal company emails.
  • No evidence of unauthorized access or compromise in any of the internal, on-premises, and production environments of their products has been found.

Our Products are Safe!

The SolarWinds cyberattack is known to have infested networks with additional payloads like the SUNBURST and Raindrop malware that can go undetected for months, if not days. Thus, Kleczynski assured that a thorough internal audit was carried out to investigate the matter at hand. The entire source code of all its products has been scanned, and he reassured stating, “Our software remains safe to use.”

Kleczynski also took the opportunity to thank FireEye, Crowdstrike, and Microsoft, who shared their resources and all the information on the SolarWinds cyberattack with them for quicker mitigation. He has reiterated the same sentiments that many cybersecurity experts have been saying for a long time – unite, associate, and fight the adversaries as one.

Related News:

FireEye Releases ‘Azure AD Investigator’ to Know SolarWinds Hacking Techniques

Google’s Project Zero Team Details Patched Bugs in Duo, Signal, JioChat, FB Messenger

Vulnerabilities in Zimbra

Natalie Silvanovich, a security researcher at Google Project Zero, disclosed critical vulnerabilities in multiple messaging and video conferencing mobile apps that allowed malicious actors to snoop into users’ conversations without their permission. The affected applications include Signal, JioChat, Mocha, Google Duo, and Facebook Messenger.

Silvanovich claimed the vulnerability in these platforms is similar to the critical flaw dubbed “Logic bug,” which was discovered in Apple’s FaceTime group chat feature in January 2019. The Logic flaw allowed threat actors to initiate a FaceTime video call and eavesdrop on victims by adding their phone number as a third person in a group chat before the other person accepted the call. Apple removed the FaceTime group chat feature and fixed the issue in a subsequent iOS update.

Silvanovich Tweets…

“The ability to force a target device to transmit audio to an attacker device without gaining code execution was an unusual and possibly unprecedented impact of a vulnerability. Moreover, the vulnerability was a logic bug in the FaceTime calling state machine that could be exercised using only the user interface of the device. While this bug was soon fixed, the fact that such a serious and easy to reach vulnerability had occurred due to a logic bug in a calling state machine — an attack scenario I had never seen considered on any platform — made me wonder whether other state machines had similar vulnerabilities as well,” Silvanovich explained.

Logic Bugs in Multiple Apps

Silvanovich stated that she found Logic vulnerabilities in Signal, Google Duo, Facebook Messenger, JioChat, and Mocha messaging apps, which are now patched. Most of these vulnerabilities allowed calls to be connected without interaction from the person on the other end. The other effects of these flaws include:

Google Duo

The vulnerability, which was fixed in December 2020, would disable the video and set up a connection to trigger the callee to leak video packets from unanswered calls. It is because Google Duo’s signaling methodology supports a feature that allows the callee to preview the caller’s video before answering, which is different from other video chat applications.

Signal

The audio call flaw, which was fixed in September 2019, in Signal’s Android app allowed the caller to hear the callee’s surroundings as the application didn’t check that the device receiving the connect message was the caller device. This caused the audio call to connect, allowing the caller to hear the callee’s surroundings.

Facebook Messenger

The vulnerability in Facebook Messenger, which was fixed in November 2020, allowed an attacker to initiate a call and send a specially crafted message to a victim who was signed in to both the app and the web browser.

JioChat and Mocha

Silvanovich found two similar vulnerabilities in JioChat (fixed in July 2020) and Mocha (fixed in August 2020). The vulnerabilities allowed a caller to force the victim’s device to send audio and video content without the user’s knowledge.

Related Story: WhatsApp vs Signal vs Telegram: Which is More Viable and Secure?

Microsoft to Launch Enforcement Mode to Address Critical “Zerologon” Flaw

Microsoft November 2021 Patch Tuesday, Windows 10, Microsoft PrintNightmare

Microsoft has alerted security admins that it is enabling Domain Controller enforcement mode by default to address a critical Remote Code Execution (RCE) vulnerability dubbed “Zerologon” that impacts the Netlogon protocol. The latest mode, which will be rolled out with the upcoming security update on February 9, 2021, will prevent vulnerable connections from non-compliant devices.

“Domain Controller enforcement mode requires that all Windows and non-Windows devices use secure Remote Procedure Call (RPC) with Netlogon secure channel unless customers have explicitly allowed the account to be vulnerable by adding an exception for the non-compliant device,” Microsoft said.

Zerologon – An Unpatched Flaw

The Zerologon (CVE-2020-1472), with a CVSSv3 score of 10.0, is a privilege escalation flaw in the Windows Netlogon Remote Protocol (MS-NRPC) that was patched in the Microsoft August Patch Tuesday. The vulnerability would have allowed attackers to hijack the Windows domain controller. All an attacker requires is local network access, which is also why it cannot be performed directly over the internet.

However, the Cybersecurity and Infrastructure Security Agency (CISA) stated that several proof-of-concept exploits caused widespread concern across the industry, and the bug remained unpatched in many government agencies.  In an emergency directive, the agency urged to update all Windows Servers with the domain controller role in any information systems that collects, processes, stores, transmits, disseminates, or maintains agency information.

Microsoft advised security admins and organizations to update their Domain Controllers with August 11, 2020, security update, monitor event logs to find out which devices are making vulnerable connections, and enable Domain Controller enforcement mode to address Zerologon flaw. In addition, the tech giant stated, “Organizations that deploy Microsoft Defender for Identity or Microsoft 365 Defender can detect adversaries as they try to exploit this specific vulnerability against their domain controllers.”

DNSMasq Critically Vulnerable to DNS Cache Poisoning Attacks

DNS attacks

Cybersecurity experts from security firm JSOF uncovered seven critical vulnerabilities in popular open-source Domain Name System (DNS) forwarding software DNSMasq, which is deployed in networking units to cache and forward Domain Identify Method requests. Dubbed as DNSpooq, the vulnerabilities include four Buffer Overflow Flaws (CVE-2020-25687, CVE-2020-25683, CVE-2020-25682, and CVE-2020-25681) and three DNS Cache Poisoning vulnerabilities (CVE-2020-25686, CVE-2020-25684, and CVE-2020-25685).

Various popular brands like Cisco, Android, Aruba, Technicolor, Red-Hat, Siemens, Ubiquiti Networks, and Comcast use DNSMasq in their products and services.  JSOF’s researchers stated that the devices that are using DNSMasq could be affected or unaffected based on how they are using the software.

“One of the interesting things about these vulnerabilities is that each one of them, on its own, has limited impact. However, the vulnerabilities could be combined and chained in certain ways to build extremely effective multi-staged attacks. This is because exploiting some of the vulnerabilities makes it easier to exploit others,” JSOF said.

What’s the impact?

The Buffer Overflow vulnerabilities include high severity risks that could potentially lead to remote code execution when configured to DNSMasq. These vulnerabilities could pose critical risks when attackers combine these with the cache-poisoning vulnerabilities to launch more effective cyberattacks.

DNS Cache Poisoning flaws can potentially result in various kinds of frauds. Scammers could exploit these vulnerabilities to route unwitting victims from a legitimate browser to a malicious one. Fraudsters can manipulate the Internet traffic, including regular Internet browsing, emails, SSH, remote desktop, RDP video and voice calls, and software updates.

“For the Buffer Overflows and Remote Code execution, devices that don’t use the DNSSEC feature will be immune. DNSSEC is a security feature meant to prevent cache poisoning attacks and so we would not recommend turning it off, but rather updating to the newest version of DNSMasq,” JSOF added.

Indian Government Asks WhatsApp to Withdraw its “Discriminatory” Policy

Whatsapp

In the latest saga of WhatsApp’s changes in its data sharing policy, the Indian Government has written a letter to WhatsApp CEO, Will Cathcart, asking him to withdraw the “discriminatory” policy changes that are challenging the “right to privacy” of Indian users bestowed upon them by the country’s constitution itself. Owing to the extensive criticism and the amount of misinformation spread related to the updated privacy policies, WhatsApp has decided to delay the changes by three months until everything is sorted.

What were the WhatsApp Privacy Policy Changes?

WhatsApp’s updated Privacy Policy mandated users to share their data with its parent company Facebook. It included sharing the metadata of users’ chat with business accounts of other Facebook companies. Moreover, WhatsApp did not allow users to opt-out of such a drastic change in the privacy policy.

Related News:

WhatsApp vs Signal vs Telegram: Which is More Viable and Secure?

Why is the Indian Government Opposing?

According to a report from a national news channel NDTV, experts in the government familiar with the matter cited concerns over WhatsApp’s data collection and sharing with the other parent and sister companies. They said, “It would create a honeypot of information about users with a Facebook group, which can invariably create security risks and vulnerabilities for all users.”

Secondly, the Ministry of Electronics and Information Technology (MeitY) is baffled by the double standards of WhatsApp. In the European Union (EU), WhatsApp has given an opt-out option to its users; however, the Indian user base, which the company states are the biggest in the world, does not get one. MeitY strongly condemned this “discriminatory treatment” and termed it “disrespectful” towards Indian citizens. In a stern voice, MeitY reminded WhatsApp “that it has a sovereign right to protect the interests of Indian citizens and it shall not compromise on that at any cost.”

After a brief study of the updated policy, the Indian government is now seeking clarity and conformance on privacy and data security concerns. It has sent a list of 14 questions asking about the disclosure of the exact categories of data that WhatsApp collects from its users in India, the permissions and user consent sought by the app, and how each of these sets of data will be used by the company post collection.

Petition in Delhi High Court Against WhatsApp’s Policy

Meanwhile, a lawyer has filed a petition against WhatsApp’s new privacy policy, which was heard in the Delhi High Court on Monday, January 18. The petitioner argued that the updated privacy policy violates users’ right to privacy under the Indian Constitution and must not come into effect. However, Kapil Sibal and Mukul Rohatgi, senior advocates and defendants of WhatsApp and Facebook,  found this argument baseless. They told the High Court that none of the private or group chats were being accessed or stored by WhatsApp, and very much remained encrypted. They further argued that it was only the business chats on WhatsApp that were getting affected.

In response to the petition, Justice Sanjeev Sachdeva said, “It is a private app. Don’t join it. It is a voluntary thing, don’t accept it. Use some other app.” Pointing at other apps like Google Maps, Justice Sachdeva stated that even others do it and “you would be surprised as to what all you are consenting to.” However, the High Court wanted more time to analyze the amount of data being shared and the data that was being leaked as per the petitioner. Thus, the matter will be listed on January 25 for further address.

Related News:

After Juspay, ClickIndia, ChqBook and WedMeGood Allegedly Suffer Data Breaches

FireEye Releases ‘Azure AD Investigator’ to Know SolarWinds Hacking Techniques

FireEye’s Red Team tools breach

The SolarWinds supply chain cyberattack took the digital world by storm, affecting government agencies and IT giants. To detail the techniques used by the SolarWinds threat actors, also known as UNC2452 actors, cybersecurity firm FireEye released a free tool, dubbed Azure AD Investigator, on GitHub.

FireEye claimed that Azure AD Investigator helps identify Indicators of Compromise (IoC) that require further verification and analysis. The tool will alert security administrators to artifacts that may require further review to determine their legitimacy.

The company also issued a report detailing the attack techniques used by SolarWinds threat actor groups in their recent cyber operations.  The report discussed how companies can boost their security landscape and remediate cybersecurity loopholes. FireEye, along with Microsoft and CrowdStrike, recently led several investigations into the SolarWinds cyberattacks.   FireEye has observed UNC2452 attackers’ tactics, techniques, and procedures (TTPs) moving laterally to the Microsoft 365 cloud using a combination of four primary techniques. These include:

  • Steal the Active Directory Federation Services (AD FS) token-signing certificate and use it to forge tokens for arbitrary users (sometimes described as Golden SAML). This would allow the attacker to authenticate into a federated resource provider (such as Microsoft 365) as any user, without the need for that user’s password or their corresponding multi-factor authentication (MFA) mechanism.
  • Modify or add trusted domains in Azure AD to add a new federated Identity Provider (IdP) that the attacker controls. This would allow the attacker to forge tokens for arbitrary users and has been described as an Azure AD backdoor.
  • Compromise the credentials of on-premises user accounts that are synchronized to Microsoft 365 that have high privileged directory roles, such as Global Administrator or Application Administrator.
  • Backdoor an existing Microsoft 365 application by adding a new application or service principal credential to use the legitimate permissions assigned to the application, such as the ability to read email, send email as an arbitrary user, access user calendars, etc.