
Microsoft released the official patches for over 83 newly discovered vulnerabilities as part of its Patch Tuesday security updates, marking the first of many for 2021. The technology giant stated that the latest security updates address flaws in around 11 of Microsoft’s products and services, including an actively exploited zero-day vulnerability. Out of 83 vulnerabilities, 10 were listed as critical, and 73 as important in severity.
The January 2021 security release consists of security updates for the following software:
- Microsoft Windows
- Microsoft Edge (EdgeHTML-based)
- Microsoft Office and Microsoft Office Services and Web Apps
- Microsoft Windows Codecs Library
- Visual Studio
- SQL Server
- Microsoft Malware Protection Engine
- .NET Core
- .NET Repository
- ASP .NET
- Azure
According to the release, the Remote Code Execution (RCE) flaw in Microsoft Defender (CVE-2021-1647) is listed as the most severe bug which could enable threat actors to infect qualified units with arbitrary code.
“According to Microsoft, this vulnerability was exploited in the wild as a zero-day, though no further details have been shared. Considering how prevalent Microsoft Defender is, this flaw provides attackers with a large attack surface. Microsoft also patched CVE-2021-1648, an elevation of privilege vulnerability in the printer driver host, splwow64 due to improper validation of user-supplied data. The vulnerability is marked as publicly disclosed by researchers at Google Project Zero and through the Zero Day Initiative. While it is labelled as an elevation of privilege vulnerability, Microsoft states that it can also be used for information disclosure,” said Satnam Narang, Staff Research Engineer at Tenable.
The latest patches also fix other critical bugs like a memory corruption flaw in Microsoft Edge Browser (CVE-2021-1705), a Windows Remote Desktop Protocol Core Security feature bypass flaw (CVE-2021-1674), and five critical RCE flaws in Remote Procedure Call Runtime.
How to Install the Latest Security Updates
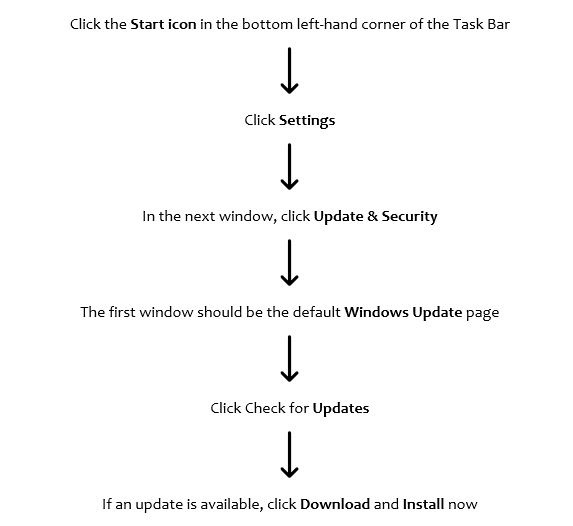
“It is important to install the latest servicing stack update. Updates for Windows RT 8.1 and Microsoft Office RT software are only available via Windows Update. In addition to security changes for the vulnerabilities, updates include defense-in-depth updates to help improve security-related features. Customers running Windows 7, Windows Server 2008 R2, or Windows Server 2008 need to purchase the Extended Security Update to continue receiving security updates,” Microsoft said in a release.

