Home Blog Page 52

Europol Arrested 106 Cybercriminals of Italian Mafia in a Sting Operation

Facebook Indicts Two Developers for Scraping Users’ Data, Europol

Europol and the European Commission are working with international security collaborations to disrupt cybercriminals and their operations globally. Recently, Europol dismantled over 106 organized threat actors linked to various cybercrimes, including SIM swapping, money laundering, and other online frauds.

As per the official release, the Spanish National Police, Italian National Police, Europol and Eurojust busted an Italian Mafia crime group that defrauded hundreds of victims through various kinds of online scams. It’s found that the group reportedly leveraged phishing and business email compromise (BEC) attacks and gained an illegal profit of over €10 million ($11.70 million).

The international operation resulted in

  • 106 arrests in Spain and Italy.
  • 16 house searches.
  • 118 bank accounts were detained.
  • Seizures include many electronic devices, 224 credit cards, SIM cards and point-of-sale terminals, a marihuana plantation and equipment for its cultivation and distribution.

Organized Cybercriminal Group

Europol stated the cybercriminal network is large and included hackers expertized in computer hacking, phishing domains creation, recruiters of cybercrime affiliates, and cryptocurrency and money laundering experts. Threat actors primarily targeted Italian nationals by tricking them into transferring large sums of amounts to bank accounts controlled by the criminal network, which later laundered to a wide network of money mules and shell companies.

“This large criminal network was very well organized in a pyramid structure, which included different specialized areas and roles. Most of the suspected members are Italian nationals, some of whom have links to mafia organizations located in Tenerife (Canary Islands, Spain),” the release stated.

Not the First Time

This is not the first time that Europol has taken down an international cybercriminal group. In a recent cross-border operation, Operation SECRETO, Europol dismantled an organized cyber threat group that defrauded the U.S. banks for €12 million ($14.4 million). The operation was coordinated by Europol and led by the Spanish National Police (Policía Nacional), and the U.S. Secret Service busted the group involved in fraud and money laundering operations. Read More Here

China Issues Stricter Ban on Cryptocurrency Activity – Global Markets Under Pressure

ONUS Log4j, Cryptocurrency Wallet Security

In a recent announcement, the People’s Bank of China issued a blanket ban on cryptocurrency activity like trading and mining in the country. The announcement sent the global crypto market into a tizzy.

The market had already suffered a major setback in April-May 2021 due to tightening regulations from China. China continues to intensify its ban and is imposing stricter policies for curbing the growing crypto market to safeguard its digital assets.

Millions of dollars were wiped off the market in a single day post the announcement as clients clamored for liquidation of their investments.

It has been reported that stringent regulations are being put in place as China is trying to develop its first-ever official digital currency.

Over a chat with CISO MAG, R “Ray” Wang, Founder, Chairman, & Principal Analyst of Constellation Research said, “The People’s Bank of China (PBOC) ban is really a reinforcement of an existing law from 4 years ago. China took the time to study the market in order to build their digital yuan and destabilize the dollar. Now they know they can build their own country backed crypto (CBC). They no longer need other cryptos and do not want money to flow out of the country.  They want to run their own belt and road metaverse economy.”

In a blog analysis Wang explained how the Metaverse Economy will grow with or without CCP China. He added, “China’s ban only delays the inevitable. The DeFi movement and cryptocurrencies demonstrate how and why individuals will conduct business outside of central banks. Moreover, the Metaverse economy is powered by cryptos. As adoption grows, a ban by China will eventually lead to digital isolation as citizens find workarounds for more efficient approaches.”

China has been issuing warnings against the usage of cryptocurrency since 2013 and had also announced a new cryptography law, effective January 1, 2020, designed to assist the development of the cryptography business and enhancing the security of cryptocurrency. This has resulted in Bitcoin miners fleeing China and large number of Investors opting for decentralized exchanges.

Nischal Shetty_WazirX
Nischal Shetty, Founder and CEO at WazirX + Crowdfire

Nischal Shetty, Founder and CEO at WazirX + Crowdfire, said, “The global markets reacted with caution leading to a drop in Bitcoin and other crypto prices. However, the markets recovered quickly, and prices seem to have stabilized. Overall, this does impact the number of participants in crypto as China has a huge crypto population. It will be interesting to see how this ban plays out as crypto is a decentralized technology making the ban hard to implement. “

How effective this ban will be, is yet to be ascertained as globally the regulators are working on a positive note to make the crypto market mainstream.


Australians Lose Over $70 Mn to Cryptocurrency Scams

Cryptocurrency scams in Australia

The government of Australia is urging civilians and organizations to be vigilant about online scams that are reported more often in the country. So far, Australians have reported over $211 million in losses to online scams this year – an 89% increase compared to the same period last year, new statistics from Scamwatch revealed. The reported losses, between 1 January and 19 September, have already surpassed the $175.6 million that were reported last year.

Operated by the Australian Competition and Consumer Commission (ACCC), Scamwatch provides information to consumers and businesses about how to detect, report, and prevent online scams.

Rise of Phone-based Scams

According to Scamwatch, most of the reported security incidents are phone-based attacks. Threat actors leveraged social engineering, impersonation, and phishing tactics to scam users and steal personal information. In total, phone-based scams accounted for over $63.6 million (31%) losses. Out of 213,000 reports that Scamwatch received, 113,000 were about phone scams. Scamwatch has identified a record high in losses to phishing scams (261%), remote access scams (144%), identity thefts (234%), and investment scams (172%) in 2021.

Cryptocurrency Scams Surge  

Investment scams have become more prevalent, with over $70 million losses reported in the first half of this year and estimated to reach $140 million by the end of the year. More than half of the investment scams were related to cryptocurrency trading, primarily through Bitcoin, as cybercriminals capitalize on users’ interest in cryptocurrency. Cryptocurrency scams are the most reported investment scams causing significant losses. Of the 1,931 reports involving a loss, 955 (49.5%) were due to cryptocurrencies loss of $29,277,896. Bitcoin accounted for over $25 million of these losses.

Bad actors pretend to be from highly profitable crypto exchanges and trading platforms that trick users into investing in their fake schemes. Threat actors also leveraged phony celebrity endorsements and gave small returns to investors to gain investors trust. In addition to financial frauds, scammers also committed personal data and identity thefts by exploiting investors’ data.

Other Key Findings:

  • People aged 65 years and older have lost maximum money so far in 2021, losing $49.1 million (23%) of total losses for the year.
  • Indigenous Australians have reported $4.3 million in losses to scams, an increase of 172% on the losses reported in the same period in 2020.
  • People who speak English as a second language made over 10,500 reports with losses of $29.9 million, representing almost 14.4% of total losses for the period.

Mitigation

Sharing sensitive information like banking details could lead to unnecessary security risks. Delia Rickard, the ACCC Deputy Chair, urged users to be vigilant on various cyber scams and frauds online. Rickard also recommended users report any suspicious activities to Scamwatch – which will work with private and public organizations, including law enforcement agencies, to help disrupt various online scams.

“Scammers are conning people out of more and more money, so it’s really important that everyone knows what to look out for and how to protect themselves. Remember, you never know who you are dealing with online. Scammers often pretend to be from a well-known organization, such as a bank or the government, and they will pretend to offer you something such as money or a benefit or claim that you are in trouble. Do not click on any links in messages that come to you out of the blue, and never provide any of your personal or banking details to someone you don’t personally know and trust. If you think something might be legitimate, call the organization or government agency back using details you find in an independent search, rather than the details provided,” Rickard added.

This Device Simplifies Password Management and Protects User Credentials

cybersecurity, password, password management,

With a mission to provide cybersecurity to individuals to safeguard themselves from threat actors, a Pune-based (Maharashtra, India) cybersecurity enthusiast came up with a password management solution in the form of a smart device.

By Minu Sirsalewala, Editorial Consultant, CISO MAG

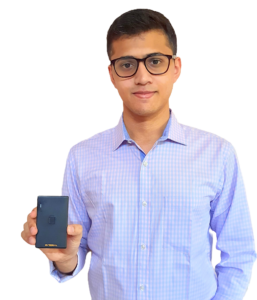
Byteseal, a product of Elementik Technologies Pvt. Ltd., is a single authentication device; it is a native credential management platform that provides end-to-end password management solutions. Users can store their login credentials in a safe, secure and encrypted manner by delivering dynamic solutions with this device.

Nikhil Wani
Nikhilesh Wani, Co-founder and CEO, Elementik Technologies Pvt. Ltd.

In an exclusive interaction with CISO MAG, Nikhilesh Wani, Co-founder and CEO, Elementik Technologies Pvt. Ltd., discussed the product and the upcoming features to address the password vulnerabilities due to human error in cybersecurity – the leading cause for most cyberattacks. The 24-year-old Wani, who has a Bachelor of Engineering (Electronics and Communication) degree, has the vision to help people take control of their digital security, but not at the cost of their freedom.

After two years of rigorous R&D, Byteseal was slated for a February 2020 release, but the onset of the pandemic disrupted the supply chain, and they were not able to launch as scheduled;  however,  it entered the market in May 2021. The company has put all the identity management solutions and products under the umbrella brand “Byteseal.”

Wani opines, “Our disruptive technologies are meant to replace the conventional method of managing passwords and makes it easy to deliver to customers a fast and secure login experience with just a tap. People and businesses will now be finally able to reduce cyberattacks and enable security for their users and clients.”

Human Factor in Cybersecurity

The Cybersecurity Framework is composed of multiple components. One aspect is malware protection, which can be taken care of with antivirus software, moving to the second part, identity management or access control. Access control systems and mechanisms based on username and password authentication are the weakest link in the cybersecurity setup, as humans tend to work with simple, repetitive passwords for multiple accounts. And when this practice is applied on a large scale at an enterprise level, it opens up a huge vulnerability to hackers. An organization may have state-of-the-art security, but all it takes is one weak password to compromise the entire system.

To solve the human error in cybersecurity, Byteseal came up with a method combining all the three authentication factors on one platform. The three authentication factors are OTP, access to tokens, and biometrics. All three are weaved into a single device termed as a personal authentication device. The device stores all passwords for all websites and can be activated with one touch.

The Advantage

The Byteseal device helps store and manage passwords, facilitating the use of complex, special character-based passwords that need not be memorized or written down for recall. In an enterprise scenario where hundreds of websites and applications are used daily and need authentication, the device can be used to manage passwords and for access control. This allows organizations to have stricter password policies in place with added control and an enhanced level of cybersecurity.

Organizations can monitor and manage the devices remotely and the user need not even know the passwords stored on the device. This helps in bypassing and eliminating the human factor.

Going beyond just passwords, the device can also detect keylogging and phishing attacks. The system detects whether the URL you’re trying to autofill with your credentials is correct and does not allow you to enter your username and password, thereby overcoming the phishing attacks.

As there is no need for manual typing of the passwords, your keys cannot be logged. And therefore, if some malware is sitting inside your computer, listening to whatever you type, they won’t be able to listen to what passwords or usernames you are typing. This works as an added security layer. The vision is to eliminate the human vulnerabilities from the Cybersecurity Framework.

Added Capabilities

The device is designed to look like an identity card. It has an option to add NFC or RFID capabilities to the device. It can also be used for access control purposes, physical access control and attendance purposes. It doubles up as your identity card as well as an authentication device.

Beta Testing

Currently, the product is available as a standalone solution for end consumers and enterprises. Soon the product will be linked for both personal and professional usage on the same device for increased efficiency and is expected to be rolled out in the next 2-3 months.

Security

As most sectors have shifted to remote work and the BYOD culture is rising, the Byteseal device can help mitigate the risk that comes with this culture. Most malicious attacks are through the end-user device, which was not a part of the native security design. The authentication device is Bluetooth enabled, and itself does not have any memory. With the USB option eliminated, even if there is any malware on the computer or end-user device, it cannot hamper the device. The device uses the Bluetooth 5.0 standard.

Around 100 customers have acquired the device both in the B2C and B2B categories. The current offer price is pegged at INR 3,000. After a few months, the company plans to move to a subscription-based model at INR 150 per month.

Wani concludes, “In India, what we have observed is that cybersecurity is only equivalent to antivirus software for many companies. This should be taken care of on a priority basis as hackers target human vulnerabilities, and this needs to be resolved on an urgent basis.”

What is Web Application Security and Why it is Important

MaliciousItaú Unibanco app,Web Application Security, web application attacks

The emerging and advanced technologies in the digital age create new security challenges for cybersecurity specialists. The application security vulnerability is the latest threat in an organization’s ever-growing challenges amidst other cyber threats. No industry sector is safe from web application security breaches. Only an experienced professional with web application security training can deal with the specific security issues surrounding websites, web applications, and web services such as APIs.

See also: EC-Council Launches a Specialized Web Application Hacking and Security Certification

Web application security is a concern that stems from the changing business norms that pushed people to adopt a work-from-home framework due to the ongoing pandemic. This blog will identify the critical issues associated with application security and what it would take for organizations to overcome this threat.

What is Web Application Security? 

Web application security includes a multitude of techniques and strategies to secure web browsers and applications. These strategies safeguard an organization’s digital assets, such as websites, mobile applications, payment systems, etc., against cyber threats. Most web application security threats occur due to the existing vulnerabilities. Cybercriminals use website vulnerability scanners to exploit the weaknesses and vulnerabilities in the applications to steal client data for personal gain.

The most common targets for web application attacks are content management systems, Database admin tools, and SaaS Applications. These applications are of high value, and a single attack can cause unprecedented damage like:

  • Loss of source code increasing the chances of data manipulation. Source codes are often sold in the black market to buyers who want to create high-value applications but on a lower budget.
  • Loss of classified information can create issues like ransom demands or identity thefts.

Failure to secure web applications can spell trouble for organizations’ effective operation. Without robust security measures, they stand at the risk of being attacked by malicious actors. Apart from financial and reputational damage, it can also result in lawsuits and breaches of compliance charges.

Therefore, preventing a web application attack is only possible if you have an experienced application security penetration tester in your security team. It is also essential to get the latest web application security tools to ensure safety against any security incidents. Web application security testers analyze the security flaws and vulnerability issues to provide solutions to the mitigation of these threats. Organizations should also ensure certain practices to avoid such breaches.

Next, we look at why the protection of your web applications is important.

Web Application Security – A Rising Concern    

Most web application attacks are unpredictable. The COVID-19 outbreak is a significant contributor to the unprecedented rise in such attacks. The pandemic-induced lockdown pushed companies to adopt a remote work framework which became the new norm gradually. Vulnerabilities in web applications raise significant security concerns, which can escalate into a full-scale attack if neglected. Recently, a cyberattack on T-Mobile led to a massive breach of data on millions of customers. The stolen data is being actively sold in the market.

The attack is an example of what happens when organizations do not invest in web application security solutions on time—no wonder the demand for experienced web application penetration testers is increasing gradually.

So, how can one take proactive steps in minimizing web applications attacks? Here are a few methods one can take for mitigating the risks of web application attacks.

Tips to Prevent Web Application Attacks   

Experienced cybercriminals can find security flaws even in the most robust systems. However, you can always take effective measures to mitigate the risks as much as possible. There are some critical steps involved in mitigating web application attacks. More delays for malicious actors mean that the good guys by your side will identify the issue and close it in no time.

Here are some important tips that will prove effective in blocking a cyberattack:

1. Encrypt Connection Through Https 

Encrypting a web server is essential as companies move to digitalize their processes. This step does not even need some high-level technical expertise or expensive web application security solutions. However, many organizations fail to incorporate this in their security strategies. Attackers often take advantage of unencrypted HTTP (Hypertext Transfer Protocol) requests and forge duplicate signatures to confuse the users. If you are not doing this, make sure to start encrypting all connections between your user’s web browser and your webserver.

These issues can be avoided through HTTPS encryption. HTTPS makes it safe to transfer data between the user and the server, thus eliminating the most common occurrences of data compromise.

2. WAF – Web Application Firewall 

WAFs are a combination of different hardware and software elements that effectively block a web application security threat. It is used to protect web applications against malicious activities. WAF is one of the highly sought-after web application security solutions in the market today.

A firewall web application would place a filtration barrier between the targeted server and the attacker. The WAF signature pools also go through continuous updates through which the tools and the user identifies the bad actors.

3. Manual Information Gathering

A web application penetration tester doesn’t rely on automated tools solely. These professionals take additional steps for manual application review, entry point identification, and code analysis. One can conduct elaborate web application security testing to learn more about minor vulnerabilities that a tool may ignore, resulting in a breach.

4. DDoS Mitigation  

DDoS attacks are a significant cause of worry for cybersecurity teams because the attack patterns are highly unpredictable. A web application penetration tester would take the necessary steps to identify suspicious user behavior and prevent further damage through timely action. DDoS mitigation should be a priority for web application security because it ensures trust between users and servers.

Benefits of Web Application Security in 2021-22  

Web application security is important due to five major reasons:

  1. Rectitude: Unique security mechanisms readily identify the authenticity of the data.
  2. Authentication: It provides the user with a unique identification that ensures the safety of their data.
  3. Authorization: The users are allowed to make changes to their data through valid credentials.
  4. Confidentiality: It establishes trust between the user and the server by making data only accessible to those who have authorized access.
  5. Availability: Confirms quick information exchange between all parties on time, without delay.

Web application penetration testers responsible for strengthening the security measures consider every possible scenario of a cyberattack and how they should act. Their training empowers them to think like a cybercriminal and produce a quick and effective solution on time. Make sure that you determine the goals of application security in advance. It will ensure that your cybersecurity team is aware of the primary threats and priorities.

Additionally, when hiring a web application penetration tester, ensure they have credible certifications. A certification like EC-Council’s Web Application Hacking and Security Training would revolutionize the status of cybersecurity and vulnerability assessment for your company.

Enhance Safety with Web Application Hacking and Security Training Certification  

EC-Council’s Web Application Hacking and Security Training Certification specializes in ethical hackers who wish to add a specific niche to their existing skills. The program doesn’t only focus on web application vulnerabilities through automated tools and techniques, but it goes beyond the conventional cybersecurity programs to enable your workforce to learn, hack, test, and secure web applications.

The course is designed in the style of capture-the-flag challenges. But unlike these competitions, the challenger finds the freedom to follow an instructor as they progress in the leaderboard. The course design and layout cover all the vital web application security best practices. The certification will prove ideal for every aspiring web application penetration tester as well as organizations looking for new ways to strengthen their cybersecurity teams.

Get Certified as a web application security expert! Register Now!

People Also Ask

1. Who is responsible for web application security?

Web application security is managed by a non-profit OSWAP foundation. The foundation identifies the common web application security threats and lists them in its database. It is used by security analysts, cybersecurity officers, and tools to update their practices and look for new threats in a more elaborate way.

2. Who can learn web application penetration testing?

Web application penetration testing is for ethical hacking and entry-level cybersecurity officers who plan to transition into a niche job profile by learning a specialized skillset.

New Cyber Campaign “Armor Piercer” Targets Indian Government Officials

Armor Piercer

Cyberattacks and malicious campaigns are becoming rampant, with new cybercriminal operations being reported more often in the security landscape. Recently, security experts from Cisco Talos uncovered a cyber espionage campaign, tracked as Armor Piercer, targeting employees in the government and defense sector in India with two Remote Access Trojans – NetwireRAT (also known as NetwireRC) and WarzoneRAT (also known as Ave Maria). The campaign was found to be distributing malicious documents to deploy RATs and access confidential data.

NetwireRAT and WarzoneRAT are packed with a variety of capabilities, including:

  • Stealing credentials from browsers
  • Execute arbitrary commands
  • Gather system information
  • File management operations such as write, read, copy, delete files, etc.
  • Enumerate, terminate processes
  • Keylogging
  • Remote desktop
  • Webcam capture
  • Credential stealing from browsers and email clients
  • Reverse shells

Armor Piercer’s Phishing Campaign

Active since 2020, the campaign leverages operational documents related to Kavach as phishing lures to trick employees. Kavach is a two-factor authentication (2FA) app operated by India’s National Informatics Centre (NIC), used by government personnel in various departments to access their emails. Armor Piercer was also found using compromised websites and fake domains to host their malware payloads. It also used multiple phishing techniques to obfuscate itself and evade security detections.

Armor Piercer Attack Vector

Armor Piercer operators delivered their malware payloads via various phishing lures to the targeted employees posed as security advisories or guides in the form of malicious Microsoft Office documents (maldocs) and archives (RARs, ZIPs). Once a victim downloads the maldoc, it automatically downloads a loader responsible for deploying the final RAT payload on the targeted endpoint.

“Apart from artifacts involved in the infection chains, we’ve also discovered the use of server-side scripts to carry out operational tasks such as sending out malicious emails and maintaining a presence on compromised sites via web shells. This provides additional insight into the attacker’s operational TTPs. Some of these lures and tactics utilized by the attackers bear a strong resemblance to the Transparent Tribe and SideCopy APT groups, including the use of compromised websites and fake domains,” the researchers said.

Commenting on the Armor Piercer cyber operation, Vishak Raman, Director, Security Business, Cisco India and SAARC, said, “Operation Armor Piercer is a grim reminder of the vulnerabilities still existing in our cybersecurity posture. To ensure end-to-end security of India’s most precious assets and information, government and defense agencies must implement a layered defense strategy that enables comprehensive visibility and coverage across all endpoints, accelerates response by leveraging automation and orchestration to enrich data, and reduces massive data sets into actionable insights through AI/ML and data analytics. Essentially, security must not be bolted on, rather built into every system and process to ensure infallible protection of people and assets.”

Conti Ransomware Attacks on Rise – CISA, FBI, NSA Issue Joint Alert

paying ransom, Conti Ransomware Attacks

Increased use of Conti ransomware in more than 400 attacks on the U.S. and international organizations has been observed by the Cybersecurity and Infrastructure Security Agency (CISA) and the Federal Bureau of Investigation (FBI). The agencies issued a joint advisory listing with the technical details of the attacks and suggestions to safeguard the organizations’ systems against the Conti attack.

In Conti ransomware attacks, hackers access an unprotected RDP port, use email phishing, malicious attachments, downloads, or vulnerabilities to gain access to a network. These cyber actors then steal files, encrypt servers and workstations, and demand ransom.

See also: Conti Ransomware Crook Leaks the Group’s Hacking Tricks

Conti is considered a ransomware-as-a-service (RaaS) model; however, its structure differs from a typical affiliate model. According to the officials, Conti’s developers are said to pay the attackers a wage rather than a percentage of the proceeds.

It was observed that the threat actors made use of Router Scan, a penetrating testing tool to maliciously scan for and brute force routers, cameras, and network-attached storage devices with web interfaces, among other techniques.

Mitigations

The following recommendations have been issued by CISA, FBI, and NSA that network defenders must apply to abate the risk of compromise by Conti ransomware attacks.

  • Use multi-factor authentication – ensure multi-factor authentication for remote access from external sources.
  • Implement network segmentation and filter traffic – to restrict the spread of ransomware there must be strict segmentation between networks and functions.
  • Eliminate unregulated communication between networks. Network traffic must be filtered to prohibit ingress and egress communications with known malicious IP addresses.
  • Enable strong spam filters to prevent phishing emails from reaching end users. Implement a user training program and create awareness among users to refrain from visiting malicious websites or opening malicious attachments.
  • Have a URL blacklist and/or whitelist in place to prevent users from accessing malicious websites.
  • Scan for vulnerabilities and keep software updated. Use a centralized patch management system. Include regular scans of network assets and upgrade software and operating systems, applications, and firmware on network assets at defined intervals.
  • Remove unnecessary applications and apply controls. Applications deemed unnecessary for daily operations should be deleted.
  • Implement software restriction policies (SRPs) or other controls to prevent programs from executing from common ransomware locations.
  • Implement execution prevention by disabling macro scripts from Microsoft Office files transmitted via email.
  • Implement endpoint and detection response tools. Endpoint and detection response tools allow a high degree of visibility into the security status of endpoints and can help effectively protect against malicious cyber actors.

According to the 2021 Cyber Threat Report from SonicWall, ransomware attacks have increased rapidly, surpassing the number of attacks in 2020 and the first half of 2021. The report revealed that over 304.7 million ransomware attacks were reported globally in H1 2021, exceeding 304.6 million attacks in 2020, a 151% increase. High-profile extortion attacks on Colonial PipelineJBS Foods, health care, energy sectors, and the recent Kaseya attack have severely disrupted operations of organizations across the globe.

Rewards for Justice Reporting

The U.S. Department of State’s Rewards for Justice (RFJ) program offers a reward of up to $10 million for reports of foreign government malicious activity against U.S. critical infrastructure. See the RFJ website for more information and how to report information securely.

BlackMatter Group Demands $5.9 Mn Ransom After Attacking NEW Cooperative

Ransomware Attack on NEW Cooperative

While the Biden administration is severely trying to curb ransomware attacks, threat actors continue to target the critical infrastructures in the country. Farm services provider NEW Cooperative is the latest victim to join the bandwagon of ransomware attacks. The Iowa-based company stated that a security incident paralyzed its operations, affecting several U.S. farming chains that began to harvest.

“We have proactively taken our systems offline to contain the threat, and we can confirm it has been successfully contained. We also quickly notified law enforcement and are working closely with data security experts to investigate and remediate the situation,” the company said in a media statement.

NEW Cooperative provides grains, feeds, fertilizers, seed resources, technology platforms, and crop protection services to several farming cooperatives across the north, central, and western Iowa.

Ransomware Risks to Agriculture Sector

It’s becoming increasingly common for ransomware operators to target critical infrastructure to disrupt essential services. The current ransomware attack has affected the operations of several grain storage elevators operated by NEW Cooperative. The timing of the security incident has caused more damage as many farmers had started their farming work.

The food supply chain in the country may be affected unless the NEW Cooperative systems go online.

BlackMatter’s Involvement?

While NEW Cooperative didn’t reveal the hackers behind the cyberattack, several security experts linked the attack to the infamous ransomware attack group BlackMatter. Reports suggest that BlackMatter operators compromised and infected NEW’s network systems and demanded a ransom of $5.9 million to restore the affected systems.  BlackMatter is relatively a new ransomware-as-a-service group (Raas) suspected to be a  successor of the infamous DarkSide ransomware group that went underground after the attack on Colonial Pipeline.

Negotiations with BlackMatter

As per a leaked private negotiation between the NEW officials and BlackMatter operators, the attackers refused to decrypt the affected systems citing that NEW Cooperative doesn’t come under critical infrastructure.

Earlier, the BlackMatter group stated that they don’t attack critical infrastructures such as health care facilities, the defense industry, nuclear power plants, water treatment facilities, the oil and gas industry, non-profit organizations, and government agencies. They further claimed that if a victim is from the sectors above, they decrypt their files for free.

Russian Turla APT Group Uses New Backdoor for Attacks

microsoft, flaws in SonicWall SRA SMA

A new backdoor used by the Russian Turla APT group to keep the attacks live has been discovered, which has been reported to be active in the U.S., Germany and Afghanistan in recent times. It is also known as TinyTurla, due to its simple and efficient capability to go undetected; the malware is like a second door to ensure the infected devices remain accessible even if the earlier malware has been detected and wiped off.

Discovered by Cisco Talos’ telemetry data, the researchers shared that the hackers used the malware “as a second-chance backdoor to maintain access to the system” if the primary access tool got removed.

The malware can be used stealthily to download, upload and/or execute files. The backdoor code is designed in a simple manner to allow it to be off the security radar.

Attack TTPs

The threat actor uses a .BAT file that resembles the Microsoft Windows Time Service, to install the backdoor. The backdoor comes in the form of a service dynamic link library (DLL) called w64time.dll. The description and filename make it look like a valid Microsoft DLL. Once up and running, it allows the attackers to exfiltrate files or upload and execute them, thus functioning as a second-stage postern when needed.

Per the Cisco Talos researchers, the malware’s DLL ServiceMain startup function doesn’t do much beyond executing a function they called “main malware” that includes the backdoor code. Referring to the DLL as “pretty simple”: It consists of just a few functions and two “while” loops, including “the whole malware logic.”

About Turla APT 

A Russian-sponsored APT group, Turla is also known as Waterbug, Venomous Bear and KRYPTON, has been in operation since the early 2000s. The group is known for targeting government entities and embassies across countries. It is believed to be behind attacks on the U.S. State Department, NASA, U.S. Central Command (CENTCOM) and various embassies located in European countries.

Its ability to remain undetected for extended periods of time has enabled the malware to evolve and come up with new techniques to attack. After the initial installation of the malware, the success depends on its continued stealthy communication with the attackers and exfiltration of data (also known as command and control or C2).

Forbid the Trojan

Enterprises can contain Turla by keeping the operating system and all third-party applications updated.

  • Do not run or install software or updates from untrusted sources
  • Look out for emails containing suspicious attachments or links
  • Ensure you are using an antimalware network appliance, a domain name system malware analysis tool, a network anomaly detection tool, or advanced endpoint security tools.

71% of Indian Organizations Attribute Cyberattacks to Vulnerabilities in Technology Deployed During Pandemic: Tenable

remote working, cyberattacks on remote workforce

Cyber Exposure company, Tenable, published a global study that revealed 71% of organizations in India attribute recent business-impacting cyberattacks on the remote workforce due to vulnerabilities in technology put in place in response to the pandemic. The data is drawn from its report titled “Beyond Boundaries: The Future of Cybersecurity in the New World of Work.”  The report is based on a commissioned study of more than 1,300 security leaders, business executives and remote employees worldwide, including 92 responses in India, conducted by Forrester Consulting on behalf of Tenable.

The study found a stark contrast between Indian organizations’ plans for a hybrid work model and the reality of securing it.

The media reports that IT/ITES companies in India such as TCS, Infosys, HCL Infosystems, Wipro and others have started calling their workforce back to the office. Some, like TCS, have opted for a permanent hybrid work model.

The Tenable study shows that 80% percent of Indian organizations plan to have employees working from home at least once a week in the next 12-24 months, while 63% plan to make a permanent move to remote work over the next two years.

cyberattacks on remote workforce, TenableSpeaking to CISO MAG, Nathan Wenzler, Tenable Chief Security Strategist, said, “The responses we got from the Indian audience are very much in line with what we saw overall. So, I don’t think we see India as being an outlier. But a huge majority of responses from the Indian audience are going to increase investment in cybersecurity, budgets, resources, and tools. And I might even say that was a higher number than we saw across the rest of the globe.”

Remote Workforce Poses New Security Challenges

The Tenable study points out that an alarming 53% of security and business leaders expressed concerns that their organizations are only somewhat or not prepared at all to secure their workforce strategy.

Specific challenges about supporting a remote workforce include the lack of employee awareness to secure home networks and personal devices (53%) and visibility into employee security practices (56%). To further compound matters, a meagre 29% felt that they have enough staff to adequately monitor the attack surface. It’s clear that organizations need to eliminate blind spots by shoring up their defenses to support the next phase of their workforce model.

“One of the things that the pandemic and remote workforce really revealed is that organizations struggle with two things: visibility and all their assets. Assets is not just your servers and workstations, but your IoT devices, your operational technology, your web applications. They don’t have good visibility into what they have. And they don’t respond quickly when those environments change,” said Wenzler.

Impact of an Atomized Attack Surface

The study also found that the fast deployment of new technologies to facilitate remote work heightened the level of risk for Indian businesses. In the past year, a staggering 88% of Indian organizations experienced a business-impacting cyberattack, with 56% of respondents indicating that the attacks targeted remote workers. It is no surprise that, as organizations adopted new technologies to embrace remote work, their software supply chain expanded. Sixty-three percent of security leaders attributed recent attacks to a third-party software vendor compromise – underscoring the need for greater visibility into the atomized attack surface.

cyberattacks on remote workforce, Tenable“The future of work is without perimeters and organizations must be prepared to secure their new reality,” said Kartik Shahani, country manager at Tenable India. “It’s more important than ever for business and security leaders to lock arms and weave cybersecurity into the fabric of their organizations’ digital infrastructure. Organizations must rethink their approach to understanding and managing cyber risk in the new world of work.”

Hybrid work models and a digital-first economy have brought cybersecurity front and center as a critical investment that can make or break short- and long-term business strategies. To address this demand, Indian security leaders plan to increase cybersecurity investments in vulnerability management (92%), cloud infrastructure and platforms (84%) and identity access management (66%).

To read the full study, visit: here