Home Blog Page 280

The Future of AI in Cybersecurity

Artificial Intelligence, AL and ML

By Dick Wilkinson, C|CISO

The buzzword for 2019 that we have all heard a thousand times is Artificial Intelligence, AI. This term has been placed on products ranging from smartwatches to washing machines and of course every security tool on the market. Advertisements lead us to believe that if you couldn’t find a way to shoehorn AI into your product in 2019, you might as well admit defeat before you even get to market. The term AI conjures up science fiction fantasy and makes us believe that the future really is now. People like to hear it and marketing teams like to sell it, but what does AI have to offer in the cybersecurity industry?

The term AI is often interchanged with machine learning. The process that is commonly applied is to collect a very large data set about some type of function, feature, behavior or use case; and then use that large data set to create some kind of predictable pattern. When you can refine your pattern of prediction to something with reliable outcomes you can integrate it into your tools and call it machine learning. If you can teach the machine to continue to collect data on its own and refine the predictions on its own, then you are approaching what most would consider AI. This is a long way away from Terminator Robots walking around securing our networks but is great progress in the right direction.

Behavior-based analysis

Cybersecurity tools currently use this data aggregation and pattern analysis in the field of heuristic modeling. The process works very well to monitor and eventually predict important items such as packet traffic or how each machine operates on your network. We apply behavior-based tolerances to these patterns and when something breaks a tolerance, it creates an alarm. Even this seemingly advanced model still relies on some strong baseline of normal behavior and has to be pre-scripted in many cases.  This method is still only as good as the original data set or programming instructions; the tolerances are hardcoded and inherently stagnant and cause many false alarms in certain instances. The limits become even more evident when the machine learning and prediction stop at machine behavior and does not include the “human” aspect. Security experts know that the user is the most dangerous part of the network, but we spend time and money predicting “machine behavior” and not “user behavior.”

I would like to describe how AI can take us to the next step in securing our networks. Place the dystopian thoughts on hold while I describe how we can observe our user behavior and create even more powerful predictions that lead to true alarms and secure networks. AI will need to move the focus from the way a machine, identified by an IP or MAC address, is behaving, and place the interest on the way the human is acting in each scenario. What I am proposing is a pattern of life analysis on how your users interact with the network on a daily, weekly and even longer-term basis. The selector that indicates the human will not be an IP or MAC address but instead is likely to be some form of biometric identification.

AI will be taught to observe identifying characteristics that all add up to the digital identity of each user

Biometric technology is already widely adopted in some sectors and will probably become ubiquitous over the next 10 years. No username and passwords, just a finger or your face will authenticate you as being you. So we would assume this network is now much less hackable, but you still have the insider threats as well as whatever unique ideas that future hackers discover to defeat biometrics.

We will rely on the greater digital participation of that user to decide if a behavior is normal or anomalous. AI will be taught to observe identifying characteristics that all add up to the digital identity of each user. A user will have a typical day based on things like when they first check their email, what programs they accessed at what times; did they enter or leave the building or secure spaces at certain times. Other identifying features such as keystroke patterns or even specific types of content in chat or email messages will help determine the behavior and identity of a user. This data is not limited to just what happens at work because your users interact with your corporate services via company-issued smartphones, BYO devices, VPN from home, or cloud-based email services.

The true function of AI will be to determine with a long arc of time and data, what “normal” looks like for a user, not a machine

The pattern of life can expand to understand that checking email at 10 o’clock at night is actually “normal” for this user when it is on a smartphone but not when it is at his desk.  The baseline will be learned by the network over time, not preprogrammed to only allow for certain tolerances; the user’s normal activities will define the tolerances. The true function of AI, in this case, will be to determine with a long arc of time and data, what “normal” looks like for a user, not a machine. If this method of AI sensing your users is adopted, then many features can be built to tune the alarm rate and tolerances of the AI algorithm. That process will fall under the CISO and other security professionals to decide what right looks like for their organization. These risk-based decisions can be built into a Risk Management Framework just like any other set of technical controls.

You can sensitize or desensitize your AI engine based on the risk tolerance of a company or department and different models could even apply to different divisions in one company. Your IT admins may be applied a strict tolerance where the guy bolting car doors together doesn’t need the same level of scrutiny. A CISO could even control costs given the assumption that running an aggressive, tight tolerance AI engine on a user will cost more than running a loose tolerance or one that collects fewer data points. These AI functions will be integrated into the SOC or SIEM platform for your organization and will become a seamless sensor just like looking at a machine log event, but it will be human-based, not IP-based.

ROI on AI-based user authentication

The technology to develop and integrate this in an aggressive way already exists, but it is expensive. Biometrics are becoming more common and basic machine learning is built into thousands of programs already. The enhanced decision making and truly flexible tolerance thresholds will be the area requiring more research and the most monetary investment.  Adoption will continue to be slowed by several factors. Digital privacy will be the biggest argument, but that will almost certainly be overcome by the convenience of using biometrics. Cost of implementation will slow adoption, but the cost trade-off of abandoning current SIEM products in favor of user tracking will help ease the burden. The biggest positive factor will be the immediate return on investment. The CISO will be able to clearly define the slew of controls that will be replaced by this new method. High-risk threats like credential-stealing scams will simply disappear when this process is implemented. Insider threats will be extremely well controlled and corporate intellectual property threats will decrease in orders of magnitude. Cyber insurance costs will dwindle to tolerable levels or may not be needed at all depending on the risk appetite of the company. The negative aspects of this user-based AI system will be overshadowed by the clear benefit to the bottom line of the company or agency. An advanced artificial intelligence system that tracks users not machines could be the goal that every CISO strives towards to reduce risk and keep the business running smoothly.

Dick Wilkinson is a senior leader with 20 years of results-focused leadership in the intelligence and cybersecurity field. E has diverse training in intelligence collection, signal analysis, space programs, ethical hacking, cyber vulnerability assessment, penetration testing, cyber program development, and project management. He undertook multiple assignments both stateside and overseas with a wide range of cultural experiences in Europe and Asia. He is a Technical Advisor to Executives at the highest levels as well as liaison relationships with many intelligence community partners. His current job is the Information System Security Officer for the court system of New Mexico. 

CISO MAG did not evaluate the advertised/mentioned product, service, or company, nor does it endorse any of the claims made by the advertisement/writer. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.
Magecart Attacks are now on FBI’s Radar

New Programming Language

The Federal Bureau of Investigation (FBI) recently issued a warning for public and private enterprises in the United States about Magecart attacks, also called e-skimming or web skimming attacks, which are carried out by exploiting security flaws in open-source online stores.

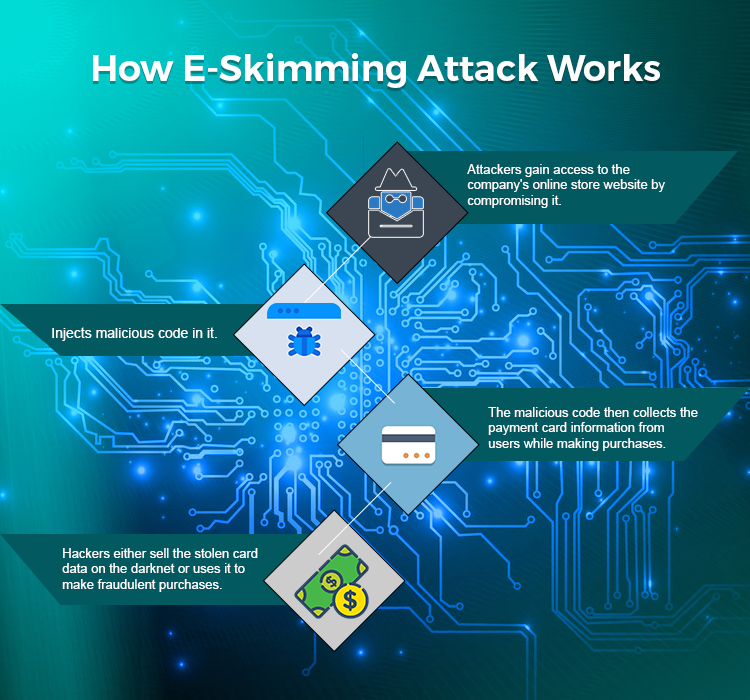
In Magecart attacks, hackers gain access to a company’s online store website by compromising it and hide malicious code in it. The malicious code then collects the payment card information from users while making purchases on the infected site. It’s said that hackers either sell the stolen card data on the darknet or uses it to make fraudulent purchases.

FBI stated that Magecart attacks have been active since 2016, but they’ve increased in 2018 and 2019, and even using diversified attack methodology to launch attacks.

Magecart Attacks

“This warning is specifically targeted to small and medium-sized businesses and government agencies that take credit card payments online. E-skimming occurs when cybercriminals inject malicious code onto a website. The bad actor may have gained access via a phishing attack targeting your employees—or through a vulnerable third-party vendor attached to your company’s server,” the FBI said in a statement.

FBI has suggested security guidelines for businesses to protect themselves from cyber-attacks, which include: Update and patch all systems with the latest security software; Change default login credentials on a regular basis; and Educate employees about safe cyber practices.

In July 2019, the Magecart hacking group was held responsible for a data breach that impacted several websites by injecting malicious code. According to a report from threat intelligence firm RiskIQ, the hackers used a “spray-and-pray” approach to compromise and plant malicious code on over 17,000 domains since April 2019. RiskIQ stated the attackers have been active in web skimming for a long time and started compromising unsecured S3 buckets in early April.

By compromising a few sites, the malicious code spread to thousands of other sites, including Picreel, Alpaca Forms, AppLixir, RYVIU, OmniKick, eGain, and AdMaxim.

Smart Bulbs can be Hacked!

Smart Bulbs Hacking

Internet-enabled smart lighting products offer several novel functionalities over traditional lamps. But a recent survey revealed these connected lights can be maliciously used to violate users’ privacy and security.

A security researcher at the University of Texas at San Antonio (UTSA) stated that hackers may use infrared-enabled smart bulbs to steal data or exploit other connected devices on the home Wi-Fi network.

According to Murtuza Jadliwala, a research expert at UTSA, smart lighting technology uses high-efficiency fixtures and automated controls based on conditions like occupancy or daylight availability. Hackers can compromise infrared-enabled smart bulbs by sending commands via an infrared invisible light emitted from the bulbs to exploit other connected IoT devices existing on the home network.

“Your smart bulb could come equipped with infrared capabilities, and most users don’t know that the invisible wave spectrum can be controlled. You can misuse those lights. Any data can be stolen from texts or images. Anything that is stored in a computer,” said Jadliwala.

“Think of the bulb as another computer. These bulbs are now poised to become a much more attractive target for exploitation even though they have very simple chips,” Jadliwala added.

Many of the recent surveys discovered unknown vulnerabilities in the devices we use often. According to the researchers from the University of Texas, the hackers can make use of internet-connected light bulbs as a covert channel to exploit the user’s private data. The researchers took the LIFX and Phillips Hue smart light systems for the study.

The research stated that hackers can launch an attack by manipulating the infrared light by creating a communication channel between the smart lights and a device that senses infrared light. And by installing a malicious agent on the phone the attackers can encode the private data and transfer them through the infrared covert channel.

The researchers also specified that the proposed threats can be mitigated by enforcing strong network systems and reducing the light transmittance and the brightness of the bulbs that stops the attacks.

Free VPN? Your PC may be a Zombie on a Botnet

Free VPN, Hola

By Best VPN Zone

The desire to save money is inherent in us, humans. When there is a cheaper or a free alternative available, we tend to go with it, as opposed to the paid option. The problem is, we do that even when our safety is at stake.

And while our physical security is something we keep in mind at most times, we rarely think about cybersecurity. It’s easy to overlook how dangerous neglecting it can be when looking at the screens of our devices. We do so many cool things with them, but what are the hidden risks?

This explains the popularity of free security products. And most of all, it concerns VPNs.

Why?

Because of how nonsensical the very concept of a “free VPN” is. Is it really “free”? The infrastructural costs have to be paid somehow. Nobody has set up a bunch of VPN servers all around the world, paying their rent and fees to register their activity in, who knows how many countries, just to provide charitable services, with no profit in mind whatsoever.

So, as the old aphorism goes: Something else becomes the product. Or rather, someone.

The situation is the same no matter what device you want to protect. Whether you’re looking for a VPN for Mac or for Windows, iOS or Android, or even for your set-top box (even more so in this case, really), there aren’t any completely free solutions. You have to forego something: either speed, bandwidth, or your security. Sometimes all three.

That’s not to say that there aren’t any acceptably reliable VPNs, that are almost free. But there is an important caveat: these are funded by a paid version. As you probably guessed, the paid version is going to be better than the free one in terms of speed, features, and traffic limitations. TunnelBear is one example of that.

It offers a paid version and a free one. It can be concluded, then, that the latter is funded by the former. And it makes sense because free users of this service are limited to 500 Mb of traffic per month, whereas there is no limit on the paid version–so there is a very clear incentive to go for the paid version.

Free, but at what cost?

So the verdict is the following: Free VPNs are, at best, not very convenient. At worst, they are plain dangerous.

Experts from VPN Review agree with that. According to them, free VPNs not only lack in features and impose speed and bandwidth limitations on their users, but keep logs on them, too.

What is scary, though, is few people know this or think about it. It seems that these considerations are outweighed by the good old desire to save money, and the even older desire not to bother.

In 2017, researchers from Australia, the U.K., and the U.S. studied 234 VPN applications available on the Google Play Store. They discovered that more than a third of these apps used malware to track users’ online behavior.

Take a look at Hola VPN, for instance. Its website claims that it is used by 200 million people as of today. Most of them use it because it is free.

The irony is, most of those users have not read the terms and conditions before installing Hola VPN. If they did, they would have learned about Hola’s business model. In lieu of payment, users contribute their “idle resources” of their computers to create a “community powered” peer-to-peer (P2P) network. So their PCs become “exit nodes” for other users.

Isn’t that scary?

If that alone did not make them reconsider, then reading about the whole Luminati debacle with selling bandwidth of Hola users to conduct DDoS attacks, will certainly get them thinking. This was reported by cybersecurity solutions company Trend Micro in December 2018. In case you haven’t about it, we will elaborate.

The Luminati debacle

Luminati is a residential proxy provider and, just like Hola VPN, it is owned by Hola Networks Ltd. As Hola’s “Terms of Service” point out, by signing up for the free service provided by Hola VPN, a user “may” become a peer in the Luminati network. Mind you, they do mention this fine print now but prior to the scandal, they did not, which is why there was a scandal in the first place.

Such a problem is not present for paid Hola users. Neither is the necessity to serve as an exit node for other Hola customers who may use one’s bandwidth and IP address to commit any sort of crime.

CISO MAG visited the Luminati website and saw a notice that reads: “Luminati is an ethical proxy network that requires consent from its Residential peers, has tight compliance procedures for its customers and serves Fortune 500 enterprises.”

This claim was not independently verified by CISO MAG.

Back to Luminati. It sells Hola users’ bandwidth to whoever is paying for it. It can then be used for any purpose, depending only on how law-abiding the buyer is.

What happened in 2015 was that a hacker bought a bunch of IP addresses that belonged to Hola VPN users from Luminati. He then used them to conduct a DDoS attack on 8chan, a popular imageboard. Say what you want about anonymous imageboards, but distributed denial of service is not fun.

Obviously, temporary disruption of the work of an entertainment website is not that big deal. However, there is nothing to prevent similar attacks against hospitals and other important facilities. Not to mention all other criminal activity that is possible to carry out by buying Hola users’ addresses from Luminati.

To quote the founder of Hola, when he was asked if all his customers knew how their IP addresses and bandwidth were or could be used, “no […] because most of them just don’t care”.

And here’s the cherry on top: “Free users of Hola do not even have access to a VPN, despite the name of the service. There is no encryption provided to them but just proxy addresses.”

You know that something is seriously wrong when other free VPNs can excuse their lackluster service by saying that at least, they don’t sell their users to be a part of a botnet.

Did those 200 million people not do any research or did they just ignore the facts that went against their desire to not leave the bubble?

One thing is certain: While there are people who are willing to do either, there are going to be more scandals like the Hola botnet one. And it is likely that every time it happens, people will act surprised that they have become the product.

CISO MAG did not evaluate the advertised/mentioned product, service, or company, nor does it endorse any of the claims made by the advertisement/writer. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.
MedusaLocker Ransomware Decoded

ransomware, ryuk ransomware, cox media

MedusaLocker Ransomware is the latest addition to the long list of ransomwares that came up in the year 2019. Researchers are still puzzled about its channel of distribution, but reports suggest that users around the globe are getting infected rapidly by this newbie.

An independent research led by Malware Hunter Team stated the various steps that MedusaLocker Ransomware follows to prep the user’s system for encryption.

  • It first creates a Registry value ‘EnableLinkedConnections’ under a certain path and sets it to ‘1’ to access mapped drives in UAC launched processes.
  • It then restarts the LanmanWorkstation service to ensure that Windows networking is running and further verifies that mapped network drives are accessible to the ransomware.
  • Multiple processes including DefWatch, sqlservr, wrapper, and others, are terminated to shut down security programs ensuring all data files are accessible for encryption.
  • Like most ransomwares, it then clears Shadow Volume Copies of files in the final step. Clearing Shadow Volume Copies ensures that all backups are rendered ineffective and backup files cannot be restored.
  • It then scans files ignoring those with certain extensions (such as .exe, .dll, .sys, .ini, .lnk .rdp) and/or certain files present in specific folders. All other files get encrypted.

It is also found that the files are getting encrypted using AES encryption. Encrypted files have file extensions such as, “.encrypted, .bomber, .boroff, .breakingbad, .locker16, .newlock, .nlocker, .skynet”. MedusaLocker also creates a scheduled task on the victim’s computer. This means it will auto-run after every 30 mins, scan for new files and encrypt these new files.

Ironically, for user convenience, MedusaLocker creates a ransom note named as HOW_TO_RECOVER_DATA.html or Readme.html. The note says, “Your files are encrypted and currently unavailable. You can check it: all files on your computer has a new expansion. By the way, everything is possible to recover (restore), but you need to buy a unique decryptor. Otherwise, you can’t return your data.” It further talks about trust and guarantee, “It’s just a business. If we do not do our work and liabilities – nobody will cooperate with us.”

Ransomware cripples the victim and makes him feel handicapped. In a recent story, a victim of the Muhstik Ransomware attack had his sweet revenge by hacking the hacker back. He even released 3,000 decryption keys along with a decryptor tool so that other affected victims of the ransomware attack would get their files back. Fingers crossed; we hope someone does the same with MedusaLocker Ransomware.

Endpoint Cybersecurity Startup Firedome Raises US$ 10 Million

Firedome Funding

Cybersecurity startup Firedome Inc. recently raised US$ 10 million in a Series A funding round led by New York-based Two Sigma Ventures along with the participation from the World Trade Ventures and Silvertech Ventures.

Founded in 2018, Firedome develops endpoint cybersecurity solutions for detecting, preventing, and reporting vulnerabilities in connected IoT devices. The Tel Aviv and New York-based startup was initially focused on securing smart home devices and is now expanding its business reach into enterprise and industrial sectors.

Firedome’s Endpoint Protection suite protects against different cyberattacks from ransomware, malware, denial of service, and fleet hijacking to remote access and crypto-jacking. Besides, the company assists with decisions regarding intrusion detection, anomalies, events analytics, response to suspicious alerts, and more. Firedome claims that its security operations center team provides customer support on the research and data analysis.

“With IoT devices proliferating rapidly, I believe there is now more than ever a need for robust endpoint device protection,” said Two Sigma Ventures partner Matt Jacobus. “There are 8 billion connected devices that exist today, ranging from complex machines with sophisticated architectures to tiny devices with limited resources, that could benefit from the proactive protection of Firedome’s lightweight agent coupled with their backend machine learning platform and security operations center.

Speaking on the new investment Moti Shkolnik, the CEO and co-founder of Firedome, said, “We were pleased to find out that IoT device companies, across industries, are not willing to compromise the security of their products and are aware of the vulnerabilities that cannot be fully eliminated by static security by design processes,”

“We were happy to witness the rapid progress of closing partnerships with tier 1 companies, about which we will be able to divulge soon. We strongly believe that real-time endpoint cybersecurity is the inevitable future of the IoT security landscape,” Shkolnik added.

Skip-2.0 Malware Provides “Magic Password” to Access Microsoft Servers

Trickbot Malware

Security researchers discovered a Chinese hacking group “Winnti” using a new malware named “Skip-2.0” to get access to Microsoft SQL (MSSQL) Servers. It’s said that the Winnti group was active since 2012 and responsible for high-profile attacks against Gaming studios and IT companies.

According to the IT security firm ESET, Skip-2.0 malware, when installed in memory, provides attackers with a “Magic Password” that allows them to access any MSSQL account running on MSSQL Server version 11 or 12.

Once exploited, the attackers can copy, alter or delete a database’s content. However, ESET stated that Skip-2.0 is a post-exploitation tool, which means that MSSQL servers must be compromised before for the attackers to have the admin access. ESET also stated that it found multiple similarities between Skip-2.0 and the PortReuse backdoor, another tool used by the Winnti group.

“We received a sample of this new backdoor called skip-2.0 by its authors and part of the Winnti Group’s arsenal. This backdoor targets MSSQL Server 11 and 12, allowing the attacker to connect stealthily to any MSSQL account by using a magic password – while automatically hiding these connections from the logs. Such a backdoor could allow an attacker to stealthily copy, modify or delete database content. This could be used, for example, to manipulate in-game currencies for financial gain,” ESET said in a statement.

“In-game currency database manipulations by Winnti operators have already been reported. To the best of our knowledge, skip-2.0 is the first MSSQL Server backdoor to be documented publicly. Note that even though MSSQL Server 11 and 12 are not the most recent versions (released in 2012 and 2014, respectively), they are the most commonly used ones according to Censys’s data,” ESET added.

A similar research from ESET recently uncovered a Russian-based hacking group “Cozy Bear”, the group behind the 2016 U.S. Presidential election hack. It stated the group has been working under the radar to attack the Foreign Ministries in Europe.

Cozy Bear, also known as APT29, is believed to be linked to the Russian intelligence service and Russian military hacking group Fancy Bear, which was involved in high profile attacks between 2014 and 2017.

The researchers stated the group continued their malicious activities while staying under the radar. Cozy Bear recently targeted ministries of foreign affairs of three different countries in Europe, as well as the U.S. embassy of a European Union country in Washington DC.

Are CISOs failing in their communication to the Board?

Board meeting, CISO, leadership

CISO MAG Editorial

The volume of security attacks and threats to organizations has reached alarming proportions, so much so that “cybersecurity” and “cyber risk” have become frequently used words among Boards of Directors.

The Board understands risk, numbers, charts, reports, and strategy. But when news of organizations getting hacked, and the unfortunate consequences, trickles into the boardroom, it triggers waves of panic. The typical questions that arise are, “What if we were hit by that malware or ransomware next? How badly would that impact our business?”.

Board members are likely to be aware of terms like “malware,” “ransomware” and acronyms like DDoS and APT, that the tech industry notoriously creates every year (heard any new ones lately?). They might need a simple explanation of say, how ransomware spreads and what it does. They’re not asking for a crash course in cybersecurity, mind you. But someone who has a deep understanding of cybersecurity and knowledge of business operations has got to answer those nagging questions. That calls for a clear communication strategy. That person must talk cybersecurity using a business lexicon.

But how? What should and shouldn’t be said? 

For its October 2019 issue, CISO MAG reached out to global CISOs, C-level executives and strategists and asked them to share strategies and tips for effective communication. Ten experienced senior management executives who served or continue to serve organizations in government and the private sector shared their best practices and communication strategies. They can be regarded as missionaries of cybersecurity, responsible for spreading awareness, top-down. That’s not an easy task, especially when reaching out to overburdened employees who have their plates heaped with work. Rallying thousands of employees in different locations to talk about best practices and security policies is a Herculean task.

But it’s a job that CISOs need to do because they know that protecting the organization from hackers and malware has more to do with people and processes. The technology is a means to achieve it, but not an end in itself.

It’s the CISO’s job to identify the risks that are most likely to impact the business – and translate that into potential losses using absolute business terms and quantifiable metrics.

However, many CISOs are failing in their communication and are not successful in influencing Board decisions.

Capgemini’s The Modern, Connected CISO report revealed 60 percent of organizations have their CISO at key board meetings, but only half of business executives think the role has a high level of influence on management decisions. One of the reasons for this could be that C-suite and cybersecurity experts don’t talk the same language.

The CISOs we interviewed for this issue told us that using data points and speaking in terms of risk are some ways to get the Board’s attention. Using common security analogies to explain a threat is a better approach than using technical jargon.

And they also shared how they keep themselves abreast with developments and how they continually train others in the organization.

Bottomline: The CISO should be an excellent communicator to win the Board’s mindshare and approval for security investment.

To learn more about the communication strategies of global CISOs, read the October issue of CISO MAG here.

How Facebook is Securing the 2020 U.S. Elections from Russian Meddling

Facebook stated that it is tightening its security for the 2020 U.S. elections after fresh signs of Russia meddling. The social media giant stated that it’s taking down accounts involved in illicit activities and stepping up searching state-controlled media trying to manipulate American voters.

Facebook pledged to use a variety of security measures, including artificial intelligence, to counter Russian attackers or other online intruders who use misleading strategies and false information to meddle in the 2020 U.S. elections.

“We have a responsibility to stop abuse and election interference on our platform. That’s why we’ve made significant investments since 2016 to better identify new threats, close vulnerabilities and reduce the spread of viral misinformation and fake accounts. Today, almost a year out from the 2020 elections in the U.S., we’re announcing several new measures to help protect the democratic process and providing an update on initiatives already underway,” Facebook said in a statement.

The new steps announced by Facebook include, Fighting Foreign Interference, Preventing inauthentic behavior, Increasing transparency, Labeling state-controlled media on their Page and in the Ad Library, Preventing the spread of misinformation, and monitoring candidates accounts, elected officials through Facebook Protect.

“As we’ve improved our ability to disrupt these operations, we’ve also built a deeper understanding of different threats and how best to counter them. We investigate and enforce against any type of inauthentic behavior. However, the most appropriate way to respond to someone boosting the popularity of their posts in their own country may not be the best way to counter foreign interference,” Facebook added.

The latest move adds to a series of measures from Facebook since 2016, after foreign bodies involved in meddling of the U.S. election campaign. The social media giant drew fire for not handling misinformation and election manipulation on the platform too well.

Earlier, Facebook claimed that a Russian group posted more than 80,000 times on its service between January 2015 to August 2017. Nearly 29 million Facebook users directly received their posts in their news feeds. The Facebook officials disclosed these numbers to the Senate Judiciary Committee on October 31, 2017.

US Legislation Launches “Mind Your Own Business” Act

France Fines Facebook and Google,Russia fines Google, Meta heavily New York City Law Department Hit by a Cyberattack

From now, the Chief Executive Officers who misuse customers’ data could end up in jail for twenty years.

The U.S. legislation recently proposed “Mind Your Own Business Act”, which prosecutes top-level executives if their companies are found misusing citizens’ information and lying about it. Authored by Senator Ron Wyden, the bill requires organizations to produce annual data protection reports personally certified by the company’s CEO, proving that they obeyed the data regulations.

“This bill is in the first stage of the legislative process. It was introduced into Congress on October 17, 2019. It will typically be considered by committee next before it is possibly sent on to the House or Senate as a whole,” said Ron Wyden.

The new legislation adheres to a draft version known as the Consumer Data Protection Act, which was released for discussion on November 1, 2018.

The proposed bill applies to the companies that hold data of more than 50 million customers or over a million people if they make a revenue of more than US$ 1 billion. In case the company intentionally certifies false reports, then they’re subjected to a fine up to US$ 5 million or face up to 20 years of imprisonment. It also provides customers the right to demand details of any personal data collected by the companies.

Companies are also required to notify their customers what information they collect and what they are going to do with it. The bill also requires companies to provide a site that enables consumers to opt-out of any personal data collection.

Recently, the New York State Legislature passed a new bill in order to strengthen its data breach policies. The new bill, dubbed as Stop Hacks and Improve Electronic Data Security Act (SHIELD), provides more transparency to consumers, while it also imposes stringent penalties on companies without proper cybersecurity measures.

According to the Attorney General Letitia James, the SHIELD Act will update the state’s breach notification laws, expand the current notification requirements for companies, increase penalties for liable companies, and increase the rights of consumers in the event of a breach. The bill imposes tough obligations on businesses that handle sensitive data of customers.  The businesses are required to maintain reasonable data security measures in case they’re collecting personal data from the customers.