
Cybersecurity solutions provider Trend Micro warned users about a new wave of attacks targeting home routers. In its research report “Worm War: The Botnet Battle for IoT Territory,” Trend Micro revealed that cybercriminals are using home routers to build botnets. The research found a surge in cyberattacks by exploiting routers, particularly in Q4 2019. Attackers made brute force log-in attempts against routers by using automated software to try common password combinations. The number of attacks increased from around 23 million in September to nearly 249 million attacks in December 2019. In March 2020, around 194 million brute force login attacks were reported.
The research stated that attackers used three types of botnet malware variants namely “Kaiten,” “Qbot,” and “Mirai”. Using these three bot source codebases, the attackers created other botnet malware variants to compromise routers and other IoT devices. The compromised routers’ details are sold on hacking forums or used to launch cyberattacks like Distributed Denial of Service (DDoS) attacks, click fraud, data theft, or account takeover.
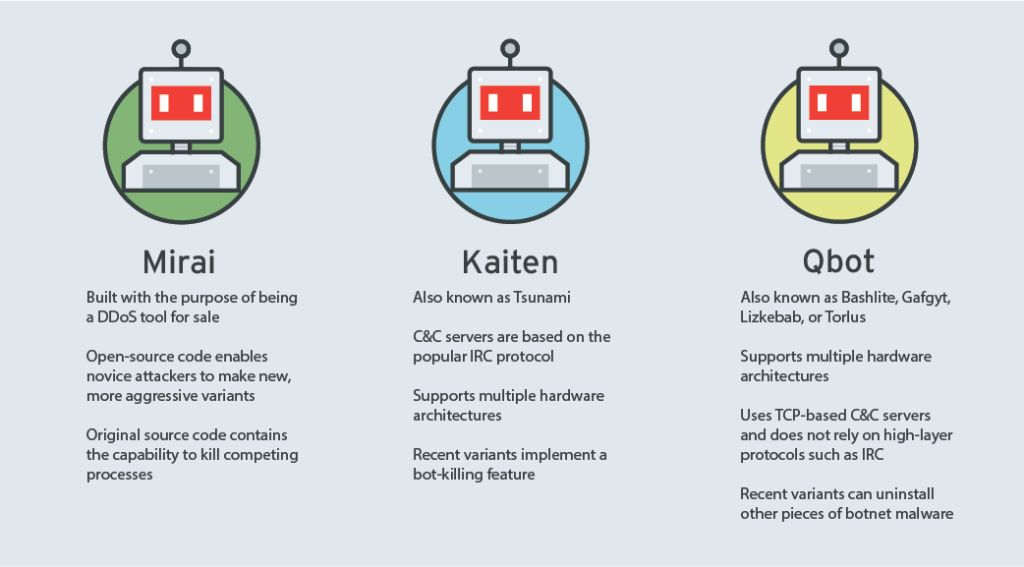
“Kaiten, Qbot, and Mirai demonstrate the capabilities that allow botnet malware to compete for dominance over connected devices. To grow a botnet and maintain its size, botnet malware families and variants need to be able to infect as many devices as possible while defeating other usurpers. Botnet malware can search for vulnerable devices and use well-known tactics such as brute force to take control of a device,” the report said.
“With a large majority of the population currently reliant on home networks for their work and studies, what’s happening to your router has never been more important. Cybercriminals know that a vast majority of home routers are insecure with default credentials and have ramped up attacks on a massive scale. For the home user, that is hijacking their bandwidth and slowing down their network. For the businesses being targeted by secondary attacks, these botnets can totally take down a website, as we have seen in past high-profile attacks,” said Jon Clay, director of global threat communications for Trend Micro.
Mitigation Measures
Trend Micro also recommended certain security measures to home router users, these include:
- Manage vulnerabilities and apply patches as soon as possible. Vulnerabilities are the main way malware infects devices. Applying patches as soon as they are released can limit the chances for potential exploits
- Apply secure configuration. Users must ensure that they are using the most secure configuration for their devices to narrow openings for compromise
- Use strong, hard-to-guess passwords. Botnet malware takes advantage of weak and common passwords to take over devices. Users can circumvent this tactic by changing default passwords and using strong passwords

