
Food delivery firm Foodora is a victim of a data breach that exposed more than 727,000 customers’ details from 14 countries across Europe including France, Finland, Austria, Spain, and Italy. The exposed data included usernames, phone numbers, addresses, full names, locations, and hashed passwords of Foodora customers. However, payment information or credit card details are not breached in the incident, according to Databreachtoday report.
Delivery Hero, the parent company of Foodora, stated that unknown members posted the leaked customers’ data on various hacking forums. The data was dumped in a series of SQL files for each country, labelled as “CustomerAddress” and “Customers.” The affected customers are getting suspicious emails from unknown third parties, the company said.
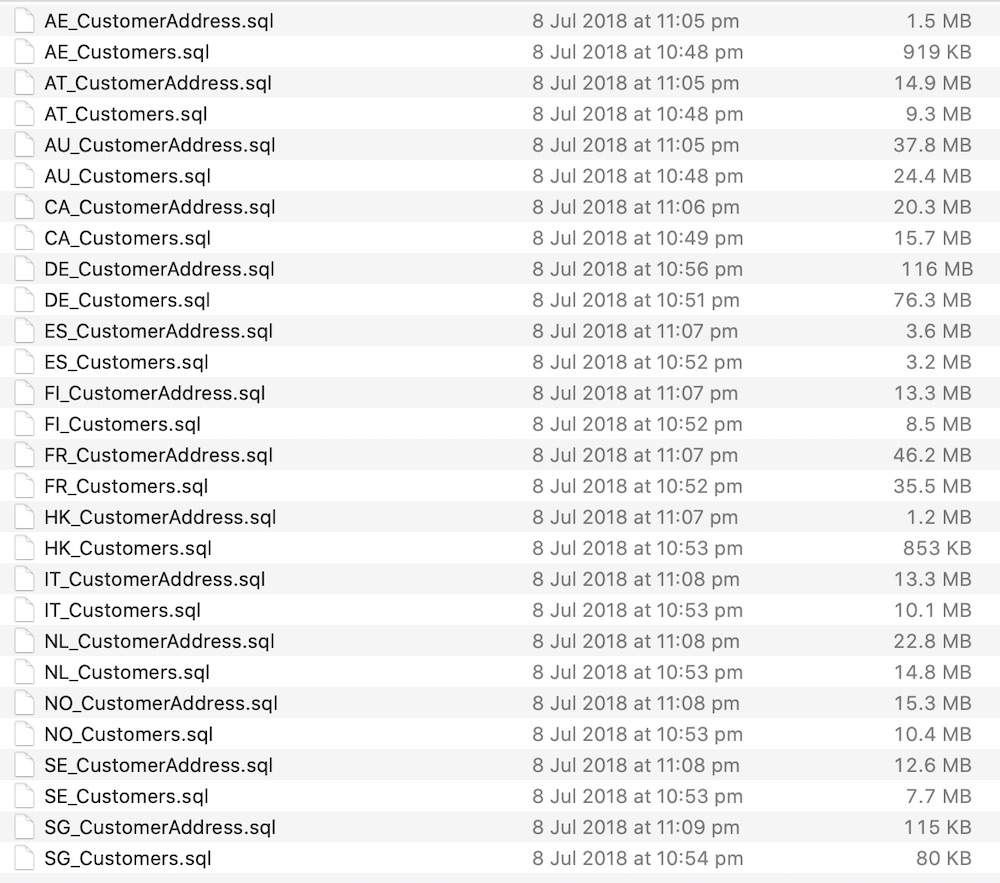
“Unfortunately, we can confirm that a data breach has been identified concerning personal data dating back to 2016. The data originates from some countries across our current and previous markets. We started a thorough internal investigation and have informed all relevant authorities. We are working closely with our security and data protection teams, as well as local authorities, to identify what caused the breach and inform the affected parties,” Delivery Hero said in a statement.
In addition, Troy Hunt, data breach expert and the creator of Have I Been Pwned data breach notification service, tweeted, “Foodora had 583k unique customers exposed in 2016. Data included names, delivery addresses, phone numbers and passwords stored as either salted MD5 or bcrypt. 73% were already in @haveibeenpwned.”
Cyberattacks on Food Delivery Services
Multiple security incidents have been reported on food delivery service providers globally. In a recent incident, threat actors launched a distributed denial-of-service (DDoS) attack on Germany-based food delivery firm Takeaway.com (Liefrando.de). Attackers demanded two Bitcoins (around US$11,000) in ransom to stop the attack. Earlier, DoorDash, a San Francisco-based food-delivery service provider, faced a massive data breach that affected data of around 4.9 million people (its customers, delivery workers, and merchants), who were using its service platform. The company said that an unauthorized third-party accessed its user data on May 4, 2019. DoorDash clarified that users who joined its services platform on or before April 5, 2018, were affected in the incident.

