
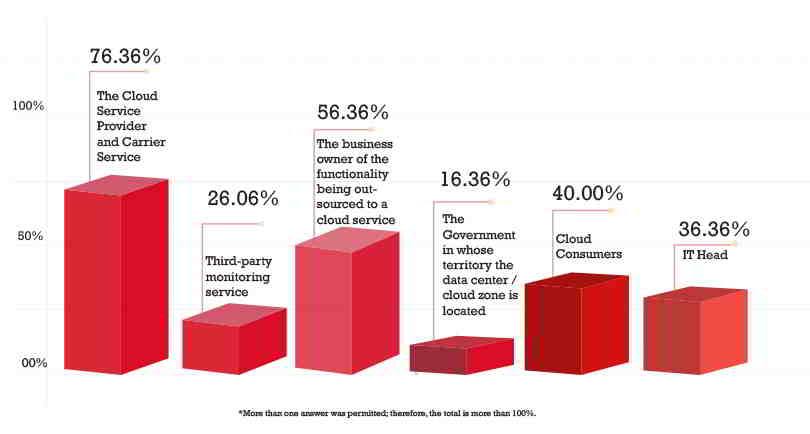
Who do you think is responsible for the security of the cloud? This question evoked mixed responses in CISO MAG’s Cloud Security survey. More than two-thirds of respondents (76.36%) said the cloud service provider (CSP) is entirely responsible for the security of the cloud. This was a multiple-choice question and from this set, some also feel it is the responsibility of the business owner of the functionality being outsourced to a cloud service. And some (40%) said it is the responsibility of the cloud consumers. It is clear there is a disconnect with consumers on security responsibility in the cloud. The complete research report on Cloud Security trends is published in the June issue of CISO MAG here: https://staging-cisomag.com/magazine/
“There is a lack of clarity or understanding of the shared responsibility model related to security. As well as, a misconception about the potential security services available to organizations as they migrate to the cloud,” said AJ Yawn, a cloud security expert who is also on the Board of ISC2.
Understanding the shared responsibility model is a critical first step for companies as they move to the cloud, without this understanding they could be exposed to security risks and weaknesses.
AWS defined a Shared Responsibility model that says “Security of the Cloud” is the responsibility of the CSP, but “Security in the cloud” is the responsibility of the customer. This model is gradually being accepted in the industry.
In the IaaS model, end-user or business owners will own the security to their systems, but implement the controls made available by the provider. It depends on how the business owner configures all the services they use on the cloud.
Much depends on their security policies and access controls. Security issues are often the result of user carelessness and unawareness, and the CSP cannot be held accountable for that. On the other hand, the CSP or MSSP should take all steps to secure the infrastructure that it provides to its customers.
Cloud experts that CISO MAG editors consulted for this survey said customers should never assume that because they were hosted on a particular cloud service provider, they inherited the compliance certifications or achievements of the CSP. This false assumption will leave them unprepared when the time for compliance assessments comes.
CISO MAG conducts a Cloud Security survey annually, and the last such survey (and research report) was published in July 2019.

 said the cloud service provider (CSP) is entirely responsible for security of the cloud.)