
Security researchers at AdaptiveMobile Security, a Cyber-Telecoms Security company, uncovered a new undetected vulnerability that’s being exploited by attackers for targeted surveillance of Android and iOS mobile phone users. It’s said that the flaw is linked to a technology embedded on SIM cards.
The vulnerability, dubbed Simjacker, is used to hijack SIM cards by sending a text message to target devices. When exploited, the vulnerability activates specific SIM card instructions which then allows hackers to spy on the victim’s active location, make fraudulent calls, force-install malware, send fake messages, and steal critical information.
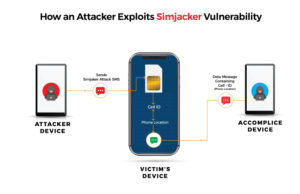
Researchers stated cybercriminals have obtained location information from over 1 billion mobile devices globally, by exploiting the Simjacker vulnerability, without users’ consent. It’s believed that the attackers originated from a surveillance company that works with government agencies to monitor individuals who bypass signaling protection.
According to AdaptiveMobile Security, the vulnerability potentially impacted countries in North and South America, including the Middle East, West Africa, Europe, and any part of the world where this SIM card technology exists.
While commenting on the discovery of the critical flaw, Cathal McDaid, CTO at AdaptiveMobile Security said, “Simjacker represents a clear danger to mobile operators and subscribers. This is potentially the most sophisticated attack ever seen over core mobile networks. It’s a major wake-up call that shows hostile actors are investing heavily in increasingly complex and creative ways to undermine network security. This compromises the security and trust of customers, mobile operators, and impacts the national security of entire countries.”
“Simjacker worked so well and was being successfully exploited for years because it took advantage of a combination of complex interfaces and obscure technologies, showing that mobile operators cannot rely on standard established defenses. Now that this vulnerability has been revealed, we fully expect the exploit authors and other malicious actors will try to evolve these attacks into other areas,” McDaid added.

