
The average enterprise ransom payments increased 33% ($111,605) in Q1 of 2020 from Q4 of 2019, according to the Coveware Ransomware Marketplace Research report. The research revealed that ransomware operators succeeded in targeting large organizations and forcing ransom payments.
It was found that Sodinokibi (used in 26.7% of attacks), Ryuk (19.6%), and Phobos and Dharma (7.8%) were the top three most used ransomware variants in Q1 of 2020. Coveware stated that Maze, Dopplepaymer, and Sodinokibi operators are using content before encrypting the data, and holding it hostage to threaten to post it unless the target agrees to pay.
| Rank | Ransomware Type | Market Share % | Change in Ranking from Q4 2019 |
| 1 | Sodinokibi | 26.7% | – |
| 2 | Ryuk | 19.6% | – |
| 3 | Phobos | 7.8% | – |
| 4 | Dharma | 7.8% | +1 |
| 5 | Mamba | 4.8% | +4 |
| 6 | GlobeImposter | 4.4% | +5 |
| 7 | Snatch | 2.6% | +1 |
Data Source: Coveware
The research highlighted that each of the ransomware variants were used to target different sizes of organizations – Ryuk ransomware was used against large organizations with more than 1,000 employees. While Sodinokibi attacked medium size enterprises with around 370 people, and Phobos focused on small businesses averaging 81 people. Ryuk earned the largest ransom payouts worth $1.4 million, compared to $327,931 for Sodinokibi and $15,761 for Phobos.
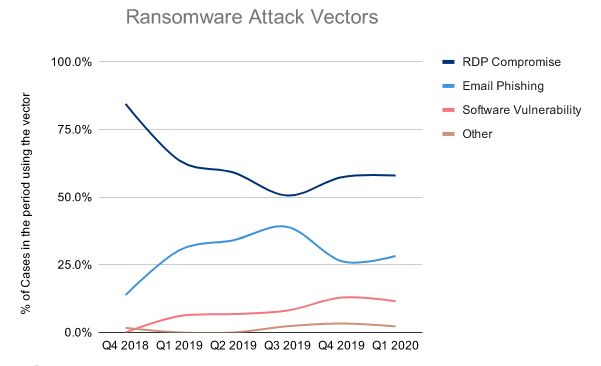
The most common attack vector that threat actors used was Remote Desktop Protocol (RDP) access points, used about 60% of the time. While email phishing attacks were reported as the second most used attack type, accounting for about 30%.
“Poorly secured Remote Desktop Protocol (RDP) access points continued to be the most common attack vector. RDP credentials to an enterprise IP address can be purchased for as little as $20 on dark marketplaces. Combined with cheap ransomware kits, the costs to carry out attacks on machines with open RDP were too economically lucrative for criminals to resist. Until the economics of carrying out ransomware balance ransomware and cyber extortion will continue to gain prevalence,” the report stated.
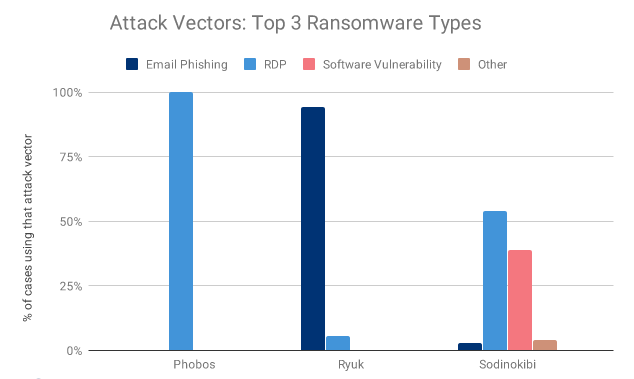
The research findings also revealed that small and medium sized service providers like law firms, IT, and CPA firms continued to be the primary target for ransomware attacks in Q1 2020. However, government organizations and educational institutions jumped in popularity due to the COVID-19 outbreak.

