Home Blog Page 64

Identity as the New Perimeter

Identity Access

In this day and age, your identity is a shared asset. Be it a calling card, passport or license — it’s the means by which you, the user, and private or public enterprises can safeguard and secure each other.

By Robert Fly is co-founder and CEO of Elevate Security

Identity is the new perimeter, and with the transition to remote work, companies have to rethink their security strategy. As end-users everywhere pushed through pandemic lockdowns and plugged in outside of company networks and security walls, there has been a visible rise in cybercrime.

According to the Verizon Business 2021 Data Breach Investigations Report, the past year saw company breaches rise by over a third compared to 2019, with ransomware doubling in frequency and passwords (stolen or taken in brutal force attacks) causing 89 percent of breaches. These statistics predated the attacks on Colonial Pipeline, JBS and Kaseya, which are only the latest examples of this trend.

A Brave New World

By transitioning to remote work, companies had to effectively cede some security controls to their employees, whose every action could – and sometimes did – render their organizations more vulnerable to malicious threats. We’re in a brave new world, where each employee’s past and future security decisions – good or bad – are now the focal point from which we validate our security posture. With this transition, we’ve begun relying on the identity of our users to verify security.

This comes down to a password and MFA code and maybe a device assessment, but we’ve forgotten an important part: each individual in our workforce has made better or worse security decisions, enjoys more or less access, and gets attacked at different frequencies. Yet we have no insight into those important factors when making trust decisions.

The old ways of managing workforce risk in the enterprise are no longer enough. Multi-factor authentication and password managers are useful but don’t fully close the gap. Awareness training and phishing simulations aren’t working either, with no direct correlation between their results and real-world attacks. And we’ve added more and more layers of technology over the last decade only to see the same attacks continue to plague us and security slowing down the business.

Confronting the Inevitable with Zero Trust and Increased Visibility

It’s inevitable that your workforce will make mistakes that could lead to ransomware, account takeover or data loss – all of which can lead to even larger reputational risks for your business – and security programs need to be built around that reality. With this reality, we need to think about how we take a Zero Trust approach to our workforce – and enhance the visibility of the human attack surface – or, the sum total of people’s actions, access, and security controls that impact an organization’s risk.

With remote work, companies have adopted identity as the centerpiece of protection. Given that at the center of identity is a person, we also need to rethink our strategy there. No one person is the same and using simple authentication based on simple risk heuristics are remnants of the old model rebranded for this new world. The one-size-fits-all workforce security controls of the past now seem a bit ham-fisted. With identity as the new perimeter, enterprise security teams need to assess the security risk of each and every end-user individually and in totality and then apply our understanding of them to feedback into proactively protecting them in our IAM solutions and beyond.

With this deep contextual visibility, we can build risk scores that

  • Authenticate a user – who they are, where they’re located, and if their device is familiar, and
  • Authorize a user to access applications or systems based on their past reputation for risky behavior – both the actions taken and how frequently they’ve been attacked. Precautions such as security controls and policy orchestration can then be tailored to protect the riskiest users and the company.

If step one is building deep visibility into security logs, alerts and incident data to understand workforce security risks, then step two is making use of it. While step one gives you historical views into your workforce risks, step two is a proactive step in doing something about it – helping maintain security in a Zero Trust environment while reducing security friction overall for the business. Your riskiest users see more friction, your less risky users see less. It involves fine-grained tailored security controls, direct feedback based on attacks, security decisions and risks, and deep integration into workflows to ensure appropriate decisions are made by systems and your security team.

Predict and Be Proactive

Unfortunately, most companies have not taken the step in understanding their workforce risk beyond simple implementations of IAM systems. Security teams are incredibly adept at implementing technologies for authentication and monitoring, but have lacked the tools, insights and automation to predictively and proactively protect their organization against future attacks. Our current technology stack has failed to protect our biggest risk – the user – but even when they do their job, users continue to mess up, and as recent research shows, no amount of training or simulation has made a meaningful difference. We need to take a different approach.

For too long, the onus has been on end-users to be more aware of company security and change their behavior. We need to bring balance to this equation and allow security teams to predictively understand individual risk and proactively protect employees based on the risk of who they are, what they do and what they’re trying to access. By using identity as the center point between individuals and technology, we tacitly acknowledge every user is a unique part of this equation.

With more people working from home, corporate networks aren’t able to protect enterprises as in the past. By taking a Zero Trust approach to workforce security with identity as the new perimeter, companies can gain deep insight into each user’s actions, access level, and how often they are attacked. Cybersecurity can stop reacting and start proactively protecting against the next attack, reducing both the frequency and impact of these incidents.


About the Author
Robert Fly_CEO_Elevate SecurityRobert Fly is the co-founder and Chief Executive Officer at Elevate Security, where he leads a team of world-class engineers to help CISOs measure, communicate and reduce human risk and keep their companies safe from cyber threats. Prior to Elevate Security, Robert spent almost two decades leading security and engineering teams at Salesforce, where he was the VP of Security Engineering, and at Microsoft, where he was the Senior Software Security Lead. He is also an investor, advisor, board member and/or CISO across a dozen global startups, including Airtable, BigCommerce, RedLock, SafeBreach, Qualia and Cobalt.

Disclaimer

Views expressed in this article are personal. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.
After Phishing and Identity Thefts, LockBit 2.0 Operations Rise in Australia

Ransomware attacks, LockBit Ransomware

Australians have become a target for different kinds of cyberattacks lately. The Australian Competition and Consumer Commission (ACCC) reported an 84% surge in identity theft scams, 75% in phishing scams, and a significant increase in remote access scams in the country. Now the Australian Cyber Security Centre (ACSC) is warning about the rise in LockBit 2.0 ransomware operations in Australia.

The ACSC identified several victim organizations in Australia that are impacted by LockBit 2.0 ransomware. Attackers successfully exploited organizations across multiple sectors, including construction, manufacturing, retail, food, and IT. LockBit operators are reportedly performing double-extortion schemes by posting compromised sensitive victim data on their dark web site LockBit 2.0, and threatening the victims to expose the compromised data online if the ransom is not paid.

“The LockBit ransomware restricts access to corporate files and systems by encrypting them into a locked and unusable format. Victims receive instructions on how to engage with the offenders after encryption. LockBit affiliates have successfully deployed ransomware on corporate systems in a variety of countries and sectors, including Australia, where the ACSC is aware of numerous incidents since 2020,” the ACSC said.

LockBit 2.0 aka ABCD

LockBit ransomware variant, also known as LockBit 2.0 or ABCD, was detected in September 2019 as a Ransomware-as-a-Service (RaaS), enabling malicious affiliates to leverage it to exploit networks of the targeted victims.

The ACSC claimed that it found LockBit operations on Russian-language cybercrime forums since January 2020. Attackers have been advertising the latest version of the LockBit RaaS as LockBit 2.0 since June 2021. The new LockBit 2.0 ransomware is bundled with built-in information stealing feature dubbed as StealBit.

Mitigations

As per the ACSC’s findings, LockBit operators are actively exploiting unpatched vulnerability CVE-2018-13379 in the Fortinet FortiOS and FortiProxy products to gain access to victim network systems. ACSC authorities urged organizations to perform serious risk assessments and necessary security precautions to secure their corporate networks against LockBit 2.0 ransomware. The mitigations include:

  • Establish processes to identify, assess, and patch vulnerabilities affecting your organization
  • Enable multifactor authentication (MFA) for all user accounts, particularly privileged accounts.
  • Educate users to reduce password re-use.
  • Encrypt sensitive data at rest. Consider segmenting networks to separate sensitive data from corporate environments.
  • Consider restricting access to web-based storage services from corporate networks.

LockBit ransomware has become popular in the cybersecurity landscape with its advanced extortion techniques and attacks. Therefore, implementing required cybersecurity measures will help organizations defend against rising ransomware variants.

Misconfigured Amazon Bucket Exposes Personal Data of Millions of Senior Citizens

Senior citizens data

Whether it’s critical corporate data or students’ information, threat actors often misuse sensitive data obtained from security data breaches. Recently, security researchers from threat intelligence firm WizCase uncovered a massive data breach affecting a misconfigured Amazon S3 bucket owned by SeniorAdvisor. The company provides consumer ratings and reviews for senior care services across the U.S. and Canada.

The unsecured bucket contained over a million files, accounting for 182 GB of data belonging to three million senior citizens. The exposed information included users’ personally identifiable information (PII), including surnames, phone numbers, emails, and dates contacted. Most of the data exposed were in the form of leads (potential customers) collected by SeniorAdvisor, probably via email or telemarketing campaigns. The misconfigured database is now secured after WizCase researchers reported the issue to SeniorAdvisor.

WizCase researchers said, “Our security team found around 2,000 scrubbed reviews. These are reviews where the user’s sensitive information has been wiped or redacted. However, this scrubbing process is useless if you have the corresponding information. The scrubbed reviews had a lead id which could be used to trace the review back to who originally wrote it. Since the lead data and these scrubbed reviews were in the same database, supposedly anonymous reviewers could have their identity revealed with a simple search operation.”

Risks Involved

The data breach left senior citizens’ data vulnerable to various attacks. Elderly users are more prone to fall victim to phishing, social engineering, and other digital scams. According to a report from the FBI, cyberattacks on senior people have been increasing exponentially. The major cybercrimes against elders include extortion, personal data breach, tech support fraud, confidential fraud, dating scams, real estate, and social media frauds.

Earlier, the U.S. Department of Justice (DoJ) issued a fraud alert asking people to be vigilant when providing sensitive information over the phone. The agency stated that cybercriminals were falsely represented themselves as DOJ authorities to obtain personal information from the call recipients as part of imposter scams.

These are the Top 4 Cybersecurity Skills In-demand in 2021

SMBs cybersecurity, Cybersecurity skills, Conti Ransomware Group Reportedly Stole 1.5TB Of Data from JVCKenwood

Amidst growing cybercrime and cyberthreats, it is wise for businesses to hire professionals with cybersecurity skills. The pandemic-induced lockdown has changed the way we work, and as more people work from home, the risk of cybercrime is increasing. While digitalization has changed the landscape of IT (Information Technology), it is not free of threats.

Cybersecurity is the practice of securing your system, networks, devices, and applications from hackers and malicious attacks. Cybersecurity is a subset of Information Security or InfoSec. Implementing cybersecurity measures to protect your business data, files, or information is essential for every business. In fact, organizations have to comply with regulations to secure data and systems; failure to do so will result in stiff penalties and fines, which will impact the balance sheet. An organization’s reputation could also be impacted, and it could experience customer churn.

Importance of Cybersecurity  

With rapid improvements in technology, such as big data and the IoT (Internet of Things), the risks of data theft and harm have increased. Companies and institutions rely on technology, and cyberattacks such as ransomware, socially engineered attacks, and others are evolving as well.

According to Cybersecurity Ventures, cybercrime will cost around $10.5 trillion annually by 2025 globally, growing by 15% every year over the next five years.

The pandemic-induced lockdown led to businesses adopting a virtual or remote-work framework, thereby increasing the risks of cyberthreats.

Therefore, professionals with cybersecurity skills are required to mitigate the threats and will always be in demand. Without them, the chances of organizations winning the fight against data breaches and cybercrime are slim.

This article helps you learn the importance of the rapidly increasing field, i.e., cybersecurity and its elements. We shall also discuss the top four cybersecurity skills in demand in 2021.

Fastest Growing Cybersecurity Skills

One cannot undermine the importance of digital security. Companies around the globe need cybersecurity specialists and IT experts to protect and recover their data, systems, and applications. Therefore, professionals need to know the in-demand cybersecurity skills required to safeguard the security of your business.

As per a report published in studyinternational.com, 301 data breaches in 2020 revealed over 5 million sensitive data records. This highlights the importance of the need for cybersecurity professionals in your organization. They hunt threats and mitigate the risks of data theft.

IT Security specialists skilled in application development security, risk management, and cloud computing will have the most job opportunities.

In-demand Cybersecurity Skills

Building a career in cybersecurity requires in-depth training and knowledge. Apart from basic computer and programming skills, one also needs to learn the important skills required for cybersecurity jobs. Let’s learn about the top four in-demand cybersecurity skills in 2021:

1. Application development security

Application development security is one of the most in-demand cybersecurity skills in 2021, per a report from Atlas VPN.

In five years, Atlas VPN forecasts a 164 percent increase in demand for this skill.

Application development experts find and patch flaws in apps to improve security in the developmental phase. Threat attacks are increasingly becoming sophisticated with the advancements in technology, so naturally, the risks are high.

Therefore, building a secure application is no small task. Application development security must include measures in all aspects of the software development cycle. It is one of the most crucial cybersecurity skills needed to secure an organization’s assets.

A few occupations, such as Software Developer, System Engineer, Cybersecurity Engineer, DevOps Engineer, and Network Architect, require the expertise of an application security specialist.

  • Expected salary in 2021: $12,266
  • Growth forecast for the next five years: 164% 

2. Cloud security

Cloud security is encompassing robust technologies and measures to prevent online data leakage and theft. Reports suggest that cloud security is in the top two in-demand cybersecurity skills in 2021.

Security measures to protect cloud computing infrastructure from internal and external threats, malware, and ransomware are the need of the hour. Therefore, the demand for professionals with a cloud security skillset is only going to increase.

Cloud security is essential for individuals and businesses because sensitive data, applications, and resources are shifting to cloud storage. The tools used by hackers are also changing along with evolving technology. As technology advances, so do the tools used by hackers. Therefore, organizations need to employ skilled cloud security professionals to protect their cloud data from theft and risks.

Some significant positions, such as Software Developers, Cloud Architects, Cybersecurity Consultants, System Engineers, and Cybersecurity Engineers, require expertise in Cloud security skills.

  • Expected salary in 2021: $15,025
  • Growth forecast for the next 5-years: 115%

3. Risk management

A Cybersecurity risk management professional analyzes data to understand the risks the organization can face and minimizes them. Chief Information Security Officers (CISOs) work closely with business stakeholders and leaders to identify the threats and their extent and build concrete steps to lower the risks.

Occupations like Cybersecurity Analyst, Cybersecurity Manager, Cybersecurity Engineer, Network Architect, and System Engineer require expertise in risk management skills.

  • Expected salary in 2021: $13,379
  • Growth forecast for the next five years: 60%  

4. Threat intelligence

Every organization or governmental institution requires security professionals skilled in cyberthreat intelligence to mitigate cyberattacks. Threat intelligence is analyzing the organization or business data for potential threats. Professionals with this cybersecurity skill are well-versed in the intent and resources of cyberthreats. Businesses can use threat intelligence data to assess the intentions and goals of threat actors and make informed security decisions.

Professions like Cybersecurity Analyst, Cybersecurity Engineer, Security Intelligence Analyst Vulnerability Analyst, and Software Developer need threat intelligence skills.

  • Expected pay in 2021: $9,609
  • Growth forecast for the next five years: 41%

Conclusion

Cybersecurity is a thriving domain with numerous career opportunities. Businesses and government agencies alike require security professionals who are proficient in cybersecurity skills to combat cybercrime.

Risk management and threat intelligence are the other top cybersecurity skills projected to grow 60% and 41%, respectively, in the next five years.

If you want to thrive in this field, you need to show your cybersecurity skills on your resume. You can join the Certified Ethical Hacker (C|EH) certification to acquire the necessary skills. A cybersecurity specialist needs to have good technical and analytical skills. They also need to adopt a wide range of other skillsets to explore and identify the threats an organization can face. CEH helps participants acquire the skills needed for cybersecurity professionals to advance their careers.

Become an Ethical Hacker 

If you want to learn the in-demand skills required for cybersecurity specialists, you should get EC-Council’s C|EH certification. CEH modules include everything you need to know about cloud security and IoT, modern exploit technologies, and attack vectors. The certification enables participants to grasp the basic and advanced technical knowledge required in this field. This certification is recognized by the United States Department of Defense and includes knowledge of a broader aspect of the entire cybersecurity domain.

Join EC-Council’s ethical hacking course and advance your career in the right direction.

20+ Job Roles | 10,000+ Job Openings | Avg. Salary of $93,000

Become a Certified Ethical Hacker


FAQs (Frequently Asked Questions)

1.What is cloud security?

Cloud security is encompassing robust technologies and measures to prevent online data leakage and theft. Reports suggest that cloud security is in the top two in-demand cybersecurity skills in 2021.

Security measures to protect cloud computing infrastructure from internal and external threats, malware, and ransomware are the need of the hour. Therefore, the demand for professionals with a cloud security skillset is only going to increase.

2. What is cloud security?

A few of the top cybersecurity skills expected to create numerous job opportunities in 2021 are cloud security, risk management, threat intelligence, application development security, incident response, security strategy and control, and health information security.


References:

  1. https://www.cm-alliance.com/cybersecurity-blog/understanding-cybersecurity-risk-management
  2. https://www.csoonline.com/article/3315700/what-is-application-security-a-process-and-tools-for-securing-software.html

“We are committed to turning companies with ideas into global industry leaders”

Israel has a booming startup ecosystem with investors, startups, research centers, and multi-national big tech companies (IBM, Intel, Microsoft, Google etc.), and with the support of academic institutions, the Israeli government, and the military organizations. This ecosystem has witnessed phenomenal growth over the years in investments, M&A, IPOs, and exits. This ecosystem has created world-leading companies. A chunk of funding for tech firms goes into Israeli startups. According to the Annual Israeli Tech Review, about $9.93 billion was invested in privately-held Israeli tech firms in 2020, up 27% year-on-year, in 578 transactions. In the first half of 2021, the total capital raised by startups in Israel exceeded $12 bn – already surpassing the 2020 figure. So, 2021 is a record-breaking year for the Israeli startup ecosystem.

CISO MAG identified Elron as a key investor with $90 million in funds.

Elron is an Israeli investment company specializing in early-stage investments, focusing on building Israeli technological cyber and enterprise software companies. It provides direct capital and assistance to startups from their early stage in accelerating team building and accelerating product-market fit.

With a proven track record of investments and M&As worldwide, Elron has spearheaded exits valued at over $1.6 billion over the past decade and manages assets exceeding $300 million.

The companies backed by Elron include Open Legacy, Sixgill, Ironscales, BrainsGate, and CartiHeal.

Brian Pereira, Editor-in-Chief, CISO MAG, interacted with Elik Etzion, CSO, Leading Enterprise Software & Cybersecurity Investments, Elron, to discuss early-stage investments in cybersecurity startups.

Etzion is joining Elron’s management team to head cyber and software investments in the company after a comprehensive career of 25 years in key Elron investment sectors.

A retired lieutenant colonel, he began his career at the top of the tech and cyber world in the IDF, where he gained diverse technological-operational experience and knowledge over the course of 20 years in Unit 8200. In his last positions in the IDF, Etzion served as deputy commander of the cyber division, head of the R&D Department, and Head of the Cyber operations Department.

Upon his discharge from the IDF, Etzion served as CISO and member of the Technology Division Management at Bank Hapoalim Group. This is one of the largest financial institutions in Israel. He enhanced the bank’s cybersecurity posture and contributed to the cyber resilience of Israel’s banking sector, alongside being party to spearheading the bank’s digital transformation.

Etzion also served as a director in SHVA and as Chairman of the Board of Directors of Masav, specializing in payments and clearance. He brings in-depth expertise and understanding, a strategic vision of the market along, and practical experience.


About the Interviewer

Brian PereiraBrian Pereira is the Editor-in-Chief of CISO MAG. He has been writing on business technology concepts for the past 27 years and has achieved basic certifications in cloud computing (IBM) and cybersecurity (EC-Council).


More stories from Brian


Details of 1 Mn International Credit Cards Exposed on Dark Web

one million card data exposed

Cybercriminals often monitor users’ financial activities to steal information that can be used to open fake accounts. They also trade sensitive financial data such as credit/debit cards numbers, CVV, and other bank details on darknet forums. Recently, Cybersecurity researchers from Group-IB detected a post in which threat actors exposed compromised card details on various darknet forums, including crdclub and xss. Advertised as AW_cards, the post connects to a file containing over one million records of stolen credit and debit card details belonging to over 1,000 banks across 100 countries, including India, the U.S., Mexico, Australia, and Brazil.

Financial Data Exposed

According to Group-IB, the leaked database contained a password-protected zip archive text file comprising one million records of data such as card numbers, expiration dates, CVV/CVC codes, name of the cardholder, Country, State, City, address, Zip code, email IDs, and phone numbers. The database contained 810 expired cards, and 27,112 cards are set to expire in August 2021.

Multiple Cards Data Impacted

According to the research findings, over 200,000 (22%) compromised cards were belonged to the Indian banks, followed by Mexico (9%), the U.S. (9%), and Australia (8%). Nearly 77% of the cards in the database were debit cards, and 23% were credit cards. Cards from multiple payment system services were exposed in the incident, including Visa (48%), Mastercard (47%), RuPay (4%), and American Express (1%).

Advertising New Carding Forum

Researchers claimed that the attackers were trying to advertise their newly established carding forum All World Cards, which provides services like trading stolen card details, identity theft, and currency counterfeiting.

“The alleged owners of the card shop had launched a massive promo campaign in the underground to advertise their new platform, which, in addition to a huge database giveaway, included a writing contest for other cybercriminals with a cash prize of USD 15,000. This post analyzes the latest one million stolen bank card record database as well as the short history of the All World Cards card shop and the activity of its alleged owners who are most likely not the newbies of the carding business,” Group-IB researchers said.

Related Story:

Conti Ransomware Crook Leaks the Group’s Hacking Tricks

Insider attacker leak data

Insider threats have always been a severe concern for organizations across the globe. Malicious actions of rogue employees keep critical corporate data at risk. Surprisingly, a recent event has proved that even cybercriminal groups are suffering from insider threats. According to a report from Naked Security, an anonymous hacker belonging to an infamous Conti ransomware group has leaked the group’s files on a darknet forum.

The files reportedly belong to the Russian-speaking ransomware group Conti. The threat actor who leaked the data has been an active affiliate of the Conti ransomware group. He claimed that “the boys are fed up” with how the extortion money is divided. The exposed information included instruction manuals and guidelines, written in Russian, on identifying victims to attack using Cobalt Strike. The leaked files instruct members on using Google to search for potential targets. The members are further required to find employee accounts with administrative privileges and leverage this data to install ransomware to encrypt their network systems.

Files exposed in the breach contained advice on various topics, including:

  • Dumping password hashes
  • Turning a defender off, manually
  • Installing and using Metasploit
  • Scanning networks for backup devices
  • Opening backdoors into a compromised network
  • Using popular exploits
  • Elevating privilege
  • Listing users

Weaponizing Cobalt Strike  

Cobalt Strike is threat simulation software used by security experts and penetration testers to identify the potential risk of a data breach or cyberattack. Several security experts stated that threat actors leverage the Cobalt Strike tool for cybercriminal activities.

“Cobalt Strike has become a very common second-stage payload for many malware campaigns across many malware families. Access to this powerful and highly flexible tool has been limited by the product’s developers, but leaked versions have long spread across the internet. Additionally, there are tons of tutorials, education videos, and other public documents that can help newcomers understand how to effectively use it, lowering the bar for entry in the cybercrime world,” a report from Intel 471 stated.

EC-Council Launches a Specialized Web Application Hacking and Security Certification

Albuquerque, New Mexico, August 3, 2021: EC-Council, creators of the Certified Ethical Hacker certification, have launched their latest training and certification program specifically for the extremely important area of web application and hacking. Vulnerabilities in web applications are increasingly a problem for the cybersecurity industry and the demand for highly skilled professionals in application security has skyrocketed during the unprecedented COVID-19 outbreak, with major industries relying on web applications to keep their businesses afloat. Due to how quickly apps can be developed and deployed, vulnerabilities are extremely common and apps are increasingly involved in the heart of company operations, making creating and managing apps in a secure way even more important.

To meet the need for specialized training in application security, the Web Application Hacking and Security course comes with the Break the Code Challenge, allowing participants to utilize a simulation to counter cyberattacks in real-world scenarios. Each section of the challenge becomes progressively more difficult and enables users to take multiple paths, only some of which are correct.

Talking about this program, Jay Bavisi, Global President, EC-Council, said, “Web Application Hacking and Security offers a comprehensive, lab-based, hands-on experiential training that will help individuals become well equipped for future challenges. It is no ordinary course, as it focuses on providing candidates with the ability of developing proficiency in the application of web application security best practices in a real-life, stressful scenario. It will enable working professionals to defend their organizations’ web applications from existing and emerging threats. With this course, we wish to develop truly skilled professionals that can help the web application security industry.”

The new initiative’s curriculum is aligned with industry requirements. The course comes with an online, remotely proctored, six-hour performance-based exam, which will lead to one of three possible certifications based on the proficiency of the tester. Anyone with basic working knowledge of the Linux command line and an understanding of OSE and file systems or languages like Bash or Python scripting can take the certification. The Web Application Hacking and Security program will benefit professionals who have worked or are currently working as penetration testers, ethical hackers, red team engineers, information security engineers, vulnerability managers, incident responders, as well as those with a basic framework established.

More information about the course is available here: Registration and course details


About EC-Council

EC-Council (International Council of E-Commerce Consultants) is a cybersecurity certification body that certifies professionals across the globe in various cybersecurity domains. EC-Council’s mission is to build and refine the cybersecurity profession around the world and is recognized globally for helping individuals, organizations, educators, and governments address workforce problems through the development and curation of world-class cybersecurity education programs, their corresponding certifications, and providing cybersecurity services to some of the largest businesses in the world.

Trusted by seven of the Fortune 10, 47 of the Fortune 100, the Department of Defense, Intelligence Community, NATO, and over 2000 of the best Universities, Colleges, and Training Companies, their programs have proliferated through 140+ countries and have set the bar in cybersecurity education.

Best known for the Certified Ethical Hacker program, they are dedicated to equipping over 230,000 information age soldiers with the knowledge, skills, and abilities required to fight and win against the black hat adversaries. EC-Council builds individual and team/organization cyber capabilities through the Certified Ethical Hacker Program, followed by a variety of other cyber programs including Certified Secure Computer User, Computer Hacking Forensic Investigator, Certified Security Analyst, Certified Network Defender, Certified SOC Analyst, Certified Threat Intelligence Analyst, Certified Incident Handler, as well as the Certified Chief Information Security Officer.

An ANSI 17024 accredited organization, they have also earned recognition by the DoD under Directive 8140/8570, in the UK by the GCHQ, CREST, and a variety of other authoritative bodies that influence the entire profession. Founded in 2001, EC-Council employs over 400 people worldwide with 10 global offices in the USA, UK, Malaysia, Singapore, India, and Indonesia. Its US offices are located in Albuquerque, NM, and Tampa, FL. Learn more at www.eccouncil.org

“I expect security options to evolve over time with the rollout of 5G”

5G

The potential threat posed by cyberterrorism has crippled both government and security experts. Whether it is cable news, newspapers, websites or social media, “cyberthreat” is hitting the headlines every day. One might think cyberwarfare is a relatively new issue that popped out just a few years ago. However, the armed forces and the U.S. Navy have been concerned about cyberwarfare for decades. In fact, the phrase “Cyber Pearl Harbor,” was coined by American security pundits to raise awareness about the dangers in the realm of digital space. The analogy refers to a potential cyberattack that has the devastating intensity of the 1941 Pearl Harbor attack by the Japanese Navy against the U.S. Even though more resources have been deployed to counter the sophistication of cyberthreats, we still have a long way to go for things to get better. In the present day and age, cybercrime is a grave threat to every individual and business in the world. And our best defense is to be cyber aware.

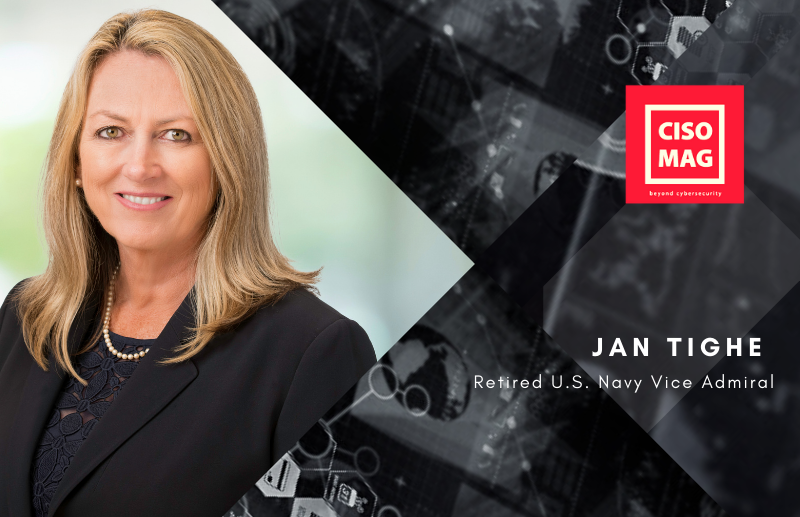
To discuss this in detail, Pooja Tikekar, Sub-Editor, CISO MAG, interviewed retired U.S. Navy Vice Admiral Jan Tighe. Tighe served as Deputy Chief of Naval Operations for Information Warfare and as the 66th Director of Naval Intelligence. Previously, she served as the Commander of U.S. Fleet Cyber Command and U.S. 10th Fleet where she was the first woman to command a numbered fleet. A career cryptologist, she served around the globe in leadership positions for both the Navy and the National Security Agency, specializing in Signals Intelligence and Cyber Operations. She earned Naval Aviation Observer Wings and supported Operation DESERT STORM in the EP-3E aircraft (electronic signals reconnaissance/ intelligence).

Tighe currently serves on the Board of Directors for Goldman Sachs, the Huntsman Corp., Progressive Insurance, IronNet Cybersecurity, the U.S. Naval Academy Foundation and serves as a Trustee for the MITRE Corp. She is a 1984 graduate of the U.S. Naval Academy and earned a doctorate in Electrical Engineering and Master of Science in Applied Mathematics from the Naval Postgraduate School, in Monterey CA. She is also a National Association of Corporate Directors (NACD) Governance Fellow.

Tighe sheds light on the mission-critical role of the Navy’s Information Warfare Community, 5G infrastructures in connecting people and machines, and the CyberQ Aptitude test for upskilling talent and leadership.

Edited excerpts of the interview follow:

You have extensive Navy experience. How do you apply your experiences and learnings from the Navy to solve cybersecurity challenges, particularly risk mitigation? And what are the best practices to keep in mind to minimize cybercrimes?

Just as military commanders develop Deliberate Campaign Plans to flesh out the details of a military response to a potential future conflict, deliberate planning for resilience and continuity of operations is an important exercise for the private sector to prepare for potential cyberattacks and minimize the risks to their companies. A military crisis is never exactly what the Deliberate Campaign Plan envisioned but serves as an excellent resource and provides response options that can be tailored to the actual crisis that you face. Private sector companies are well served by thinking through and practicing their responses to a cyberattack.

The best defenses against cybercrime, and specifically ransomware, include: having the ability to restore your system from your backups stored off-network in an acceptable amount of time-based on your risk appetite; multi-factor authentication, or continuous authentication through behavioral-based analytics; and an effective patching program to minimize vulnerabilities.

Over a decade ago, the Navy’s Information Warfare Community (IWC) was formed to effectively combat adversaries targeting U.S. national security. How is it meeting the needs of warfighting in the current Information Age, while simultaneously providing accurate information to the forces? Do you see some parallels here?

It’s important to understand that the Navy’s Information Warfare Community is all about warfighting. We may play both a lead and supporting role depending on the mission. I see parallels in the private sector as Technology and Cybersecurity teams typically see themselves supporting corporate operations, but in crises, their work may become mainline of effort to defend or restore corporate systems for business continuity.

The IWC also integrates the Navy’s information-based capabilities, including cryptology. And you started your career as a cryptologist. Since many aspects of IT security rely on encryption and cryptography, do newer methods such as the Advanced Encryption Standard (AES) promise complete concealment of data?

Complete concealment is a lofty goal. Assuming it is implemented correctly, and until quantum computing is a reality, commercially available, authenticated end-to-end encryption such as Wickr is a valuable capability in building zero trust architectures – in both the public and private sectors.

As technology evolves, so does connectivity. 5G isn’t just a buzzword anymore. 5G networks are slowly being inducted everywhere. How would it help mission-critical services in better decision-making? And would it endanger data privacy? What are the security threats you foresee from 5G?

5G is the next leap ahead in mobility architecture connecting people, machines, and sensors with much higher throughput, capacity, reliability, and lower latency than 4G offers. Specifically, 5G Enhanced Mobile Broadband is expected to be up to 100 times faster than 4G LTE. 5G will also support greater densities of Massive Machine-Type Communications, which are required for the growing number of Internet of Things (IoT) and the Industrial IoT sector.

5G Ultra-Reliable Low Latency Communications underpin mission-critical services for autonomous vehicles, factory automation, and safety/security systems where communications delays are not an option. Reducing data latency is a critical element in control systems where multiple sensors feed into automated “decisionmaking” for systems like the self-driving car, the highly automated factory floor, military unmanned vehicles, and cyber defense. The more reliable and less latent the sensor data, the more autonomously the machines can operate, collaborate, and complete human intended missions or outcomes with less hands-on human intervention.

Self-driving cars will be much safer than a car with a human at the wheel. Increasing the automation in factories will be more efficient and effective. 5G could also enable more computing power and collaboration at the edge in military unmanned vehicles, which could make them more autonomous, effective, and/or lethal depending upon the mission.

I expect security options to evolve with the rollout of 5G. Clearly, there is a risk that if global 5G infrastructure is overwhelmingly underpinned by Chinese-provided technologies (namely Huawei and ZTE), it can then be used to support Chinese state-sponsored malicious cyber operations, including espionage, IP theft, disruption of critical services and infrastructure, and (increasingly) influence operations. We need to assure global 5G connectivity to (at least) our closest allies with trusted 5G infrastructure and account for the fact that some of the global 5G infrastructures will be untrustworthy.

Since the pandemic took over the world, cyberattacks grew more sophisticated and increased in volume. And the SolarWinds Hack is an indisputable example. State actors breached both tech bigwigs like Microsoft as well as the U.S. Treasury and the Dept. of Homeland Security. SolarWinds garnered attention because it shed light on the need for best security practices within the government and for the integration between the government and the private sector. What is your take on it?

We need to stop trying to defend ourselves in our individual silos and find a way to create a collective defense, which can start in individual sectors, (e.g. energy, finance, manufacturing), then expand across sectors, and optimally to the public sector. If you can detect anomalous behavior (e.g. IronNet’s IronDefense) in your network traffic, share and correlate those alerts across different organizations (e.g. IronDome), you can accelerate the identification of malicious activity by the SOC and enable defensive actions.

In this scenario, everybody benefits from the investigation, analysis, and result sharing by a single company’s security team. If we were all working together to eliminate false positives and to identify the most dangerous threats, we could see a dramatic impact on our ability to protect against attacks. SolarWinds is a prime example. If we had a collective defense in place, it may have helped analysts who did not see the comprehensive threat. Correlating the same analogous activity across multiple networks could have alerted analysts earlier to the threat. We really need to get after a collective defense and stop fighting alone in our individual silos.

The shortage of cybersecurity talent is key issue today. Recently, EC-Council, along with the University of Maryland’s Applied Research Lab for Intelligence and Security, and Haystack Solutions collaborated to launch CyberQ Aptitude to help uncover aptitude for cybersecurity regardless of background. This testing is also in use by the U.S. Intelligence Community and the DoD. Do you think testing of this kind would help organizations mitigate talent shortages, or even form better teams based on their cognitive abilities?

Cognitive and aptitude testing has helped revolutionize talent pipelines for some fields that have the most demanding mental requirements. CyberQ Aptitude is the cyber equivalent successor to the military’s Defense Language Aptitude Battery (DLAB), which has significantly improved the language training success rates from less than 25% to greater than 75%. Some of the scientists behind the updated DLAB created CyberQ aptitude to allow us to build our cyber warriors, while shaving hundreds of billions from the required investment.

CyberQ

CyberQ Aptitude will give managers the tools to build teams that align with organizational needs. This kind of alignment will dramatically improve retention because people will be supporting problems that most appeal to their natural cognitive wiring. This will also give managers an ability to do succession planning, aligning junior team members with the same cognitive fingerprint as their senior, cyber rockstars.

CyberQ Aptitude will change upskilling programs from a form of corporate gambling to focused talent development. The upskilling leadership will be able to lay out a training program with high confidence that learners can pick up the material and generate the required cyber effects.

Do you also think the CyberQ Aptitude test will help organizations broaden the recruitment and retention horizon?

Neither the private sector nor most government agencies have sufficient talent pipelines to support sustainable talent acquisition plans. CyberQ Aptitude offers the way to find significant numbers of future cyber geniuses in places we haven’t looked. We can find the marginalized, underrepresented raw talent that never would have considered cyber and attract them to global, complex problems that have urgent societal impact. This can help solve the talent shortage facing the public and private sectors while mitigating some of the hiring risks. CyberQ Aptitude will give the training leaders confidence that the candidates will be able to execute the cyber mission, after having mastered the course material. CyberQ Aptitude has repeatedly shown its ability to identify nontechnical, high-potential talent that excels in cyber training.

Coming back to cryptology, its role and discipline have evolved over the years. Do you think it is one of the critical cyber skills to learn in these pressing times, when confidential data is vulnerable at all times, whether stored or in transit?

Cryptology includes information security, which is clearly a critical skill. Whether you are putting protections on the front end or you’re actively mitigating threats that are hitting your front door. Honing your analytical skills in your intellectual curiosity is probably the most foundational thing that you can do in this area.

Lastly, is there anything you would like to add?

In general, I think it’s important to recognize the risk to our operational technologies that can be found in industrial control systems and manufacturing factories. A key lesson from the Colonial Pipeline attack is that if you operate machinery and industrial control systems, you need to be certain that those systems are not connected to your IT systems or directly accessible from the open internet. Typically, operational technologies are not easily restored like an information technology system and the effects of having ransomware infect and not just encrypt, but probably destroy the operational technologies would be a much longer recovery process than what we saw in Colonial Pipeline, where they shut down the pipeline as a preventative measure, even though they believed there was no connectivity between their IT and their OT systems.

If we step back and examine the big picture, talent is at the heart of our ability to protect and defend our systems. We have to engage our primary and secondary educational systems to prepare our future cyber workforce. That workforce needs to be as diverse as our population and we are a long, long way from that goal. It is imperative that we identify programs and resources that can support, encourage, and empower the young people of this country to understand what cybersecurity truly means and how they can be a part of it.

This interview first appeared in the July 2021 issue of CISO MAG.


About the Author

Pooja Tikekar is the Sub Editor at CISO MAG, primarily responsible for quality control. She also presents C-suite interviews and writes news features on cybersecurity trends.

More from the author.


How to Ensure Data Management Excellence

data management excellence

In response to high-profile data breaches, staggering fines, and rapidly evolving privacy and data requirements, CIOs and CISOs are facing a critical mandate: to enable their investigative teams with the tools and solutions needed to quickly, easily and securely investigate external cyberthreats, internal security lapses and compliance practices.

 SPONSORED CONTENT 

Recent surveys of C-level executives and CIOs reveal that Ensuring Compliance (52%), Data Security (52%), and Incident Response (43%) are top priorities.

This responsibility is extraordinarily challenging given that:

  • Investigations are multiplying and diversifying.
  • Litigation data is becoming almost exclusively digital.
  • Global trends like bring your own device (BYOD), the internet of things (IoT), working remotely, proliferating privacy regulations and cloud computing are complicating organizations’ ability to conduct effective investigations.
  • Investigations are becoming more collaborative within the enterprise, involving nonlegal professionals that require real-time, remote access to forensic technologies.
  • Existing data management and investigative capabilities can’t keep up with the explosion of data across a growing range of devices, platforms and systems.

In this guide, we’ll cover how CIO, CISO, and CLO priorities are converging, and how to better work together to create outcomes that:

  • Help ensure compliance with complex regulations
  • Place data management as a critical business initiative
  • Cover gaps in incident response processes

The guide is designed to walk CIOs, CISOs and their technical teams through the trends, challenges and solutions that may impact their technology planning including:

  • Global developments and security issues affecting compliance, investigative and e-discovery Processes.
  • Market observations and predictions demonstrating the increasing urgency for and move towards achieving excellence in incident response inside corporations.
  • Strategies for increasing collaboration and efficiency, while reducing waste, risks and costs.
  • Category-specific solution checklists and questions to leverage as they chart their technology maps and evaluate different types of solutions.
  • Exterro’s point of view on why these leaders should take a holistic approach to manage legal governance, risk and compliance challenges.
Learn all about this and much more, by downloading the Whitepaper.