Home Blog Page 186

Google Ads Gear-up to Implement SCC Post EU-U.S. Privacy Shield Invalidation

Google Ads, Google LLC, Google Ads honors EU-U.S. Privacy Shield Invalidation

On July 16, 2020, the European Court of Justice (ECJ) annulled the “EU-U.S. Privacy Shield” framework, which was accepted by the European Union (EU) four years back on July 12, 2016, and came into effect since August 01, of the same year. The ECJ cited gaps in the data security measures of the U.S. Surveillance Law and regarded them as “inadequate” to protect the data privacy rights of the EU citizens as defined under the General Data Protection Regulation (GDPR) formulated in 2018. Abiding by the judgment, Google, a tech giant that harnesses and uses personal data for certain features and apps, is all set to move towards Standard Contractual Clauses (SCCs) for transfers of online advertising data out of Europe Economic Area, Switzerland and the U.K.

By Mihir Bagwe, Tech Writer, CISO MAG

  Key Highlights  

  • EU-U.S. Privacy Shield was invalidated by ECJ on July 16, 2020.
  • ECJ asked businesses to follow the Standard Contractual Clauses (SCC) provision.
  • Google has already adapted the SCC for addressing its data transfer requirements of Google Cloud and G Suite products.
  • It is now all set to move Google Ads to SCC from August 12, 2020.
  • As a result, it will be updating their existing Google Ads Data Processing Terms, Google Ads Controller-Controller Data Protection Terms and Google Measurement Controller-Controller Data Protection Terms.
  • The invalidation is proving costly and time consuming for many businesses.

Google Moves to Standard Contractual Clauses (SCC)

This is not the first instance of scrapping a data transfer framework between the transatlantic. In 2015, a similar framework known as Safe Harbor was taken down by the ECJ and thus, companies were asked to use the SCC to authorize the transfer of data across the continents. Similarly, the ECJ has again asked companies to revert to the SCCs and data regulators to keep a close eye on the GDPR compliance of the U.S. companies.

Adhering to this, Google has already implemented the SCC to address EU data-transfer requirements for Google Cloud Platform and G Suite. However, one of its most aggressively profit-making products – Google Ads – was still not aboard this ship. But this is all set to change on August 12, 2020. Google Ads has sent an intimation to all its users stating that it honors the ECJ’s ruling of invalidating the EU-U.S. Privacy Shield and is moving towards the SCC.
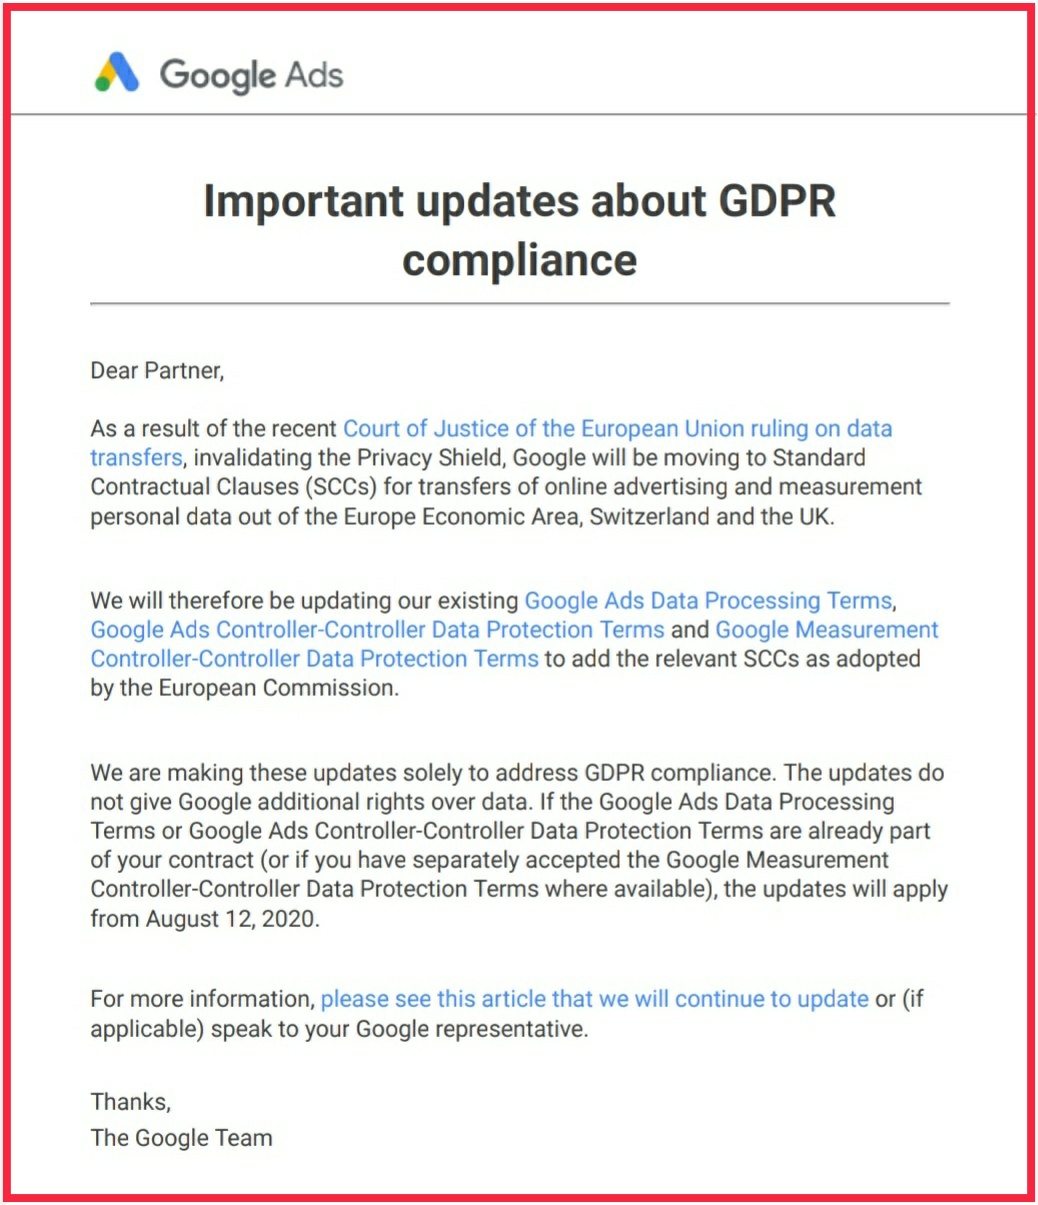
Google Ads GDPR Compliance Notice
Google’s Mail

The effect of these changes will be seen in the existing Google Ads Data Processing Terms, Google Ads Controller-Controller Data Protection Terms and Google Measurement Controller-Controller Data Protection Terms. Google was also quick to clear the air that they are implementing the SCC only to fulfill the GDPR compliance and that these changes will not give them any additional data rights over its users.

Effects of EU-U.S. Privacy Shield Invalidation

ECJ’s ruling came as a shock to the U.S. Department of Commerce. However, it is optimistic and looking forward to improving the personal data privacy measures of the Privacy Shield. They strongly feel that the framework can be reestablished in the coming years for the ease of businesses between the two continents.

In the meanwhile, the existing members of the shield, of which 70% are small and medium-sized enterprises (SMEs), are facing an uphill task reverting to the SCCs in the wake of the ongoing pandemic. Many businesses have contracted resources and are bootstrapped on the financial front.  The legal teams of software companies that solely relied on the Privacy Shield are scampering to update their terms and conditions and issuing updated versions of existing contracts if they wish to continue processing EU data. Companies are now completely dependent on their lawyers for creating thousands of new contracts, which also need to be signed manually as per SCCs requirement. Hence, this shift to Standard Contractual Clauses is not only proving to be costly but also a time-consuming affair.

About the Author

CISO MAG Writer - Mihir Bagwe
Mihir Bagwe is a Tech Writer and part of the editorial team at CISO MAG. He writes news features, technical blogs, and conducts interviews on latest cybersecurity technologies and trends.


Other Posts from the Author:

Online Shopping or Scam? FBI Alerts Consumers About Fraudulent E-Commerce Schemes

online shopping, International Fraud Awareness Week

The FBI warned consumers to be vigilant while shopping online, as cybercriminals are targeting e-commerce shoppers to steal sensitive information. In a security alert, the FBI stated that it has seen a spike in online shopping scams. Attackers are targeting shoppers by redirecting them to fraudulent websites via social media platforms and search engines.

Online Shopping or Monetary Loss?

According to the Federal Trade Commission (FTC), the number of complaints on online shopping scams has grown every year and victims have lost a total of $420 million dollars since 2015. The commission received more than 86,000 complaints related to online shopping issues in 2019.

The FBI received several complaints from victims stating they have not received items they purchased and were led to fraudulent websites via ads on social media platforms or while searching for specific items on online shopping pages. Complaints reported to the FBI include:

  • Disposable face masks shipped from China were received regardless of what was ordered.
  • The payment was made using an online money transfer service.
  • The retail websites provided valid but unassociated U.S. addresses and telephone numbers under a ‘Contact Us’ link, misleading victims to believe the retailer was located within the U.S.
  • Many of the websites used content copied from legitimate sites; in addition, the same unassociated addresses and telephone numbers were listed for multiple retailers.

Some victims who complained to the vendor about their shipments were offered partial reimbursement and told to keep the face masks as compensation. Others were told to return the items to China in order to be reimbursed, which would result in the victim paying high postage fees, or agreeing to a partial reimbursement of the product ordered without returning the items received. All attempts made by the victims to be fully reimbursed, or receive the actual items ordered, were unsuccessful.

– FBI 

How Attackers Target Online Shoppers

The FBI listed the indicators of the fake websites that attackers used to target online shoppers:

  • Instead of .com, the fraudulent websites used the Internet top-level domains (TLD) “.club” and “.top.”
  • Websites offered merchandise at significantly discounted prices.
  • Uniform Resource Locator (URL) or web addresses were registered recently (within the last six months).
  • Websites used content copied from legitimate sites and often shared the same contact information.
  • The websites were advertised on social media.
  • Criminal actors utilized a private domain registration service to avoid personal information being published in the WHOIS Public Internet Directory.

How to Spot/Avoid a Fraudulent Shopping Site

Based on victims’ complaints, the FBI said that fake shopping sites have multiple things in common and can be easily detected with simple security checks, including:

  • Do your homework on the retailer to ensure it is legitimate.
  • Check the WHOIS Public Internet Directory for the retailer’s domain registration information.
  • Check other websites regarding the company for reviews and complaints.
  • Check the contact details of the website on the “Contact Us” page, specifically the address, email, and phone number, to confirm whether the retailer is legitimate.
  • Be wary of online retailers offering goods at significantly discounted prices.
  • Be wary of online retailers who use a free email service instead of a company email address.
  • Do not judge a company by their website; flashy websites can be set up and taken down quickly.

The FBI recommended online shoppers to be alert about unreliable offers/low prices on an online store, when compared to other online stores.


Operation North Star: A New Phishing Campaign Disguised as Job Posting

Doxing attacks

McAfee’s advanced threat research team discovered a new phishing campaign linked to the North Korean hackers targeting the U.S. defense and aerospace sectors with fake job opportunities. The campaign, which is dubbed as “Operation North Star,” began in late March and lasted till May 2020, McAfee said in a security alert.

Operation North Star’s Modus Operandi

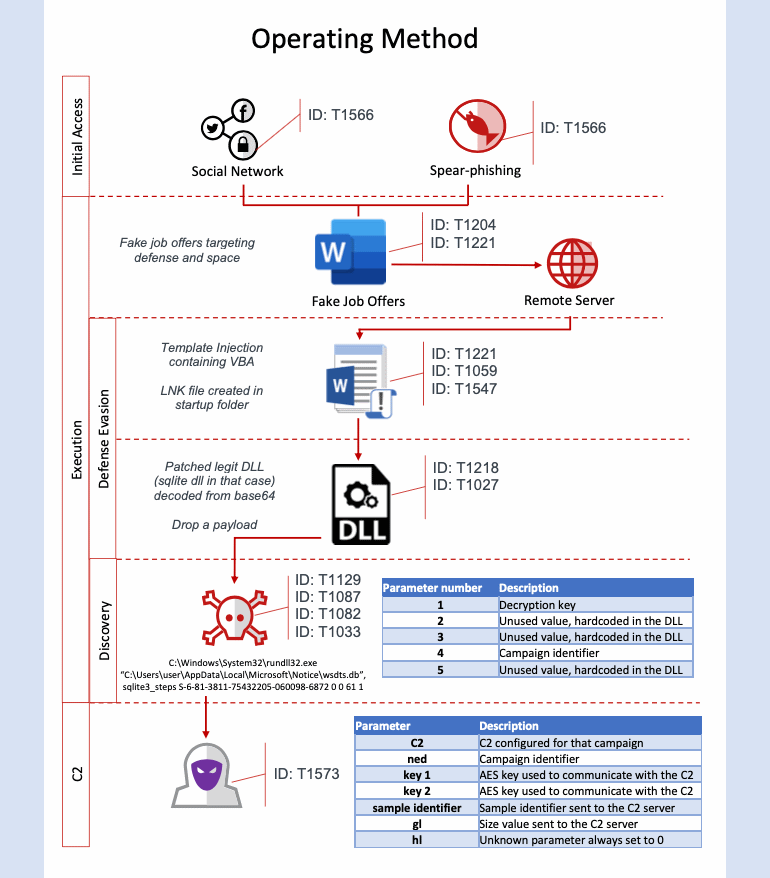
The hackers impersonated recruiters and  sent malicious emails with Microsoft Office templates to high-profile employees  with an aim of injecting malware in the targeted devices to obtain  network systems access and steal data. The Microsoft Office templates were hosted on a command and control server and the download link was embedded in the first stage document. The malicious documents contained job postings  from leading U.S. defense  contractors to lure victims into opening them and ultimately execute the payload.

The hackers coaxed the victims to recruit for leading U.S. defense and aerospace programs and groups including:

  • F-22 Fighter Jet Program
  • Defense, Space and Security (DSS)
  • Photovoltaics for space solar cells
  • Aeronautics Integrated Fighter Group
  • Military aircraft modernization programs

McAfee researchers also observed fake job offers pertaining to sectors outside of defense and aerospace, such as a finance position for a leading animation studio.

Attack Overview

Image Source: McAfee

The researchers also stated that the attack techniques or TTPs (Techniques, Tactics, and Procedures) of Operation North Star are similar to previously discovered campaigns associated with “Hidden Cobra,” a North Korean state-sponsored hacking group which was active from 2017 to 2019.

Hidden Cobra group consists of multiple threat actor groups like Lazarus, Kimsuky, KONNI, and APT37, which target organizations around the world by gathering data around military technologies to cryptocurrency theft from leading exchanges.

“Our analysis indicates that one of the purposes of the activity in 2020 was to install data gathering implants on victims’ machines. These DLL implants were intended to gather basic information from the victims’ machines with the purpose of victim identification. The data collected from the target machine could be useful in classifying the value of the target. McAfee ATR noticed several different types of implants were used by the adversary in the 2020 campaigns,” the researchers said in a report.

“The TTPs of this campaign align with those of previous Hidden Cobra operations from 2017 using the same defense contractors as lures. The 2017 campaign also utilized malicious Microsoft Word documents containing job postings relating to certain technologies such as job descriptions for engineering and project management positions involving aerospace and military surveillance programs. These job descriptions are legitimate and taken directly from the defense contractor’s website. The exploitation method used in this campaign relies upon a remote Office template injection method, a technique that we have seen state actors use recently,” the report added.


Securing the Hybrid Workforce Begins with Three Crucial Steps

hybrid workforce

The global shift to a remote workforce has redefined the way organizations structure their business models. As executives reestablish work policies to accommodate remote employees well beyond the initially anticipated duration, a new era of work will emerge: the hybrid workforce, one more largely split between office and remote environments. While this transition brings a wave of opportunity for organizations and employees, it also opens new doors for bad actors to capitalize on strained IT departments who have taken on additional responsibility to ensure sensitive data remains secure, whether on or off the corporate network.

By Rick Vanover, Senior Director of Product Strategy for Veeam Software

While threats to company data range in attack method, ransomware continues to be the most prominent risk known to organizations worldwide, with a 41% increase in 2019 alone. It’s important that companies focus on acknowledging this threat and deploying strategies to prepare, defend and repair incidents, before adapting to a hybrid workforce model. This process will prevent organizations from falling victim to attacks where data loss or ransom payment are the only unfortunate options. To win the war on ransomware, organizations should incorporate a plan for IT organizations that ensures they have the resilience needed to overcome any attack. Let’s explore three crucial steps for ransomware resilience in more detail.

1. Focus on education first, avoid reactive approaches to threats later

Education – beginning after threat actors are identified – should be the first step taken on the path towards resilience. To avoid being caught in a reactive position, should a ransomware incident arise, it’s important to understand the three main mechanisms for entry: internet-connected RDP or other remote access, phishing attacks and software vulnerabilities. Once organizations know where the threats lie, they can tactfully approach training with strategies to refine IT and user security, putting additional preparation tactics in place. Identifying the top three mechanisms can help IT administration isolate RDP servers with backup components, integrate tools to assess the threat of phishing attacks to help spot and respond correctly, and inform users on recurrent updates to critical categories of IT assets, such as operating systems, applications, databases and device firmware.

Additionally, preparing how to use the ransomware tools in place will help IT organizations familiarize themselves with different restore scenarios. Whether it be a secure restore process that will abort when malware is detected or software that can detect ransomware ahead of restoring a system, the ability to perform different restore scenarios will become invaluable to organizations. When an attack does happen, they will recognize, understand and have confidence in the process of working towards recovery. By taking the education aspect of these steps seriously, organizations can decrease the ransomware risks, costs and pressure of dealing with a ransomware incident unprepared.

2. Implement backup solutions that maintain business continuity

An important part of ransomware resiliency is the implementation of backup infrastructure to create and maintain strong business continuity. Organizations need to have a reliable system in place that protects their servers and keeps them from ever having to pay to get their data back. Consider keeping the backup server isolated from the internet and limit shared accounts that grant access to all users. Instead, assign specific tasks within the server that are relevant for users and require two-factor authentication for remote desktop access. Additionally, backups with an air-gapped, offline or immutable copy of data paired with the 3-2-1 rule will provide one of the most critical defenses against ransomware, insider threats and accidental deletion.

Furthermore, detecting a ransomware threat as early as possible gives IT organizations a significant advantage. This requires tools in place to flag possible threat activity. For endpoint devices displaced remotely, backup repositories that are set up to identify risks will give IT further insight into an incredible surface area to analyze for potential threat introduction. If implementations don’t prohibit attacks, another viable option is encrypting backups wherever possible for an additional layer of protection – threat actors charging ransom to prevent leaking data do not want to have to decrypt it. When it comes to a ransomware incident, there isn’t one single way to recover, but there are many options aside from these that organizations can take. The important thing to remember is that resiliency will be predicated on how backup solutions are implemented, the behavior of threat and the course of remediation. Take time to research the options available and ensure that solutions are implemented to protect your company.

3. Prepare to remediate an incident in advance

Even when there are steps in place that leverage education and implementation techniques to combat ransomware before an attack hits, organizations should still be prepared to remediate a threat if introduced. Layers of defense against attacks are invaluable, but organizations need to also map out specifically what to do when a threat is discovered. Should a ransomware incident happen, organizations need to have support in place to guide the restore process so that backups aren’t put at risk. Communication is key, having a list of security, incident response, and identity management contacts in place if needed – inside the organization or externally – will help ease the process towards remediation.

Next, have a pre-approved chain of decision makers in place. When it comes time to make decisions, like whether to restore or to fail over company data in an event of an attack, organizations should know who to turn to for decision authority. If conditions are ready to restore, IT should be familiar with recovery options based on the ransomware situation. Implement additional checks for safety before putting systems on the network again – like an antivirus scan before restoration completes – and ensure the right process is underway. Once the process is complete, implement a sweeping forced change of passwords to reduce the threat resurfacing.

The threat that ransomware poses to organizations both large and small is real. While no one can predict when or how an attack will happen, IT organizations that have a strong, multi-layered defense and strategy in place have a greater chance for recovery. With the right preparation, the steps outlined here can increase any organization’s resiliency – whether in office, remote or a combination of the two – against a ransomware incident and avoid data loss, financial loss, business reputation damage or more.

About the Author

Rick VanoverRick Vanover (Cisco Champion, VMware vExpert) is a Senior Director of Product Strategy for Veeam Software based in Columbus, Ohio. Vanover’s experience includes system administration and IT management; with virtualization, cloud and storage technologies being the central theme of his career recently.
Disclaimer

CISO MAG did not evaluate/test the products mentioned in this article, nor does it endorse any of the claims made by the writer. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same. CISO MAG does not guarantee the satisfactory performance of the products mentioned in this article.

3 in 4 Security Leaders See Cybersecurity as a Top Priority in 2020

Harness Your System, Free Decryptor, federal government, cybersecurity

CrowdStrike Inc., the developer of cloud-delivered endpoint protection solutions, stated that organizations are seeing cybersecurity as a top priority in 2020.

In its recent survey, “2020 CrowdStrike Asia Pacific and Japan (APJ) State of Cybersecurity Report” the company stated that 74% of respondents believe there should be more investment in cybersecurity to enhance organizations’ security posture. Nearly, 44% of security leaders said the pandemic accelerated their move to cloud solutions, while 82% said COVID-19 changed the way they interact or deliver products and services to customers. CrowdStrike also found a jump in cybercrimes by over 330% since the start of the year, as compared to cybercrimes in 2019.

Other notable findings include:

  • Though organizations have changed their IT environments to accommodate remote workers, 39% of respondents have not changed their security programs because of COVID-19, potentially exposing their organizations to cyber risks from new and more sophisticated attacks.
  • Employee education and communication are key to a successful cybersecurity strategy, yet 20% of business leaders do not know what to do in the event of a data breach, and 36% of respondents have not received communications about COVID-19 themed malware. Moving forward, 76% of APJ business leaders say they plan on additional security training in the future.
  • As we look to the new normal, 67% of business leaders believe that their organizations should invest more in building a remote work environment.
  • The top cybersecurity challenges expected in the next 18 months include remote workforce (54%), new regulation (49%) and costs of compliance (48%), with limited budgets (47%) and additional training (41%) ranking not far behind.

Andrew Littleproud, Vice President, APJ at CrowdStrike, said, “The speed and size of change to a remote workforce led to some inevitable gaps, particularly in the cybersecurity of organizations. Business leaders understand these gaps and expect to address them in the recovery, going beyond good enough’ security measures to ensure their employees remain secure against sophisticated threat activity regardless of where they are located. In the new business normal, it will be vital to implement solutions that can be quickly deployed at scale to detect new threats, adhere to new regulations, and leverage the cloud so they can be easily managed remotely.”

The survey findings are based on the responses from 2,017 business leaders in Australia, New Zealand, India, Singapore, Philippines, Thailand, Malaysia, Indonesia, Hong Kong, and Japan.


Meet the Teen “Mastermind” Behind the Greatest Twitter Hack

Twitter hack

Twitter and Twitterati went berserk on July 15, 2020, when a high-profile hack compromised nearly 130 Twitter accounts including verified accounts of known personalities like Jeff Bezos, Bill Gates, Elon Musk, Barack Obama, Joe Biden, and corporate accounts of Apple, Uber and many more. It was a one of a kind hack, and ever since, it has been termed as “The Greatest Twitter Hack,” simply because multiple verified accounts were hacked simultaneously for scamming people.

The FBI Crackdown

The cybercriminals quite literally basked in the glory of their achievements as they successfully collected more than $118,000 by scamming people. However, their happiness was cut short by the Federal Bureau of Investigation (FBI). With regard to the case, the FBI has now arrested a 17-year-old, Graham Ivan Clark, a resident of Tampa, Florida, and pressed 30 counts of felony charges against him for perpetrating the Twitter hack. The FBI also found out that there were two more people, 19-year-old Mason John Sheppard from the U.K. and 22-year-old Nima Fazeli from Orlando, Florida, who acted as accomplices to Clark.

This is not a game… these are serious crimes with serious consequences.

– Andrew Warren, Florida State Attorney

Things We Now Know

  • FBI has arrested Graham Ivan Clark and pressed 30 charges of Felony against him including organized fraud, communications fraud, identity theft, and hacking.
  • Clark had two more accomplices, a 19-year-old Mason John Sheppard from the U.K. and 22-year-old Nima Fazeli from Orlando.
  • The hack reportedly began on May 3, 2020, when Clark, aka Kirk#5270 (Discord username), through social engineering means convinced a Twitter employee that he was a colleague of his and required credentials to access the internal systems of Twitter for certain work.
  • Clark impersonated himself later as a Twitter employee and approached two other hackers (Fazeli aka “Rolex#037” and Sheppard aka “ever so anxious#0001” – both are Discord usernames).
  • He modified the settings of an account owned by Rolex#037 as a proof-of-concept and sold him access to the Twitter account @foreign.
  • Similarly, Clark also sold Sheppard access to multiple Twitter accounts, such as @xx, @dark, @vampire, @obinna, and @drug
  • The FBI tracked the trio from various sources.
    • It used data shared on social media and news outlets to get chat logs and user details from Discord.
    • They further obtained data from Coinbase about the Bitcoin addresses involved in the hacks.
    • After correlating the data, they found that unknowingly some of the culprits had used their original driving licenses and email IDs to register with cryptocurrency exchanges for withdrawing the scammed money.

“This is not an ordinary 17-year-old”

Andrew Warren, Florida state attorney, in a press conference said, “This is not an ordinary 17-year-old. This could have had a massive, massive amount of money stolen from people, it could have destabilized financial markets within America and across the globe; because he had access to powerful politicians’ Twitter accounts, he could have undermined politics as well as international diplomacy. This is not a game… these are serious crimes with serious consequences.”

According to the officials, Clark is charged as an adult in the State of Florida and shall get sentenced accordingly, if found guilty in any of his 30 charges. Similarly, Fazeli faces a maximum of five years in prison and a $250,000 fine, if found guilty for one count of computer intrusion. However, Sheppard is being charged on three counts, which include computer intrusion, wire fraud conspiracy, and money laundering conspiracy. The maximum for these crimes is a 20-year in a prison sentence and a $250,000 fine.

That Refurbished Smartphone Might be Unsafe to Use!

That Refurbished Smartphone Might be Unsafe to Use!

A new investigation from the consumer advocacy organization Which? revealed that 3 in 10 second-hand smartphones are vulnerable to being hacked as they are no longer supported by security updates from the manufacturer, leaving the future owners open to potential cyber risks. If your phone is not running on the latest version of its software, your device security and data privacy may be at risk, Which? said.

The investigation centered around three pre-owned mobile phone retailers, SmartFoneStore, Music Magpie, and CeX. Almost a third (31%) of the phones at CeX could be vulnerable. A fifth (20%) of the phone models found on Music Magpie and one in six (17%) on SmartFoneStore are also exposed to cyberthreats.

According to Which?, some of the phones being resold without security updates include Apple iPhone 5, Huawei P10, Google Pixel XL, Samsung A8 Plus, and the Samsung Galaxy S7. In the wake of the Which? investigation, Music Magpie has removed the unsupported devices from its platform. SmartFoneStore also issued an update, adding a warning on unsupported devices so consumers are aware before they buy them.

Other findings from the investigation include:

  • Around 62% said they think a mobile phone is broken down for parts when it is sent for recycling, but Which? investigation found most phones are actually resold.
  • Music Magpie told Which? it refurbishes 95% of the products it receives from consumers, all of which are resold in the U.K. It sells more than 250,000 phones a year.
  • CeX said the majority of phones are resold in the U.K. – it sold approximately one million phones in 2019.
  • SmartFoneStore, which sources phones from businesses and retailers, told Which? it sells around 2,000 per month.

“Out-of-support devices might not immediately have problems, but without security updates, the risk to the user of being hacked is increased. The lack of robust, sustainable solutions for the disposal of mobile phones is an ongoing concern. With effective options in place to resell pre-owned devices, the potential is there to prolong their lifespans – but until manufacturers offer complete transparency about how long devices will be supported, and those offering only a couple of years of support do better, it is more difficult to take advantage of these services without putting consumers at risk,” Which? said in its analysis.

Kate Bevan, Which? Computing editor, said, “Keeping mobile phones in circulation for longer is better for the environment but it shouldn’t come at the cost of customer security. Unless manufacturers become more transparent, and those offering vital updates for only a couple of years do better, there is a risk that second-hand phones will be vulnerable to hackers or end up dumped in a landfill site. If your mobile phone is no longer receiving security updates you should consider upgrading as soon as possible. While you continue to use an out-of-support device, you must take steps to mitigate the risks – including using mobile antivirus software, managing app permissions and only downloading from official stores.”


Fake or Real? How to Spot Malicious or Fake Apps

Mobile Apps Security, mobile apps

Software applications are no more limited to smartphones; the app ecosystem has expanded from mobiles to watches, laptops, and television. Whether it is Google Play Store or Apple’s App Store, there are multiple apps available for  free download. However, most of these free apps come with several security risks.

By Rudra Srinivas, Feature Writer, CISO MAG

Even with multiple security checks and scans in place, several counterfeit and malicious apps remain undetected and make their way to the Play Store. In this article we will show you how to spot these malicious apps.

The Malicious Intent

Threat actors use imposter apps to perform various criminal activities like spreading malware, installing adware, stalking users’ movements, or accessing personal information. Recently, digital security solutions provider Avast reported a 51% increase in the use of spying and stalking apps globally between March and June 2020, compared to the preceding months, January and February 2020.The FBI issued a warning about threat actors targeting users with fake banking apps to compromise bank accounts. In an official statement, the FBI stated that online and mobile banking apps witnessed a 50% surge in usage since the beginning of 2020.

How to Spot Fake Applications

We often find multiple apps on the Play Store with the same name. An alert user can detect these imposter apps with proper security checks before downloading these. Securing your devices is essential when it comes to protecting your data against malicious apps. Here are some ways to detect fake apps:

1. Check for Discrepancies in the App Icon

Threat actors always use the legitimate app icon to trick users into downloading them. Whenever we search for a particular app on the Play Store,  a list of the similar names and app icons appear, which also includes the counterfeit apps. Try to differentiate fake and legitimate apps by observing the app’s icon. You will certainly find some inconsistencies between fake and genuine apps.

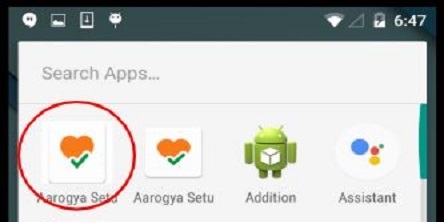
Recently, SonicWall researchers discovered several fake apps in India, which are named after the legitimate Aarogya Setu app, India’s official COVID-19 app. It is observed that the malware operators used the same code for fake apps, by re-branding the icon and application name. The researchers stated that the copy is imperfect, the icon appears stretched and can be identified by comparing it with the legitimate app (as shown in the image below).

Image Source: SonicWall

2. Observe App and its Developer’s Name

Though multiple apps have same name and icon, they are unlikely to have the same developer’s name. Fake apps usually have spelling mistakes in the app’s name or in its description.  Double-check the app’s name and its developer’s name, and make sure they are spelled correctly.

3. Watch the Download Count

Popular apps like WhatsApp and Facebook will have a higher download count. Security experts stated that if an app has 5,000 or less downloads, it is perhaps the wrong listing and maybe it is a fake one. Look for the download numbers before downloading a popular app.

4. Screenshots and Reviews

Counterfeit apps have misspelled words and strange photos in screenshots. Reading app reviews will give you a fair idea of what users think about it. Usually, fake apps have fake reviews, but you may find legitimate reviews from users who already downloaded the app and realized it was fake. A quick look at the screenshots and reviews will help you find the legitimacy of the app.

5. App Publish/Update Date and Permissions

A new app from a popular company will have a “recent publish date” and for old apps have “updated on date”. Imposter apps often have recent publish date. Look at the permissions that the app is asking for while installing. For instance, a third-party messaging app will ask for permission to access a user’s phone book and contacts, but if it is asking unwanted permissions like access to the audio, camera, or more, you have reason to be suspicious.

How to Delete Fake Apps

If a user deletes a fake app from the device by simple uninstalling it (i.e. long pressing the icon and selecting ‘Uninstall’), only the genuine app is removed, while the malicious app would still be available in the background of the device. The only way to remove the malicious apps is to remove it from Settings > apps > uninstall. After removing the malicious app, restart your phone, so all traces of it are completely removed from memory.

Don’t Just Remove, Report!

Finding a fake app or deleting it after knowing about it is not enough. You need to report it to Google  so that it is removed permanently from the Play Store. Google delists thousands of malicious/fake apps from its Store every year. If you find a fake app, report it by selecting the “Flag as Inappropriate” option so that Google can review and remove it from the Play Store.

Conclusion

Be responsible and prevent others from suffering the consequences of the malicious app that you just experienced. And do stay alert when installing new apps.
When downloading an app from the Google Play store, look for the Verified by Play Protect or Google Play Protect logo. That’s an assurance that the app has fulfilled Google’s rigorous internal safety standards and protocols.  But it does not necessarily mean that the app is always secure, as there have been past instances of malicious apps having earned this label only to be taken off the store later after their true intentions became known.

About the Author


Rudra Srinivas is a Feature Writer and part of the editorial team at CISO MAG. He writes news and feature stories on cybersecurity trends.


Cybersecurity Automation Defining the Future of Information Security Ecosystem

93% of Organizations Believe Human Error Cause Cloud Data Breaches

Cybercrime has gradually evolved into a thriving industry and is expected to inflict over $5 trillion worth of damages annually by 2021, making the prevention and detection of cyber vulnerabilities paramount. Persistent efforts by enterprises to combat and mitigate the risks arising out of cyberattacks have led to the convergence of AI and ML across the cybersecurity landscape, triggering the onset of automation practices. Cybersecurity automation is being hailed as the next big step in information security, attributed especially to the cumbersome endeavors required for manually managing cybersecurity policies. As multi-cloud environments push the boundaries of enterprise networks, cybersecurity automation will have an important role in preventing cybercriminals from gaining unfettered access to private data.

By Sachin Kasnale, Senior Research Analyst – Sustainable & Smart Technologies, Global Market Insights

Reports from cybersecurity experts and industry research have consistently highlighted the shortage of skilled IT security personnel. In 2019, it was estimated that over 40% of organizations lacked the required cybersecurity skills to improve their security posture. Ironically, this is also one of the biggest challenges while implementing cybersecurity automation, with only 30% of organizations featuring an in-house team capable enough to use security automation. One effective strategy for enterprises to overcome these challenges is to forgo universal automation and opt for specific requirements, which are those pain points where automation will benefit them the most. A few of such areas can be:

  • Integrating internal security data analytics with an external threat intelligence
  • Upgrading existing cybersecurity tools with automation functionalities
  • Basic remediation tasks should be automated on priority

One of the biggest potential areas of application for cybersecurity automation is vulnerability assessment. The global vulnerability assessment market is projected to exceed $10 billion by 2025, driven majorly by the need to identify, classify, and remediate vulnerabilities that attackers could exploit to access confidential data. However, as a greater number of devices are getting connected to the existing network, it becomes increasingly difficult for cybersecurity professionals to manage the network traffic while ensuring security. This is where cybersecurity automation can step in. It can effectively scan devices or apps in the existing network, detect vulnerabilities, and provide a detailed report that can be used to correct security threats proactively.

Another major trend making inroads into cybersecurity automation ecosystem is DevOps-based security automation. DevOps, which is a combination of various interrelated practices & tools to increase the speed of application development and delivery, can assist software development teams in testing the security of newly deployed code at a quicker pace compared to traditional software management processes. The newly committed code can be automatically tested for security vulnerabilities and faulty code can be instantaneously stopped from going into production. DevOps-based testing & development applications are witnessing a soaring rate of adoption, with estimates of the DevOps-based software testing industry exceeding $1.5 billion by 2025. DevOps will also provide a cultural shift of organizations with a more flexible, agile approach toward automation practices.

Cybersecurity exerts immense importance on achieving zero-day threat detection and malware protection. However, majority of enterprises are currently involved with issues, such as disparate security tools, manual management of processes, and an overwhelming amount of security data to be analyzed. It is worth noting that in 2019, enterprises in the U.S. took an average of over 200 days to detect a data breach and another 50 days to neutralize it. For every such breach that went undetected for over 100 days, the total damages inflicted were more than $8 million. This may seem as a major precursor to initiate a shift of enterprises toward cybersecurity automation. However, the implementation of AI and ML to achieve automation is still a challenging task. Enterprises must realize that implementation of cybersecurity automation will not yield them perfect results, there may also exist several false positives. Striking a balance between reducing false positives while not ignoring real threats requires large datasets and continuous training of ML models, which enterprises need to consistently upgrade and improve.

A plethora of cybersecurity tools & vendor sprawl is another intimidating issue while implementing cybersecurity automation. The complications in choosing an effective automation solution are further amplified by the prevailing trend of “best-in-breed” security strategy, where enterprises end up choosing the best possible vendor for each security requirement. While this may appear as the best go-to-strategy at the moment, its repercussions are felt later in the form of incompatibility between different solutions, lack of integration, and performance bottlenecks. The evolving cloud landscape also means that an increasing number of vendors & solutions needs to be evaluated. A few enterprises may find themselves lying on the other end of the spectrum marred by vendor lock-in issues. To address both the challenges, organizations need to embrace the open architecture culture and implement open platforms, which will offer them seamless integration with a broad gamut of third-party solutions and services.

The 10 most crucial steps while implementing a cybersecurity automation approach are:

  1. Formulating the exact requirements for automation and selecting the right tool
  2. Consistently monitoring the most vulnerable areas specific to the organization and developing automation policies around these areas
  3. Enterprises must clearly understand their capabilities and opt for automation tools that address their most crucial pain points
  4. Skills need to be upgraded. If the IT teams cannot function in sync with the evolving technology, the true value of automation cannot be realized.
  5. Security experts are a valuable resource and must only be deployed for the most important of tasks
  6. Data ingestion & analytics is a must. This data later serves as a foundation for improving automation ML models.
  7. Once enterprises get a feel of using automation, they can design their own policies & rules to achieve the required actionable intelligence
  8. Integration of ML across all threat prevention solutions
  9. Ensuring that tools and solutions are always updated and deliver high uptime
  10. Automation must not be underused or overused, and it is on the enterprises to achieve a middle ground.

About the Author

Sachin KasnaleSachin Kasnale is a Senior Research Analyst – Sustainable & Smart Technologies, Global Market Insights. He has over three years of experience in tracking emerging technology markets focusing on the evolution of the latest enterprise and telecom networking trends and their revenue impact on global and regional markets. Kasnale has an engineering degree in Computer Science and an MBA in marketing.
Disclaimer

CISO MAG did not evaluate/test the products mentioned in this article, nor does it endorse any of the claims made by the writer. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same. CISO MAG does not guarantee the satisfactory performance of the products mentioned in this article.

American Consumers Want More Control and Visibility into How Companies Use Their Personal Data: KPMG

personal data collection, Personal data. Data Privacy

A new KPMG survey revealed that U.S. consumers are becoming increasingly concerned with, and distrustful of, how companies use, manage and protect their personal data. According to the survey, 56% of Americans reported wanting more control over their personal data and insisted that both corporations and government must play an active role in protecting personal data.

The findings in the “New Imperative for Corporate Data Responsibility” report are based on the results from a survey of 1,000 respondents in the U.S. The sample was balanced to reflect the national representation of age, race, gender, and region. The online survey was fielded between May 19, 2020, and May 21, 2020.


As per the report, 97% of American consumers indicated that data privacy is important to them, with 87% characterizing it as a human right. However, consumers are deeply suspicious of what companies are doing with their data: 68% don’t trust companies to ethically sell personal data and 54% don’t trust companies to use personal data in an ethical way.

With consumers indicating that they see data privacy as a human right, and new legislation expected in the years ahead, it is critical that companies begin to mature privacy programs and policies. Consumer demands for the ethical use of data and increased control over their own data must be a core consideration in developing data privacy policies and practices.

– Orson Lucas, Principal, Cyber Security Services, KPMG 

Even though respondents indicated that data privacy is important to them, most Americans still engage in online behaviors they consider risky.

Key Findings

  • About 75% of Americans say they consider it risky to use the same password for multiple accounts, use public Wi-Fi, or save a card to a website or online Yet, more than 40% engage in those behaviors.
  • While 65% of Americans reported avoiding opening email attachments from unknown senders, only 31% install mobile device security software and 20% use their own virtual private network (VPN) when possible.

Part of the challenge for corporations will be getting employees and customers to do their part in protecting their own data. Developing defensible notices with understandable language and data protection controls that guide employees and consumers have to be embedded in the data security agenda.

– Steve Stein, Principal, Cyber Security Services, KPMG, and Co-author of the new report.

While most survey respondents indicated that consumers themselves have a responsibility to protect consumer data, even more, want the government and companies to play a role. KPMG found that:

  • 9 in 10 Americans insist companies (91%) and the government (90%), have a responsibility to protect consumer data.
  • Almost all (91%) agree the following data privacy rights of the California Consumer Privacy Act should be extended to all U.S. Citizens: the right to delete personal data, and the right to know how their data is being used.
  • More than nine in 10 Americans say companies should put data privacy guidelines and policies in place, be held responsible for corporate data breaches, take corporate data responsibility seriously, and take the lead in establishing corporate data responsibility.

Prior to  January 1, 2020, U.S. companies already had some regulation impacting the collection and use of consumer data including Gramm-Leach-Bliley Act, Fair Credit Reporting Act, Health Insurance Portability and Accountability Act, state data breach laws, and others (including General Data Protection Regulation for Europe). With the advent of the California Consumer Privacy Act, the expectations have been raised and consumers (at least in California) have increased the right to reject the sale of their data and additional rights to access and delete.  We would expect other states to follow and may see a Federal statute in the coming years that codifies these rights for all Americans.  Murkier perhaps is whether Americans, when given such rights, will act on these rights.

– Steve Stein

Business Recommendations

To be able to provide consumers with increased control over their data, KPMG recommends businesses to consider leveraging data discovery and protection tools, and explore novel uses of emerging technologies such as blockchain and artificial intelligence (AI). These technologies can help organizations better track the source of their data, assure its accuracy, make it easily discoverable, protect it and build greater external visibility into the data being collected.

In fact, according to a survey of 600 global technology executives conducted in late March/early April, KPMG found that improving cybersecurity and data privacy is one of the top four objectives for which their organizations are investing in emerging technologies such as process automation, smart analytics, cloud computing, artificial intelligence, and blockchain.

Additionally, KPMG also recommends:

  • Mature data privacy programs and policies. It is critical that companies begin to mature privacy programs and policies before new legislation come into effect. Specifically, companies should consider adopting a principles-based approach to retain the flexibility needed to comply with the evolving regulatory environment and technology landscape.
  • Provide customers with greater control over their data. With expanding requirements to give consumers greater control over their personal data — businesses should consider leveraging data discovery and protection tools, and exploring novel uses of blockchain, and artificial intelligence.
  • Conduct privacy assessments to manage data privacy challenges in light of COVID-19. As new return-to-work solutions are introduced amid COVID-19, companies should conduct privacy impact assessments. Specifically, where new technologies and processes are implemented, it is prudent to assess and document the potential implications and decisions around data privacy.
  • Make sure consumers are aware of your data privacy strategy. To build trust and goodwill with consumers, companies that develop strong data privacy controls will want to make sure consumers know about them.