Home Blog Page 134

Effective Security Incident Handling – The Need of the Hour

effective security incident handling, incident response, incident response strategy, incident response playbook,

Today, cyberattacks are getting more complex, precise, and targeted than ever before. Add to this the sheer volume of security alerts and false positives; it is like finding a pin in a haystack. Naturally, the IT teams are suffering burnout, leaving organizations with humongous security and corresponding monetary risks.

According to a recent survey on the Cost of a Data Breach in 2020, the global average cost of a data breach stood at $3.86 million for the current year. These numbers were a shade lower than last year (where the average cost was $3.92 million); however, when it came to the Middle East region, the numbers have nearly doubled ($5.97 million per breach). It is the second-highest only behind the U.S., where the average cost per breach amounts to $8.64 million in monetary losses.

Any scale or level of breach does not just affect your business or clients but also the reputation of your organization, which is the utmost important asset. In a digital economy, facing a security incident, cyberattack, or data breach, is highly inevitable. However, remediating that threat and quick recovery from the aftermath is what counts. It limits the scope of damages that affects the reputation. But how do we do it? Is incident response the answer to it? If yes, then what are the steps for effective security incident handling?

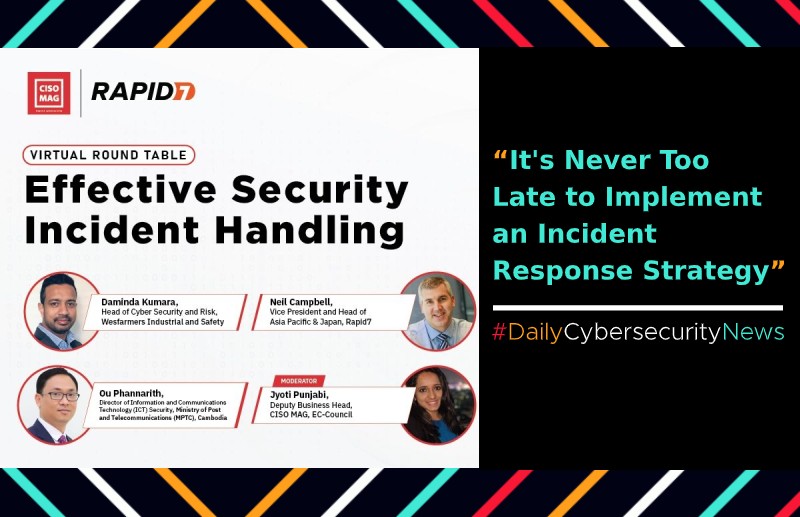
To discuss this, CISO MAG got on board Daminda Kumara, Head of Cyber Security and Risk, Wesfarmers Industrial and Safety; Phannarith Ou, Director of ICT Security, Ministry of Post and Telecommunications, Cambodia; and Neil Campbell, VP and Head of Asia Pacific & Japan, Rapid7; in a virtual round table that was moderated by Jyoti Punjabi, Deputy Business Head, CISO MAG, EC-Council.

The discussion was divided into two parts, where the first half was dedicated to developing a comprehensive incident response plan, whereas in the second part, the panel discussed the post-incident response methodology.

Developing an Incident Response Playbook

Although you cannot control how and when the threat actors target your company, you can always control how you respond. Responding quickly and effectively to cyber incidents can help improve your company’s cyber resilience.

effective security incident handling, incident response, incident response strategy, incident response playbook,

“If an organization does not already have an incident response strategy in place then this is a huge problem. This should have been done 10-15 years back.”

– Daminda Kumara, Head of Cyber Security and Risk, Wesfarmers Industrial and Safety

When asked, “When and where should an organization develop an incident response strategy?,” Daminda Kumara said, “If an organization does not already have an incident response strategy in place, then it is a huge problem. They should have designed this 10-15 years ago.” Concurring with Kumara, Neil Campbell said, “Yes, it should have been there for years, but it’s never too late.”

As far as the new or upcoming organizations are concerned, the panel asked them to prioritize cybersecurity and incident response as the top priority. “Every organization needs to have an incident response playbook. This playbook will be your go-to for any incident,” the panelists said in unison.

However, for creating this playbook, Kumara suggested to seeking inputs from all stakeholders, finance teams, supply chains, admin, HR, etc., highlighting that all departments need to be involved because each department has its own take on what is important, vulnerable, and needs to be protected. Thus, involve as many people as possible, and define every stakeholder’s role in case of an incident.

Campbell added, “Have an incident response playbook in a checkpoint format so that it is easier to understand and follow. Also, these checkpoints need to include respective law enforcement and external parties based on the operational domain of your organization.”

Another important team that could steer you away from reputational damage in case of incident response is the public relations (PR) team. This team should always be in the loop in case of incident response. Because, as Campbell said, “Communication and PR can either help you or hurt you.” So, take a cue and put PR on the first page of your incident response playbook.

Additionally, have mock incident response drills just like we have fire drills. Run simulations of attacks. Create red and blue teams if required and handle all scenarios of fake cyberattacks. How does this help? It helps create muscle memory. It always keeps you in shape and readiness. It is not just a defensive but a highly proactive approach to cybersecurity, which many do not even consider. It requires analysts to fend off attackers, review the results of their response, and apply lessons learned to avoid a repeat threat.

What Should be a Post Incidence Response

The answer to this question was given in the first part itself – refer to the Incident Response Playbook that you have defined. As said earlier, cyberattacks and breaches are inevitable aspects of the modern digital world. Thus, when they occur, immediately spring into action and start following your playbook.

The priority after any security incident is stopping the spread. For this, you need to depend on your IT team. But if it is beyond their understanding, seek expert help. Hire a third-party technology and cybersecurity partner that can do this for you if you already don’t have it. However, Campbell suggests to “choose them wisely.” Because you should not go overboard and select the top or the best, this can bore a hole in your pocket. Instead, as Campbell said, “choose one according to your needs and industry.”

effective security incident handling, incident response, incident response strategy, incident response playbook,

“Post incidence Review (PIR) is a good opportunity for learning what went wrong.”

– Neil Campbell, VP and Head of Asia Pacific & Japan, Rapid7


Once you have taken care of the technical aspect of the incident response, move towards the communications part. Before any other stakeholder is informed, it is mandatory to inform the law enforcement authorities. Various countries have various frameworks in place, which adhere to different timeframes for reporting an incident. The GDPR gives only 72 hours for reporting; however, the ACSC in Australia gives 30 days for reportage. So, know the laws applicable to your geography and adhere to it.

In your incident response playbook, you should have already noted the list of all internal and external stakeholders other than the law enforcement authorities that need to be informed about the incident. Write a letter and inform all of them individually on a personal level. Also, as Phannarith Ou said, “Be honest in your communication.” If it is your mistake, then accept it and tell what remedial measures are being taken to resolve the issue. Maintain transparency at all points of time. Give them an entire blueprint of recovery and issue updates about the ongoing process. This makes them not lose trust in your organization and helps them in retaining confidence.

Campbell pointed out, “Honesty and accuracy in your statements are very important in all your incident response communications. Because at some point this communication might be dragged into court and the lawyers will scrutinize every statement that you have made. So do not take that chance.” Kumara suggested an added filter for all communications. He said, “Get your executive from the incident response team to approve and endorse all communications related to the incident response written by the PR team, so that accuracy is maintained.”

effective security incident handling, incident response, incident response strategy, incident response playbook,

“For cybercrime framework, look at international best practices. Baseline them and localize them according to your own needs and geography.”

– Phannarith Ou, Director of ICT Security, Ministry of Post and Telecommunications, Cambodia

At the end of the discussion, a Q&A session was hosted for all curious attendees. One of the most frequently asked questions was if there was a framework that would help create a playbook for comprehensive incident response. Ou delightfully answered this question by saying, “For the cybercrime framework, look at international best practices. Baseline them and localize them according to your own needs and geography.” Campbell also suggested the attendee to refer ISO/IEC DIS 27035-3(en) standard, which is specially developed for incident response and referred to as a baseline by many global companies.

The session saw a fruitful discussion on effective security incident handling and covered almost all aspects of the pre-and post-incident response, and typically stressed the need of having a well-defined playbook that could be your go-to in times of chaos.

CISO MAG would like to take this opportunity to thank all our panelists and attendees for their valuable time and feedback in making this virtual round table discussion a huge success!

Related News:

The State of Ransomware: From Evolution to Progression

The Evolving Role of Endpoint Detection and Response

Episode #6: How Insurance Fraud is Evolving (and Anti-fraud Measures)

Evolution of Insurance Fraud, BAE Systems Applied Intelligence

Insurance Fraud continues to evolve as it has done for centuries. Fraudsters, too, have evolved their techniques and upped their game. Dennis Toomey, Global Director, Counter Fraud Analytics and Insurance Solutions – BAE Systems Applied Intelligence, talks about the role of technology and the evolution of fraud in the insurance sector. Interestingly, he says there is a convergence of Fraud, Cybersecurity, Risk, and Compliance.

Toomey, with 28 years of international experience, provides top-class consulting on counter fraud analytics and operations to individuals and corporate organizations to help position their companies at the forefront of their industries. He guides them to develop strategic plans to advance their companies’ mission and objectives and to promote revenue, profitability, and growth as an organization.

Toomey says fraudsters are highly adaptive and continually change tactics, strategies, and even modes of operation. In past years, most schemes seemed focused on false auto thefts and property arsons. Fraud schemes today have shifted much more to bodily injuries and suspicious activities by medical providers. Workers’ compensation and auto insurance most notably have seen these changes in tactics. In response, insurers increasingly are adopting advanced analytics to counter the changing nature of the fraudulent activity.

Fraudsters can test system thresholds by filing many different applications online and manipulating rates by changing rating factors to reduce the premium. In addition, analysis suggests that a significant amount of claims fraud is perpetrated through illegally obtained policies. By shifting from a reactive to a more proactive posture, insurers are reducing fraud at policy inception and denying rate evaders a chance to file false claims once the ill-gotten policy is in force.

A growing challenge is rising point-of-sale or underwriting fraud to illicitly reduce premiums, observes Toomey.

Disruptive technology like RPA, AI, and data analytics are helping in curbing or detecting fraud. For instance, the time window for investigations has reduced from five years to one year, thanks to technology.

Europol and European Commission Launch New Decryption Platform to Combat Encryption Misuse

Network Encryption, DSCI Whitepaper on Encryption

Europol and the European Commission jointly launched a new decryption platform to boost Europol’s encryption capabilities during criminal investigations. The innovative decryption platform, controlled by Europol’s European Cybercrime Centre (EC3), was created in collaboration with the European Commission’s Joint Research Centre. The platform allows the authorities to decrypt information that is obtained lawfully in criminal investigations.

The agencies stated that the new platform leverages in-house expertise and includes both software and hardware tools to provide effective assistance to national Member State investigations. EC3 works to reinforce the law enforcement response to cybercrime in the European Union and also focus on diminishing various cybercriminal activities like online fraud, identity thefts, and information misuse, etc.

“The launch of the new decryption platform marks a milestone in the fight against organized crime and terrorism in Europe. In full respect of fundamental rights and without limiting or weakening encryption, this initiative will be available to national law enforcement authorities of all Member States to help keep societies and citizens safe and secure,” the official notice stated.

Ylva Johansson, EU Commissioner for Home Affairs, said, “This decryption platform will help police to investigate terrorism and organized criminality. It will be important in the fight against online child sexual abuse. National police forces can now send lawfully obtained evidence to Europol for decryption.”

The decryption platform is a step towards safeguarding the fundamental rights of the citizens.

Europol’s Executive Director Catherine De Bolle said, “The new Europol Decryption Platform, funded by the European Commission, will allow us to further enhance our support for Member State investigations. This is the result of successful inter-organizational collaboration within the EU and shows the potential for further joint work and support for the EU innovation hub for internal security.”

Minimize COVID-19 Workplace Disruptions, With Help from CISA

COVID-19 cybersecurity lessons

COVID-19 has disrupted today’s workplace for the foreseeable future. Beginning in mid-March 2020, employees transitioned in mass from their onsite offices to a variety of off-site locations. Federal workers are not expected to return to the office almost a year later, and many businesses are still struggling with if and when to bring their employees back onsite. To help address cybersecurity-related issues, the Cybersecurity and Infrastructure Security Agency (CISA), part of the Department of Homeland Security, developed a short guide on teleworking best practices. CISA published the Telework Essentials Toolkit on October 5, 2020.

By Thomas Wolfe, Head of Strategic Development, TalaTek

CISA was established on November 16, 2018, after the Cybersecurity and Infrastructure Security Agency Act of 2018 was signed into law. Its mission is to “address interoperability among the public safety community at all levels of government, foster intergovernmental cooperation, and identify and leverage common synergies.” Its role is to improve cybersecurity across the federal government, increase cybersecurity protections, and coordinate cybersecurity programs with the states. Its programs are applicable to both the public and private sectors.

CISA’s Telework Essentials Toolkit is broken into three sections that target guidance to executive leaders, IT professionals, and teleworkers.

The four strategic areas to help executive leaders drive cybersecurity strategy, investment, and culture are:

  1. Organizational policies and procedures
  2. Cybersecurity training requirements
  3. Moving organizational assets
  4. Cyber secure, hybrid culture

The six technical and tactical areas to help IT professionals develop security awareness and vigilance are:

  1. Patching and vulnerability management
  2. Enterprise cybersecurity controls
  3. Multi-factor authentication
  4. Organizationally approved products
  5. Frequent backup
  6. Domain-based message authentication

The four technical and tactical areas to help teleworkers develop increased security awareness and vigilance are:

  1. Configure and harden
  2. Secure practices and organizational policies
  3. Opening email attachments by clicking links
  4. Communicating suspicious activities

Like any good toolkit, the tools in this resource are designed to be used together to build a secure workplace. Common themes for each group include establishing and following organizational policies and procedures, taking basic security measures, and developing security awareness.

Enacting Organizational Policies and Procedures

All organizations, regardless of size, need to enact clear and consistent cybersecurity policies that employees at every level can follow. The Toolkit addresses this for each group. Executives can find links from organizations such as the National Institute of Standards and Technology and the National Cybersecurity Alliance on driving strategy, development, implementation, updating, and championing cybersecurity and telework policies and procedures.

IT professionals get details on how to implement and monitor these policies and procedures. Links to other CISA resources such as “Guidance on Supplementing Passwords with Multifactor Authentication” can show IT staff how to get started.

Teleworkers are also integral to successful cybersecurity practices and are encouraged to follow organizational policies, practices, and procedures for handling sensitive data (once leadership establishes and communicates them).

Taking Basic Security Measures

Whether remote workers are using company-provided devices or their own laptops, they need to observe and obey basic security measures. And it’s up to company executives to address the secure configuration and updates to those devices in the policies and procedures. CISA makes it clear that both the IT professional and the teleworker must patch, update, configure, and harden the devices they use.  The Toolkit offers links to resources such as “NSA Telework and Mobile Security Guidance” and “Making Your Remote Workforce Cyber Ready.”

IT professionals must execute and maintain the patch and vulnerability management policy to keep organizational hardware and software up to date and continuously scan for vulnerabilities. Links to “CISA Tips and Understanding Patches and Updates” and “GCA Patch to Protect” can show them how.

Teleworkers get how-to help on configuring and hardening their home network by changing the default password to a complex one and reconfiguring routers to use WPA2 or WPA3.

Driving Security Awareness

It can’t be said enough. Hackers and cybercriminals are constantly on the lookout for weaknesses and vulnerabilities. And the human element—remote employees working on home networks—are an organization’s weakest link. So it’s vital to cultivate a culture of cyber awareness and vigilance and to include security training for employees at every level. The Toolkit provides resources to develop such programs. Executive leaders can find links to the “Cyber Readiness Institute Cyber Readiness Program” and “Creating a Cyber Ready Culture in Your Remote Workforce: Five Tips.”

Tips for IT professionals include keeping up to date on new cybersecurity controls such as zero-trust architecture and new collaboration and teleconferencing tools.

Teleworkers get information warning them of the dangers of opening email attachments and clicking links as well as advice on communicating suspicious activities to company leadership.

The Telework Toolkit also includes additional resources, including the Global Cyber Alliance’s Cybersecurity Toolkit for Small Businesses, and links to additional CISA guidance for all three levels.

This is not CISA’s first foray into teleworking safety. CISA has provided many additional teleworking resources and guidance since the coronavirus has changed the landscape of how and where people work. These include General Teleworking Guidance, VPR Related Guidance, Video Conferencing Guidance, and Wireless Related Guidance.

With a COVID-19 resurgence predicted for this winter and no end in sight, CISA’s Teleworking Toolkit comes at a vital time for many organizations that are unsure of how to navigate the waters.


About the Author

Thomas WolfeThomas Wolfe has more than a decade of business development, project management, technical writing, and editing; he has proposal writing and management experience in the public and private sectors. In his business development and proposal writing/management capacity, Thomas has been instrumental in winning awards with a combined amount of more than $100M. In his technical writing, editing, and project management capacities, Thomas has supported such federal agencies as the Federal Aviation Administration, General Services Administration, Department of Homeland Security, and Department of Education, among others. Thomas graduated from West Virginia University with a major in English, Professional Writing, and Editing. Thomas’ personal pursuits include reading, collecting vinyl records, and hiking the Appalachian Trail, with a goal of hiking the AT from Harpers Ferry National Historic Park in West Virginia to Grayson Highlands State Park in Virginia (509 miles).
Disclaimer

Views expressed in this article are personal. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.


Related stories:

The Underbelly of COVID-19: Malware and Ransomware Ramp Up

COVID-19 Pandemic is a Silver Lining for Cybersecurity

What Edward Snowden Taught Us About Insider Threats

Insider Threats

We all know the name, Edward Snowden. Variously described as a whistleblower, hero, or even a traitor, in the security community, he is what is known as an ‘insider threat.’ With Snowden and his wife recently seeking dual citizenship in Russia and the U.S., his story has been brought back into the spotlight, offering an opportunity to reflect on what his actions taught the world, and particularly cybersecurity professionals, about the danger of both malicious and unintentional insider risks.


By Trevor Daughney, VP, Product Marketing, Exabeam

A former contractor to the CIA, in 2013 Snowden copied and released thousands of classified documents to journalists, many relating to secret and controversial government surveillance activities in the U.S. and abroad. As details were gradually released in the media during subsequent months, the scandal surrounding Snowden grew, and having fled to Moscow, he has been living in Russia since, the subject of ongoing criminal charges from the U.S. government.

The Complex Nature of Insider Threats

Snowden’s story is just one example of the potential risk posed by insider threats. But his activities, while being the highest-profile, are by no means typical of the scenarios faced by most organizations, particularly in the commercial context.

In most cases, insider threats will take three key forms. The “compromised” insider is considered by many to be the most problematic because this person has generally done nothing but innocently click on a link or input a password. This is often the result of phishing campaigns, which present users with a link to an authentic-looking website to convince them to input login credentials or other sensitive data.

As the name suggests, the “malicious” insider is typically an employee or contractor who steals information for financial gain or seeks to disrupt or damage an organization to hurt, punish, or embarrass it. The various Apple engineers who were charged with data theft for stealing driverless car secrets for a China-based company are just one of many examples.

And alternatively, but no less dangerous, is the “accidental” or “negligent” insider. This can be particularly challenging, because irrespective of how much care organizations and employees take over cybersecurity, mistakes happen. Something as simple as an employee leaving a workstation unlocked in a shared area could result in a data breach. Accidental incidents can even happen to executives — for example, a CEO might not even think twice about sending sensitive information to their personal account to work on over the weekend. The point is, no one is immune from the risks associated with insider threats, so the way organizations approach these various challenges is central to their safety.

These are far from isolated risks. According to the Information Risk Research Team at Gartner, for example, insider threats account for 50-70% of all security incidents, and for security breaches specifically, insiders are responsible for three-quarters of them. The consequences can be severe, with the Ponemon Institute estimating that insider threats cost $8.76 million per year per affected company. This is not least because it takes an average of 280 days to identify and contain each breach — a frightening scenario for any organization to face. Unfortunately, the cost is only increasing with each passing year. From 2018 to 2019, the cost of a single malicious insider attack increased by 15%, from $1.4 million in 2018 to $1.6 million in 2019.

Protection and Mitigation

One of the biggest issues when it comes to insider threats is that they can be very hard to predict, let alone mitigate. If an outsider is trying to get around a firewall, for example, software and security protocols can be employed to prevent it. However, most traditional cybersecurity solutions don’t turn that focus inwards to reveal what happens within the organization.

While increasing awareness about insider threats has helped organizations address some of the core risks, there remain a series of steps that many still don’t apply as rigorously as they should. The first is simple: invest in training. Without a doubt, some accidental and compromised insider attacks can be prevented by simply training end-users on spotting and avoiding phishing attempts.

Next, focus on user behaviors. Most security protocols can benefit from user and entity behavior analytics (UEBA), and by understanding typical behaviors, security teams can more easily detect when a problem occurs. And thirdly, organizations should arm themselves with the technology infrastructure and tools to see the whole picture and address the layered challenge of insider threats. Systems powered by artificial intelligence and machine learning are now used by organizations around the world as the foundation for effective, proactive protection, with security information and event management (SIEM) systems one example of how these technologies are being applied to the risks posed by human error, negligence, and malicious insiders.

In the current climate of uncertainty and risk, organizations that can double down on their approach to insider threats will be better placed to protect their employees, systems, and data in the long term. A proactive strategy that blends technology and training can eliminate the insider threat blindspots that still pose a major risk across millions of organizations today.


About the Author

Trevor DaughneyTrevor Daughney is Vice President of Product Marketing at Exabeam. Trevor is a marketing executive with a track record of building high performing teams to take enterprise cybersecurity SaaS and software technology and turn them into successful global businesses. Prior to Exabeam, he led enterprise product marketing at McAfee, Ping Identity, and Symantec. Trevor approaches marketing with a global mindset and builds on his experiences living and working in the US, Canada, and Asia. He has an MBA from the University of California, Berkeley.
Disclaimer

Views expressed in this article are personal. The facts, opinions, and language in the article do not reflect the views of CISO MAG and CISO MAG does not assume any responsibility or liability for the same.


Related story: Insider Threats: A Byproduct of the New Normal

After U.S., Vietnam Government Suffers Supply Chain Attack

Vietnam

Security researchers identified a supply-chain attack targeting the Vietnam Government Certification Authority (VGCA) that compromised the agency’s digital signature toolkit. According to an investigation from the security firm ESET, cybercriminals exploited the software installers hosted on the VGCA’s website “ca.gov.vn” to inject spyware known as PhantomNet or Smanager.

The Vietnamese government has mandated the use of digital signatures and digitally signed documents. The VGCA is the authorized certificate provider. It also develops and distributes a digital signature toolkit and offers cryptographic certificates used to sign documents.

The “SignSight” Attack

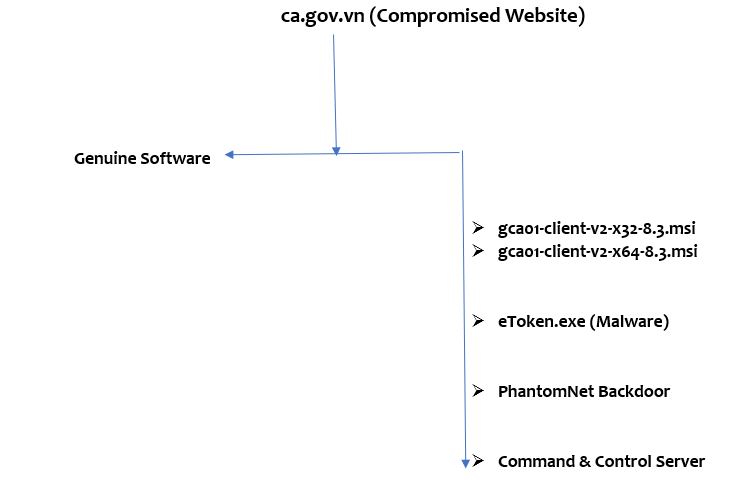
The researchers named the cyber operation as SignSight attack, which occurred from July 23 to August 16, 2020. ESET researchers stated that cybercriminals modified two software installers, “gca01-client-v2-x32-8.3.msi” and “gca01-client-v2-x64-8.3.msi” for 32-bit and 64-bit Windows systems, which are available for download on the agency’s website. Attackers manipulated the software and added a backdoor to compromise users of the legitimate application.

“We were able to confirm that those installers were downloaded from ca.gov.vn over the HTTPS protocol, so we believe it is unlikely to be a man-in-the-middle attack,” ESET researchers said.

The URLs that redirected the users to malicious installers include:

https://ca.gov[.]vn/documents/20182/6768590/gca01-client-v2-x64-8.3.msi

https://ca.gov[.]vn/documents/20182/6768590/gca01-client-v2-x32-8.3.msi

PhantomNet Supply-Chain Attack

The users could get affected by PhantomNet spyware if the compromised software hosted on the official website is downloaded and installed on the targeted system. Once installed, the altered software hides its malware and runs the PhantomNet backdoor that tricks users as a regular file named “eToken.exe.”

The Attack Flow                                              

“We believe that the website has not been delivering compromised software installers as of the end of August 2020 and ESET telemetry data does not indicate the compromised installers being distributed anywhere else. The Vietnam Government Certification Authority confirmed that they were aware of the attack before our notification and that they notified the users who downloaded the Trojanized software,” the ESET researchers added.

SolarWinds Hack Affected Yet Another Tech Giant – Microsoft

Microsoft Affected in SolarWinds Hack

The SolarWinds Orion IT management software hack is now acting like a tornado, sucking up everything and growing larger with every passing moment. SolarWinds, in its SEC filing, acknowledged that nearly 18,000 of its customers were affected in their software hack and that they were all notified about it. However, no customer names were disclosed, and it took down the client list post the disclosure of the hack. But five days after the official notification, Microsoft has now accepted that they were hacked. It is probably one of the reasons why they partnered with FireEye to create a Killswitch for stopping the Sunburst malware in the first place.

Related News:

Microsoft and FireEye Create a “Killswitch” for Sunburst Malware Affecting SolarWinds’ Orion

Microsoft Feels the Ripples of SolarWinds Hack

The U.S. National Security Agency (NSA), on Thursday, issued a “cybersecurity advisory” describing how threat actors were leveraging the abused authentication mechanisms for disrupting Microsoft Azure cloud services. It directed users to lock down their systems and observe the remedial measures as prescribed by Microsoft.

However, this was just the tip of the iceberg. The actual impact was to be known only a day later when Microsoft said, “Like other SolarWinds customers, we have been actively looking for indicators of this actor and can confirm that we detected malicious SolarWinds binaries in our environment, which we isolated and removed.” The spokesperson who issued this statement also added that there were no traces of the hackers further using their compromised systems to move parallelly. Sources have suggested that Microsoft’s cloud services have been extensively used by hackers to scroll through new potential targets while the mainframe remains untouched.

Related News:

U.S. Government Takes the Wind Out of SolarWinds’ Sails…for the Time Being!

The Affected Parties

The investigation of the hack has been ongoing, and the list seems to be getting appended with a new name every passing moment. But Microsoft seems to have answers to what geo targets and the industries were most affected by the SolarWinds hack.

Microsoft President Brad Smith, in a blog post, stated that 80% of the targets were from the U.S.; however, threat actors also targeted seven other nations – Belgium, Canada, Israel, Mexico, Spain, and the United Arab Emirates. He further noted that since the investigation is still on, this list could get bigger.

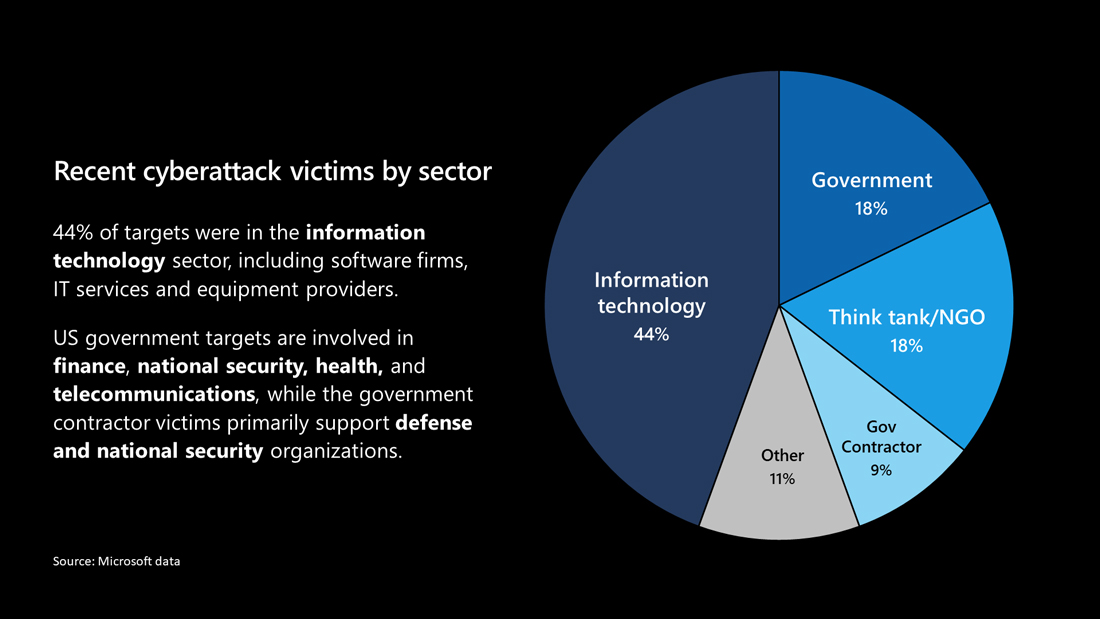
Microsoft has also shared the list of sectors that were affected by the SolarWinds hack based on the data gathered from Microsoft’s Defender Anti-Virus software. This list not only includes the IT and Governmental sector but also non-governmental organizations and think tanks, which is rather surprising.

Microsoft affected in SolarWinds Hack

At the end of the blog, Brad Smith said something that is the need of the hour:

This is a third and final sobering development worth noting from what has obviously been a challenging year. This comes from the intersection between cyberattacks and COVID-19 itself.


We live in a more dangerous world, and it requires a stronger and more coordinated response.


A more effective strategy as we enter a new year.


Put simply, we need a more effective national and global strategy to protect against cyberattacks. It will need multiple parts, but perhaps most important, it must start with the recognition that governments and the tech sector will need to act together.

Related News:

White House Confirms Cyberattack on U.S. Dept of Treasury and Commerce

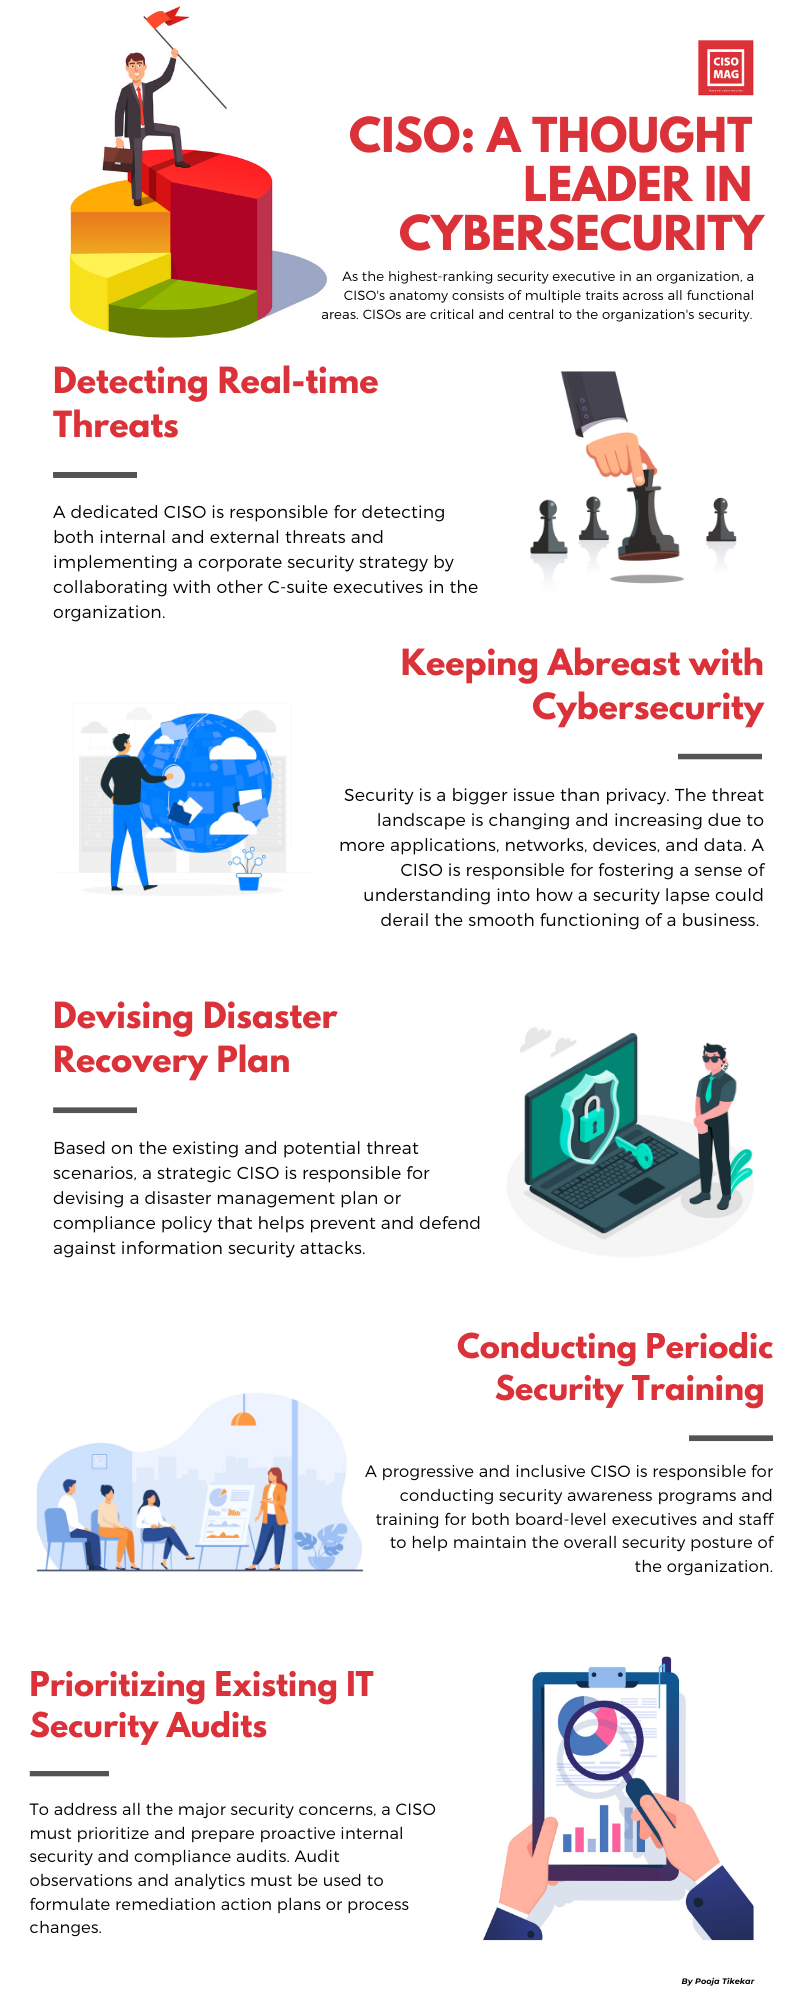
Are You a Thought Leader CISO? [INFOGRAPHIC]

1 in 3 CISOs feel biggest challenge of endpoint solution is its complexity

Information security is a growing concern for small and big businesses alike. While we do everything we can in our power to protect the enterprise, Chief Information Security Officers or CISOs will always be central to security. A CISO is a thought leader with the technical know-how of risk-free business operations. He is tasked with multiple responsibilities, and in the present times – when everyone is working remotely – CISOs have been crucial in ensuring seamless business continuity.

Here are the key traits of a thought leader CISO:

CISO_ A Thought Leader


Read CISO MAG to learn about CISO strategies and best cybersecurity practices. Get all the 2020 Editions here. Subscribe now!

About the Author

Pooja Tikekar is a Feature Writer and part of the editorial team at CISO MAG. She writes news reports and feature articles on cybersecurity technologies and trends.

More from the author.


Irish Data Regulator Fines Twitter $547K for 2019 Data Breach

PM Modi Twitter

Seems like Twitter’s is ending 2020 on a bitter note! From multiple data breaches to a series of celebrity account hacks, the social networking giant suffered multiple challenges in 2020. And the latest fine from Ireland’s data regular adds to its woes. On December 15, the Irish Data Protection Commission (DPC) fined Twitter €450,000 ($547,000) as an “effective, proportionate, and dissuasive measure” for a data breach that occurred in January 2019. The data leak was a result of a vulnerability that made users’ private tweets public.

The DPC’s investigation found that Twitter infringed Article 33(1) and 33(5) of the GDPR guidelines by delaying notifying the breach on time to the authorities.

“The draft decision in this inquiry, having been submitted to other Concerned Supervisory Authorities under Article 60 of the GDPR in May of this year, was the first one to go through the Article 65 (dispute resolution) process since the introduction of the GDPR and was the first Draft Decision in a big tech case on which all EU supervisory authorities were consulted as Concerned Supervisory Authorities,” the DPC said in a statement.

As per the GDPR guidelines, organizations are required to notify about any data breaches, to the respective data regulators, within 72 hours after becoming aware of the incident. It is also mandatory for data breach victims to document what data has been compromised and how they responded to it.

Twitter Says…

Commenting on the data breach fine, Twitter’s Chief Privacy Officer Damien Kieran said, “Twitter worked closely with the Irish Data Protection Commission (IDPC) to support their investigation. We have a shared commitment to online security and privacy, and we respect the IDPC’s decision, which relates to a failure in our incident response process. An unanticipated consequence of staffing between Christmas Day 2018 and New Years’ Day resulted in Twitter notifying the IDPC outside of the 72-hour statutory notice period. We have made changes so that all incidents following this have been reported to the DPC in a timely fashion.

We take responsibility for this mistake and remain fully committed to protecting the privacy and data of our customers, including through our work to quickly and transparently inform the public of issues that occur. We appreciate the clarity this decision brings for companies and consumers around the GDPR’s breach notification requirements. Our approach to these incidents will remain one of transparency and openness,” Kieran added.

Microsoft and FireEye Create a “Killswitch” for Sunburst Malware Affecting SolarWinds’ Orion

Sunburst killswitch, Sunburst malware kill switch, Sunburst malware detection, sunburst malware fix, sunburst malware, fix for sunburst malware

The recently reported supply chain attack on the SolarWinds Orion platform has grabbed the attention of many eyeballs because the Orion IT management platform is used by several U.S. government agencies like the Dept. of Treasury, Dept. of Commerce, and Dept. of Homeland Security. Apart from the public sector clientele, SolarWinds Orion is also extensively used by companies in the private domain, including Boeing and Los Alamos National Laboratory. Thus, the extent of damage caused by the attack can only be estimated till the final assessment reports come in.

Related News:

White House Confirms Cyberattack on U.S. Dept of Treasury and Commerce

However, to stop further spread of the nefarious Sunburst malware and to provide interim relief to SolarWinds’ clients, a group of tech firms — Microsoft, FireEye, and GoDaddy ­ — collectively devised a “Killswitch” to take control of one of the domains that attackers used for transmitting the malicious code into victims’ systems.

Sunburst Malware Killswitch

FireEye, in its report, stated that the hacked networks were seen communicating with a malicious domain name, avsvmcloud[.]com, which is one of the many domains that attackers had set up to control and communicate with the affected systems. Thus, gaining control over this domain would at least provide relief to SolarWinds by preventing further spread. For this, researchers from Microsoft and FireEye shook hands, and with the help of domain registrar company, GoDaddy, devised a “killswitch” to take over the malicious domain.

The story was first reported by investigative journalist Brian Krebs, who  stated, “There were signs over the past few days that control over the domain had been transferred to Microsoft.”  FireEye, in its statement, accepted applying a killswitch to the domain and has additionally reconfigured it so that the Sunburst malware does not operate under certain conditions.

Shedding more light on the Killswitch application, a FireEye spokesperson said,

Depending on the IP address returned when the malware resolves avsvmcloud[.]com, under certain conditions, the malware would terminate itself and prevent further execution. FireEye collaborated with GoDaddy and Microsoft to deactivate SUNBURST infections.

This killswitch will affect new and previous SUNBURST infections by disabling SUNBURST deployments that are still beaconing to avsvmcloud[.]com. However, in the intrusions FireEye has seen, this actor moved quickly to establish additional persistent mechanisms to access to victim networks beyond the SUNBURST backdoor.

This killswitch will not remove the actor from victim networks where they have established other backdoors. However, it will make it more difficult for the actor to leverage the previously distributed versions of SUNBURST.

Since the trio of the tech companies now has control over the malicious domain, it could very well mean that more names of SolarWinds’ affected clients will be revealed.

Related News:

U.S. Government Takes the Wind Out of SolarWinds’ Sails…for the Time Being!