
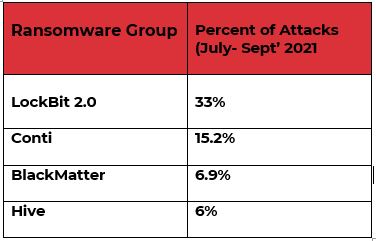
Despite constant cybersecurity awareness and law enforcement actions, ransomware operators continue to evolve their hacking techniques to deploy file-encrypting malware, causing damages to targeted critical systems. An analysis from Intel 471 researchers found 612 ransomware attacks attributed to 35 different ransomware variants. Of the attacks, over 60% were tied to four ransomware variants – LockBit 2.0, Conti, BlackMatter and Hive.
“The rise in the ransomware variants Intel 471 has tracked comes as some more notable variants of years past have faded into obscurity. While it’s common practice for ransomware groups to suddenly disappear and re-emerge under a new name, groups’ motives for doing so aren’t well-known. The past few months have been different: we’ve seen several groups go quiet after external actions have forced groups to slow down operations or shut down altogether,” the report said.
According to the report, the most prevalent ransomware variants from July-September 2021 were:
Most Affected Sectors
- Manufacturing
- Consumer and industrial products
- Professional services and consulting
- Real estate
And the impact on life sciences, health care, financial services, and nonprofit sectors was lesser.
Also Read: Rags to Riches! The Evolution of Ransomware Operators
The Rise of New Ransomware Groups
The ransomware threat landscape increased rapidly with various ransomware variants and attacks. The NCC group revealed that the number of ransomware attacks reported in November 2021 had increased by 1.9% compared to October 2021. There is a 50% increase in organizations targeted by new ransomware variants like PYSA and LockBit, with a 400% rise in government sector victims.
“Be it due to law enforcement, infighting amongst groups, or people abandoning variants altogether, the RaaS groups dominating the ecosystem at this point in time are completely different than just a few months ago. Yet, even with the shift in the variants, ransomware incidents as a whole are still on the rise,” the report added.
What the Experts Say
 Speaking to CISO MAG about the rise of ransomware attacks, cybersecurity researcher Bob Diachenko said, “Ransomware evolves similarly to any software proposition on the market – there are large groups operating as marketplaces with ransom-as-a-service solutions, state-sponsored APTs, and many independent actors, most of which are simply trying to reach a low-hanging fruit in the form of misconfigured databases.”

