
Dickey’s BBQ Pit, a popular barbecue restaurant chain in the U.S., is the latest victim of a data theft. Security experts from cybersecurity firm Gemini Advisory uncovered a data leak incident that appears to have been active since July 2019. Hackers illicitly obtained over three million customers’ credit card information after compromising Dickey’s Point-of-Sale (POS) systems in 156 restaurant locations out of 469.
The data breach came to light after attackers posted the stolen data for sale on Joker’s Stash, a dark web marketplace for trading stolen cards data. The researchers stated that the hackers were advertising a massive collection of payment card details for sale, dubbed “BLAZINGSUN,” at $17 per card. It also found that the payment transactions were processed via the outdated magstripe method.
“BLAZINGSUN would contain 3 million compromised cards with both track 1 and track 2 data. They purportedly came from 35 US states and some countries across Europe and Asia,” the advertisement claimed.
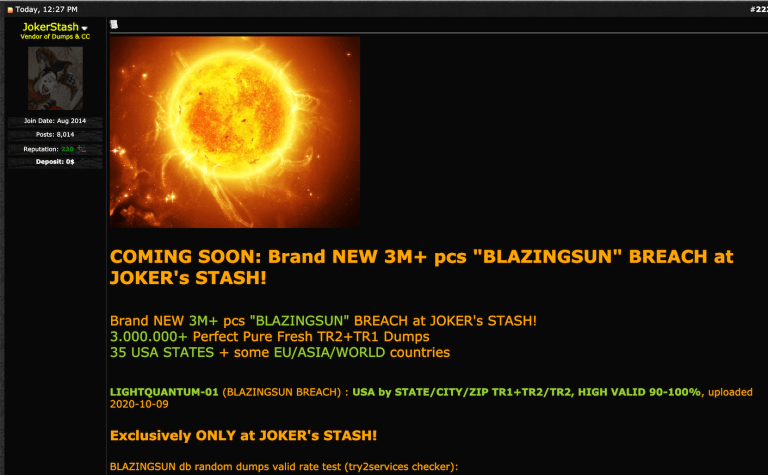
While it is unclear how long the attackers were in the network, Dickey’s stated it has reported the incident to the FBI for further investigation. The company also asked its customers to monitor their banking statements for any fraudulent activity. “Based on previous Joker’s Stash major breaches, the records from Dickey’s will likely continue to be added to this marketplace over several months,” the researchers added.
Joker’s Stash – A Hacker’s Marketplace
A similar report from Gemini Advisory revealed that hackers kept payment card details of Wawa’s customers on Joker’s Stash. In an official statement, Wawa confirmed that hackers tried to sell customers’ card information that breached in the security incident occurred on December 10, 2019. The data belonged to 30 million Americans and over one million foreigners from more than 100 different countries. It is believed that Joker’s Stash contains debit/credit card details from the U.S., European, and global cardholders, including their geolocation data like state, city, and ZIP Code.

 systems)